Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

XWorm

8
Global rank
7 infographic chevron month
Month rank
6 infographic chevron week
Week rank

XWorm is a remote access trojan (RAT) sold as a malware-as-a-service. It possesses an extensive hacking toolset and is capable of gathering private information and files from the infected computer, hijacking MetaMask and Telegram accounts, and tracking user activity. XWorm is typically delivered to victims' computers through multi-stage attacks that start with phishing emails.

RAT
Type
Ex-USSR
Origin
15 July, 2022
First seen
11 October, 2026
Last seen

How to analyze XWorm with ANY.RUN

RAT
Type
Ex-USSR
Origin
15 July, 2022
First seen
11 October, 2026
Last seen

IOCs

IP addresses
135.232.92.137
135.233.95.135
20.190.159.68
48.209.138.168
86.99.231.143
23.52.181.212
204.79.197.203
48.192.1.64
23.11.40.157
150.171.109.100
172.211.123.248
92.123.104.22
23.207.210.139
150.171.109.104
48.209.138.189
74.179.77.164
2.23.246.101
104.126.37.130
20.190.159.2
131.253.33.203
Hashes
eb62f37cf7a250d71cebd722f32c840e25b6bbabf1c6bd51c198b4f76d8829c4
fe8fd00b2d78caf6724c444a383dd3fd9eb2eb8e5d85d48ead88fa9fdd176df0
0f62f28ed58691b144b6ade2edf53cc9706d35d71fea48ae15cebbaebebbd376
a8894cd6fd264efccd2a1ab326e566a074a6ad9be7623639d6a83fbaf4878fa5
b3f953b4da6ed51954d2e35427b7abfaf97927fda526eccff4153fcfeab214da
bc3c08b67f4af98419e23d46abb094554a4bbc7a87b948e9958def69270d19ad
57e1d79347748f6d9f398783942afbf071b943cc3ba50ceed9289558fdaf41d5
2ba2b60589e90fd793c5b184daef74fc2e7ab4aedf06fae8ce678c04e18c0a46
e57d504c3db46de712f62f5604abcac0f97e67dc516adcbb2f5be543a86a31a7
21379eec5b36274a49cea6d8910544175764c38969097b106e790b3c1254940a
df30570b987151d3f8583fccebb8caba792f66c0d1f736b43cef0abd247ee0c0
a8bd235303668981563dfb5aae338cb802817c4060e2c199b7c84901d57b7e1e
60c1da5e2e7ef58cef79504e7209086509d74d27ef347ea59a7f432c4cf56041
f503f62c81c5ca541d6b3cca94537f372a2e83924829d0b8b889149baf2dca69
cfdb9ac8feda4192f8cad311286db4ca33bc204c94cd718c35bad41f4dfc3354
c0b54b77c49e8ed92ae0de6791b2a39affcceef06fca399a428ac89237815759
902928d11d3f23cea4486649e8bb0d565c12f390d7a7073eb6f9e77f67999570
1a2672684aafaed7e40d909affde42bd1283a877ba400802d13967a0effff171
0202b502ee0f0547eab58d8e7bbf6c561ba0d4eb71a48fdf3c51e200cede073d
906055e56391a9362ff2e354e21a9e0ded69135ecadbea28eabcdf931686acbd
Domains
th.bing.com
ocsp.digicert.com
self.events.data.microsoft.com
crl.microsoft.com
slscr.update.microsoft.com
www.bing.com
ecs.office.com
nexusrules.officeapps.live.com
settings-win.data.microsoft.com
google.com
oneocsp.microsoft.com
dns.msftncsi.com
client.wns.windows.com
fe3cr.delivery.mp.microsoft.com
activation-v2.sls.microsoft.com
login.live.com
www.microsoft.com
watson.events.data.microsoft.com
play.google.com
update.googleapis.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f11%2f2026%2c%204%3a05%3a13%20pm
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.c9a5f8c1-9d31-4bf3-802b-962ce601e1a7&pid=dsb
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://watson.events.data.microsoft.com/telemetry.request
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 6051
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 7861
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 11489
comments 0

What is XWorm malware?

XWorm is a remote access trojan (RAT) that gives cybercriminals unauthorized access to a victim's computer. It is a modular malware, meaning that it can be customized to perform a variety of malicious tasks, such as stealing sensitive data and cryptocurrency, launching DDoS attacks, and deploying ransomware. It first came into the spotlight in July 2022 and is believed to have originated in the ex-USSR.

XWorm is sold as a malware-as-a-service (MaaS), which makes it extremely dangerous. It lowers the barrier to entry and opens hacking opportunities to more people. Since its first appearance in the global threat landscape in July 2022, XWorm has gone through several iterations. As of August 2023, the 4.2 version and the 5.0 version were the latest ones available for purchase.

Criminals use multi-stage attacks to deploy XWorm on victims’ computers. For example, an attack might start with a phishing email that contains a malicious Word document attachment. When the document is opened, it will load an .rtf file from an external link. This file will contain an Excel spreadsheet with macros that will execute a PowerShell script, which will then download XWorm onto the computer.

Technical details of the XWorm malicious software

XWorm is developed with the .NET Framework, which makes it a significant threat to Windows systems. The malware is also configurable, offering a wide range of tools for manipulating the infected machine.

Here are some of XWorm’s key capabilities:

  • Encrypted connection: XWorm is capable of maintaining a secure connection with its C&C server, even during poor network conditions.
  • Information gathering: The malware can collect a wide range of information from the infected computer, including credit card numbers, browsing history, bookmarks, downloads, as well as Firefox and Chromium passwords and cookies.
  • Account hijacking: XWorm can hack Discord, Telegram, and MetaMask accounts, as well as get hold of WiFi keys and product keys.
  • User activity tracking: The malware enables attackers to monitor the victim’s activities on their computer by logging their keystrokes, automatically saving webcam images, listening to their microphone, scanning their network connections, and viewing opened windows.
  • Clipboard access: XWorm can retrieve the information that has been copied to the clipboard and replace victims’ crypto wallet credentials with those of the attacker.
  • File management: It can gain control of a computer’s file system to transfer sensitive documents and content to its C2 or download additional malware and run it.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

In order to bypass User Account Control (UAC), XWorm attempts to get administrator permissions on the infected computer. This allows it to make changes to the system without requiring user consent. To ensure persistence, the malware adds itself to the list of programs that run automatically when the computer starts up by editing the registry.

It is also polymorphic, meaning that the malware’s code regularly transforms itself to throw detection software off course. Although XWorm has a built-in functionality to terminate its execution once it senses that it is launched in a virtualized environment, the ANY.RUN sandbox has no problem identifying the malware.
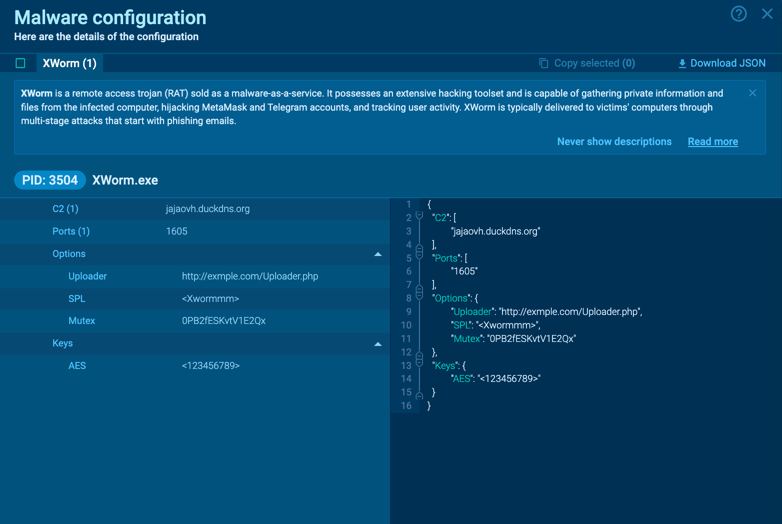
XWorm’s configuration

XWorm’s configuration

Execution process of XWorm

The malicious behavior of XWorm can be easily uncovered by uploading it to the ANY.RUN sandbox. Here is a sample of this malware on the platform.

Immediately upon execution, XWorm drops an executable file into the Startup directory (“C:\Users\admin/AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\XWorm.exe”) and into the Roaming directory (“C:\Users\admin/AppData\Roaming\XWorm.exe”).
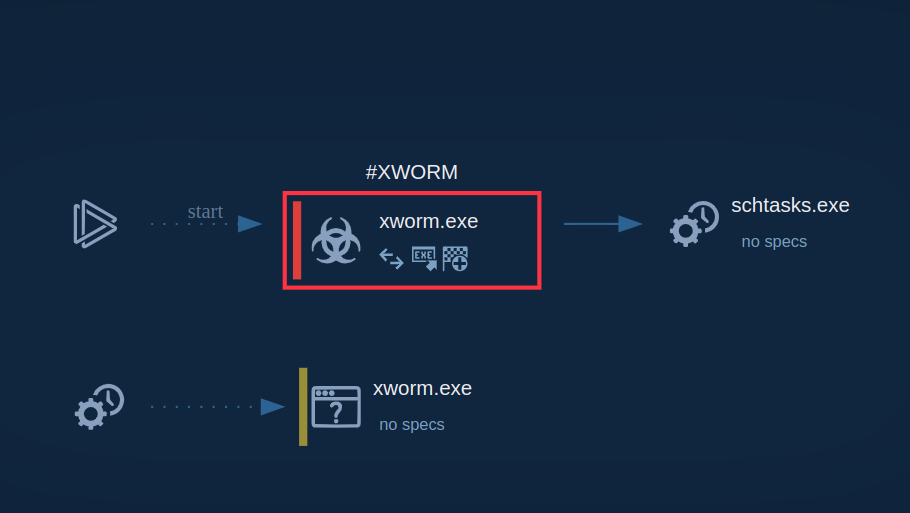
XWorm’s process graph

XWorm’s process graph

For the latter directory, a persistent service is created using the Task Scheduler. Malware checks for an external IP, which we can bypass with ANY.RUN’s Residential Proxy feature. After this, XWorm starts sending beacons to the C&C server, waiting for commands to execute.

Read a detailed analysis of XWorm in our blog.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Distribution methods of the XWorm malware

As with most malware families, email phishing campaigns serve as XWorm’s main gateway to victims’ computers. The attack begins with an email containing an attachment. By exploiting different social engineering techniques, threat actors can persuade a user to download the attached file and open it.

Analysts have observed several file formats used by attackers, including .rtf, .lnk, and .pdf. In most cases, the email attachment itself does not contain any macros and is used primarily to kick off a chain reaction that involves downloading several other files, executing PowerShell scripts, and finally delivering the payload.

Such attacks can be facilitated by specialized tools, such as Freeze[.]rs and SYK Crypter, which are equipped with advanced capabilities for circumventing defense systems to drop a variety of malware families including Remcos RAT, njRAT, and RedLine Stealer.

One of the most recent XWorm attacks targeted businesses in Germany. It involved sending a .docx document to victims with a name that suggested it contained hotel reservation information. Instead of using macros, the file exploited the Follina vulnerability (CVE-2022-30190) to run external malicious files and a PowerShell script, which eventually dropped XWorm.

Conclusion

XWorm retains considerable staying power due to the consistent updates and wide availability, making it a top concern for organizations around the world. To protect your system from this threat, you need to have a stricter approach towards handling any links or files arriving in your inbox from unknown senders.

Instead of downloading documents and opening URLs, you can first analyze them in the ANY.RUN sandbox to quickly understand whether the file is malicious or not. ANY.RUN also provides you with a detailed report about the malware, such as its IOCs and TTPs. This information can be used to protect your organization from future attacks.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
GREENBLOOD screenshot
GREENBLOOD
greenblood
GREENBLOOD is a Go-based ransomware that uses concurrent ChaCha8 encryption to lock entire Windows environments in under a minute while systematically destroying backups, disabling defenses, and threatening double extortion through a Tor-based data leak site.
Read More
Agent Tesla screenshot
Agent Tesla
agenttesla trojan rat stealer
Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold.
Read More
Ransomware screenshot
Ransomware
ransomware
Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying.
Read More
DoubleTrouble screenshot
DoubleTrouble
doubletrouble
DoubleTrouble is a new-generation Android malware designed to quietly infiltrate mobile devices, harvest sensitive data, hijack financial operations, and maintain long-term persistence. Unlike commodity Android trojans, it blends advanced evasion, dual-stage infection, and dynamic payload updates, making it a rising mobile threat for both consumers and organizations.
Read More