Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
34
Global rank
34 infographic chevron month
Month rank
41 infographic chevron week
Week rank

RedLine Stealer is a malicious program that collects users’ confidential data from browsers, systems, and installed software. It also infects operating systems with other malware.

Stealer
Type
ex-USSR
Origin
1 March, 2020
First seen
6 October, 2026
Last seen
Also known as
RedLine

How to analyze RedLine Stealer with ANY.RUN

Type
ex-USSR
Origin
1 March, 2020
First seen
6 October, 2026
Last seen

IOCs

IP addresses
23.3.89.106
2.19.198.50
57.153.246.3
109.238.86.106
20.165.94.54
23.59.18.102
40.126.32.140
23.11.41.157
131.253.33.203
193.178.158.57
172.211.123.250
48.192.1.65
142.251.151.119
193.178.158.107
23.207.210.132
74.178.240.61
23.216.77.10
48.209.6.48
95.100.158.113
20.190.159.73
Hashes
f7e4aae30ab2bda60bead5fd5a29a36685d768df007d3399d3047768babae200
b6dcec10039fba99019a6de818d433847efad62fae59851e328ec42396dfd9cb
48630371e6b16f2762363848c0b42a8e68a16c94c104c66b9f53d5e0e043c77f
1440e81f80958229541b1da9d33a03e9aa5848545033c98eff59e332aa2b59e9
69da8695703652e366c1d93bda1544ff25d6033fa6ee4985ad8b6a3b721fe2fb
9976b3be2bccc1e252ab830916d22d705464c051e0dea8cbf5b7c180507b1007
83b3fb548b094aa66bbf9da57c4d5a49acaa76914121e90aa05fb53ab47367e0
3118a029c644a831c1ae3e55047b2598462c70c45053425d985de24c22b04eb1
fb96993b3255d2127fc439f4711b4fb5b41f35d0c9bd2dc6d16acf27efe58223
66e6eed42917b8a0dd2a80c8bddbe153841bd7c307ae8fc09bf81be8e6549461
870d8065347e60122d782496b9ba1880ea7826ad86febcc3b19e056f1da894c3
e417ba1cf0820012cb021e0379e03eb86214af14d73da2211028a1a2e946499f
2afb23be1a2d4970aa3c9ef5931c0eae79f7b328d2de1c7002e01553e80cca7e
98f8d63319caa0e0c1befc36dc4ab07d39e8da0441f8637545baf66369d0df2d
9ff0a33b9f8c9b3a9d433027b92a89c884f8f56f6b479e4280b511e83c875ac4
9c0e7f829b46760aab20eda352a6429d98dd902feb26614737dc696ebc7d690e
8c84975c307fe358a91a274cf1c5660efc3da98886911b30694f5ba9d59f0844
09f7928f9e6a8a76325a97d2211a0b46ee7084ad5d77bc502ff304754d3c5854
fc6baefabf70531614823a4a3ee6fd5b85d3fd62462b87ec79b301d0ca8ba75f
bf9093ed2e66c0312cce9a42ac851ef1f8c707a2aecbd63dc8e4ff6eb3097b53
Domains
www.microsoft.com
fe3cr.delivery.mp.microsoft.com
settings-win.data.microsoft.com
self.events.data.microsoft.com
slscr.update.microsoft.com
ecs.office.com
login.live.com
activation-v2.sls.microsoft.com
google.com
www.google.com
www.bing.com
ocsp.digicert.com
oneocsp.microsoft.com
th.bing.com
client.wns.windows.com
crl.microsoft.com
watson.events.data.microsoft.com
dontlookhere.com
pagead2.googlesyndication.com
17.aa.4t.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.google.com/
http://www.bing.com/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://193.178.158.107/login.php
http://193.178.158.107//uploads/3be88cae27594406_16.php
http://1844336234//
http://193.178.158.57/bin/e6efd8bd3bf0fae2_moratorium_0.96.2.9_install.exe
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
http://193.178.158.107/bin/91ee2c4a395d400d_persevering_5802.5.8372_install.exe
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://193.178.158.107//uploads/068449785ecaa0ce_20.php
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is RedLine Stealer?

RedLine Stealer or RedLine is malware that can collect users’ confidential information and deliver other malicious programs. The availability and flexibility of the stealer cause financial loss, data leakage, targeting both enterprise and personal devices. Healthcare and manufacturing sectors suffer the most from these attacks.

The malware appeared in March 2020 according to the Proofpoint investigation. Since then RedLine has just gained steam. It was on the rise during the COVID-19 pandemic and is still active. On July 1st, 2021 the malware was found on the legit-looking website that provides privacy tools. However, based on the payload analysis, only malware can be found there.

General description of RedLine malware

RedLine is an infostealer that takes information about users from browsers, systems instant messaging, and file transfer protocol clients. The main target is passwords, credit card information, username, location, autofill data, cookies, software set, and even hardware configuration like keyboard layout, UAC settings, etc. The virus is also capable of stealing cryptocurrency.

The malicious program acts as a typical stealer such as Raccoon or Pony: it uploads and downloads files, executes commands, and reports information about the infected machine. Moreover, attackers make use of RedLine to deliver ransomware, RATs, trojans, and miners.

The infostealer is quite popular as there is no problem finding it. Underground forums, C&C panels offer different options such as malware-as-a-service versions or a subscription. The price varies from $100 to $200.

One cannot tell that RedLine Stealer is a sophisticated malware like ransomware. It has the usual features typical for this family. However, it is .Net malware written in C# and the code quality is high enough to reveal an experienced programmer behind it. Cybercriminals also work hard to update malware, like downloading secondary payloads and advanced filtering features.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

RedLine malware analysis

ANY.RUN allows researchers to perform the analysis and watch the RedLine in action in an interactive sandbox simulation
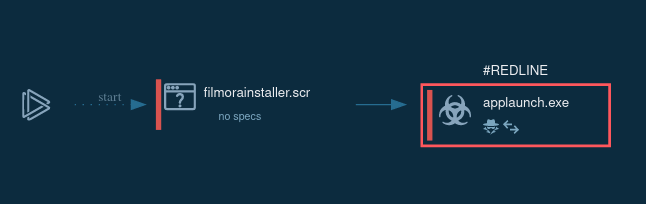
redline stealer process graph

Figure 1: Displays the lifecycle of RedLine in a visual form as a process graph generated by ANY.RUN
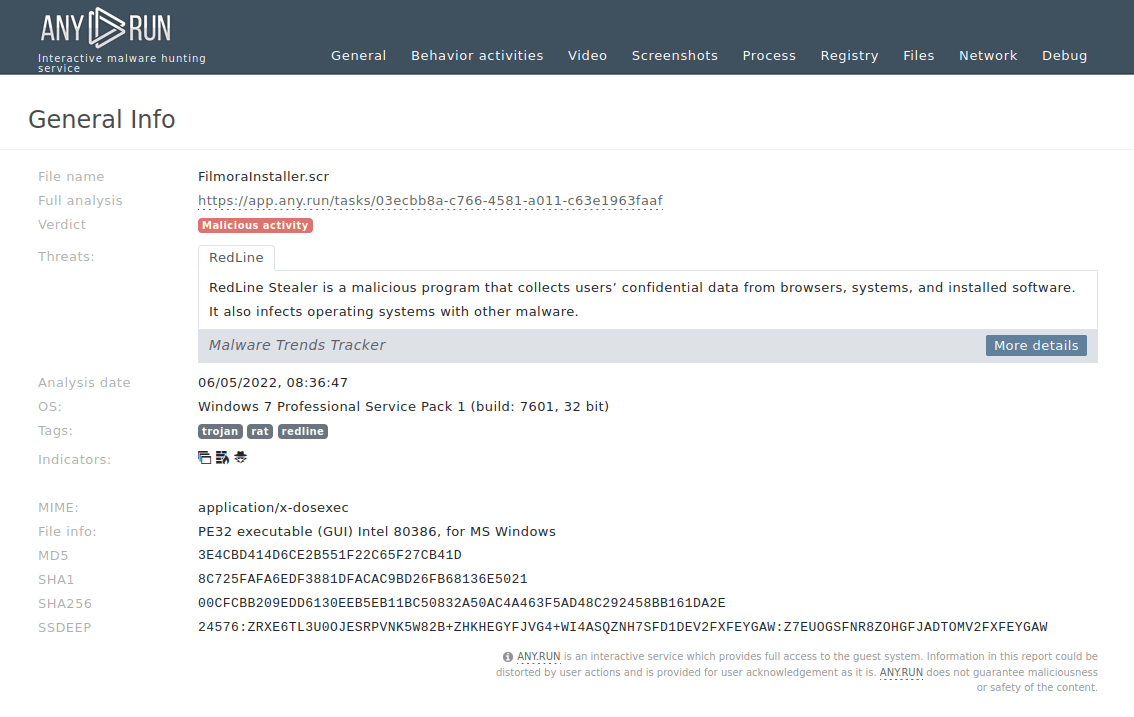
redline stealer report

Figure 2: A customizable text report generated by ANY.RUN allows users to take an even deeper look at the malware and helps to share the research results.

RedLine Stealer execution process

Typically the execution process of that stealer is plain and straightforward. Based on the analysis, the main binary launches itself and the parent process stops. It also may be dropped from another binary or be the main binary itself. When a child process is created, the main malicious activity starts – RedLine collects information from the infected system such as passwords and others, and sends it to the Command & Control panel. When all information is collected and sent, the stealer just quits execution. Stolen information is sent in both non-encrypted and base64 encoded formats.

Distribution of RedLine

Attackers are not very creative with the delivery method of the virus. However, as the ransomware story, the method works perfectly – social engineering for different email campaigns including business email compromise, spam, fake updates, ads in Google result in malicious attachments or links. We can notice the big variety of file formats here:

  • Office
  • PDF
  • RAR and ZIP
  • Executable files
  • JavaScript

If you open the files in the attachment, RedLine will download other malicious programs.

How to detect RedLine infostealer using ANY.RUN?

At the moment, analysts can quickly recognize the info stealer because it will be tagged after Suricata IDS rules are triggered. Since the malicious program sends the stolen info to its panel just right after the start of the execution, it won't take a lot of time.

Conclusion

The best way to protect your organization or device from RedLine is to be cautious with suspicious files and links that get into your email. Your staff should be aware that even trustworthy sources can lead to infection and password or other credentials’ theft. It won’t take long to check a file in a sandbox such as ANY.RUN. Several minutes will be enough to detect RedLine and you will be good to go. Stay safe.
HAVE A LOOK AT

OnyxC2 screenshot
OnyxC2
onyxc2
OnyxC2 is a sophisticated Malware-as-a-Service platform sold on cybercrime forums that provides a turnkey solution for high-volume credential theft. The malware targets over 200 applications, scraping sensitive data from browsers, cryptocurrency wallets, and business-critical tools like FTP and email clients. It employs advanced evasion techniques, such as DLL sideloading and browser fingerprinting, to deliver encrypted payloads through legitimate signed binaries.
Read More
Neptune RAT screenshot
Neptune RAT is a Visual Basic .NET remote access trojan that gives attackers full control over infected Windows machines while stealing credentials from 270+ applications, hijacking cryptocurrency transactions, spying on victims in real time, and, in its most destructive mode, wiping the operating system entirely. Marketed openly on GitHub, Telegram, and YouTube as the "Most Advanced RAT," it is distributed under a malware-as-a-service model.
Read More
Cobalt Strike screenshot
Cobalt Strike
cobaltstrike
Cobalt Strike is a legitimate penetration software toolkit developed by Forta. But its cracked versions are widely adopted by bad actors, who use it as a C2 system of choice for targeted attacks.
Read More
Phobos screenshot
Phobos
phobos ransomware
Phobos is a ransomware that locks or encrypts files to demand a ransom. It uses AES encryption with different extensions, which leaves no chance to recover the infected files.
Read More
Backdoor screenshot
Backdoor
backdoor
A backdoor is a type of cybersecurity threat that allows attackers to secretly compromise a system and conduct malicious activities, such as stealing data and modifying files. Backdoors can be difficult to detect, as they often use legitimate system applications to evade defense mechanisms. Threat actors often utilize special malware, such as PlugX, to establish backdoors on target devices.
Read More
Gh0st RAT screenshot
Gh0st RAT
gh0st
Gh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.
Read More