Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Amadey

41
Global rank
42
Month rank
38 infographic chevron week
Week rank

Amadey is a formidable Windows infostealer threat, characterized by its persistence mechanisms, modular design, and ability to execute various malicious tasks.

Infostealer
Type
Likely ex-USSR
Origin
13 October, 2018
First seen
7 October, 2026
Last seen
Also known as
Amadey Bot

How to analyze Amadey with ANY.RUN

Infostealer
Type
Likely ex-USSR
Origin
13 October, 2018
First seen
7 October, 2026
Last seen

IOCs

IP addresses
3.250.92.156
23.11.41.157
48.209.138.189
2.16.164.11
135.232.92.137
88.221.169.152
20.190.160.130
2.21.239.135
48.192.1.65
2.16.204.139
172.211.123.248
204.79.197.203
74.178.240.51
23.216.77.19
23.52.181.212
74.178.240.61
48.192.1.64
20.190.159.75
95.100.158.114
23.207.210.139
Hashes
83f780cc5a06c91f35c200b45c2188d7714e72e53ddf8b483bc2cb77cc9a09b1
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
18fd6b193be1d5416a3188f5d9e4047cca719fa067d7d0169cf2df5c7fed54c0
9b8f8da7eff6082cd10031be23515de939663e89df599f14b7c506349b5881af
db0df14a9b2b7d568ebc94061b87e76fa4b50fb0ff9c9c3c5dd0de253a26ee43
d62e4f303b24580fbe37700b2e4c2769b633565dbe0ad95ba3cc345b5ce595d9
f7e4aae30ab2bda60bead5fd5a29a36685d768df007d3399d3047768babae200
ceebae7b8927a3227e5303cf5e0f1f7b34bb542ad7250ac03fbcde36ec2f1508
602c4c7482de6479dd2e9793cda275e5e63d773dacd1eca689232ab7008fb4fb
913eaaa7997a6aee53574cffb83f9c9c1700b1d8b46744a5e12d76a1e53376fd
58a8d69df60ecbee776cd9a74b2a32b14bf2b0bd92d527ec5f19502a0d3eb8e9
47576cae321c80e69c7f35205639680bf28010111e86e228ed191b084fac6b91
5b8d47451f847c1bde12caca3739ca29860553c0b6399ee990d51b26f9a69722
e2991a6f7a7a4d8d3c4c97947298fd5bacb3eaa2f898cee17f5e21a9861b9626
0aa66dff8a7ae570fee83a803f8f5391d9f0c9bd6311796592d9b6e8e36be6fc
a0415f14f5d72ad24e9c3a5c91517a0e3d22e1adbc3505c0c6e918b961f7a07d
c15ab85438728bf2c60d72b1a66af80e8b1ce3cf5eb08ba6421ff1b2f73acdf4
29d93dee7c01b2264778bc6b75f6ef76ea6ac53e9f4a334d83707229e7f482d2
b6cd5c6f2b54d89142679d599ed0a5dee6955a3b3f6b6673e46afe7a5a303cdc
6c15cb256b1c22170292589c6f589e64e164eb36ec7e84f0bd48149babb7c5fc
Domains
fe3cr.delivery.mp.microsoft.com
self.events.data.microsoft.com
ocsp.digicert.com
mynexa.io
slscr.update.microsoft.com
settings-win.data.microsoft.com
ecs.office.com
crl.microsoft.com
www.bing.com
www.microsoft.com
activation-v2.sls.microsoft.com
oneocsp.microsoft.com
google.com
th.bing.com
login.live.com
client.wns.windows.com
dns.msftncsi.com
nexusrules.officeapps.live.com
class1004.dothome.co.kr
www.benshamcentre.co.uk
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://mynexa.io/hfv23svj2/index.php
http://mynexa.io/hfv23svj2/plugins/cred.dll
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://193.148.56.155/111.exe
http://102.220.161.23/bin/screenconnect.clientsetup.exe
http://91.92.34.63:8888/quickb.msi
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Amadey malware

First seen about 5 years ago, Amadey is a modular bot that enables it to act as a loader or infostealer. It is designed to perform a range of malicious activities, including reconnaissance, data exfiltration, and loading additional payloads, which range from banking trojans to DDoS tools. It targets all versions of Microsoft Windows.

This malware’s capabilities include:

  • Privilege escalation
  • UAC bypassing
  • Keystroke logging
  • Screen capture
  • Downloading additional malware

While many adversaries primarily use this malware as a keylogger to steal credentials, it can also transform infected devices into spam email senders or add them to a botnet that adversaries use to launch DDoS attacks.

However, that’s not everything this threat is capable of. Owing to its modular design, Amadey can significantly expand its range of attack targets, enabling the extraction of a broader variety of information, such as files, login credentials, and cryptocurrency wallets.

Furthermore, current Amadey variants can recognize more than 14 antivirus solutions. This ability allows the malware to intelligently deploy a payload designed to evade the specific antivirus product installed on the compromised device.

In addition, this malware can move laterally, propagating to devices within the same network by pushing EternalBlue exploit onto victims. Although outdated, EternalBlue remains relevant, especially in public sectors like government and education, where end-of-life software usage is widespread.

As for the origin of this threat, little is known at this point. Older activity associated it with GandCrab campaigns, which might connect Amadey to the REvil gang or one of their affiliates. Additionally, Amadey is distributed on Slavic-speaking underground forums, which possibly places its origin in one of the ex-USSR territories.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

How to get more information from Amadey malware

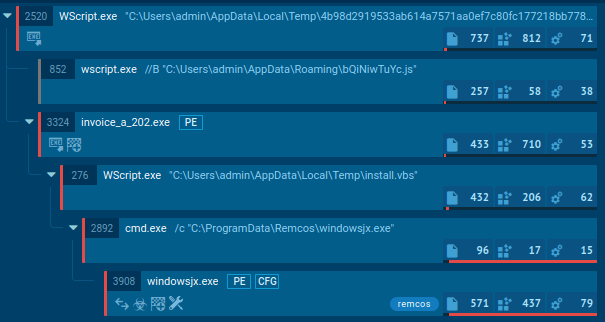
In ANY.RUN, users can safely detonate Amadey samples and analyze it dynamically in a fully interactive cloud sandbox. Our service automatically collects and displays the execution data in user-friendly formats, such as this process graph.

Analyze malware for free in a fully interactive cloud sandbox – sign up now!
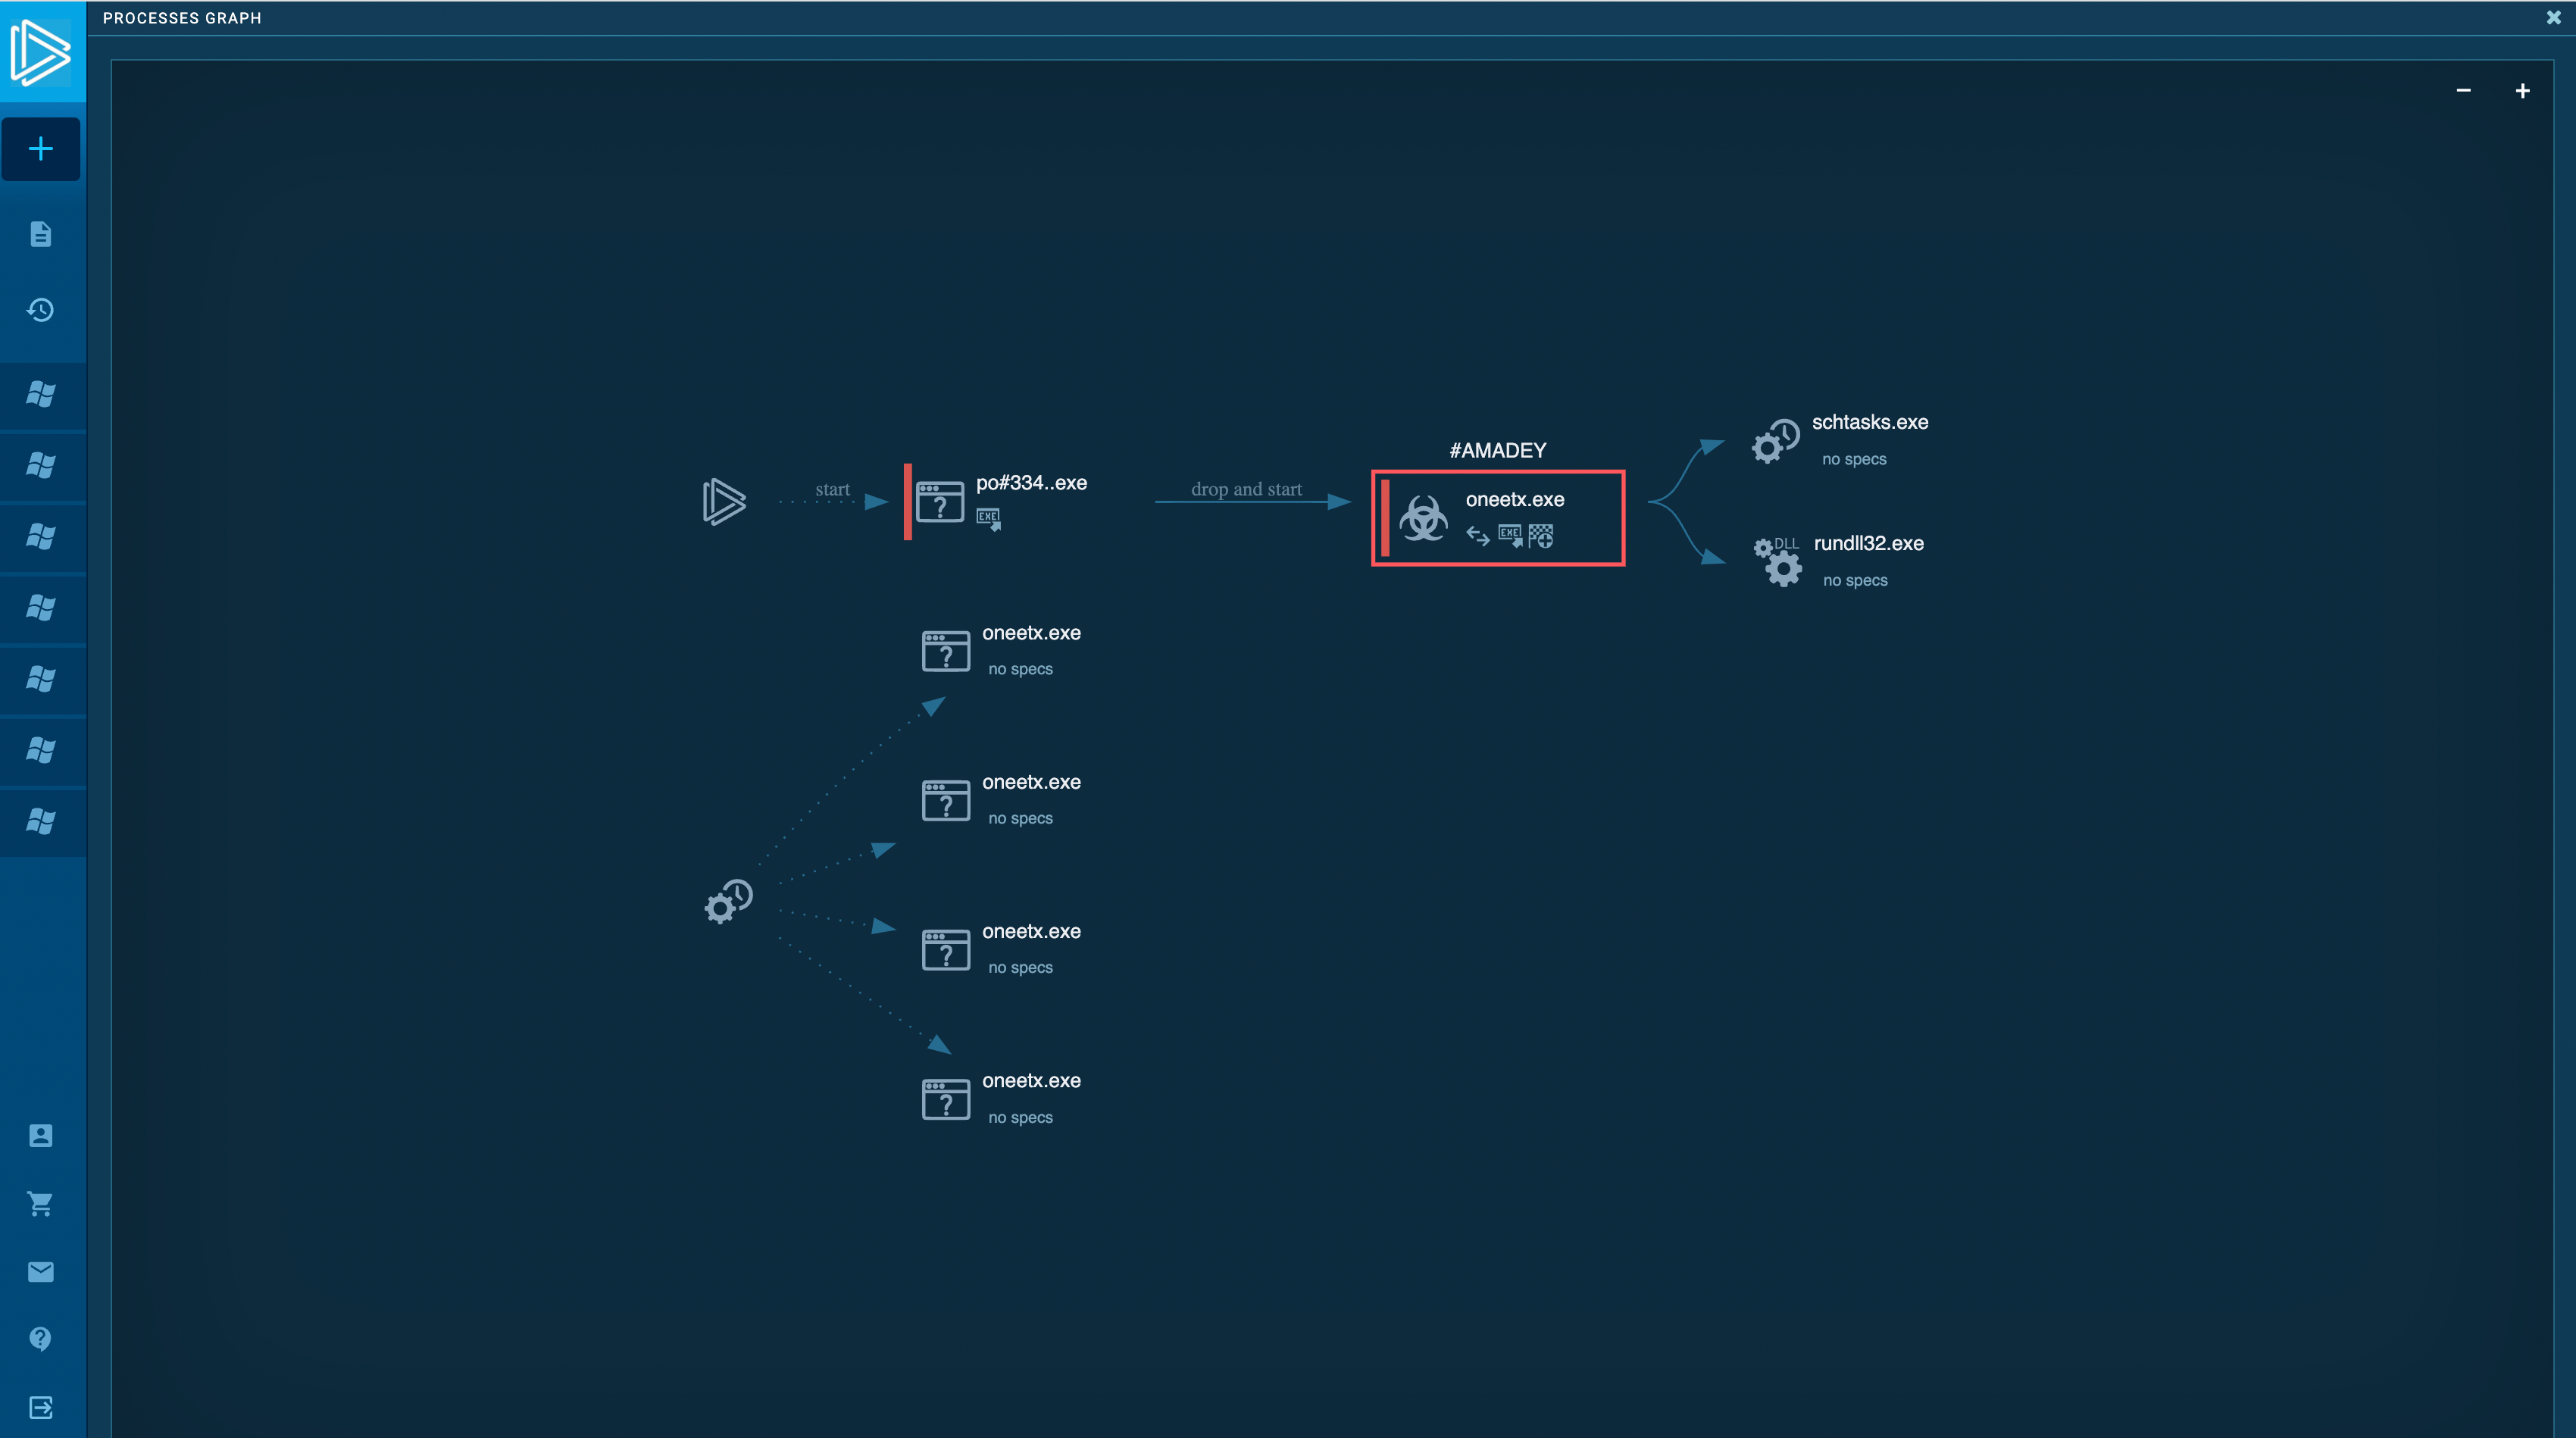
amadey Figure 1: A graph showing Amadey’s execution process

ANY.RUN detects Amadey using Suricata rules, allowing analysts to identify both new and old samples from this family. We also provide configuration details. This way, analysts can access important sample information like its version, options, and C2 addresses. The configuration is typically extracted within the first 10 seconds of launching a task. This ensures quick access to information.
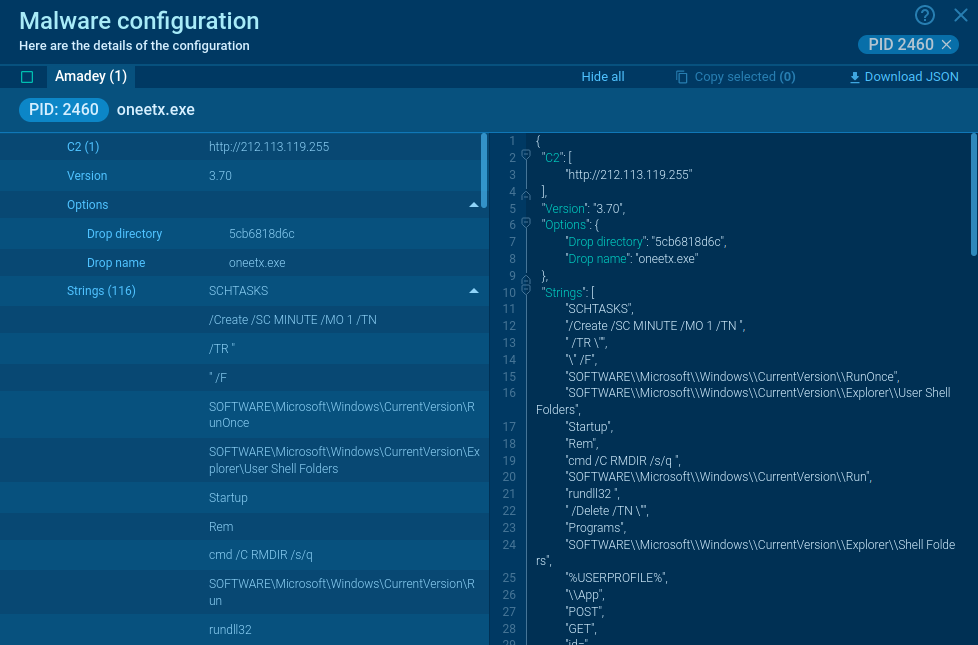
amadey malware Figure 2: Amadey’s malware configuration

Amadey infostealer execution process

Once, when Amadey initiates its execution, the malware duplicates itself into a TEMP folder (sometimes naming itself bguuwe.exe). Following that, it modifies the Registry and creates a scheduled task to achieve persistence. Subsequently, Amadey sets up C2 communication and transmits a system profile to the adversary's server. While active, Amadey takes screenshots at regular intervals and stores them in the TEMP directory, ready to be transmitted to the C2 server with subsequent POST requests.

Amadey often serves as a loader for other malicious programs, such as in this task.

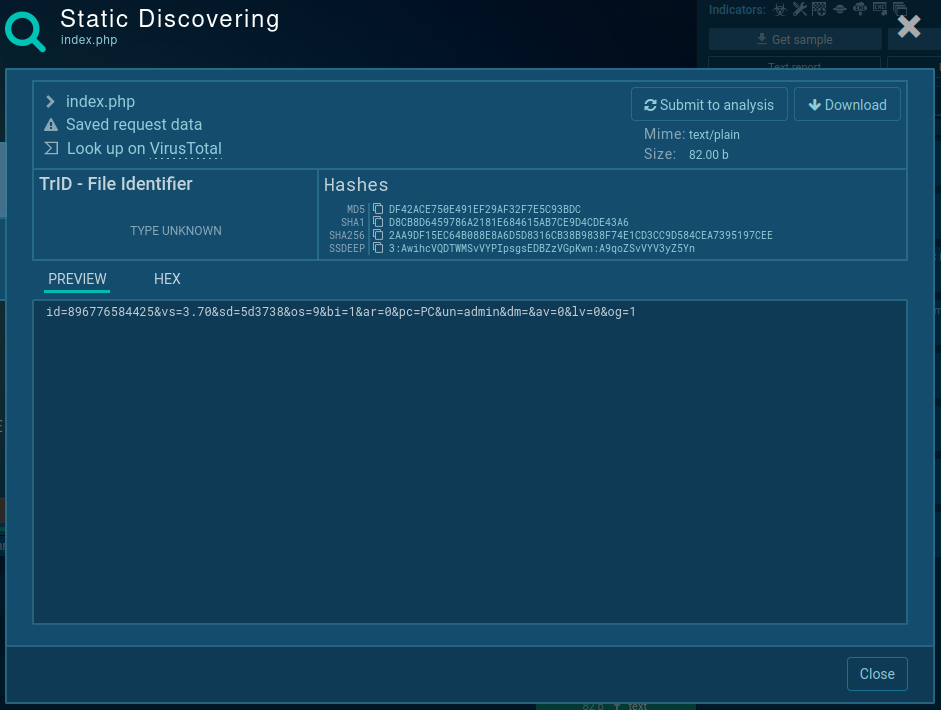
Also, Amadey has a very specific structure of POST requests, that can be used to identify it with a high degree of probability:

Figure 3: Information about infected machine, exfiltrated by Amadey and sent to C2 amadey malware
Distribution of Amadey

Amadey primarily relies on spear-phishing emails containing malicious attachments, such as Microsoft Office documents, to target specific organizations or individuals. The email content is carefully crafted to appear legitimate, enticing the victim to open the attachment.

Alternatively, Amadey can employ exploit kits (Fallout and Rig), drive-by downloads, or be dropped as a payload by other malware (in recent cases it was distributed by SmokeLoader).

Amadey malware conclusion

Amadey malware presents a notable challenge for cybersecurity researchers. Its persistence and evasion techniques, coupled with a highly customizable modular architecture, make it a high-level threat. Understanding its various infection vectors, exploitation methods, and malicious activities is essential to develop effective countermeasures and improve our overall cybersecurity posture.

You can efficiently detect and examine threats such as Amadey, with the help of ANY.RUN interactive sandbox, which provides analysis results in minutes.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Stealer screenshot
Stealer
stealer
Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns.
Read More
BlackMoon screenshot
BlackMoon
blackmoon
BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.
Read More
Kamasers screenshot
Kamasers
kamasers
Kamasers is a multi-functional DDoS botnet malware that transforms infected machines into remotely controlled attack nodes. It combines network-layer flooding capabilities, resilient command-and-control (C2), and payload delivery, making it not just a disruption tool but a gateway to broader compromise.
Read More
PureCrypter screenshot
PureCrypter
purecrypter
First identified in March 2021, PureCrypter is a .NET-based loader that employs obfuscation techniques, such as SmartAssembly, to evade detection. It has been used to distribute malware families including AgentTesla, RedLine Stealer, and SnakeKeylogger. The malware is typically delivered through phishing campaigns and malicious downloads, often masquerading as legitimate files with extensions like .mp4 or .pdf. PureCrypter utilizes encryption and compression to conceal its payloads and can inject malicious code into legitimate processes to maintain persistence on the infected system.
Read More
Trojan screenshot
Trojan
trojan trojan horse
Trojans are a group of malicious programs distinguished by their ability to masquerade as benign software. Depending on their type, trojans possess a variety of capabilities, ranging from maintaining full remote control over the victim’s machine to stealing data and files, as well as dropping other malware. At the same time, the main functionality of each trojan family can differ significantly depending on its type. The most common trojan infection chain starts with a phishing email.
Read More
Qilin Ransomware screenshot
Qilin ransomware (predecessor known as “Agenda”) is a rapidly evolving ransomware-as-a-service (RaaS) operation targeting organizations worldwide. Known for double extortion tactics (encrypting files while also threatening to leak stolen data) Qilin has quickly gained notoriety for its customization, flexibility, and impact on critical infrastructure.
Read More