Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
99
Global rank
114 infographic chevron month
Month rank
142 infographic chevron week
Week rank

Arkei is a stealer type malware capable of collecting passwords, autosaved forms, cryptocurrency wallet credentials, and files.

Stealer
Type
ex-USSR
Origin
21 May, 2018
First seen
29 September, 2026
Last seen
Also known as
ArkeiStealer

How to analyze Arkei with ANY.RUN

Type
ex-USSR
Origin
21 May, 2018
First seen
29 September, 2026
Last seen

IOCs

IP addresses
48.192.1.65
2.16.241.227
48.209.138.189
95.100.102.101
23.48.23.146
172.211.123.248
57.153.246.3
48.209.133.15
128.24.231.65
23.219.160.19
135.233.45.222
48.209.138.168
128.24.231.64
172.211.123.250
2.23.246.9
48.209.6.48
2.16.204.156
184.86.251.7
2.16.241.219
135.234.160.246
Hashes
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
e908466af6563b62d8f8c4bc870beb33b8fdb8682bf7c775a40ea1c6a8f49bf5
d5cf930756370de6c8bc9e98003056761655b80e4ad0337602ad0d33740a6d8f
772c8625cde6caf1573e9e61f43a9cdcda1e9d957c67f190a9685ddc036df1f7
0e24672ae24a06f2c30bfeaa1c72bdd0916285097115fb105ef00b7c926375a7
54a5ec6205c8e24ca57013f57ffc10f374ddfc91b2187eff643be92f5e7fd602
6f20d866841c4514782a46142df22b70b8da9783c513e3d41d8f3313483fe38d
a3acc39d4b61f9cc1056c19176d1559f0dacbb0587a700afdbe4d881040ccd52
d8dfd5dc5157e30aa9e241e4a7d13513dedf608045b6736716ea6c5ca4047855
516cde928be7cf45bedd28cb9bed291035aa9106a21335a922ca1e0987a8fdb6
3081af04bbaf03a33b15a177af37f0e46ffdc09469bdd3200795f52626a6d693
cde4f13166c5a8ca794977b62911e567cdf7bb6b420c934f0c5b284df81c25c2
da8c749e3f0119f91875ddaa116f265d440150c8f647dd3f634a0eb0b474e2c9
e86dcc7ad5556b7202d34b1cbac72e3bb0b97b19fc43919ac7321da94a8f3973
c4838a24ad388f934b04dbf9dba02a8bc6e9e58d0a1076477b47b5987a5c2d64
6ebe8f7e33db530652a0b1c6394ec4f50a2fcc0b4a31d1ab33db65d6815dd087
24c2811e92c20a88522cd9872020bdce2f882d6718962eac26f5fb4c97e14ded
34f6a1822d880608e7124d2ea0e3da4cd9b3a3b3b7d18171b61031cedbe6e72f
0532248fc289611fe2255aa94cbed9de496f9fcd144eee6fcedd2a1eb25ee554
Domains
www.bing.com
google.com
client.wns.windows.com
settings-win.data.microsoft.com
crl.microsoft.com
www.microsoft.com
activation-v2.sls.microsoft.com
self.events.data.microsoft.com
watson.events.data.microsoft.com
ecs.office.com
go.microsoft.com
login.live.com
slscr.update.microsoft.com
fe3cr.delivery.mp.microsoft.com
ocsp.digicert.com
nexusrules.officeapps.live.com
oneocsp.microsoft.com
validation-v2.sls.microsoft.com
startolete-vn.ug
1.pool.ntp.org
URLs
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://watson.events.data.microsoft.com/telemetry.request
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Arkei malware

Arkei is a stealer designed to exfiltrate information from infected systems. Typical for this malware type, it is distributed using Malware-as-a-Service (MaaL) model, which means that anyone can use the malware with minimal technical knowledge — all you need is to purchase access to a control pane from a website that sells the service.

This malware — which is written in C++ — targets Windows systems and is considered a medium impact and medium risk threat.

Having been around since 2018, Arkei has become popular among adversaries: not only is it widely used, but it has spawned several forks including Mars, Oski, and Vidar stealer, which we have covered before in the ANY.RUN trends trackers.

Arkei is capable of retrieving a variety of information from infected machines, including:

  • Form autosaves stored in the browser
  • Login and passwords
  • Files
  • Cryptocurrency wallets

Cryptocurrency owners are at the highest risk and are the main targets of Arkei. It can extract data from around 40 crypto wallet extensions, including MetaMask that accounts for over 80% of web3 wallet usage.

The stealer also targets more than 30 web browsers, including Chrome, Firefox, Microsoft Edge, Opera, Brave, and TOR.

Arkei can also target 2FA extensions, a capability it has had roughly since the beginning of 2022. It's unclear how attackers are planning to use this data, but it's certain that this development could pose new risks for both corporate and private users.

The specific data types that the malware targets depend on its configuration file — a ​​Base64-encoded file with the .PHP extensions — and will vary from campaign to campaign. The attacker can use it to set Arkei's behavior with custom rules, and target specific information.

It is important to note that Arkei terminates execution on machines from the ex-USSR regions.

The stealer identifies the region by accessing the language identifier of the Region Format setting. This behavior is typical for malware originating from the ex-USSR territories, which gives an insight into Arkei’s origin.

Arkei is equipped with multiple evasion techniques that help it avoid detection. For example, it checks that the computer name is not set to ​ “”HAL9TH”” and the username to “”JohnDoe” — these are the default settings of the Windows Defender emulator. It also checks if several DLLs are loaded in a process against a list of antivirus and emulation software.

Once it's time to gather the data, Arkei compiles its findings into a .zip archive, gives it a random 12-character name, and sends it to its control server. In addition to the information specified by the config file, it captures a system screenshot and extracts system information.

How to get more information from Arkei malware

You can obtain Arkei’s malware configurations in the ANY.RUN's sample.
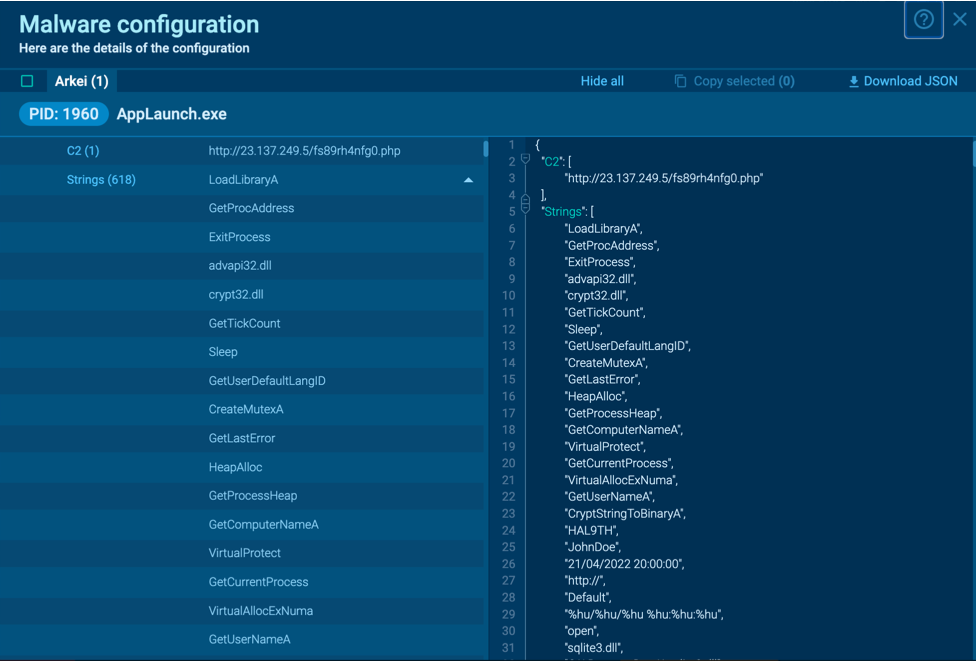
Malware configuration of Arkei stealer Figure 1: Arkei configuration automatically extracted by ANY.RUN

Users can access comprehensive malware configuration data on ANY.RUN interactive online sandbox in as little as 10 seconds after starting the sandbox. There's no need to wait for the emulation to finish running.

Arkei execution process

After a system is infected, a TCP connection is established with the hacker's remote server. The server sends encoded Base64 parameters to the malware, including search path templates and file search masks. Using these parameters, the malware determines which information it needs to steal from the victim's computer.

The malware then requests the libraries necessary for its operation from the remote server. These libraries are sent as ZIP archives.

Subsequent communication with the server involves sending stolen files to the C2 server. Some threat actors use packing techniques on Arkei samples (T1027.002) to avoid detection by signatures. An example of this behavior can be seen in this task we recorded in ANY.RUN.

After launching the packed sample, the AppLaunch.exe process is created in the system, which is part of the .NET Framework. The malicious code is then injected into this process.

Distribution of Arkei

Arkei finds its victims in a number of ways. It’s delivered with malicious email campaigns in infected attachments, distributed through malicious ads, and is sometimes found in cracked software.

Adversaries use trojan horse tactics to entice potential victims into installing Arkei to their systems: social engineering techniques can be utilized, such as offering a free version of a premium software.

Arkei has also been tied to campaigns utilizing SmokeLoader — an advanced modular malware used to gain an initial foothold in the system and drop other executables. Although Smoke Loader, as you probably have guessed from its name, is primarily used as a loader, it can be armed with information stealing functionality itself — double the threat, when used together with Arkei.

Conclusion

Arkei is a that poses a significant risk to users' sensitive data, particularly crypto wallets.

But users can keep their login and password information, files, and 2FA data secure by following these best practices:

  • Avoiding clicking on suspicious links
  • Being vigilant with emails from unknown senders
  • Staying clear from lurid ads
  • Being mindful where they download software from

You can identify and analyze threats like Arkei — and more — in a matter of minutes using ANY.RUN’s interactive sandbox. Sign up for a demo!
HAVE A LOOK AT

Latrodectus screenshot
Latrodectus
latrodectus
Latrodectus is a malicious loader that is used by threat actors to gain a foothold on compromised devices and deploy additional malware. It has been associated with the IcedID trojan and has been used by APT groups in targeted attacks. The malware can gather system information, launch executables, and detect sandbox environments. It uses encryption and obfuscation to evade detection and can establish persistence on the infected device.
Read More
Octo screenshot
Octo
octo coper
Octo malware, also known as ExobotCompact or Coper, is a sophisticated Android banking trojan that has evolved from earlier malware family Exobot. It poses a significant threat to financial institutions, mobile users, and enterprise networks.
Read More
Loader screenshot
Loader
loader downloader
A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection.
Read More
WhiteSnake screenshot
WhiteSnake
whitesnake
WhiteSnake is a stealer with advanced remote access capabilities. The attackers using this malicious software can control infected computers and carry out different malicious activities, including stealing sensitive files and data, recording audio, and logging keystrokes. WhiteSnake is sold on underground forums and often spreads through phishing emails.
Read More
UpCrypter screenshot
UpCrypter
upcrypter
UpCrypter is a sophisticated malware loader that functions as a delivery mechanism for remote access tools. Distributed through global phishing campaigns targeting Windows systems, this actively maintained tool serves as the central framework for deploying various RATs including PureHVNC, DCRat, and Babylon RAT, enabling attackers to establish persistent remote control over compromised systems.
Read More
GuLoader screenshot
GuLoader
guloader
GuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
Read More