Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
11
Global rank
20 infographic chevron month
Month rank
26 infographic chevron week
Week rank

Vidar is a dangerous malware that steals information and cryptocurrency from infected users. It derives its name from the ancient Scandinavian god of Vengeance. This stealer has been terrorizing the internet since 2018.

Trojan
Type
ex-USSR
Origin
1 December, 2018
First seen
9 October, 2026
Last seen

How to analyze Vidar with ANY.RUN

Type
ex-USSR
Origin
1 December, 2018
First seen
9 October, 2026
Last seen

IOCs

IP addresses
74.179.77.204
40.126.31.129
48.209.138.189
135.232.92.97
149.154.167.99
48.192.1.65
92.123.104.31
172.211.123.249
23.52.181.212
150.171.109.99
23.11.41.157
131.253.33.203
104.21.93.196
204.79.197.203
172.67.214.50
74.178.240.61
2.20.143.40
74.178.240.51
2.20.142.182
150.171.109.100
Hashes
496aca80e4d8f29fb8e8cd816c3afb48d3f103970b3a2ee1600c08ca67326dee
b71aa52080a403228f1972add0244c1054fbed8ee51691b79de9d382e8042391
6812868550892220e7c035cc61116a6543416102e0259ead49ff0a40f64eb962
a05abacc771f9fc05e4a6f3f978e62507b1b469c96ba3d3e6dbdeba4335100cd
97fe967ec8ceed48a3ffdb5e3cd529026cb89f76b8c0ad76a4e8b46e1a1f77e9
cb369fd0504e616ba4f05bcc143d12132261c7e829bff13b32d354794bb67503
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
f508309fca7182e2c3018369b41c1cc7655eb3fbbb3eeb89ab8bb046860ae7d3
67f5eabad8d277c331d34b4f92c4022e61c4d995101cfff06cb7862a4ea8bbc0
801645d9dbaa3b3f6aa3a74b668aebc55194c1cd0932c71ae37d5d97ee6e8403
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
0d321a100be42a3ad510587083b1a492eb43e01a6e21a9975d3aa8861f854050
3800a41b441e60803ac9ee6f700555619888b0b7a882ef557325f2b6b7843b2d
5b0812b3fc5278f1e23e14454866facc6dad6ff21e8661f4a83400b2e0bb4279
7137c55b5f15fa20a99691d5a3f793da1f19569a20258494ae2156b92bb0b8a7
6dbbeaa56054fb7a585d70dfd5448c3277626916de9c4c4f0f95898e1d10689f
faa4a1f8aa2a3ca703f5d023fd8dbe07947253a02716f188b46cd74bc89067ef
0d2a947c41c4c2e11d39fe7c64dedd1bbb248fe0fce4be695c6d38ba4b7c5880
0c958a87c1017bd115121433a44f9a183684dc1bb06e7425670d0e48e6735260
60bd7c62fa684703fe8448ea100e02cc408d5200baeb68832a6cd40b01bca56d
Domains
www.bing.com
t.me
ecs.office.com
google.com
slscr.update.microsoft.com
ocsp.digicert.com
ik.333vip.org
settings-win.data.microsoft.com
self.events.data.microsoft.com
activation-v2.sls.microsoft.com
fe3cr.delivery.mp.microsoft.com
login.live.com
nexusrules.officeapps.live.com
www.microsoft.com
client.wns.windows.com
crl.microsoft.com
oneocsp.microsoft.com
visam.info
drive.usercontent.google.com
rdrcfgwugqswg.org
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
https://t.me/bj00tyr
https://ik.333vip.org/
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f8%2f2026%2c%209%3a03%3a44%20pm
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.dd482747-0b27-423b-a458-0ac58ffc4b0e&pid=dsb
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://172.236.214.203/
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 2474
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 4783
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 7302
comments 0

What is Vidar malware?

Vidar is an information stealer trojan that was first identified in December 2018. It is either a fork of Arkei or the result of its evolution. Named after the god of vengeance from Scandinavian mythology, Vidar is used to steal information from infected systems, take screenshots, steal cryptocurrency, and more.

General description of Vidar malware

Vidar is presumed to have originated in a Russian-speaking country since the malware is configured to stop execution if it detects that it is being run on a machine that is located in one of the ex-USSR nations or on one that has a Russian keyboard layout.

Being another cyber threat that is available for purchase based on the MaaS (Malware-as-a-Service) business model, Vidar can be purchased on its “official” website for a hefty price tag of $700, at least for the PRO version. Though, a stripped-down version of the malware can be obtained for just $250.

According to the Vidar trojan analysis, malware is written in the C++ programming language. Purchasing account grants the attacker access to a control panel where the cybercriminal can set up the infostealer malware to target particular information on the victims’ PC. Like Arkei, cybercriminals need to take precautions to secure the main payload themselves, using crypto or a packer. The control panel displays the current builder version, user settings, malware status, and logs. It should be noted that Vidar data stealer uses domain names to search for C&C servers, where stolen data is being dropped, changing every four days. Though they are steadily changing, a constant response is required.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Vidar is capable of stealing text files in multiple formats, browser cookies and history, browser records, including data from TOR, as well as autofill value information, including banking and credit card details. Based on the Vidar analysis, the stealer malware can search for cryptocurrency wallet information, take screenshots and act as a message stealer, recording private messages from various software.

What’s more, Vidar is also known to be able to steal digital coins from offline wallets. In fact, holders of Litecoin, Bitcoin, Ethereum, Zcash, and DashCore are in potential danger, as these are the cryptocurrencies currently supported by this infostealer malware.

After collecting all targeted information, this stealer malware archives it and sends the stolen data to a control server, after which Vidar removes traces of its work and deletes itself from the system.

Vidar analysis

An analysis recorded in ANY.RUN malware hunting service allows us to take a closer look at the lifecycle of Vidar and perform Vidar analysis.
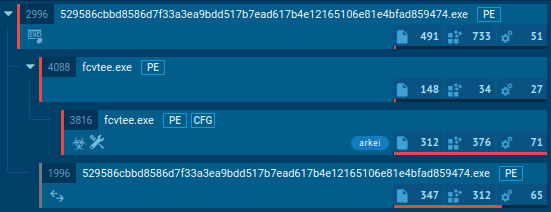
arkei execution process tree

Figure 1: A visual process graph generated by ANY.RUN
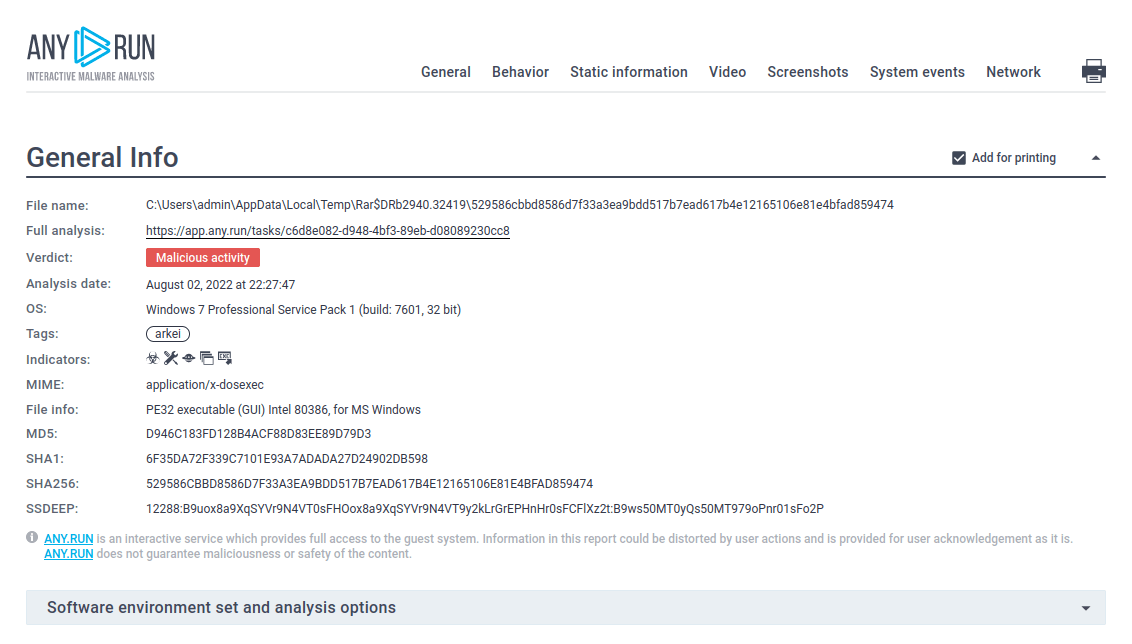
text report of the arkei malware analysis

Figure 2: The customizable text report provided by ANY.RUN is a perfect tool to share the results of an analysis

Vidar execution process

According to the Vidar analysis, after the user downloads and runs a malicious file, it spawns a child process and collects information from the infected system. Often, after the information was collected, the malware kills and deletes itself from the system through a command-line command.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

How to avoid infection by Vidar malware?

When spread via spam email campaigns like NanoCore or Agent Tesla, the Vidar stealer requires the user to download and run a malicious file to enter an active state and begin execution. Therefore, following some basic cybersecurity rules can ensure that users will stay safe from Vidar malware and the incident response team will work effectively.

As such, users should be careful when downloading attachments in emails from unknown senders. The best practice is to avoid downloading such files altogether, therefore not putting oneself in danger at all.

In addition, downloading only licensed software from trustworthy sources and avoiding gaming hacking clients greatly reduced the risk of being infected with malware such as Vidar trojan, which uses these attack vectors to infect victims.

The distribution process of Vidar

According to the Vidar trojan analysis, Vidar is distributed through spam email campaigns as a malicious attachment, like other malware. In addition, cases of Vidar being distributed using shady software and gaming hack clients have also been recorded. Vidar infostealer targets users all over the world, except some ex-USSR countries, including Russia.

How to detect Vidar using ANY.RUN?

Some malware creates files in which it named itself. You can find such info about Vidar trojan using ANY.RUN's Static Discovering during your Vidar analysis. Open either the "Files" tab in the lower part of the task's window or click on the process and then on the "More Info" button in the appeared window. After that, all you need to do is click on the file.
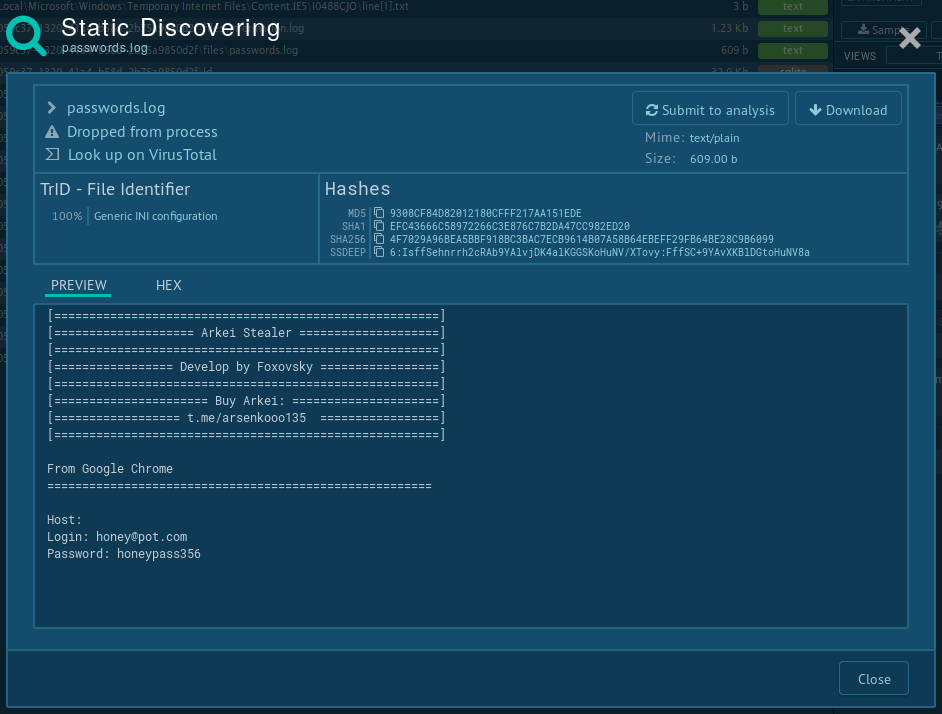
arkei vidar log file Figure 3: Vidar's log file

Conclusion

Vidar is a hazardous information stealer trojan, distributed as malware as a service. Thanks to its extensive stealer feature set, Vidar trojan can be used to retrieve a wide variety of information, including stealing select cryptocurrency coins from the users. Additionally, Vidar is capable of stealing data from TOR.

Thankfully, malware hunting services like ANY.RUN allows researchers to conduct extensive studies of malware samples in a secure environment, allowing them to spread information about the danger and develop effective countermeasures and incident response.

Create your free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

Kratos screenshot
Kratos
kratos
Kratos is a mature Phishing-as-a-Service (PhaaS) platform that evolved from the Sneaky2FA kit to specialize in stealing Microsoft 365 credentials through sophisticated Adversary-in-the-Middle (AiTM) techniques. The service provides low-skilled affiliates with a turnkey solution featuring an advanced administrative dashboard, integrated anti-bot defenses, and real-time data exfiltration via the Telegram Bot API. Although an international law enforcement action known as Operation Olympus Blade disrupted its central infrastructure in July 2026, the kit remains a primary example of the industrialization of modern cybercrime.
Read More
Caminho Loader screenshot
Caminho Loader
caminho caminholoader
Caminho Loader is a Brazilian-origin Loader-as-a-Service operation that uses steganography to conceal .NET payloads within image files hosted on legitimate platforms. Active since March 2025, it has delivered a variety of malware and infostealers to victims within multiple industries across South America, Africa, and Eastern Europe.
Read More
Greatness screenshot
Greatness is a Phishing-as-a-Service (PhaaS) platform that enables cybercriminals, even those with limited technical skills, to launch sophisticated phishing attacks primarily targeting Microsoft 365 (M365) credentials. It acts as a man-in-the-middle (MitM) proxy, facilitating credential theft and MFA bypass while providing affiliates with easy-to-use tools like attachment builders and Telegram notifications.
Read More
Roning Loader screenshot
Roning Loader
roning
RoningLoader is a multi-stage Windows loader designed to operate quietly while preparing systems for deeper compromise. It abuses trusted system tools and interferes with security controls to reduce the chances of early detection. Instead of acting as a final payload, it creates conditions for follow-on malware to execute more effectively. Its use of staged execution and code injection allows attackers to blend into legitimate activity and escalate impact. This makes early behavioral detection critical before the attack chain progresses further.
Read More
DarkGate screenshot
DarkGate
darkgate
DarkGate is a loader, which possesses extensive functionality, ranging from keylogging to crypto mining. Written in Delphi, this malware is known for the use of AutoIT scripts in its infection process. Thanks to this malicious software’s versatile architecture, it is widely used by established threat actors.
Read More
JOMANGY screenshot
JOMANGY is a PHP webshell and backdoor family targeting vulnerable FreePBX servers. It is designed to establish long-term access to compromised VoIP infrastructure, enable toll fraud, and survive remediation attempts through multiple self-reinforcing persistence mechanisms. Unlike many traditional webshells, JOMANGY employs a highly resilient architecture that can automatically restore itself even after partial removal.
Read More