Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
14
Global rank
14 infographic chevron month
Month rank
21 infographic chevron week
Week rank

Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold.

Trojan
Type
Likely Turkey
Origin
1 January, 2014
First seen
8 October, 2026
Last seen

How to analyze Agent Tesla with ANY.RUN

Type
Likely Turkey
Origin
1 January, 2014
First seen
8 October, 2026
Last seen

IOCs

IP addresses
40.126.31.3
48.209.133.15
172.217.117.4
192.178.183.91
142.251.127.84
82.221.136.52
142.251.127.138
74.178.240.51
23.11.41.157
34.104.35.123
23.59.18.102
23.207.210.132
135.232.92.137
142.251.156.119
48.192.1.64
142.251.110.100
208.95.112.1
23.216.77.26
2.20.142.139
142.251.20.101
Hashes
bb9f8df61474d25e71fa00722318cd387396ca1736605e1248821cc0de3d3af8
eaea1c7eeb2af4fcb59c7db541df61057c4ccdb8a4d4f70af75776d70aa1850c
7852fce59c67ddf1d6b8b997eaa1adfac004a9f3a91c37295de9223674011fba
b1e963d702392fb7224786e7d56d43973e9b9efd1b89c17814d7c558ffc0cdec
f3f05881c3398017cfb6d4a164335d3718827eea20e3523363bd185d0350e2d8
d2c5dd1d14eb67ca3f368137abb4f564d0a93afbb233d3d6a45d0023fdeedbc8
997b8c23966676b1b2e7884a692b57f0e6a7fe79aa4608d96fd3473dd85eb744
7b303900bfe7f667dea9072d086af5b94d9b34f6bceeac4087684440c1cfaeac
968867efa47aef0a8525f2fd7ee913721523da07db8b8cc398cd79ca5d937d85
006396ccfb508bd2a9bc2a586542991b0f8a87bd7ba97d561cc30928eccd776d
2c108f1c817b0bbc74957efb26edcde62381dc44ef0a12b1979afc4aafe0fafa
466c9819692ed91c8ab383b4ed4e853d03c4db2dbf663612eaf6abaae0640812
8b9d2b7401b08005431d7a2134d71245760aa299f8095248c6bf5917f46dfde8
1cb0c988f02a80625c2801ac311f251b6efa69d1b713bd36be00970df966f422
3178c9c33a890dd150368897706eb98bce65192c2f2c01f2bbc08d03d98eb863
e536ee8a7e7aa4e95cb8677a189d5a9cd810257612300237d3d48a425342d109
ed19efe359b80ce5e81c007aaa46de3b062864b2f8ef1408ca7fe38ff8d3a419
a4dcb1c7eda6c08e769a7e2638b1614eff417c1311dde34499f21cea2ca0e62e
627111172517a58b7e9a89f6ec1edee904b7a96c7f0c5941e4fa8ba77b85a5bd
0f238237055274c95c143f322d865406fa5bb648f3d733bd623aad162adcb539
Domains
tauranfarms.cc
activation-v2.sls.microsoft.com
ecs.office.com
client.wns.windows.com
update.googleapis.com
edgedl.me.gvt1.com
ip-api.com
optimizationguide-pa.googleapis.com
slscr.update.microsoft.com
th.bing.com
dl.google.com
clients2.google.com
www.google.com
www.bing.com
nexusrules.officeapps.live.com
login.live.com
sb-ssl.google.com
self.events.data.microsoft.com
safebrowsingohttpgateway.googleapis.com
clientservices.googleapis.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://clients2.google.com/time/1/current?cup2key=8:kdzcfkiomrsdziqsvwabewxzmpuuwqw0xsmx3xkrnfy&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://safebrowsingohttpgateway.googleapis.com/v1/ohttp/hpkekeyconfig?key=aizasya2klwbx3mkfo30om9lufyqhpqloa_bnhe
https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=133
https://accounts.google.com/listaccounts?gpsia=1&source=chromiumbrowser&json=standard
https://tauranfarms.cc/download.php?id=ca0vmaqmuyw4u27
https://update.googleapis.com/service/update2/json?cup2key=14:sclwghh_uvyvuctfmpgmzym0g6lc2pjreezgxfzevju&cup2hreq=45ef3131f5a49530a0928ca18f535f75b3983a390f48f88028a0d27cdc1fa0cd
https://sb-ssl.google.com/safebrowsing/clientreport/download?key=aizasya2klwbx3mkfo30om9lufyqhpqloa_bnhe
https://optimizationguide-pa.googleapis.com/v1:getmodels?key=aizasya2klwbx3mkfo30om9lufyqhpqloa_bnhe
https://optimizationguide-pa.googleapis.com/downloads?name=1679317318&target=optimization_target_language_detection
https://optimizationguide-pa.googleapis.com/downloads?name=1753110098&target=optimization_target_notification_permission_predictions
https://optimizationguide-pa.googleapis.com/downloads?name=1753110074&target=optimization_target_geolocation_permission_predictions
https://optimizationguide-pa.googleapis.com/downloads?name=1728324084&target=optimization_target_omnibox_on_device_tail_suggest
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://optimizationguide-pa.googleapis.com/downloads?name=240731042075&target=optimization_target_segmentation_compose_promotion
https://optimizationguide-pa.googleapis.com/downloads?name=5&target=optimization_target_page_topics_v2
https://optimizationguide-pa.googleapis.com/downloads?name=1788275283&target=optimization_target_client_side_phishing
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2367
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 3913
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11489
comments 0

What is Agent Tesla malware?

Agent Tesla is a password stealer spyware that has been around since 2014. The malware can be used by attackers to spy on victims, allowing them to see everything that has been typed in supported programs and web-browsers.

Being marketed and sold on its own website, which falsely claims that the program is a legitimate keylogger created for personal use, the Agent Tesla virus has become extremely popular in the hacker community. Not lastly due to its ease of use and tech support, available on the “official” website where this malware is being sold by the attackers, as well as on the dedicated Discord server. Despite claiming the legitimacy of the software, support staff gives advice on utilizing the virus illegally. It is thought that Agent Tesla spyware has originated in Turkey.

General description of Agent Tesla

The spyware is created using .Net software framework. It is aimed at stealing personal data and transmitting it back to the C2 server. The malware is able to access information from web browsers, email clients, and FTP servers.

In addition, Agent Tesla malware can capture screenshots and videos. It can also record clipboard information and form values. The virus was being distributed on agenttesla-dot-com where attackers could purchase it for as little as $15. However, depending on the requested options the package price could easily reach roughly $70.

Uniquely, creators of the malware have set up a sort of an ecosystem around the program, providing 24/7 customer support as well as pre-matched purchase plans that include various options tailored for different budgets and goals. The virus is supplied with a dedicated builder that has a simple-to-use control panel. It allows even a non-technically savvy attacker to pack the payload into a malicious document. What’s more, after 2015 the control panel of Agent Tesla has been expanded with extensive automation functionality, allowing the attacker to automatically capture snapshots or remotely activate the webcam on a victim’s PC in set intervals.

Based on the analysis, the malware comes equipped with multiple persistence mechanisms that help it avoid antivirus detection. As such, it can resume operation automatically after a system reboot. It is also able to turn off Windows processes to stay hidden.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Malware analysis of Agent Tesla

The interactivity of ANY.RUN service allows tracking activities in real-time and watching Agent Tesla in action in a controlled, safe environment with full real-time access to the sandbox simulation. A video recorded by the ANY.RUN gives us the ability to take a closer look at the lifecycle of this virus. You can also analyze fresh samples and IOCs in our threat intelligence feed in the public submissions.
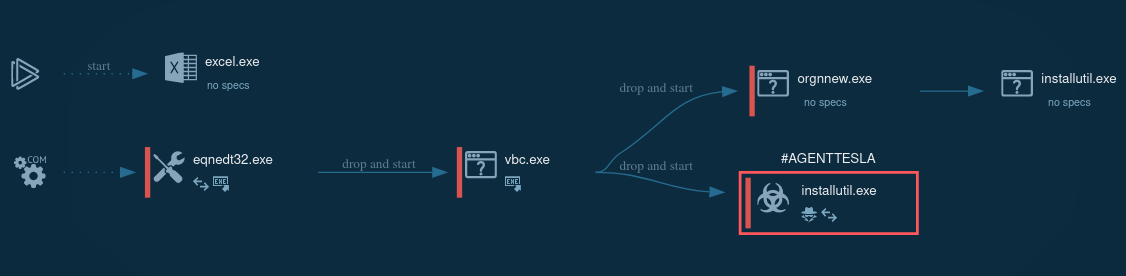
agent tesla execution process graph Figure 1: A lifecycle graph generated by ANY.RUN

How to avoid infection by Agent Tesla?

Agent Tesla malware is not an easy one to identify. The most robust way to stay safe is to exhibit caution when opening suspicious emails or visiting unknown links. Above all, one must be careful to download attachments in emails from unknown senders and try to identify scams.

Distribution of Agent Tesla

The malware is distributed at large via spam email campaigns like Vidar or IcedID. It is usually delivered to victims in malicious documents, or via malicious web links. Upon visiting such a link, a contaminated document will be automatically downloaded to a victim’s PC.

If opened, the document will trigger the download of the actual virus. The spyware saves itself in the “%temp%” folder and then automatically executes. Email campaigns usually target individuals working in different industries. Topics of malicious emails can be extremely diverse.

Agent Tesla execution process

Agent Tesla keylogger is mostly spread via Microsoft Word documents that contain an embedded executed file or exploit. Once clicked, an executable file is downloaded and renamed. The downloaded file runs itself and creates a child process which in turn can create another child process.

The malware is able to use Regsvcs and Regasm to proxy the code execution through a trusted Windows utility. The research and threat intelligence team can pay attention that in the given example RegSvcs.exe process is stealing personal data.
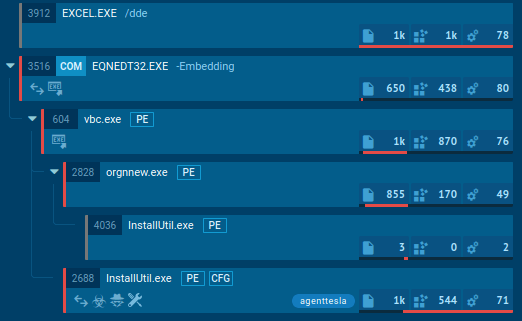
process tree of the agent tesla execution Figure 2: A process tree of the Agent Tesla execution

Since the main purpose of Agent Tesla RAT is stealing personal information you can identify it by behavioral activities. To do so, try the analysis of the indicators of a malicious process (most often it's an injected "RegAsm.exe"). If there is the indicator "Actions looks like stealing of personal data" in the "Process details" section you probably are dealing with the Agent Tesla trojan. Also, you can identify what information the malware has stolen by clicking on the indicator. You can navigate through by clicking right and left arrows in the appeared window.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

How to get more Agent Tesla data using ANY.RUN?

Often Agenttesla packets encryption is unsuccessful and with ANY.RUN service's "Network Stream" analysts can take a look at what data this malware stole. To do it open the "Connections" tab in the lower part of the task's window and simply click on the connection which sent data. Not unusual that you can find inside this information even the attacker’s SMTP credential.
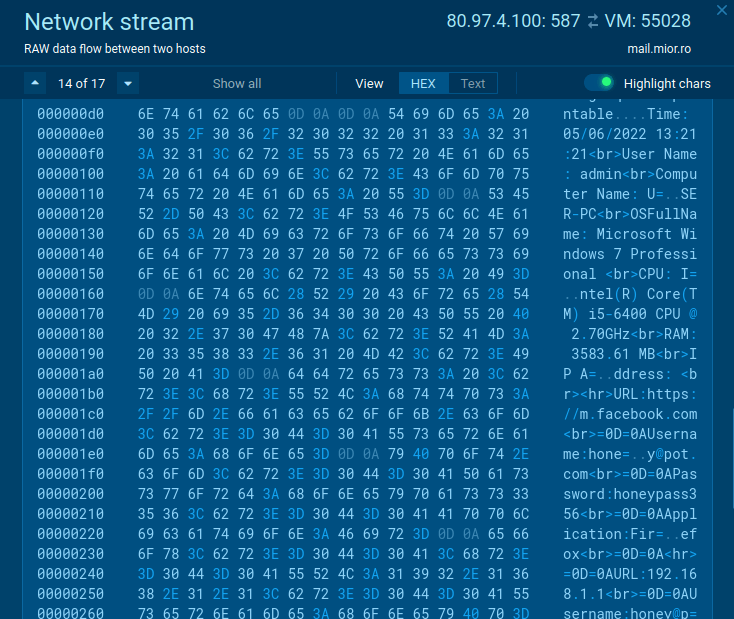
agent tesla's network stream without encryption Figure 2: Agent Tesla’s Network stream without encryption

Gathering threat intelligence on Agent Tesla malware

To collect up-to-date intelligence on Agent Tesla, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Agent Tesla.
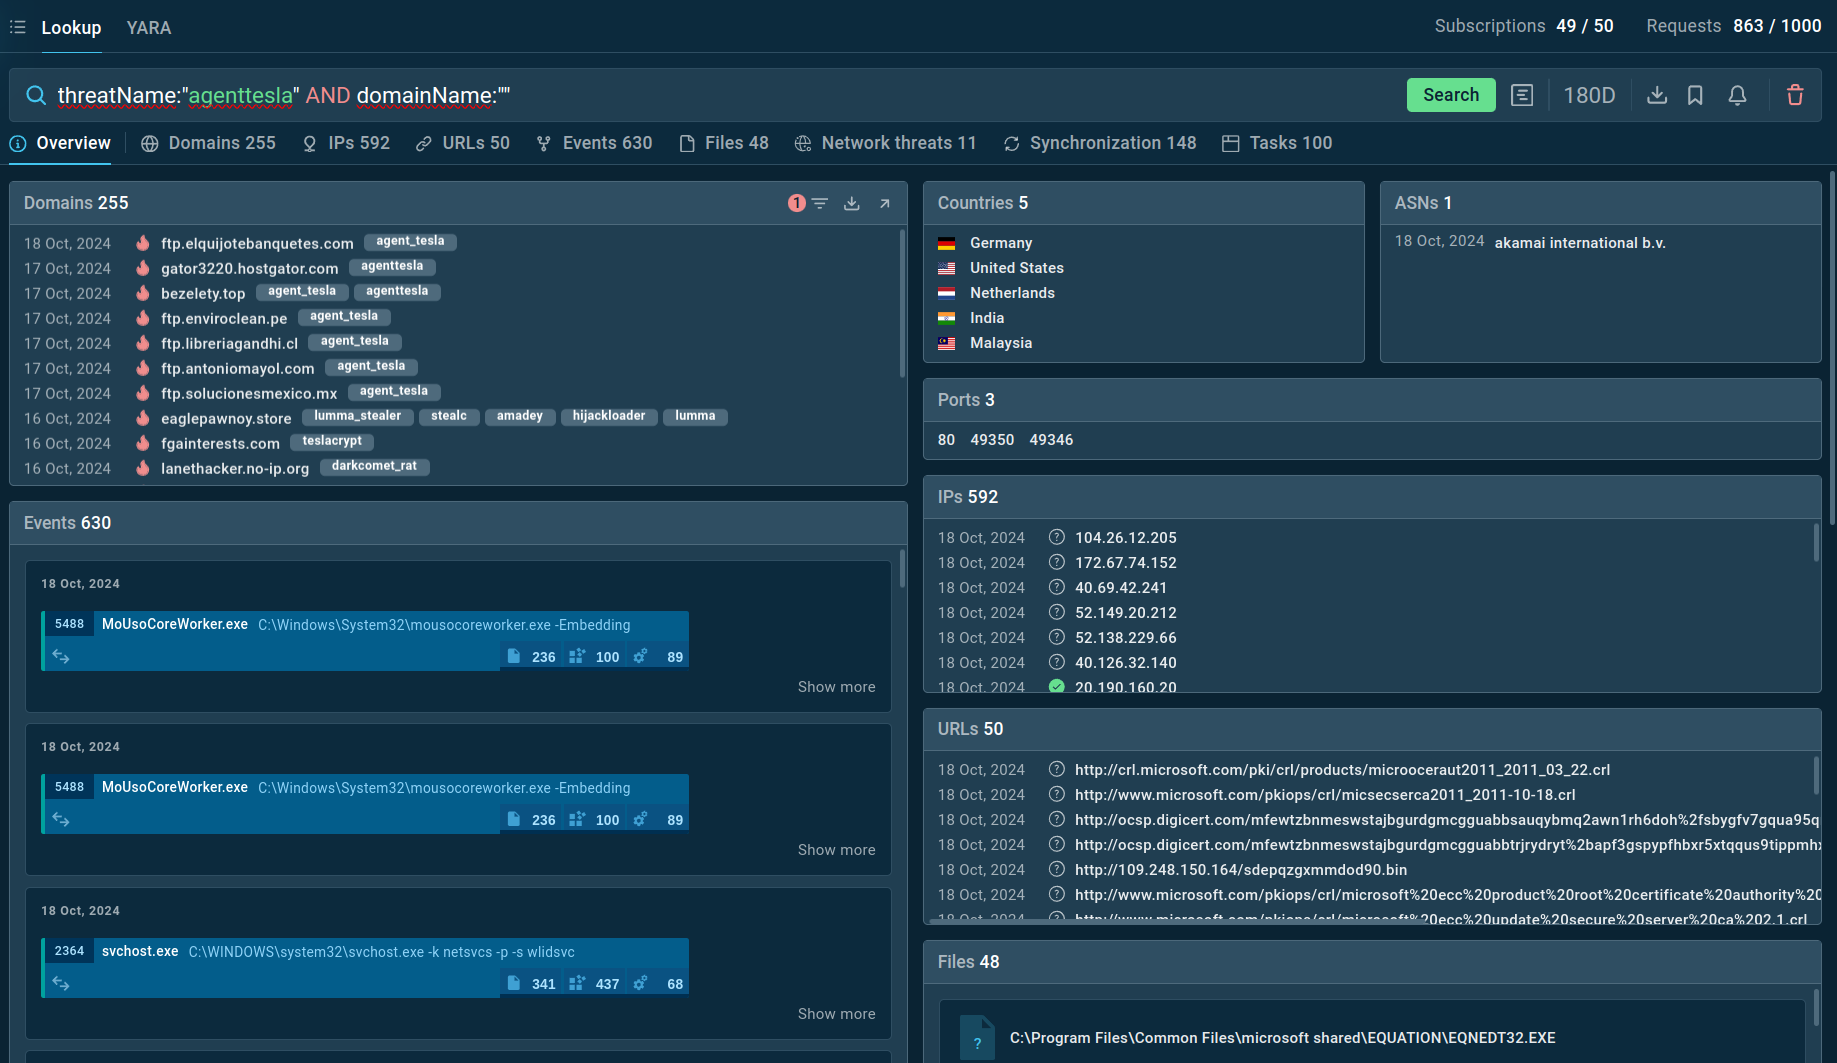
Agent Tesla ANY.RUN Search results for Agent Tesla in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"agenttesla" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from Agent Tesla samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

According to threat intelligence reports, since its creation, Agent Tesla trojan has been used by over 6,300 customers. Unfortunately, the popularity of the virus is only continuing to rise. The upward trend is of, course, supported by the ease of use which allows even novice attackers to set up attacks.

A company-like service provided by the virus creators also plays a significant role. The danger of Agent Tesla for incident response and threat intelligence teams lies not only in the fact that it can be used by almost anybody but also in its ability to open doors to more destructive viruses. Thankfully, interactive analysis services such as ANY.RUN allows professionals to examine the malware behavior in detail and set up appropriate security responses.

Create your free ANY.RUN account to analyze malware and phishing without limits!

HAVE A LOOK AT

CastleLoader screenshot
CastleLoader
castleloader
CastleLoader is a modern malware loader designed to quietly establish initial access and deliver follow-up payloads such as stealers, RATs, and ransomware. It focuses on stealth, flexibility, and rapid payload rotation, making it an effective tool for financially motivated threat actors and a persistent problem for enterprise defenders.
Read More
DarkCloud screenshot
DarkCloud
darkcloud
DarkCloud is an infostealer that focuses on collecting and exfiltrating browser data from the infected device. The malware is also capable of keylogging and crypto address swapping. DarkCloud is typically delivered to victims’ computers via phishing emails.
Read More
Caminho Loader screenshot
Caminho Loader
caminho caminholoader
Caminho Loader is a Brazilian-origin Loader-as-a-Service operation that uses steganography to conceal .NET payloads within image files hosted on legitimate platforms. Active since March 2025, it has delivered a variety of malware and infostealers to victims within multiple industries across South America, Africa, and Eastern Europe.
Read More
Rootkit screenshot
Rootkit
rootkit bootkit
A rootkit is a type of malicious software designed to provide unauthorized administrative-level access to a computer or network while concealing its presence. Rootkits are tools used by cybercriminals to hide their activities, including keyloggers, spyware, and other malware, often enabling long-term system exploitation.
Read More
DeerStealer screenshot
DeerStealer
deerstealer
DeerStealer is an information-stealing malware discovered in 2024 by ANY.RUN, primarily targeting sensitive data such as login credentials, browser history, and cryptocurrency wallet details. It is often distributed through phishing campaigns and fake Google ads that mimic legitimate platforms like Google Authenticator. Once installed, it exfiltrates the stolen data to a remote command and control (C2) server. DeerStealer’s ability to disguise itself as legitimate downloads makes it particularly dangerous for unsuspecting users.
Read More
Salvador Stealer screenshot
Salvador Stealer
salvador
Salvador Stealer is a powerful, information-stealing Android malware designed to silently infiltrate systems, extract sensitive data, and exfiltrate it to cybercriminals. Often sold on underground forums, it is part of the growing ecosystem of “stealers-as-a-service” (SaaS) tools that target individuals and organizations alike.
Read More