Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
73
Global rank
48 infographic chevron month
Month rank
50 infographic chevron week
Week rank

WarZone RAT is a remote access trojan, which is written in C++ and offered as a malware-as-a-service. It packs a wide range of capabilities, from stealing victims’ files and passwords to capturing desktop activities. WarZone RAT is primarily distributed via phishing emails and receives regular updates from its C2.

RAT
Type
Ex-USSR
Origin
4 December, 2018
First seen
15 September, 2026
Last seen
Also known as
AVE_MARIA
Ave Maria

How to analyze WarZone with ANY.RUN

RAT
Type
Ex-USSR
Origin
4 December, 2018
First seen
15 September, 2026
Last seen

IOCs

IP addresses
107.174.192.179
150.171.28.11
118.194.235.187
208.95.112.1
188.114.96.3
149.154.167.99
104.18.23.222
2.16.204.161
142.251.155.119
142.251.20.132
139.99.85.213
74.178.240.51
154.91.34.165
104.26.12.64
142.250.154.97
172.217.117.4
154.23.184.57
98.177.107.142
23.59.18.102
142.251.14.95
Hashes
74441313bb1fb62500484443c4937e90d4e335351a4fcd12a9ac48448500e33e
2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
4094d158e3b0581ba433a46d0dce62f99d8c0fd1b50bb4d0517ddc0a4a1fde24
99653a38c445ae1d4c373ee672339fd47fd098e0d0ada5f0be70e3b2bf711d38
c158322bd963d2a68ffc878d72213a7394d8c16de72279771ffc924365eec0df
59345c006cd9bde5ef532aae1f119758d45030993181c272bb0dd6fc0c5d01e5
2ae1142b08d296c25000e451237ea919f981da28f6a723d39540f43f18bac762
5639c845d56dedecd2cfdb082b734593b5d618a87f1bd8ec612a8b3f4245566a
32ae9531405ef3c59448fe6dbd3be435e726eb17f3ca0d16530a4c6317dea286
7c68f28c6995f47dd77596bab28c6b4388ff93840c3becfd37733ddb640cd0cd
40cf1af5650b699a947899d2b43a00dcb64cdeaf080651c82a7930910c1c03f4
ec249b0dab6fda20cc24f0f25a504c55a05b23fb6cbb4938aa7a41df0c8744b6
0162159b64eb092f94964faf937f263fb9947b25d40e0d82bd3224d136a140de
77eed9211cd8464482f0da3fac4c0f003c2b8a6d76f15445927e66400f102d60
6558013f984e594bb57534910ce0b17bfa15da3cc9bb4b6e0b5c6e4ddf9eb14e
a7109b8374dffa7a0cd69558990f7e96fea9ef61736d89043dad5a6694cdfa4a
758a0b404b3daadbd0d4e88a0bedf5c21d5507392f7b54d4906ffea49d58ab32
558bbe6193a202dcb00cc441421f5d838764e495b8e4d2e10877db7f661b8cd5
db3ac1fd3d65df45d805adb8dfe0c5209db07ef93406db17dfb783dd8048720a
19acfa0adce363a9c9a3be73f5ec0fac0dcf3c630ce18125fd265040ad6ffb6c
Domains
tpc.googlesyndication.com
api.edgeoffer.microsoft.com
fe3cr.delivery.mp.microsoft.com
settings-win.data.microsoft.com
static.admaster.cc
msedge.b.tlu.dl.delivery.mp.microsoft.com
identitytoolkit.googleapis.com
lh3.googleusercontent.com
must-directed.gl.at.ply.gg
api.telegram.org
edge.microsoft.com
googleads.g.doubleclick.net
activation-v2.sls.microsoft.com
bucket-cf-weur-a.uploadnow.io
nexusrules.officeapps.live.com
www.bing.com
api.pcloud.com
client.wns.windows.com
slscr.update.microsoft.com
edge-consumer-static.azureedge.net
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:wre-eutrtw_lzyylfryn5gipqsah5d90nzfi4jwh-im&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://uploadnow.io/f/0bcds7g
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://uploadnow.io/en/share?utm_source=0bcds7g
https://cdn.uploadnow.io/_next/static/css/df97d9751ec3abda.css
https://cdn.uploadnow.io/_next/static/css/cda03e3a1ab65c17.css
https://cdn.uploadnow.io/_next/static/css/ae110469aab9e883.css
https://cdn.uploadnow.io/_next/static/css/5ded0d5ca9ecc5c1.css
https://cdn.uploadnow.io/_next/static/chunks/webpack-541c27ed8494cc3b.js
https://cdn.uploadnow.io/_next/static/chunks/framework-b6335179e7eea00c.js
https://cdn.uploadnow.io/_next/static/chunks/main-86f0684c1b20f38d.js
https://cdn.uploadnow.io/_next/static/chunks/pages/_app-a7a0c0b843b84887.js
https://cdn.uploadnow.io/_next/static/chunks/62867-950590631f5ceb03.js
https://cdn.uploadnow.io/_next/static/chunks/38993-a4121c3c0d1b9d33.js
https://cdn.uploadnow.io/_next/static/chunks/41480-7aa8c357827879bd.js
https://cdn.uploadnow.io/_next/static/chunks/3816-6a0007c41b67cb89.js
Last Seen at
Last Seen at

Recent blog posts

post image
How MSSPs Can Prove Their Value When “Nothing...
watchers 1129
comments 0
post image
Enterprise Threat Intelligence Buying Guide:...
watchers 1423
comments 0
post image
ANY.RUN & SentinelOne: One Workspace, Ins...
watchers 3017
comments 0

What is WarZone RAT malware?

WarZoneRAT is a remote access trojan (RAT) that has been distributed via the malware-as-a-service (MaaS) model since 2018 on both Clearnet and Darknet.

The range of capabilities of the malware includes information stealing, infected systems manipulation, and initiation of targeted attacks against organizations. Easy accessibility, frequent updates, and the ever-expanding set of features make WarZone RAT one of the most prevalent RATs in the global threat landscape.

When it was first discovered, researchers believed that the malware is fairly simple and won't follow Ryuk ransomware's story. After the later analysis, it was revealed that this virus has advanced functions under its hood, such as privilege escalation and remote camera control. According to the analysis, Ave Maria Trojan is capable of stealing a wide range of data from infected machines. Even such well-protected information such as credentials stored in Mozilla Firefox is not safe despite the utilized PK11 encryption.

However, some parts of the malware appear to be unfinished. And it looks like the authors are still working on expanding its functionality even further. Considering how effective this RAT already is, this idea is nothing but worrying.

WarZoneRAT uses a DLL hijacking exploit that, at this point, doesn’t have a foreseeable fix. It allows the malware to escalate privileges of a Windows process and enable a malicious process to gain administrative control of an infected machine. Unfortunately, the malware is also capable of avoiding detection on many target machines.

Once the malware achieves this initial target, it downloads additional plugins and even other viruses like Lokibot to the machine.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Technical details of WarZoneRAT

WarZoneRAT operates by infiltrating a target's computer through a range of techniques, such as phishing emails. Once installed, it establishes an encrypted link with its command and control (C2) server, allowing the attacker to manage the compromised computer from a remote location.

The malware is equipped with a broad selection of features, some of which include:

  • Hidden remote access: Attackers can gain full control of the victim's machine to manipulate it and steal data, while staying completely invisible.
  • Password recovery: The malware is capable of extracting passwords from popular browsers and email clients.
  • File management: Malicious actors can interact with the infected computer’s file management system by uploading and downloading files, especially different kinds of payload, as well as executing them.
  • Offline keylogging: WarZoneRAT can record keystrokes, making it easy for hackers to discover sensitive information entered by the victim, including passwords and credit card numbers.
  • Screen capturing: The program can be configured to monitor desktop activity and take screenshots.
  • Updates: It can receive updates from its C2, thus evolving and utilizing new tools to circumvent security infrastructure.

One noteworthy aspect of WarZone RAT is its use of C++. While many RATs are built with .NET Framework (e.g., njRAT), which limits their operation to MS Windows, WarZoneRAT can function on any system with a C++ compiler.

The malware also implements obfuscation and evasion techniques to make detection a challenge. For instance, WarZone RAT can bypass User Account Control (UAC) to escalate privileges, installing itself on the victim's system. It also leverages process hollowing, which involves executing malicious binary as part of a legitimate process. Additionally, it makes use of anti-debugging mechanisms, complicating analysts’ investigations.
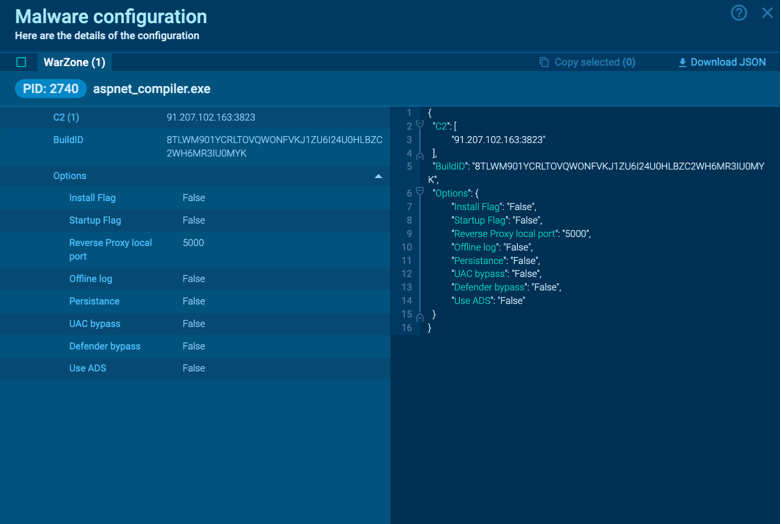
WarZoneRAT’s configuration WarZoneRAT’s configuration

WarZoneRAT execution process

By uploading a sample of WarZone RAT to the ANY.RUN sandbox, you can see the complete execution path of this malware, which may vary in different versions of WarZoneRAT.

Once the RAT makes its way into the system and begins execution, it uses cmd to collect information about the network configuration. To evade process-based defenses, it often employs process injection. In our case, Warzone utilizes the process hollowing technique (T1055.012) to inject its malicious code into the legitimate process aspnet_compiler.exe.

After WarZone RAT starts the hijacked process, it begins its malicious activity, such as stealing sensitive information and collecting credentials. In our sample, the malware does not receive a response from the Command & Control (C&C) server and is waiting for further instructions.
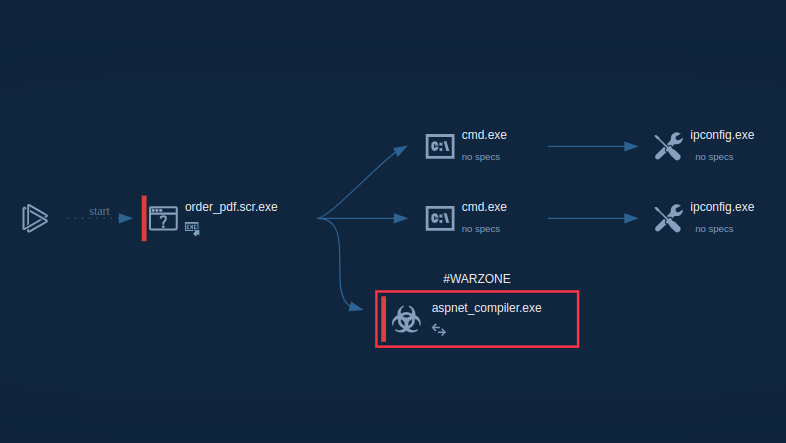
WarZoneRAT’s process graph WarZoneRAT’s process graph

Distribution methods of the WarZone RAT malware

Although there are plenty of ways WarZoneRAT can make it to a victim’s computer, the malware has been observed to utilize phishing emails as the primary method of distribution, which is also extensively employed by Vidar. Such emails contain malicious attachments that, when opened, install the malware on the victim's computer. For example, one of the occurrences of this malware was attributed to fake Hungarian government emails, which contained a WarZoneRAT executable in a .zip folder.

Additionally, the malware can be distributed as part of Microsoft 365 files, particularly .doc and .xml ones, injected with malicious code. When users open such files, the payload instantly gets downloaded, infecting their systems. The malware also can be accidentally downloaded by unsuspecting users visiting malicious websites. Similarly, some of the samples of this program were found on cloud storage platforms, disguising themselves as ordinary files.

How to detect WarZone RAT using ANY.RUN?

Unlike ransomware, WarZone RAT malware performs information stealing offline which causes it to save data locally on an infected system. To get the analysis of what information was stolen by Ave Maria RAT, take a look inside files that it creates using "Static Discovering." These files often have names in the dd-mm-yy_hh.mm.ss format. To open a file, click on a file’s name and start the analysis.
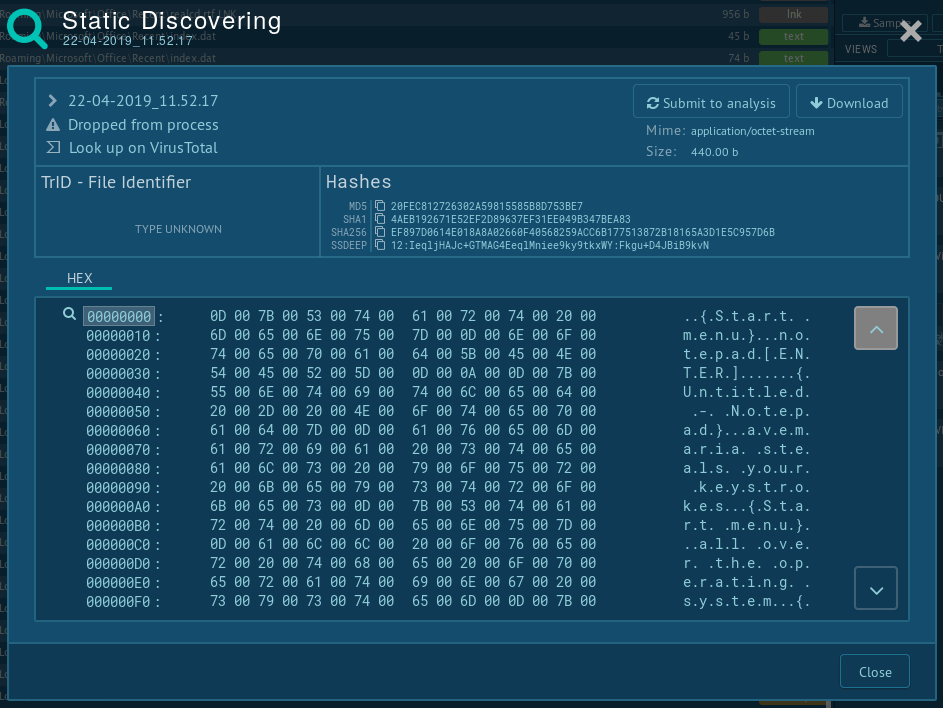
information stolen by ave maria Information is stolen by WarZone RAT

Conclusion

WarZoneRAT is a serious threat to organizations and individuals, and it is vital to be aware of the malware's capabilities and distribution methods to avoid infection. The most effective solution to protecting your infrastructure from this malicious program is to steer clear of downloading attachments and files from senders and sources you do not know or trust.

You can also check any suspicious file or URL in the ANY.RUN sandbox to receive a conclusive verdict on whether it is malicious or not.
HAVE A LOOK AT

MassLogger screenshot
MassLogger
masslogger
MassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems. It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
Read More
NetSupport RAT screenshot
NetSupport RAT
netsupport
NetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
Read More
GuLoader screenshot
GuLoader
guloader
GuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
Read More
StrelaStealer screenshot
StrelaStealer
strela
StrelaStealer is a malware that targets email clients to steal login credentials, sending them back to the attacker’s command-and-control server. Since its emergence in 2022, it has been involved in numerous large-scale email campaigns, primarily affecting organizations in the EU and U.S. The malware’s tactics continue to evolve, with attackers frequently changing attachment file formats and updating the DLL payload to evade detection.
Read More
Latrodectus screenshot
Latrodectus
latrodectus
Latrodectus is a malicious loader that is used by threat actors to gain a foothold on compromised devices and deploy additional malware. It has been associated with the IcedID trojan and has been used by APT groups in targeted attacks. The malware can gather system information, launch executables, and detect sandbox environments. It uses encryption and obfuscation to evade detection and can establish persistence on the infected device.
Read More
Octo screenshot
Octo
octo coper
Octo malware, also known as ExobotCompact or Coper, is a sophisticated Android banking trojan that has evolved from earlier malware family Exobot. It poses a significant threat to financial institutions, mobile users, and enterprise networks.
Read More