Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
29
Global rank
27 infographic chevron month
Month rank
36 infographic chevron week
Week rank

njRAT is a remote access trojan. It is one of the most widely accessible RATs on the market that features an abundance of educational information. Interested attackers can even find tutorials on YouTube. This allows it to become one of the most popular RATs in the world.

Trojan
Type
Middle East
Origin
1 January, 2013
First seen
7 October, 2026
Last seen
Also known as
Bladabindi
Njw0rm

How to analyze njRAT with ANY.RUN

Type
Middle East
Origin
1 January, 2013
First seen
7 October, 2026
Last seen

IOCs

IP addresses
172.211.123.249
48.209.138.189
135.233.95.144
23.207.210.146
34.125.74.130
204.79.197.203
2.21.20.144
162.159.142.9
23.52.181.212
74.179.77.164
20.190.159.2
23.11.206.75
48.192.1.65
104.126.37.178
52.110.17.3
4.150.223.101
52.110.17.46
150.171.28.11
74.178.240.61
150.171.109.99
Hashes
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
e2c2da27bf6e2c2f8d076b9a95419a249754dc51ce6a4940c80b4af6ec9472e1
3d30d22ea3c9d3c0674002ab57562ac017eb56e26d683e451d346e19c6721532
9a30667f8a16794f3a5c4301bc1208356a3b9104dd2e3bbacbfe7ca62d05289e
0e60b52689f3627486b9a77bb4f88bea0d8665a94f7f1ffc960a1fbc427626b7
d1614ad99aded9f6f5c1be7fe7ffa5124bd04a526580da3818ea8a954e852aa6
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
6c69ce0fe6fab14f1990a320d704fee362c175c00eb6c9224aa6f41108918ca6
5f4229d18e5606330146ee13bdf726e10c1e06cbb15368c47f1ae68abe9ce4ba
Domains
crl.microsoft.com
fe3cr.delivery.mp.microsoft.com
th.bing.com
self.events.data.microsoft.com
slscr.update.microsoft.com
ecs.office.com
login.live.com
google.com
www.microsoft.com
activation-v2.sls.microsoft.com
www.bing.com
rony.publicvm.com
ocsp.digicert.com
oneocsp.microsoft.com
settings-win.data.microsoft.com
client.wns.windows.com
edge.microsoft.com
edge-consumer-static.azureedge.net
omex.cdn.office.net
api.edgeoffer.microsoft.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceasmayxgarewr3pgr9svwmg%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbr0tbevyklx7a9ylold9hqmcwdxfgqu3pggslehmvkx8utfb6ncihnaqhycezmaaaale%2bvmfuqbvyaaaaaaaas%3d
https://officeclient.microsoft.com/config16/?lcid=1033&syslcid=1033&uilcid=1033&build=16.0.16026&crev=3
https://ecs.office.com/config/v2/office/outlook/16.0.16026.20146/production/cc?&clientid=%7bd61ab268-c26a-439d-bb15-2a0dedfca6a3%7d&application=outlook&platform=win32&version=16.0.16026.20146&msoversion=16.0.16026.20002&sdx=fa000000002.2.0.1907.31003&sdx=fa000000005.1.0.1909.30011&sdx=fa000000006.1.0.1909.13002&sdx=fa000000008.1.0.1908.16006&sdx=fa000000009.1.0.1908.6002&sdx=fa000000016.1.0.1810.13001&sdx=fa000000029.1.0.1906.25001&sdx=fa000000033.1.0.1908.24001&sdx=wa104381125.1.0.1810.9001&processname=outlook.exe&audience=production&build=ship&architecture=x64&language=en-us&subscriptionlicense=false&perpetuallicense=2019&licensecategory=6&licensesku=professional2019retail&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7b0d00cba4-e6b1-48c5-a4e1-418f896e867a%7d&labmachine=false
https://roaming.svc.cloud.microsoft/rs/roamingsoapservice.svc
https://messaging.lifecycle.office.com/getcustommessage16?app=6&ui=en-us&src=bizbar&messagetype=bizbar&hwid=04111-083-043729&ver=16.0.16026&lc=en-us&platform=10%3a0%3a19045%3a2%3a0%3a0%3a256%3a1%3a&productid=%7b1717c1e0-47d3-4899-a6d3-1022db7415e0%7d%3a00411-10830-43729-aa720%3aoffice%2019%2c%20office19professional2019r_retail%20edition&clientsessionid=%7b0d00cba4-e6b1-48c5-a4e1-418f896e867a%7d&datapropertybag=%7b%22audience%22%3a%22production%22%2c%22audiencegroup%22%3a%22production%22%2c%22audiencechannel%22%3a%22cc%22%2c%22flight%22%3a%22ofsh6c2b1tla1a31%2cofcrui4yvdulbf31%2cofhpex3jznepoo31%22%7d
https://editor.svc.cloud.microsoft/nleditor/cloudsuggest/v1
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is njRAT Malware?

njRAT, also called Bladabindi and Njw0rm is a remote access trojan that is used to remotely control infected machines. Because of its availability, excess of online tutorials, plenty of information, and a robust core feature set along with several implemented evading techniques made njRAT one of the most widely used RATs in the world.

This malware was detected for the first time in 2013, however, some related RATs have been observed by researchers in 2012. The highest surge of njRAT trojan attacks was recorded in 2014 in the middle east, which is the most targeted region for this malware.

In Q2 2024, it became the third most widespread malware according to ANY.RUN's report.

General Information about njRAT

njRAT trojan is built on the .NET framework. This RAT gives hackers the ability to control the victim’s PC remotely. njRAT allows attackers to activate the webcam, log keystrokes, and steal passwords from web browsers as well as multiple desktop apps.

In addition, the malware gives hackers access to the command line on the infected machine. It allows to kill processes as well as remotely execute and manipulate files. On top of that, njRAT is capable of manipulating the system registry. When infected, Bladabindi trojan will collect several bits of information about the PC that it got into, including the name of the computer, operating system number, country of the computer, usernames, and OS version.

Also, this malware is able to target cryptocurrency wallet applications and steal cryptocurrency from PCs. For example, it is known to be able to grab bitcoins and even access credit card information which sometimes can be stored in crypto apps as a means to purchase cryptocurrency.

After infecting a computer the malware uses a variable name and copies into %TEMP%, %APPDATA%, %USERPROFILE%,%ALLUSERSPROFILE% or %windir% – a behavior not uncommon for this time of malware. It can also copy itself into <any string>.exe, to ensure that it will be activated every time the victim switches on their computer.

njRAT trojan has a few tricks up its sleeve to avoid detection by antivirus software. For example, it uses multiple .NET obfuscators to obstruct its code. Another technique that the malware uses is disguising itself into a critical process. This does not allow the user to shut it down. It also makes njRAT hard to remove from the infected PCs. Bladabindi RAT can also deactivate processes that belong to antivirus software, allowing it to stay hidden. njRAT also knows how to detect if it has been run on a virtual machine which helps the attackers to set up countermeasures against researchers.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Authors of Bladabindi are leveraging Pastebin to avoid investigation by cybersecurity researchers. njRAT downloads additional components and executes secondary-stage payloads from Pastebin. So, the malware has no need to establish a traditional command-and-control (C2) server. The Pastebin creates a pathway between njRAT infections and new payloads. With the trojan acting as a downloader, it will grab encoded data dumped on Pastebin, decode, and deploy.

For spreading, njRAT can detect external hard drives connected via USB. Once such a device is detected, the RAT will copy itself onto the connected drive and create a shortcut.

Who created njRAT?

Creators of njRAT are members of an underground hacker community named Sparclyheason. Evidently, they have created a very popular and destructive malware. njRAT was classified as “severe” by Microsoft Malware Protection Center.

In fact, following a large malicious campaign in 2014, Microsoft shut down four million websites in an effort to filter traffic that was going through no-ip.com domains.

njRAT malware analysis

ANY.RUN allows researchers to watch the njRAT in action in an interactive sandbox simulation.
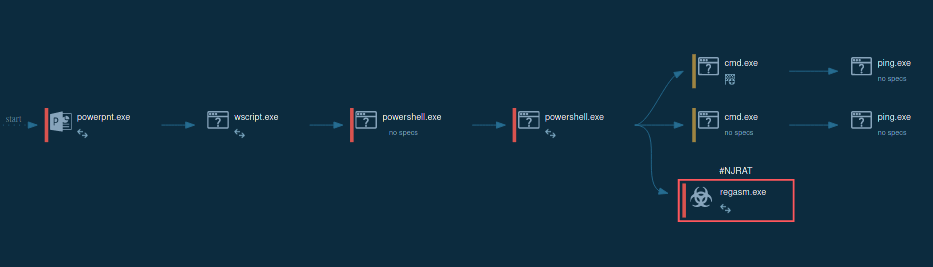
njRAT execution process graph

Figure 1: Displays the lifecycle of njRAT in a visual form as a process graph generated by ANY.RUN malware hunting service
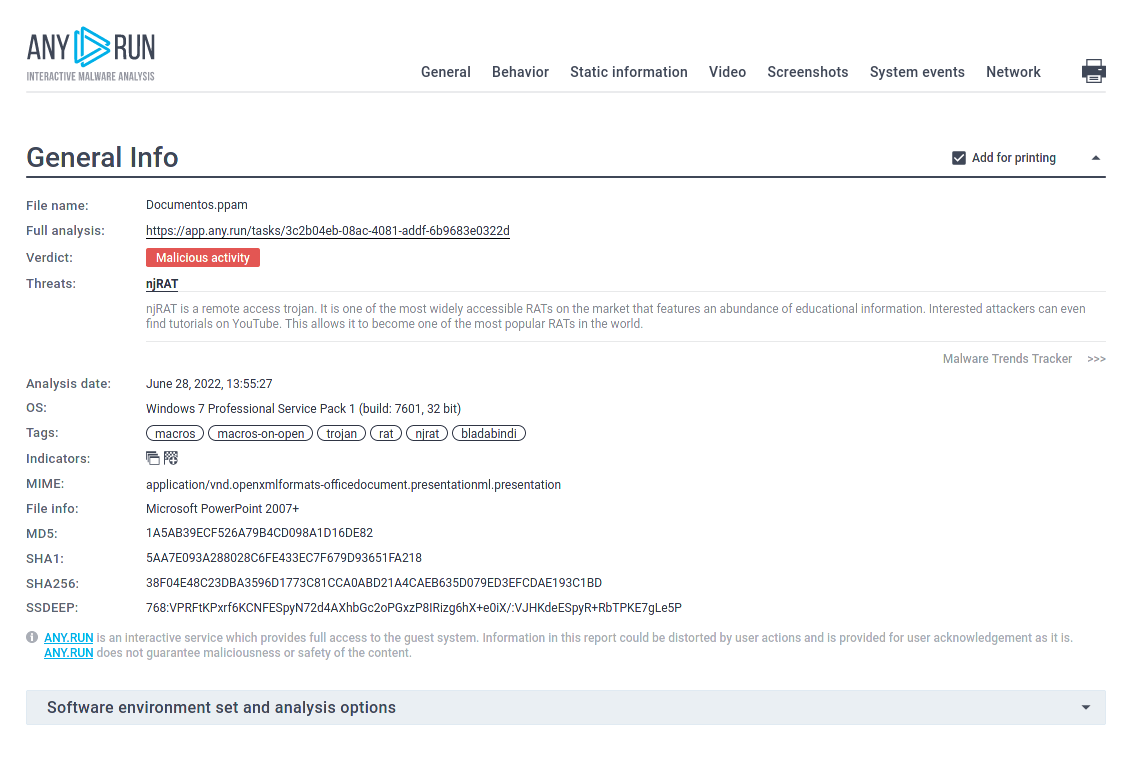
text report of the njRAT malware analysis

Figure 2: A customizable text report generated by ANY.RUN allows to take an even deeper look at the malware and helps to share the research results

njRAT execution process

In our simulation, after njRAT got into the target device and began execution it instantly started its malicious activity. Usually, the initial file renames itself and creates a child process. Sometimes njRAT trojan injects its code into legitimate processes such as RegSvcs.exe and RegAsm.exe.

The malware also has the ability to run itself through Task Scheduler. This child process executes the main malicious activity. Such activity includes stealing information, connecting to C2 servers, and changing the autorun value in the registry to run itself when the operating system starts.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Distribution of njRAT

njRAT trojan uses quite a few attack vectors to infect its victims. For example, the malware is known to target Discord users as part of spam campaigns. In addition, leverage cracks and keygens in well-known software in order to trick users. It installs malicious packages to infect the machine.

Another known distribution method was through a compromised website that tricked users into downloading a fake Adobe product update which in turn installed njRAT malware to the PC. Bladabindi was also featured in phishing email campaigns. In this case, it was delivered to potential victims as a malicious attachment.

In October 2020 mailspam used the 'shipment tracking' theme, faking popular courier and postal services. Malicious packages contain attachments in Zip format with an encoded Visual Basic script (VBE) payload and components.

Moreover, crooks use cloud-based storage platforms more often. Attackers host malicious files there to deliver malicious software, and even use them as part of a command and control (C&C) architecture. That is why it's crucial to know general malware removal instructions and analyze viruses in a safe environment.

How to detect NJRAT using ANY.RUN?

To determine whether the sample under review is njRAT or not, you can take a look at the changes that it made in the registry. To do so, open the Advanced details of process section of the malicious process and look at the "Registry changes" tab in the "Events" section. If a process has created a key with the name [kl] into the path HKEY_CURRENT_USER\Software\32_characters_and_digits, you can be sure that the given sample is njRAT.
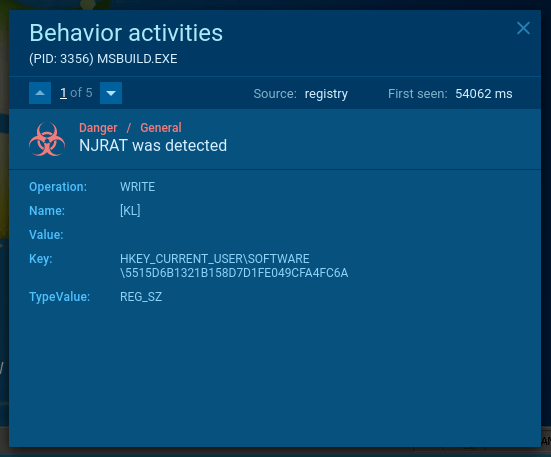
njrat registry changes Figure 3: Сhanges made by njRAT in registry

Conclusion

The relative ease of operation, multiple tutorials on how to set up this malware, and very extensive information stealing feature set have made this RAT one of the most popular remote access trojans in the world.

Even though the peak of its activity was recorded in 2014 and targeted mostly the middle east and India, the njRAT trojan remains to be extremely popular today. This malware is known to have targeted both private and corporate victims and poses a lot of danger to internet users, especially considering that it can be delivered by packages to potential victims in several ways, and preventing infection is much harder in some cases than in others.

Even though Bladabindi malware creators have taken several steps to hinder the analysis, malware hunting services like ANY.RUN allows professionals to easily study njRAT malware samples or other RATs like Orcus RAT or WSHRAT and share the research results with the world to improve global cybersecurity.

Create your free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
Bluesky Ransomware screenshot
BlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
Read More
BlackMoon screenshot
BlackMoon
blackmoon
BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.
Read More