Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Remcos

11
Global rank
4 infographic chevron month
Month rank
5
Week rank

Remcos is a commercially distributed remote administration and surveillance tool that has been widely observed in unauthorized deployments, where threat actors use it to perform remote actions on compromised machines. It is actively maintained by its vendor, with new versions and feature updates released on a frequent, near-monthly basis.

Remote access tool
Type
Unknown
Origin
1 June, 2016
First seen
8 October, 2026
Last seen

How to analyze Remcos with ANY.RUN

Remote access tool
Type
Unknown
Origin
1 June, 2016
First seen
8 October, 2026
Last seen

IOCs

IP addresses
172.67.214.31
104.21.23.229
48.209.133.15
74.179.77.204
23.11.41.157
172.211.123.248
150.171.109.104
204.79.197.203
20.190.159.128
23.59.18.102
135.232.92.97
48.192.1.65
2.16.204.156
48.192.1.64
188.114.96.3
172.67.181.103
188.114.97.3
104.21.90.207
172.67.199.194
48.209.138.168
Hashes
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
e2c2da27bf6e2c2f8d076b9a95419a249754dc51ce6a4940c80b4af6ec9472e1
957c6fe441e5328b5cb1d15a51034a50555edf70d22d5d49d9a0f6100dab73c2
8c948fcbb8b8a0ef398d54d3c46020e8dc7a7c71c90962aae3f762a935ff65bd
db830cf9011121e79ba4a1207886b38ad57f36090924b5057101e9b7c587162b
6f0021d57484a1c20b2cc77c68cd456878e9cb53de589103cd47ca6198c923d3
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
ef0ad71e7061479b7f95e1df58f265ad0787f21c042b9104adc1acd71172d174
1c65be1230c5c2370a158fdda18d3c96da557657a6d6fd417a8f466dd6674cab
f504f00e5cd1426bd5ae13d91bf1e1bcc0a30a7b79444435f9098f01b59d3001
34931cd28b1a57618529b58777e9d3f352aaed4d4f75227b8a58e60faf047932
fb7cb1281e59d9c480dadef87714ffd9959925ceca62a0e5edf0239f542c4e2d
0e60b52689f3627486b9a77bb4f88bea0d8665a94f7f1ffc960a1fbc427626b7
d1614ad99aded9f6f5c1be7fe7ffa5124bd04a526580da3818ea8a954e852aa6
b6b10a07faa634027f3780e77fc3b165dcf7d37e800195bff5e147ccc492b828
9867cd38dbcd58ea2759199eda7ac0fa47b070a76398890d7e05b5a7df9dc935
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
a8caa227bb4d3f5f831ba8756cb24a675dc0a97043eeefbdc0fca0b47ff3dd69
15fe159b564d7aea28f48dcb0ad9d32863da9cbff6a9c9707e83f05c773e1155
8804d2766bdbe34b6d37ee6494630bdffa6263d7ecd7433a869f6110404e2c22
Domains
qq88198.com
ocsp.digicert.com
slscr.update.microsoft.com
api.qq88198.com
backdoor.qq88198.com
activation-v2.sls.microsoft.com
oneocsp.microsoft.com
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
google.com
self.events.data.microsoft.com
malware.qq88198.com
c2.qq88198.com
crl.microsoft.com
www.microsoft.com
ecs.office.com
www.bing.com
settings-win.data.microsoft.com
www.qq88198.com
login.live.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f8%2f2026%2c%204%3a21%3a33%20am
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.dd482747-0b27-423b-a458-0ac58ffc4b0e&pid=dsb
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://31.40.204.114/1.jpg
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 230
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2820
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4352
comments 0

What is Remcos?

Remcos is a commercially distributed remote administration and surveillance tool developed and marketed by Breaking Security, a company registered in Hong Kong. The tool is advertised for legitimate purposes including remote device management, authorized penetration testing, security audits, and approved remote administration.

However, security researchers and threat intelligence organizations have extensively documented abuse of Remcos by unauthorized threat actors in numerous phishing campaigns, espionage operations, and targeted attacks against critical infrastructure, government agencies, and commercial organizations.

Remcos: Technical details

Remcos has been available since 2016 and receives active updates with new releases documented nearly every month. The tool is sold through legitimate commercial channels.

The software is equipped with features commonly found in remote administration tools, such as remote desktop control, file management, keystroke logging, and screenshot capabilities. These same technical capabilities have made it an effective tool for malicious deployment by threat actors when installed without authorization.

Unauthorized deployments of Remcos employ multiple delivery techniques in phishing campaigns. Threat actors have been observed distributing Remcos through deceptive executable files with names designed to appear legitimate, as well as through Microsoft Office documents that exploit application vulnerabilities to facilitate remote payload download and execution. Such cases also involve the use of anti-analysis techniques and code obfuscation to evade detection by security software.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Remcos analysis in a malware sandbox

ANY.RUN’s Interactive Sandbox provides a safe, cloud-based environment for detonating programs and URLs to detect the presence of malicious activity.

ANY.RUN sandbox analysis of an unauthorized Remcos deployment documents the following execution chain:
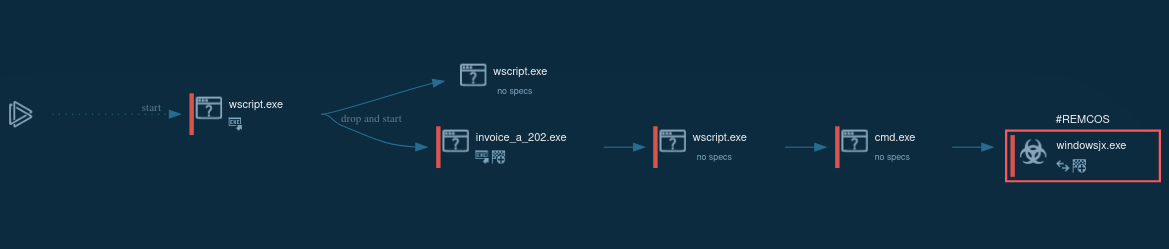
  • Following initial compromise through phishing vectors, observed samples initiated Visual Basic Script (VBS) execution, which spawned command-line processes to download and execute the primary Remcos payload.

process graph of the Remcos execution Figure 1: Displays the lifecycle of an unauthorized Remcos use as presented by a visual graph generated by ANY.RUN
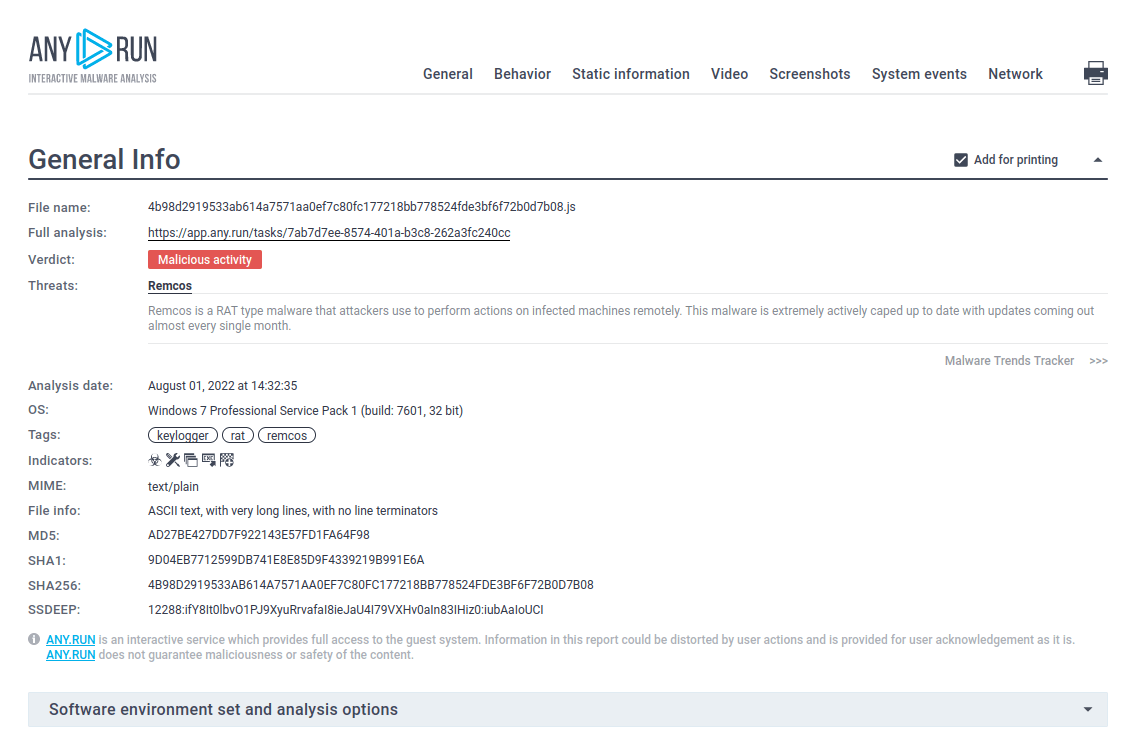
  • Post-execution behaviors documented in threat intelligence include information collection activities, registry modification to establish persistence mechanisms, and command-and-control (C2) server communication to enable remote operator control.
  • These execution patterns are consistent with documented threat actor campaigns using Remcos for unauthorized access and data collection operations.

text report 0f the Remcos trojan analysis Figure 2: A customizable text report generated by ANY.RUN is a feature specifically developed to simplify the sharing of analysis results.

How to detect Remcos using ANY.RUN’s Interactive Sandbox?

Security analysts can identify unauthorized Remcos deployments through registry artifact analysis. Threat actors deploying Remcos have been observed creating registry entries in the user hive containing identifying markers.
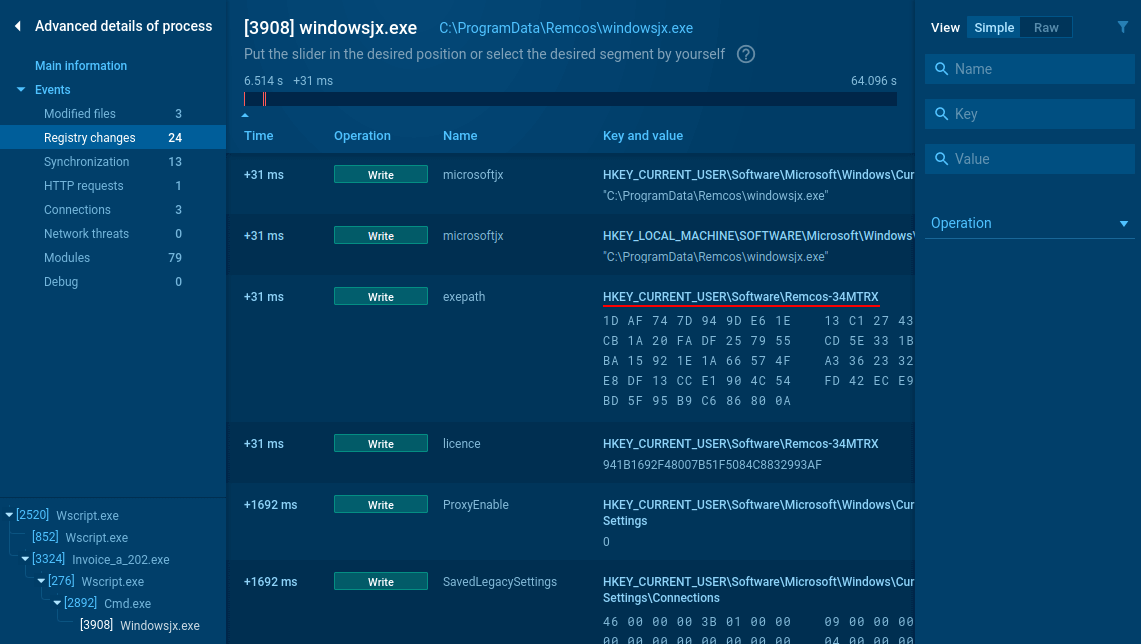
remcos log file Figure 3: Remcos registry changes analysis

When analyzing suspicious processes in ANY.RUN’s Interactive Sandbox, examiners can review registry modification events by selecting the process and accessing the detailed information view. The presence of registry keys matching the pattern "HKEY_CURRENT_USER\Software\Remcos-{digits_letters}" is a strong indicator of unauthorized Remcos deployment and can be used as a forensic artifact for detection and incident response.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Gathering Threat Intelligence on Remcos Deployments

Security teams can collect up-to-date intelligence on unauthorized Remcos deployments using ANY.RUN’s Threat Intelligence Lookup.

The service provides access to a centralized repository of millions of IOCs, IOAs, and IOBs extracted from live interactive malware analysis sessions conducted in the ANY.RUN Sandbox by a community of 500,000+ researchers and 15,000 SOCs.

With 40+ customizable search parameters—including file hashes, IPs, domains, command lines, registry paths, MITRE techniques, and process artifacts—analysts can efficiently identify and correlate Remcos-related indicators across sandbox sessions.
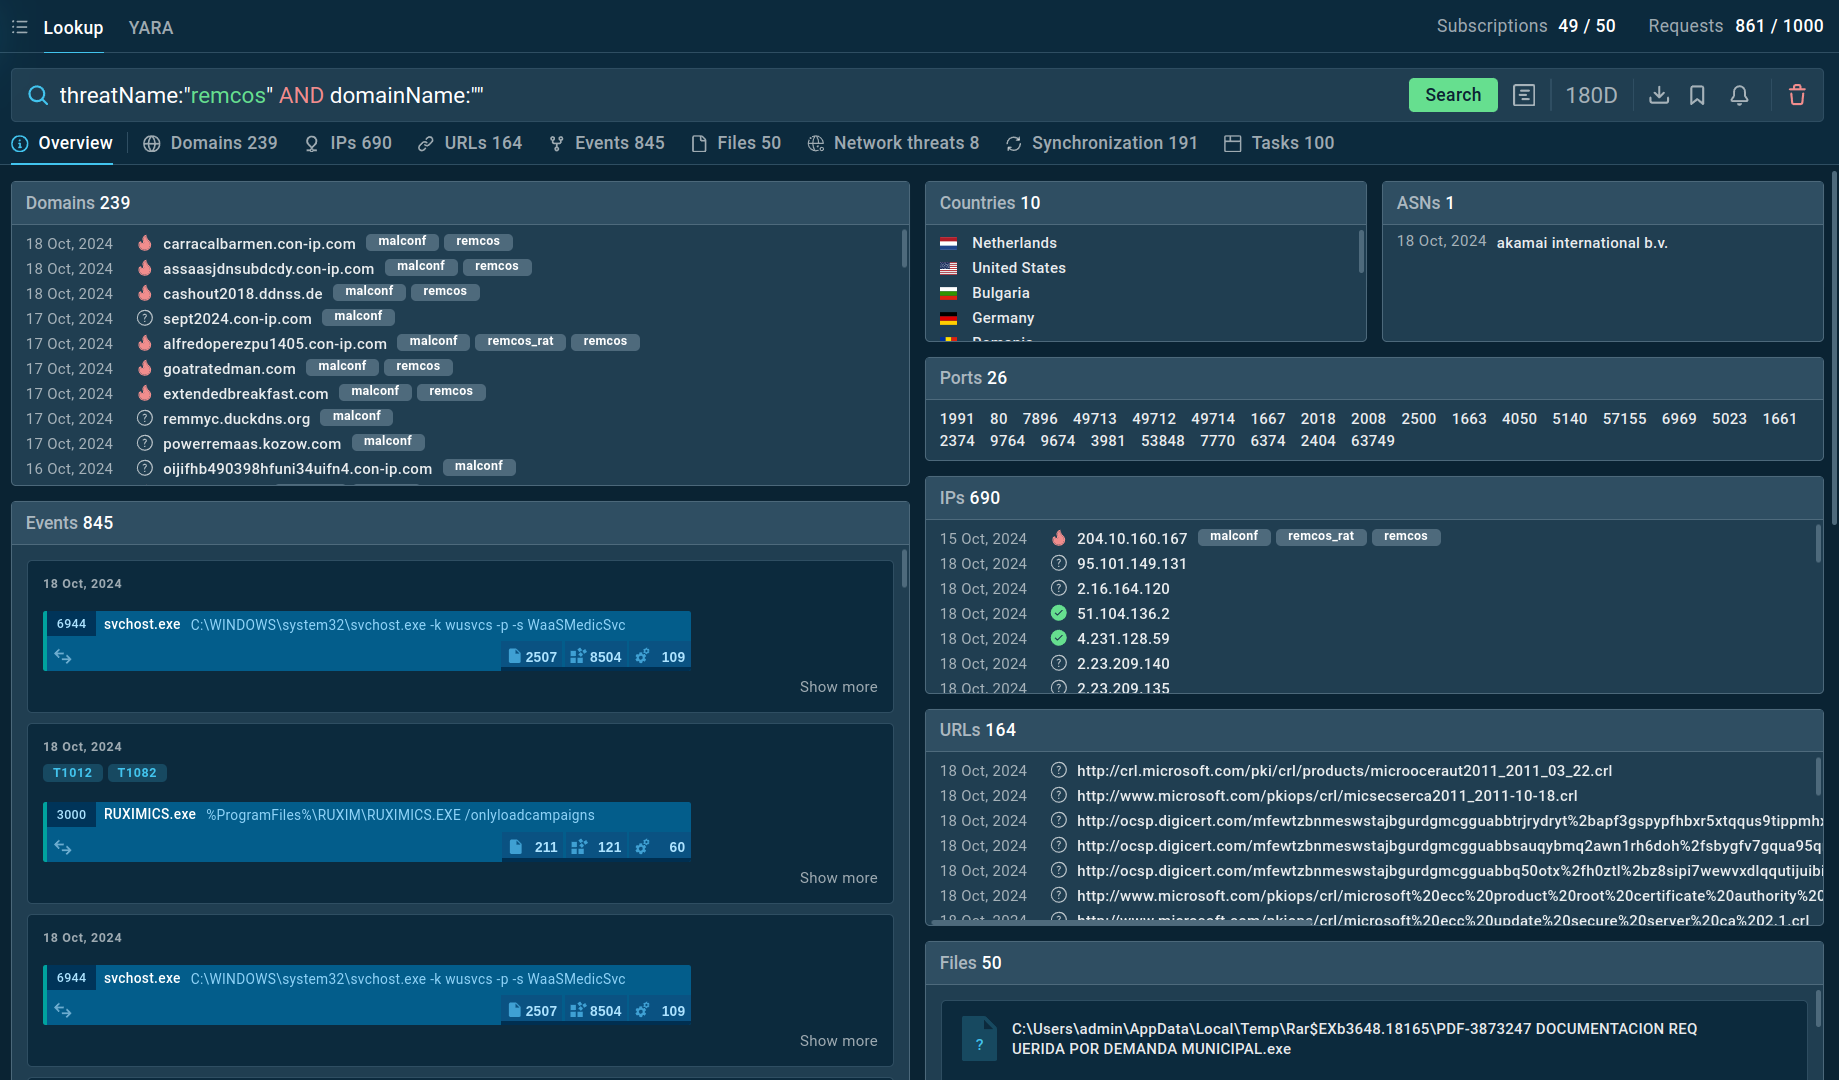
Remcos ANY.RUN Figure 4: Search results for Remcos in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"remcos" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from Remcos samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Remcos Deployment Methods in Malicious Campaigns

Threat intelligence reports document multiple distribution vectors for unauthorized Remcos deployments, including bundling with mass mailing tools marketed as legitimate distribution services. Analysis of phishing campaigns reveals that Remcos payloads most frequently arrive via malicious email attachments, with threat actors employing social engineering lures to prompt users to enable macros in Microsoft Office documents.

A common attack chain:

  • Phishing emails with deceptive lures targeting specific industries (news media, energy sector)
  • Office documents requiring macro activation to initiate payload reconstruction
  • Dropper execution in standard locations (%APPDATA%, %TEMP%)
  • Secondary download of primary Remcos payload from actor-controlled infrastructure

Once macros are enabled, the reconstructed executable downloads and launches the Remcos component, establishing persistence and C2 communication as documented in sandbox executions.

Conclusion

Unauthorized deployments of Remcos represent a significant security concern, as threat actors can obtain access to feature-rich remote access capabilities at relatively low cost and leverage them to manage compromised hosts at scale. When abused in this way, Remcos has been used to create and control networks of infected devices, exfiltrate data, and maintain long-term access in support of broader malicious campaigns.

Fortunately, modern analysis and threat intelligence solutions provide security teams with extensive capabilities to investigate suspicious samples, observe execution behavior, and enrich indicators related to Remcos-based activity. Interactive sandboxing and integrated threat intelligence from ANY.RUN enable analysts to safely analyze suspected Remcos deployments, correlate them with known campaigns, and implement effective countermeasures across their environments.

Create an ANY.RUN account to start your first investigation!
HAVE A LOOK AT

BlindEagle screenshot
BlindEagle
blindeagle
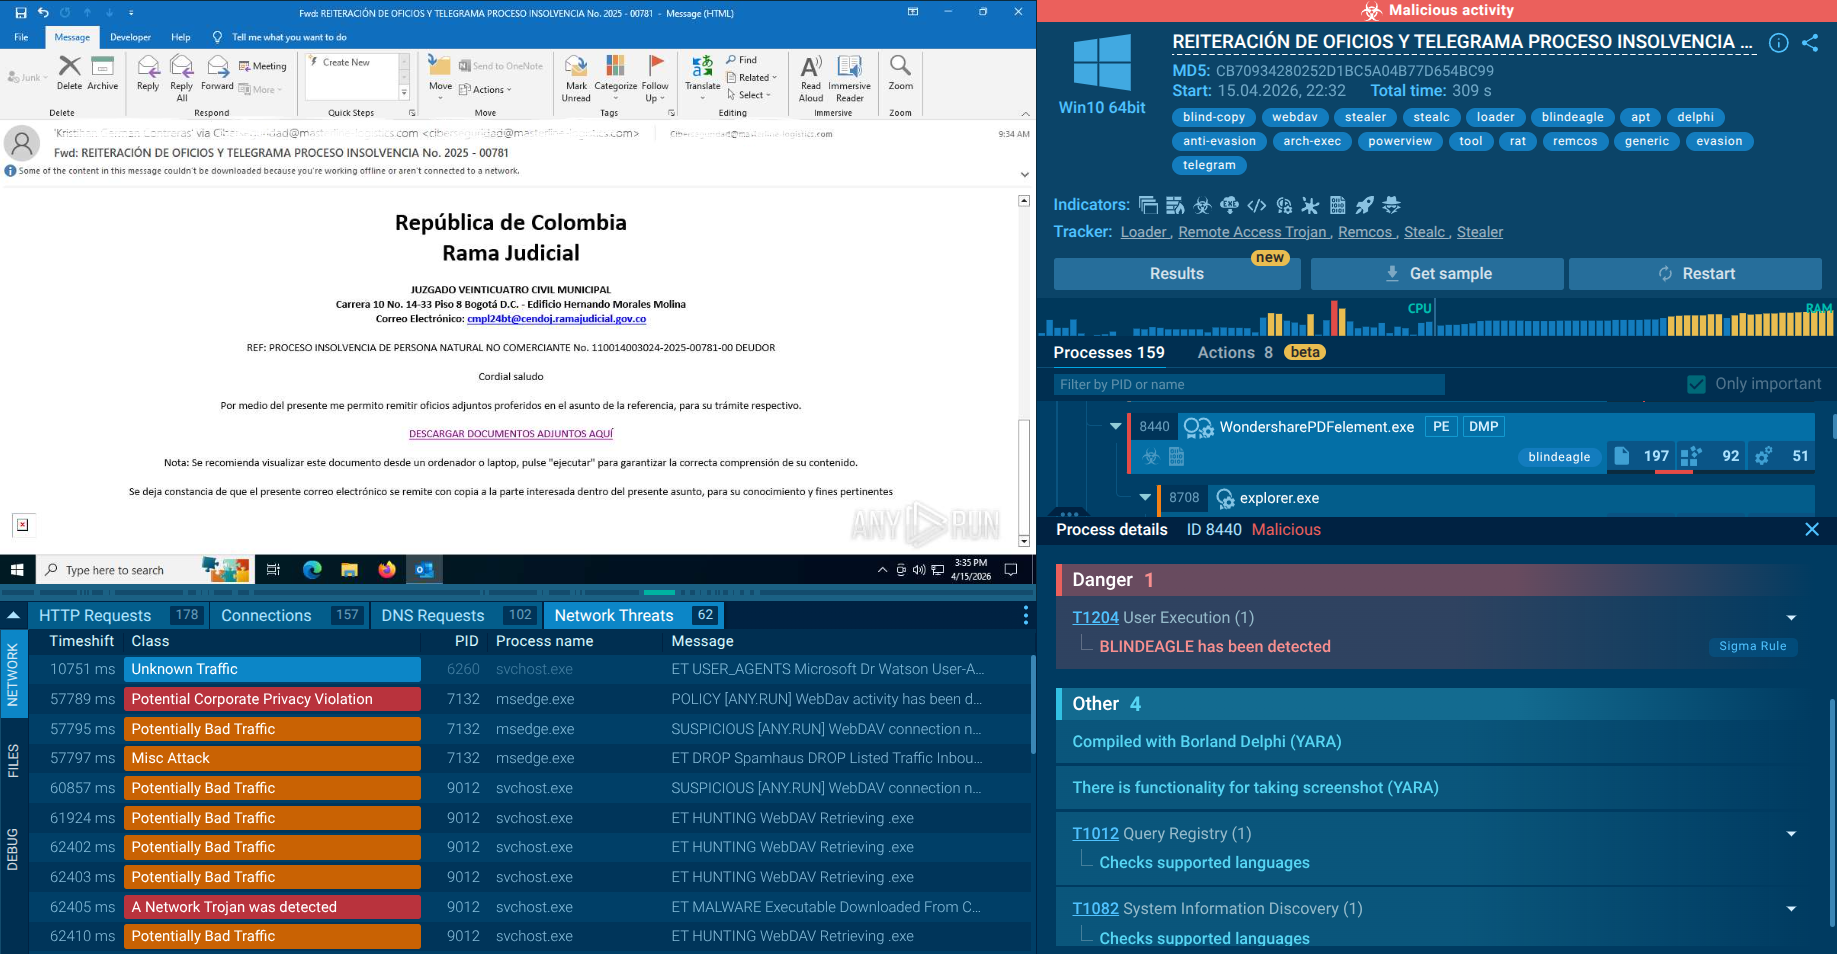
BlindEagle is a cyber threat actor primarily associated with espionage and credential theft campaigns targeting organizations in Latin America, especially Colombia. Active since at least 2018, the group relies heavily on phishing, remote access trojans (RATs), PowerShell scripts, and social engineering to infiltrate systems and maintain persistence. BlindEagle is known for continuously evolving its delivery mechanisms and malware stack to bypass detection and compromise high-value targets.
Read More
Emmenhtal screenshot
Emmenhtal
emmenhtal
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
Read More
Crypto malware screenshot
Crypto malware
miner xmrig jsminer
Crypto mining malware is a resource-intensive threat that infiltrates computers with the purpose of mining cryptocurrencies. This type of threat can be deployed either on an infected machine or a compromised website. In both cases the miner will utilize the computing power of the device and its network bandwidth.
Read More
Gunra screenshot
Gunra
gunra
Gunra ransomware, a financially motivated threat actor that emerged in April 2025, deploys double-extortion tactics to encrypt victims' data and threaten leaks of exfiltrated information, primarily targeting Windows and Linux systems across healthcare, manufacturing, and other sectors worldwide.
Read More
Tycoon 2FA screenshot
Tycoon 2FA
tycoon
Tycoon 2FA is a phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) protections, particularly targeting Microsoft 365 and Gmail accounts. Its advanced evasion techniques and modular architecture make it a significant threat to organizations relying on MFA for security.
Read More
X-Files screenshot
X-Files
xfiles
X-FILES Stealer is a sophisticated malware designed to infiltrate systems and steal sensitive information, targeting login credentials for email, social media, and other personal accounts. It captures data and transmits it back to the attacker’s command-and-control server. X-FILES Stealer employs advanced evasion techniques to avoid detection, making it a persistent threat in the cyber landscape.
Read More