Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Lumma

25
Global rank
29 infographic chevron month
Month rank
35 infographic chevron week
Week rank

Lumma is an information stealer, developed using the C programming language. It is offered for sale as a malware-as-a-service, with several plans available. It usually targets cryptocurrency wallets, login credentials, and other sensitive information on a compromised system. The malicious software regularly gets updates that improve and expand its functionality, making it a serious stealer threat.

Stealer
Type
ex-USSR
Origin
1 August, 2022
First seen
7 October, 2026
Last seen
Also known as
Lumma Stealer
LummaC2 Stealer

How to analyze Lumma with ANY.RUN

Type
ex-USSR
Origin
1 August, 2022
First seen
7 October, 2026
Last seen

IOCs

IP addresses
2.16.204.136
20.190.160.131
150.171.28.11
142.251.14.139
3.250.92.156
150.171.22.17
150.171.109.107
150.171.109.100
204.79.197.203
23.11.41.157
192.178.183.132
23.194.190.156
150.171.27.11
2.21.239.135
74.178.76.128
104.18.22.222
48.209.6.48
23.59.18.102
172.211.123.250
74.179.77.164
Hashes
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
6c69ce0fe6fab14f1990a320d704fee362c175c00eb6c9224aa6f41108918ca6
5f4229d18e5606330146ee13bdf726e10c1e06cbb15368c47f1ae68abe9ce4ba
ec78ddd4ccf32b5d76ec701a20167c3fbd146d79a505e4fb0421fc1e5cf4aa63
41ce6a7b18364efecced0419b42165d4f86c43643bbe1043014d4142cf86186a
57f81a5fcbd1fefd6ec3cdd525a85b707b4eead532c1b3092daafd88ee9268ec
89082fb05229826bc222f5d22c158235f025f0e6df67ff135a18bd899e13bb8f
e848603b7a73a88e3fe7bffa20e83397f5d1e93e77babb31473cc99e654a27b7
985976b776e729835e047c81d3d731a6c488a6459aa8918dbc8ec808c0bf73a1
Domains
clients2.googleusercontent.com
edge.microsoft.com
th.bing.com
copilot.microsoft.com
config.edge.skype.com
www.bing.com
update.googleapis.com
crl.microsoft.com
client.wns.windows.com
edge-consumer-static.azureedge.net
www.microsoft.com
ecs.office.com
api.edgeoffer.microsoft.com
self.events.data.microsoft.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
targett.top
google.com
ocsp.digicert.com
slscr.update.microsoft.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:bkce-1l1d2kjubygveijh3jndf5zvv6mjtq67acq0xe&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
http://targett.top/
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791399817&lafgdate=0
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d292%2526e%253d1
https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
https://update.googleapis.com/service/update2/json?cup2key=14:afjez1qjv4prdbqejolzusblay6cu5paft1hscqry2a&cup2hreq=b3018a3e70876275cf036d429fbe71961b6c0e0c21ceaeda52560dcc4daa8c33
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://clients2.googleusercontent.com/crx/blobs/azpvhcqildrgqxyclcenwovmaua7lwu2mln7dephdl7eqkp9gczqmiehkjncu7a_eigr4ip8elijgyg1mgbqewwsojngu_j8zva9cfi_aj--ikwjbypwnpfv9nmzws17bigaxlka5c7tdptpcgaddf44n1nzr3cqv7qk/ghbmnnjooekpmoecnnnilnnbdlolhkhi_1_110_1_0.crx
https://edge.microsoft.com/abusiveadblocking/api/v1/blocklist
https://edge.microsoft.com/autofillservice/core/page/-3047183916597030249/3890546538494314769?cidalgoversion=2
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is Lumma Stealer malware?

Lumma is a widely accessible malware stealer that is sold openly across Dark Web forums and Telegram channels. Although not as popular as other stealers, such as RedLine and Formbook, it has gained considerable traction among cybercriminals that focus on exfiltrating sensitive information from unsuspecting victims. Operated by a group believed to originate from former USSR countries, LummaC2 Stealer has been actively evolving since its initial emergence in 2022, getting substantial updates that enhance its capabilities.

Lumma Stealer poses a significant threat to a wide range of computer systems, targeting devices running Windows operating systems from Windows 7 up to Windows 11. This broad compatibility allows the malware to infiltrate a vast network of systems, increasing its potential reach and impact.

Since it operates under a malware-as-a-service model, Lumma Stealer is accessible to anyone with the financial means to purchase a subscription. This accessibility has contributed to the malware's widespread adoption. There are three subscription plans, each providing a varying range of features to users, including access to a command-and-control (C2) panel, which allows criminals to monitor and manage the malware's activities on compromised machines.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of the Lumma Stealer malicious software

Lumma enables criminals to engage in a variety of illicit activities and a has a long list of capabilities, including:

  • Data exfiltration: The malware effectively gathers sensitive information from targeted applications, including login credentials, financial data, and personal details.
  • Regular updates: LummaC2 Stealer receives automatic updates on a regular basis.
  • Data log collection: Lumma Stealer collects detailed data logs from compromised endpoints, including information extracted from browsers and cryptocurrency wallets.
  • Loader capability: The stealer can drop additional malware onto compromised machines, expanding its malicious capabilities and potential impact.

Lumma malware analysis shows a vast range of features that make it a versatile tool for cybercriminals. For instance, all data transmitted by the stealer is decrypted on the server side, which makes it more difficult to analyze the malware’s traffic during the exfiltration process.

Another notable capability of the malware is its neighbor detection, which notifies operators about other instances of the malware running on the same system. The malware supports ARM, x86, and x64 architectures, demonstrating its cross-platform compatibility and ability to target a wide range of devices.

The stealer can also be configured to be used via a Telegram bot.

Execution process of Lumma Stealer

ANY.RUN lets us expose the malicious activities of Lumma Stealer and collect IOCs by uploading its sample to the sandbox.

Since stealers are trying their best to hide their activities, the execution chain of malware Lumma is kept as simple as possible. Therefore, there are not a lot of processes, and no usage of system tools occurs inside the infected OS. After the payload makes its way into the infected system, it immediately starts execution.
Lumma graph shown in ANY.RUN The process graph of Lumma Stealer demonstrated by the ANY.RUN sandbox

The only process of the malware is responsible for carrying out all malicious activities, including data theft, C&C server communication, etc. If there is no connection with the C&C, Lumma stops its execution.

Gathering threat intelligence on Lumma malware

To collect up-to-date intelligence for Lumma stealer malware analysis and better understand what is Lumma malware, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Lumma Stealer.
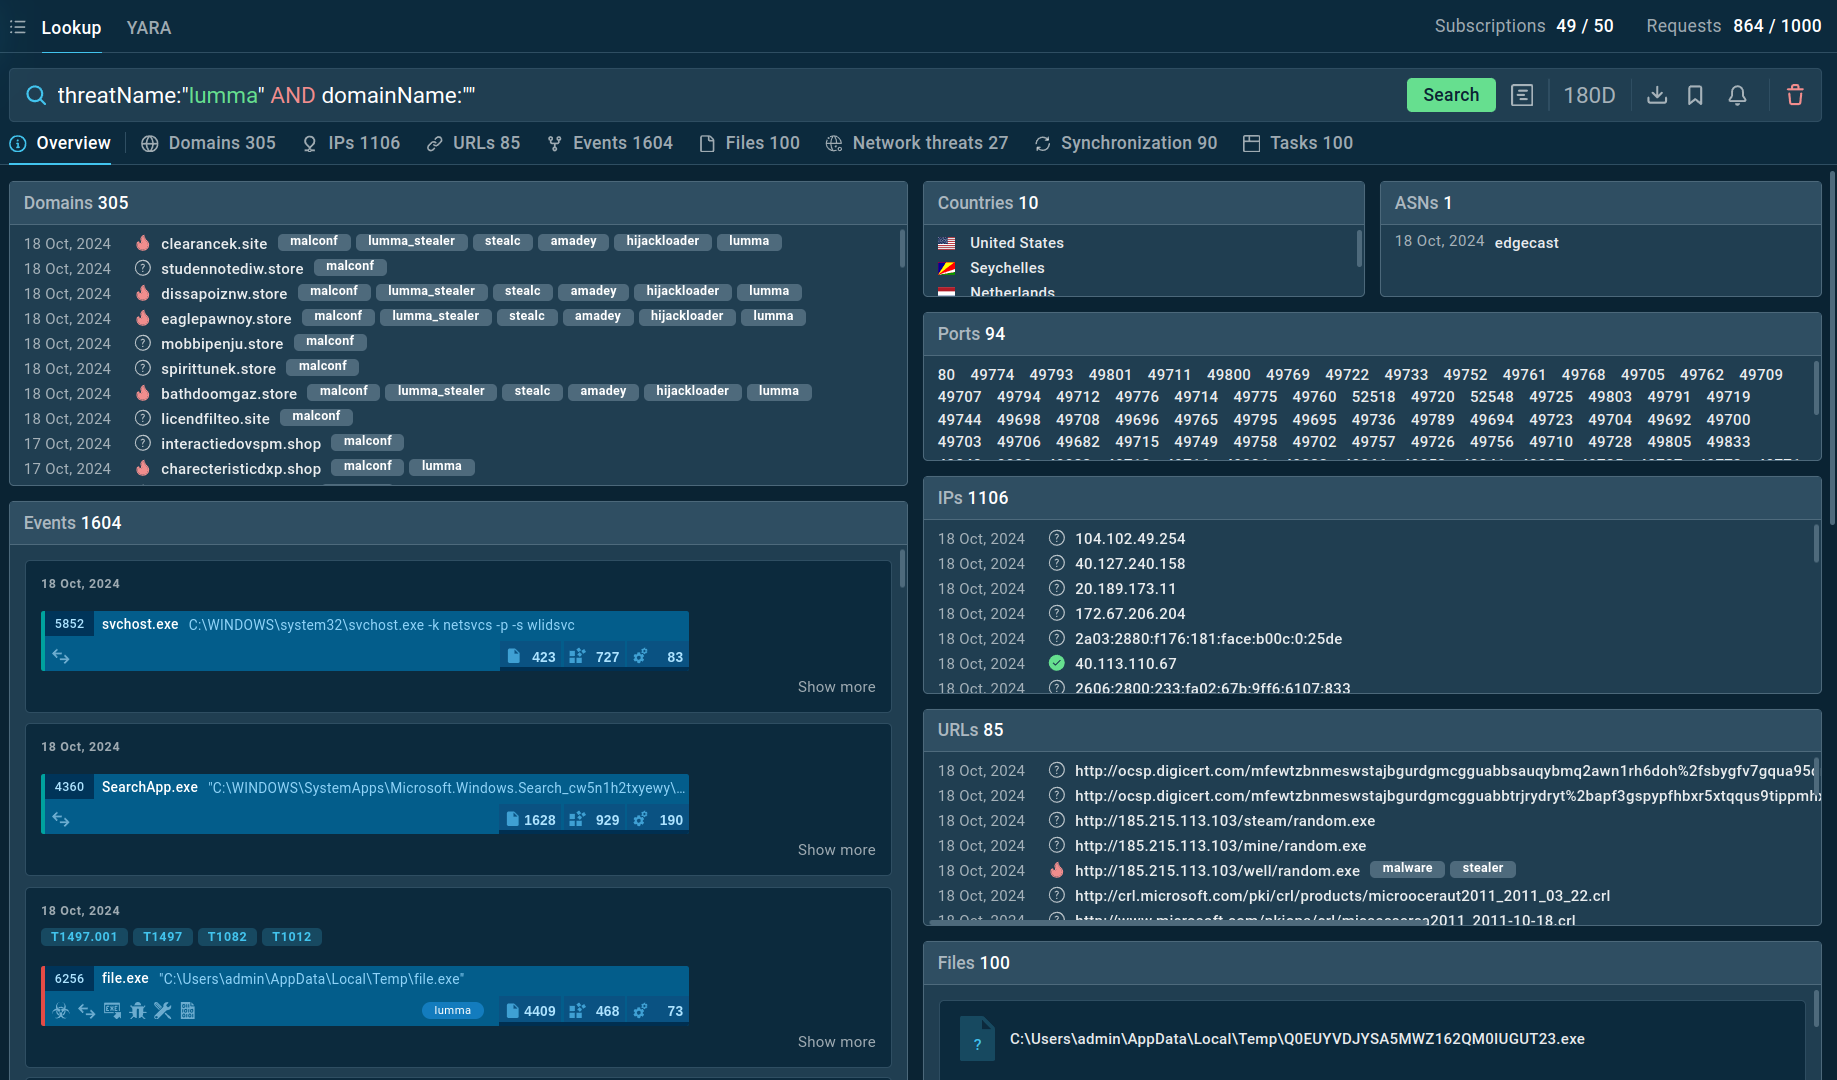
Lumma ANY.RUN Search results for Lumma Stealer in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"Lumma" AND domain:"" will generate a list of files, events, domain names, and other data extracted from Lumma samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Distribution methods of the Lumma Stealer malware

Lumma malware is utilized by numerous threat actors, both individuals and groups, who employ a variety of ways to deliver the payload to the target system.

  • Fake Software: One of the most prevalent methods used to distribute Lumma Stealer is through fake software. When unsuspecting users download and install these fake applications, they introduce the malware onto their systems.
  • Phishing Emails: Phishing emails remain a widely used attack vector for malware distribution, including Lumma Stealer. Cybercriminals craft emails that appear to be from legitimate sources, such as banks, e-commerce platforms, or social media networks.
  • Discord Messages: In some cases, Lumma Stealer operators have taken to targeting users through direct messaging on Discord, a popular chat platform. These actors engage with victims, attempting to build trust and persuade them to download infected executables under false pretenses.

Conclusion

The growing threat of LummaC2 Stealer calls for a proactive approach to cybersecurity. As this malware becomes more common, individuals and organizations must be aware of its diverse delivery methods and take steps to protect themselves. Malware analysis sandboxes, such as ANY.RUN are a valuable tool for identifying and analyzing Lumma Stealer.

ANY.RUN is an advanced tool that provides a unique way to study malware. You can interact with infected systems in a safe cloud environment to observe how the malware behaves. It goes beyond simple observation by generating a detailed report that includes IOCs and malware configuration information, enabling you to take action against malware threats.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

Greatness screenshot
Greatness is a Phishing-as-a-Service (PhaaS) platform that enables cybercriminals, even those with limited technical skills, to launch sophisticated phishing attacks primarily targeting Microsoft 365 (M365) credentials. It acts as a man-in-the-middle (MitM) proxy, facilitating credential theft and MFA bypass while providing affiliates with easy-to-use tools like attachment builders and Telegram notifications.
Read More
Godfather screenshot
Godfather
godfather
The Godfather malware is an Android banking Trojan capable of bypassing MFA that targets mobile banking and cryptocurrency applications. Known for its ability to evade detection and mimic legitimate software, it poses a significant threat to individuals and organizations by stealing sensitive data and enabling financial fraud.
Read More
Backdoor screenshot
Backdoor
backdoor
A backdoor is a type of cybersecurity threat that allows attackers to secretly compromise a system and conduct malicious activities, such as stealing data and modifying files. Backdoors can be difficult to detect, as they often use legitimate system applications to evade defense mechanisms. Threat actors often utilize special malware, such as PlugX, to establish backdoors on target devices.
Read More
Gh0st RAT screenshot
Gh0st RAT
gh0st
Gh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.
Read More
Cobalt Strike screenshot
Cobalt Strike
cobaltstrike
Cobalt Strike is a legitimate penetration software toolkit developed by Forta. But its cracked versions are widely adopted by bad actors, who use it as a C2 system of choice for targeted attacks.
Read More
Phobos screenshot
Phobos
phobos ransomware
Phobos is a ransomware that locks or encrypts files to demand a ransom. It uses AES encryption with different extensions, which leaves no chance to recover the infected files.
Read More