Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
23
Global rank
18
Month rank
17 infographic chevron week
Week rank

FormBook is a data stealer that is being distributed as a MaaS. FormBook differs from a lot of competing malware by its extreme ease of use that allows even the unexperienced threat actors to use FormBook virus.

Spyware
Type
Unknown
Origin
1 January, 2016
First seen
8 October, 2026
Last seen
Also known as
Xloader

How to analyze Formbook with ANY.RUN

Type
Unknown
Origin
1 January, 2016
First seen
8 October, 2026
Last seen

IOCs

IP addresses
104.21.69.83
52.123.128.14
204.79.197.203
40.126.31.67
81.88.57.70
48.209.6.48
150.171.110.209
172.211.123.249
74.179.77.204
195.110.124.133
2.16.204.138
2.16.168.50
23.11.41.157
52.110.17.34
150.171.109.106
48.192.1.65
4.150.223.108
135.233.95.135
128.24.231.64
23.59.18.102
Hashes
0e60b52689f3627486b9a77bb4f88bea0d8665a94f7f1ffc960a1fbc427626b7
d1614ad99aded9f6f5c1be7fe7ffa5124bd04a526580da3818ea8a954e852aa6
9867cd38dbcd58ea2759199eda7ac0fa47b070a76398890d7e05b5a7df9dc935
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
a8caa227bb4d3f5f831ba8756cb24a675dc0a97043eeefbdc0fca0b47ff3dd69
15fe159b564d7aea28f48dcb0ad9d32863da9cbff6a9c9707e83f05c773e1155
8804d2766bdbe34b6d37ee6494630bdffa6263d7ecd7433a869f6110404e2c22
bf02b8145c23041a63b1effc7e682f7e133c10586d109059bdfb0e9bba379ab9
1afc60240d835261992e3b373b472c22ce227b80ed5c79da1f5c25c7e0a22580
6fd389580859411d5a1bc228f47f56aef1431807950d296f804a1879057ad54e
15a6bf64d615ecdd929e16310b499a876ef26a011b1ef890bd1e940b0ef6edd1
46573c4bd738ddf92013ecffe025f55007b6aac9cdae1b7d5aa430eb23d488b2
b8edfd927d5ea3aa0b3bcd61b672c31947f864a307c5b2e2d0907514e3fae053
9b1c2cc904339abf0fef2480db8ed4934d6ae6c220280d5bd7c2ffda02078197
880173bc91f18375ee9175f958ba3f874efe3b521de81dddcc00a0e8fdf07435
a03dbfd0e2016d6098bcbcd39239fa02d4e16c3cf36e835874a9039a79ae4c1a
bfed9d59257c1987f97cf254231ee7e246c71b9009673f38d62516ff0ecafd9c
ceee2d9677558913f0ecc78a600c2cc262f848c84e0511761f82f4a64e97b8b7
56f9cb3dea3fd96f5d26bd2f66fad03c2dfe17f83e9f473787d5a5bc7f27d7f3
3cc3fb7c0f9859c6df5255a6de848b7f42d8f4cf81c77d8ff44d45c7ad3669ac
Domains
slscr.update.microsoft.com
editor.svc.cloud.microsoft
www.sineshub.online
fe3cr.delivery.mp.microsoft.com
www.notforspoofing.net
self.events.data.microsoft.com
roaming.svc.cloud.microsoft
messaging.lifecycle.office.com
ecs.office.com
oneocsp.microsoft.com
activation-v2.sls.microsoft.com
crl.microsoft.com
www.microsoft.com
www.bing.com
www.s2bconstruction.ca
officeclient.microsoft.com
ocsp.digicert.com
client.wns.windows.com
settings-win.data.microsoft.com
omex.cdn.office.net
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceasmayxgarewr3pgr9svwmg%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbr0tbevyklx7a9ylold9hqmcwdxfgqu3pggslehmvkx8utfb6ncihnaqhycezmaaaale%2bvmfuqbvyaaaaaaaas%3d
https://officeclient.microsoft.com/config16/?lcid=1031&syslcid=1031&uilcid=1031&build=16.0.16026&crev=3
https://ecs.office.com/config/v2/office/outlook/16.0.16026.20146/production/cc?&clientid=%7bd61ab268-c26a-439d-bb15-2a0dedfca6a3%7d&application=outlook&platform=win32&version=16.0.16026.20146&msoversion=16.0.16026.20002&sdx=fa000000002.2.0.1907.31003&sdx=fa000000005.1.0.1909.30011&sdx=fa000000006.1.0.1909.13002&sdx=fa000000008.1.0.1908.16006&sdx=fa000000009.1.0.1908.6002&sdx=fa000000016.1.0.1810.13001&sdx=fa000000029.1.0.1906.25001&sdx=fa000000033.1.0.1908.24001&sdx=wa104381125.1.0.1810.9001&processname=outlook.exe&audience=production&build=ship&architecture=x64&language=de-de&subscriptionlicense=false&perpetuallicense=2019&licensecategory=6&licensesku=professional2019retail&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7bc2353813-ffc0-4fb9-909b-0acbfad23df5%7d&labmachine=false
https://roaming.svc.cloud.microsoft/rs/roamingsoapservice.svc
https://messaging.lifecycle.office.com/getcustommessage16?app=6&ui=de-de&src=bizbar&messagetype=bizbar&hwid=04111-083-043729&ver=16.0.16026&lc=de-de&platform=10%3a0%3a19045%3a2%3a0%3a0%3a256%3a1%3a&productid=%7b1717c1e0-47d3-4899-a6d3-1022db7415e0%7d%3a00411-10830-43729-aa720%3aoffice%2019%2c%20office19professional2019r_retail%20edition&clientsessionid=%7bc2353813-ffc0-4fb9-909b-0acbfad23df5%7d&datapropertybag=%7b%22audience%22%3a%22production%22%2c%22audiencegroup%22%3a%22production%22%2c%22audiencechannel%22%3a%22cc%22%2c%22flight%22%3a%22ofsh6c2b1tla1a31%2cofcrui4yvdulbf31%2cofhpex3jznepoo31%22%7d
https://editor.svc.cloud.microsoft/nleditor/cloudsuggest/v1
https://self.events.data.microsoft.com/onecollector/1.0/
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.s2bconstruction.ca/t4ji/?ea7=icxsyu_ztvo_o4n1&p39=rbew22hv3hoz58ioujuoonultc2skciw8iyruuefxmqqspateixazv1r1mhy5j8utc641ynxych5gmh++krkb+cta38fnnf04pm+yjrhirv2p7ziifwiurhile1xvy5amtrh+6w=
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is FormBook malware?

FormBook stealer is an infostealer‍ trojan available as a malware-as-service. This malware is often used by attackers with low technical literacy and little programming knowledge. FormBook can be used to steal various information from infected machines.

Despite how easy it is to set up and use, the malware has advanced stealing and evasion functions including the ability to pull stored and recorded user input. In addition, the FormBook stealer is capable of searching for, viewing, and interacting with files, and taking screenshots. Even though the stealing capability of this virus can be considered somewhat average, its ease of operation, the injection schema, and a set of effective measures that the malware takes to avoid detection by antivirus software made FormBook a popular virus in the hacker community and, unfortunately, its popularity is only continuing to rise in 2019.

General description of the FormBook stealer

Written in C and x86 assembly language, FormBook is sold as a PHP control panel and can be purchased on highly accessible online forums for merely 30 dollars.

Uniquely, unlike the majority of existing viruses that exploit the latest vulnerabilities or zero-days, FormBook can inject into processes and set up function hooks utilizing already known issues. Hence the claim made by the makers, that the virus will work flawlessly regardless of the Windows version.

Together with its stealer functionality and evasion techniques, the virus knows how to execute instructions from a control server that includes starting new processes, their injection, and rebooting the victim’s PC. What’s more, the virus is able to record Windows’ ntdll.dll module into memory and call it directly, which makes API monitoring and user-mode hooking almost insufficient.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

FormBook malware analysis

A video simulation recorded on the ANY.RUN interactive malware analysis service allows us to take an in-depth look at the behavior of this clever virus and other malware such as Dridex and Lokibot with their elaborate anti-evasion techniques.
formbook execution process graph

Figure 1: Processes created by FormBook during execution as shown by ANY.RUN simulation

  • As shown by the ANY.RUN simulation, firstly the virus established connection to the CnC server;
  • After this, a malicious executable file, in this analysis's case pretending to be a .png is being dropped or overwritten and executed;
  • Then, FormBook proceeds to steal the personal data and change the autorun value in the registry. Also, the virus loads DLL from Mozilla Firefox creates files in the user directory, and starts CMD.EXE to set up persistence and later begin process injection;
  • Finally, injected Firefox.exe is executed for logging keystrokes, stealing clipboard data, and extracting authentication information from browser HTTP sessions.

Distribution of the FormBook stealer

According to FormBook analysis, malware is usually distributed via email campaigns that utilized a wide array of infecting mechanisms and can contain a number of various file attachments. Among the most commonly observed attachments are either PDFs, DOC or EXE, or ZIP, RAR, ACE, and ISO files.

Campaigns in which the virus is distributed through files with PDF extensions are known to utilize shipping-related themes and usually include a download link that points at the malicious code instead of the actual virus. DOC and EXE campaigns utilize macros to install and run the virus. Often, the virus is retrieved as a .PDF file in such a case. Finally, archive campaigns are considered to be the most common attack vector for this virus and usually revolve around a business-related theme, such as a payment order. In the case of this attack vector, attachments either contain a link to the FormBook stealer EXE file or install and run the virus on victims' PCs directly.

In 2020 Formbook has become quite popular as it used Covid-themed emails for decoys with subject headings such as “Government Response to Coronavirus Covid-19”.

FormBook execution process

Sandbox simulation performed on the ANY.RUN interactive malware hunting service allows us to detect and investigate the behavior of FormBook in a lot of detail.
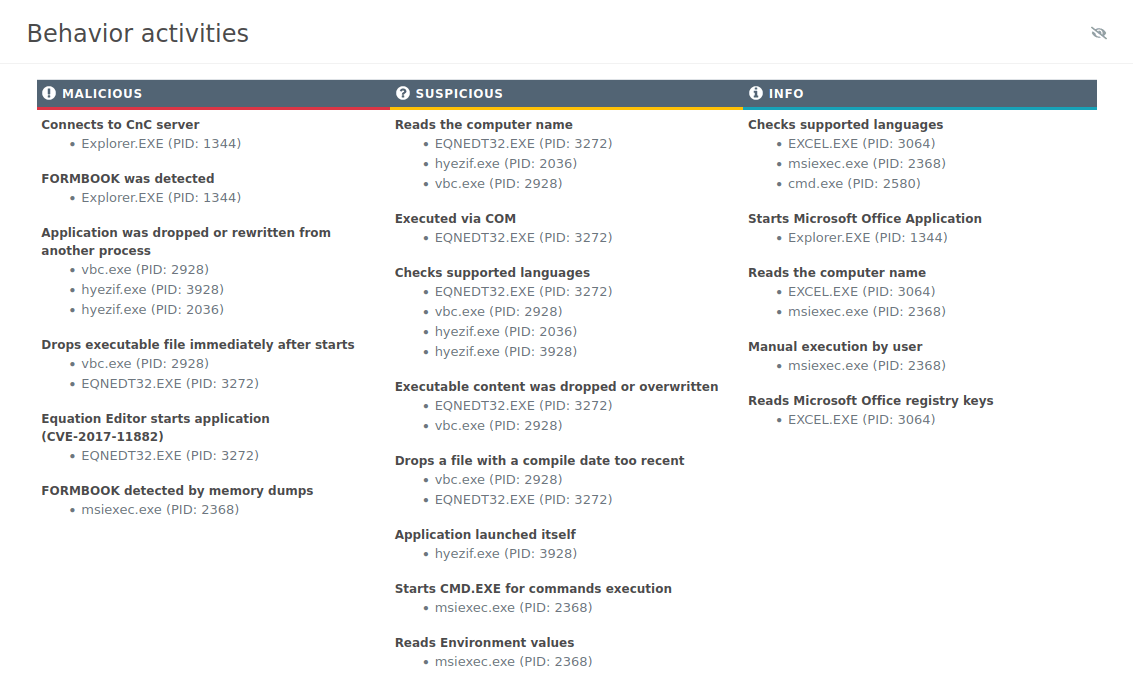
text report of the formbook malware analysis

Figure 2: A text report generated by ANY.RUN

After downloading the malicious file the only thing needed to start the contamination is for the file to be opened. In a case when Microsoft Office file (doc, xls, rtf) is used as an infection source, after it is opened the malware exploits the CVE-2017-11882 vulnerability, thus Microsoft Office Equation Editor proceeds to download a malicious executable file and run it.

After infecting the victim's PC, the virus copies and renames itself into a directory that differs based on the privileges of the user. If an admin account is used, the virus installs itself in either %ProgramFiles% or %CommonProgramFiles%. On the other hand, if the privileges are not elevated, then the virus will copy itself into %TEMP% or %APPDATA.

Also, Formbook trojan changes the autorun value in the registry depending on is it was running with normal or elevated privileges. Next, the malware copies itself into a directory it proceeds to check if it’s being run on a virtual machine or analyzed, evaluating the best anti-evasion option that can be utilized in a particular situation. Meanwhile, the virus will try to evaluate the USERNAME environment variable to find out if it’s launched in simulation, while also checking for the presence of debuggers. It should be noted that the malware uses particularly clever techniques while performing an analysis, for example, all shared strings such as command server names are decoded only briefly if they are absolutely required, which makes FormBook highly elusive. In the next step, the virus uses the same injection method to an active explorer.exe process which is only employed as a non-permanent staging ground.

The virus occasionally performs injections into web browser processes and explorer.exe. After injecting into the process, the virus chooses a random application from a static list. Then, the virus proceeds to run the chosen application in suspended mode and copy itself in the address space of the suspended process, thus mimicking a genuine Microsoft process. Next, the virus exits the original process which leaves FormBook's dead code in explorer.exe as a result. From this stage, new FormBook processes can inject targeted applications like web browser processes, which in the case of this particular ANY.RUN simulation is Firefox.

Depending on the objective process, the virus can establish various function hooks. Being run from inside the context of an already generated process, the virus starts to go through every currently active process, trying to identify targeted programs. As soon as a target is found, FormBook will inject itself into it and install a particular set of API hooks, that are based on the target program. The data is then saved in files in the %APPDATA% directory until it is sent to the C&C server. Pay attention to this function to detect malware.

How to avoid infection by FormBook?

The best counteraction technique is to exhibit caution when receiving emails with attachments from unknown senders. Attackers usually use social engineering to trick victims into downloading and opening infected files.

Deleting any suspicious emails from the inbox is a good way to stay safe. If the infection is already detected, a good practice is to carry out an analysis of all devices connected to the network for established CnC or potentially malicious URL connections. Once a suspicious email is received, perimeter settings can be adjusted to block all related emails in the future. Finally, if an infected file is already downloaded, the host should be quarantined until the threat is completely mitigated.

How to detect Formbook using ANY.RUN?

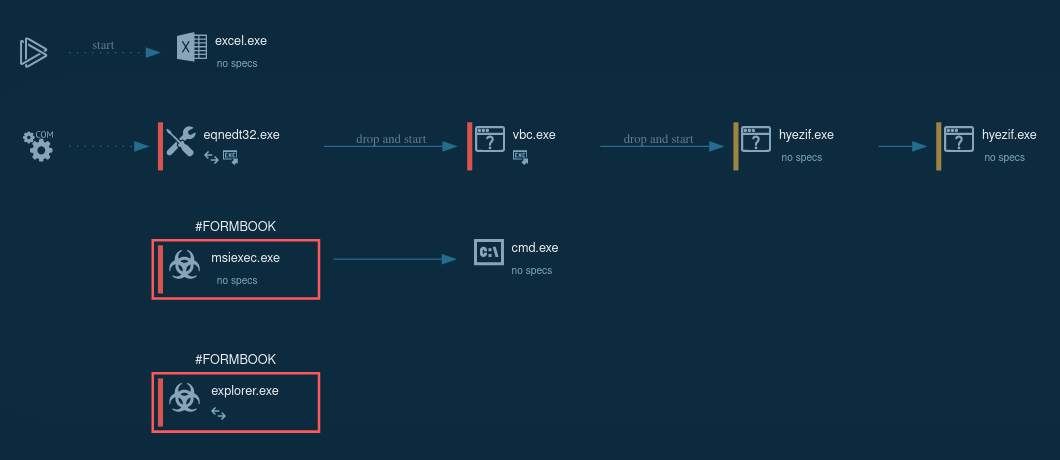
Formbook trojan usually injects into explorer.exe and another processes from the list, such as firefox.exe and msiexec.exe. Knowing this malware's function you can take a look at the process tree after a while during execution and easily determine either the sample is Formbook or not.
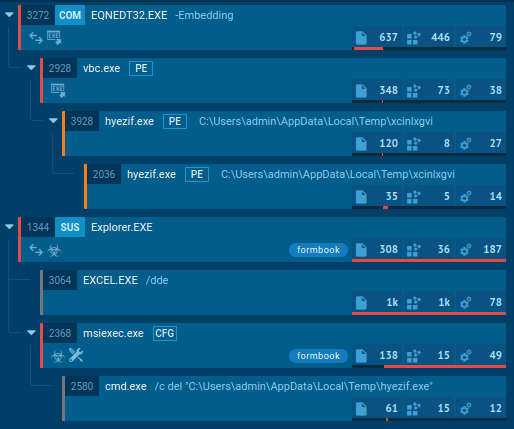
formbook execution process tree Figure 3: A tree of processes created by Formbook during its execution

Conclusion

Thanks to extreme ease of use and low cost, FormBook is gaining traction in the criminal community. Not only is the virus's functionality freely accessible for download on open hacker forums and easy to set up without any programming knowledge, but it also comes equipped with some highly advanced anti-evasion techniques, that make detecting it with anti-virus software ultra-difficult. ANY.RUN interactive malware hunting service enables to study FormBook in detail from a secure environment and implement cybersecurity measures accordingly.
HAVE A LOOK AT

BTMOB RAT screenshot
BTMOB RAT
btmob
BTMOB RAT is a remote access Trojan (RAT) designed to give attackers full control over infected devices. It targets Windows and Android endpoints. Its modular structure allows operators to tailor capabilities, making it suitable for espionage, credential theft, financial fraud, and establishing long-term footholds in corporate networks.
Read More
Fog Ransomware screenshot
Fog is a ransomware strain that locks and steals sensitive information both on Windows and Linux endpoints. The medial ransom demand is $220,000. The medial payment is $100,000. First spotted in the spring of 2024, it was used to attack educational organizations in the USA, later expanding on other sectors and countries. Main distribution method — compromised VPN credentials.
Read More
Sneaky 2FA screenshot
Sneaky 2FA
sneaky2fa
Sneaky 2FA is an Adversary-in-the-Middle (AiTM) phishing kit targeting Microsoft 365 accounts. Distributed as a Phishing-as-a-Service (PhaaS) through a Telegram bot, this malware bypasses two-factor authentication (2FA) to steal credentials and session cookies, posing a significant threat to individuals and organizations.
Read More
Remus Stealer screenshot
Remus Stealer is a sophisticated 64-bit information stealer operating under a Malware-as-a-Service (MaaS) model. Identified as a direct evolution of the infamous Lumma Stealer, Remus specializes in harvesting credentials, cookies, and cryptocurrency wallets while utilizing blockchain technology for command-and-control (C2) resilience.
Read More
MetaStealer screenshot
MetaStealer
metastealer
MetaStealer is an info-stealing malware primarily targeting sensitive data like login credentials, payment details, and browser history. It typically infects systems via phishing emails or malicious downloads and can exfiltrate data to a command and control (C2) server. MetaStealer is known for its stealthy techniques, including evasion and persistence mechanisms, which make it difficult to detect. This malware has been actively used in various cyberattacks, particularly for financial theft and credential harvesting from individuals and organizations.
Read More
PhantomEnigma screenshot
PhantomEnigma
phantomenigma
PhantomEnigma (also known as Operation Phantom Enigma) is a sophisticated crimeware operation primarily targeting banking organizations and the public sector in Brazil. The campaign is characterized by its strategic abuse of compromised legitimate infrastructure, specifically Brazilian government (.gov.br) portals and municipal websites, to host and distribute malicious payloads.
Read More