Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Arechclient2

87
Global rank
107 infographic chevron month
Month rank
93 infographic chevron week
Week rank

The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.

RAT
Type
Unknown
Origin
1 November, 2019
First seen
7 October, 2026
Last seen
Also known as
SectopRAT

How to analyze Arechclient2 with ANY.RUN

RAT
Type
Unknown
Origin
1 November, 2019
First seen
7 October, 2026
Last seen

IOCs

IP addresses
48.209.133.15
135.232.92.97
40.126.31.130
74.179.77.204
172.211.123.248
204.79.197.203
23.11.41.157
188.114.97.3
178.104.144.200
23.207.210.132
23.216.77.34
48.192.1.65
23.3.89.97
23.59.18.102
135.233.95.144
48.209.6.48
23.207.210.139
95.100.158.114
40.126.32.134
34.254.75.158
Hashes
a2ca52e34b6138624ac2dd20349cde28482143b837db40a7f0fbda023077c26a
7acd65117ee6ac8bd996562c51b078c6dfa77e83125d948e6ca6418602cbe43c
f7b24f2eb3d5eb0550527490395d2f61c3d2fe74bb9cb345197dad81b58b5fed
fbcfe23a2ecb82b7100c50811691dde0a33aa3da8d176be9882a9db485dc0f2d
0f1bad70c7bd1e0a69562853ec529355462fcd0423263a3d39d6d0d70b780443
1fe8f6113488865c546d2faa55b21482662ce4be19d4f505eeefa09bc3131489
c007da2e5fd780008f28336940b427c3bfd509c72a40bfb7759592149ff3606e
5d69a932a077fee044b193c28e84564143f5c7e51079ab48e88fef74ab0b77b7
1884d6f5cf148a1be91d1b94d5bafd842eb95e68f9d8e40e7c5c954a3252bb01
dafd7f458025ad4ea6c64828e12fe63655397bb2aca648c906dfdbeb55abfac5
db0df14a9b2b7d568ebc94061b87e76fa4b50fb0ff9c9c3c5dd0de253a26ee43
1dd327a27edf466d4a401466212e90bd8ede524fe1cf53def8892c34d0d1c9a7
2c61b864e35770fef1e8e5f3f79d98a3b5849c3692a2358128611eabdc3aad92
2e7e10e9ea8577210cbb326dc27a54d5724d446aeeb8d204511e56b6874b6927
889e8deee31e0bf4e6759c734996c05ef622c68edcc382c5f97f43cdb41f58f5
c2c1c74d36570091bcf1f0b5eb80dc6a2d971ba31ca9c161c3f86bdbfe9367be
bbd76fd1c5f9e400b7b3ab30b3c5b27722802b11b3e41fc282783c5f4161c26e
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
ecc8d7540d26e3c2c43589c761e94638fc5096af874d7df216e833b9599c673a
Domains
slscr.update.microsoft.com
ecs.office.com
fe3cr.delivery.mp.microsoft.com
google.com
ocsp.digicert.com
client.wns.windows.com
www.bing.com
nexusrules.officeapps.live.com
www.microsoft.com
oneocsp.microsoft.com
crl.microsoft.com
login.live.com
activation-v2.sls.microsoft.com
microsoft.com
bulpscfpjirjqlzyga.bulpscfpjirjqlzyga
self.events.data.microsoft.com
settings-win.data.microsoft.com
upstream.foxtrail.vip
th.bing.com
bsc-dataseed1.binance.org
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
https://upstream.foxtrail.vip/fabrics.a3x
https://upstream.foxtrail.vip/autoit3.exe
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://login.live.com/ppsecure/deviceaddcredential.srf
https://login.live.com/rst2.srf
https://bsc-dataseed1.binance.org/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://98.142.252.140:9000/wmglb
http://98.142.252.140:9000/wbinjget?q=5d68c0521e7bb9dfbf808c55051f606f
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 3822
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 5883
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 8789
comments 0

What is Arechclient2 malware?

Arechclient2 is a .NET Remote Access Trojan (RAT) that was first observed in 2019. It is also widely known under the name SectopRAT. This malware is designed to steal sensitive data from browsers and cryptocurrency wallets, posing a significant threat to users' personal and financial information.

The distribution of Arechclient2 is typically carried out through malicious links, executable file uploads, and fake application updates. In some cases, it may be distributed as an LNK file or as an ISO file containing a malicious executable, making it difficult for users to detect and avoid infection.
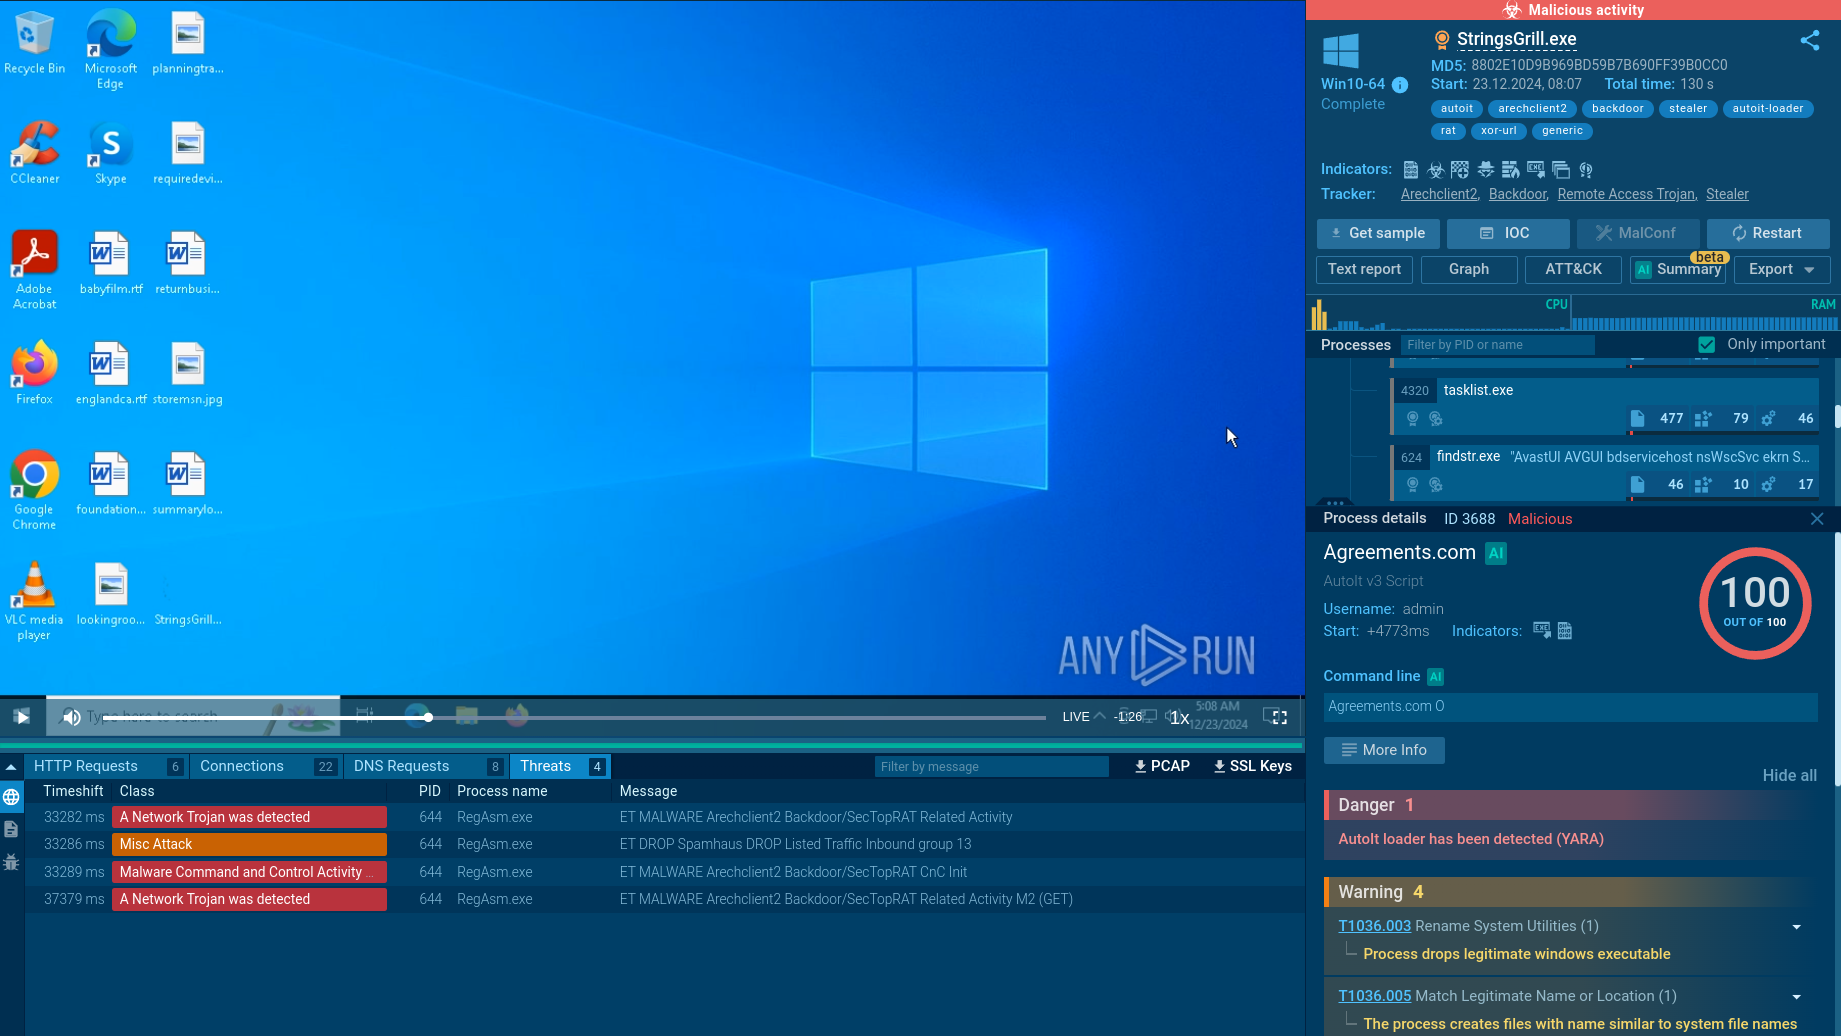
Arechclient2 analyzed inside ANY.RUN sandbox Arechclient2 analyzed inside ANY.RUN sandbox

Analysis in ANY.RUN’s interactive malware sandbox shows that ArechClient2 makes considerable use of scripts and process injection to facilitate infection.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Arechclient2 malware technical details

Some of the primary capabilities of the Arechclient2 malware include:

  • Collection of sensitive information, including browser credentials.
  • Use of Base64 encoding for code obfuscation.
  • Temporary pausing of activities for evasion of automated security tools.
  • Adjustment of Windows Defender settings for detection evasion.
  • Employment of code injection for manipulation of legitimate processes.
  • Maintenance of persistence through script execution on startup.
  • Exchange of encrypted and plain text data with its command and control (C2) server.

Arechclient2 execution process

Let’s take a closer look at the stages of Arechclient2 infection by analyzing its sample inside ANY.RUN’s cloud sandbox for malware analysis.
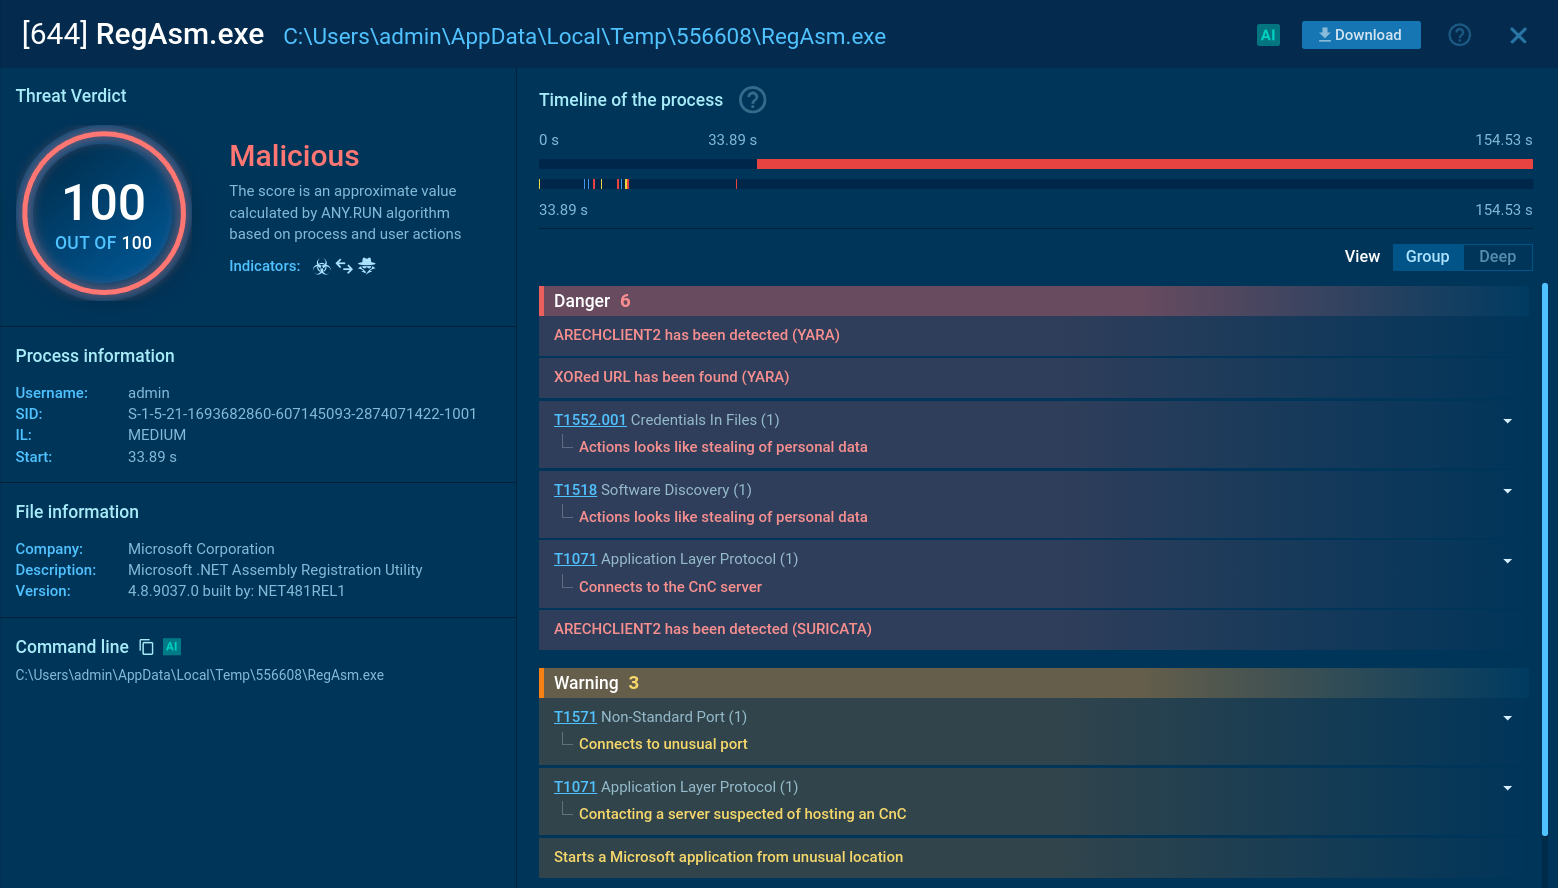
Arechclient2 malicious process inside ANY.RUN sandbox ANY.RUN identifies malicious processes and lists all the actions performed by the malware

The process starts with the delivery of a malicious first-stage payload, which can vary between campaigns. It may be distributed as an LNK file or as an ISO file containing a malicious executable. These files are often spread through unknown initial attack vectors, likely involving social engineering or phishing tactics that trick users into executing them.

When the LNK file is double-clicked, it starts the system utility forfiles.exe to achieve indirect command execution by running PowerShell. An ISO file is mounted like a CD, and the executable may run automatically, initiating the infection process. Upon execution, the payload may extract files into a newly created directory within the victim’s temporary files. This extraction process also initiates multiple child processes crucial to the RAT’s functionality. The execution chain often uses AutoIT, further complicating detection efforts.
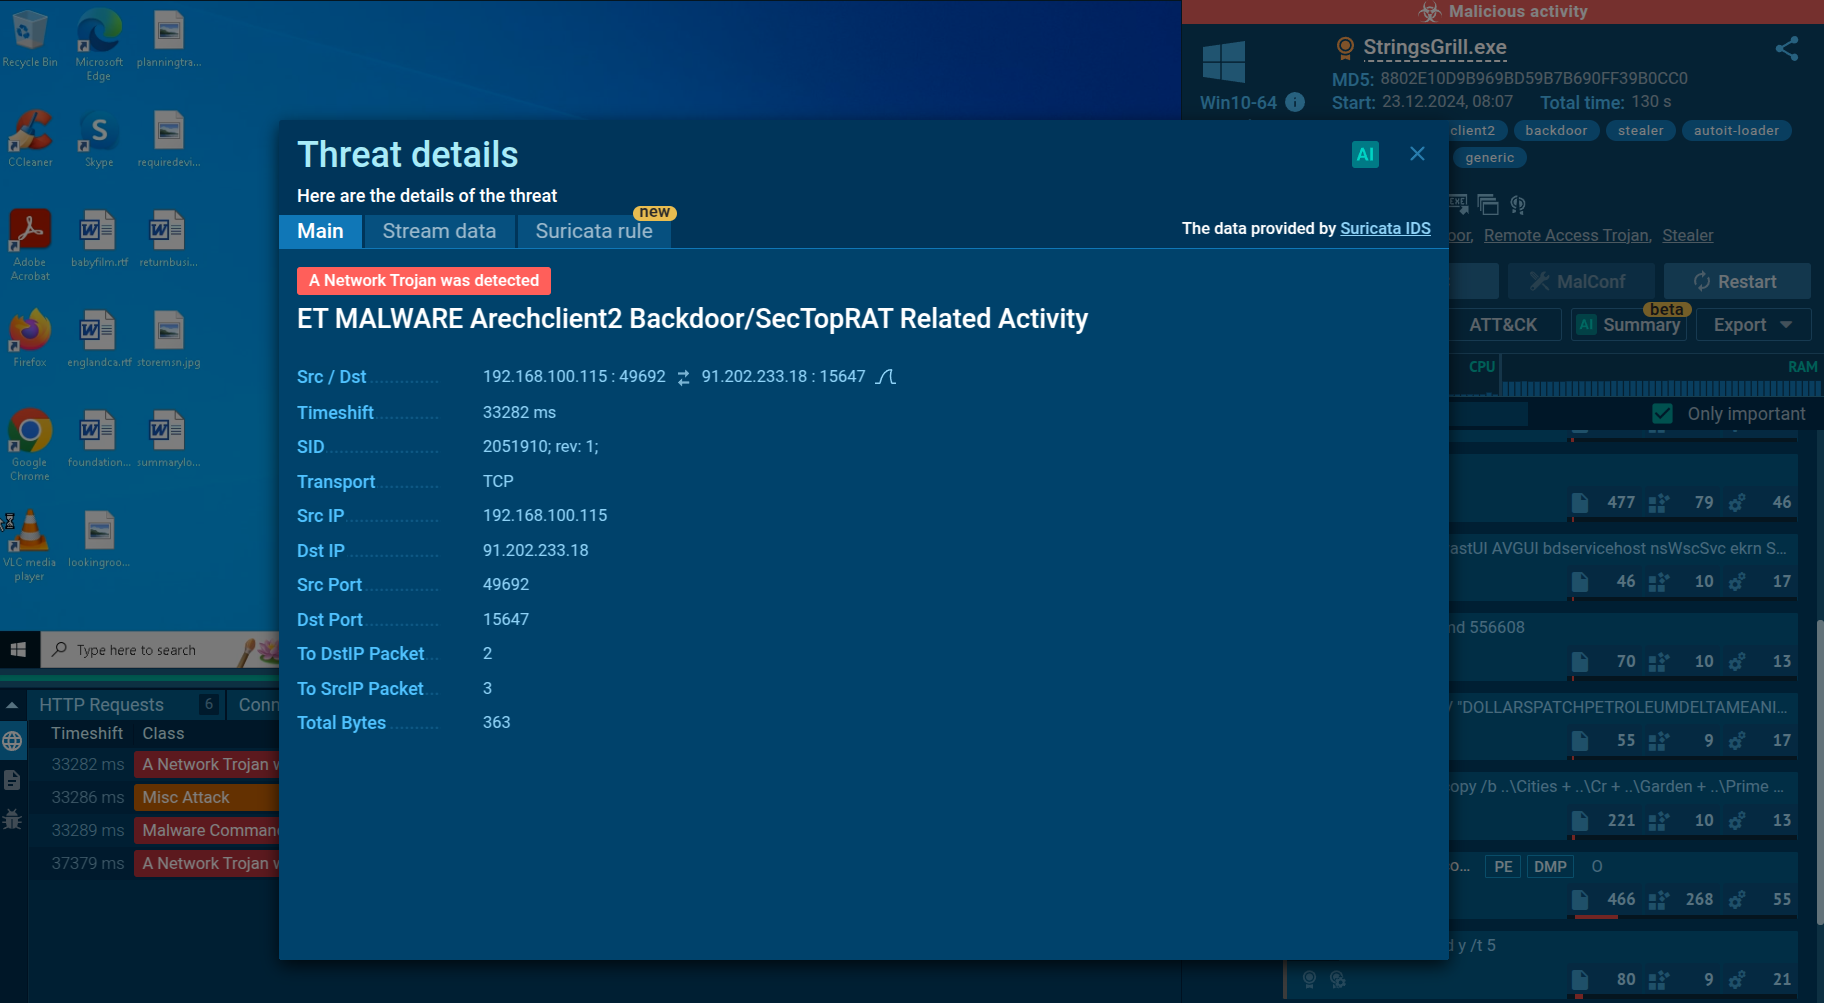
Arechclient2 Suricata analysis inside ANY.RUN sandbox ANY.RUN uses Suricata IDS to spot malicious network activities

The malware injects its payload into legitimate processes (e.g., InstallUtil.exe) using a function that facilitates injection while avoiding antivirus hooks by copying necessary files from system directories. This step is critical for maintaining stealth and ensuring continued control over the infected machine. Arechclient2 connects to its command and control (C2) server on port 15647 to receive commands. The communication includes encrypted data, which can switch to plaintext if encryption is disabled during interception. This allows attackers to issue commands remotely, manipulate settings, or extract sensitive information from the victim’s system.
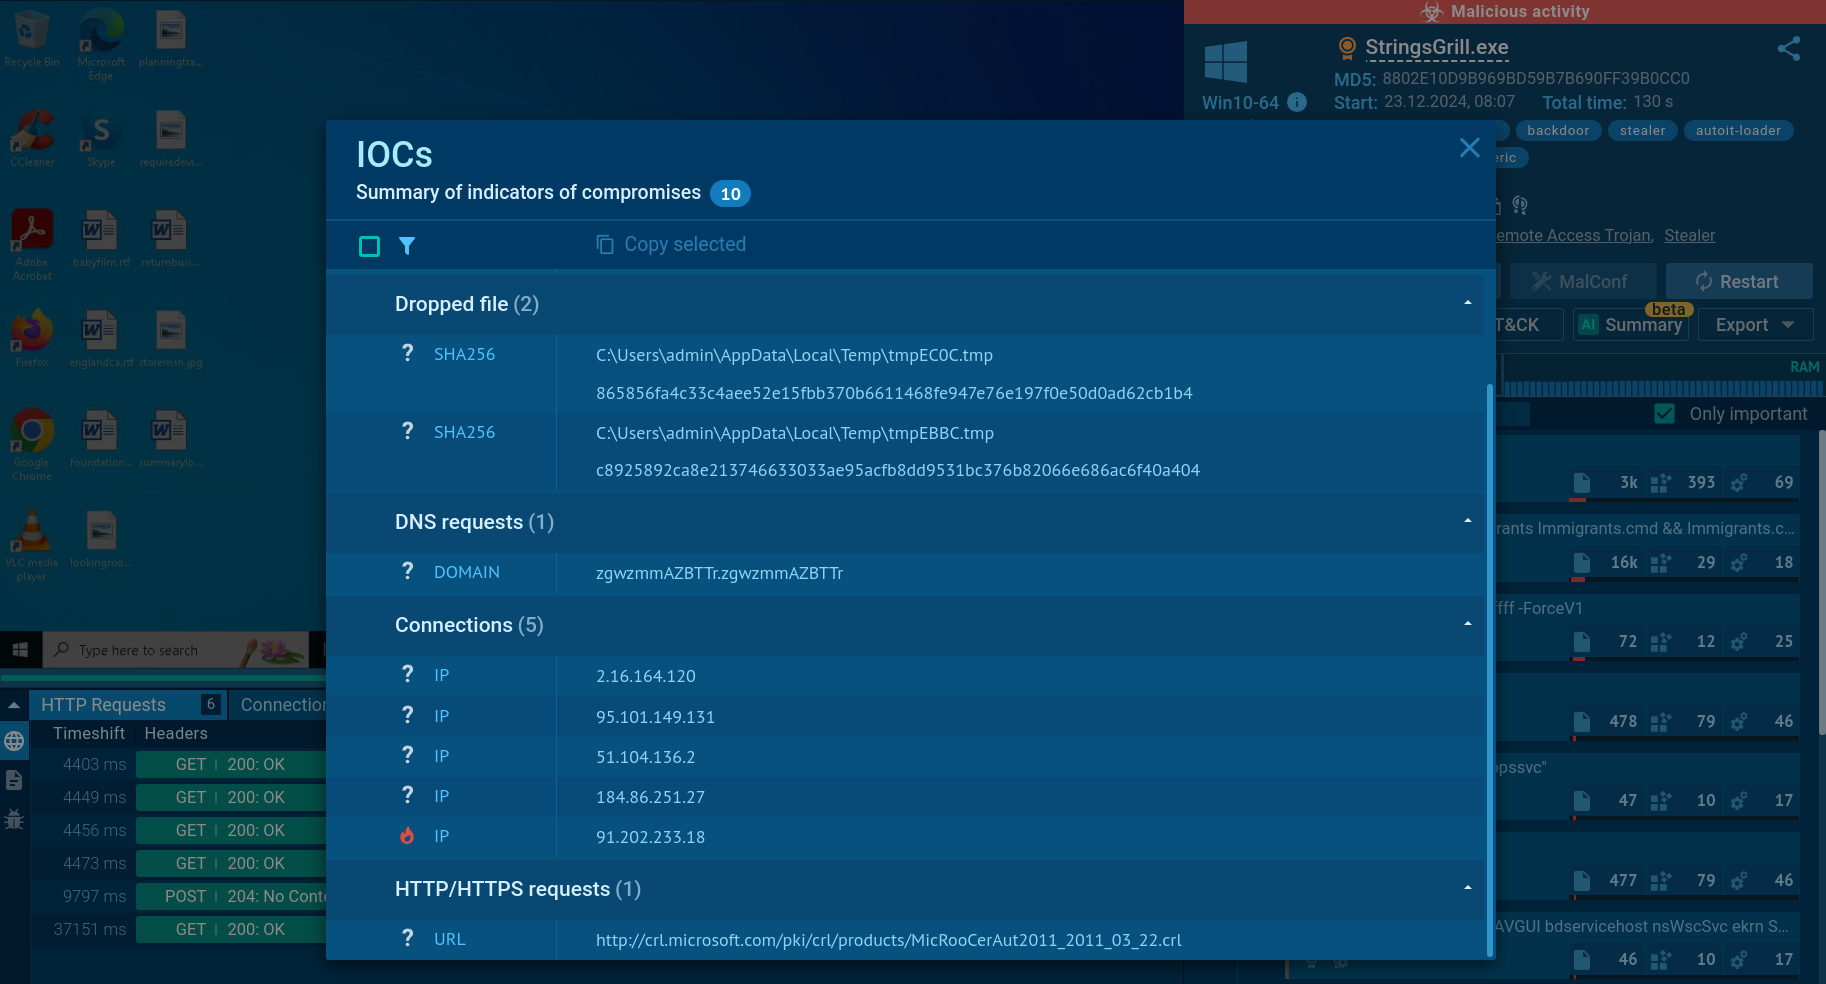
Arechclient2 IOCs inside ANY.RUN sandbox After analysis in ANY.RUN, you can collect a detailed threat report and IOCs

The RAT can extensively profile victim systems, stealing sensitive information such as browser data and cryptocurrency wallet details. It can also launch hidden sessions to monitor user activity without detection.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Arechclient2 distribution methods

ArechClient2 uses various methods to trick users into clicking on harmful links that look legitimate.

Phishing techniques are employed to convince users to open files containing malicious content, which starts the infection process.

One common distribution method is to disguise the malware as updates for popular applications like Brave Browser, TOR, Signal, and Telegram.

By appearing as genuine updates, the malware takes advantage of users' trust in these applications to increase the chances of infection.

Gathering Threat Intelligence on Arechclient2 Malware

To obtain up-to-date intelligence on ArechClient2, utilize Threat Intelligence Lookup from ANY.RUN. This service grants access to a vast database containing Indicators of Compromise (IOCs), Indicators of Attack (IOAs), and Indicators of Behavior (IOBs) from millions of malware analysis sessions performed within the ANY.RUN sandbox. With over 40 customizable search parameters, users can retrieve data on threats, including IPs, domains, file names, and process artifacts associated with ArechClient2.
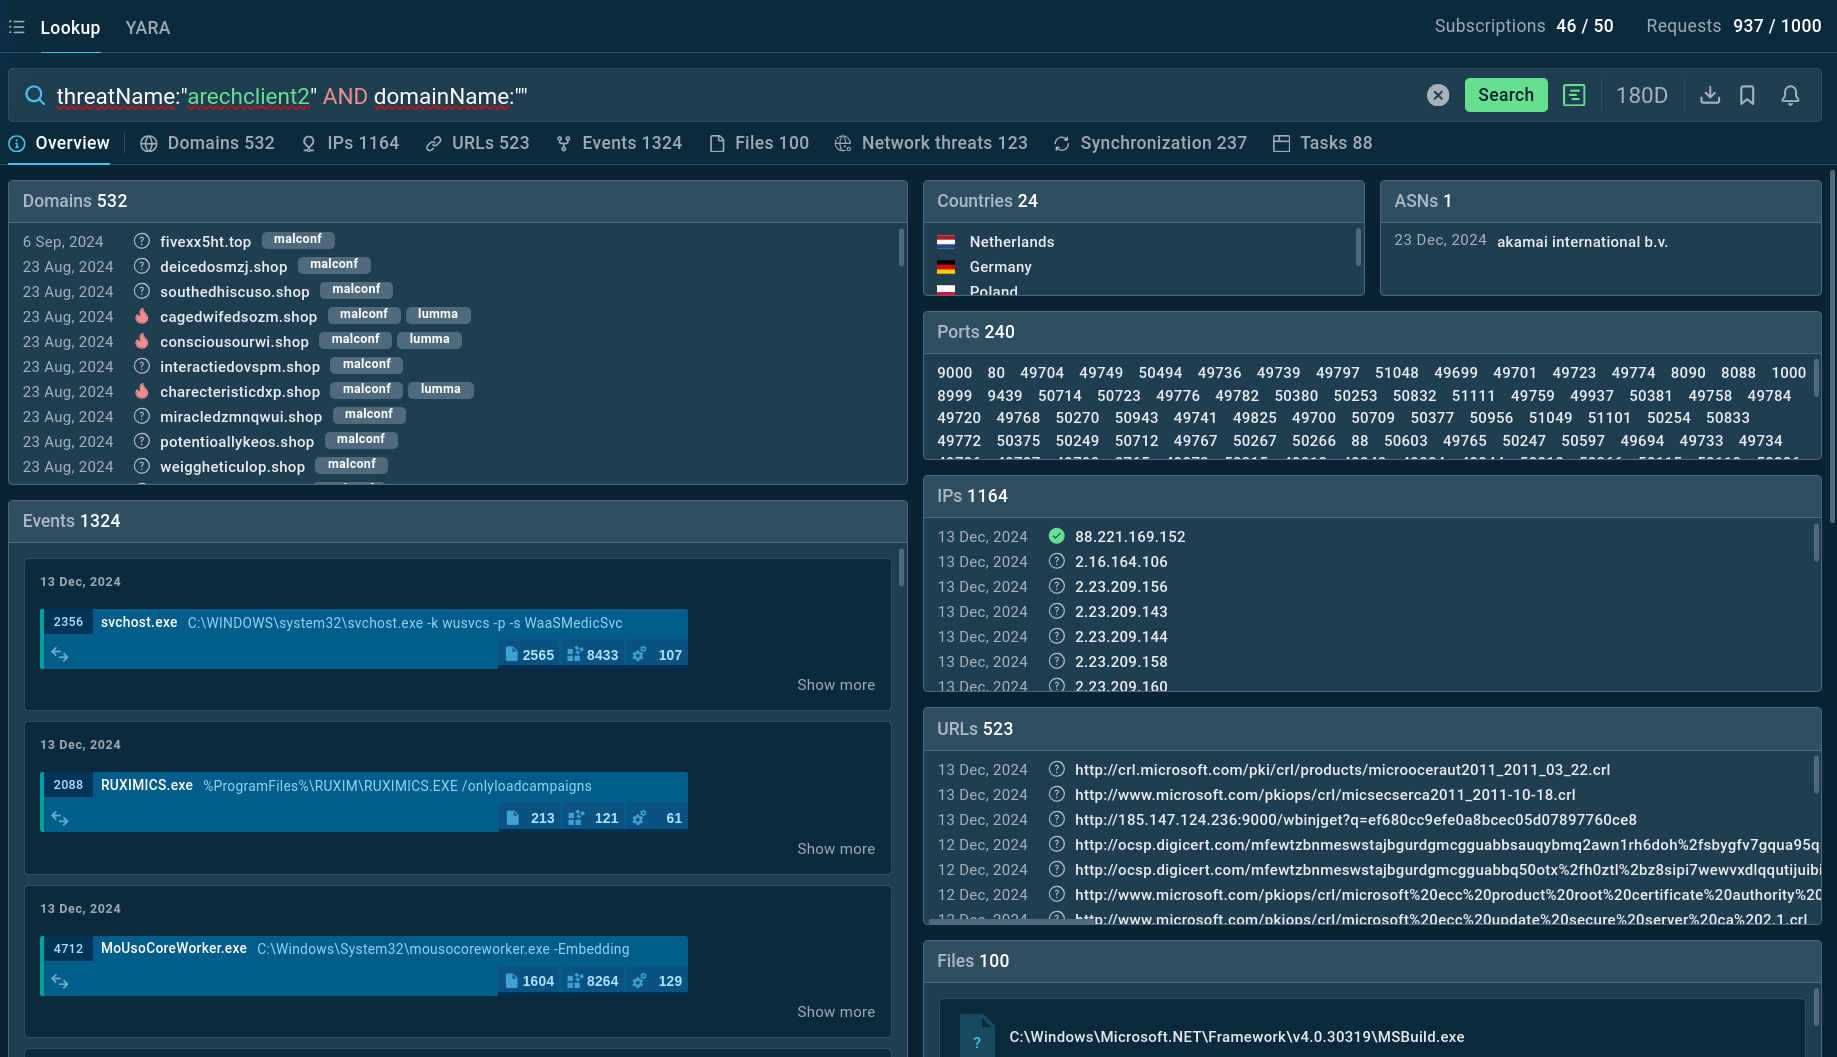
Arechclient2 results inside ANY.RUN's TI Lookup TI Lookup helps you enrich your investigations with additional threat context

For instance, to gather information on ArechClient2, you can search using its threat name or related artifacts. Inputting a query like threatName:"arechclient2" AND domainName:"" will produce a list of files, events, domain names, and other data extracted from malware samples, along with sandbox sessions that can be examined in detail to gain in-depth understanding of this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Arechclient2, also known as SectopRAT, is a sophisticated malware able to evade detection and circumvent security systems. Its activity may lead to direct financial losses.

Whether you would like to research Arechclient2 in detail, or just check some suspicious link or file, use ANY.RUN’s Interactive Sandbox. It knows how to withstand VM-detection techniques and is integrated with Threat Intelligence Lookup to provide you with the data for proactive protection measures.

Sign up for a free ANY.RUN account to analyze cyber threats with no limit →
HAVE A LOOK AT

Mallox screenshot
Mallox
mallox
Mallox is a ransomware strain that emerged in 2021, known for its ability to encrypt files and target database servers using vulnerabilities like RDP. Often distributed through phishing campaigns and exploiting exposed SQL servers, it locks victims' data and demands a ransom. Mallox operates as a Ransomware-as-a-Service (RaaS), making it accessible to affiliates who use it to conduct attacks.
Read More
PhantomEnigma screenshot
PhantomEnigma
phantomenigma
PhantomEnigma (also known as Operation Phantom Enigma) is a sophisticated crimeware operation primarily targeting banking organizations and the public sector in Brazil. The campaign is characterized by its strategic abuse of compromised legitimate infrastructure, specifically Brazilian government (.gov.br) portals and municipal websites, to host and distribute malicious payloads.
Read More
MetaStealer screenshot
MetaStealer
metastealer
MetaStealer is an info-stealing malware primarily targeting sensitive data like login credentials, payment details, and browser history. It typically infects systems via phishing emails or malicious downloads and can exfiltrate data to a command and control (C2) server. MetaStealer is known for its stealthy techniques, including evasion and persistence mechanisms, which make it difficult to detect. This malware has been actively used in various cyberattacks, particularly for financial theft and credential harvesting from individuals and organizations.
Read More
Remus Stealer screenshot
Remus Stealer is a sophisticated 64-bit information stealer operating under a Malware-as-a-Service (MaaS) model. Identified as a direct evolution of the infamous Lumma Stealer, Remus specializes in harvesting credentials, cookies, and cryptocurrency wallets while utilizing blockchain technology for command-and-control (C2) resilience.
Read More
Sneaky 2FA screenshot
Sneaky 2FA
sneaky2fa
Sneaky 2FA is an Adversary-in-the-Middle (AiTM) phishing kit targeting Microsoft 365 accounts. Distributed as a Phishing-as-a-Service (PhaaS) through a Telegram bot, this malware bypasses two-factor authentication (2FA) to steal credentials and session cookies, posing a significant threat to individuals and organizations.
Read More
MicroStealer screenshot
MicroStealer
microstealer
MicroStealer is a rapidly emerging infostealer first prominently observed in late 2025. It specializes in stealing browser credentials, active session data, screenshots, cryptocurrency wallets, and system information. It spreads quickly with low detection rates thanks to a sophisticated multi-stage delivery chain and exfiltrates data via Discord webhooks and attacker-controlled servers.
Read More