Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
139
Global rank
114 infographic chevron month
Month rank
138 infographic chevron week
Week rank

Phobos is a ransomware that locks or encrypts files to demand a ransom. It uses AES encryption with different extensions, which leaves no chance to recover the infected files.

Ransomware
Type
Unknown
Origin
1 October, 2017
First seen
5 October, 2026
Last seen

How to analyze Phobos with ANY.RUN

Type
Unknown
Origin
1 October, 2017
First seen
5 October, 2026
Last seen

IOCs

IP addresses
74.178.76.128
52.123.129.14
2.16.204.143
172.211.123.248
131.253.33.203
23.11.41.157
2.16.164.66
23.59.18.102
57.153.246.3
2.21.239.135
74.178.240.51
20.190.159.73
20.184.175.6
204.79.197.203
2.20.142.160
20.190.160.64
48.192.1.65
172.211.123.250
23.48.23.172
48.209.6.48
Hashes
cd2c00ce027687ce4a8bdc967f26a8ab82f651c9becd703658ba282ec49702bd
db423c828a9abdaf9d3491f1ee6f5e6548e0fcea712988ac9cf7f33f1b2531d4
6ef5127702ad14aea69b02f9f63ad275fe38c7d34a260188e4fcc7d4a38fb2fc
1202d17bc8f69abd93af854a62f19c21b52e81dba9de9ac21fdedbaa1d5cd08d
43f846c12c24a078ebe33f71e8ea3b4f75107aeb275e2c3cd9dc61617c9757fc
951c2c2719695e41f0cb9bc1bf45052aa5d08ce5c7013d70796508b1f648d152
31c9a209865ccc83da6cff63541ac8c0fa6b7cbe22e2770e026fb4226981cff7
f8a6bfefce87f910cf29ce33c3c4da85930bed6e3610123d6e5d1cc09703a4eb
38e441c7d006fc27c87a9905779421a23c78dc2047039eb00f34fff7b0e3bcf3
784130d9cb5ce54158dc696f7665f9a26e386b662cc2a75a253f3e7774f19fe9
50c040404dfd35cbc41ba1adeab1cf7fa1ec86cc55cc9a7967be505b868bb481
fe81141e60dd6d470b39b53eb6bbe105b25bb52ecee15be827028e3647033244
4eae9fe4db27954f66fc8df16aa04f3a9a178bc15295486cd9936a385677b9af
ce186df39109fcfec4b6ebd82202e9c96370624861d7bdeb9fdfbbdbb1094b96
072a57893da340f7e7d493d61cbeec480753c1aebbd4318188f4a72892a2dc47
c38ab059b07510b99dde747f96f73a5d7be3e086faa208cce944fef70da68f84
64ace11933178f702081009fbd6a1b1191303d091fc73d8ee3ce32a51861b59d
e286852d9c23af268a401ff50af9ba14f219ee39bca59a623195fb1f43a16d23
4ae4a3bd92019cac4eb3415d5524bb0a109f75252d443b4cad942f5d797e33b9
3fe79e2e91fd15d2da96b835a3a6305f5de6515d33a69f898ef1a875e15120a1
Domains
ocsp.digicert.com
ecs.office.com
login.live.com
fe3cr.delivery.mp.microsoft.com
google.com
crl.microsoft.com
www.microsoft.com
settings-win.data.microsoft.com
oneocsp.microsoft.com
client.wns.windows.com
www.bing.com
th.bing.com
self.events.data.microsoft.com
slscr.update.microsoft.com
activation-v2.sls.microsoft.com
copilot.microsoft.com
api.edgeoffer.microsoft.com
edge.microsoft.com
example.com
edge-consumer-static.azureedge.net
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://ecs.office.com/config/v2/office/officeclicktorun/16.0.16026.20140/production/cc?&clientid=%7b48ba7fdf-353c-4fe5-8d8f-9e31911a3891%7d&application=officeclicktorun&platform=win32&version=16.0.16026.20140&msoversion=16.0.16026.20140&processname=officeclicktorun.exe&audience=production&build=ship&architecture=x64&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7b87bf6967-e8ad-4109-8d5a-f1b1113cb9eb%7d&labmachine=false
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceasmayxgarewr3pgr9svwmg%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbr0tbevyklx7a9ylold9hqmcwdxfgqu3pggslehmvkx8utfb6ncihnaqhycezmaaaaoqpopjdxrqzsaaaaaaa4%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbr0tbevyklx7a9ylold9hqmcwdxfgqu3pggslehmvkx8utfb6ncihnaqhycezmaaaale%2bvmfuqbvyaaaaaaaas%3d
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
https://self.events.data.microsoft.com/onecollector/1.0/
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
Last Seen at

Recent blog posts

post image
Fake AI Tools Put US Companies at Risk: Insid...
watchers 832
comments 0
post image
What's Really Attacking Your Industry? Insigh...
watchers 2482
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 10164
comments 0

What is Phobos Ransomware?

Phobos Ransomware encrypts data until a ransom is paid. 77% of Phobos attacks are successful according to the latest research. This malicious program was recorded in the wild for the first time in October 2017.

General description of Phobos Ransomware

Phobos ransomware appeared in 2017 in Dharma, also known as the CrySIS, family. A year later Phobos developed and spread rapidly. In 2019, it accounted for 8.9% of the submitted ransomware attacks. The First-quarter of 2020 showed that the Phobos strain was noted as one of the most common ransomware with 9.70% of submissions. It constantly gets updates and new versions.

The ransomware targets organizations all over the world. Phobos compromises RDP servers that are open or have weak security. Then cyber criminals send ransom notes, where the victim is asked to contact one of the emails to get the decryption key.

Phobos attackers exactly like Dharma ones can discuss ransom amounts depending on the company. The Ransom amount can reach 20,000 USD in Bitcoin. It is lower than usual ransomware demands because Phobos chooses small companies as victims. And sometimes cybercriminals don’t give up the decryption key even after the payment.

The malicious program uses encrypt data using AES and adds extensions to infected files such as .phobos, .phoenix, .actin, .help, .mamba and others. These files can be fully or partially encrypted.

Phobos is named after the Greek god of fear, but there is nothing divine about it. Criminals buy this malware in RaaS packages, so even without deep technical knowledge, they have an opportunity to design their own strain and organize an attack on the chosen victim.

Phobos malware analysis

The ANY.RUN malware hunting service features a video that displays the complete execution process of Phobos.
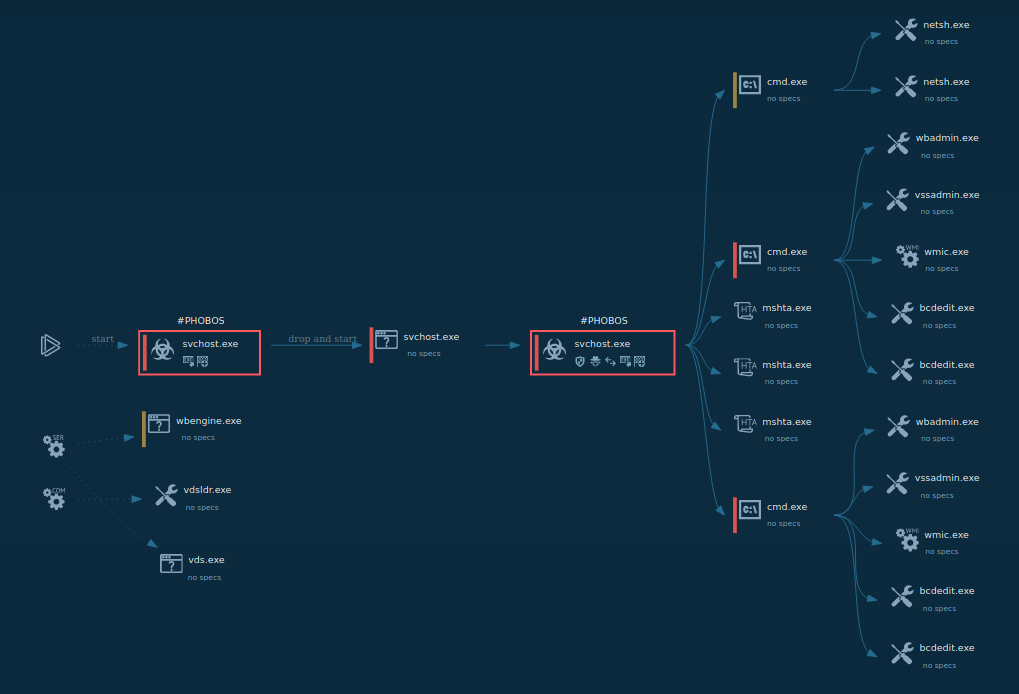
phobos ransomware process graph

Figure 1: Shows the graph of processes created by the ANY.RUN interactive malware analysis service
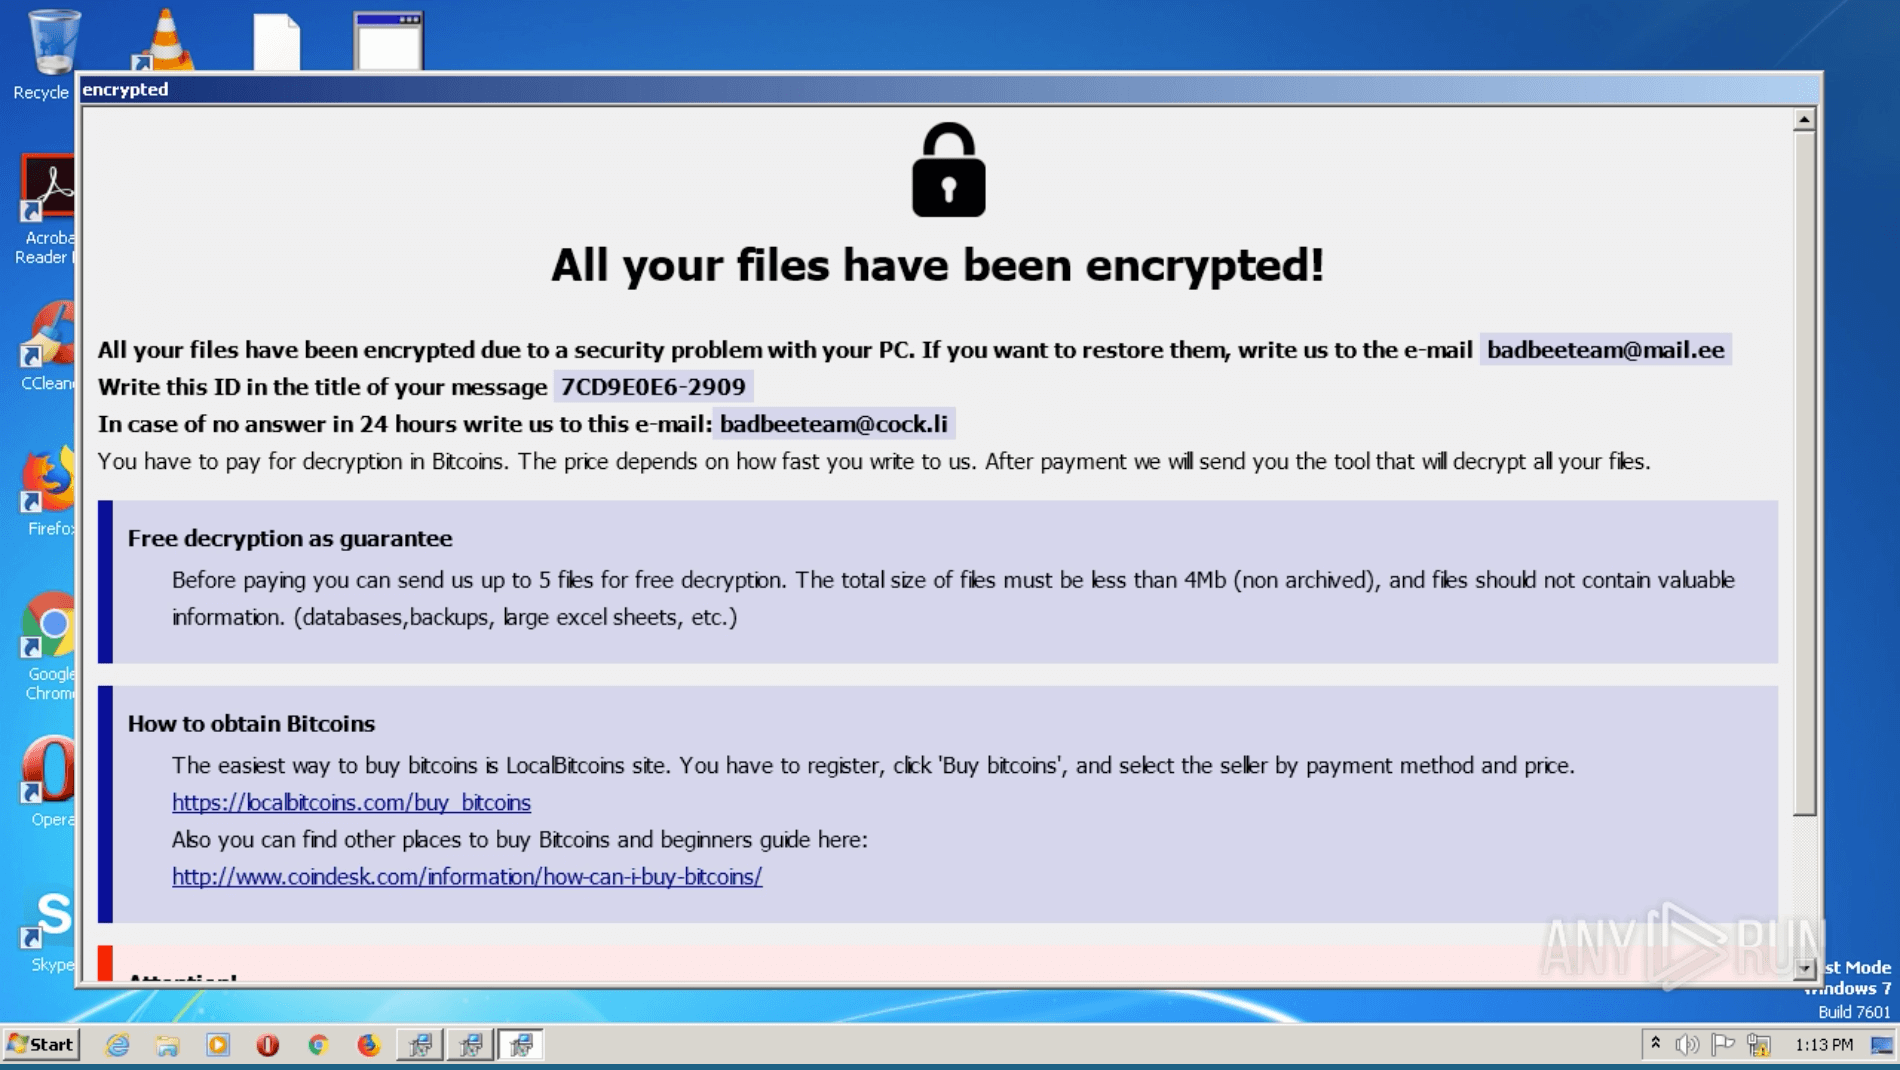
phobos ransom note

Figure 2: Phobos ransom note

Phobos Ransomware execution process

The execution process of the Phobos ransomware is relatively typical for this type of malware such as Troldesh. The executable file makes its way into an infected system and runs, then the main malicious activity begins. After the start of execution, the Ransomware deletes shadow copies. Interestingly though, as soon as it encrypts all targeted files, Phobos pops up a ransom note on the desktop, which is the ransomware executable file itself.

Phobos Ransomware distribution

Phobos has several ways to end up on your machine:

  • phishing emails with attachments
  • poorly secured RDP ports
  • fake updates
  • exploits
  • deceptive downloads
  • web injectors
  • repacked and infected installers

These distribution methods help attackers to steal victims’ information and encrypt the data by running Trojan or other malware. And a variety of the infected files is huge: documents, PDF and text files, databases, photos and videos, archives, etc. They can be located both in internal and external folders. Phobos gets rid of files’ shadow copies and backups.

Conclusion

Phobos is not a new type of ransomware, moreover, it has some similarities to Dharma. There is no need for criminals who use Phobos to be qualified specialists. Nevertheless, this ransomware always evolves, and its attacks are effective. It has a lot of ways to get into your device to get a ransom. That is why Phobos can be a serious threat to organizations.
HAVE A LOOK AT

Mallox screenshot
Mallox
mallox
Mallox is a ransomware strain that emerged in 2021, known for its ability to encrypt files and target database servers using vulnerabilities like RDP. Often distributed through phishing campaigns and exploiting exposed SQL servers, it locks victims' data and demands a ransom. Mallox operates as a Ransomware-as-a-Service (RaaS), making it accessible to affiliates who use it to conduct attacks.
Read More
Mirage2FA screenshot
Mirage2FA
mirage2fa
Mirage2FA is a Phishing-as-a-Service toolkit designed to compromise Microsoft 365 accounts and bypass conventional MFA through Adversary-in-the-Middle attacks. It uses malicious HTML, XHTML, and SVG files to deliver JavaScript loaders that connect victims to attacker-controlled phishing infrastructure. The toolkit relays authentication in real time, capturing credentials, 2FA codes, and authenticated session cookies. It also uses browser fingerprinting, WebSockets, obfuscation, and rotating infrastructure to evade detection and maintain access to compromised accounts.
Read More
Raspberry Robin screenshot
Raspberry Robin
raspberryrobin
Raspberry Robin is a trojan that primarily spreads through infected USB drives and exploits legitimate Windows commands. This malware is known for its advanced obfuscation techniques, anti-debugging mechanisms, and ability to gain persistence on infected systems. Raspberry Robin often communicates with command-and-control servers over the TOR network and can download additional malicious payloads.
Read More
Overlord RAT screenshot
Overlord RAT
overlord
Overlord RAT is a cross-platform remote access framework with Go-based agents and a TypeScript/Node/Bun server. It supports encrypted WebSocket C2, remote control, persistence, and multiple operating systems, including Windows, Linux, and macOS.
Read More
Interlock screenshot
Interlock
interlock
Interlock is a relatively recent entrant into the ransomware landscape. First identified in 2023, it's a multi-functional malware strain used in ransomware-as-a-service (RaaS) operations.
Read More
BTMOB RAT screenshot
BTMOB RAT
btmob
BTMOB RAT is a remote access Trojan (RAT) designed to give attackers full control over infected devices. It targets Windows and Android endpoints. Its modular structure allows operators to tailor capabilities, making it suitable for espionage, credential theft, financial fraud, and establishing long-term footholds in corporate networks.
Read More