Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
101
Global rank
92 infographic chevron month
Month rank
88 infographic chevron week
Week rank

Dharma is advanced ransomware that has been observed in the wild since 2016. It is considered to be the second most profitable RaaS operation by the FBI. The malware targets hospitals and state organizations, encrypts files, and demands a payment to restore access to lost information.

Ransomware
Type
Unknown
Origin
24 August, 2017
First seen
4 October, 2026
Last seen

How to analyze Dharma with ANY.RUN

Type
Unknown
Origin
24 August, 2017
First seen
4 October, 2026
Last seen

IOCs

IP addresses
69.222.184.7
73.237.28.132
210.127.88.188
58.222.58.214
174.141.87.185
128.229.248.20
107.249.152.244
4.185.56.82
217.60.195.226
45.158.25.76
210.249.136.175
79.78.235.239
210.43.247.12
211.234.111.223
73.198.107.110
210.24.185.198
218.21.158.18
113.142.242.239
43.22.41.45
184.239.240.82
Hashes
d96856cd944a9f1587907cacef974c0248b7f4210f1689c1e6bcac5fed289368
aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
72f6b34d3c8f424ff0a290a793fcfbf34fd5630a916cd02e0a5dda0144b5957f
5fc25c30aee76477f1c4e922931cc806823df059525583ff5705705d9e913c1c
46079c0a1b660fc187aafd760707f369d0b60d424d878c57685545a3fce95819
2eb96422375f1a7b687115b132a4005d2e7d3d5dc091fb0eb22a6471e712848e
b7ee468f5b6c650dada7db3ad9e115a0e97135b3df095c3220dfd22ba277b607
76d8e4ed946deefeefa0d0012c276f0b61f3d1c84af00533f4931546cbb2f99e
5c9bc70586ad538b0df1fcf5d6f1f3527450ae16935aa34bd7eb494b4f1b2db9
72c639d1afda32a65143bcbe016fe5d8b46d17924f5f5190eb04efe954c1199a
7102f8d9d0f3f689129d7fe071b234077fba4dd3687071d1e2aeaa137b123f86
d6708d1254ed88a948871771d6d1296945e1aa3aeb7e33e16cc378f396c61045
058eb7ce88c22d2ff7d3e61e6593ca4e3d6df449f984bf251d9432665e1517d1
f5183b8d7462c01031992267fe85680ab9c5b279bedc0b25ab219f7c2184766f
ec359f50ca15395f273899c0ff7c0cd87ab5c2e23fdcfc6c72fedc0097161d4b
0b7ed6e2c81e12a0caa32aa89831a68c26b6de783343ca88fbdc3632945cd463
ea1c3e010bd4dc31758d6b11db96e5e9ebaca967d4209169e9998c37610693ef
ed1fc183893beb454e0afd01235106637c441e597e962285fcbbcfc6df9f21f6
f2c17a067ea57b1908e46c8d5e78699f2b9371cf25f1e3a9bc25083ae928a96b
ccff90eb951ac70f01134e0ad8736d0567060b7a535dc742b9508f8a5d69bb33
Domains
crl3.digicert.com
xvasyijoifann.ru
60aaf9c6.salamanderprocessing.pages.dev
dns.google
abortinoiwiam.shop
audicontadores.com
login.live.com
erxtbgrqmvdwo.biz
yr1.c.lencr.org
mnurlogistics.az
sirhirssg.su
toolshare.com.tr
nodejs.org
atirflee.world
client-download.steampowered.com
grupocaprem.com
fussionmd.com
gro.runtimeforge.cc
cs.go.kg
www.blackhattoolz.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://185.213.240.64/bot.exe
http://158.94.208.124/bin/screenconnect.clientsetup.exe
http://178.16.52.209/agent.exe
http://193.178.158.57/bin/bc116af5e724cfa4_zx.exe
http://193.178.158.57/bin/67dbf1a8e19934e4_thread_hijacking_cayoy4nb.exe
http://193.178.158.57/bin/e6efd8bd3bf0fae2_moratorium_0.96.2.9_install.exe
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2621
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4166
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11716
comments 0

What is Dharma ransomware?

Dharma is a ransomware-type malware. A malicious program that encrypted files and demands a ransom to restore information. Dharma, a member of the CrySIS family, has been around since August 2017, targeting organizations such as hospitals. It managed to earn attackers over $25 million in ransom payments.

General description of Dharma ransomware

Dharma is considered to be advanced ransomware that uses powerful encryption. As a new variant of the CrySIS family, it was first spotted in the wild in 2017. It was operated by an unknown cyber gang who managed to remain mostly in the shadows to this day. CrySIS was offered as a RaaS (Ransomware-as-a-Service), meaning that “clients” could use it, if they purchased the ransomware from the attackers. This means that those who purchase the malware carry out the actual attacks rather than original creators.

Threat actors changed the name over to Dharma after decryption keys for CrySIS were leaked in late 2016. That was the first, but not the only time somebody published the decryption keys, but it was the only time attackers renamed the malware and re-branded the product.

Some researchers believe that Dharma is one of the most popular RaaS malware out there right now. The popularity of this ransomware is partly due to the constant updates that attackers have been rolling out throughout the years it was active.

In fact, there were instances where three new versions of the malware were reported during the same week. In addition, Dharma proved to be very adaptive, changing distribution channels as the underground community moved from mass spam emails to more targeted attacks in 2018 and 2019.

Another part that contributed to the popularity of Dharma is its flexibility. Although the ransom amount is usually set to one Bitcoin, it can be customized depending on the victim profile. This means that for smaller organizations that can’t pay this much (mind you, Bitcoin cost almost 20,000 USD in 2017), the payment amount can be lowered.

Although not unique to this malware, this flexibility and customization greatly enhanced its effectiveness. In fact, the FBI named Dharma the second most profitable ransomware operation.

Now, despite all of the above, Dharma has never really been available to the general public. The only places it could be found were inconspicuous underground forums. At least, until recently.

In late 2019, the source code of Dharma was observed being put for sale for 2,000 USD.

This made many researchers worried, as some predicted that putting the source code for sale will result in somebody uploading it to the public internet. If ransomware as advanced as Dharma gets in the hands of a mass audience, we can be up for a lot of trouble.

It should also be noted that in 2019 researchers reported new ransomware called Phobos, which has almost the same code as Dharma. Although some speculated that this could be another rebranding, Dharma samples are still constantly being found about as often as instances of Phobos malware use.

Dharma malware analysis

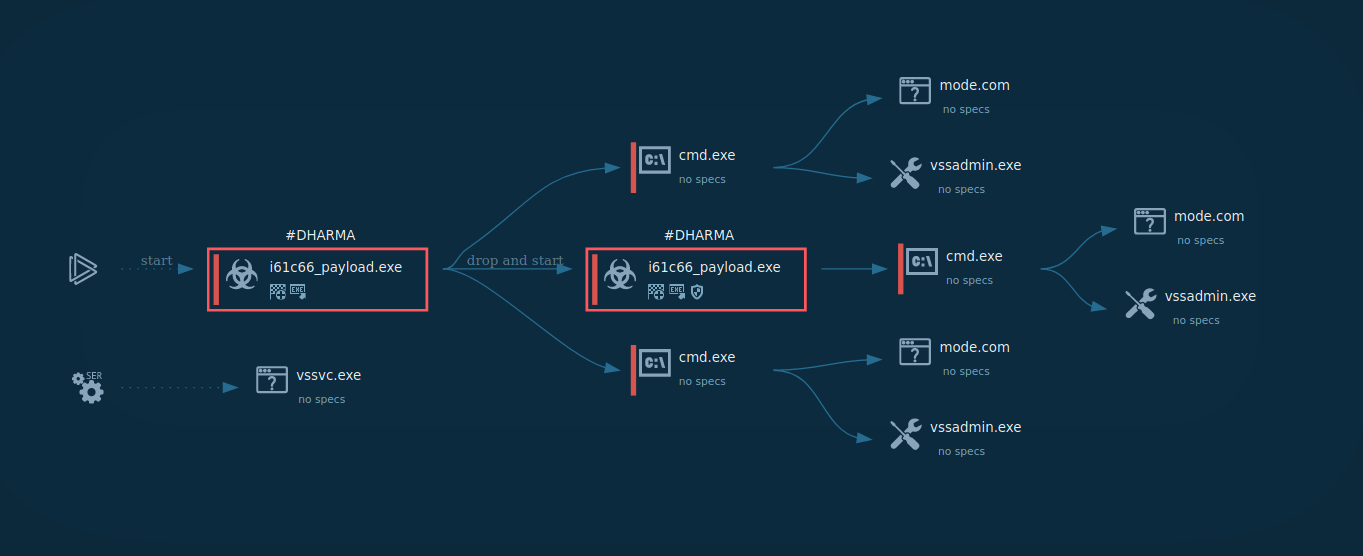
A video recorded in the ANY.RUN interactive malware hunting service shows how the execution of this ransomware unfolds from the victim’s point of view.
raccoon_process_graph

Figure 1: Displays the execution process of the Dharma ransomware This graph was generated by ANY.RUN.
raccoon_process_graph

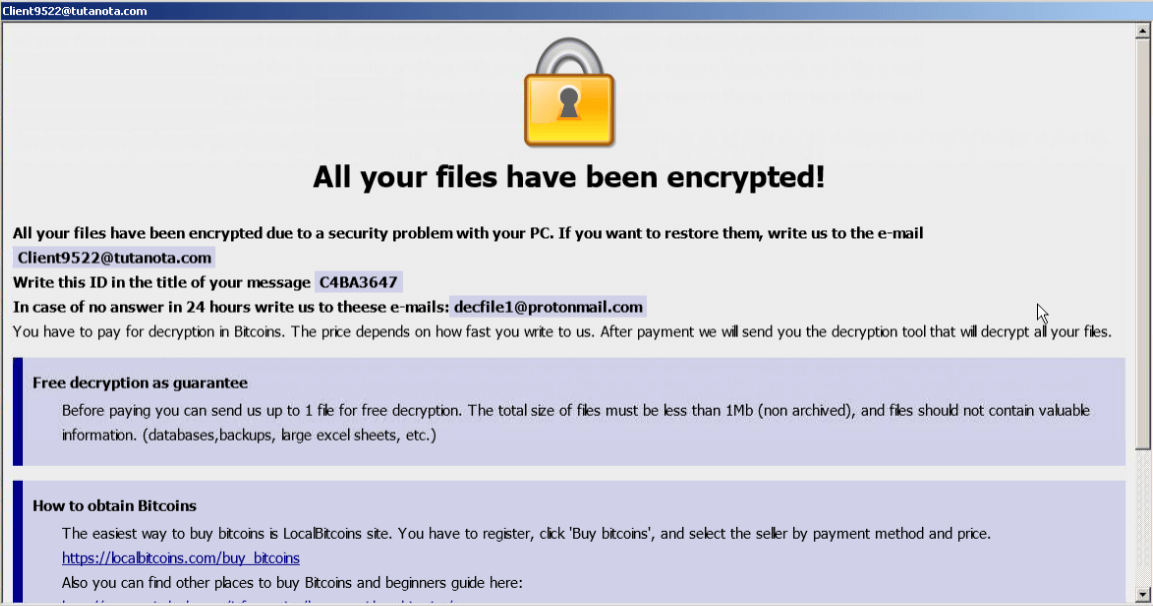
Figure 2: Displays the Dharma ransomware ransom note

Dharma ransomware execution process

The execution process of the Dharma ransomware is relatively typical for this type of malware such as WannaCry. After the executable file makes its way into an infected system and runs, the main malicious activity begins. After the start of execution, the ransomware deletes shadow copies. After it encrypts all targeted files, Dharma drops a ransom note on the desktop.

Dharma ransomware distribution

Dharma has been observed using multiple distribution methods, but the following three are the most common.

  • Targeted emails with malicious attachments or links.
  • Use of compromised legitimate software, often antiviruses.
  • Targeted campaigns that abuse the RDP protocol.

Out of the three distribution channels, spam email campaigns are the most straightforward. It is also how threat actors relied on the most during the first years of malware operation, launching widespread campaigns and relying on sheer numbers of potential recipients.

However, as users and organizations become more educated about the dangers of cyberattacks, spam emails lose effectiveness. Dharma operators quickly adapted and restored to the other two methods for payload delivery.

Another method that Dharma is known to use is utilizing real compromised software. For example, some attacks involved targeted email campaigns that contained a download link. What made these attacks stand out is that upon clicking the link, the payload would be downloaded along with a compromised legitimate program. The program then would launch an installer designed to direct the victim's attention while the executable file is running in the background.

Finally, the last common distribution method is through the use of compromised RDP. RDP is a protocol developed by Microsoft used to establish a connection between multiple PCs over a network. It’s a completely legitimate protocol that technicians use to carry out remote technical support, among other uses. However, if a session becomes compromised, it gives hackers the ability to download and execute the malicious file as long as they have access to the remotely connected PC.

Conclusion

Dharma is dangerous ransomware. Since 2017 its popularity has been only growing, and continued use indicates that members of the underground hacking community see it as a reliable option. Given that even the FBI considers Dharma to be one of the most effective malware in its class, it’s no wonder that this malware is in demand.

However, even more, worrying is that despite all the attention that Dharma has been getting over the years, creators of this ransomware managed to evade researchers and evolve the ransomware along the way continually.

Although decryptors do exist for some versions of Dharma, the only reason they could be created is that somebody from the inside leaked master keys. Apart from these instances, little progress has been made to crack the encryption algorithm used by Dharma.

And now, with the source code appearing for sale, we run the risk of it popping up on the global Internet, which can spawn a new, massive wave of Dharma attacks.

Keeping this in mind, researchers should take time to study Dharma behavior to prepare for potential attacks carefully. Thankfully, ANY.RUN provides all the necessary tools to carry out Dharma analysis in a secure online environment.
HAVE A LOOK AT

Miolab Stealer screenshot
Miolab Stealer is a macOS malware threat designed to steal user credentials and sensitive files without raising immediate suspicion. It relies on fake system prompts and legitimate built-in tools to make malicious actions look routine. Instead of causing obvious disruption, it quietly collects valuable data and prepares it for exfiltration from the device. By blending deception with trusted macOS behavior, it increases the chance that the attack will go unnoticed in its early stages. This makes early behavioral detection critical before the theft of credentials and files is complete.
Read More
Qilin Ransomware screenshot
Qilin ransomware (predecessor known as “Agenda”) is a rapidly evolving ransomware-as-a-service (RaaS) operation targeting organizations worldwide. Known for double extortion tactics (encrypting files while also threatening to leak stolen data) Qilin has quickly gained notoriety for its customization, flexibility, and impact on critical infrastructure.
Read More
Kamasers screenshot
Kamasers
kamasers
Kamasers is a multi-functional DDoS botnet malware that transforms infected machines into remotely controlled attack nodes. It combines network-layer flooding capabilities, resilient command-and-control (C2), and payload delivery, making it not just a disruption tool but a gateway to broader compromise.
Read More
PureCrypter screenshot
PureCrypter
purecrypter
First identified in March 2021, PureCrypter is a .NET-based loader that employs obfuscation techniques, such as SmartAssembly, to evade detection. It has been used to distribute malware families including AgentTesla, RedLine Stealer, and SnakeKeylogger. The malware is typically delivered through phishing campaigns and malicious downloads, often masquerading as legitimate files with extensions like .mp4 or .pdf. PureCrypter utilizes encryption and compression to conceal its payloads and can inject malicious code into legitimate processes to maintain persistence on the infected system.
Read More
Trojan screenshot
Trojan
trojan trojan horse
Trojans are a group of malicious programs distinguished by their ability to masquerade as benign software. Depending on their type, trojans possess a variety of capabilities, ranging from maintaining full remote control over the victim’s machine to stealing data and files, as well as dropping other malware. At the same time, the main functionality of each trojan family can differ significantly depending on its type. The most common trojan infection chain starts with a phishing email.
Read More
Stealer screenshot
Stealer
stealer
Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns.
Read More