Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
114
Global rank
88 infographic chevron month
Month rank
76 infographic chevron week
Week rank

Troldesh is ransomware — a malware that demands a payment in order to unlock encrypted files. It is also can search and steal information from the banking programs if such are found on the infected machine.

Ransomware
Type
Unknown
Origin
1 January, 2014
First seen
4 October, 2026
Last seen
Also known as
Encoder.858

How to analyze Troldesh with ANY.RUN

Type
Unknown
Origin
1 January, 2014
First seen
4 October, 2026
Last seen

IOCs

IP addresses
69.222.184.7
73.237.28.132
210.127.88.188
58.222.58.214
174.141.87.185
128.229.248.20
107.249.152.244
4.185.56.82
217.60.195.226
45.158.25.76
210.249.136.175
79.78.235.239
210.43.247.12
211.234.111.223
73.198.107.110
210.24.185.198
218.21.158.18
113.142.242.239
43.22.41.45
184.239.240.82
Hashes
d96856cd944a9f1587907cacef974c0248b7f4210f1689c1e6bcac5fed289368
aac73b3148f6d1d7111dbca32099f68d26c644c6813ae1e4f05f6579aa2663fe
72f6b34d3c8f424ff0a290a793fcfbf34fd5630a916cd02e0a5dda0144b5957f
5fc25c30aee76477f1c4e922931cc806823df059525583ff5705705d9e913c1c
46079c0a1b660fc187aafd760707f369d0b60d424d878c57685545a3fce95819
2eb96422375f1a7b687115b132a4005d2e7d3d5dc091fb0eb22a6471e712848e
b7ee468f5b6c650dada7db3ad9e115a0e97135b3df095c3220dfd22ba277b607
76d8e4ed946deefeefa0d0012c276f0b61f3d1c84af00533f4931546cbb2f99e
5c9bc70586ad538b0df1fcf5d6f1f3527450ae16935aa34bd7eb494b4f1b2db9
72c639d1afda32a65143bcbe016fe5d8b46d17924f5f5190eb04efe954c1199a
7102f8d9d0f3f689129d7fe071b234077fba4dd3687071d1e2aeaa137b123f86
d6708d1254ed88a948871771d6d1296945e1aa3aeb7e33e16cc378f396c61045
058eb7ce88c22d2ff7d3e61e6593ca4e3d6df449f984bf251d9432665e1517d1
f5183b8d7462c01031992267fe85680ab9c5b279bedc0b25ab219f7c2184766f
ec359f50ca15395f273899c0ff7c0cd87ab5c2e23fdcfc6c72fedc0097161d4b
0b7ed6e2c81e12a0caa32aa89831a68c26b6de783343ca88fbdc3632945cd463
ea1c3e010bd4dc31758d6b11db96e5e9ebaca967d4209169e9998c37610693ef
ed1fc183893beb454e0afd01235106637c441e597e962285fcbbcfc6df9f21f6
f2c17a067ea57b1908e46c8d5e78699f2b9371cf25f1e3a9bc25083ae928a96b
ccff90eb951ac70f01134e0ad8736d0567060b7a535dc742b9508f8a5d69bb33
Domains
crl3.digicert.com
xvasyijoifann.ru
60aaf9c6.salamanderprocessing.pages.dev
dns.google
abortinoiwiam.shop
audicontadores.com
login.live.com
erxtbgrqmvdwo.biz
yr1.c.lencr.org
mnurlogistics.az
sirhirssg.su
toolshare.com.tr
nodejs.org
atirflee.world
client-download.steampowered.com
grupocaprem.com
fussionmd.com
gro.runtimeforge.cc
cs.go.kg
www.blackhattoolz.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://185.213.240.64/bot.exe
http://158.94.208.124/bin/screenconnect.clientsetup.exe
http://178.16.52.209/agent.exe
http://193.178.158.57/bin/bc116af5e724cfa4_zx.exe
http://193.178.158.57/bin/67dbf1a8e19934e4_thread_hijacking_cayoy4nb.exe
http://193.178.158.57/bin/e6efd8bd3bf0fae2_moratorium_0.96.2.9_install.exe
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1128
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2922
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10390
comments 0

What is Troldesh ransomware?

Troldesh, also known as Encoder.858, is ransomware belonging to the Shade ransomware family. It was created in 2014. The malware encrypts files on the victim's machine and demands a ransom for the data to be restored.

Attempting to get as much information as possible, the malware also scans the target PC for banking files or banking programs to squeeze every last penny.

General description of Troldesh

Attacking Windows users mainly in Russia, Ukraine, and Germany, Troldesh is one of Russia's most commonly used encryption software.

In addition to this behavior, Troldesh ransomware often comes in conjunction with two particular malware samples, namely Mexar, and Teamspy, which allows attackers to control the victim's PC remotely and gives the virus the ability to install other malware, including trojans on the infecting PC.

In fact, unlike most other ransomware Nemty or others, this virus does not stop executing after encrypting the victim's files. Instead, it starts an infinite loop where it requests URLs of other malicious programs from the command server, downloading and installing them on a contaminated machine. This strategy means that most victims contaminated with Troldesh may end up with a whole host of infections on their PC. And even with removal tools and decryptors, it can be challenging to get rid of this issue.

Even though the malware itself has not evolved a lot throughout its lifespan, attackers' method to demand the ransom has changed. The first malware samples were used to provide an email address at which the victim could contact the hackers and negotiate the payment. In newer campaigns, ransom node demands victims to use the Tor browser to navigate to a payment page that is located on the Dark Web.

Trodlesh, as part of the Shade family, shares several familiarities with related malware: they are written in C++, utilize CTL, use a static link with a Tor client. Every particular malware sample also has a hardcoded URL of the command server. Malicious programs of this family are also known to exhibit similar or identical behavior. As such, they create ten identical ransom notes in two languages – Russian and English and name them README1.txt or README10.txt.

Troldesh malware analysis

A video simulation recorded on ANY.RUN allows us to examine the lifecycle of the Troldesh malware in a lot of detail.
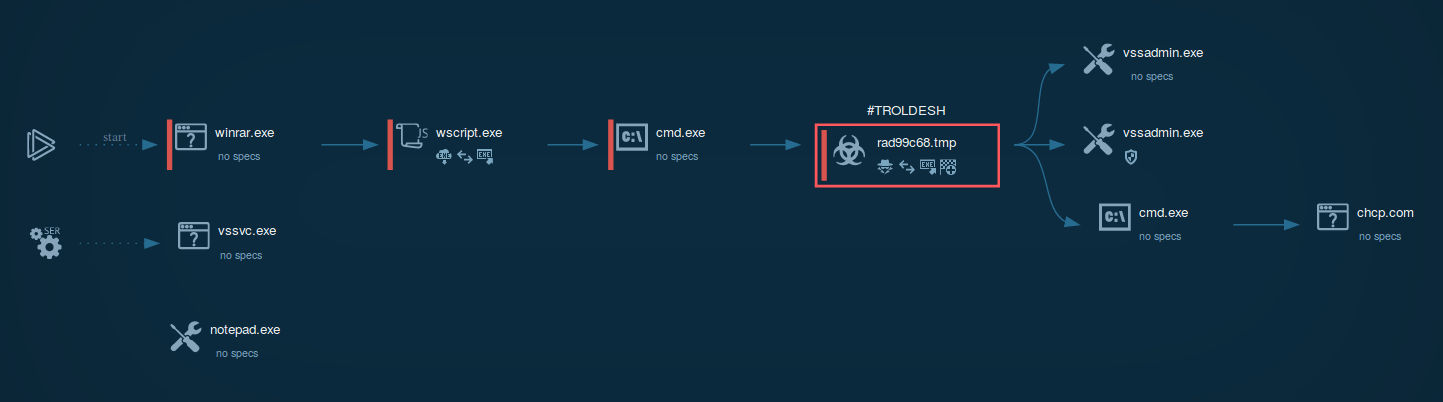
process graph of a troldesh ransomware execution Figure 1: Process graph generated by ANY.RUN helps us visualize the life cycle of the virus

Troldesh execution process

Troldesh ransomware is spread in the form of a script file, either Javascript or JScript. Usually, these files are packed in an archive file that is sometimes protected with a password. In the simulation performed on ANY.RUN, after a script file was unpacked and launched, it installed an executable file from the internet. It should be noted that in the case of Troldesh, executable files typically have "not suspicious" extensions along with the likes of .jpg. After being downloaded, the files are renamed and executed.

As shown in the ANY.RUN simulation, after running, the file immediately began performing the malicious activity, namely: encrypting files, stealing personal data, deleting shadow copies, and changing autorun values in the registry. Files encrypted by the latest versions of Troldesh are known to have a .crypted000007 extension which was also the case in our simulation. Lastly, after encryption was completed, the malicious executable file dropped ransomware instructions on the desktop.
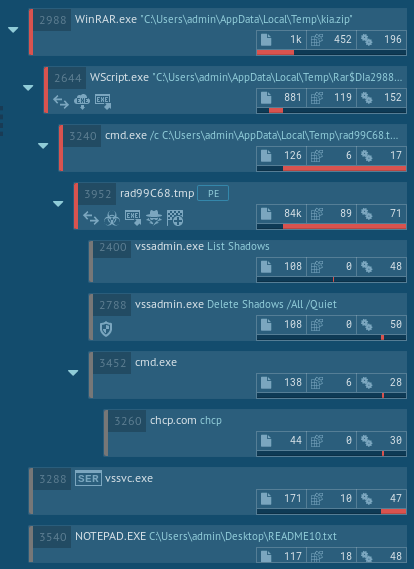
process tree of a troldesh ransomware execution Figure 2: Process tree of a Troldesh ransomware execution

How to avoid infection by Troldesh?

Since Troldesh is commonly distributed using malspam campaigns that mimic real company newsletters, a good way of staying safe is thoroughly checking for the authenticity of emails before downloading any attachments. If necessary, one can get in touch with a company that is the presumable author of the newsletter and verify that they have sent the email.

Once infected, Troldesh installs several secondary malware samples on the victim's PC, thus after Troldesh removal – malware deletes itself from the PC, it is vital to conduct a global system scan and make sure that one's machine is not swarming with other viruses as well.

Distribution of Troldesh

Troldesh ransomware is known to utilize two main attack vectors – email spam and exploit kits. Malspam campaigns usually mimic legitimate information newsletters from actual Russian companies, including banks and large supermarket chains. The emails themselves contain an archive file in which another script file is included.

Upon unpacking the archive and clicking on the file, a malicious loader is installed. It in turn downloads and installs the main payload – Troldesh itself. The loader is known to be stored on legitimate but compromised WordPress websites where it is hidden as an image file.

Troldesh is also known to utilize Axpergle and Nuclear exploit kits, and these attacks are, arguably, more dangerous than email spam as they don't require active actions from the user for the contamination process to begin. Instead, upon visiting a compromised URL, which can be a website hosted by the attackers or a legitimate website that has been hacked, the malware utilizes a vulnerability either in the browser itself or in one of the browser plugins, successfully penetrating into the users PC and starting the execution automatically. Thus, victims can get infected without ever realizing the danger, so get a removal program and a decryptor.

Communication with C&C

Address information of C&C servers is embedded in the body of each malware sample. Servers themselves are hosted on the dark web and communication is established with the use of a Tor client.

Once installed on a victim's PC, the malware requests a public key value from the server to encrypt the victim's files. Should the connection attempt fail, the virus uses one of one hundred private key values stored in its memory.

How to detect Troldesh using ANY.RUN?

Since Troldesh ransomware writes into the registry analysts can detect it by looking at registry keys. Choose the process by clicking on it in the process tree of the task then click on the "More info" button. In the "Advanced details of process" window switch to the "Registry changes" tab and take a closer look. If the analyzed sample writes a value "906D0F2E2F604F839E04" with the name "xi" into the key HKLM\SOFTWARE\System32\Configuration it's Troldesh.
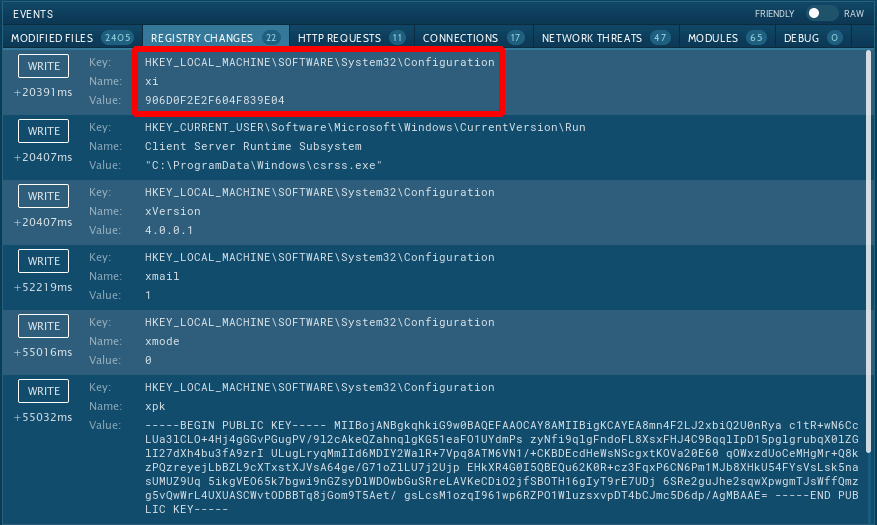
Registry changes created by Troldesh Figure 3: Registry changes created by Troldesh

Conclusion

Troldesh is an extremely dangerous ransomware that is able to contaminate victims who simply end up browsing to the wrong place at the wrong time, ending up on a website hacked by the attackers. Unlike much other ransomware that simply demands money in exchange for user's encrypted data, Troldesh doesn't stop there and goes the extra mile to spread other dangerous malware samples on a victim's PC.

Utilizing analysis services like ANY.RUN is a great way to examine the virus from a safe environment and develop a sufficient defense strategy.

P.S.

On the 27th of April, 2020 authors behind Troldesh ransomware announced that they stopped distribution of the ransomware and publish the decryption keys with a decryptor and instructions. They said that apologize to all the victims of the trojan and hope that the keys they published will help them to recover their data. The same scenario had a couple of other ransomware writers, even the infamous Maze.

You can take a look at the task in which their keys and tool were used to decrypt data.
HAVE A LOOK AT

Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
GREENBLOOD screenshot
GREENBLOOD
greenblood
GREENBLOOD is a Go-based ransomware that uses concurrent ChaCha8 encryption to lock entire Windows environments in under a minute while systematically destroying backups, disabling defenses, and threatening double extortion through a Tor-based data leak site.
Read More
Agent Tesla screenshot
Agent Tesla
agenttesla trojan rat stealer
Agent Tesla is spyware that collects information about the actions of its victims by recording keystrokes and user interactions. It is falsely marketed as a legitimate software on the dedicated website where this malware is sold.
Read More
Ransomware screenshot
Ransomware
ransomware
Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying.
Read More
DoubleTrouble screenshot
DoubleTrouble
doubletrouble
DoubleTrouble is a new-generation Android malware designed to quietly infiltrate mobile devices, harvest sensitive data, hijack financial operations, and maintain long-term persistence. Unlike commodity Android trojans, it blends advanced evasion, dual-stage infection, and dynamic payload updates, making it a rising mobile threat for both consumers and organizations.
Read More