
After months of using ANY.RUN Interactive Sandbox, a US-based MSSP expanded its security stack with ANY.RUN Threat Intelligence. By bringing known malicious indicators directly into its SIEM, the team could reduce manual checks and focus deeper investigations on threats that required behavioral analysis. This helped the growing MSSP increase operational capacity without compromising service quality.
We talked to the MSSPs’ Head of SOC about how they achieved more connected security workflows, reduced manual checks, and brought threat context into their existing stack by expanding the use of ANY.RUN solutions.
The Starting Point: A Growing MSSP
Before expanding its use of ANY.RUN, the organization (which preferred to remain anonymous – Ed.) was looking for a way to scale without sacrificing investigation quality. The MSSP company was expanding its customer base, maintaining strong service quality, and taking on larger clients, including enterprises with thousands of endpoints to protect.
Behind these results was a close-knit SOC team of one manager and five analysts. They had established effective investigation processes, relying on SIEM enrichment and open-source IOC checks. But taking on more customers also meant more alerts to investigate, more SLA commitments to meet, and growing pressure on staffing costs:
We were getting more customers and more alerts to deal with. Hiring more analysts was one option, but we also wanted to improve the way we worked.
As they started to scale their services, operational improvements became necessary. The number of customers and alerts increased, and the team needed to handle a larger workload without compromising investigation quality or putting additional pressure on analysts. The goal was to find a better balance between quality and speed.
Integrating Sandbox into SOC Workflows
The US-based MSSP was already using ANY.RUN Interactive Sandbox on an individual basis, but its role in the company’s SOC operations was limited. With more alerts to process, the team decided to integrate Sandbox into its existing security workflows by moving to the Enterprise Suite plan.
They integrated Sandbox with its existing SIEM using ANY.RUN’s API. This allowed analysts to incorporate sandbox analysis into their established investigation process rather than working with it as a separate tool.
The team already knew Sandbox was useful because we’d been using it for a while. The next step was making it part of how the whole company worked.
Operational Improvements
The integration of ANY.RUN Sandbox allowed the team to build on its existing success by achieving:
- Faster investigations: Analysts spent less time checking suspicious activity and gathering evidence.
- Less manual work: Automated Interactivity handled routine analysis steps.
- Better teamwork: Analysts could share findings and avoid repeating each other’s work.
- Smoother workflows: Sandbox became part of their existing SOC processes instead of a separate tool.
Overall, we were spending less time on each alert. That made it easier to meet our SLAs, and the reports helped us show customers what we’d done during investigations.
Explore all ANY.RUN integrations
How Integration Translated into Business Outcomes
They also helped the company improve service delivery and support its growing customer base.
- Easier SLA compliance: Less time spent per alert helped the team meet customer response-time commitments.
- 25% greater SOC capacity: The team could handle more alerts with the same five analysts, supporting customer growth without proportional hiring costs.
- Better cost efficiency: More efficient investigations reduced the analyst effort required per alert, helping the MSSP scale without relying solely on additional hiring.
Better Visibility Led to Greater SOC Capacity
The challenge that remained was a lack of wider visibility.
Sandbox provided deep insights into threats, but for a broader overview of what was happening in other organizations, industries, and security teams, the company needed swift access to threat intelligence.
“Could some of the threats we analyze be identified earlier?” was the question now standing before the MSSP’s team lead.
The Sandbox gave our analysts the evidence they needed to understand threats. But we wanted to see whether we could identify more of those threats earlier, before an analyst had to investigate them manually.
That’s why, after about half a year of using the integrated Sandbox, the MSSP adopted ANY.RUN Threat Intelligence to bring malicious IOC data into its SIEM. This allowed the team to identify known malicious indicators earlier in the monitoring and triage process, before analysts needed to investigate each suspicious object manually.
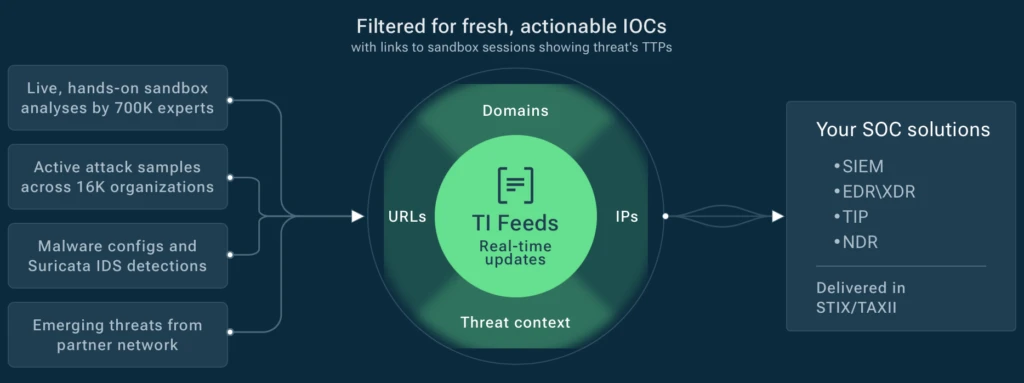
The team integrated ANY.RUN Threat Intelligence Feeds with its SIEM through an out-of-the-box integration.
For the MSSP, this created an important change. When a suspicious indicator matched intelligence from TI Feeds, the integrated security platform could automatically tag it as malicious. Analysts could use that result during triage instead of starting every investigation with the same manual checks.
We were already improving our metrics from the Sandbox. Adding feeds meant we could basically bring threat knowledge from other companies into our workflow instead of manual analysis.
According to ANY.RUN data (not related to this particular customer case – Ed.), approximately 30% of unique malicious IOCs from studied Sandbox sessions had already been observed by ANY.RUN and were present in TI Feeds before investigation.
In other words, some indicators that analysts encounter during behavioral investigations may already be known through threat intelligence.
For the MSSP, this meant making better use of its existing resources, increasing operational capacity, and supporting further business growth without compromising service quality.
An Updated SOC Pipeline for Handling More Alerts
After integrating ANY.RUN Threat Intelligence, the MSSP also started using Threat Intelligence Lookup to examine individual indicators, related infrastructure, and threat activity across different industries.
This gave analysts additional context for prioritizing suspicious activity and deciding which cases required deeper investigation, helping maintain consistent triage quality across customer environments.
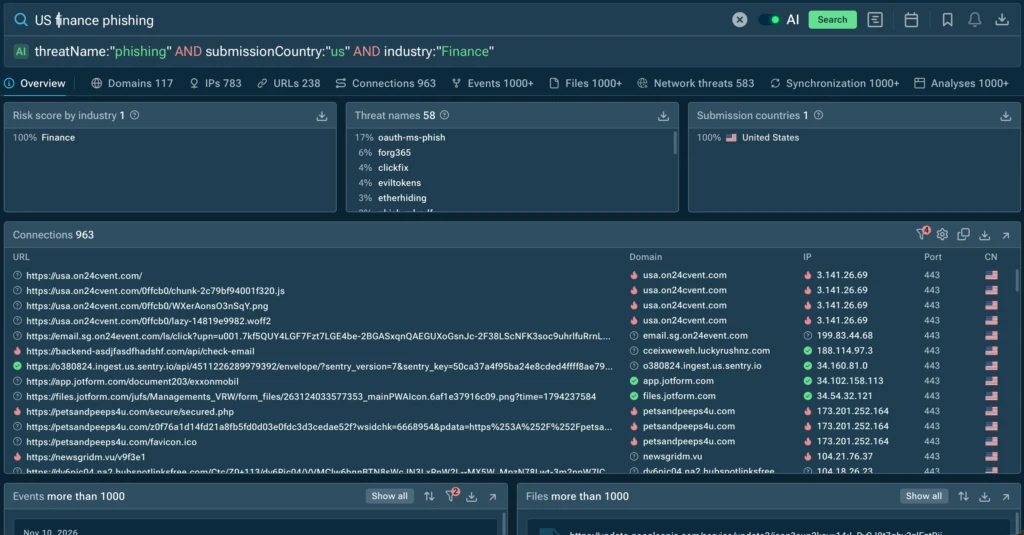
Industry-related context added another layer of visibility, helping the MSSP assess threats in relation to the sectors its customers operated in. For a provider serving companies across different industries, this meant more relevant context for prioritizing suspicious activity and deciding what required further analysis.
That’s how the team updated its approach to threat detection and triage to achieve a more connected process:
SIEM monitoring + TI Feeds matching → Initial triage → Sandbox behavioral analysis or TI Lookup enrichment when needed → Informed response decision
Adding threat intelligence meant getting more value from its existing Sandbox investment.
With TI Feeds helping identify known malicious indicators earlier, analysts could focus deeper investigations on cases requiring additional behavioral evidence or threat context. This made the workflow more efficient without compromising investigation quality.
Instead of treating threat intelligence and malware analysis as separate activities, the MSSP could use them at different stages of the same investigation.
The biggest improvement was how the solutions worked together. With threat intelligence we recognize malicious activity before it becomes a risk, while Sandbox remains our go-to when we needed deeper evidence.
The Business Payoff: Scaling without Sacrifices
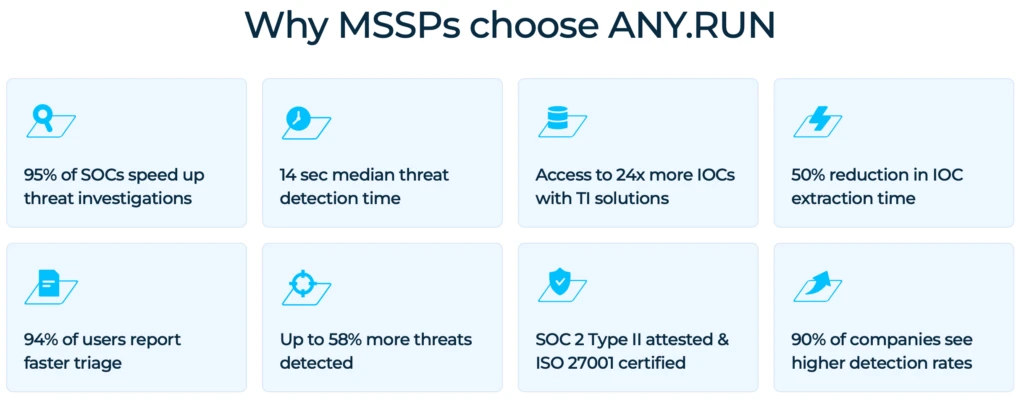
By integrating malware analysis and threat intelligence, the MSSP found a better balance between investigation quality and speed.
We were handling around 30% more alerts with the same team. Having threat intelligence connected to our existing stack meant we didn’t have to change much to work better.
The main improvements were:
1. 30% More Alerts Handled
Reducing repetitive work helped the MSSP process more alerts and support its growing customer base.
2. Better SLA Performance
Faster investigations and more focused triage helped the team meet response-time commitments while maintaining service quality.
3. 25% Greater SOC Capacity
Integrating malware analysis and threat intelligence helped the MSSP increase analyst productivity and scale operations more cost-effectively.
5. Broader Threat Context
TI Lookup helped analysts assess suspicious activity in the context of different industries, supporting more consistent prioritization across customer environments.
These improvements helped the MSSP scale its operations while maintaining investigation quality and improving speed.
Want to Improve Your SOC or MSSP Investigation Workflow?
Explore how ANY.RUN Threat Intelligence can help your SOC identify known threats earlier, reduce manual IOC checks, and focus investigation resources where they matter most.
Built on threat data from 16K+ SOCs and 700K+ security experts, it helps growing MSSPs increase operational capacity while maintaining service quality.
About ANY.RUN
ANY.RUN provides interactive malware analysis and threat intelligence solutions that help security teams detect, investigate, and respond to cyber threats.
TI Feeds bring malicious indicators into existing monitoring workflows to support earlier threat identification. TI Lookup provides context for IOC investigation and prioritization, while Interactive Sandbox delivers behavioral evidence for deeper threat analysis. Together, these solutions help SOC teams reduce repetitive work, accelerate triage, and make better-informed investigation decisions.
0 comments