
Every employee-reported suspicious email requires triage, but manually submitting messages for deeper analysis and transferring results between tools slows down SOC operations.
The new ANY.RUN integration for KnowBe4 PhishER automates the behavioral analysis stage of phishing triage by connecting PhishER with ANY.RUN Interactive Sandbox. Selected emails are automatically submitted for analysis, with verdicts returned directly to PhishER to reduce manual work and support faster, evidence-based decisions.
About the ANY.RUN Sandbox Integration for KnowBe4 PhishER
KnowBe4 PhishER helps security teams manage suspicious emails reported by employees through configurable Rules, Actions, and automated classification workflows.
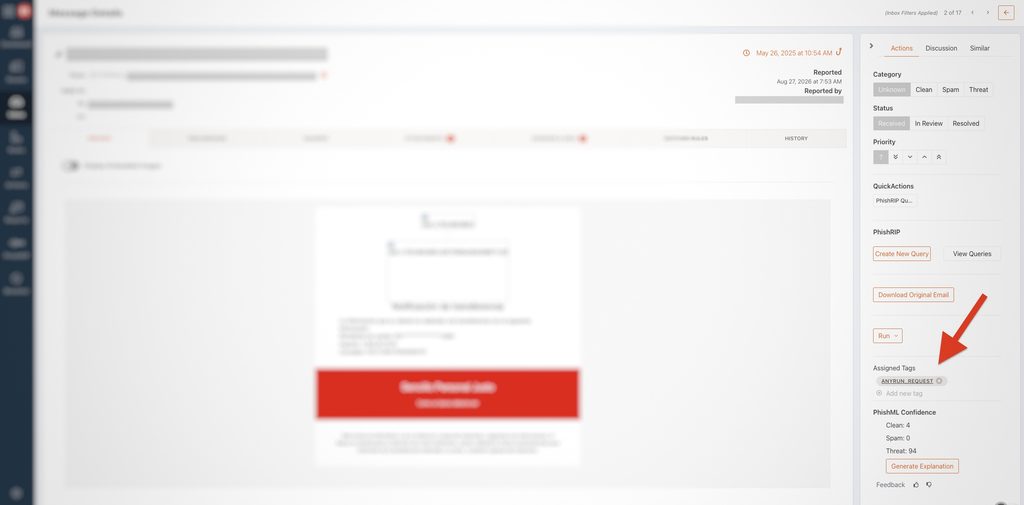
The new self-hosted ANY.RUN integration extends this process with behavioral analysis, allowing organizations to:
- Automate Suspicious Email Analysis: Automatically submit flagged emails from PhishER to ANY.RUN Sandbox, eliminating manual transfers and repetitive analysis setup.
- Get Actionable Threat Verdicts: Receive MALICIOUS, SUSPICIOUS, or CLEAN verdicts directly in PhishER to quickly determine which emails need further investigation.
- Detect Hidden Phishing and Malware Threats: Use behavioral analysis to uncover malicious activity in suspicious attachments and links that requires deeper validation.
- Trigger Faster Phishing Response: Use Sandbox verdicts in PhishER Rules and Actions to route malicious emails for response and suspicious cases for further review.
- Investigate Complex Threats in Depth: Open the linked Sandbox analysis to examine attack behavior, malicious infrastructure, and IOCs when a case requires deeper investigation or escalation.
For deployment and configuration instructions, see the official KnowBe4 integration guide.
The integration checks PhishER for matching messages at a configurable interval, set to five minutes by default. It then queues selected emails for analysis and returns the results once the Sandbox task is completed.
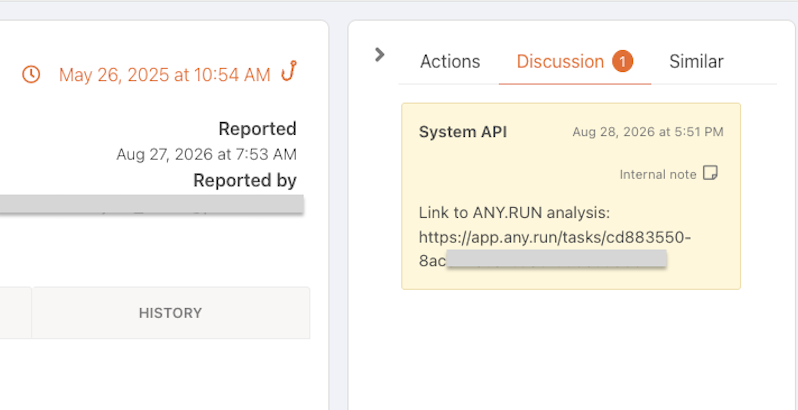
Organizations can also integrate ANY.RUN into their existing PhishER workflows. By default, the integration processes emails tagged ANYRUN_REQUEST, but teams can configure it to recognize their existing tags or apply additional filtering criteria. This allows them to add automated Sandbox analysis to established phishing triage processes while keeping their current Rules and Actions.
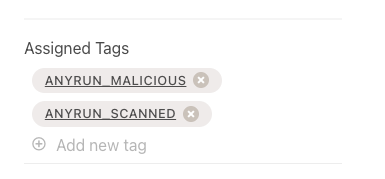
This keeps phishing triage and workflow automation in PhishER, while ANY.RUN provides the behavioral evidence needed to evaluate suspicious messages.
How Your SOC Operations Improve with the Integration
Integrating ANY.RUN Interactive Sandbox into KnowBe4 PhishER helps SOC teams improve phishing triage at every stage, from initial email analysis to threat validation and response.
By automating repetitive tasks and bringing behavioral verdicts into existing workflows, the integration helps analysts investigate suspicious emails faster, make more accurate decisions, and reduce unnecessary escalations.
| SOC Process | How ANY.RUN Strengthens It | Result for SOC |
|---|---|---|
| Email Triage | Automatically submits flagged emails for sandbox analysis. | Less manual work and faster triage. |
| Threat Detection | Uncovers malicious behavior in suspicious attachments and links. | Higher detection accuracy and fewer missed threats. |
| Threat Validation | Returns behavioral verdicts directly to PhishER. | Faster classification and more confident decisions. |
| Incident Response | Enables PhishER Rules and Actions based on Sandbox verdicts. | Faster response initiation and fewer manual handoffs. |
| Case Escalation | Gives Tier 2 direct access to detailed behavioral evidence. | Fewer uncertainty-driven escalations and faster follow-up investigations. |
Reduce Phishing Triage Time and Analyst Workload
Manually exporting suspicious emails, submitting them to a sandbox, monitoring the analysis, and transferring results back to the original case adds repetitive work to every phishing investigation.
The ANY.RUN integration automates these steps. Once an email meets the organization’s configured criteria, it is submitted for analysis, and the result is returned directly to PhishER.
This reduces the time analysts spend on routine investigation tasks and helps them focus on evaluating threats and determining the next response action. 94% of ANY.RUN users report faster triage, demonstrating the operational value of integrating behavioral analysis into daily investigations.
Result: For enterprise SOC teams and MSSPs handling large volumes of suspicious emails, fewer manual handoffs can improve investigation throughput and reduce pressure on analysts during periods of increased phishing activity.
Improve Phishing Detection with Behavioral Evidence
Phishing emails can contain malicious attachments, suspicious links, or content designed to deceive users into interacting with attacker-controlled resources. Identifying these threats often requires examining their behavior beyond the initial email assessment.
ANY.RUN Interactive Sandbox provides behavioral analysis of suspicious content, helping analysts identify malicious activity and understand the evidence behind a verdict.
Through the integration, this analysis becomes part of the established phishing triage process. Selected emails receive a behavioral verdict, while analysts can open the associated Sandbox task to examine processes, network communications, extracted IOCs, and other technical evidence.
ANY.RUN Interactive Sandbox helps security teams achieve a 36% higher detection rate, highlighting the value of behavioral evidence when investigating threats that require deeper validation.
Result: SOC teams can identify more malicious emails requiring further investigation and reduce the risk of incorrectly classifying dangerous content as safe.
Increase Triage Consistency and Reduce Unnecessary Escalations
Phishing investigations can vary considerably depending on an analyst’s experience and the procedures followed during initial triage.
The ANY.RUN integration helps SOC managers establish consistent criteria for behavioral analysis through existing PhishER Rules and Actions.
Emails matching those criteria follow the same submission and analysis process, and their verdicts are returned in a standardized format.
This gives Tier 1 analysts additional evidence to support classification decisions and helps reduce escalations caused primarily by uncertainty. When a case requires deeper investigation, Tier 2 analysts can follow the linked Sandbox task to examine the underlying malicious behavior.
ANY.RUN helps SOC teams reduce Tier 1-to-Tier 2 escalations by 30%, demonstrating how behavioral evidence can help analysts resolve cases with greater confidence.
Result: Teams can improve triage consistency across shifts while reserving senior analyst time for cases that require more advanced investigation.
Accelerate Phishing Response with Automated Verdict-Based Workflows
The value of phishing investigation depends on how quickly its findings can support the next response decision.
With the ANY.RUN integration, analysis results become available as verdict and status tags within PhishER, where they can be used by the organization’s existing Rules and Actions.
For example, a MALICIOUS verdict can serve as a trigger for the next phishing-response action, while a SUSPICIOUS result can route the message for additional review.
This reduces manual handoffs between analysis and subsequent response steps, helping security teams act on behavioral findings more consistently. ANY.RUN helps teams achieve a 21-minute faster Mean Time to Respond, showing the potential impact of faster threat validation on overall SOC response performance.
Result: SOC managers gain greater control over how phishing investigations progress, from defining which messages require sandbox analysis to configuring the actions that follow each verdict.
Conclusion
The ANY.RUN Sandbox integration for KnowBe4 PhishER helps security teams make behavioral analysis a consistent part of their phishing triage operations.
By automating email submission and returning analysis verdicts to PhishER, the integration reduces repetitive analyst work, supports more accurate threat classification, and helps organizations build faster, more consistent phishing-response processes.
The integration is self-hosted and available to paid ANY.RUN customers with Sandbox API access and eligible trial users. An active KnowBe4 PhishER license is required.
About ANY.RUN
Trusted by more than 700,000 cybersecurity professionals and 16,000 organizations, ANY.RUN helps security teams detect and investigate malware and phishing threats faster.
Our Interactive Sandbox provides real-time behavioral analysis of suspicious files and URLs, helping analysts identify malicious activity, investigate attacks, and make informed response decisions.
ANY.RUN Threat Intelligence Lookup and Threat Intelligence Feeds complement behavioral analysis with threat data from real-world investigations, helping organizations strengthen monitoring, triage, incident response, and threat hunting.
0 comments