Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
83
Global rank
95 infographic chevron month
Month rank
70 infographic chevron week
Week rank

Raccoon is an info stealer type malware available as a Malware as a Service. It can be obtained for a subscription and costs $200 per month. Raccoon malware has already infected over 100,000 devices and became one of the most mentioned viruses on the underground forums in 2019.

Stealer
Type
ex-USSR
Origin
1 February, 2019
First seen
12 October, 2026
Last seen
Also known as
Mohazo
Racealer

How to analyze Raccoon with ANY.RUN

Type
ex-USSR
Origin
1 February, 2019
First seen
12 October, 2026
Last seen

IOCs

IP addresses
40.126.31.3
92.123.104.18
48.209.133.15
95.169.205.186
172.211.123.250
2.21.20.150
40.126.32.76
92.123.104.17
48.209.138.189
74.178.76.128
135.232.92.97
23.52.181.212
89.185.85.53
92.123.104.31
20.165.94.63
48.209.138.168
142.251.150.119
92.122.215.95
151.101.1.91
49.13.77.253
Hashes
d56587f01ef3ef0c4af3d5fde831fd6a04de133d599604ace8fcda9bbc9d0862
6f8ae6d8046764d29a23ccb306fbd0053aae28f281550927ee070cd0e2e9715d
5dcd36a5c107b362b96358361d5841b445e0bbb1a52fb9b0238facb537293426
9beb662fc210c37a95bcf7576a505e0a00ad2747759c5cd1e5c3651b4761c6a2
f0c5ccd7bba16a735ceccece243cc08b8700d966fb9fac908de7f10b362dc93b
9cd6bec1def9f1147de9fcb0b8c16f329b6873704072e7512e63fb0a1b82bb1b
e9b2b8ba6e99a66f316d56d7b6b23c6ae1ff9e1651ea19b1c666549d21e9b623
012d0d42f927953f170062c14d958f0997810a22aae169227eba99fd117fecc7
7daf73fb5ecdb4a5932ca00b250e912b02396a83651ec7057dc67fb399fc26cf
21b53dda90fb2041aa77a317643f10bca79a9dc0d8b3738823cd0ac8883c1ce1
f323bdadf5f28410587616681874d55719535e4f146a8fb9fc4a19a697e17d83
6205a0584082a825a046e733e34760f37cc2b7c1e4b2b921b7e317e5c1454bec
e6949f0dd2e1269355e6c04feaa94fc90675f3bf4b6f38a35eed06efccd721a8
a205aef94126376ea355b4e7a76229c6c18fc8ba1d925f5f1453a7446d972eff
a81992a770e09293af9cc1cbaa3c637cde13352edbc504c065d83e69d9bc9b6a
8e0f9d4673cd0909710ee621caafa614b2fa8a2f55e6dee23d948610bd7144a5
d770c3e77c587a6d10707750e63332927d46316d7909760fa94bc8a00b5823ff
4ecbf7114883cfbb77ecb4e0008ab1f6d2b06c5ba727ae4ec551962af61e0d36
c8f44feab6fe509590eb2e6cee2efbd9fbe9119d5c91da9a105bad75863dbe34
e7103164b532a7e095f652e9f6a93a9e929eae88a4022e34c5eed980c65c3d34
Domains
settings-win.data.microsoft.com
ecs.office.com
google.com
login.live.com
slscr.update.microsoft.com
www.microsoft.com
self.events.data.microsoft.com
crl.microsoft.com
fe3cr.delivery.mp.microsoft.com
www.bing.com
messaging.lifecycle.office.com
teleta.top
officeclient.microsoft.com
mozilla.map.fastly.net
normandy.tombstone.experimenter.prod.webservices.mozgcp.net
safebrowsing.googleapis.com
nexusrules.officeapps.live.com
www.facebook.com
star-mini.c10r.facebook.com
www.google.com
URLs
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://89.185.85.53/
http://teletop.top/agrybirdsgamerept
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/web/xlsc.aspx?t=5&dl=1&f=9&wsbc=1
https://officeclient.microsoft.com/config16/?lcid=1033&syslcid=1033&uilcid=1033&build=16.0.16026&crev=3
https://ecs.office.com/config/v2/office/word/16.0.16026.20146/production/cc?&clientid=%7bd61ab268-c26a-439d-bb15-2a0dedfca6a3%7d&application=word&platform=win32&version=16.0.16026.20146&msoversion=16.0.16026.20002&sdx=fa000000002.2.0.1907.31003&sdx=fa000000005.1.0.1909.30011&sdx=fa000000006.1.0.1909.13002&sdx=fa000000008.1.0.1908.16006&sdx=fa000000009.1.0.1908.6002&sdx=fa000000016.1.0.1810.13001&sdx=fa000000029.1.0.1906.25001&sdx=fa000000033.1.0.1908.24001&sdx=wa104381125.1.0.1810.9001&processname=winword.exe&audience=production&build=ship&architecture=x64&language=en-us&subscriptionlicense=false&perpetuallicense=2019&licensecategory=6&licensesku=professional2019retail&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7b4be2475d-bf31-4467-8da7-54ba2528fe44%7d&labmachine=false
https://roaming.officeapps.live.com/rs/roamingsoapservice.svc
https://omex.cdn.office.net/addinclassifier/officesharedentities
https://fs.microsoft.com/fs/4.27/flatfontassets.pkg
Last Seen at

Recent blog posts

post image
What's Really Attacking Your Industry? Insigh...
watchers 1619
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 9523
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 10768
comments 0

Raccoon is an information stealer malware — a virus that threat actors use to retrieve sensitive data from infected machines. Also known as Mohazo and Racealer, this is a modern malware that was first sighted in 2019.

Although some consider this a relatively basic malware, excellent service from creators, who distribute it as malware as a service and a user-friendly, simplistic dashboard, helped make Raccoon quite popular. In fact, the malware has already managed to infect upwards of 100,000 devices and became one of the most mentioned viruses in hacker communities.

General description of Raccoon malware

Raccoon malware comes with fairly basic info stealer functions like RedLine and by itself lacks any kind of antivirus protection. There are also no functions that would complicate the analysis of the malware. However, Raccoon developers do suggest using a third-party crypter.

When it comes to the core functionality this virus depending on the configuration enabled by an attacker, can check system settings, capture screenshots, collect basic information like OS version, IP and username and steal passwords and logins from a variety of browsers. On top of that, the stealer can retrieve information from Microsoft Outlook as well as steal cryptocurrency wallets.

When the data collection process ends the data is packed into a .ZIP archive that is then sent to the attackers' server.

The functions described above are rather basic, however, reportedly excellent service provided by the malware creators helped make this virus quite popular. The team behind this virus pushes out constant improvements and fixes based on user feedback.

By providing an easy-to-use dashboard Raccoon developers ensured that even non-technically savvy attackers can operate this malware successfully by customizing its configurations effortlessly. Hundreds of thousands of infected victims in a matter of months since the malware’s release is the result.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Speaking of the team behind Raccoon. The identities of the people behind this virus are a mystery, but some known members of the hacker community are known to have connections with this virus. Evidence suggests that one of the people behind Raccoon is known in the online community as glad0ff. A long known hacker who is responsible for the development of multiple malicious programs like crypto miners and RATs.

However, he does not seem to be working alone as some information about the disputes within the team has been leaked online. For instance, in one message an individual accuses someone-else from the of stealing from a common account, leaving the project, and attempting to scam customers.

There is also reason to believe that Raccoon was developed by Russian-speaking hackers. This is suggested by mistakes in the English language found in the control panel as well as the fact that the malware stops execution if it detects that the victim is from Russia, Ukraine, Belarus, Kazakhstan, Kyrgyzstan, Armenia Tajikistan, or Uzbekistan. In addition, technical support is available in Russian and English languages, which also points to a potential x-USSR origin of the attackers.

Raccoon malware analysis

A video available in the ANY.RUN malware hunting service shows how a machine gets infected with Raccoon in real-time.

Read a detailed analysis of Raccoon Stealer 2.0 in our blog.
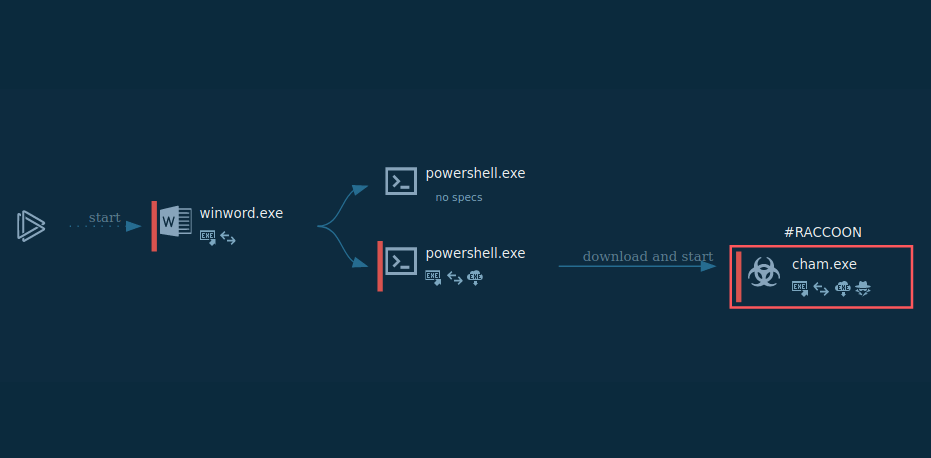
raccoon_process_graph

Figure 1: Here we can see the execution process of Raccoon. This graph was created in ANY.RUN.
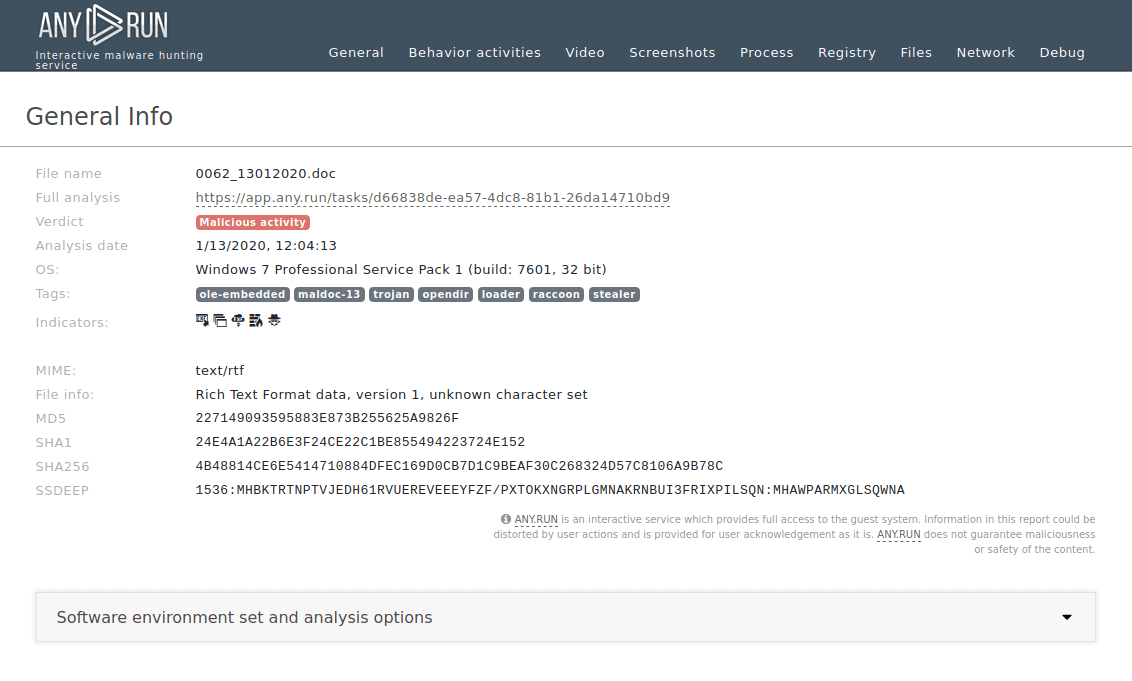
racoon_text_report

Figure 2: Shows a text report that can help collect data about the malware execution in one place or make a presentation.

Raccoon execution process

Since Raccoon malware is a pretty standard example of a stealer-type malware, its execution process does not exactly stand out. In our analysis case, after the malware made its way into the infected system (does not matter which delivery method it would use) it downloaded additional modules from the Internet. These modules are mostly DLL dependencies which Raccoon requires to work correctly. After that, the malware began stealing information from browsers and the system and stored stolen data in an archive file. The file, in turn, was sent to the C2 server. Probably the same C&C server it was built in. Note that some versions of the Raccoon malware delete themselves after execution while others don't.

Raccoon stealer distribution

Raccoon stealer malware is distributed using multiple channels like browsers, however, the most popular destruction method is through the use of exploit kits. Attackers can even manage campaign configurations via the control panel. The malware utilizes mainly the Fallout exploit kit. This delivery method makes it possible for the infection to occur even without active user interaction — victims get infected while simply surfing the web.

The malware also makes its way to victim’s PCs Microsoft Office document attachments that are being distributed in mail spam campaigns. The contaminated document contains a macro that downloads the malware when enabled.

In addition, hackers have set up a Dropbox account where the malware is stored inside a .IMG file. Attackers use social engineering to trick victims into opening a malicious URL and download the infected file.

Finally, the last distribution method is “bundled malware”. When users download real software from suspicious websites sometimes Raccoon comes as an unwanted part of the package bundled with the legitimate program.

How to detect Raccoon using ANY.RUN?

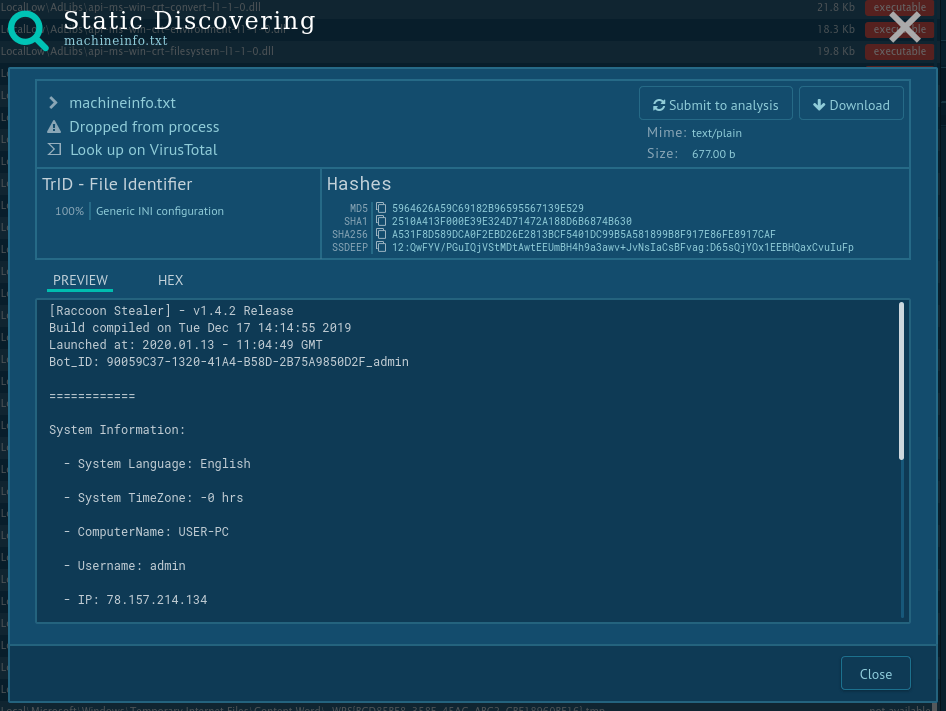
Some malware creates files in which it named itself. You can find such info about Raccoon malware trojan using ANY.RUN's "Static Discovering". Open either the "Files" tab in the lower part of the task's window or click on the process and then on the button "More Info" in the appeared window. After that, all you need to do is just click on the file.
raccoon_static_discovering

Conclusion

While Raccoon malware is not a very technically advanced malicious program like Ursnif or Hawkeye, Raccoon sure made a lot of noise in the underground community in 2019, when it was first released. Available as a service for $200 per month, it came equipped with everything necessary to start a malware attack. And if a customer couldn’t do it on their own, they could always get support from the team behind this malware.

In fact, underground forums are filled with raving feedback about the excellent work of Raccoon support staff. Some even say that they were treated like real VIPs.

Developers have also shown that they are capable of rolling out updates very quietly and promise to upgrade the malware with Keylogger functionality in the near future.

While technical simplicity makes this threat relatively easy to defend against at the moment, growing popularity, extreme ease of use, and potential future improvement certainly suggest that this malware can become a big phenomenon. Some even say that Raccoon will replace Azorult.

ANY.RUN malware hunting service provides researchers with the ability to study samples of Raccoon in a controlled interactive environment and learn as much as possible about this malware. Hopefully, together we will neutralize or at least medicate the fallout from this and other cybersecurity threats.
HAVE A LOOK AT

DoubleTrouble screenshot
DoubleTrouble
doubletrouble
DoubleTrouble is a new-generation Android malware designed to quietly infiltrate mobile devices, harvest sensitive data, hijack financial operations, and maintain long-term persistence. Unlike commodity Android trojans, it blends advanced evasion, dual-stage infection, and dynamic payload updates, making it a rising mobile threat for both consumers and organizations.
Read More
Spynote screenshot
Spynote
spynote
SpyNote, also known as SpyMax and CypherRat, is a powerful Android malware family designed primarily for surveillance and data theft, often categorized as a Remote Access Trojan (RAT). Originally emerged in 2016, SpyNote has evolved significantly, with new variants continuing to appear as recently as 2023–2025.
Read More
Stealer screenshot
Stealer
stealer
Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns.
Read More
BlackMoon screenshot
BlackMoon
blackmoon
BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.
Read More
Trojan screenshot
Trojan
trojan trojan horse
Trojans are a group of malicious programs distinguished by their ability to masquerade as benign software. Depending on their type, trojans possess a variety of capabilities, ranging from maintaining full remote control over the victim’s machine to stealing data and files, as well as dropping other malware. At the same time, the main functionality of each trojan family can differ significantly depending on its type. The most common trojan infection chain starts with a phishing email.
Read More
Qilin Ransomware screenshot
Qilin ransomware (predecessor known as “Agenda”) is a rapidly evolving ransomware-as-a-service (RaaS) operation targeting organizations worldwide. Known for double extortion tactics (encrypting files while also threatening to leak stolen data) Qilin has quickly gained notoriety for its customization, flexibility, and impact on critical infrastructure.
Read More