Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
121
Global rank
112 infographic chevron month
Month rank
73 infographic chevron week
Week rank

Hawkeye often gets installed in a bundle with other malware. This is a Trojan and keylogger that is used to retrieve private information such as passwords and login credentials. This is an advanced malware that features strong anti-evasion functions.

Keylogger
Type
Unknown
Origin
1 January, 2013
First seen
5 October, 2026
Last seen
Also known as
Predator Pain
HawkEye Reborn

How to analyze Hawkeye with ANY.RUN

Type
Unknown
Origin
1 January, 2013
First seen
5 October, 2026
Last seen

IOCs

IP addresses
23.11.41.157
104.86.59.63
57.153.246.3
104.86.35.74
20.190.160.131
135.232.92.137
2.19.122.21
2.19.11.122
74.178.240.51
128.24.231.65
204.79.197.203
172.211.123.248
2.19.122.22
23.209.214.100
2.19.11.101
23.59.18.102
48.209.6.48
2.16.204.160
2.23.246.9
20.190.159.73
Hashes
2df94dc1c58e952a1ebd1ae1185a291a8a573982ca90ec1bbb87b81126002668
e8f64f6f49b8231476e1028b75f2a3e5317ed506db6d1a265dbf3c28eb3e1d1a
6304d83ed98e2886606b9d2d692e79b91eff0e64d4b072b56c8d9d72ff4ae415
62099532750dad1054b127689680c38590033fa0bdfa4fb40c7b4dcb2607fb11
7056685ca86432159da135e5425d29a878f3e3b6366d3ac620dd693a39219c4f
6f1b1dab8bbbd0230cfbc01a22a6a72d6543c897e6408ed12f6535a0ae21ac0f
b3d510ef04275ca8e698e5b3cbb0ece3949ef9252f0cdc839e9ee347409a2209
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
e2118aee167eda03915eb961e0d72e46a4bbd56137eac54848d08dae4fd17c6d
b94f8ee5d6d8862eba179fb009895c4ec9d700dedcc75e4f5110fdb519893ec0
eda3eb55cd455e1ca9b5f997bd63307eae93827e9fe62513311201dca92f2321
f471b5df4052842492dda7f04cc17992f5d169ae1ef7c1acb515fe80acfda280
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
83b41e286d54ceb6832002be39f4c76dc6fb8ab40213c8cb43d823de1492fccc
61d7144128fcb51dcb95abc63f6d300654ba2f9162bbd781415b508a18a975ee
38d0f423e4089ea4202f1c1ba576f033f05a88dab38c8d527e8699a2aad5e80a
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
e908466af6563b62d8f8c4bc870beb33b8fdb8682bf7c775a40ea1c6a8f49bf5
b27632f6c07617e3de1115440c7dd6fde3364fccf5a14181df7fc8dfb83439df
4a4f02a2339d08f3cf660e2455d0739bd81d23810c6291a42fa90413ef5d4627
Domains
go.microsoft.com
ocsp.digicert.com
www.microsoft.com
self.events.data.microsoft.com
login.live.com
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
slscr.update.microsoft.com
activation-v2.sls.microsoft.com
settings-win.data.microsoft.com
oneocsp.microsoft.com
ecs.office.com
crl.microsoft.com
google.com
www.bing.com
nexusrules.officeapps.live.com
whatismyipaddress.com
licensing.mp.microsoft.com
smtp.gmail.com
cool3dmods.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 2189
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 4562
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 6963
comments 0

What is Hawkeye malware?

Hawkeye, also known as Predator Pain, is a dangerous trojan and keylogger - a malware used to steal information from PCs. It has very advanced detection evasion and information stealing functionality. Hawkeye can be combined with other malicious software to steal passwords from email clients and web browsers.

Available as a service on the dark web, Hawkeye can be used even by non-technically savvy attackers. In addition, this malware is known to have been advertised for some time on the general Internet on its own website, which today is unavailable. What’s more, the creators of Hawkeye have developed a unique business model in which intermediaries are used for reselling the malware.

General description of Hawkeye

Hawkeye keylogger is capable of stealing a variety of information from the victim's PC, including passwords from mail clients, web browsers, and bitcoin wallet information, as ransomware does. Furthermore, this malware can take screenshots, have a keylogger functionality, and retrieve data from the Internet download manager to employ JDownloader to steal passwords.

Predator Pain targets victims worldwide, but its attacks are being registered most often in the countries with the wealthiest economies, according to the GPD data, such as the USA, Canada, Italy, and others.

Hawkeye keylogger employs a sophisticated technique to stay hidden from the antiviruses called process hollowing. In essence, the Trojan generates a new instance of a harmless process to swap the native code with a malicious one subsequently. The 8 version of Hawkeye keylogger is different from previous iterations of the malware. Instead of running the main malicious code as a new process, the latest build injects the payload into MSBuild.exe, RegAsm.exe, and VBC.exe, which are a part of the .NET framework, enabling the virus to further disguises itself as a real and harmless process.

Another difference between the newest Predator Pain version from the older ones is that instead of being written in C, now it uses .NET and calls the native Windows API directly.

The primary function of the Hawkeye keylogger is to record the key and mouse presses along with window context and clipboard data. In addition, the malware has special modules that allow it to derive information from certain applications, including a popular video game Minecraft, the FTP client FileZilla and others.

Somewhat standardly, Predator Pain utilizes real BrowserPassView and MailPassView tools to save data from browsers and emails. In addition, the malware is able to activate and take control of the webcam if the infected machine has one connected.

To prevent detection and analysis, Hawkeye comes equipped with a series of anti-evasion tools besides processes hollowing. For instance, the malware sets a delay before being executed, which helps it trick some of the automated sandbox analysis tools. It also comes equipped with a technique that targets specific antivirus processes and stops them from executing and blocks access to several domains used by antivirus programs for updating.

What’s more, the malware takes active steps to prevent the victim from disabling its own processes by taking control over command prompt, registry editor, and task manager. At the same time, Hawkeye constantly scans the computer for other malicious programs and instantly deletes them if found.

Hawkeye keylogger malware analysis

The execution process of the Predator Pain keylogger can be reviewed in a lot of detail in a video recorded in the ANY.RUN malware hunting service
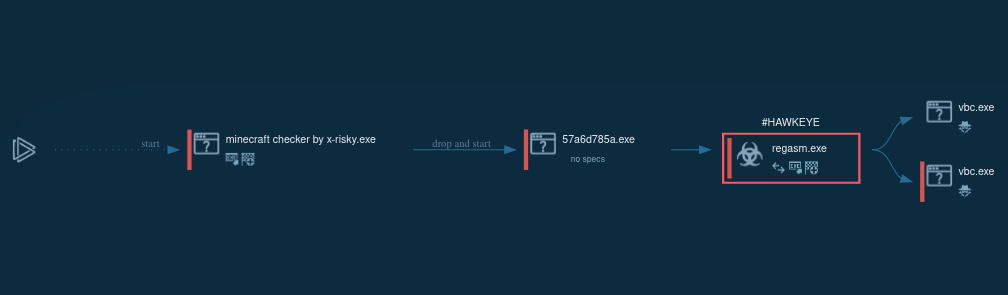
hawkeye execution process graph

Figure 1. a visual process graph generated by ANY.RUN allows reviewing the lifecycle of the Hawkeye quickly
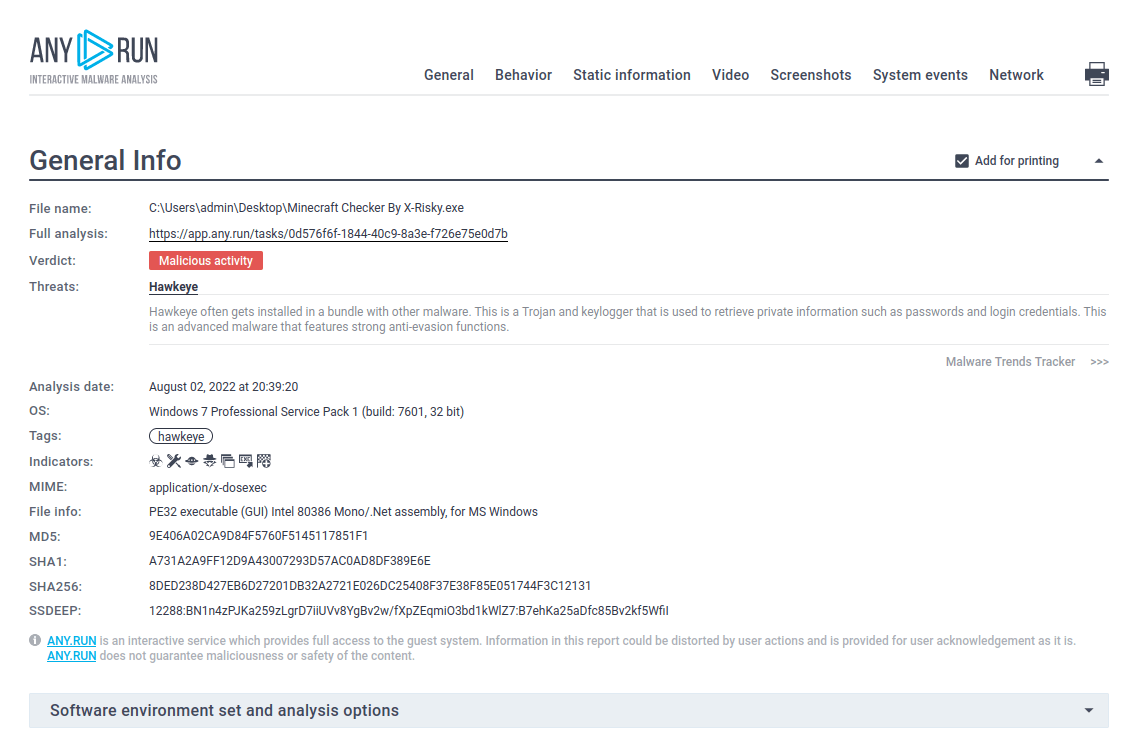
text report of the hawkeye malware analysis

Figure 2. ANY.RUN also allows researchers to generate customizable text reports which are a great way to present the analysis results
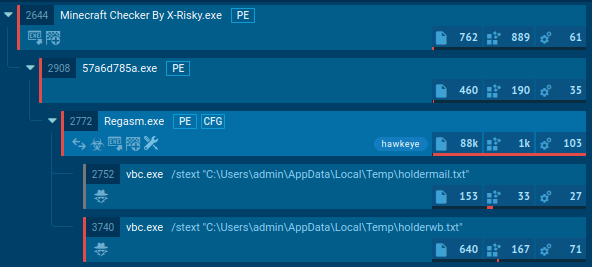
Hawkeye execution process

hawkeye execution process tree

Figure 3. Execution processes of Hawkeye as displayed by the ANY.RUN malware hunting service

Hawkeye keylogger often reaches users' devices through phishing emails, most commonly as a malicious Microsoft Office file, such as Docx file. After the user opens the downloaded file, it either asks the user to enable macros or uses vulnerabilities to download and execute the main payload. In most cases, it downloads itself into the %AppData% folder. To maintain its presence, the malware adds itself to the autorun registry. It also uses process hollowing to hide its code in legitimate processes. For example, the 8 version of Hawkeye, presented in this task from our simulation, injects itself into MSBuild.exe, RegAsm.exe, or VBC.exe. Before sending information to the control server, Hawkeye saves stolen data in Tmp files into the %Temp% folder. Usually, these Tmp files are deleted after the information is sent to a control server.
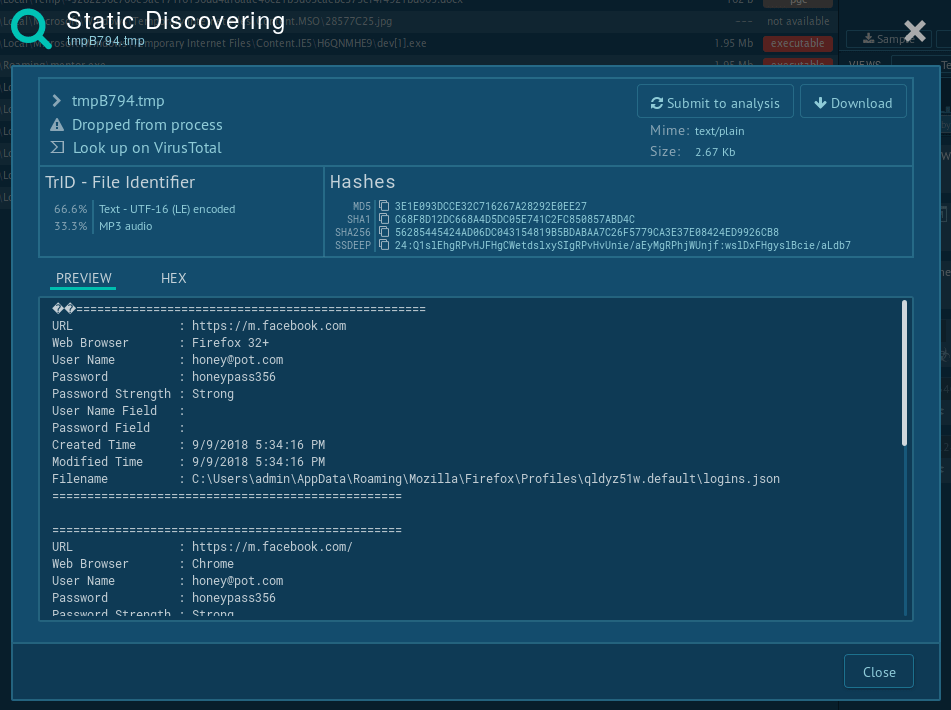
stolen by hawkeye data saved in tmp file

Figure 4. Information saved in .TMP file

How to avoid infection by Hawkeye?

Following some common online hygiene guidelines is a good way to stay safe from getting infected with Hawkeye. In addition, users should be careful when downloading free software from unknown or suspicious websites and carefully check the URLs when downloading any software in general.

In addition, after receiving a suspicious email or an email from an unidentified sender, users should be cautious when downloading attachments. Although the opened document prompts the user to enable macros or activate the editing, users must never follow these instructions as they most likely indicate the file's malicious nature.

Distribution of Hawkeye

Hawkeye trojan uses multiple distribution methods, including packaging within free downloadable programs or disguised as legitimate software. Hawkeye can also be installed on the victim’s PC manually if the attacker gains remote or physical access to the machine.

However, the most commonly used distribution method is email phishing, the same as ransomware, where the malware is distributed as a malicious attachment, usually a Microsoft Word document. The technique is used by different malware, including Ursnif and Raccoon. Known phishing campaigns usually revolve around notifications regarding an issue with a real product, quotation requests, payment orders, or random or personal, disturbing topics aimed at tricking the victim into downloading the attachment.

In most cases, the Microsoft Office opens the document with a warning, and Hawkeye displays a message prompting to enable editing. Thus, the user must interact with to make the trojan start the execution process. However, in some other cases, the malware uses Microsoft Office exploits, allowing Hawkeye to start the execution without any user interaction.

How to detect Hawkeye using ANY.RUN?

Some versions of this malware create files that allow analysts to say for sure that this is Hawkeye. First, click on the malicious process in the process tree and then click the "More info" button. Then, in the upper-right corner of the "Events" panel, switch from "Friendly" to "Raw." Now you see all operations with files that were performed by a chosen process. Often, this malware family tries to create files with "Reborn" in their names. And based on that type, you can determine that it is Hawkeye.
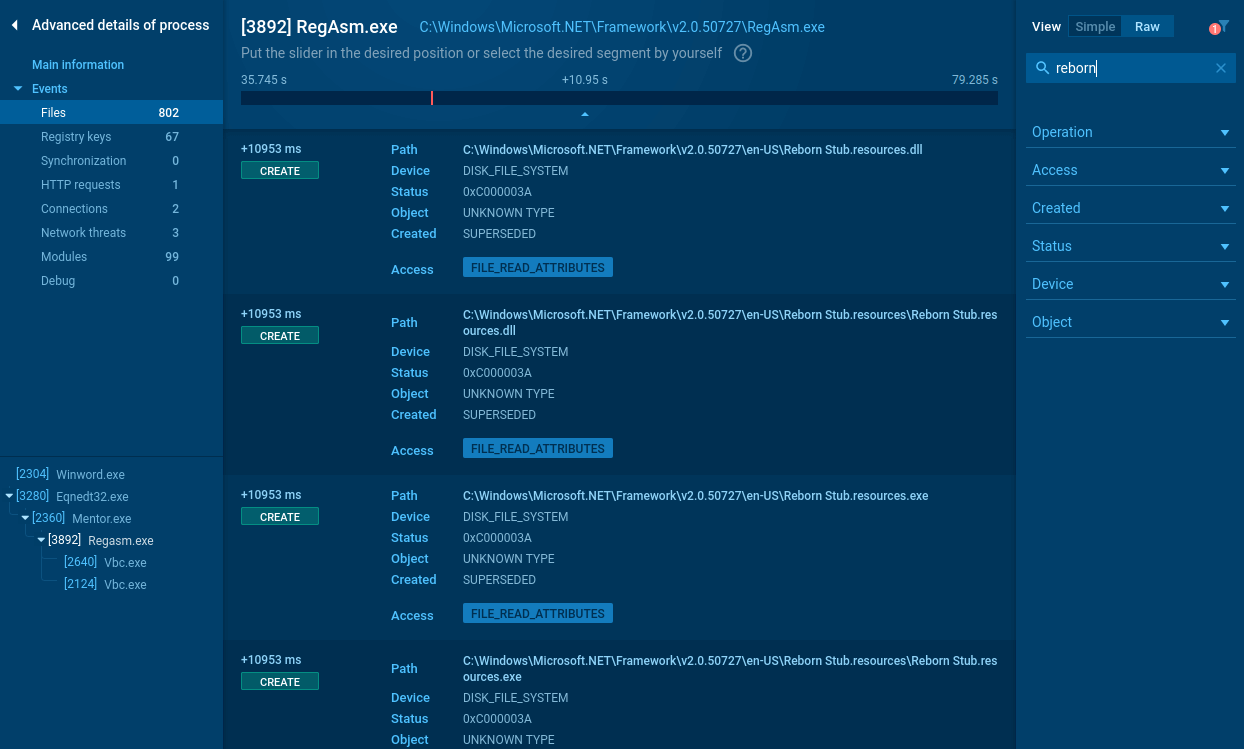
Files created by hawkeye Figure 5: Files created by Hawkeye

Conclusion

Carrying extremely advanced anti-evasion techniques and robust info-stealing functionality, Hawkeye presents a danger to corporations and individuals all around the globe. Unfortunately, the distribution of malware as a service allows even non-technically savvy cybercriminals to set up effective attack campaigns, contributing to the overall popularity of the virus.

Furthermore, Hawkeye trojan uses a set of special techniques to complicate the analysis and trick automated analysis services and confuse the development of countermeasures.

However, interactive analysis services like ANY.RUN gives researchers the ability to examine malware even as elusive as Hawkeye is and conduct effective studies.
HAVE A LOOK AT

Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Bumblebee Loader screenshot
Bumblebee Loader
bumblebee
Bumblebee is a highly adaptable malware loader, often used by threat actors linked to the Conti and TrickBot cybercrime groups. Since its discovery in 2021, Bumblebee has been leveraged in phishing campaigns and email thread hijacking, primarily to distribute payloads like Cobalt Strike and ransomware. The malware employs obfuscation techniques, such as DLL injection and virtual environment detection, to avoid detection and sandbox analysis. Its command-and-control infrastructure and anti-analysis features allow it to persist on infected devices, where it enables further payload downloads and system compromise.
Read More
Maze screenshot
Maze
maze ransomware
Maze is ransomware — a malware type that encrypts the victim’s files and restores the data in exchange for a ransom payment. One of the most distinguishable features of Maze is that it is one of the first malware of the kind to publicly release stolen data.
Read More
Sliver screenshot
Sliver
sliver
Sliver is an open-source command-and-control (C2) framework that has been increasingly adopted by threat actors as an alternative to tools like Cobalt Strike. Developed by security firm Bishop Fox, Sliver was initially intended for legitimate security testing and red teaming exercises. However, its robust features and open-source nature have made it attractive to malicious actors seeking to control compromised systems.
Read More
Virlock screenshot
Virlock
virlock
Virlock is a unique ransomware strain that combines encryption capabilities with file infection techniques. First observed in 2014, it stands out due to its polymorphic nature and ability to embed its code into compromised files, ensuring continued propagation. Once it infects a system, it encrypts files and locks the screen, demanding a ransom for file recovery and system access.
Read More
Lumma screenshot
Lumma
lumma
Lumma is an information stealer, developed using the C programming language. It is offered for sale as a malware-as-a-service, with several plans available. It usually targets cryptocurrency wallets, login credentials, and other sensitive information on a compromised system. The malicious software regularly gets updates that improve and expand its functionality, making it a serious stealer threat.
Read More