Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
103
Global rank
84 infographic chevron month
Month rank
82
Week rank

Orcus is a modular Remote Access Trojan with some unusual functions. This RAT enables attackers to create plugins using a custom development library and offers a robust core feature set that makes it one of the most dangerous malicious programs in its class.

RAT
Type
Canada
Origin
1 April, 2016
First seen
6 October, 2026
Last seen
Also known as
Schnorchel

How to analyze Orcus RAT with ANY.RUN

RAT
Type
Canada
Origin
1 April, 2016
First seen
6 October, 2026
Last seen

IOCs

IP addresses
23.11.206.107
48.209.138.189
23.3.89.112
135.232.92.97
23.11.41.157
172.211.123.249
48.209.133.15
20.190.160.132
23.207.210.139
204.79.197.203
23.52.181.141
20.165.94.63
23.52.181.212
40.126.32.134
48.192.1.65
52.110.17.34
2.16.204.141
184.24.77.40
40.126.31.1
172.211.123.248
Hashes
508bc318c5e27308ae8cdc011ba45d92b6105accbce30f4633042a7980da339e
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
ea856aa03f09f6e226c7275c60568c254e8747ae2c4df32c2229c2ea7f1137c0
8ec532d747658a59a84430d0589dbb2316036a7b656d4da7de157077b630a7ef
cb77920eccbfd294945a00bbb54988370227fac8590d9be0d7914aa5bd3695fd
16e962a419494bb753c1a241430fc85955ff2b2bbcc879abdfe2370fabbd28ac
c6b32680b20fcd3d907aa0fe4eef66b5709ac91704acd6bceef263457d46866e
f99ef5bf79a7c43701877f0bb0b890591885bb0a3d605762647cc8ffbf10c839
a709c2551b8818d7849d31a65446dc2f8c4cca2dcbbc5385604286f49cfdaf1c
5be04ac4fe549cb4bde2f93a01a54ef8aa18df6fbf612fcb33d6794f53d1eb34
9a30667f8a16794f3a5c4301bc1208356a3b9104dd2e3bbacbfe7ca62d05289e
0f3618ce0a669ebf70900aed21b75d5e15d9d347872ef8be8a8d8d0eb746de32
49d50c77702d159242179e5017f9d3be7d538680e7bc75564853ca41c0e913c5
75fdf3a98513bbe5f55d7846c2f618be92e5b49506f216261bf2e89f02492b0c
f93ea10f636d5e4c7a92a68cd0268fcec1ecbb277327591075a7034e5f28aecb
c3f0f957038af881e91a7192e53b2982c488754f8759324275e306eb1ba7d068
43b399ef4bcc5f1fa39dc0b5aff90181d6671552ebab494d3c217d75c62e29c6
58f6f67935c3f24cde4713753239b7c488d2a55792ed9f48708ccfd87acf782a
ab85eb0708ce9da16b55e7230114e83e4787a631eda6285e7369ee107b081055
78a0f229ed413e15b38e751d2926c67d722be14b8c951a0ac3e5e15b17f9346e
Domains
th.bing.com
nexusrules.officeapps.live.com
crl.microsoft.com
slscr.update.microsoft.com
login.live.com
google.com
activation-v2.sls.microsoft.com
edge.microsoft.com
officeclient.microsoft.com
fe3cr.delivery.mp.microsoft.com
ocsp.digicert.com
ecs.office.com
self.events.data.microsoft.com
settings-win.data.microsoft.com
www.bing.com
client.wns.windows.com
oneocsp.microsoft.com
www.microsoft.com
go.microsoft.com
firefox.settings.services.mozilla.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/dsb/scenario?name=trendingsearchwithcache&cc=us&setlang=en-us
https://login.live.com/ppsecure/deviceaddcredential.srf
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=t&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=1&cvid=0c3e9ce95abe4af097d0eb09f1d91ee1&ig=d60a14f1aef54ebbbb3973404b2706f9
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=ta&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=2&cvid=0c3e9ce95abe4af097d0eb09f1d91ee1&ig=fa1070452df54d7aade2393cb1efa451
https://www.bing.com/as/api/windowscortanapane/v2/suggestions?qry=tas&setlang=en-us&cc=us&nohs=1&qfm=1&seahisoff=1&cp=3&cvid=0c3e9ce95abe4af097d0eb09f1d91ee1&ig=f6d974140dd84e38ab5cba60483ec1b4
https://www.bing.com/web/xlsc.aspx?t=5&dl=1&f=9&wsbc=1
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Orcus RAT?

Orcus, previously known as Schnorchel, is a Remote Access Trojan, which enables remote control of infected systems. Although Orcus RAT malware is mostly a typical member of the RAT family, it has some competitive advantages over similar malware and unique features.

In addition, Orcus RAT has a modular structure, and it gives users the ability to create custom plugins for the malware. The modularity of this trojan gives it higher than standard scalability and management, allowing it to tailor the malware to the needs of various campaigns.

The first time we heard about this malware was from a forum post by one of its authors. The post announced the development of a new RAT that was named Schnorchel at the time. Soon after the announcement, the malware became commercially available under the name “Orcus RAT” and was presented to the public as legal software for remote administration, similar to Teamviewer. Interestingly, the authors claimed that the abbreviation RAT stood for Remote Administration Tool and not Remote Access Trojan.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

General description of Orcus RAT

Apart from a few exceptions, Orcus RAT malware has a relatively standard but robust feature set for a technologically advanced Remote Access Trojan. The malware can grab screenshots and record user input, activate the webcam, steal passwords, record audio, and steal information. In addition, Orcus comes with the ability to detect if it’s being launched on a virtual machine to complicate the analysis by security researchers.

The functions described above already make this malware quite capable. However, it offers a few unusual functions that enhance its functionality. Namely, the RAT in question supports plugins, and besides offering the ability to build them, it has a whole library of already created plugins that attackers can choose from. Furthermore, Orcus RAT plugins can be written in multiple languages, including C#, C++, and VB.Net.

To make the development of extensions more streamlined, malware creators rolled out a dedicated development environment. What’s more, those who lack the skills to build plugins from scratch on their own can follow detailed tutorials and benefit from well-maintained documentation libraries.

Additionally, Orcus had a Github page where authors have published samples of created plugins.

Another relatively unique feature that the malware authors packed into this virus is real-time scripting. Real-time scripting allows Orcus to write and run code on machines that it infected.

Speaking of Orcus RAT malware authors, we know that the virus was developed by a 36-year-old John Revesz, also known as “Armada" on the underground forums. In 2019, Canadian authorities accused Revesz of operating an international malware distribution scheme.

In his defense, Revesz claimed that the RAT is, in fact, a legitimate program for remote administration, and his company “Orcus Technologies” is a legal business. However, an examination of the functionality clearly revealed that the software is intended for malicious use cases, which resulted in the arrest of Revesz.

It is believed that Revesz wasn’t working alone. Therefore, a joint development effort theory makes sense, especially considering the technological complexity of certain aspects of this malware. For example, Orcus RAT consists of multiple components, with the control panel being a separate component. In addition, the server that the malware establishes a connection with after infection does not hold an admin panel. This architecture provides several advantages to the attackers, for example, the ability to share access to infected PCs from the same server. Additionally, it allows for greater scalability or infected networks.

Orcus RAT malware analysis

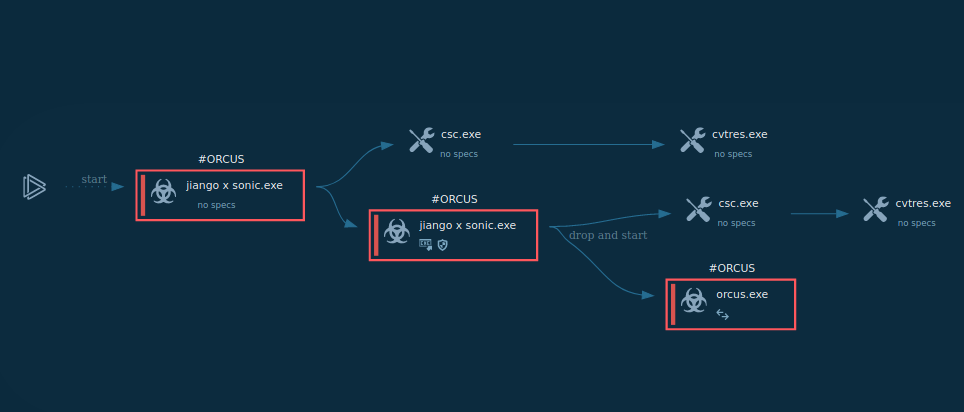
A video recorded in the ANY.RUN interactive malware hunting service displays the execution process of Orcus RAT in real-time.

Read a detailed analysis of OrcusRAT in our blog.
process_graph_of_orcus_rat_execution

Figure 1: Displays the execution process of the Orcus RAT. This visualization was generated by ANY.RUN.
text_report_of_orcus_rat_execution

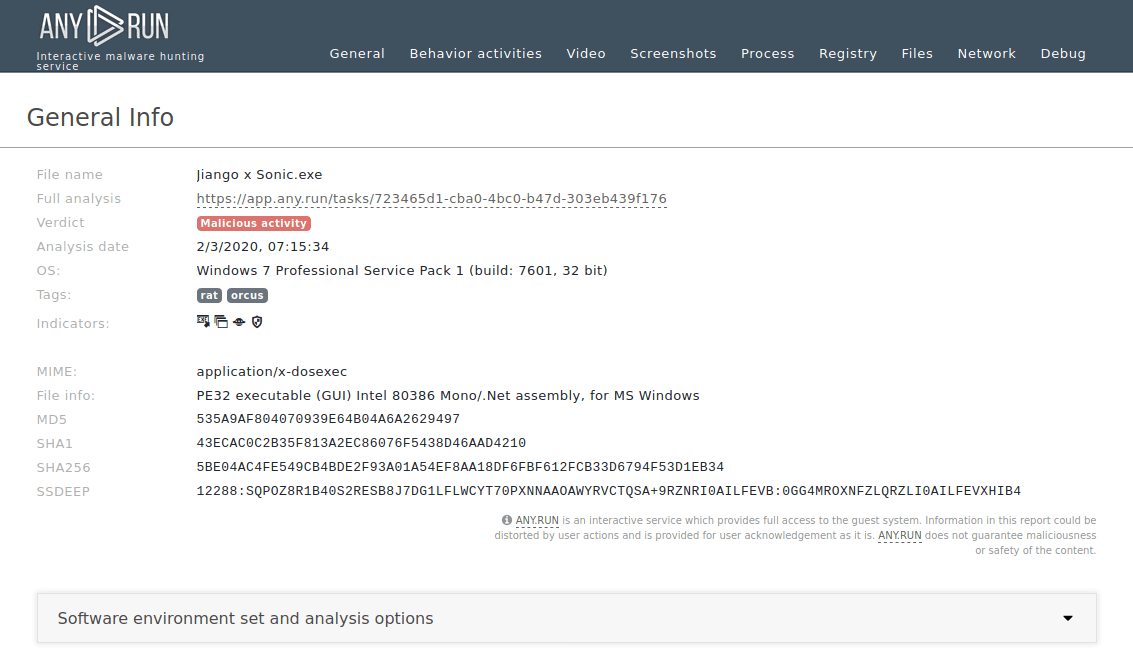
Figure 2: Displays a text report generated by ANY.RUN. Text reports are useful for demonstration and can be customized by a user to show necessary data.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Orcus RAT execution process

The execution process of the Orcus RAT is straightforward. This malware often disguises itself as a cheat code or crack, so it is mostly delivered to a system as an archive file with the compressed executable file inside. Since this trojan was written in C#, it often uses .NET infrastructure, available in Windows. To compile the C# source code, our sample started Visual C# compiler, which, in turn, started the Resource File To COFF Object Conversion Utility. After it was compiled, the executable file began its execution and malicious activity. Note that Orcus remote access tool does not always make its way into an infected system, as described above. In some cases, it comes as a precompiled executable file which only needs a user to double click on it to start the execution.

Orcus RAT malware distribution

Orcus RAT commonly makes its way into target machines as a downloadable attachment in malicious spam emails. Campaigns are often highly targeted and aim at organizations rather than at individuals.

Attackers use phishing and social engineering to trick victims into downloading an attachment or visiting a link that points to a server that holds the payload. In order to begin execution, Orcus does require user input. However, in most cases, it is unable to infect the system without user interaction.

How to detect Orcus RAT?

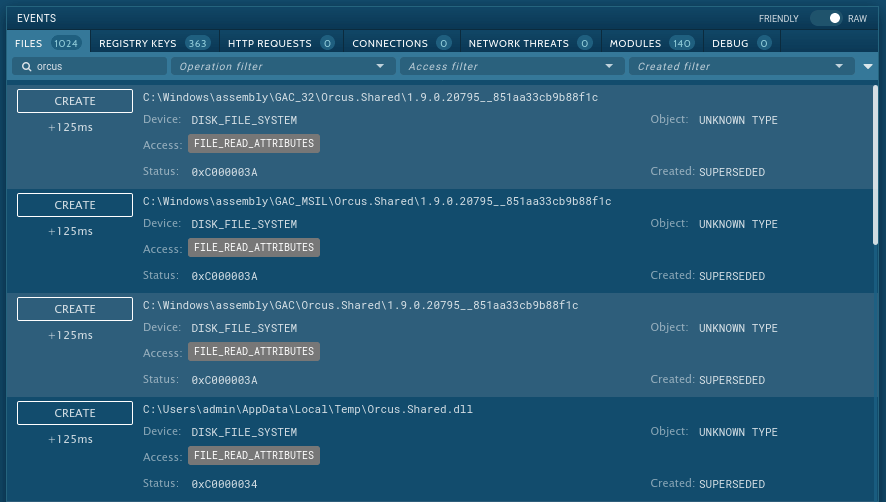
This malware creates files that allow analysts to detect it with a high degree of certainty. To identify the Orcus RAT, open the "Advanced details of process" by clicking on the "More info" button and switch events display to "Raw." This trojan often creates files with "Orcus" in the names, so all we need is to find such a file. To make it easier, type the word "Orcus" in the filename field. If such a file is found, you can be sure that Orcus RAT is in front of you.
files_created_by_orcus_rat

Figure 3: Files created by Orcus RAT

Conclusion

Orcus RAT malware is a sophisticated trojan that offers some unusual functions on top of solid basic info-stealing capabilities. Technical complexity was complemented by an affordable price of just 40 USD. Today, interested users can download a leaked version of Orcus for free. Unfortunately, this, along with excellent support and documentation, ensured the popularity of Orcus RAT.

Since its deployment in 2016, researchers have been observing Orcus RAT campaigns, and the popularity of this malware is still on the rise. As a result, we can expect several new attacks utilizing malicious software in the future.

Researchers can analyze Orcus RAT using the ANY.RUN malware hunting service to study this malware or other RATS such as Quasar RAT or njRAT. ANY.RUN is an interactive sandbox that allows researchers to stop and correct the simulation at any point, which ensures pure research results. In addition, useful information that can be obtained from the analysis can be added to our growing database of cyber threats to help combat internet crime worldwide.
HAVE A LOOK AT

Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
Bluesky Ransomware screenshot
BlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
Read More
BlackMoon screenshot
BlackMoon
blackmoon
BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.
Read More