Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

SVCStealer

145
Global rank
160 infographic chevron month
Month rank
125 infographic chevron week
Week rank

SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.

Stealer
Type
Unknown
Origin
1 January, 2025
First seen
6 October, 2026
Last seen

How to analyze SVCStealer with ANY.RUN

Type
Unknown
Origin
1 January, 2025
First seen
6 October, 2026
Last seen

IOCs

IP addresses
48.209.138.168
23.32.238.120
23.11.41.157
131.253.33.203
23.3.89.97
48.192.1.64
2.21.239.138
40.126.32.76
74.178.240.61
48.209.138.189
23.59.18.102
74.178.76.54
172.211.123.248
192.162.199.186
57.153.246.3
40.126.31.129
48.192.1.65
2.16.241.218
20.165.94.54
23.52.181.141
Hashes
ca62ac5062da0659d8e6fca164a102d2d9f9ef8c4d461fce5459560b4c30270e
4412319ef944ebcca9581cbacb1d4e1dc614c348d1dfc5d2faaaad863d300209
1513329660c876e166fde7919d705ecfa5339732849159685c59847be92b7478
5163454ca221b153694829adb542ce7b41a2759659c5da04a8df7c0e7c541560
5c2c6f73710215dca493e1bfc6fd84aedc3e11eb13069f8b4b1fee5fe49e9b73
83ad6ea5c240002d70a2fa3df1f50a91d87dcc5cc157e71a3c845748fbe61ef3
d5e2baf51b4d9aa0467a6bb851ba7b3a6015e5414b46c68b7b9f07c93f75b16a
02a19cc446e25ce84b7fd8ea98e2a59d661805be4bee15e048d4220c743e650c
fd8e10b611964ed2299c8e33b501dc8877a59fbc1fa9567e582a380e8b6eddcf
138167d8f03d48e88da0aec3df38f723bc1895822f75660cccb5e994814bee90
9976b3be2bccc1e252ab830916d22d705464c051e0dea8cbf5b7c180507b1007
9c0e7f829b46760aab20eda352a6429d98dd902feb26614737dc696ebc7d690e
79539b128a136f2ce914b307520916f89df2df1286f4e465a6ea726ea934b056
ffe8bad1f958e9a02f8194398c94f44db3d5c51ee0a9501efbbd8ffe8caf08e5
eb6b03c0d1bc65588af02ef11cd1b2d32814979cee1e538cbc962e17282f5aba
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
fbacc64c19e482e225d7f9042d191345ea63af2d42d547c66c07d5ee6e01e46c
4acd7adff5c2193e7b0b9a6f8235534d67772ff3d7fa59b1215de011d7455ad9
df3934740546e59befa158654a31f97380629af8a19966e8af135a1840925fd6
14219a41f1e1b3d5a3081e8b3369f5ef05fe41bba5b9fd08b98b18bbdab1ecf3
Domains
ecs.office.com
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
crl.microsoft.com
slscr.update.microsoft.com
www.bing.com
settings-win.data.microsoft.com
self.events.data.microsoft.com
google.com
oneocsp.microsoft.com
th.bing.com
login.live.com
activation-v2.sls.microsoft.com
www.microsoft.com
ocsp.digicert.com
watson.events.data.microsoft.com
go.microsoft.com
nexusrules.officeapps.live.com
edge.microsoft.com
arc.msn.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://196.251.107.186/svbia/post.php
http://192.162.199.186/svbia/post.php
http://62.60.226.232/svbia/post.php
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 4611
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 6582
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 9728
comments 0

What is SVCStealer?

SVCStealer, an information-stealing malware, was first identified in late January 2025 by SEQRITE researchers. It is written in Microsoft Visual C++ and designed to harvest sensitive data from compromised systems:

  • Login credentials from browsers and other applications.
  • Financial data, such as credit card and cryptocurrency wallet details.
  • Personal files and system information, which can be used for identity theft or sold on dark web forums.
  • Messaging app data from platforms like Discord and Telegram, enabling further social engineering attacks.

SvcStealer focuses both on individuals and on business sectors with valuable data, such as finance, telecommunications, and healthcare. It primarily gains access through spear phishing attacks, where malicious email attachments trick users into executing the malware. These attachments often masquerade as legitimate files to exploit user trust. Social engineering is also engaged with messages posing as legitimate communications, often mimicking trusted entities like Google Meet or medical centers.

Once executed, the malware establishes a foothold on the victim's system and connects to C2 servers to receive further instructions or exfiltrate data. It does not rely on complex network infiltration but uses phishing as the primary vector.

SvcStealer maintains persistence by continuously beaconing to its C2 server, awaiting further commands, which may include downloading additional payloads.

It does not rely on traditional persistence mechanisms like registry modifications or scheduled tasks but ensures ongoing communication with its C2 server using backup IP addresses if the primary connection fails.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

SVCStealer’s Business Impact

  • Data Theft: Loss of sensitive personal and financial information, leading to identity theft, financial fraud, or data sales on underground forums.
  • Operational Disruption: Termination of monitoring processes can hinder system administration, delaying detection and response.
  • Secondary Infections: As a gateway for additional malware, SvcStealer can escalate initial breaches into more severe incidents, such as ransomware or backdoor deployment.
  • Financial Loss: Stolen financial data or cryptocurrency can result in direct financial losses for individuals or organizations.

SVCStealer Execution Process and Technical Details

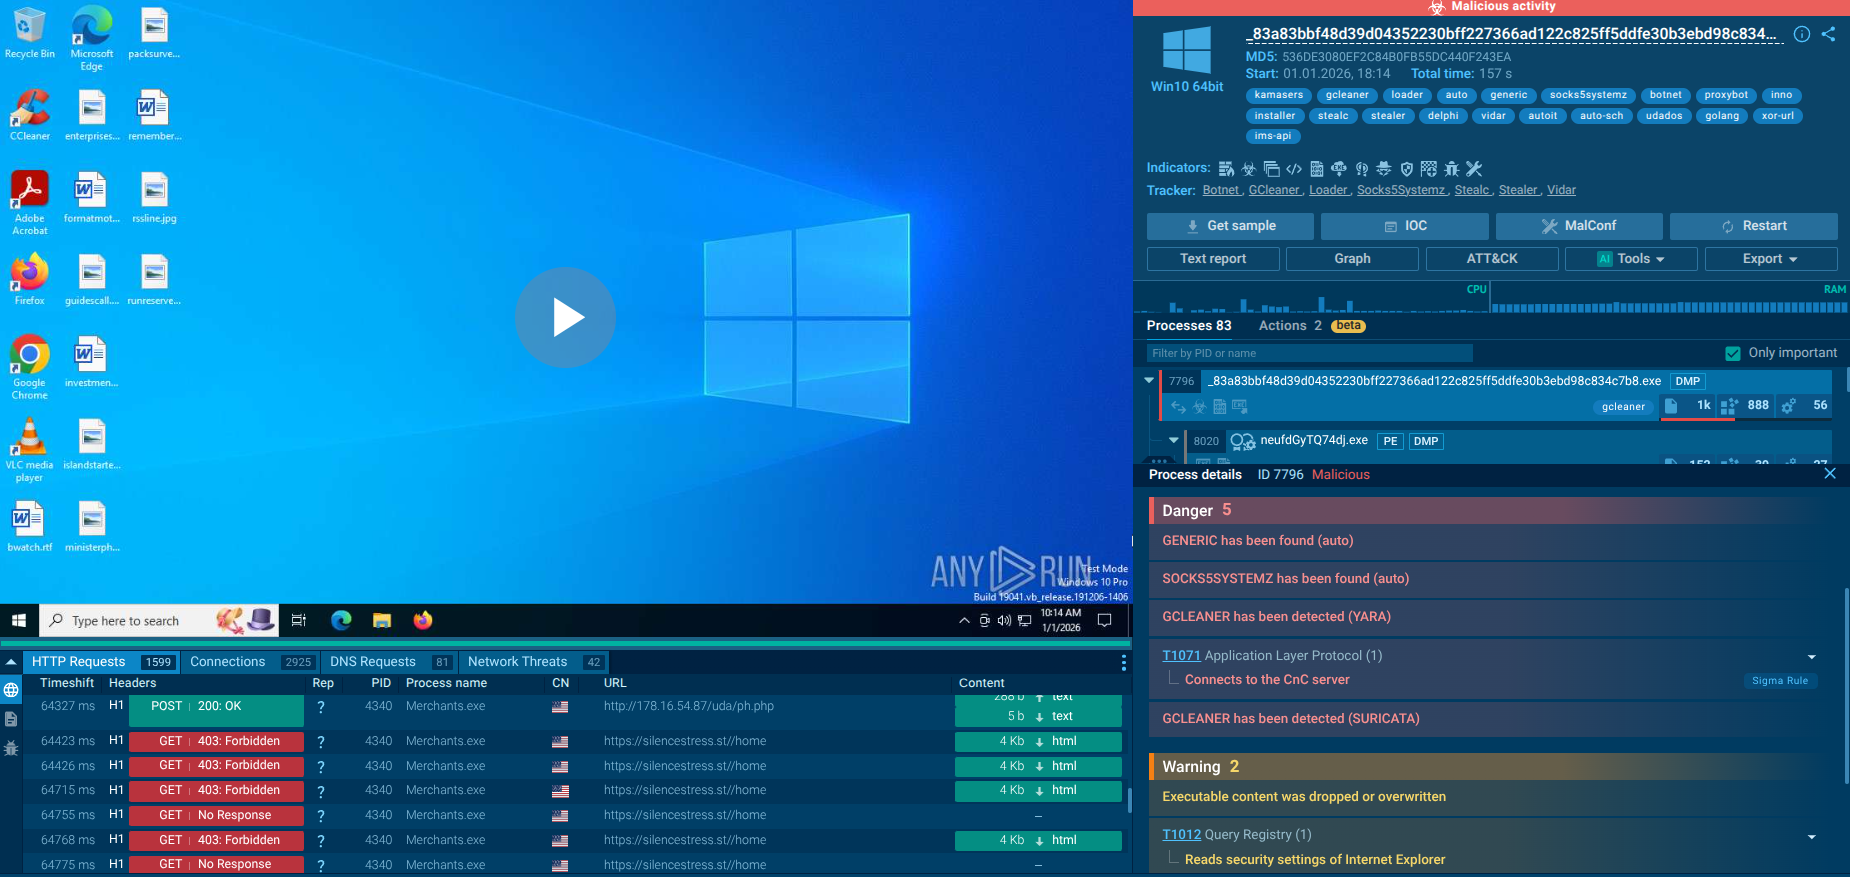
In spite of being quite recently discovered, SVCStealer has already been actively researched by ANY.RUN’s Interactive Sandbox users including over 500,000 threat analysts and 15,000 SOC businesses. We can choose a public analysis session of the stealer’s sample and watch its execution chain:

View the analysis and gather actionable data.
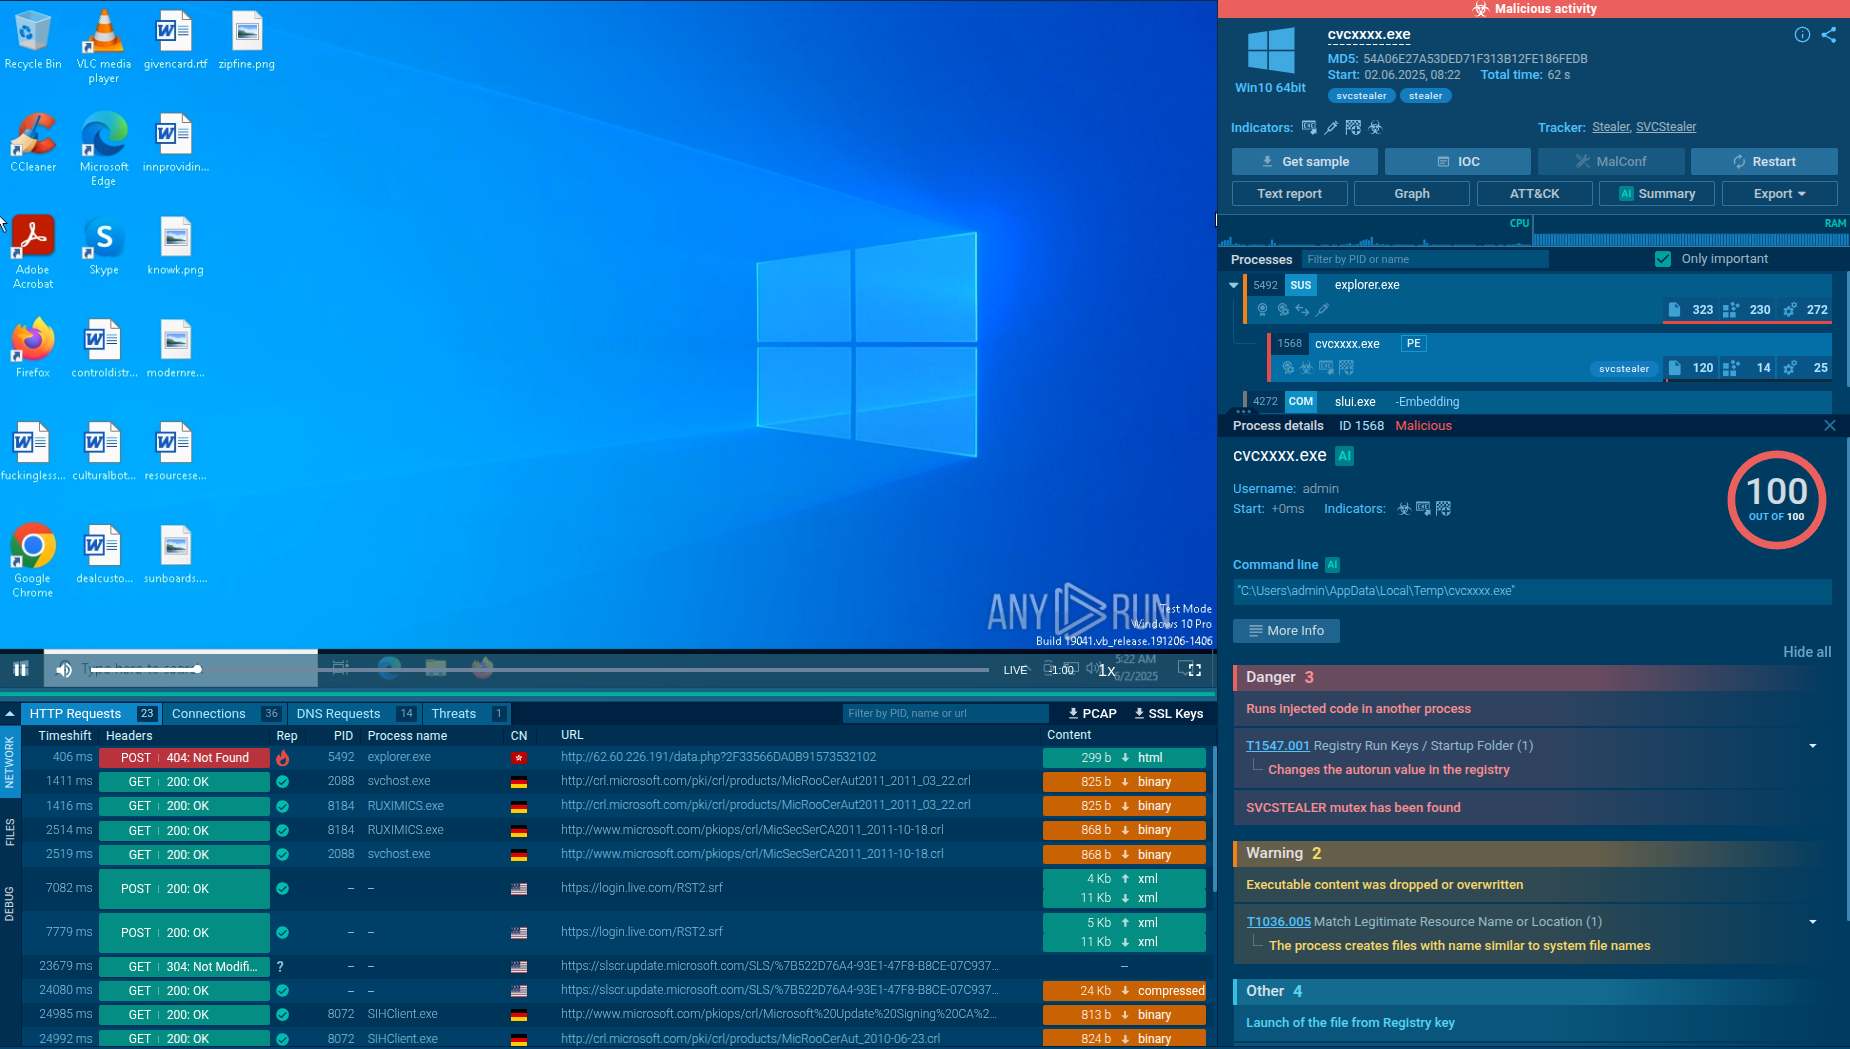
SVCStealer analysis in ANY.RUN Sandbox SVCStealer sample in ANY.RUN's Interactive Sandbox

SvcStealer is primarily distributed via spear-phishing emails that contain malicious documents or executables. When executed, it generates a unique 11-character alphanumeric folder name derived from the volume serial number of the infected system’s root directory. This folder is created in either the “C:\ProgramData” or “%AppData%” path. This method ensures that only one instance of the malware runs on the system. If the folder already exists, SvcStealer terminates itself to prevent multiple infections, functioning similarly to a mutex.
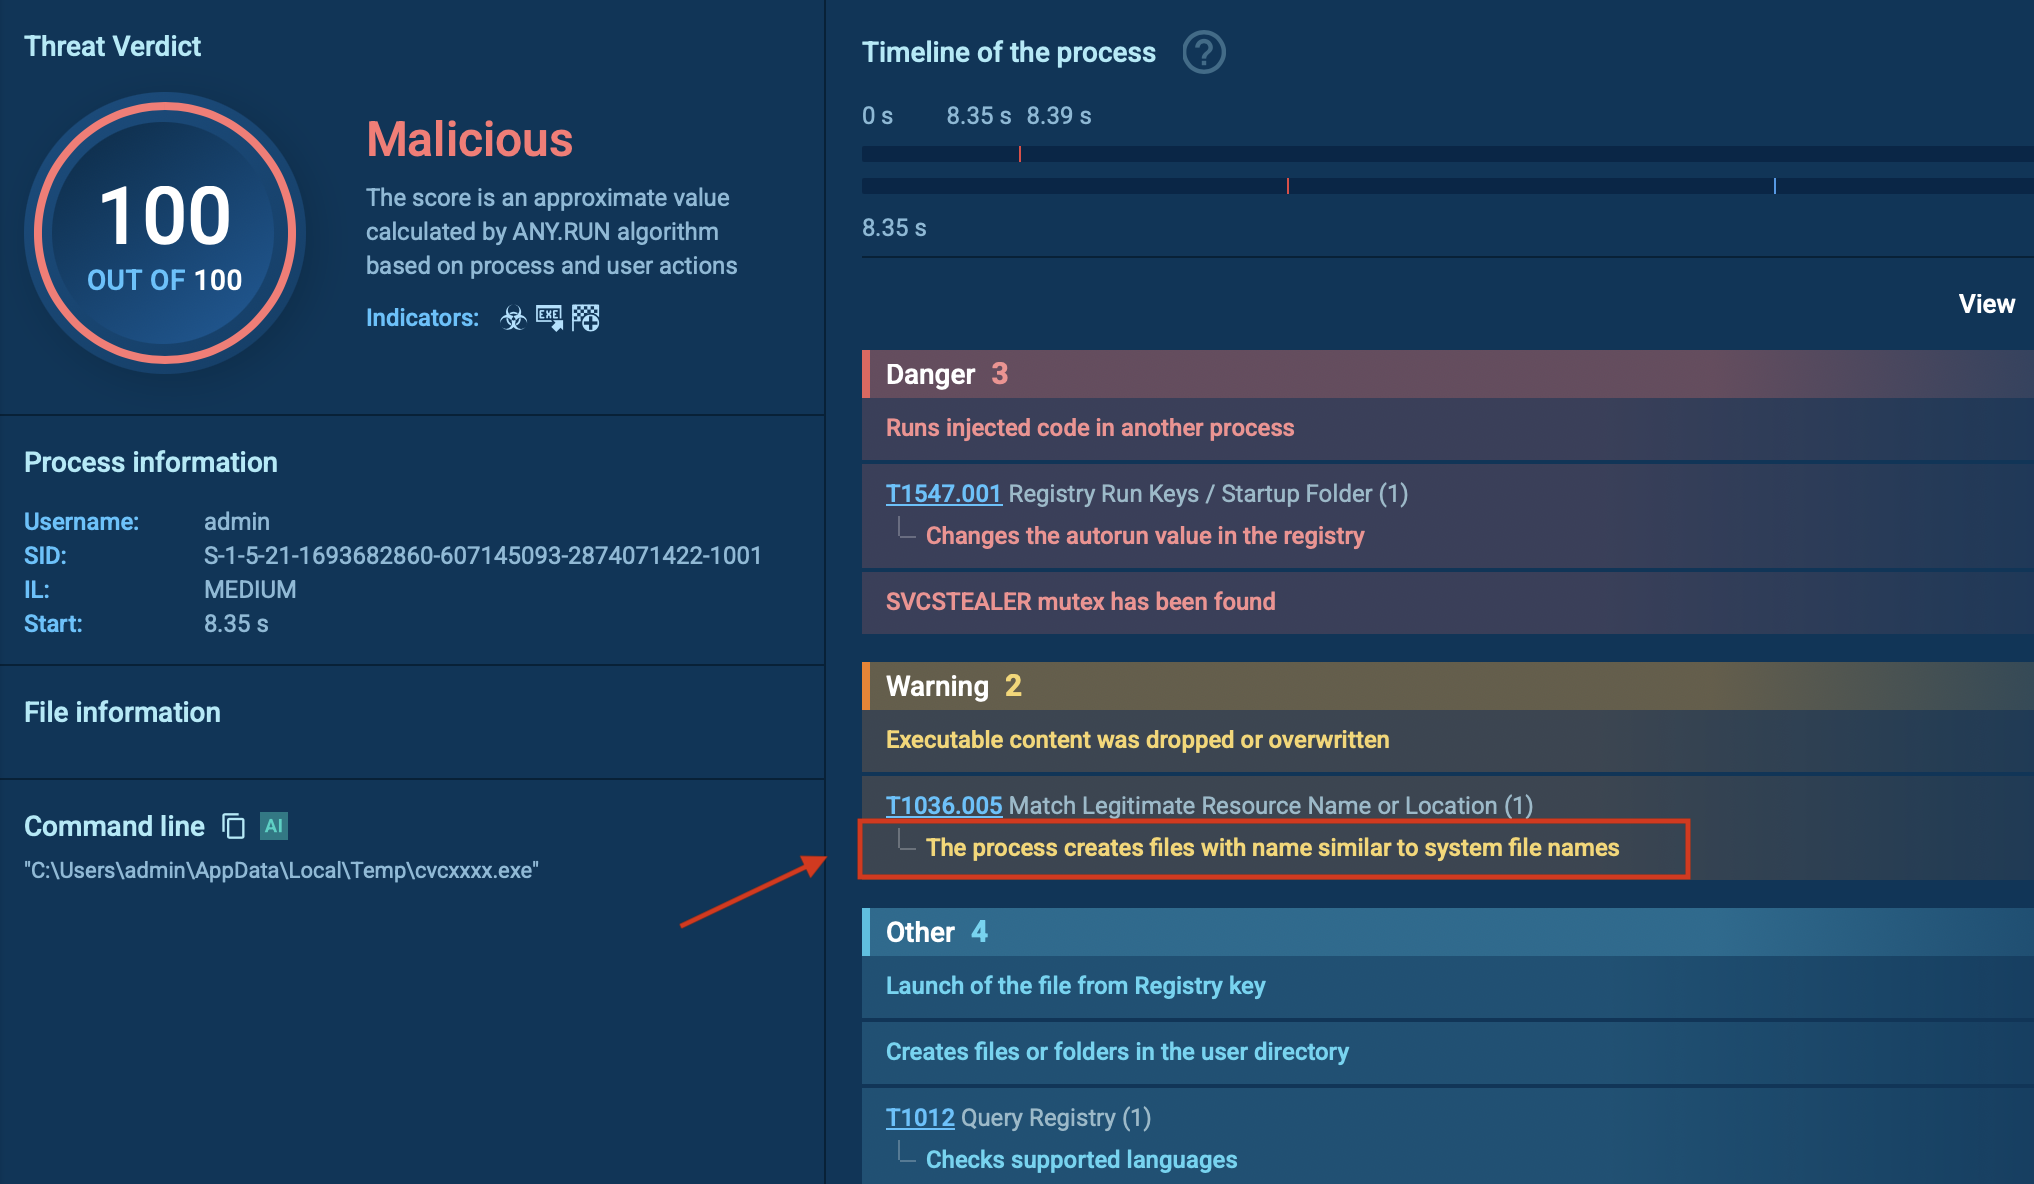
SVCStealer process in ANY.RUN Sandbox SVCStealer creates the folder with name similar to system name

Once active, SvcStealer attempts to evade detection by terminating common system monitoring and analysis tools. It targets processes such as Taskmgr.exe, ProcessHacker.exe, procexp.exe, and procexp64.exe. This prevents administrators and security software from identifying its activity.

The malware then begins harvesting sensitive information from the victim’s machine. It collects cryptocurrency wallet data stored in a dedicated “Wallets” folder, along with credentials and data from messaging applications like Discord, Telegram, 64gram, and Tox.

Browser data is also targeted, including content from Google Chrome, Opera, Microsoft Edge, Brave, and other browsers. This browser data often includes saved passwords, credit card details, browsing history, and other stored information. In addition, SvcStealer gathers system information, lists of installed applications, running processes with their process IDs, screenshots of the desktop, and files with specific extensions such as .jpg, .pdf, .docx, and .wallet.

After completing data collection, the malware compresses the harvested information into a ZIP archive within the generated folder. It then attempts to connect to its Command and Control (C2) server over HTTP using port 80. The stolen data is typically exfiltrated via HTTP POST requests. Once the transmission is successful, SvcStealer deletes the ZIP file and other artifacts to cover its tracks and minimize detection.

SvcStealer’s primary focus is data theft rather than extensive lateral movement. However, it can facilitate lateral movement by downloading additional tools or malware (e.g., via C2 commands) that enable network reconnaissance or privilege escalation. Its ability to act as an entry point for secondary payloads suggests potential for lateral movement if instructed by the attacker, though no specific lateral movement tactics are documented.

Gathering Threat Intelligence on SvcStealer

Leverage threat intelligence solutions like ANY.RUN’s TI Lookup to gather indicators of compromise associated with SvcStealer campaigns and block them in your network. You can start your research with the malware’s name and further investigate found IOCs with over 40 search parameters in TI Lookup.
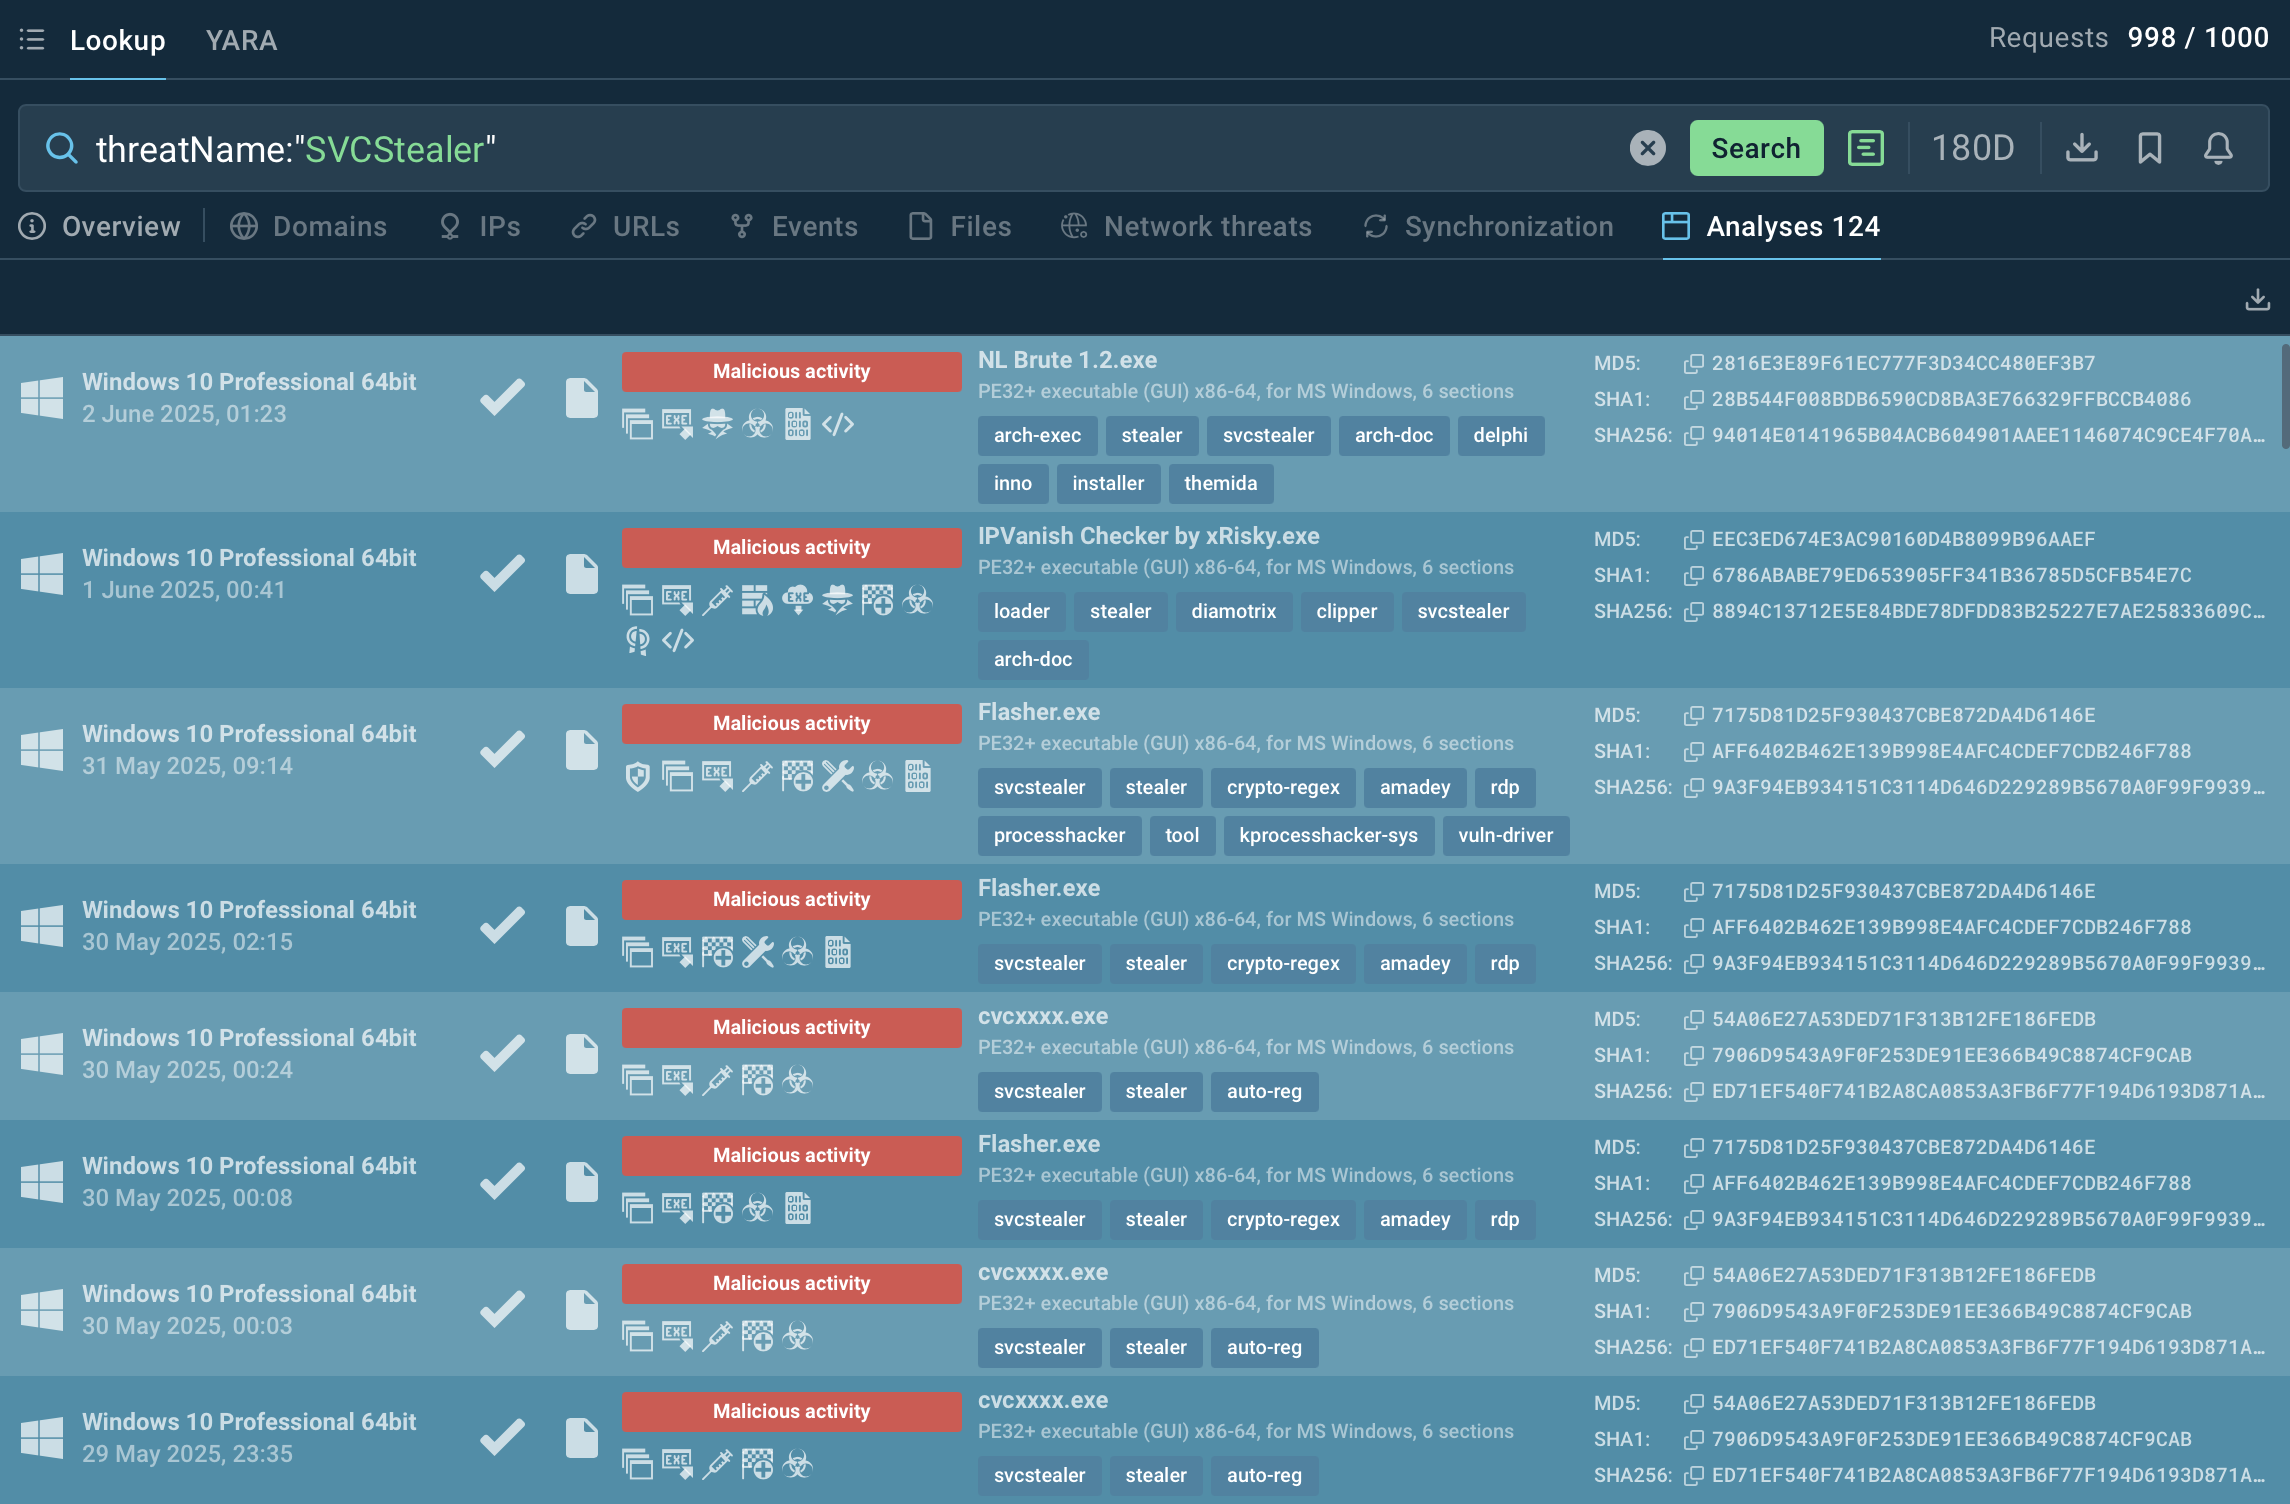
threatName:"SVCStealer"

SVCStealer samples Analyses of SVCStealer samples found via TI Lookup

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

SVCStealer is a dangerous info-stealer with advanced evasion techniques, primarily targeting credentials and financial data. Defending against it requires a mix of endpoint security, network monitoring, and user awareness. Organizations should employ threat intelligence to stay updated on new variants and attack methods.
Threat Intelligence Lookup gives verdict and context on IOCs in seconds: start with 50 trial searches.

HAVE A LOOK AT

PureCrypter screenshot
PureCrypter
purecrypter
First identified in March 2021, PureCrypter is a .NET-based loader that employs obfuscation techniques, such as SmartAssembly, to evade detection. It has been used to distribute malware families including AgentTesla, RedLine Stealer, and SnakeKeylogger. The malware is typically delivered through phishing campaigns and malicious downloads, often masquerading as legitimate files with extensions like .mp4 or .pdf. PureCrypter utilizes encryption and compression to conceal its payloads and can inject malicious code into legitimate processes to maintain persistence on the infected system.
Read More
Kamasers screenshot
Kamasers
kamasers
Kamasers is a multi-functional DDoS botnet malware that transforms infected machines into remotely controlled attack nodes. It combines network-layer flooding capabilities, resilient command-and-control (C2), and payload delivery, making it not just a disruption tool but a gateway to broader compromise.
Read More
Qilin Ransomware screenshot
Qilin ransomware (predecessor known as “Agenda”) is a rapidly evolving ransomware-as-a-service (RaaS) operation targeting organizations worldwide. Known for double extortion tactics (encrypting files while also threatening to leak stolen data) Qilin has quickly gained notoriety for its customization, flexibility, and impact on critical infrastructure.
Read More
Trojan screenshot
Trojan
trojan trojan horse
Trojans are a group of malicious programs distinguished by their ability to masquerade as benign software. Depending on their type, trojans possess a variety of capabilities, ranging from maintaining full remote control over the victim’s machine to stealing data and files, as well as dropping other malware. At the same time, the main functionality of each trojan family can differ significantly depending on its type. The most common trojan infection chain starts with a phishing email.
Read More
BlackMoon screenshot
BlackMoon
blackmoon
BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.
Read More
Stealer screenshot
Stealer
stealer
Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns.
Read More