Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

BlackMoon

106
Global rank
86 infographic chevron month
Month rank
51 infographic chevron week
Week rank

BlackMoon also known as KrBanker is a trojan aimed at stealing payment credentials. It specializes in man-in-the-browser (MitB) attacks, web injection, and credential theft to compromise users' online banking accounts. It was first noticed in early 2014 attacking banks in South Korea and has impressively evolved since by adding a number of new infiltration techniques and information stealing methods.

Trojan
Type
Unknown
Origin
1 February, 2014
First seen
8 October, 2026
Last seen
Also known as
KrBanker

How to analyze BlackMoon with ANY.RUN

Type
Unknown
Origin
1 February, 2014
First seen
8 October, 2026
Last seen

IOCs

IP addresses
49.235.189.22
95.101.9.148
20.190.160.132
48.209.138.189
23.197.142.186
52.110.17.32
23.11.41.157
199.232.214.172
23.213.161.106
185.199.108.133
43.228.157.73
23.146.242.246
124.44.3.74
112.125.88.19
185.199.111.133
140.82.121.4
163.181.254.205
49.81.64.182
61.249.139.64
64.89.163.22
Hashes
1c65be1230c5c2370a158fdda18d3c96da557657a6d6fd417a8f466dd6674cab
7ed34d7c8e0d558ff0248a4aeb0daf16adc98ce1cffddcff1cf47a6540367e78
f7e4aae30ab2bda60bead5fd5a29a36685d768df007d3399d3047768babae200
ceebae7b8927a3227e5303cf5e0f1f7b34bb542ad7250ac03fbcde36ec2f1508
602c4c7482de6479dd2e9793cda275e5e63d773dacd1eca689232ab7008fb4fb
913eaaa7997a6aee53574cffb83f9c9c1700b1d8b46744a5e12d76a1e53376fd
58a8d69df60ecbee776cd9a74b2a32b14bf2b0bd92d527ec5f19502a0d3eb8e9
47576cae321c80e69c7f35205639680bf28010111e86e228ed191b084fac6b91
5b8d47451f847c1bde12caca3739ca29860553c0b6399ee990d51b26f9a69722
e2991a6f7a7a4d8d3c4c97947298fd5bacb3eaa2f898cee17f5e21a9861b9626
0aa66dff8a7ae570fee83a803f8f5391d9f0c9bd6311796592d9b6e8e36be6fc
a0415f14f5d72ad24e9c3a5c91517a0e3d22e1adbc3505c0c6e918b961f7a07d
c15ab85438728bf2c60d72b1a66af80e8b1ce3cf5eb08ba6421ff1b2f73acdf4
29d93dee7c01b2264778bc6b75f6ef76ea6ac53e9f4a334d83707229e7f482d2
b6cd5c6f2b54d89142679d599ed0a5dee6955a3b3f6b6673e46afe7a5a303cdc
6c15cb256b1c22170292589c6f589e64e164eb36ec7e84f0bd48149babb7c5fc
4b7e76aeb75289faca76434ea6e9874e9504ad2bc3d8d47550eadbcc8294857e
232d6fe34d7151920232eaae9c515f36400ab64136dcc5b802d6245ac6f5d56b
9660537a7b62996478555c6f57c1962c78fb3972f19370b2e395c44842818a1f
afb66138ebe9b87d8b070fe3b6e7d1a05ed508571e9e5b166c3314069d59b4e4
Domains
login.live.com
ctldl.windowsupdate.com
officeclient.microsoft.com
ocsp.digicert.com
dns.msftncsi.com
settings-win.data.microsoft.com
fs.microsoft.com
google.com
class1004.dothome.co.kr
www.benshamcentre.co.uk
aidlifempowerment.com
kimyen.net
down.ruanmei.com
www.drgenov.com
hnjgdl.geps.glodon.com
rabbids.cc
tobecation.github.io
softdl.360tpcdn.com
www.saf-oil.ru
zz.woshisaob.club
URLs
http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?61119525e607a86c
http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab?3a594196b279919d
http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/pinrulesstl.cab?5824b154ef18ba2c
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://www.msftconnecttest.com/connecttest.txt
https://fs.microsoft.com/fs/windows/config.json
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://193.148.56.155/111.exe
http://102.220.161.23/bin/screenconnect.clientsetup.exe
http://91.92.34.63:8888/quickb.msi
http://102.220.161.23/bin/support.client.exe
http://176.65.139.201/bot.exe
http://193.178.158.57/bin/6107cbb0a359ada5_pyinfector.exe
http://46.19.140.40:8443/securityhealthsys.exe
http://46.19.140.40:8443/loader.exe
http://172.245.155.97/33/gfg.hta
http://144.172.116.239/40/goodthingsforme.hta
http://193.178.158.57/bin/f83ecc00a27c5716_hwbp_syst_b2nasg1e.exe
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 1389
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 3845
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 5997
comments 0

What is BlackMoon malware

BlackMoon (KRBanker) is one of the most sophisticated banking trojans, exploiting MitB attacks and web injections to steal financial data. Its stealthy evasion techniques, 2FA bypasses, and browser manipulation make it highly dangerous. Initially used in attacks targeting South Korea, it has since spread all over the world and threatens individuals and organizations in any region.

At the dawn of its “career" in 2015-2016, it employed a “pharming” technique to steal banking credentials. It redirected users to a fake website that imitated one of the banking sites and invited visitors to submit their payment data. The data is sent to C2 servers controlled by attackers, 2FA is bypassed by injecting fake OTP fields or session hijacking.

Beside luring information out of users, the malware generates fake alerts on banking websites prompting users to download a malicious security tool. BlackMoon employs a number of anti-detection and persistence mechanics. It injects itself into legitimate system processes, modifies Windows Registry, schedules tasks and startup entries. It also changes signatures to evade static detection, uses code obfuscation and targets specific banking URLs to minimize noise in network logs.

Blackmoon is detectable with threat intelligence tools by a number of indicators: associated domains, IPs, hashes, as well as known behavioral patterns. Network monitoring tools are triggered by outbound traffic to suspicious C2 servers, abnormal DNS queries, HTTP requests with suspicious headers related to web injections.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of BlackMoon malware

BlackMoon has some unique and some typical for malware of this type features that make it effective and hard to oppose.

  • Its infiltration methods of choice are phishing emails, social engineering, and malvertising as ways of delivering malicious attachments or links to fake banking login pages.
  • It also is distributed via malicious software disguised as legitimate banking or security tools.
  • It establishes itself in the system by modifying registry keys and injecting itself into legitimate system processes like explorer.exe.
  • It infiltrates into popular browsers and modifies banking login pages.
  • Fake login forms send users’ credentials to attackers’ C2 servers.
  • The information BlackMoon is aimed to steal includes online banking credentials (usernames, passwords), credit card details, personal identification information. It may gather them by logging keystrokes, capturing screenshots, and intercepting data entered into web forms.
  • KRBanker can provide attackers with remote access to the infected system to execute commands, upload additional malware, or exfiltrate data.
  • The measures of protection against BlackMoon must include proactive hunting for the malware indicators within the network using threat intelligence and forensic tools. Patch management, endpoint protection, multi-factor authentication, network segmentation must be employed.

The Execution process of BlackMoon

Within ANY.RUN's Interactive Sandbox, we can observe the malware's entire execution chain in a safe virtual environment.
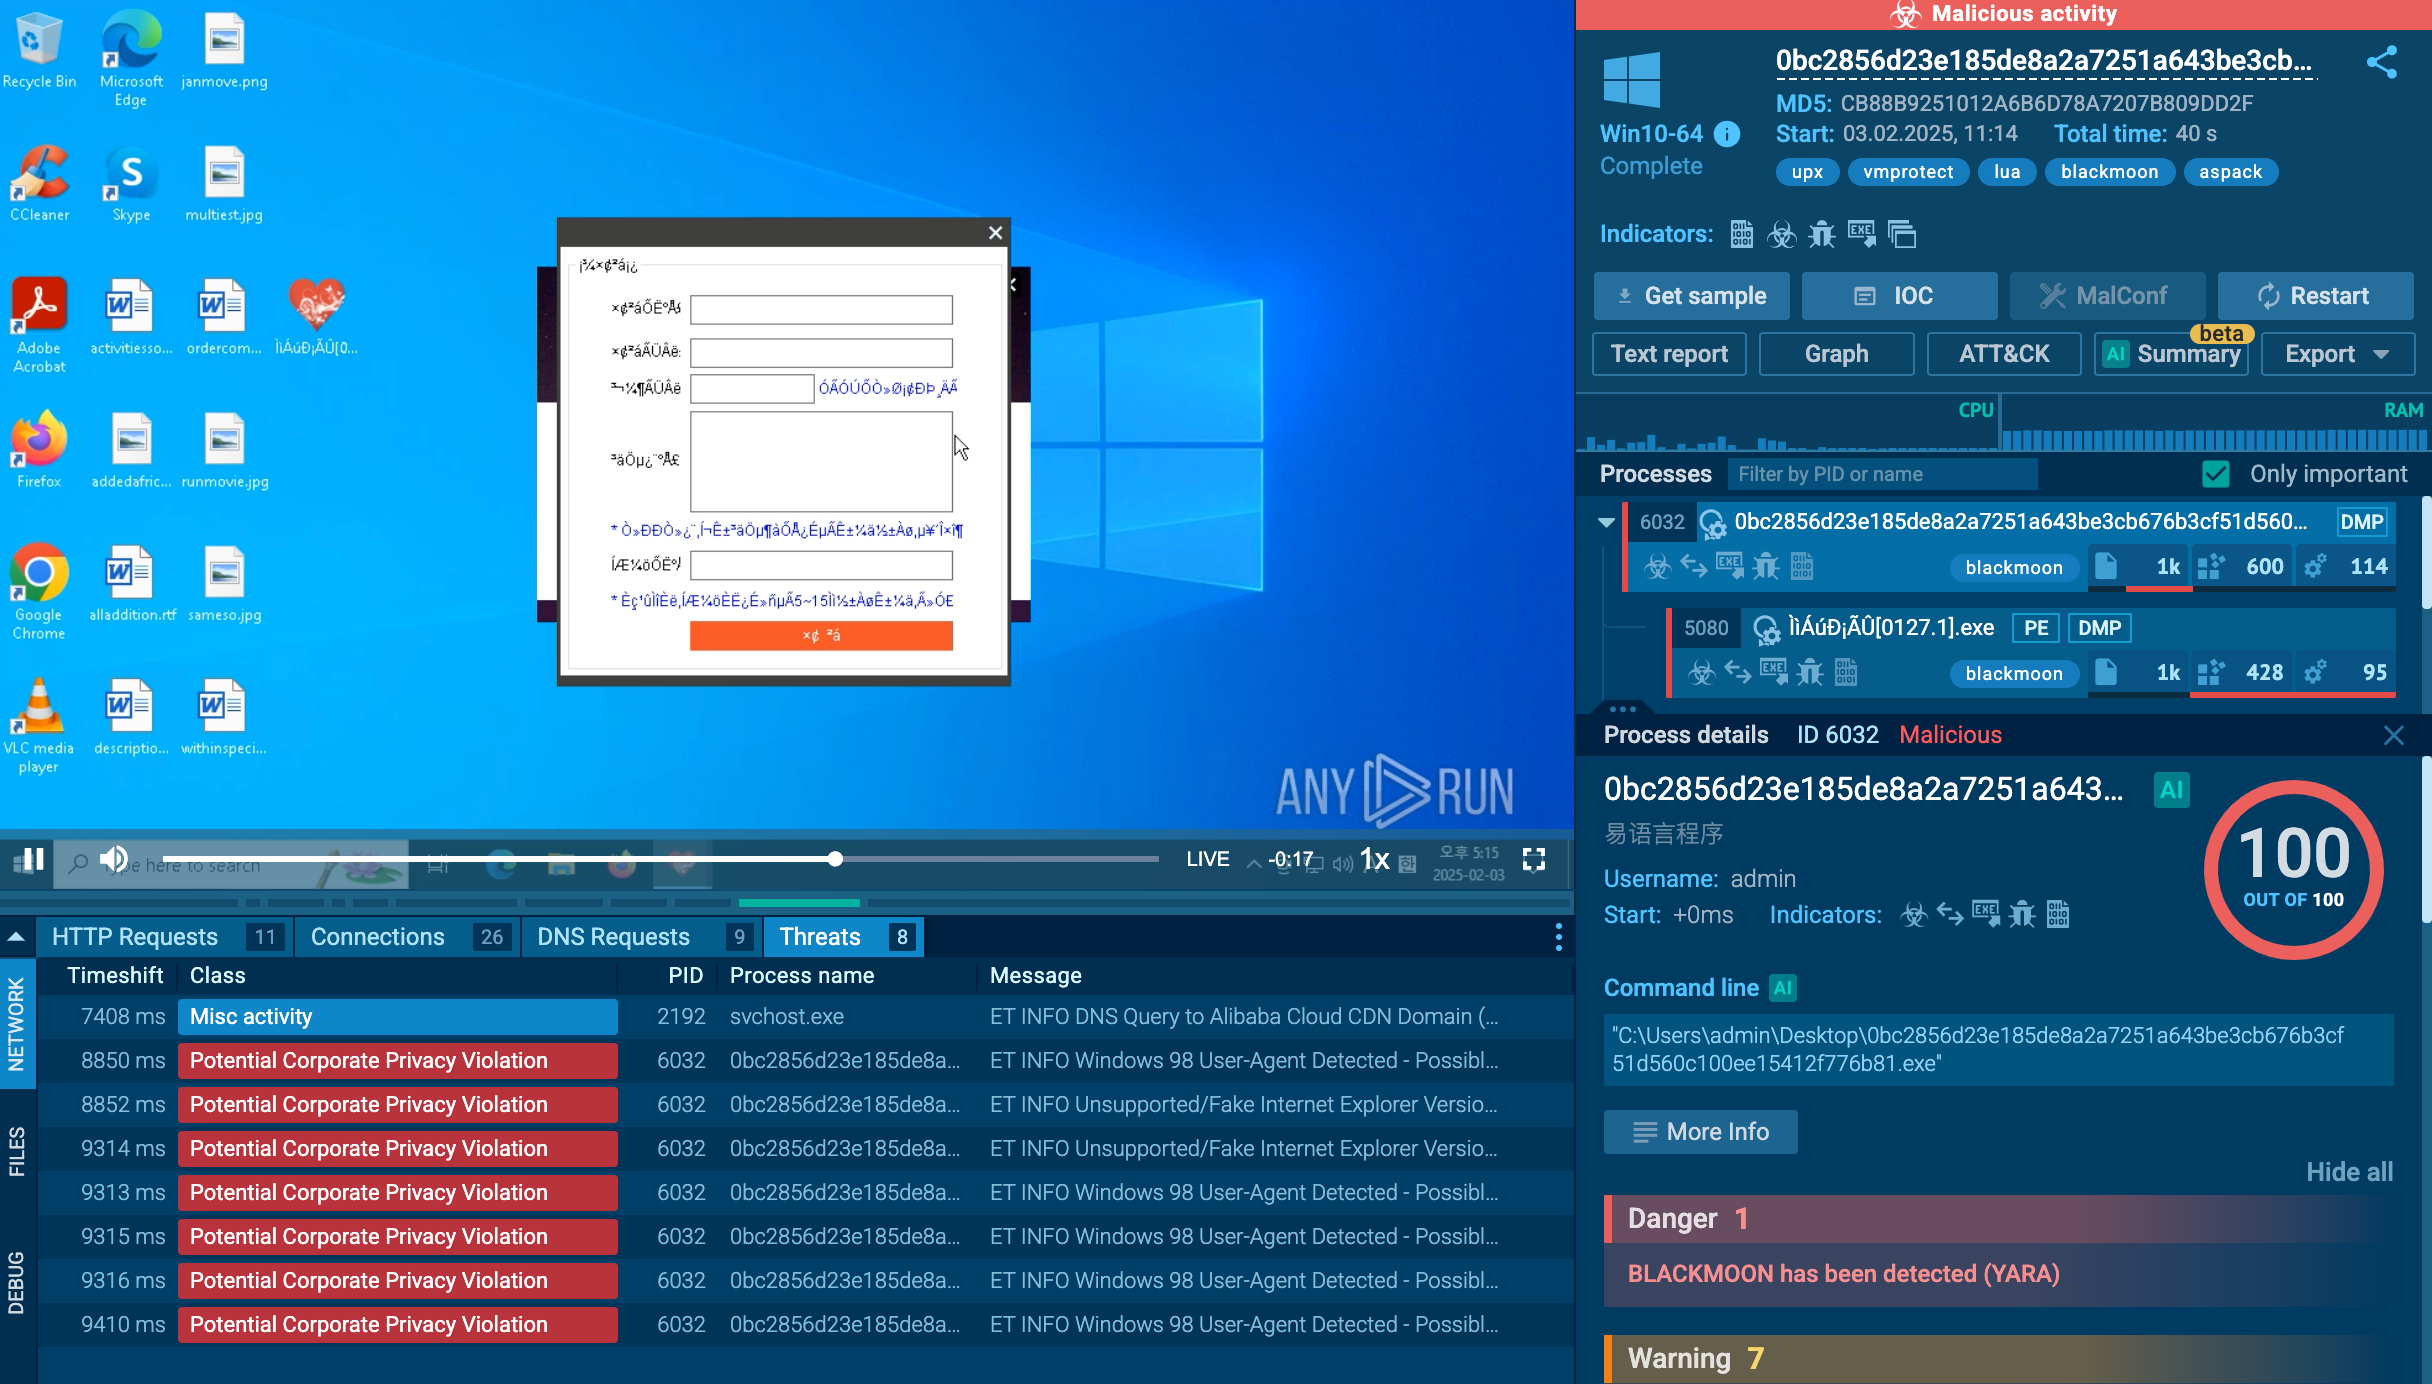
BlackMoon malware in the ANY.RUN Sandbox KRBanker detonated in ANY.RUN’s Interactive Sandbox

BlackMoon malware employs a multi-stage execution chain specifically designed for financial theft, frequently targeting South Korean banking institutions. The infection process typically begins with a dropper file delivered through phishing campaigns or exploit kits that leverage browser vulnerabilities.

Once executed, this dropper retrieves additional components necessary for the BlackMoon Trojan’s full functionality. The malware’s operation is divided into three distinct stages. In the first stage, the Mini Downloader fetches a second component, which in turn initiates the next phase. The second stage uses the KRDownloader to complete the installation.

After successfully downloading its payload, KRDownloader executes it and then self-deletes to evade detection. The payload commonly includes credential theft features, often deploying man-in-the-browser techniques to intercept user credentials during interactions with banking websites. Once installed, BlackMoon persists on the system by modifying registry keys and, in some cases, altering the local Hosts file. These changes redirect users attempting to access legitimate banking sites to attacker-controlled phishing pages.
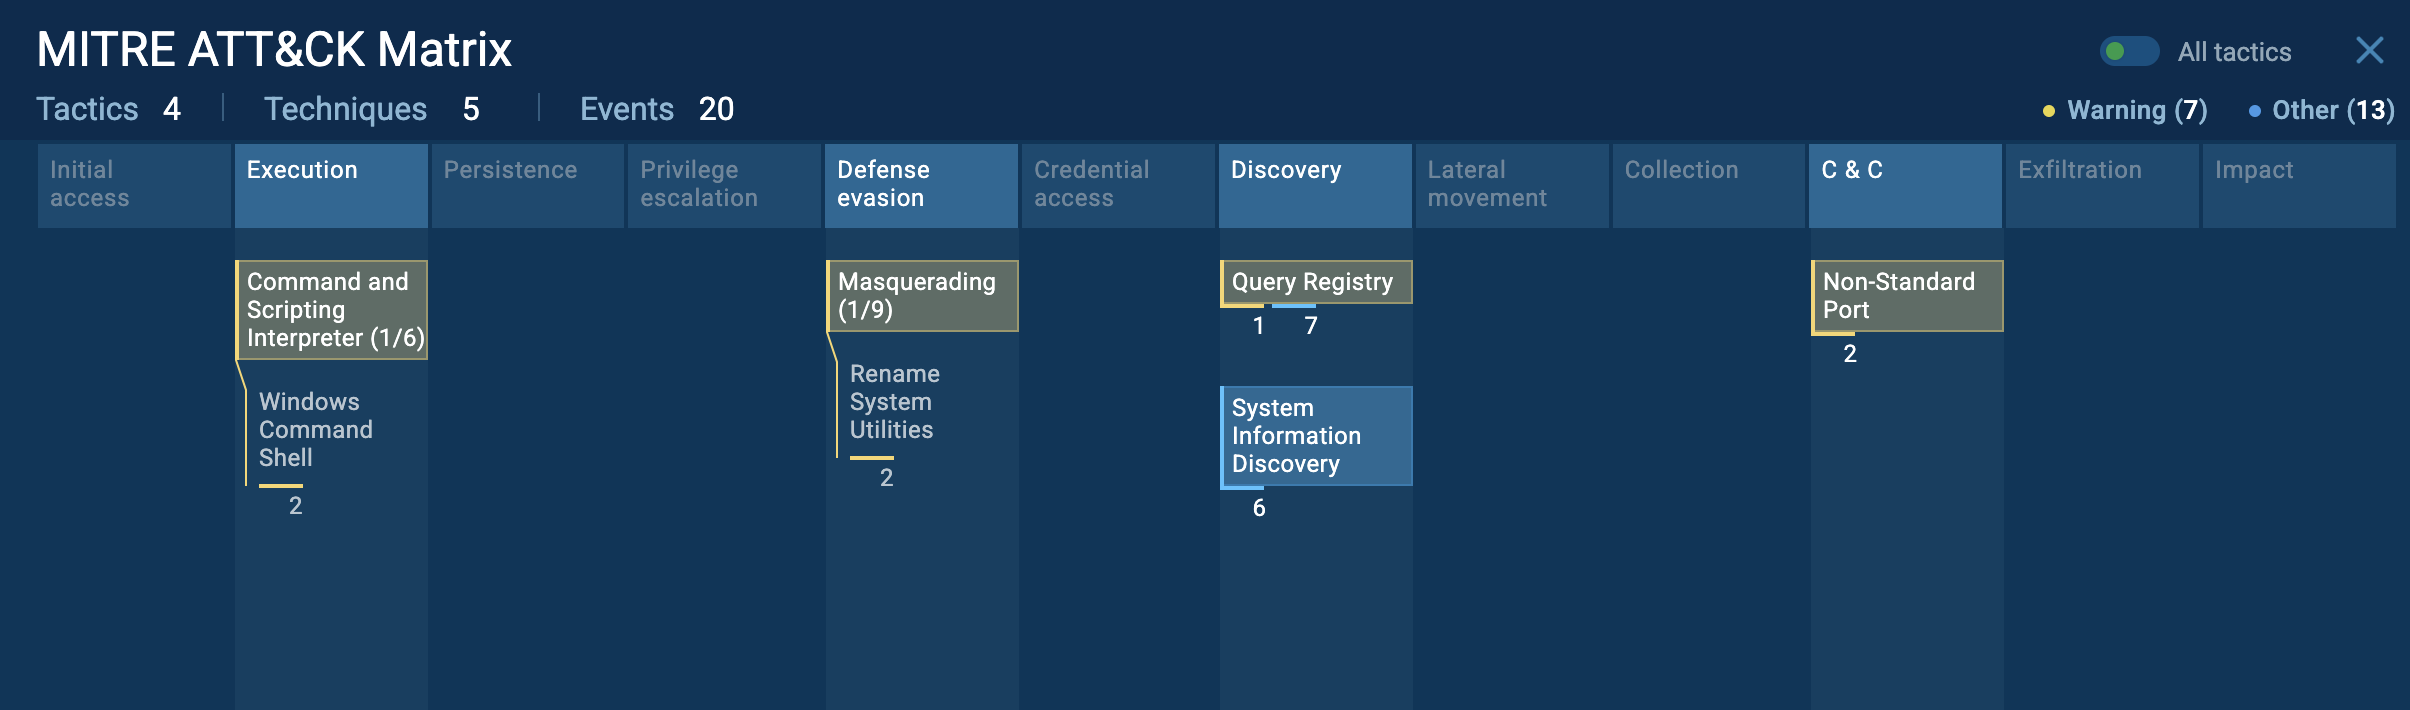
BlackMoon TTPs in the ANY.RUN Sandbox The tactics and techniques of Blackmoon mapped in the sandbox

The use of a Proxy Auto-Config (PAC) file further enhances stealth, allowing BlackMoon to intercept and manipulate web traffic without immediately arousing suspicion. Beyond credential theft and phishing, BlackMoon maintains communication with its command-and-control (C&C) servers to receive updates and instructions. It retrieves encoded configuration blocks from hardcoded URLs, dictating operational parameters and target websites. This communication channel is critical for retaining control over infected devices and adjusting to new targets or evasion methods.

Overall, BlackMoon’s carefully orchestrated, multi-stage downloader framework maximizes stealth and efficiency in delivering its malicious payload. This layered approach not only complicates analysis for security researchers but also enhances its effectiveness in compromising financial institutions and stealing sensitive user information.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Collect Threat Intelligence on BlackMoon Ransomware

Explore BlackMoon’s IOCs, IOBs and IOAs via ANY.RUN’s Threat Intelligence Lookup searches and collect data for setting up detection and response in your network.
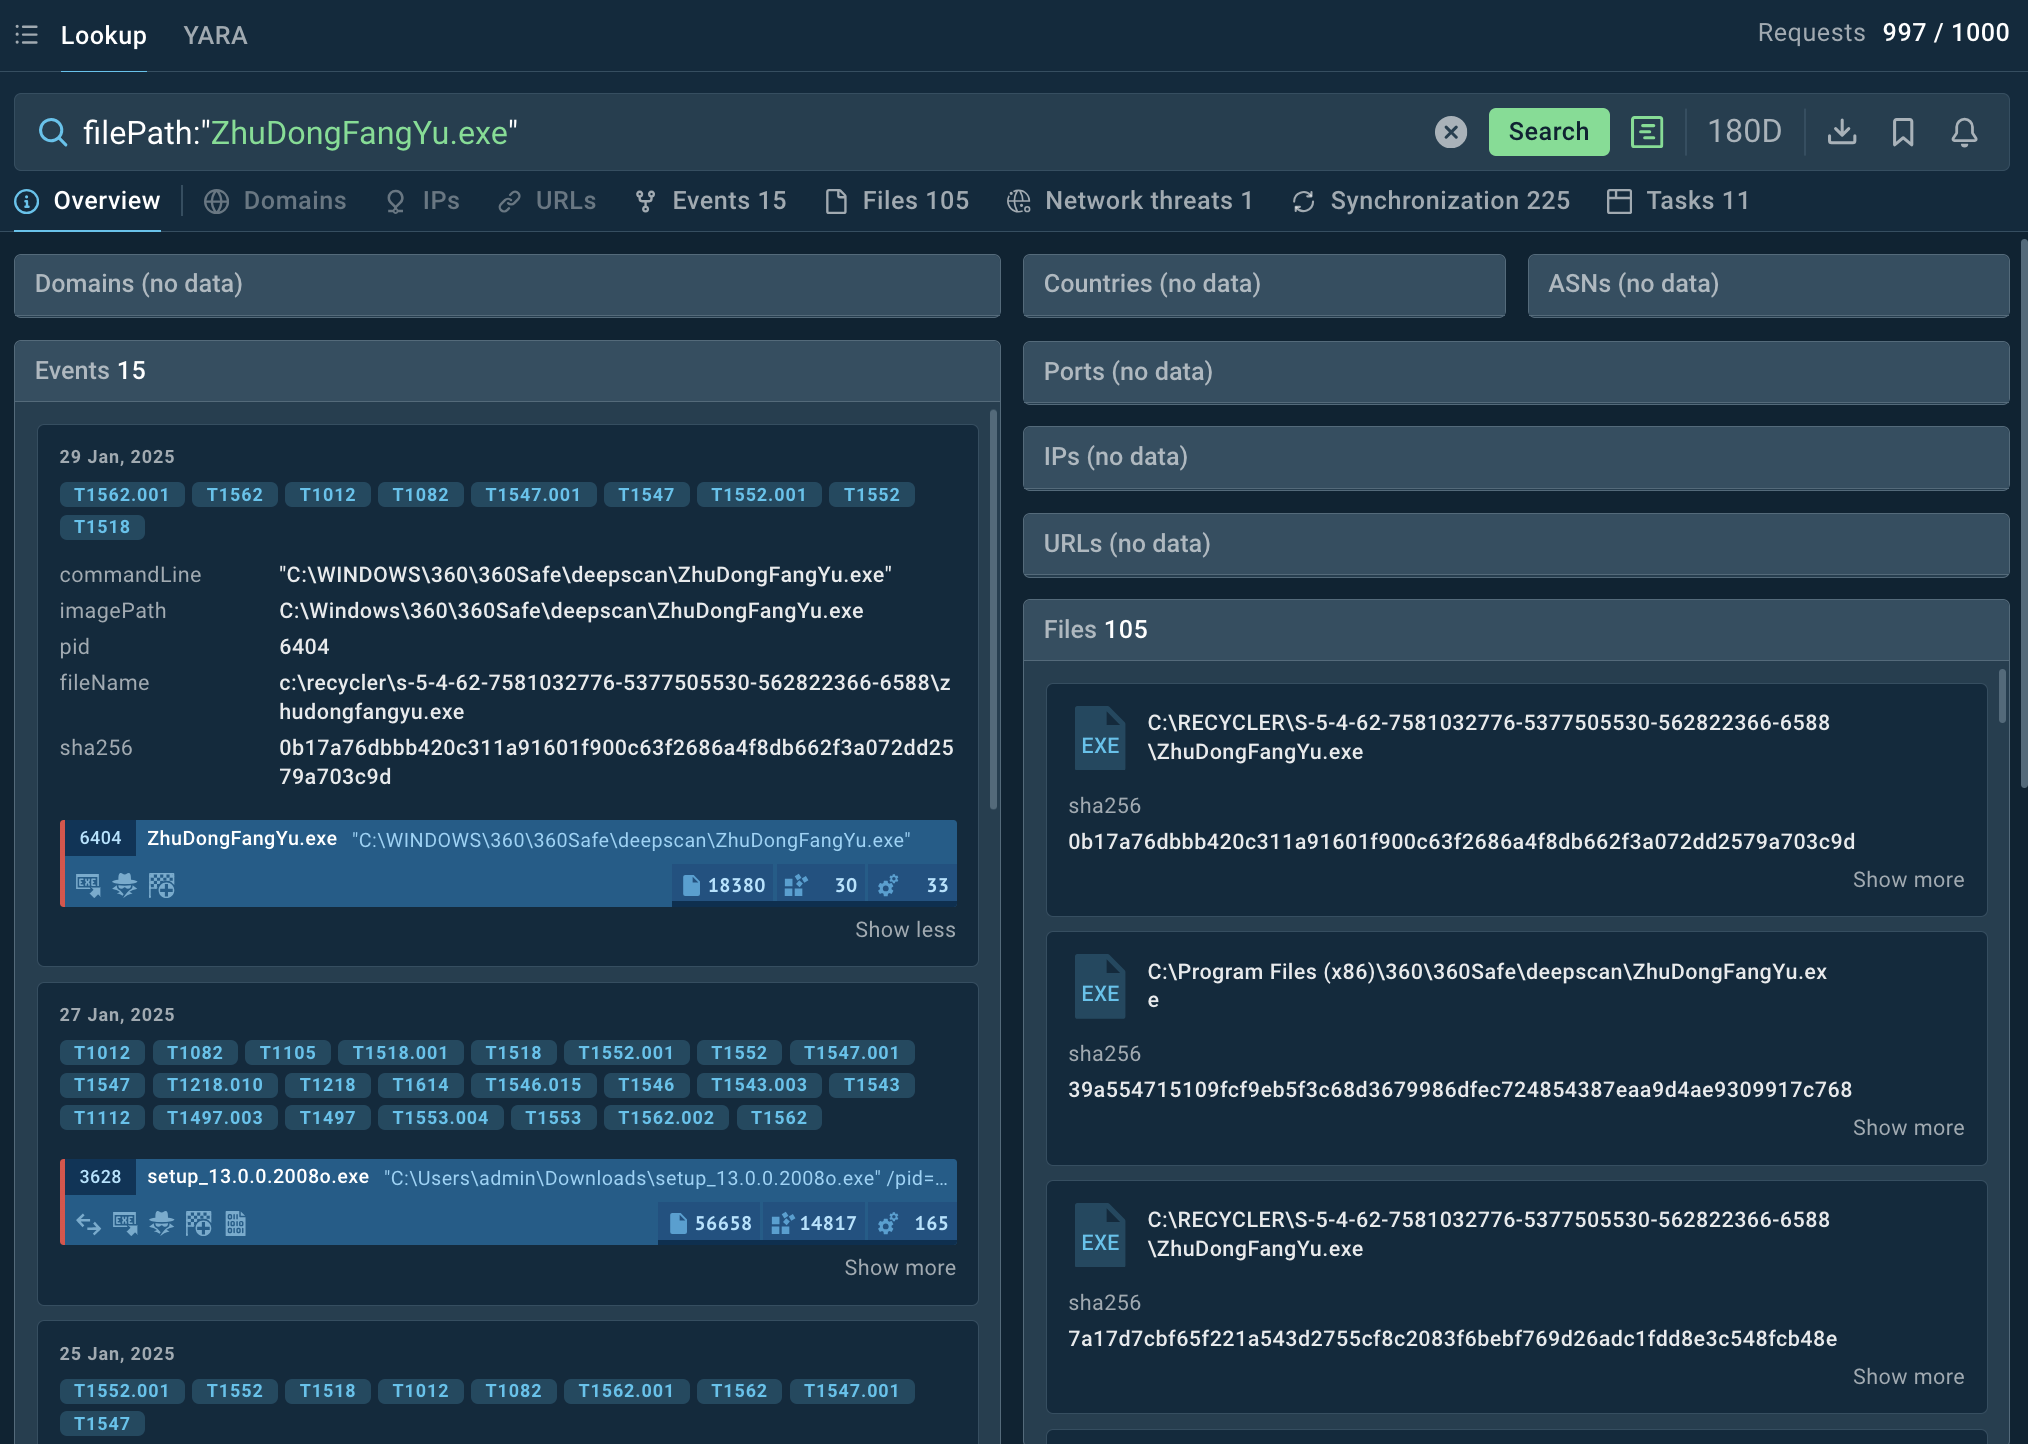
BlackMoon in the ANY.RUN TI Lookup TI Lookup overview of a malicious file associated with Blackmoon attacks

Leverage TI feeds to track C2 infrastructure, malware hashes, keep a watch over evolving tactics of KRBanker via MITRE ATT&CK mappings. For example, we can use the following query filePath:"ZhuDongFangYu.exe" to find sandbox reports featuring the file named ZhuDongFangYu commonly used in BlackMoon attacks.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

BlackMoon malware distribution methods

KRBanker typically spreads through:

  • Drive-by Downloads: Users visiting compromised or malicious websites can get infected via exploit kits that use browser vulnerabilities.
  • Phishing Emails & Social Engineering: Victims receive malicious attachments or links leading to fake banking login pages.
  • Trojanized Software: Users install malware disguised as legitimate banking or security tools.

Conclusion

BlackMoon remains highly dangerous because it leads directly to financial losses through critical data theft. Its stealthy evasion techniques, 2FA bypasses, and browser manipulation also put it in the high-risk group. Using threat intelligence-driven detection and response, security teams can monitor IOCs, implement behavioral analytics, and harden authentication mechanisms to combat this evolving banking malware threat.

Sign up for ANY.RUN to analyze malware and phishing threats for free.
HAVE A LOOK AT

Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
DarkComet screenshot
DarkComet
darkcomet rat darkcomet rat
DarkComet RAT is a malicious program designed to remotely control or administer a victim's computer, steal private data and spy on the victim.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
EvilTokens screenshot
EvilTokens
eviltokens
EvilTokens is a phishing-as-a-service (PhaaS) toolkit that emerged in mid-February 2026. It automates device code phishing attacks against Microsoft 365 and Entra ID environments. Unlike traditional credential-harvesting phishing, EvilTokens tricks users into completing legitimate authentication on Microsoft's own login pages, resulting in the issuance of valid OAuth access and refresh tokens directly to the attacker, effectively bypassing MFA without stealing passwords.
Read More
AsyncRAT screenshot
AsyncRAT
asyncrat
AsyncRAT is a RAT that can monitor and remotely control infected systems. This malware was introduced on Github as a legitimate open-source remote administration software, but hackers use it for its many powerful malicious functions.
Read More
Phantom Stealer screenshot
Phantom Stealer
phantomstealer
Phantom Stealer is a commercially available Malware-as-a-Service infostealer targeting Windows systems. It harvests browser passwords, session cookies, payment data, cryptocurrency wallets, system information, screenshots, and application data.
Read More