Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

EvilProxy

7
Global rank
53 infographic chevron month
Month rank
62 infographic chevron week
Week rank

EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.

Phishingkit
Type
Unknown
Origin
1 August, 2022
First seen
13 October, 2026
Last seen

How to analyze EvilProxy with ANY.RUN

Type
Unknown
Origin
1 August, 2022
First seen
13 October, 2026
Last seen

IOCs

IP addresses
104.18.94.41
150.171.109.106
150.171.28.11
2.21.239.135
23.59.18.102
20.234.74.24
150.171.22.17
150.171.27.11
74.125.250.129
13.107.246.44
142.251.14.94
92.223.97.79
150.171.109.100
150.171.109.107
172.211.123.250
16.15.207.226
142.251.14.95
135.233.95.144
16.182.72.226
142.251.14.139
Hashes
11a49f853eb8befe94fef278d487125cd20930b9e41c4c0934394443e7f00878
7852fce59c67ddf1d6b8b997eaa1adfac004a9f3a91c37295de9223674011fba
2d905d7b28b1afd313753d14f6a916a2e56ec4c1316bfa43046b09214ceb6090
baa0872250e769c30b6b7a8a1b2028eaf6af35113e47efd8f0b4ccfb98a52a32
5cd2c5e6acb885e542255eb1854c22a2491dafb4e2cbeac7fae6a40c485d3ea7
5c76fedcdb60416a8489d6b660b44cab538a41d37d8cd4e6a1be4de4a4714c62
fdf61e20fd2c0108e0ea28da4daca0035205b4b7fc031a3974b865b704de160a
266da3069a00ae9193ac11ae63771f5aeefa18b1862a441e03d319fde7bc1680
c955e57777ec0d73639dca6748560d00aa5eb8e12f13ebb2ed9656add3908f97
afd588d7d1c94d797ef932006d524de973f6fc54556e62f0f340412c87f99d58
01ba4719c80b6fe911b091a7c05124b64eeece964e09c058ef8f9805daca546b
51eb16447d65a8e85488cc5b300daa11092e03134afc7e587392a1563640ca8d
b58b77da7d6b8189a959a9003a2f3b2adef58b01d8bb1251c1361d843f3a1e6b
8e6db1634f1812d42516778fc890010aa57f3e39914fb4803df2c38abbf56d93
90cdaf487716184e4034000935c605d1633926d348116d198f355a98b8c6cd21
8737d721808655f37b333f08a90185699e7e8b9bdaaa15cdb63c8448b426f95d
1d2cde2e778a731cbd158758f735e1bcc2508a8252720d261d94068aff45aacc
7f04991cb2d08512ee29d864bc64cdad078ebc2af93cca9005b194e5b64e747b
240db4b6929a09b094dfcd13ad8f7b1e484ae4425f72e9ffb7c50a16aa69a7f2
a30ddcd349703aff7464c34bef3fffdff405ee50c113440d7c8693c02d210972
Domains
edge.microsoft.com
login.live.com
fonts.gstatic.com
fonts.googleapis.com
medcovery.s3.us-east-1.amazonaws.com
activation-v2.sls.microsoft.com
update.googleapis.com
api.fontshare.com
stun.cloudflare.com
xpaywalletcdn.azureedge.net
www.microsoft.com
docu-peek-view.lovable.app
aadcdn.msauth.net
arc.msn.com
slscr.update.microsoft.com
challenges.cloudflare.com
copilot.microsoft.com
stun.l.google.com
digitalgift.criticalsatellites.com
static.edge.microsoftapp.net
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:dashieijeo8agnn3zqgrwufemmtufxdn7tz7tix3fls&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://medcovery.s3.us-east-1.amazonaws.com/doc10064/index.html
https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
https://xpaywalletcdn.azureedge.net/mswallet/expresscheckout/v1/getglobalconfig?edgechannel=stable&edgeversion=133.0.3065.92&configversion=0
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791913039&lafgdate=0
https://medcovery.s3.us-east-1.amazonaws.com/favicon.ico
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d298%2526e%253d1
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
Last Seen at

Recent blog posts

post image
What's Really Attacking Your Industry? Insigh...
watchers 1699
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 9585
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 10824
comments 0

What is EvilProxy malware?

EvilProxy is a reverse-proxy phishing kit sold on dark-web marketplaces that has been active since mid-2022. The platform operates as a commercial service with subscription-based offerings for 10, 20, and 31 days. This advanced toolkit has fundamentally changed how cybercriminals conduct phishing attacks by providing even low-skilled threat actors with the capability to bypass multi-factor authentication (MFA) protections.

The toolkit got notorious for letting attackers create convincing replicas of legitimate websites while maintaining real-time communication with the authentic service. This reverse-proxy architecture allows EvilProxy to intercept and manipulate communications between victims and legitimate services without detection. The service targets major platforms including Apple, Google, Facebook, Microsoft, Twitter, GitHub, GoDaddy, and even niche platforms like PyPI.

What sets EvilProxy apart from traditional phishing kits is its sophisticated evasion capabilities. The platform incorporates advanced detection mechanisms to identify security researchers, automated analysis systems, and virtual machines. When suspicious activity is detected, EvilProxy can redirect connections to legitimate websites or completely drop connections to avoid analysis.

Similar to other phishkits like Tycoon 2FA and Sneaky2FA, EvilProxy primarily relies on phishing as its initial infection vector. Phishing emails impersonating legitimate organizations or services are the most common method. These emails often contain urgent requests, security alerts, or enticing offers to trick recipients into clicking malicious links.

The links can be disguised through URL shorteners, legitimate-looking domain names, or by embedding them within seemingly harmless attachments (e.g., HTML files). Attackers heavily leverage social engineering tactics to manipulate victims.

Once an account is compromised via EvilProxy, the attackers can use it to send out more phishing emails to the victim's contacts, leading to a chain reaction of compromises within an organization or its network.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

What EvilProxy Can Do to User Device

When a user visits an EvilProxy-hosted phishing page, the malicious service:

  • Captures login credentials entered by the user in real-time.
  • Harvests session cookies and authentication tokens automatically.
  • Bypasses device-based security measures by operating at the application layer.
  • Maintains persistent access through stolen session tokens, even after the initial interaction.
  • Installs secondary malware may follow once initial access is obtained.
  • Can potentially access stored passwords and autofill data if users interact with the fraudulent interface.

The endpoint device itself may not show traditional signs of infection, making EvilProxy attacks particularly insidious. Users may notice unusual login notifications or unexpected account activity, but the device's security software typically cannot detect the attack since no malicious code is installed locally.

How EvilProxy Threatens Businesses and Organizations

EvilProxy poses severe threats to businesses and organizations across multiple dimensions:

  • Executive Targeting: Threat actors are increasingly using toolkits like EvilProxy to pull off account takeover attacks aimed at high-ranking executives at prominent companies. This can lead to business email compromise (BEC) attacks, fraudulent financial transactions, and corporate espionage.
  • Scale of Operations: Security researchers have observed that EvilProxy facilitates over one million attacks monthly, indicating the massive scale of potential exposure for organizations worldwide.
  • Multi-Factor Authentication Bypass: The service's ability to harvest session cookies thereby bypassing non-phishing resistant MFA means that even organizations with robust security policies may be vulnerable.
  • Data Exfiltration: Once inside, attackers can access confidential files, source code, or customer records.
  • Lateral Movement: Access to one account can help escalate privileges or compromise other users.
  • Reputational Damage and Compliance Violations: Especially in industries with strict data regulations.
  • Supply Chain Risks: By targeting platforms like GitHub and PyPI, EvilProxy can potentially compromise software development pipelines and create supply chain vulnerabilities.
  • Financial Impact: Successful account takeovers can lead to direct financial losses through fraudulent transactions, regulatory compliance violations, data breach costs, and reputation damage.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

How Does EvilProxy Function?

EvilProxy operates through a reverse-proxy architecture that works as an intermediary between victims and legitimate services. The operation involves several key components:

  1. Reverse Proxy Technology: Actors use the kit to proxy victim's session, which means, EvilProxy creates a transparent tunnel between the victim and the real service.
  2. Real-Time Credential Harvesting: When users enter credentials on the phishing page, EvilProxy simultaneously submits these credentials to the legitimate service, capturing the resulting authentication tokens and session cookies.
  3. Session Token Theft: The service intercepts and stores session tokens generated during the authentication process, allowing attackers to maintain access even after the initial phishing interaction concludes.
  4. Anti-Detection Measures: EvilProxy incorporates an advanced fingerprinting technology to detect security researchers, automated analysis tools, and virtual machines. The bad actors are especially diligent when it comes to detecting possible virtual machines, typically used by security analysts to research malicious content.
  5. Dynamic Content Delivery: The PhaaS can serve different content based on the victim's location, device type, and other characteristics to maximize the success rate of attacks.

EvilProxy Attack Chain Live

ANY.RUN’s Interactive Sandbox contains thousands of EvilProxy samples that can be found with the aid of ANY.RUN’s Threat Intelligence Lookup:
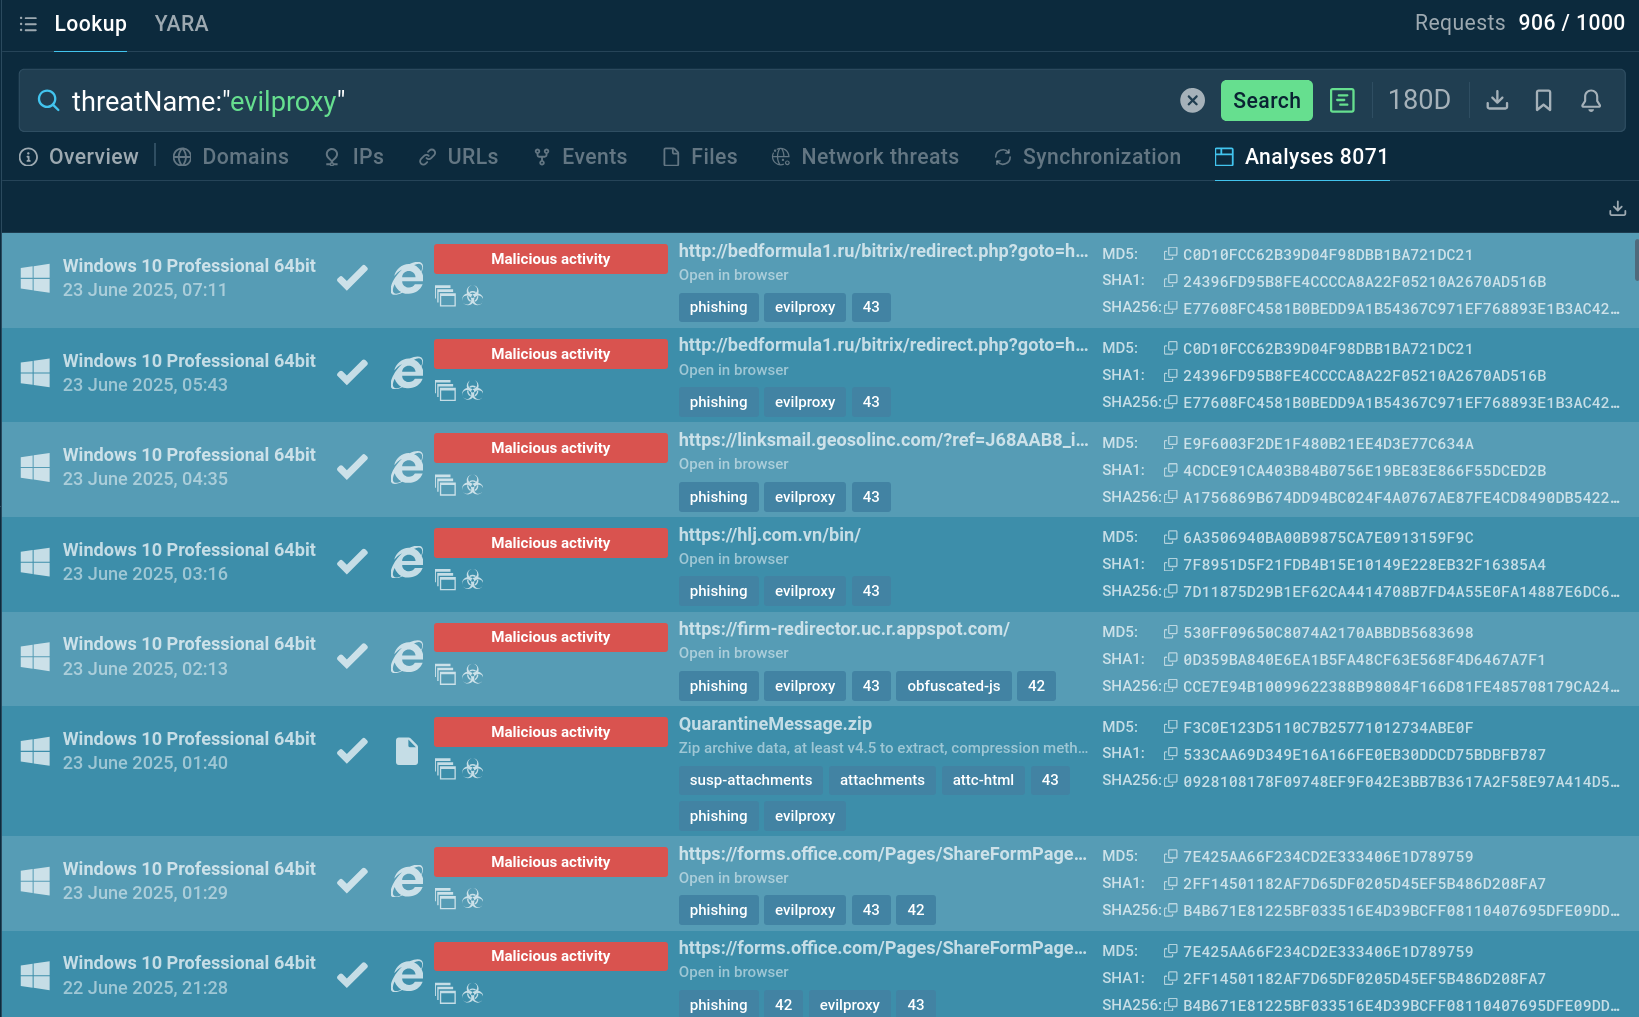
threatName:"evilproxy"

EvilProxy malware samples found via TI Lookup EvilProxy malware samples found via Threat Intelligence Lookup

You can choose a freshly submitted analysis session and view EvilProxy in action along with its network connections, process details, attackers’ TTPs, and IOCs extracted from the malware’s configuration.

Watch an analysis session of EvilProxy fresh sample
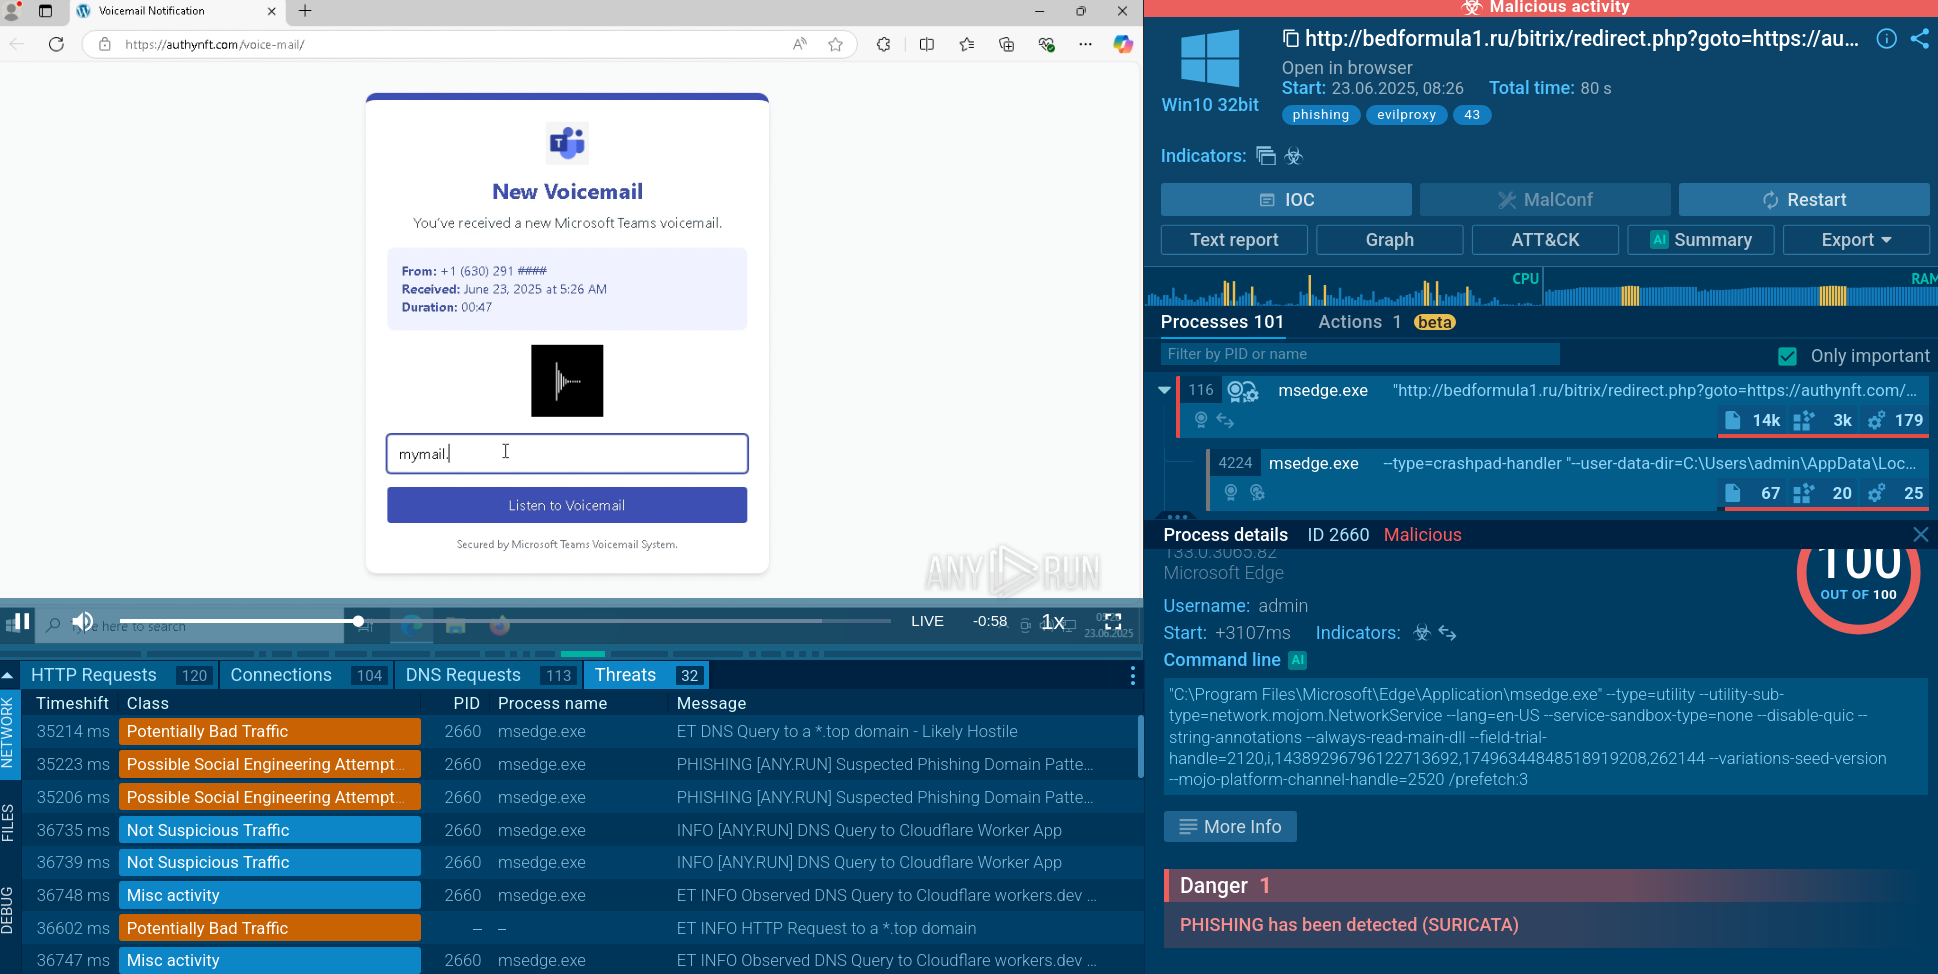
EvilProxy analysis in Interactive Sandbox EvilProxy attack analysis in ANY.RUN Interactive Sandbox

The execution chain of the EvilProxy phishing kit begins when a victim receives a phishing email that appears to originate from a trusted service or brand, such as DocuSign, Adobe, Concur, or another legitimate-looking website. These emails often contain a malicious link that exploits an open redirect vulnerability on a legitimate domain, allowing attackers to bypass email security filters and avoid detection.

When the victim clicks the link, they are redirected through several legitimate websites before landing on a phishing page that impersonates a genuine login portal—typically Microsoft 365 or a similar service. In one observed task, the lure involved a fake voicemail message that prompted the user to enter their email address, after which they were redirected to a counterfeit Microsoft login page. Another case involved a fake "Secure Vault" prompt.

View another analysis session of EvilProxy
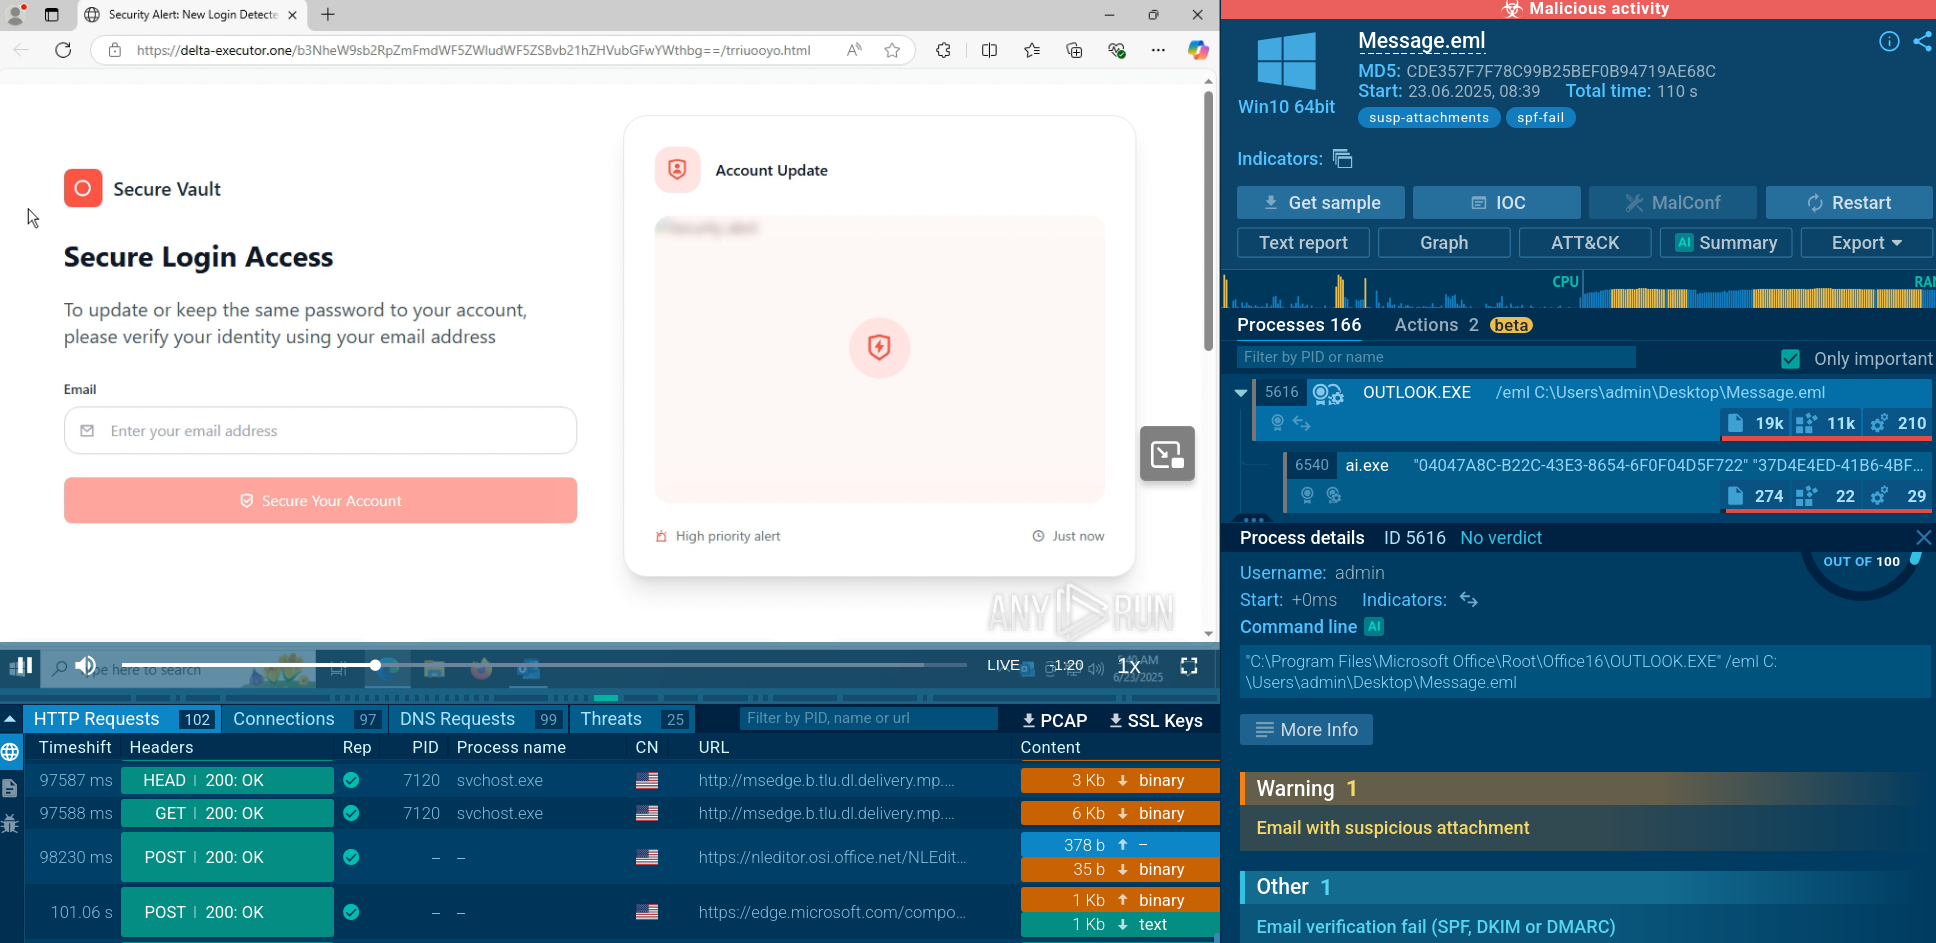
EvilProxy analysis in Interactive Sandbox EvilProxy attack abusing Secure Vault

The phishing pages are powered by the EvilProxy framework, which acts as a reverse proxy. It fetches live content from the real login page and displays it to the victim, making the phishing site look legitimate. As the victim enters their username, password, and two-factor authentication (2FA) code, EvilProxy intercepts these credentials in real time. The stolen credentials and 2FA tokens are immediately used on the attacker’s side to generate a valid session cookie, effectively bypassing MFA protections.

The attacker hijacks the session by proxying the victim’s traffic, allowing them to impersonate the victim and access the legitimate service without needing to re-enter credentials or 2FA tokens. This enables persistent access to the account. To evade detection, EvilProxy employs techniques such as browser fingerprinting, IP reputation checks, and filtering out connections from security researchers, bots, VPNs, proxies, Tor nodes, and virtual machines.

ANY.RUN’s Residential Proxy feature in the Sandbox helps users mask their traffic to appear as if it originates from real consumer devices rather than hosting environments, enabling full observation of the phishing attack chain without being blocked.
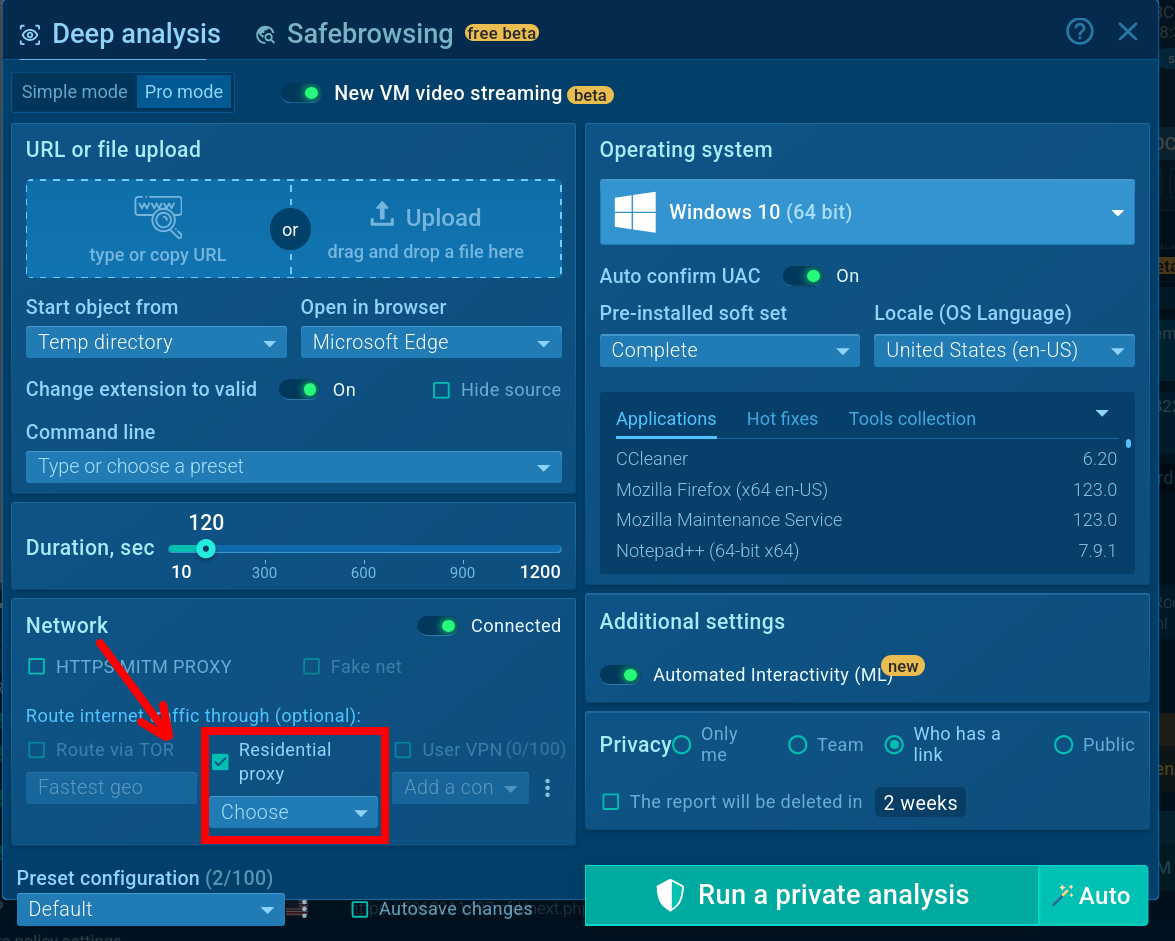
EvilProxy analysis in Interactive Sandbox Set up Residential Proxy when starting a new analysis in Interactive Sandbox

Gathering Threat Intelligence on EvilProxy malware

Threat intelligence provides actionable data for proactively defending against EvilProxy and the like.

ANY.RUN’s Threat Intelligence Lookup supports quick IOC checks for immediate verdicts but also allows deep research that brings understanding of malware’s behaviors, architecture, and tactics.

Extract IOCs from Sandbox analyses and explore them further via Threat Intelligence Lookup:
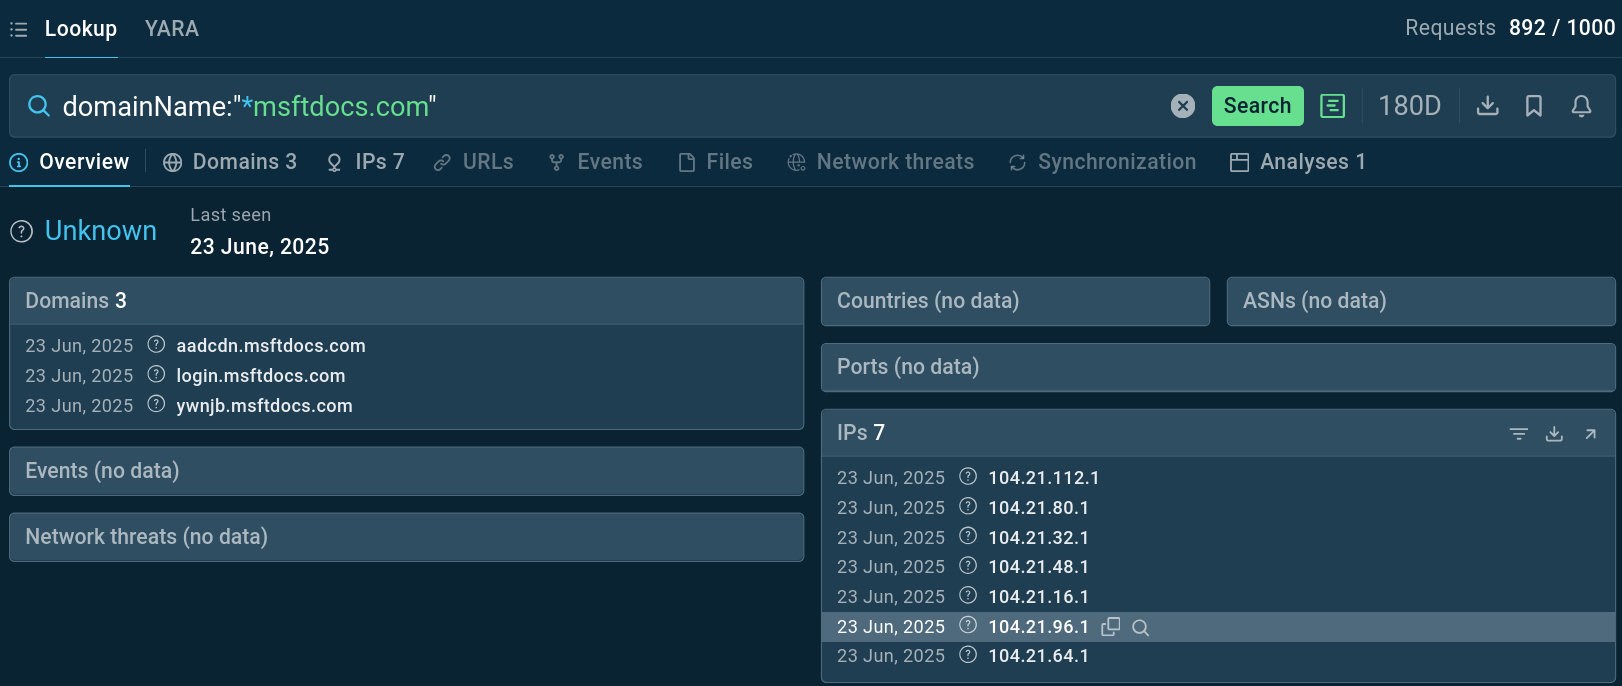
domainName:"*msftdocs.com"

EvilProxy domains in TI Lookup Search for EvilProxy-associated domain IOCs by pattern

Threat intelligence empowers defenders to:

  • Identify and block EvilProxy domains and IPs in near real-time.
  • Gather IOCs related to active EvilProxy campaigns.
  • Analyze infrastructures associated with EvilProxy operators.
  • Track adversary tactics, techniques, and procedures (TTPs) to preemptively defend against evolving campaigns.
  • With TI feeds, SOC teams can enrich alerts, prioritize responses, and reduce false positives.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

EvilProxy is a powerful weapon in the phishing landscape, offering a turnkey solution for bypassing MFA and hijacking sessions. It demonstrates the growing professionalization of cybercrime and underscores the urgent need for organizations to upgrade their defenses. Traditional security measures are no longer enough—organizations must adopt phishing-resistant MFA, leverage threat intelligence, and continually train users to recognize the signs of these highly convincing attacks.

Gather actionable intelligence via ANY.RUN’s TI Lookup: start with 50 trial requests.
HAVE A LOOK AT

 screenshot
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
Read More
Grandoreiro screenshot
Grandoreiro
grandoreiro
Grandoreiro is a Latin American banking trojan first observed in 2016. It targets mostly Spanish-speaking countries, such as Brazil, Spain, Mexico and Peru. This malware is operated as a Malware-as-a-Service (MaaS), which makes it easily accessible for cybercriminals. Besides, it uses advanced techniques to evade detection.
Read More
Razr screenshot
Razr
razr
Razr is a destructive ransomware that infiltrates systems to encrypt files, rendering them inaccessible to users. It appends the ".razr" extension to the encrypted files and drops a ransom note, typically named "README.txt," instructing victims on how to pay the ransom to obtain the decryption key. The malware often spreads through phishing emails with malicious attachments or by exploiting vulnerabilities in software and operating systems. Razr employs strong encryption algorithms, making it challenging to decrypt files without the attackers' key.
Read More
Chaos Ransomware screenshot
Chaos ransomware is a malware family known for its destructive capabilities and diverse variants. It first appeared in 2021 as a ransomware builder and later acted as a wiper. Unlike most ransomware strains that encrypt data to extort payment, early Chaos variants permanently corrupted files, while later versions adopted more conventional encryption techniques.
Read More
DEVMAN screenshot
DEVMAN
devman
DEVMAN is a fast-evolving malware family targeting Windows environments with a mix of credential theft, remote control capabilities, and persistence techniques typical of modern crimeware. Initially observed in early 2025, DEVMAN quickly became a favorite tool among cybercriminal groups thanks to its stealth, modular structure, and ability to bypass traditional AV solutions.
Read More
Phantom Stealer screenshot
Phantom Stealer
phantomstealer
Phantom Stealer is a commercially available Malware-as-a-Service infostealer targeting Windows systems. It harvests browser passwords, session cookies, payment data, cryptocurrency wallets, system information, screenshots, and application data.
Read More