Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Tycoon 2FA

4
Global rank
51 infographic chevron month
Month rank
55 infographic chevron week
Week rank

Tycoon 2FA is a phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) protections, particularly targeting Microsoft 365 and Gmail accounts. Its advanced evasion techniques and modular architecture make it a significant threat to organizations relying on MFA for security.

Phishingkit
Type
Unknown
Origin
1 August, 2023
First seen
11 October, 2026
Last seen

How to analyze Tycoon 2FA with ANY.RUN

Type
Unknown
Origin
1 August, 2023
First seen
11 October, 2026
Last seen

IOCs

IP addresses
138.113.27.253
77.76.13.29
177.5.52.207
95.100.158.113
142.0.129.97
38.6.188.136
48.209.138.189
198.2.227.72
163.181.254.192
188.114.97.3
163.171.130.131
38.57.235.66
92.122.215.75
82.29.53.91
163.171.242.128
98.98.86.10
107.148.127.33
103.114.163.29
2.21.20.152
150.171.109.104
Hashes
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
8612988c08c771a0d50a93625019f71c0bf2892ec98e03d81d0990af30211741
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
a41670d52423ba69c7a65e7e153e7b9994e8dd0370c584bda0714bd61c49c578
54241ebe651a8344235cc47afd274c080abaebc8c3a25afb95d8373b6a5670a2
bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
de6d7b7c2427ec4e738407d7834b71941f69166b030355e00f325ff1391df5a1
cf26310b073b0891996ecd761c6cb53f00193dee524213a9fb34225d636ec4b7
aa12205b108750cf9fa0978461a6d8881e4e80da20a846d824da4069d9c91847
08978a1425dec304483bbb7dd0e55a7d850c4561abd41bac1be5d93d70465174
243befbd6b67a21433dcc97dc1a728896d3a070dc20055eb04d644e1bb955fe7
Domains
edge-consumer-static.azureedge.net
d12h904ujoahzy.cloudfront.net
tupian.aepoi.cn
img.tangyoufushi.fun
bumufdz688h7.ummxzaie.com
img.meituan.net
2026100406.beijingimg.cc
www.879331779916-lewojdtqmigw.cc
knsioha.wtumcbbs.space
mpp18.doqgxb.com
ms.htst273h.com
monkey.cszpra.com
ga2k3b.oss-accelerate.aliyuncs.com
_7378._https.wb65.7378cy98.com
ksnia.jincheng-bio.com
cm4lg.zvhtu.com
kisuiy.suhe.ink
eusieugm.zvhtu.com
d18wfmxtvthwf6.cloudfront.net
ksnia.yvjzu.cn
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:jd1eeoehp--zysdtapywu9xycdxzi7aqjq0y1x_z1bs&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791706682&lafgdate=0
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://2026101104.60bbb.com/favicon1.ico?t=1791706687273
http://2026101104.60bbb.com/
http://2026101104.60bbb.com/template/06/css/style.css
http://2026101104.60bbb.com/6-js/index.js
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://2026101104.60bbb.com/6-js/top.js
http://2026101104.60bbb.com/6-js/mu2.js
http://2026101104.60bbb.com/6-js/mu1.js
http://2026101104.60bbb.com/6-js/tb.js
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 6005
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 7821
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 11434
comments 0

What is Tycoon 2FA?

This Adversary-in-the-Middle (AiTM) phishing kit became known in 2023, with significant updates observed through 2025. The PhaaS model allows even low-skilled attackers to deploy sophisticated phishing campaigns

Tycoon 2FA can intercept user credentials and session cookies to bypass MFA, enabling unauthorized access to accounts even with additional security measures. Organizations using cloud services are at the most risk.

The kit is distributed via Telegram channels starting at $120 for 10 days, with prices varying by domain extension (.com, .net, .org, etc.).

Tycoon 2FA has a multi-stage attack process through social engineering and compromised infrastructure, including phishing emails and QR codes; redirects to fake login pages; exploitation of legitimate services (e.g., Milanote for project collaboration).

Read detailed breakdown of Tycoon2FA’s defense evasion techniques

Victims are directed to a counterfeit login page mimicking Microsoft 365 or Gmail, where they unknowingly enter their credentials. A custom CAPTCHA (previously Cloudflare Turnstile, now HTML5 canvas-based) filters out automated bots and security tools, ensuring only human users proceed.

If MFA is enabled, Tycoon 2FA acts as a man-in-the-middle, relaying MFA prompts and capturing session cookies in real time upon successful authentication. These cookies grant attackers unauthorized access to the victim's account without needing further credentials. Attackers reuse session cookies to bypass security controls and access accounts even if credentials are reset.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Tycoon 2FA Prominent Features

  • MFA Bypass: By capturing session cookies, Tycoon 2FA renders traditional MFA (e.g., SMS, authenticator apps) ineffective, compromising even security-conscious organizations.
  • Targeted Attacks: Primarily targets Microsoft 365 and Gmail, critical for enterprise and cloud environments, leading to potential data breaches, financial loss, or ransomware deployment.
  • Ease of Use: As a PhaaS platform, it provides ready-to-use templates and admin panels, enabling even low-skilled attackers to launch sophisticated campaigns.
  • Longevity: Advanced evasion techniques allow campaigns to remain undetected longer, increasing the number of compromised accounts.
  • Exploitation of Legitimate Infrastructure: Using compromised legitimate accounts and services like Milanote enhances credibility and evades traditional email security filters.
  • Scalability: Over 1,200 domains associated with Tycoon 2FA were identified between August 2023 and February 2024, indicating widespread use.

Tycoon 2FA Execution Process and Technical Details

ANY.RUN’s Interactive Sandbox, trusted by over 500,000 threat analysts and 15,000 SOC teams, contains an impressive collection of malware samples featuring Tycoon 2FA attacks. Let’s scrutinize the phish kit’s strategy and tactics on an illustrative analysis session.

View the analysis and gather actionable data.
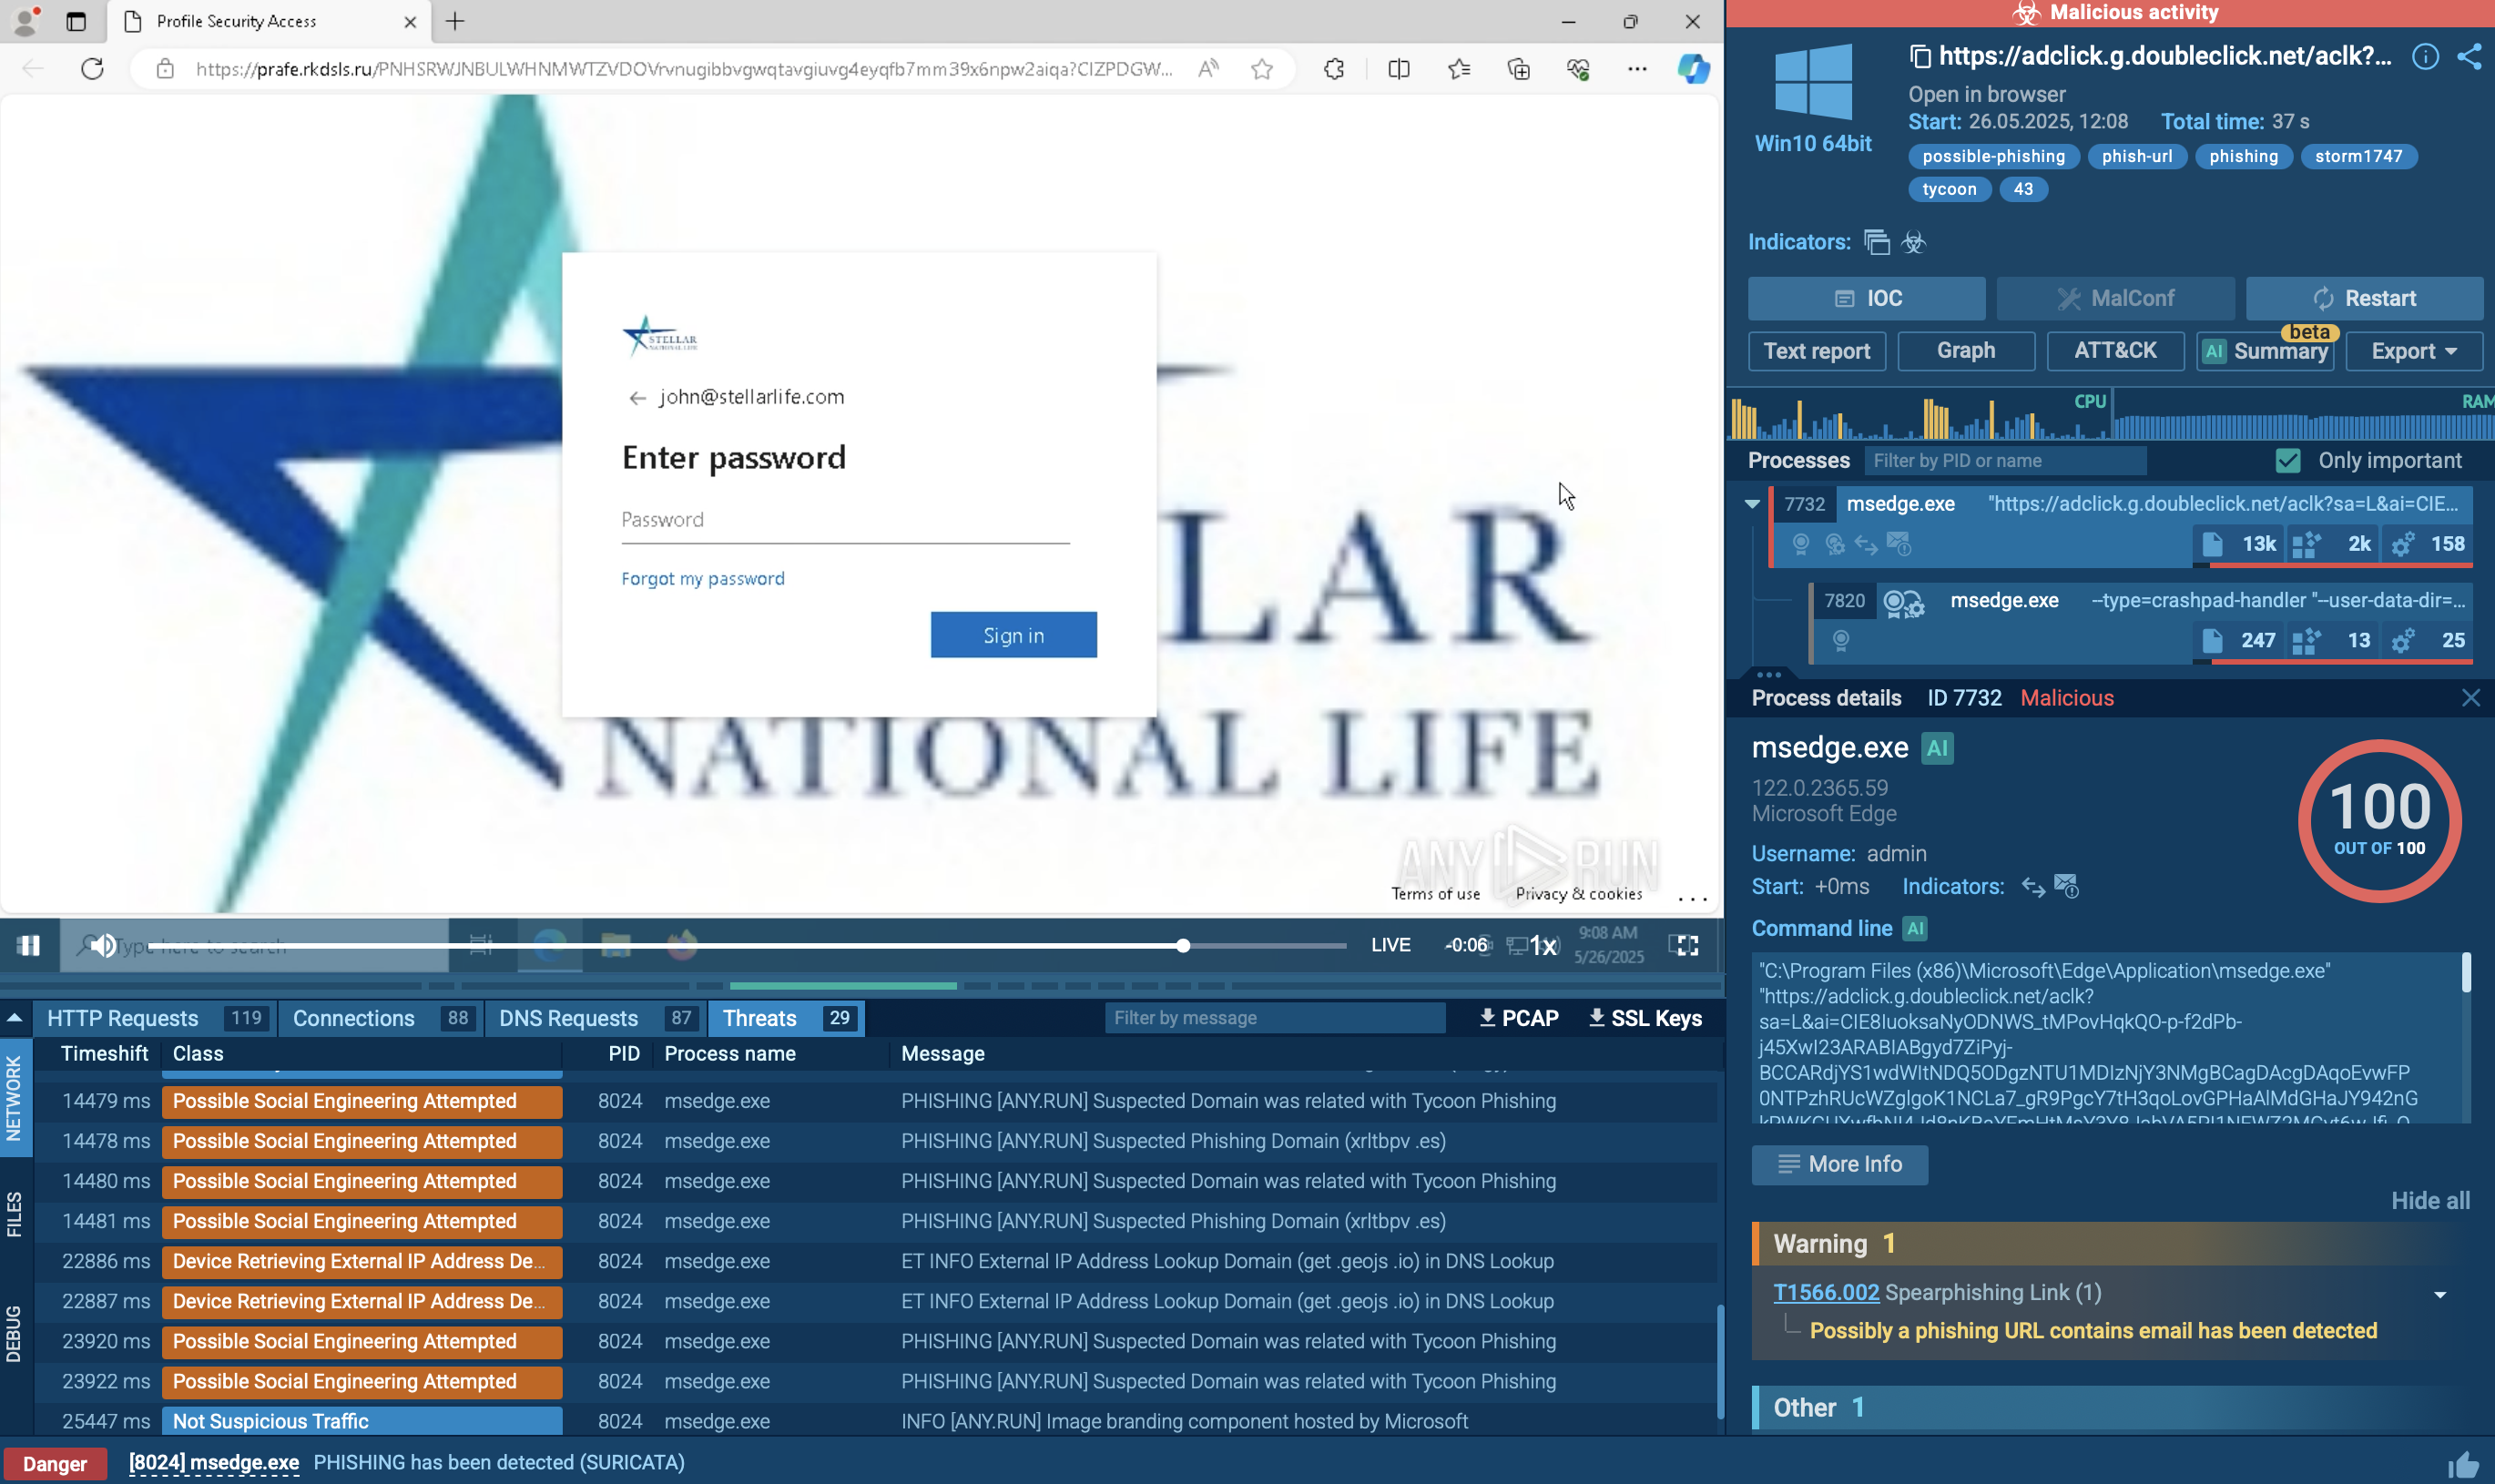
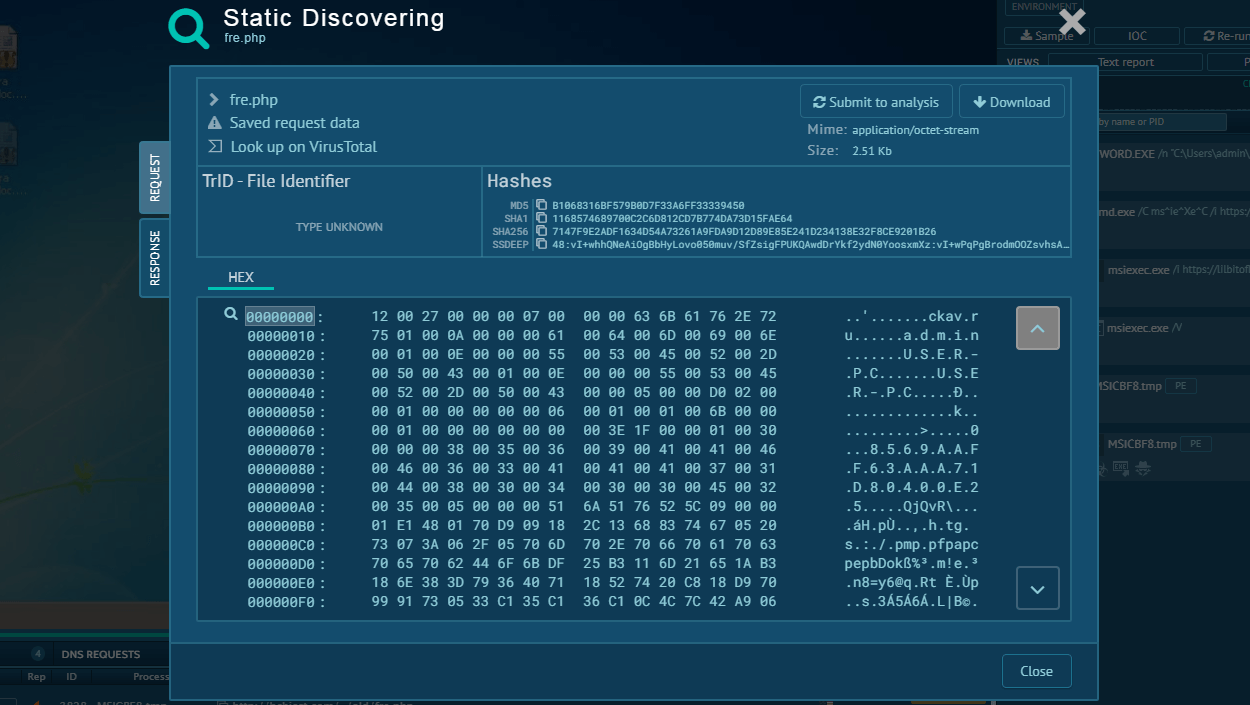
Tycoon 2FA analysis in ANY.RUN Sandbox Tycoon 2FA sample in ANY.RUN's Interactive Sandbox

The execution chain typically begins with phishing emails or QR codes that direct victims to malicious URLs. These messages often impersonate trusted services and may be sent via legitimate platforms to enhance credibility. When a victim clicks the link, they are redirected through several intermediate pages, including CAPTCHA challenges such as reCAPTCHA or Cloudflare CAPTCHA, which are used to block bots and avoid automated detection systems.

ANY.RUN supports Automated Interactivity (ML) capable of handling such challenges in submitted tasks, including those sent via API. These CAPTCHA steps also help attackers evade sandbox detection by filtering out non-human traffic. During this redirection process, the kit performs environment checks by analyzing IP addresses, user agents, and browser fingerprints to identify security researchers or automated tools. These detections are ineffective against ANY.RUN, which uses residential proxies to simulate legitimate user traffic. If suspicious activity is detected, the visitor is redirected to a benign website to avoid raising alarms.

After passing the environment checks, the victim is taken to a fake login page that closely imitates Microsoft 365 or Gmail authentication portals. These pages are tailored to match the victim’s organization by modifying branding elements using legitimate services. Built with obfuscated and randomized JavaScript and HTML, these pages are designed to evade detection by signature-based security tools.

When the victim submits their credentials and, if prompted, an MFA code, the phishing kit captures the information in real time and forwards it to the legitimate Microsoft or Gmail servers via a reverse proxy. This enables the attackers to intercept valid session cookies, effectively bypassing MFA. With these session tokens, attackers gain persistent, unauthorized access without needing to reauthenticate.

To complicate analysis, payloads and exfiltrated data are often encrypted using AES, while URLs are randomized and malicious resources are delayed until after CAPTCHA completion to avoid detection by automated scanners.

What are the best-known Tycoon 2FA attacks?

  • Initial Emergence (August 2023): Identified by Sekoia, targeted Microsoft 365 with AiTM phishing, used phishing emails and Cloudflare Turnstile CAPTCHAs, compromised enterprise accounts.
  • Campaign Expansion (October 2023 - February 2024): Over 3,000 phishing pages, targeted Microsoft 365 and Gmail, used QR codes and Milanote, employed invisible Unicode obfuscation, caused widespread credential theft.
  • Custom CAPTCHA Evolution (Mid-2024): Shifted to HTML5 canvas-based CAPTCHA, added anti-debugging scripts and malformed URLs, prolonged campaign lifespans, targeted corporate accounts.
  • Advanced Obfuscation (April-May 2025): Added browser fingerprinting and payload encryption, rejected Tor/scanner traffic, disabled context menus, increased MFA bypass success.
  • Common Traits: PhaaS sold via Telegram for $120+, bypassed MFA via session cookie theft, targeted Microsoft 365/Gmail, used legitimate services, linked to 1,200+ domains.
  • Impacts: Hit financial sector for fraud, enabled enterprise breaches and ransomware, used stolen credentials for BEC.
  • Detection Challenges: Evaded detection with Unicode obfuscation, custom CAPTCHAs, and dynamic code; no specific threat actor, linked to Saad Tycoon Group.

Gathering Threat Intelligence on Tycoon 2FA Phish Kit

To counter Tycoon 2FA, organizations should adopt a proactive, multi-layered defense strategy informed by threat intelligence. Solutions like ANY.RUN’s Threat Intelligence Lookup help to detect and block known Tycoon 2FA infrastructure like domains and IPs at the network edge.

Make an easy entrance to Tycoon 2FA investigation by searching the threat by the name via TI Lookup. View any analysis session to get acquainted with the phish kit operators’ TTPs and gather indicators of compromise to set up alerts and defenses.
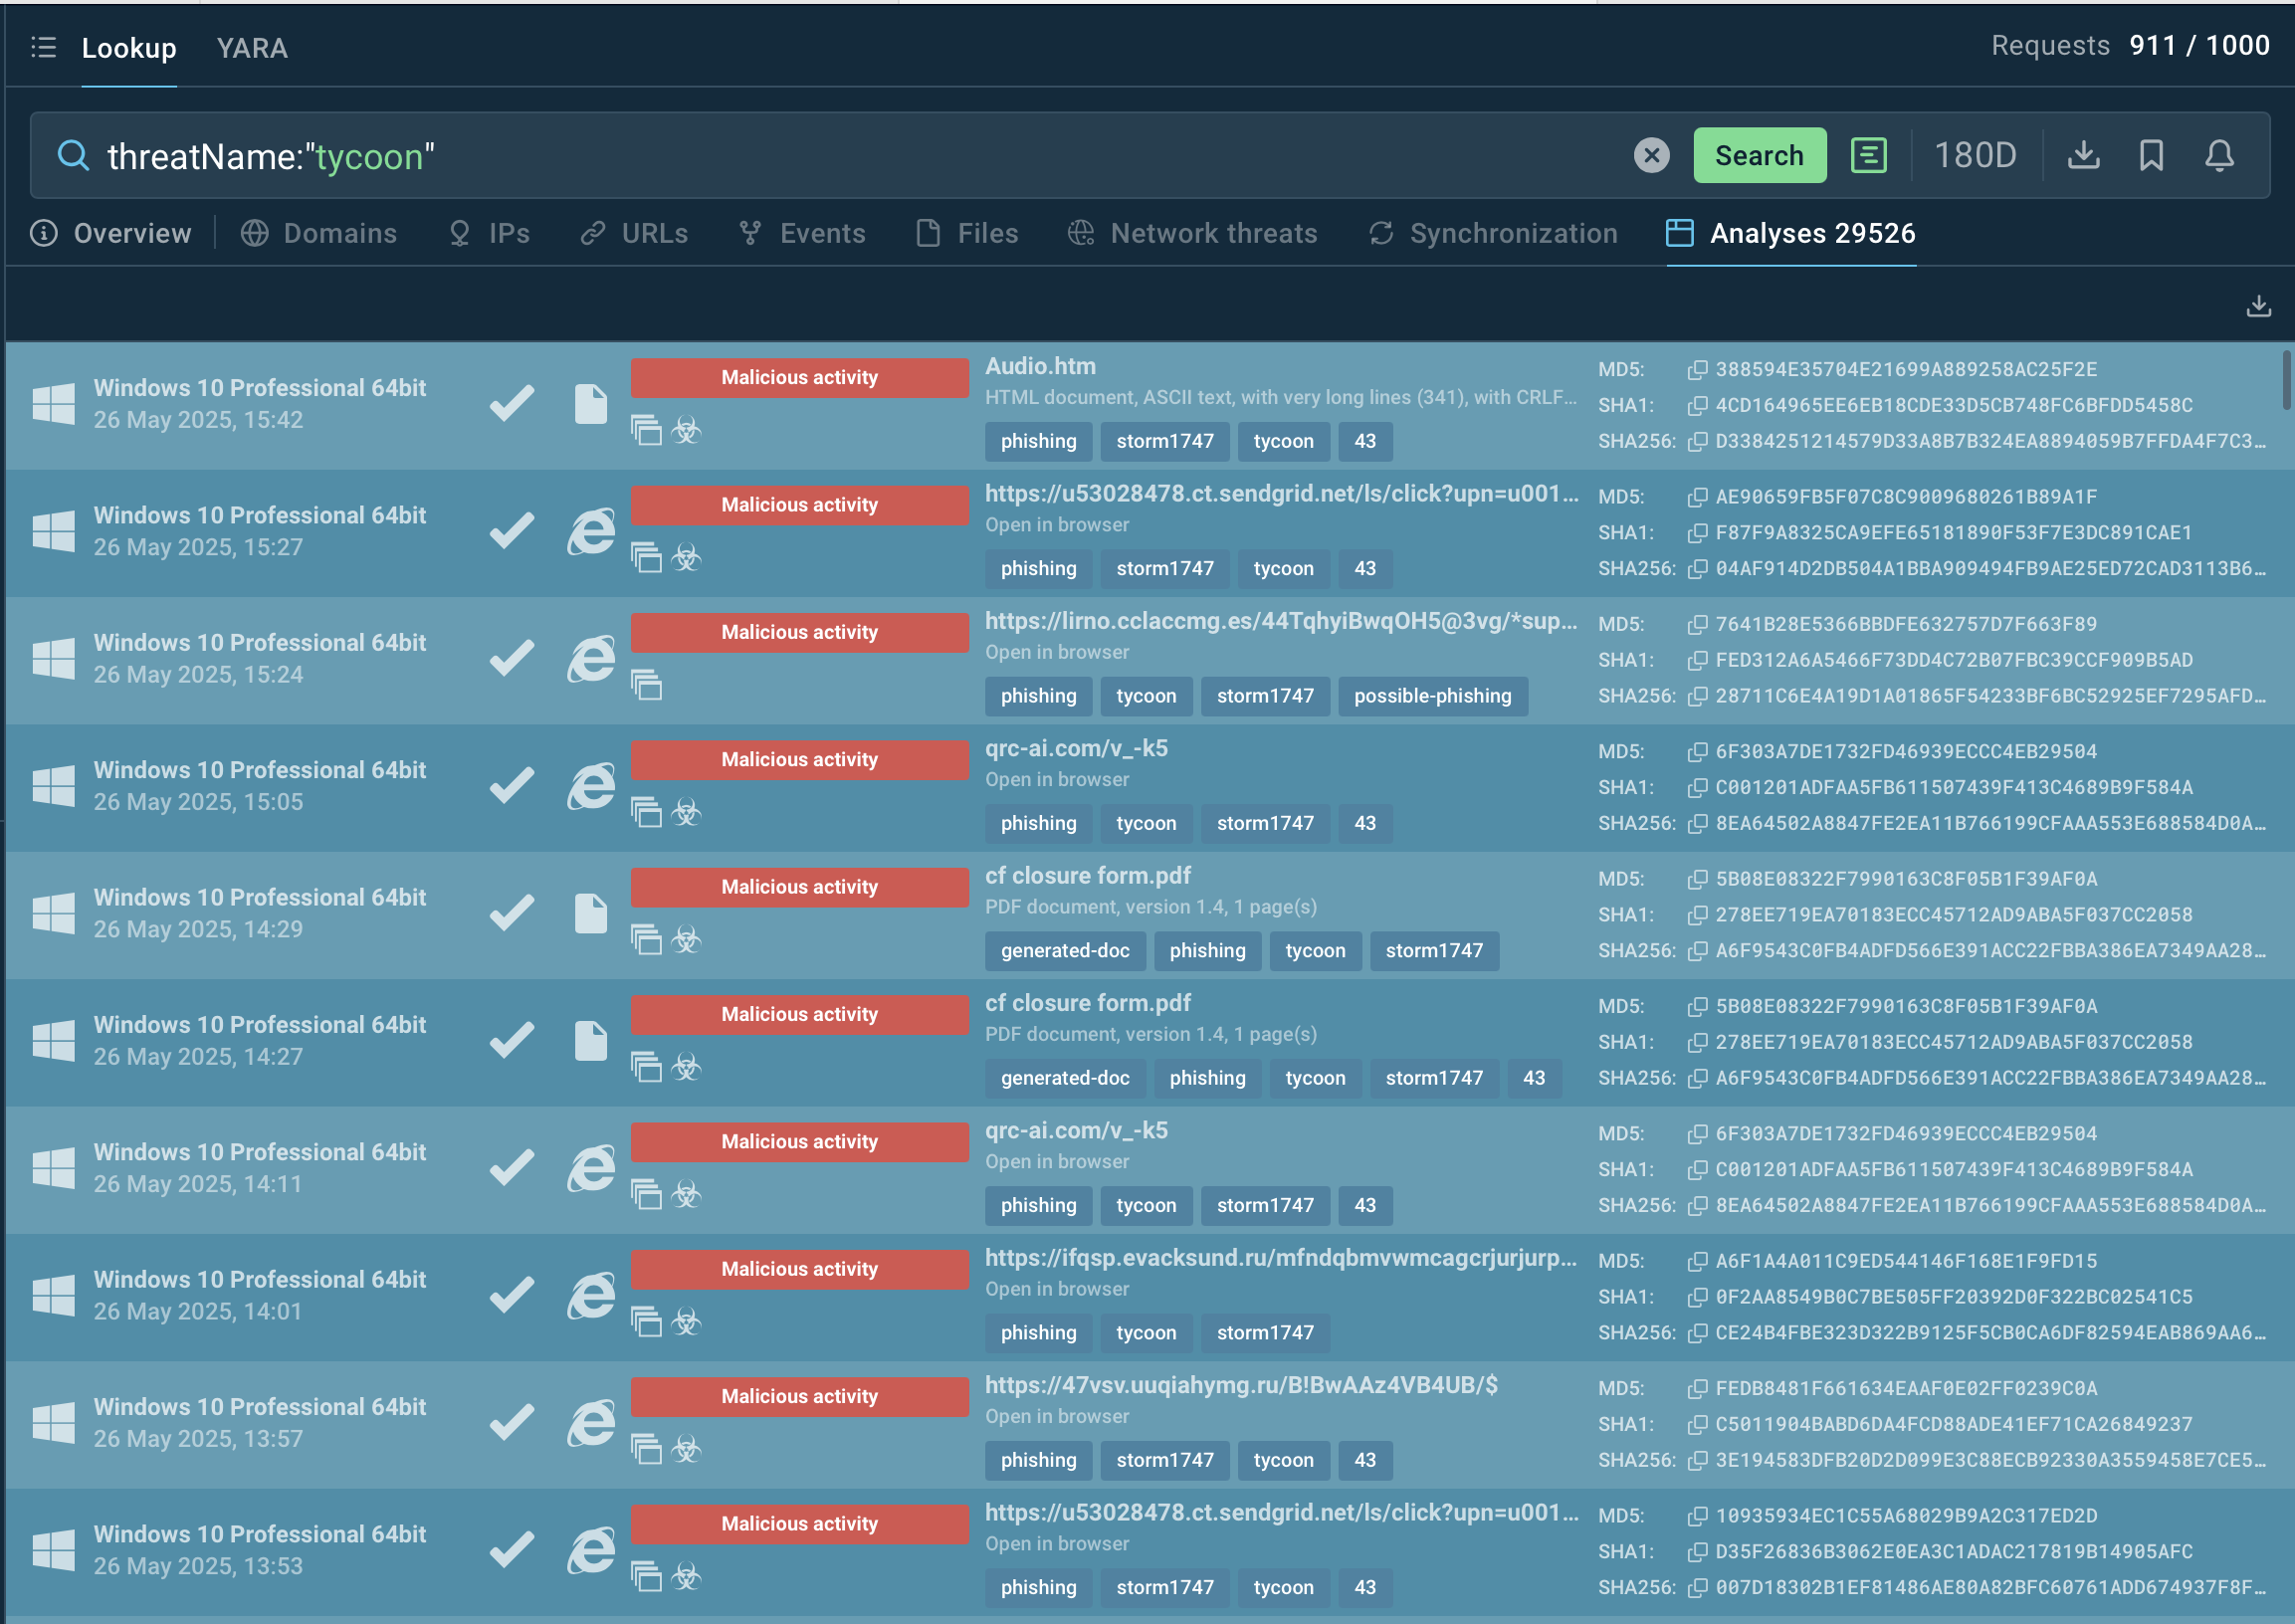
threatName:"tycoon"

Tycoon 2FA samples Sandbox malware analyses featuring Tycoon 2FA
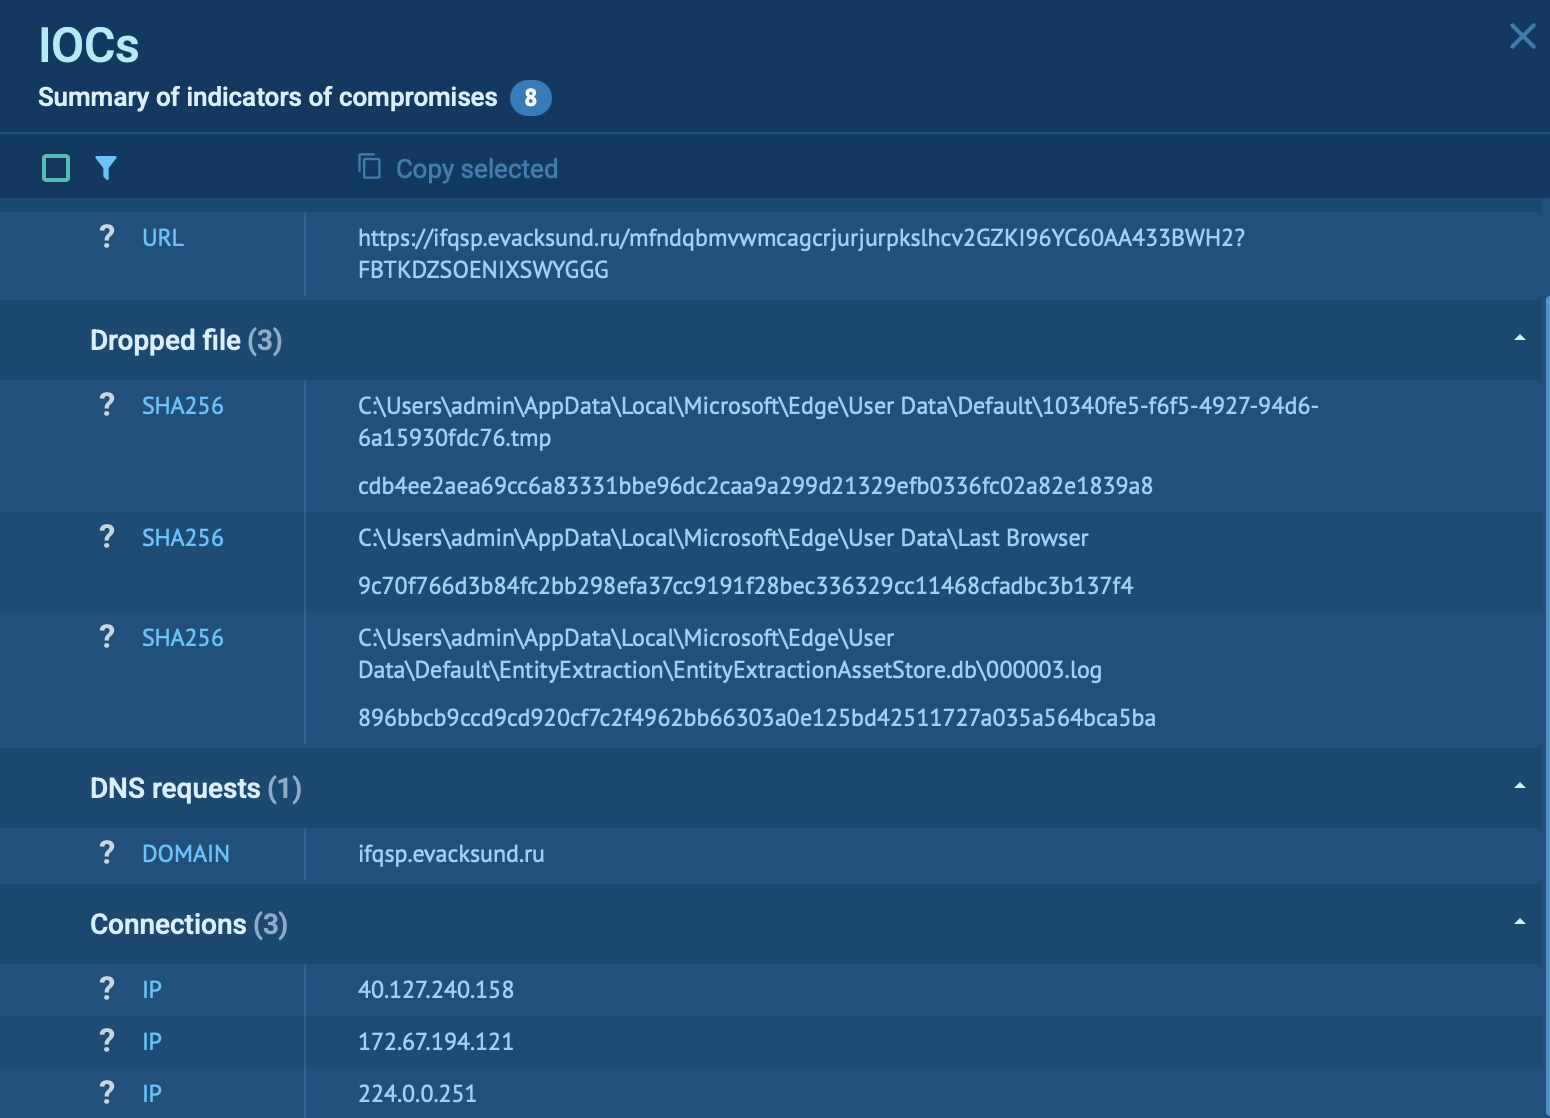
Tycoon 2FA IOCs in Sandbox Tycoon 2FA IOCs extracted from a malware sample

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Tycoon 2FA is an evolved phishing kit that poses a significant threat due to its ability to bypass MFA, leverage legitimate infrastructure, and employ advanced evasion techniques like invisible Unicode obfuscation, custom CAPTCHAs, and anti-debugging scripts. Its ease of use and scalability make it accessible to a wide range of cybercriminals, amplifying its impact.

Detection and counteraction require a combination of behavioral monitoring, advanced threat intelligence, phish-resistant MFA, and user awareness.

Use Threat Intelligence Lookup to shoot Tycoon 2FA on approach: start with 50 trial searches.
HAVE A LOOK AT

UpCrypter screenshot
UpCrypter
upcrypter
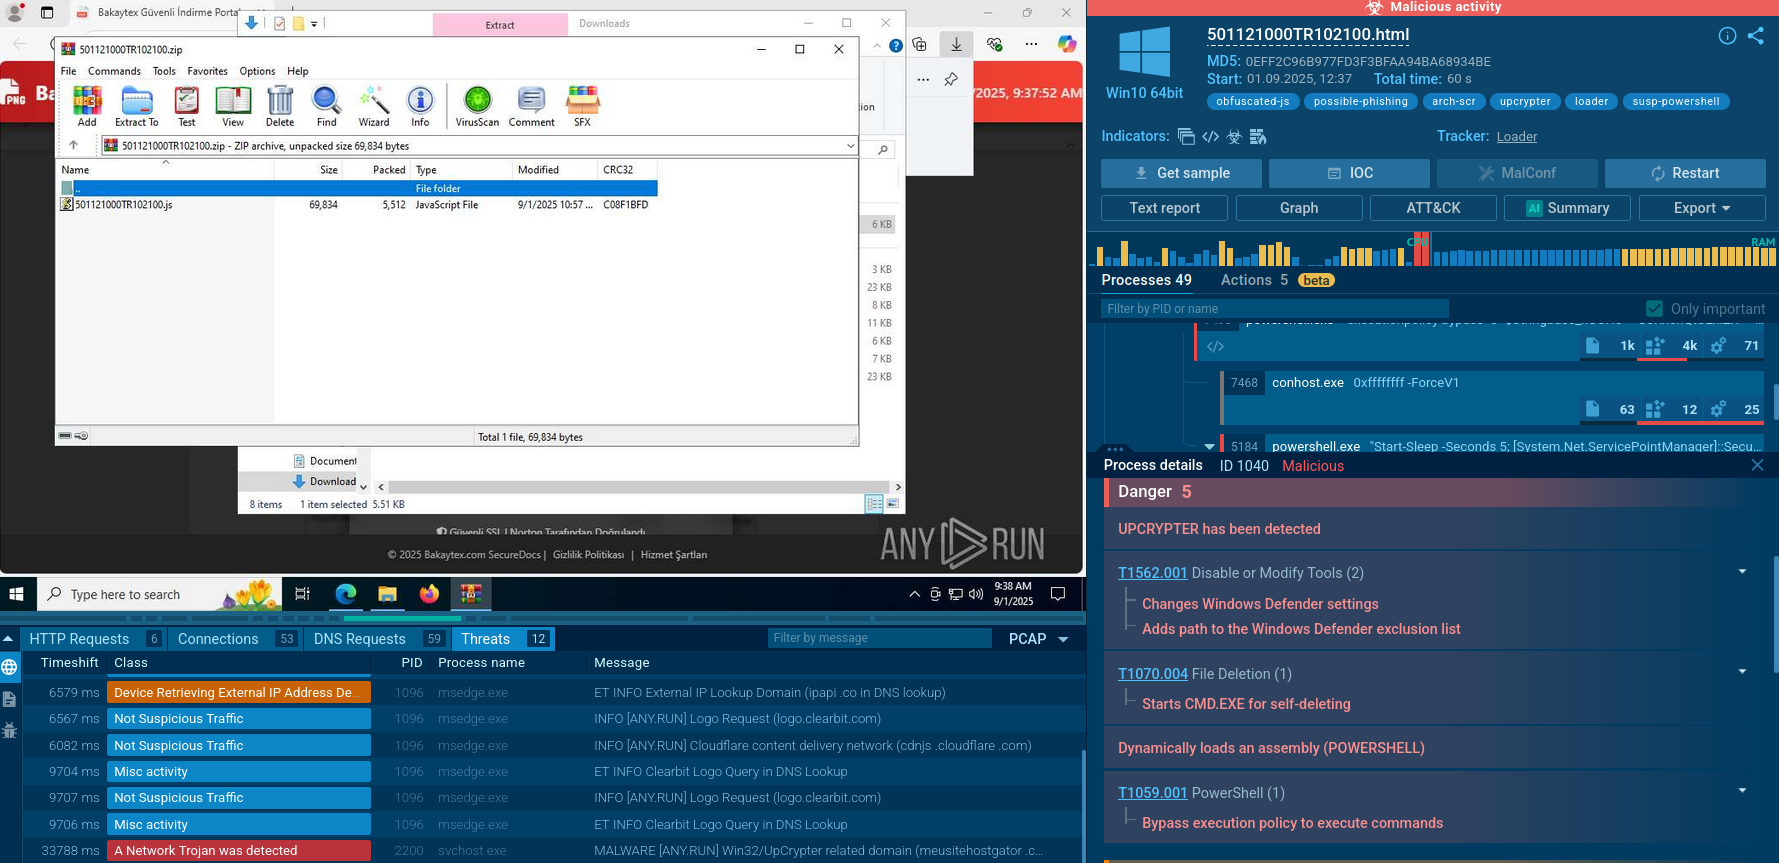
UpCrypter is a sophisticated malware loader that functions as a delivery mechanism for remote access tools. Distributed through global phishing campaigns targeting Windows systems, this actively maintained tool serves as the central framework for deploying various RATs including PureHVNC, DCRat, and Babylon RAT, enabling attackers to establish persistent remote control over compromised systems.
Read More
LokiBot screenshot
LokiBot
lokibot loader trojan
LokiBot was developed in 2015 to steal information from a variety of applications. Despite the age, this malware is still rather popular among cybercriminals.
Read More
ClickFix screenshot
ClickFix is a sophisticated social engineering technique that tricks users into manually executing malicious commands on their devices. It masquerades as a "quick fix" for fake technical issues, CAPTCHA verifications, or error messages, often hijacking the clipboard to paste harmful PowerShell or terminal commands. This user-assisted approach helps it bypass traditional security controls, leading to infostealers like Lumma Stealer, RATs, and other malware.
Read More
Crocodilus screenshot
Crocodilus
crocodilus
Crocodilus is a highly sophisticated Android banking Trojan that emerged in March 2025, designed for full device takeover. Disguised as legitimate apps, it steals banking credentials, cryptocurrency wallet data, and enables remote control, rapidly evolving into a global threat targeting financial users across Europe, South America, and Asia.
Read More
CryptoWall screenshot
CryptoWall
cryptowall
CryptoWall is a notorious ransomware family that emerged in early 2014 and rapidly became one of the most destructive cyber threats of its time. This malware encrypts victims' files using strong AES encryption, demands ransom payments in Bitcoin, and has generated hundreds of millions of dollars for cybercriminals.
Read More
DragonForce screenshot
DragonForce
dragonforce
DragonForce is a ransomware strain operating under the Ransomware-as-a-Service (RaaS) model. First reported in December 2023, it encrypts files with ChaCha8, renames them with random strings, and appends “.dragonforce_encrypted.” By disabling backups, wiping recovery, and spreading across SMB shares, DragonForce maximizes damage and pressures victims into multimillion-dollar ransom negotiations. It has targeted manufacturing, construction, IT, healthcare, and retail sectors worldwide, making it a severe threat to modern enterprises.
Read More