Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Virlock

119
Global rank
93 infographic chevron month
Month rank
93 infographic chevron week
Week rank

Virlock is a unique ransomware strain that combines encryption capabilities with file infection techniques. First observed in 2014, it stands out due to its polymorphic nature and ability to embed its code into compromised files, ensuring continued propagation. Once it infects a system, it encrypts files and locks the screen, demanding a ransom for file recovery and system access.

Ransomware
Type
Unknown
Origin
1 December, 2014
First seen
4 October, 2026
Last seen

How to analyze Virlock with ANY.RUN

Type
Unknown
Origin
1 December, 2014
First seen
4 October, 2026
Last seen

IOCs

IP addresses
85.210.196.11
135.232.92.97
2.19.198.218
200.119.204.12
92.122.215.99
142.251.14.138
172.211.123.248
200.87.164.69
23.3.89.96
23.52.181.141
23.11.41.157
204.79.197.203
74.179.77.204
40.126.32.76
52.123.129.14
190.186.45.170
135.233.45.221
52.110.17.3
72.246.29.11
23.3.89.97
Hashes
4dc0a8afbf4dbb1a67b9292bb028b7f744f3029b0083c36307b1f84a00692a89
c02029ff5ab6a02609696cd2fec95ddf19af86a81ad8e8b3d9282b01ef6622d8
0f015363e17b4320aa73bb7db01a87773bb171120ef59cb9ebdc13c857df1692
ef915dd4448ccbca5796b09221c0fa2c2dab8ec950b631f8a7a5942915bc7cf8
c327c0485909f634c456cea42f7db6353fa4942efe43a2c336d3932784c927ed
65127bddfa103894c24642aa48d89e24eb585012a08ea5480c3de01767046ba3
9e92ce536f18f7d4dc586dfe63f823c059523190b35b3a076706089b993025b4
17e73bdf62066e914e5e15cc36f393fc2c309cb8f4e407d4a9d25b3b17f99851
d9a72057efb41e5f4003e197f33fd7e2c8acc9109733dc0333bb8c0113ba2d99
081a53e5b6cf5577c773354195ad16901b24a3f7e2bbe101d0dd2b09780073f4
3a786b997d94f323c286560b2a8fc0131b2bb86db9fb54a71e284666fdd0490e
e68295eb5aecfa93fe885325400f49ae4ca1564815b42058fa4617b1d8880621
60c9e95dca328d38e7028b5b20733e12bfa97e5a21be55e345bb1af5fa4693ab
85b9f24e2fa557f230a0b2cef3290422cbc4b10c3fe52a4d683f857eb6dc9b06
35e2a7cdbdd95759d784e963fbb3e0294ae92d9c2b6ae2c256e3a48d78702e6e
323353b3adc7a579c5ba2cabf5e03552121f1f22dcd44bda962c8bdb01d987fd
47fe817237f0b3f86bcc6530e45d794f9f9c6da34ff4f9958b8fbb955dcb81a2
c81e5fb092b620e5b143f55da7611896483945d82b28629d44398d0990d94f79
f6bd9de6b0bd6a87b37dc006c1018e34bf138a0f49f390953b094391f5338680
e5e496a9d4969a188a55aa9fbfa06a76f314829623ddca20fa4de4a439b1cfdc
Domains
activation-v2.sls.microsoft.com
go.microsoft.com
dns.msftncsi.com
google.com
ocsp.digicert.com
fe3cr.delivery.mp.microsoft.com
nexusrules.officeapps.live.com
self.events.data.microsoft.com
www.bing.com
www.microsoft.com
login.live.com
oneocsp.microsoft.com
settings-win.data.microsoft.com
ecs.office.com
crl.microsoft.com
watson.events.data.microsoft.com
slscr.update.microsoft.com
client.wns.windows.com
officeclient.microsoft.com
edge.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://google.com/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://officeclient.microsoft.com/config16/?syslcid=1033&build=16.0.16026&crev=3
https://ecs.office.com/config/v2/office/officeclicktorun/16.0.16026.20140/production/cc?&clientid=%7b48ba7fdf-353c-4fe5-8d8f-9e31911a3891%7d&application=officeclicktorun&platform=win32&version=16.0.16026.20140&msoversion=16.0.16026.20140&processname=officeclicktorun.exe&audience=production&build=ship&architecture=x64&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7b05d4952b-d354-4a1c-9aea-8525263ac8d4%7d&labmachine=false
https://login.live.com/ppsecure/deviceaddcredential.srf
https://www.bing.com/rp/anzunpnvy0ol0xwxs0rljxjjluo.br.js
https://www.bing.com/threshold/xls.aspx
https://www.bing.com/web/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/manifest/threshold.appcache
https://www.bing.com/as/api/windowscortanapane/v2/init
https://www.bing.com/rb/1e/cc,nc/8qgg5w3ncsqflirnejktkex2-pa.css?bu=ehmbcockexmxcnmdcp8kexl5qgqscnl5&or=w
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is Virlock ransomware?

Virlock is a unique form of ransomware that combines traditional file encryption with virus-like propagation methods. First identified in 2014, it not only encrypts files but also embeds its malicious code into them, allowing it to spread across systems via shared drives and removable media. Once executed, Virlock locks the victim's screen and displays a ransom note, often masquerading as a legal warning, demanding payment for file recovery and system access.

You can see an example of a ransom note displayed inside ANY.RUN’s sandbox:
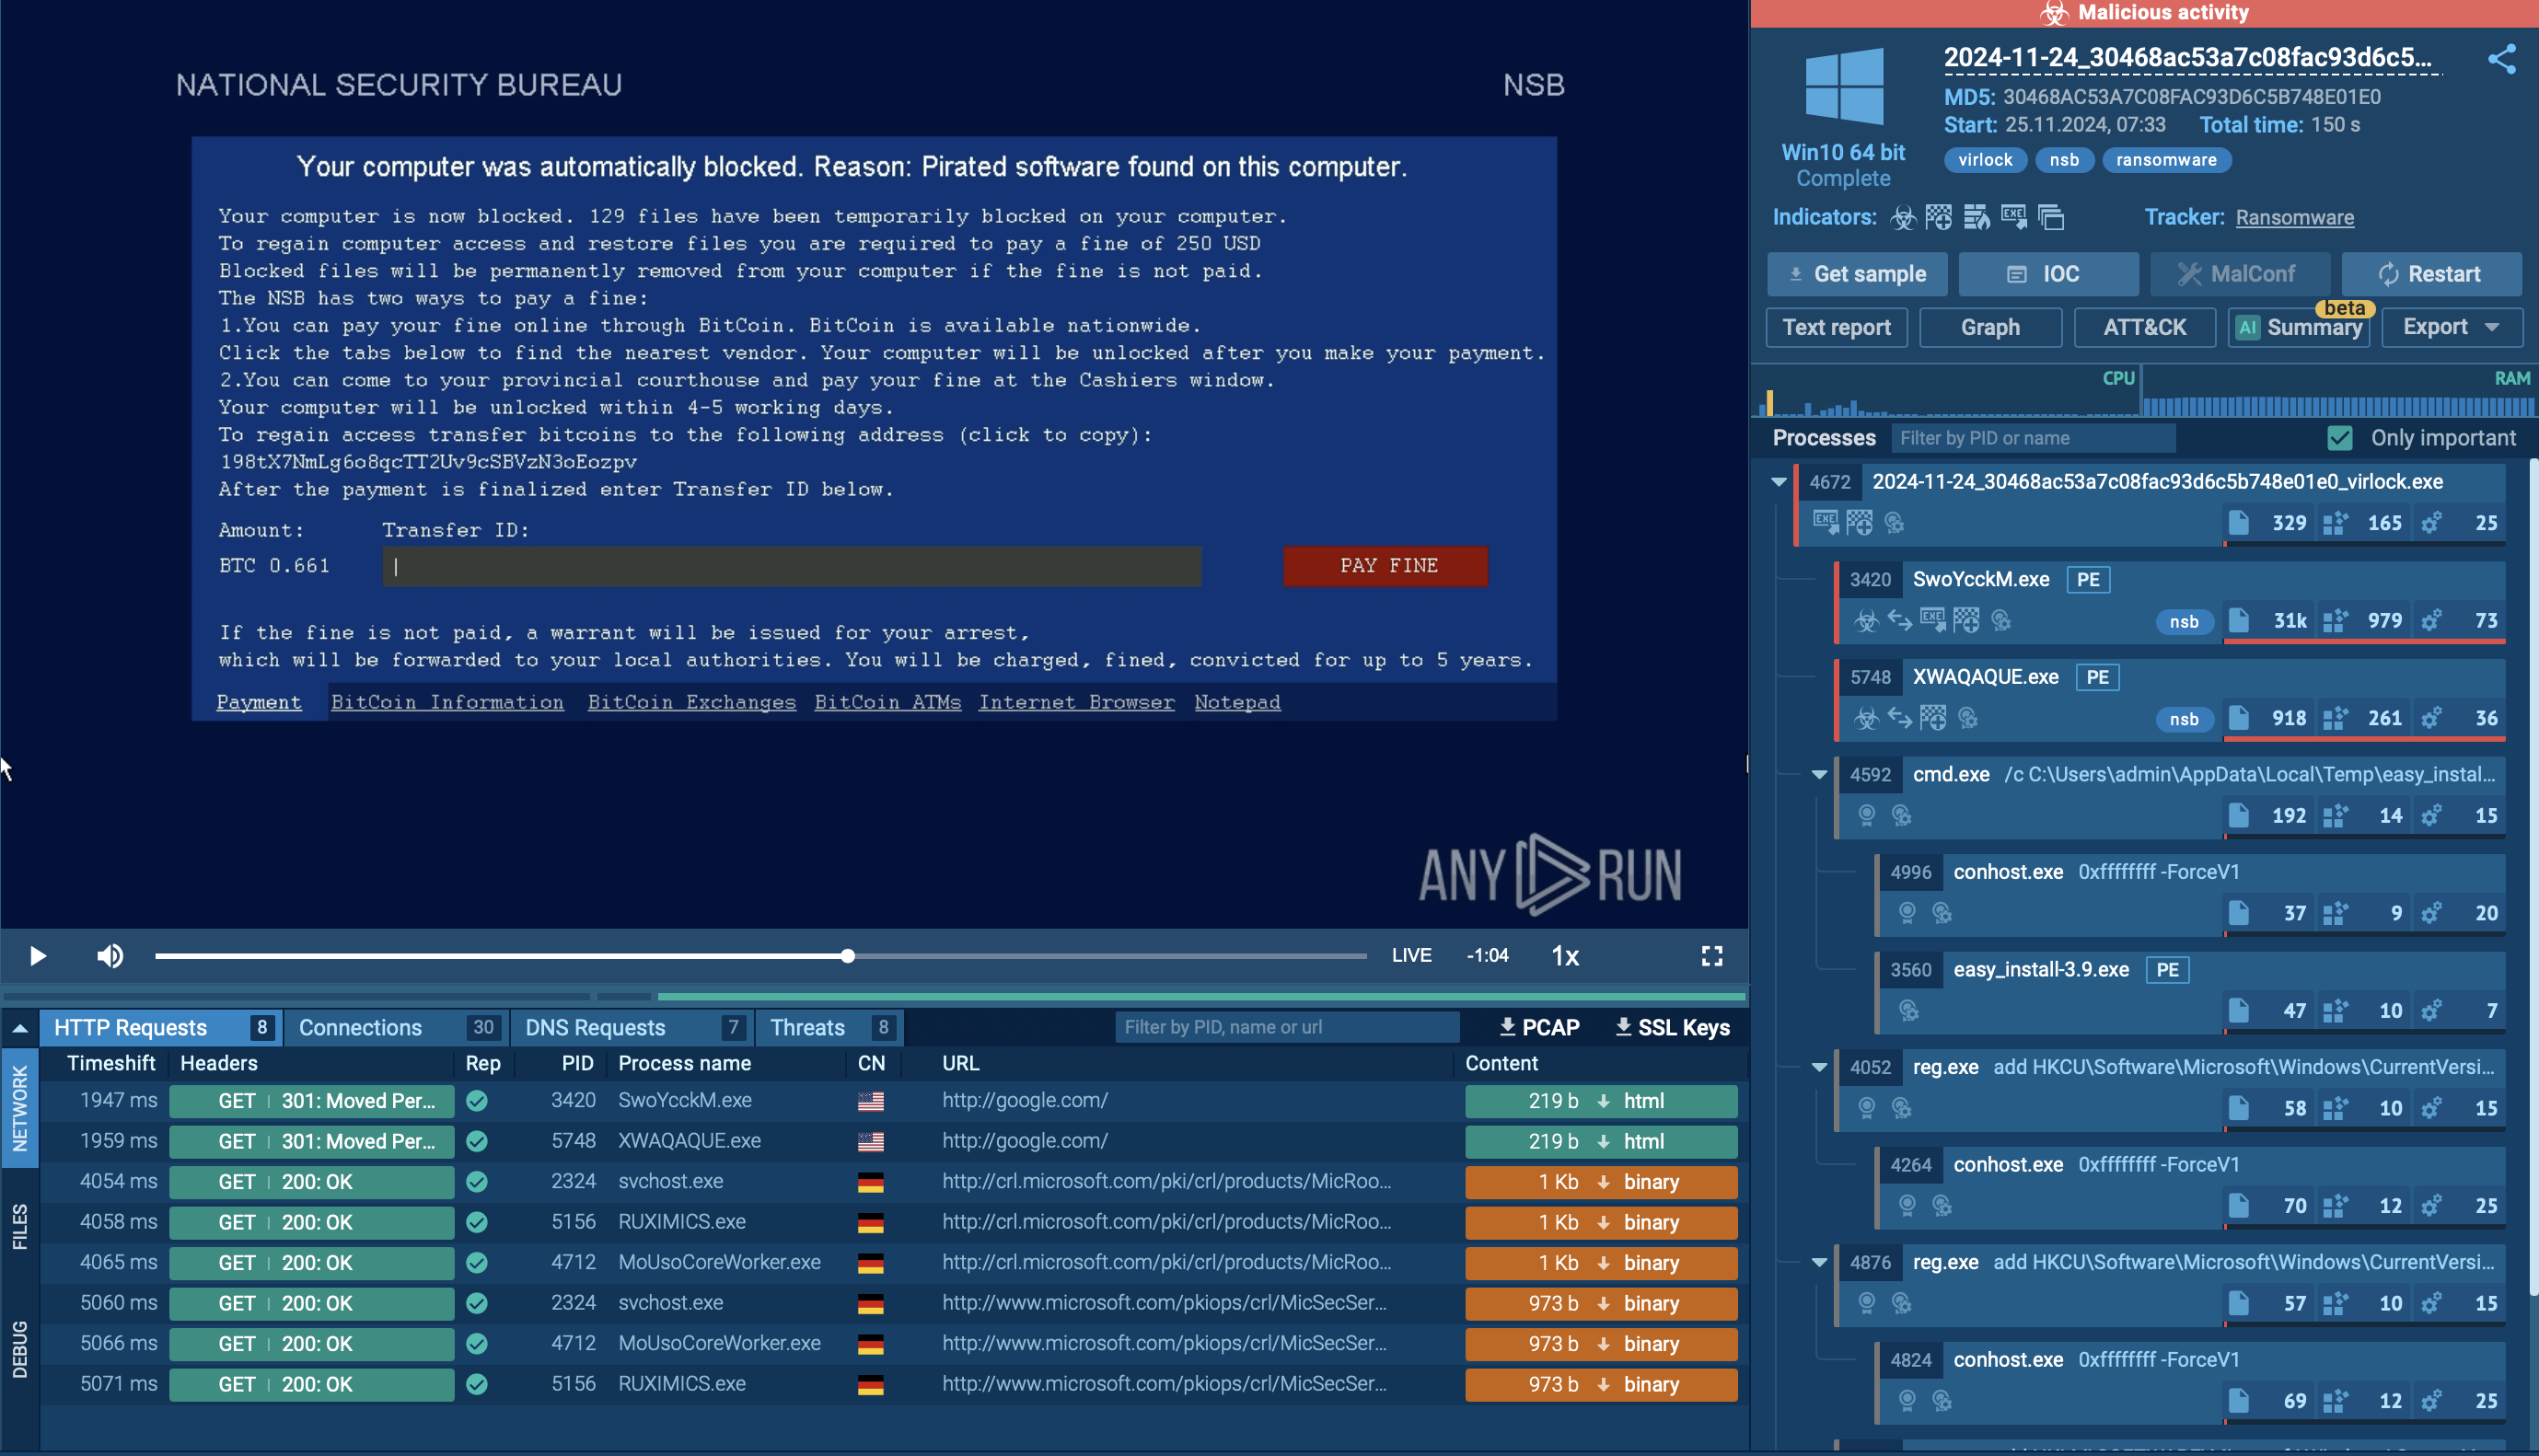
Virlock note in ANY.RUN sandbox Ransom note displayed in ANY.RUN sandbox

While specific large-scale attacks attributed solely to Virlock are not extensively documented, its unique propagation method poses significant risks, especially in environments that rely heavily on file sharing and collaboration tools. In 2016, security researchers highlighted Virlock's capability to spread through cloud storage and collaboration applications, emphasizing the potential for rapid, widespread infection within organizations.

Virlock's ability to both encrypt files and convert them into infectious agents makes it particularly dangerous. Even if a ransom is paid, residual infected files can lead to reinfection.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Virlock ransomware technical details

Virlock employs polymorphic techniques to evade detection. It changes its code structure with each infection, making it difficult for traditional signature-based antivirus solutions to recognize and block it.

The primary technical functionalities of Virlock ransomware include:

  • Alters its code structure with each infection to evade signature-based detection.
  • Embeds itself into various file types, converting them into carriers of the malware.
  • Displays a full-screen ransom message, preventing user access to the system.
  • Encrypts user files, rendering them inaccessible without a decryption key.
  • Spreads through shared applications and cloud storage platforms.
  • Modifies system registry entries to ensure it runs upon system startup.
  • Employs methods to hinder analysis and detection by security tools.
  • Customizes ransom messages based on the victim's geographic location.
  • Registers itself as a service to maintain persistence on the infected system.
  • Disables task manager and explorer processes to prevent user intervention.

The Virlock ransomware employs several layers of encryption, including XOR and XOR-ROL (rotate left) algorithms, to obfuscate its code and hinder analysis.

After infecting files, Virlock appends an .exe extension and modifies system settings to hide file extensions, making it harder for users to identify infected files.

Besides, this ransomware drops multiple instances of itself in different locations and registers them as services or startup entries, ensuring it remains active even if some instances are removed.

Virlock ransomware execution process

To see how Virlock operates, let’s upload its sample into ANY.RUN’s sandbox.

When Virlock is executed on a non-infected machine, it initiates by deploying three instances of itself, each with a specific function:
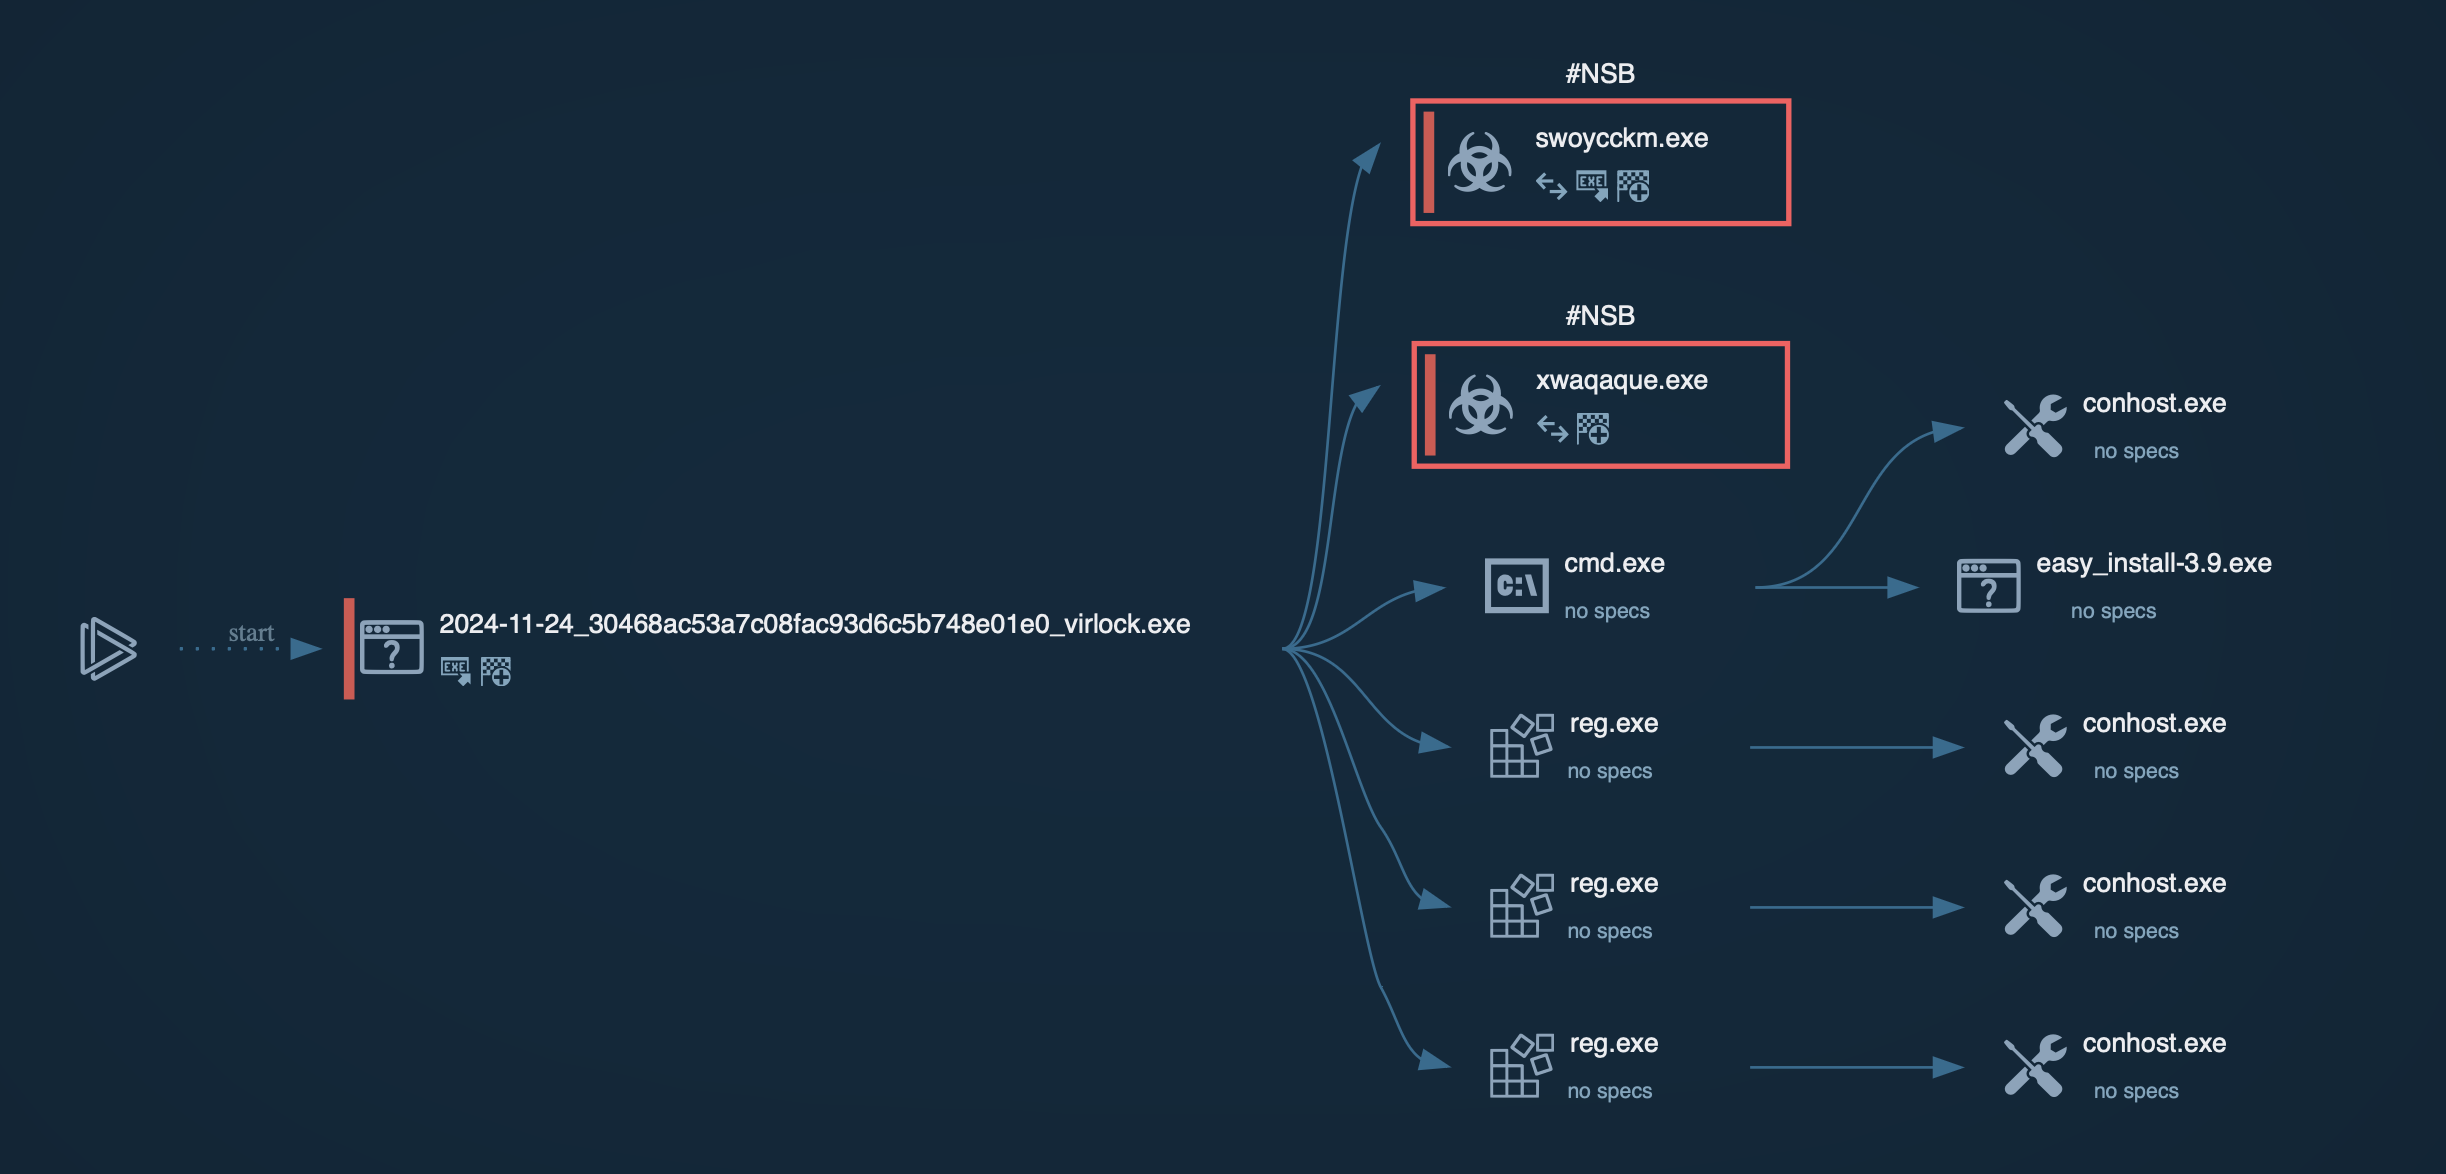
  • Instance one: Responsible for infecting files.
  • Instance two: Locks the victim's screen.
  • Instance three: Establishes persistence by registering as a Windows service.

Process graph of Virlock in ANY.RUN sandbox Process graph generated by ANY.RUN sandbox

Virlock targets various file types, including documents and binary files. Upon locating these files, it encrypts their contents and appends its malicious code to the original file. This process transforms each infected file into a carrier capable of further spreading the ransomware. Any user who opens an infected file inadvertently activates the malware, enabling it to propagate within networks, particularly in cloud environments.
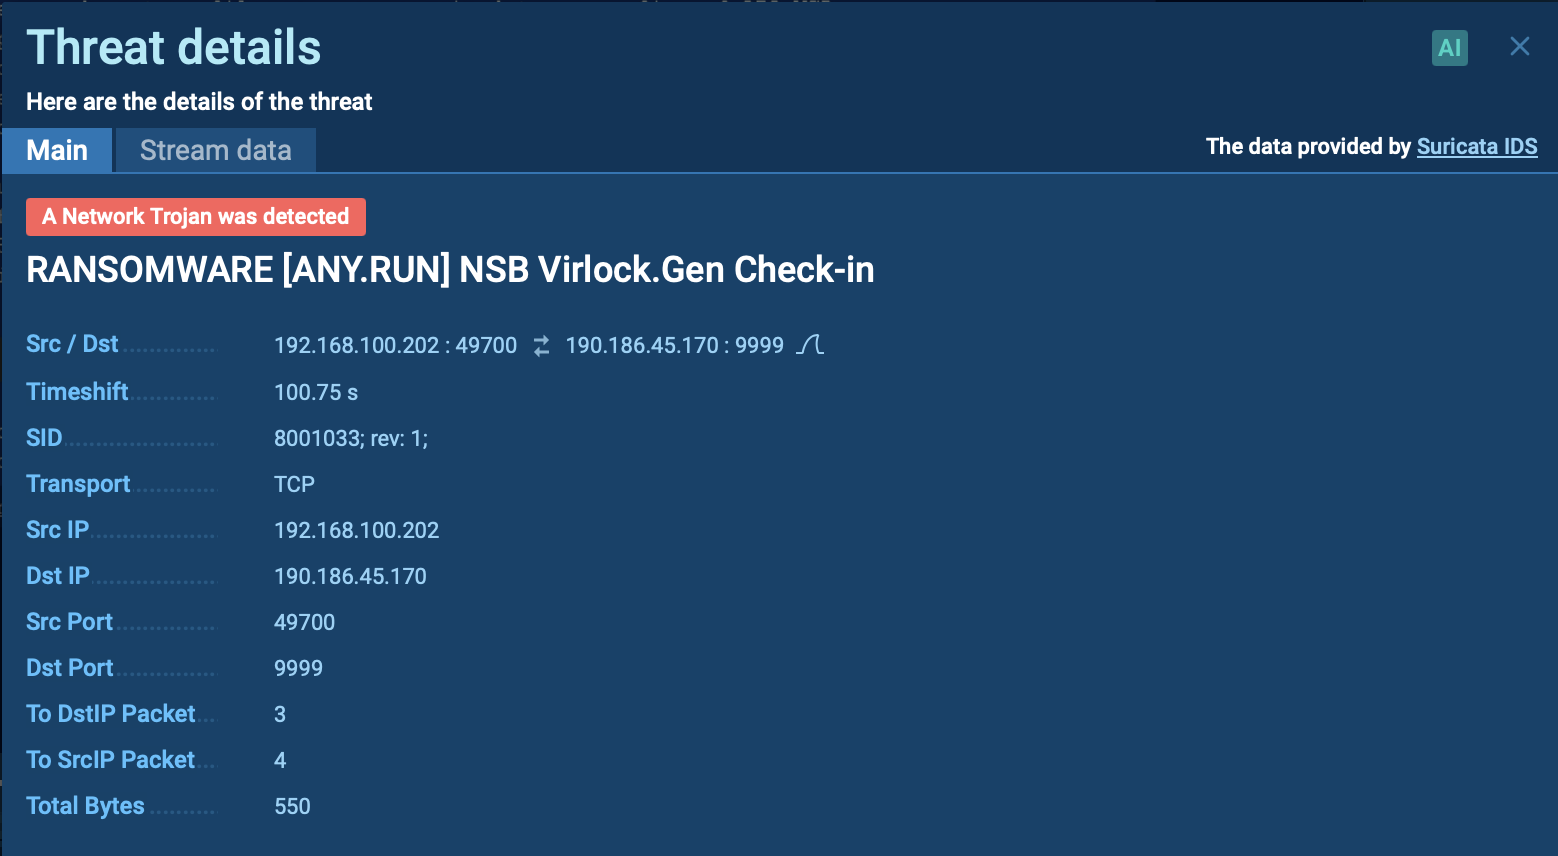
Suricata rule of Virlock in ANY.RUN sandbox Suricata rule triggered by Virlock ransomware inside ANY.RUN’s sandbox

To ensure its continued operation even after system reboots, Virlock modifies the Windows registry:

  • It adds entries to the Run registry keys under both HKCU (Current User) and HKLM (Local Machine), ensuring that its instances are executed automatically at startup.
  • The third instance registers itself as a Windows service, maintaining persistence and functionality even if terminated manually.

During its operation, the second instance disables critical system processes such as explorer.exe and taskmgr.exe, effectively locking the victim’s screen.

It also customizes the ransom message based on the victim's geolocation, demanding payment in Bitcoin to unlock the system. The ransom note often masquerades as an anti-piracy warning from law enforcement, threatening legal consequences to pressure victims into paying quickly.
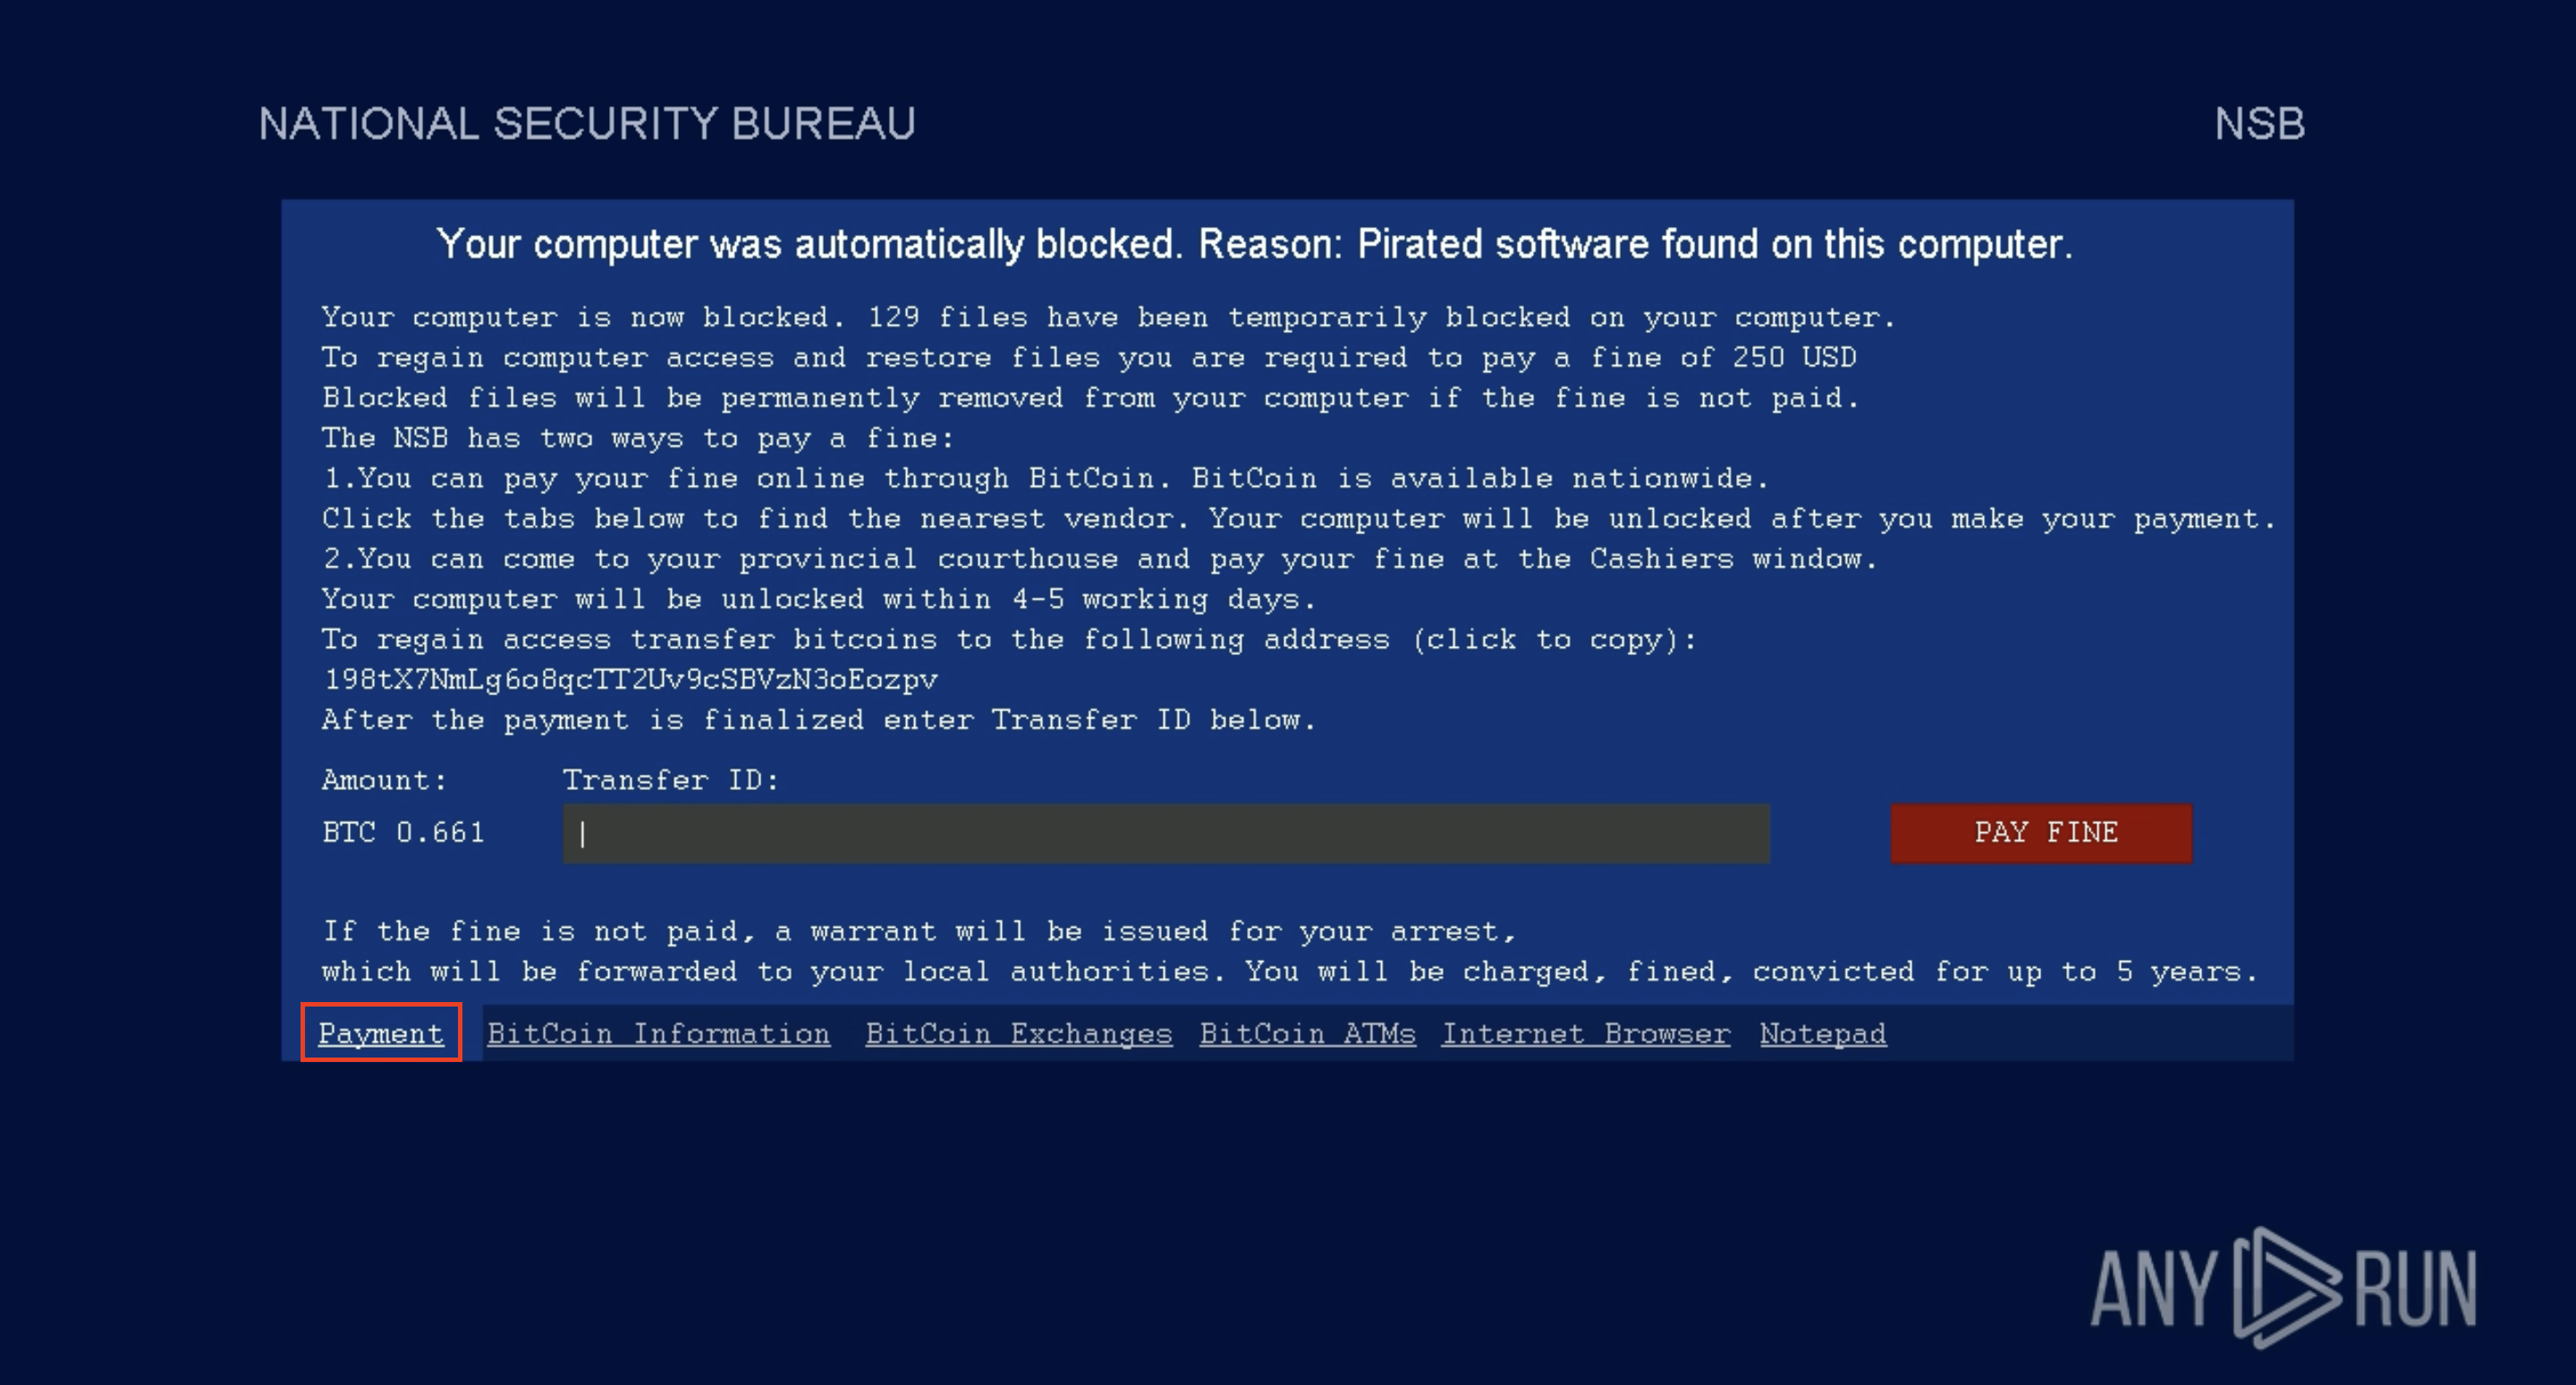
Ransom note of Virlock in ANY.RUN sandbox Virlock ransom note requiring payment in Bitcoin

Virlock employs a variety of anti-debugging measures and heavily obfuscated code to hinder analysis and detection:

  • It uses XOR encryption for its payloads, complicating the efforts of traditional antivirus solutions to identify and neutralize the ransomware.
  • Dynamic code execution and frequent polymorphic changes make its detection challenging.

The ransom note leverages social engineering to manipulate victims, presenting itself as a warning from legal authorities. This tactic is designed to create urgency and confusion, leaving victims less likely to explore alternative options before complying with the ransom demands

Virlock ransomware distribution methods

  • Email attachments: Virlock is often delivered through phishing emails containing malicious attachments. When recipients open these attachments, the ransomware executes and infects the system.
  • Malicious URLs: Attackers use deceptive links in emails or on compromised websites. Clicking these links can initiate the download and execution of Virlock.
  • Infected executable files: Virlock embeds itself into executable files. Running these infected files can lead to system compromise.
  • Cloud storage and collaboration tools: Virlock can spread through shared applications and cloud storage platforms. Infected files uploaded to these services can propagate the ransomware to other users who download and open them.
  • Removable media: The ransomware can infect files on USB drives or other removable media. When these devices are connected to another system, the malware can spread.
  • Network shares: Virlock can propagate through network shares by infecting files accessible to multiple users, facilitating its spread within organizational networks.

Gathering Threat Intelligence on Virlock Ransomware

To collect up-to-date intelligence on Virlock ransomware, use Threat Intelligence Lookup.

This powerful service provides access to a vast database populated with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox. With over 40 customizable search parameters, you can search for specific data related to Virlock, including IPs, domains, file hashes, file names, and process artifacts.
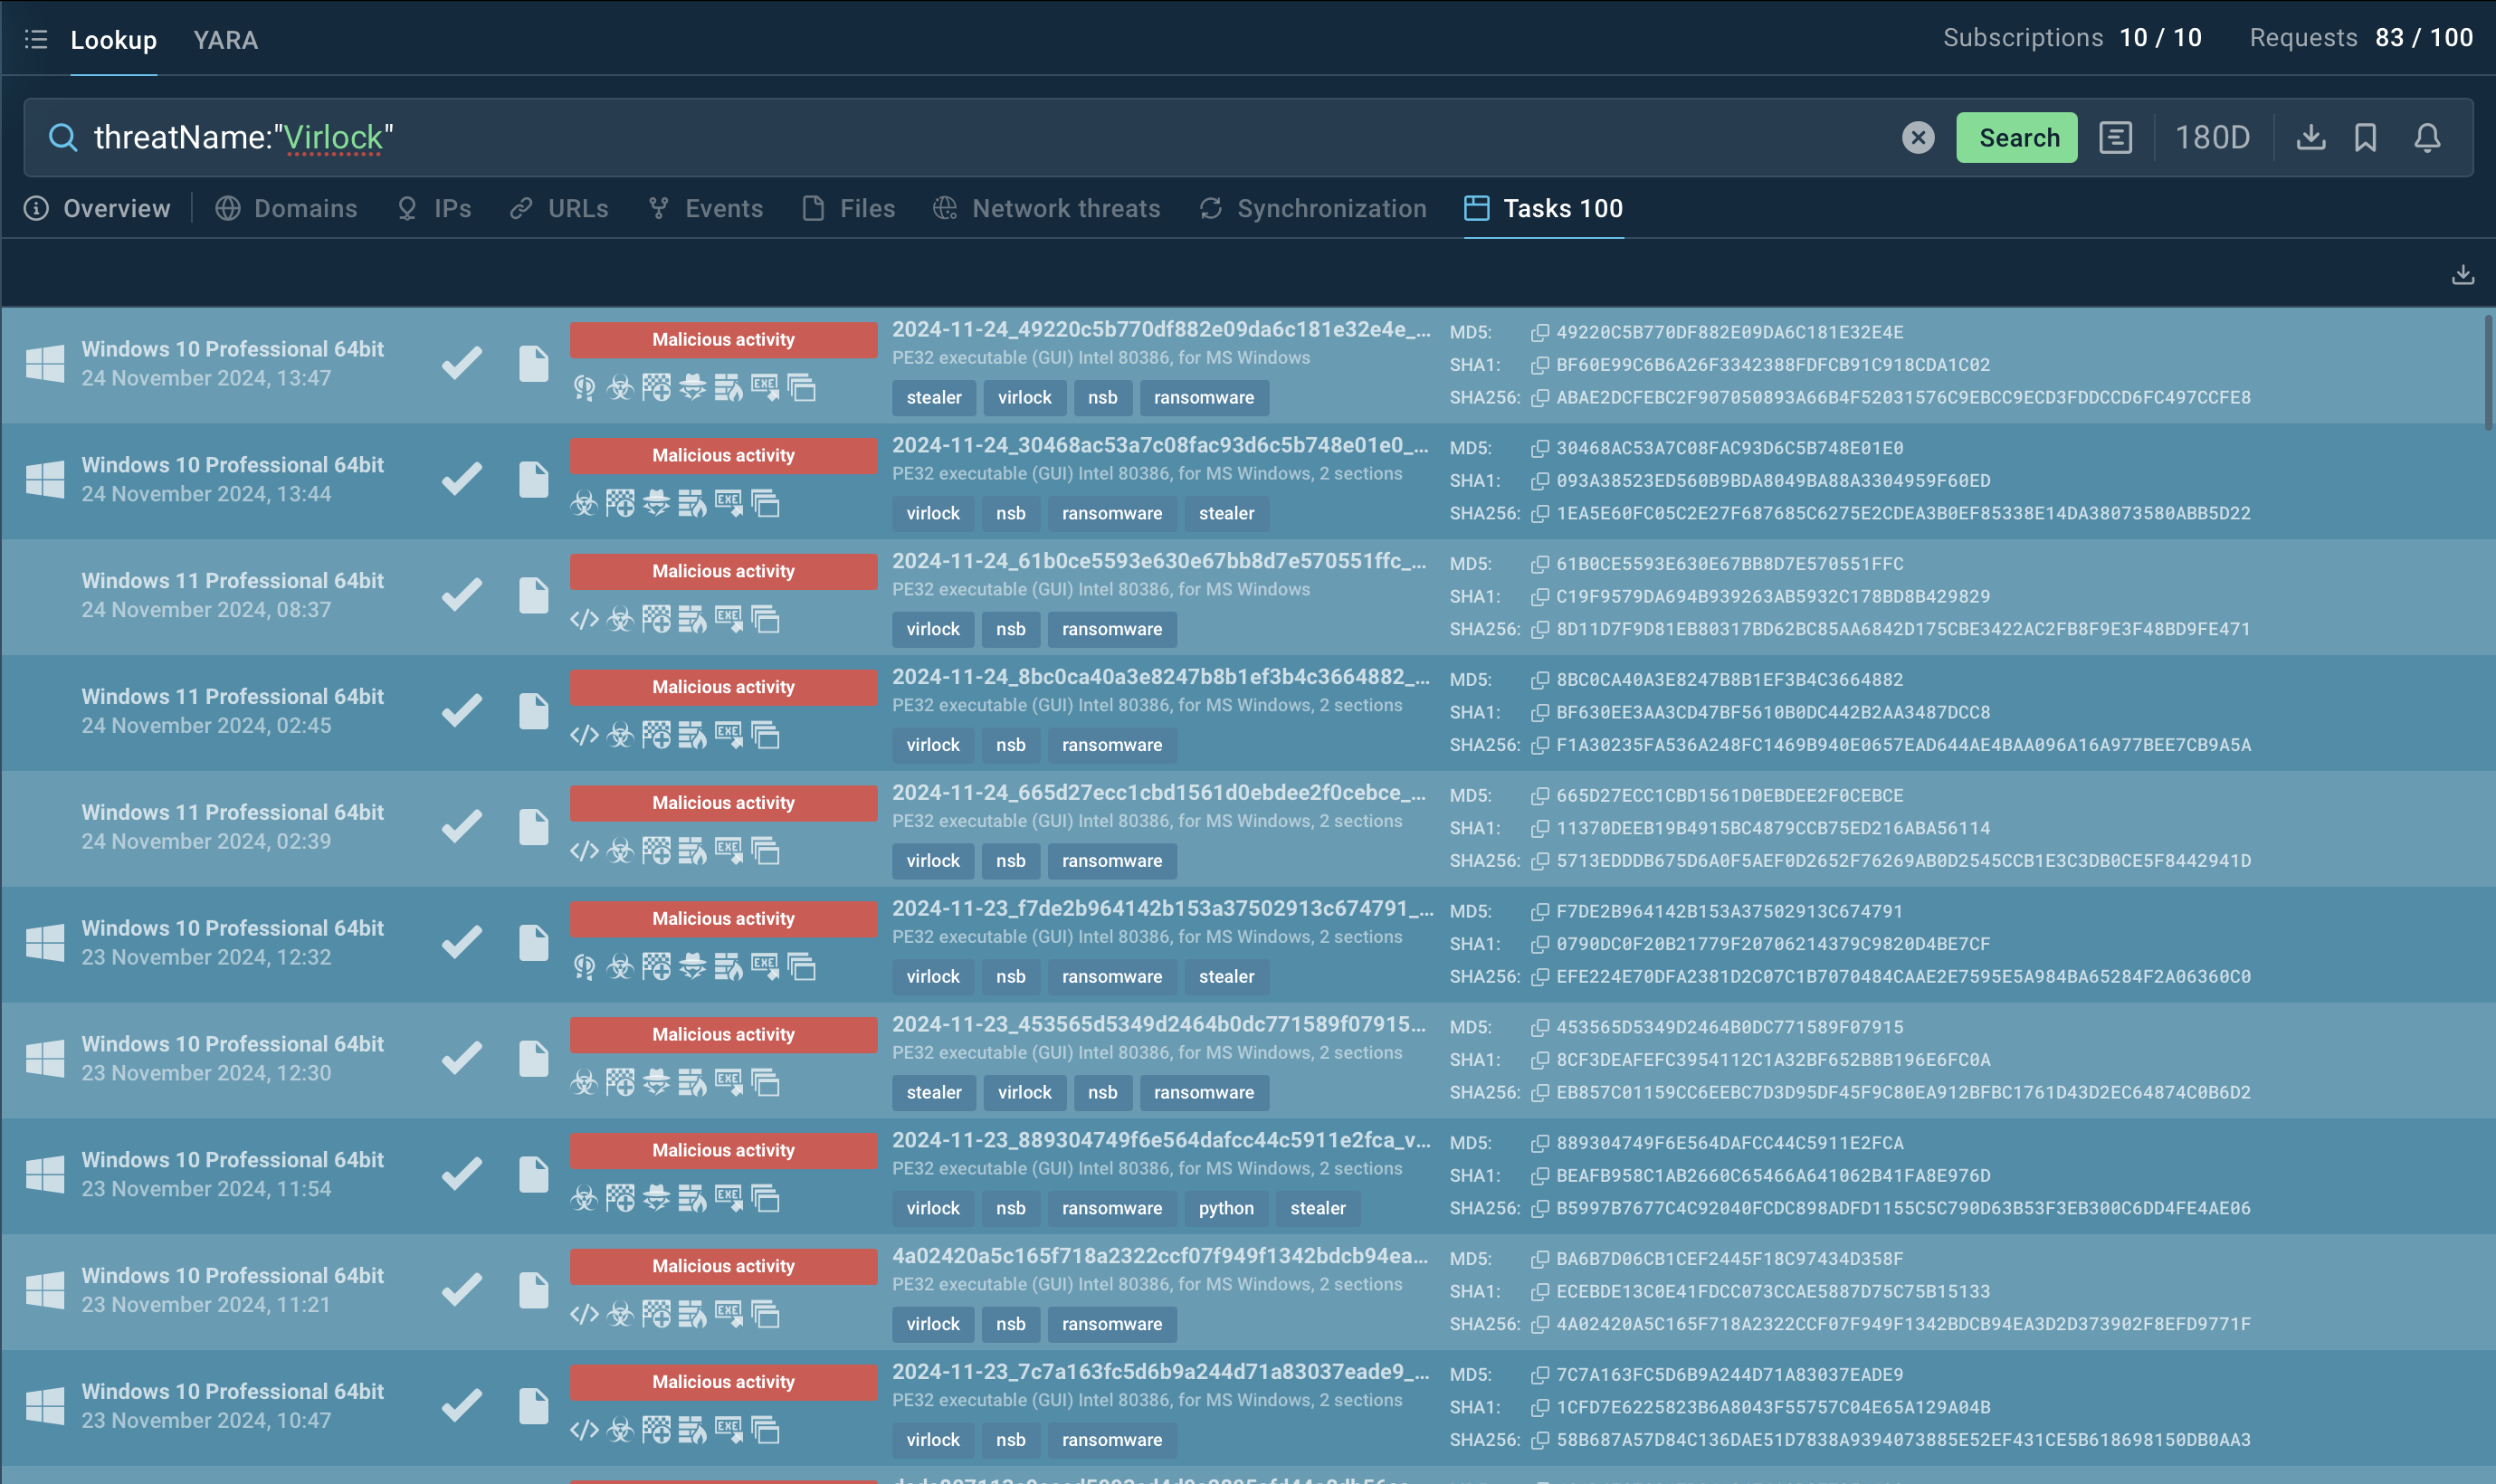
Lookup search of Virlock in ANY.RUN sandbox Virlock Lookup Search in ANY.RUN

To gather intelligence on Virlock, you can search directly for its name or use related artifacts. For example, submitting a query like threatName:"Virlock" in Threat Intelligence Lookup will return a comprehensive list of associated samples and sandbox results, giving you actionable insights into the malware's behavior and indicators of compromise.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Virlock ransomware is a serious threat due to its ability to mutate, infect files, and evade detection, making it both difficult to detect and contain. Using tools like ANY.RUN is essential for proactively analyzing suspicious files and URLs to prevent potential attacks.

ANY.RUN offers real-time malware analysis with features like dynamic sandboxing, behavior tracking, and support for Windows and Linux. Its interactive platform simplifies threat detection and provides detailed insights to enhance cybersecurity defenses.

Sign up for a free ANY.RUN account today and start analyzing emerging threats with no limits!
HAVE A LOOK AT

DeerStealer screenshot
DeerStealer
deerstealer
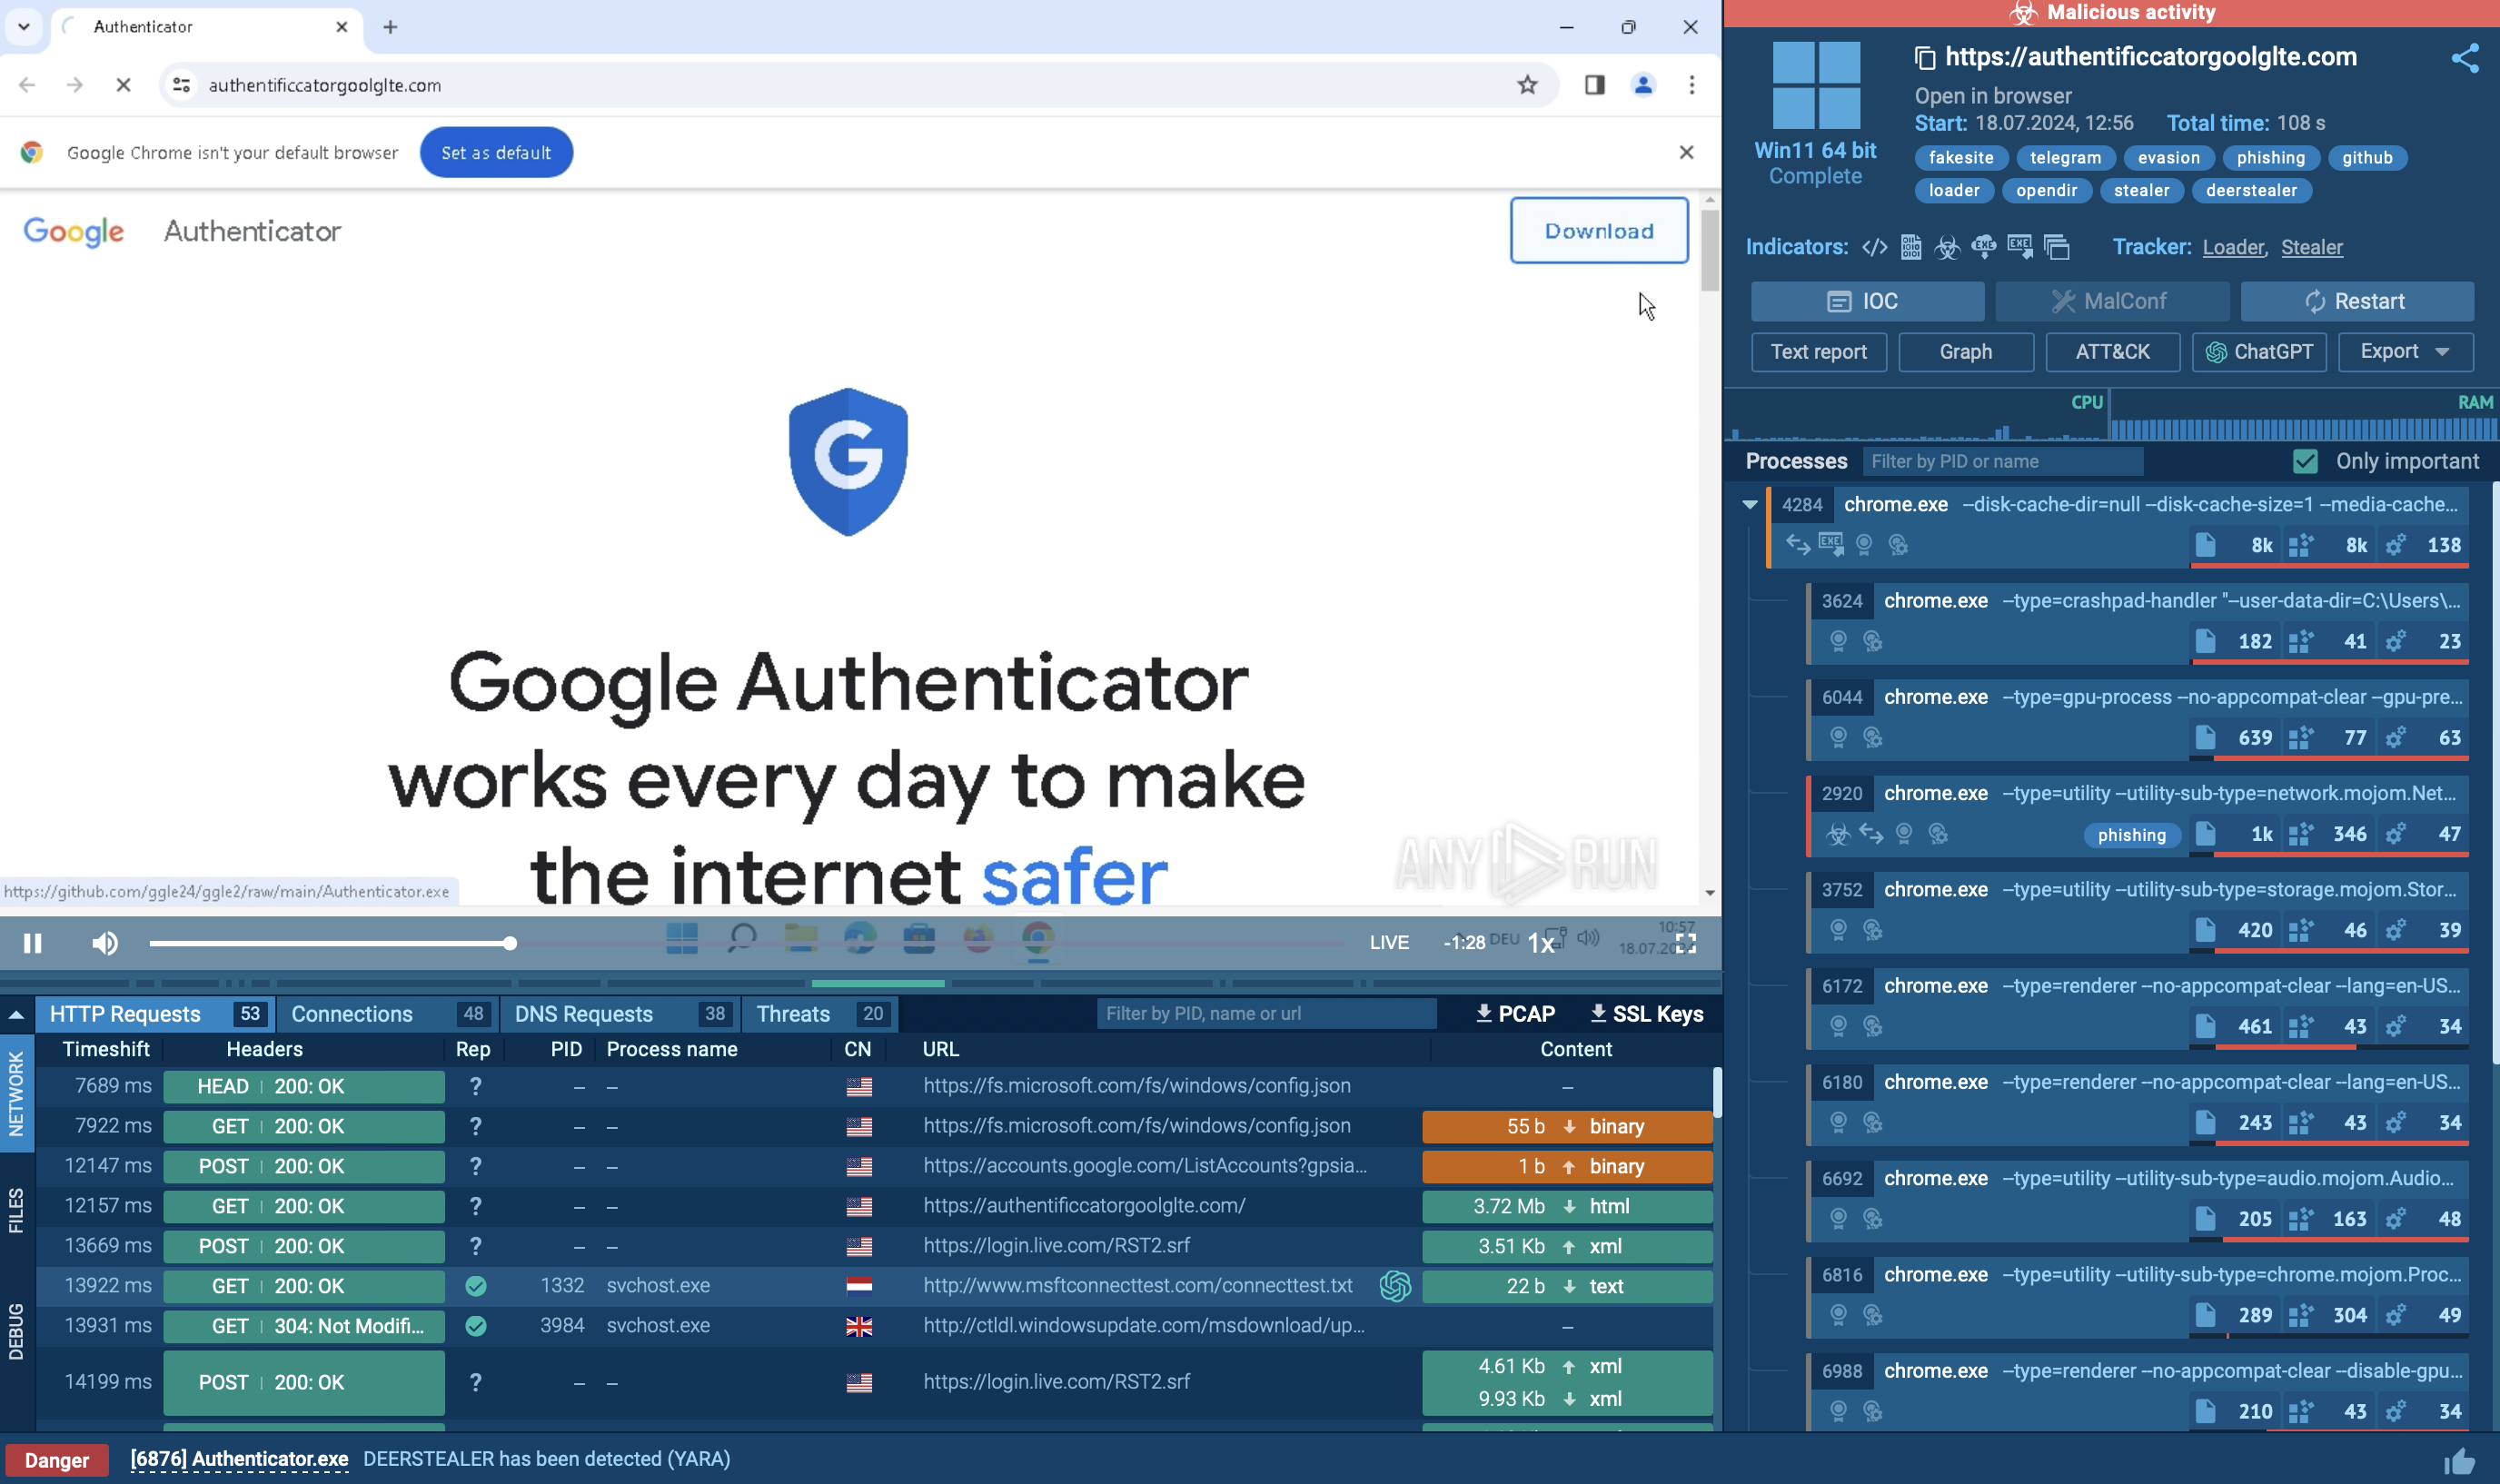
DeerStealer is an information-stealing malware discovered in 2024 by ANY.RUN, primarily targeting sensitive data such as login credentials, browser history, and cryptocurrency wallet details. It is often distributed through phishing campaigns and fake Google ads that mimic legitimate platforms like Google Authenticator. Once installed, it exfiltrates the stolen data to a remote command and control (C2) server. DeerStealer’s ability to disguise itself as legitimate downloads makes it particularly dangerous for unsuspecting users.
Read More
PXA Stealer screenshot
PXA Stealer
pxastealer
PXA Stealer is an information-stealing malware that targets individuals and organizations in 60+ countries. It spreads via phishing, archives, and fake software updates. DLL sideloading, decoy documents, and obfuscation help it evade security tools. Exfiltrated data is exfiltrated and monetized through underground marketplaces.
Read More
CastleLoader screenshot
CastleLoader
castleloader
CastleLoader is a modern malware loader designed to quietly establish initial access and deliver follow-up payloads such as stealers, RATs, and ransomware. It focuses on stealth, flexibility, and rapid payload rotation, making it an effective tool for financially motivated threat actors and a persistent problem for enterprise defenders.
Read More
DarkCloud screenshot
DarkCloud
darkcloud
DarkCloud is an infostealer that focuses on collecting and exfiltrating browser data from the infected device. The malware is also capable of keylogging and crypto address swapping. DarkCloud is typically delivered to victims’ computers via phishing emails.
Read More
Rootkit screenshot
Rootkit
rootkit bootkit
A rootkit is a type of malicious software designed to provide unauthorized administrative-level access to a computer or network while concealing its presence. Rootkits are tools used by cybercriminals to hide their activities, including keyloggers, spyware, and other malware, often enabling long-term system exploitation.
Read More
Salvador Stealer screenshot
Salvador Stealer
salvador
Salvador Stealer is a powerful, information-stealing Android malware designed to silently infiltrate systems, extract sensitive data, and exfiltrate it to cybercriminals. Often sold on underground forums, it is part of the growing ecosystem of “stealers-as-a-service” (SaaS) tools that target individuals and organizations alike.
Read More