Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Sneaky 2FA

1
Global rank
8 infographic chevron month
Month rank
10 infographic chevron week
Week rank

Sneaky 2FA is an Adversary-in-the-Middle (AiTM) phishing kit targeting Microsoft 365 accounts. Distributed as a Phishing-as-a-Service (PhaaS) through a Telegram bot, this malware bypasses two-factor authentication (2FA) to steal credentials and session cookies, posing a significant threat to individuals and organizations.

Phishingkit
Type
Unknown
Origin
1 October, 2024
First seen
8 October, 2026
Last seen

How to analyze Sneaky 2FA with ANY.RUN

Type
Unknown
Origin
1 October, 2024
First seen
8 October, 2026
Last seen

IOCs

IP addresses
162.159.207.0
104.18.95.41
20.59.87.226
150.171.109.100
159.65.145.213
142.250.154.101
48.209.133.15
74.178.76.128
104.18.94.41
74.125.250.129
150.171.22.17
104.18.23.222
192.178.183.132
95.100.158.106
150.171.27.11
23.52.181.212
20.190.160.128
162.159.142.9
150.171.109.105
150.171.109.101
Hashes
f4a93cf3834c5f3bbbab2ba619425fb1415050a847f5bc12cd6b0bab5e68074e
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
6c69ce0fe6fab14f1990a320d704fee362c175c00eb6c9224aa6f41108918ca6
5f4229d18e5606330146ee13bdf726e10c1e06cbb15368c47f1ae68abe9ce4ba
ec78ddd4ccf32b5d76ec701a20167c3fbd146d79a505e4fb0421fc1e5cf4aa63
41ce6a7b18364efecced0419b42165d4f86c43643bbe1043014d4142cf86186a
57f81a5fcbd1fefd6ec3cdd525a85b707b4eead532c1b3092daafd88ee9268ec
89082fb05229826bc222f5d22c158235f025f0e6df67ff135a18bd899e13bb8f
Domains
fonts.googleapis.com
code.jquery.com
crl.microsoft.com
brunhild.challenges.cloudflare.com
www.bing.com
challenges.cloudflare.com
config.edge.skype.com
self.events.data.microsoft.com
edge.microsoft.com
stun1.l.google.com
clients2.googleusercontent.com
www.microsoft.com
api.edgeoffer.microsoft.com
google.com
images.google.dk
update.googleapis.com
arc.msn.com
prinse.pw
edge-consumer-static.azureedge.net
xpaywalletcdn.azureedge.net
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:my2yw6nwlokucfia4eowm9kf6rvheilqcwqwoj3fl4a&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://xpaywalletcdn.azureedge.net/mswallet/expresscheckout/v1/getglobalconfig?edgechannel=stable&edgeversion=133.0.3065.92&configversion=0
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://images.google.dk/favicon.ico
https://images.google.dk/url?q=https%3a%2f%2fprinse.pw%2fbccx&sa=d&source=calendar&ust=1791832800000000&usg=aovvaw3kaazrudgzvesn3ke_c7et
https://login.live.com/ppsecure/deviceaddcredential.srf
https://prinse.pw/bccx
https://prinse.pw/bccx/
https://challenges.cloudflare.com/turnstile/v0/api.js
https://challenges.cloudflare.com/turnstile/v0/g/4df4a60fa397/api.js
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791431337&lafgdate=0
https://challenges.cloudflare.com/cdn-cgi/challenge-platform/h/g/turnstile/f/av0/rch/nvypv/0x4aaaaaafqpa_ch7wqt5bxh/auto/fbe/new/normal?lang=auto
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://prinse.pw/favicon.ico
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is Sneaky 2FA malware?

Sneaky 2FA phishing kit is a malware strain designed to bypass two-factor authentication (2FA), a critical security layer used by individuals and organizations worldwide. By hijacking authentication processes in real-time, this malware undermines what many consider a key safeguard in modern cybersecurity.

It often works as part of a larger attack chain, coordinating with infostealers, remote access trojans (RATs), and phishing kits. Its modular architecture, stealth capabilities, and real-time data interception make it a significant threat in today’s digital landscape.

First detected in October 2024, it is a full-featured phishing kit that compromises Microsoft 365 accounts. Sold via a Telegram-based PhaaS model, it provides cybercriminals with obfuscated source code for independent deployment.

Sneaky 2FA employs advanced anti-bot and anti-analysis measures, such as Cloudflare Turnstile challenges and IP filtering, to evade detection. Its fake Microsoft authentication pages, complete with auto-filled email fields and blurred legitimate interface screenshots, create a convincing illusion of authenticity. Nearly 100 domains hosting Sneaky 2FA phishing pages have been identified.

Sneaky 2FA propagates through multiple distribution channels, leveraging both technical and social engineering techniques:

  • Phishing email campaigns have been observed sending email with pseudo payment receipts to make users open bogus PDF documents containing a QR code that redirects them to a malicious site.
  • Attackers embed QR codes in seemingly legitimate documents, which redirect users to phishing sites when scanned with mobile devices.
  • Campaigns often use urgent or compelling subject lines related to account security, payment notifications, or business-critical communications to encourage immediate action.
  • Attackers may compromise legitimate websites to host phishing pages, lending credibility to malicious content.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

What Sneaky 2FA Can Do to Your Device

Sneaky 2FA's impact extends beyond simple credential theft. Once attackers gain access to Microsoft 365 accounts, they can perform:

  • Session Hijacking: Steal active authentication sessions, allowing immediate access to user accounts without triggering additional security prompts

  • Persistent Access: Maintain long-term access to compromised accounts through stolen authentication tokens

  • Data Exfiltration: Access and download sensitive emails, documents, and organizational data stored in Microsoft 365 services

  • Account Takeover: Gain complete control over user accounts, including the ability to change passwords and security settings

  • Lateral Movement: Use compromised accounts as stepping-stones to access other systems and accounts within the organization

    How Sneaky 2FA Threatens Businesses and Organizations

Sneaky 2FA poses severe risks to businesses, particularly those reliant on Microsoft 365 for operations:

  • Business Email Compromise (BEC) and Financial Losses: Attackers can use compromised executive accounts to initiate fraudulent wire transfers or manipulate business transactions. Sneaky 2FA falls under the class of business email compromise attacks.
  • Data Breaches: Exposure of key corporate data, including customer info, financial records, and strategic plans, leading to business failures, regulatory fines, and reputational damage.
  • Operational Disruption: Compromised accounts can disrupt workflows, especially in critical infrastructure sectors.
  • Supply Chain Attacks: Attackers can use hijacked accounts to target partners or clients, amplifying the impact.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

How Does Sneaky 2FA Function?

Sneaky 2FA doesn't directly compromise individual computers but rather targets cloud-based accounts and services. The attack starts when users receive phishing emails containing links or QR codes that appear to be from Microsoft or other trusted sources.

After clicking malicious links, they are directed to convincing replicas of Microsoft 365 login pages hosted on attacker-controlled infrastructure. Sneaky 2FA as an adversary-in-the-middle intercepts information sent between a device with Microsoft 365 and a phishing server.

Even when users complete legitimate two-factor verification, the system captures and stores authentication tokens that can be replayed to gain account access. With valid session tokens, attackers can access Microsoft 365 accounts without triggering additional security prompts, effectively bypassing multi-factor authentication.

Samples of Sneaky2FA in action can be observed in ANY.RUN's Interactive Sandbox where the whole attack chain is dissected in a safe virtual machine environment.

Watch an analysis session of Sneaky 2FA fresh sample
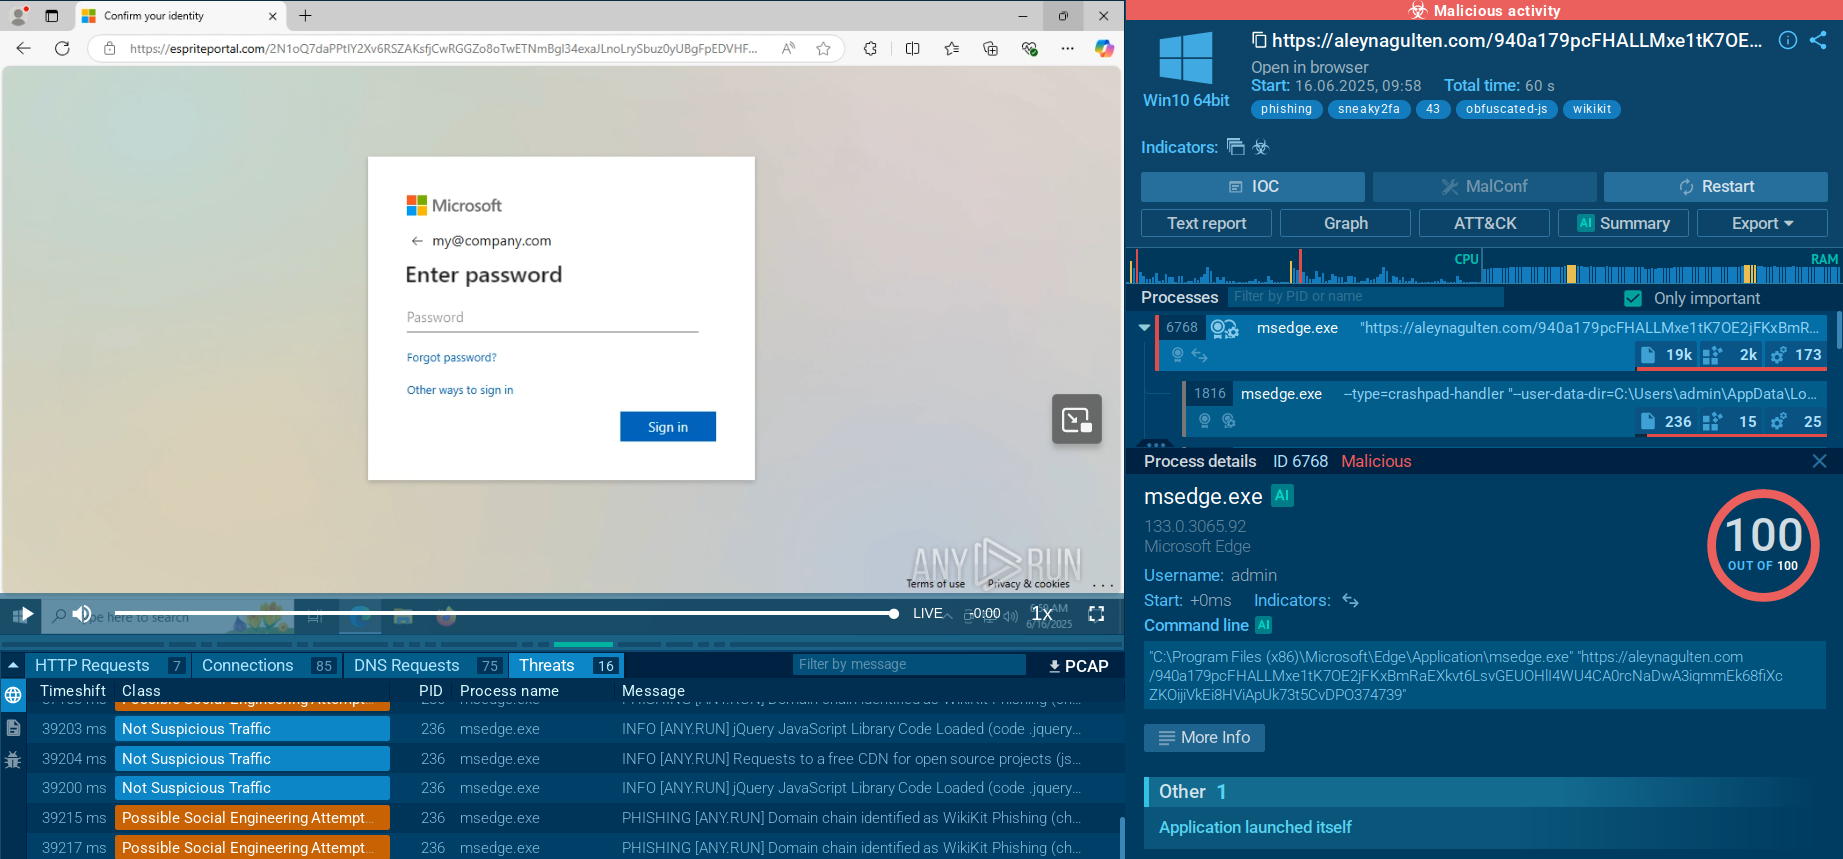
Sneaky 2FA analysis in Interactive Sandbox Sneaky 2FA analysis in ANY.RUN Interactive Sandbox

The attack unfolds through a carefully orchestrated series of steps designed to bypass two-factor authentication on Microsoft 365 accounts.

When a victim receives a phishing email, it typically appears as a legitimate security alert or notification from Microsoft 365, encouraging them to click a link. This link may contain an "autograb" feature that pre-fills the victim’s email address on the fake login page, increasing the illusion of authenticity.

Upon clicking the link, the victim encounters first a fake 'Access document' or other lure and then is redirected to a Cloudflare CAPTCHA designed to verify that they are human and to filter out automated bots, proxies, VPNs, or suspicious IP addresses and automated sandboxes without ML recognition. ANY.RUN has Automated interactivity (ML) which will click CAPTCHA. Visitors flagged as bots or researchers are redirected to harmless pages, such as a Wikipedia article, to avoid raising suspicion.

Once the victim passes the challenge, they are presented with a highly realistic fake Microsoft 365 login page, complete with blurred background images taken from actual Microsoft sites to enhance credibility. The victim enters their password, which is immediately captured by the phishing server. The kit then detects the victim’s configured 2FA method and prompts for the second authentication factor.

Acting as an adversary-in-the-middle, the phishing kit captures the 2FA code in real time as the victim submits it. With this information, the attackers hijack the session cookies, effectively bypassing the need for the 2FA code in subsequent accesses and gaining full control over the victim’s Microsoft 365 account.

If user submits URL or a file through API Throughout this process, the Sneaky 2FA kit employs multiple anti-detection techniques, including obfuscation of HTML and JavaScript code (tag obfuscated-js), embedding junk data and base64-encoded images, and using anti-debugging measures to thwart analysis via browser developer tools. The kit’s traffic filtering mechanisms ensure that only genuine targets are exposed to the phishing pages, minimizing the risk of detection by security researchers or automated defenses.

Gathering Threat Intelligence on Sneaky 2FA Malware

Threat intelligence plays a crucial role in defending against Sneaky 2FA and phishing kits in general by providing actionable data about attack patterns, indicators of compromise, and emerging threats. Indicators of Compromise enable proactive blocking of phishing infrastructure, and understanding Sneaky 2FA’s tactics, techniques, and procedures informs detection rules.

Start from searching Sneaky 2FA by the threat name in ANY.RUN Threat Intelligence Lookup:
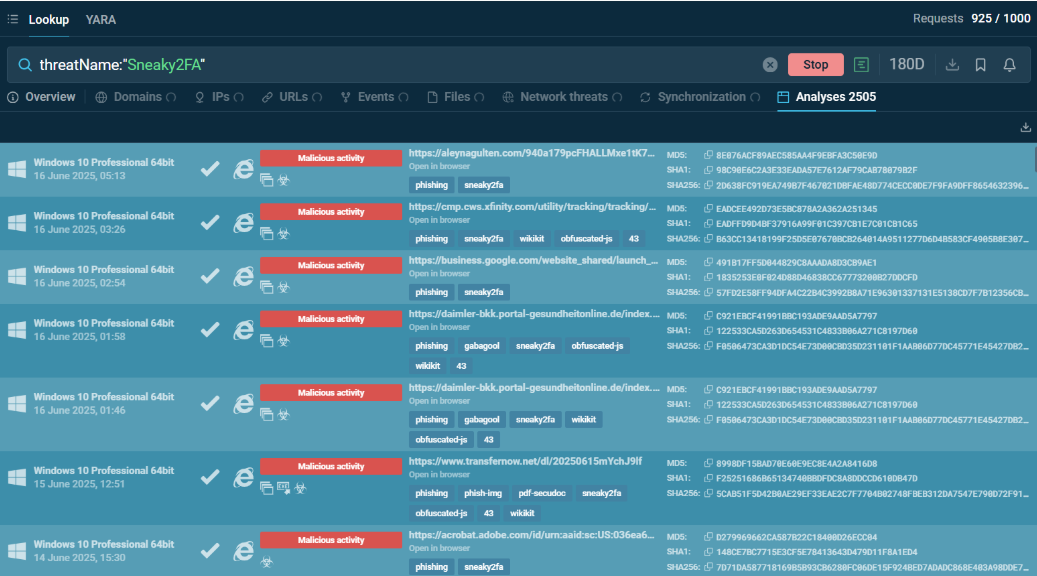
threatName:"Sneaky2FA"

Sneaky 2FA in TI Lookup Sneaky 2FA sandbox analyses found via ANY.RUN TI Lookup

Extract IOCs from analysis sessions and come back to TI Lookup to research them, enrich them with context, and find associated indicators.
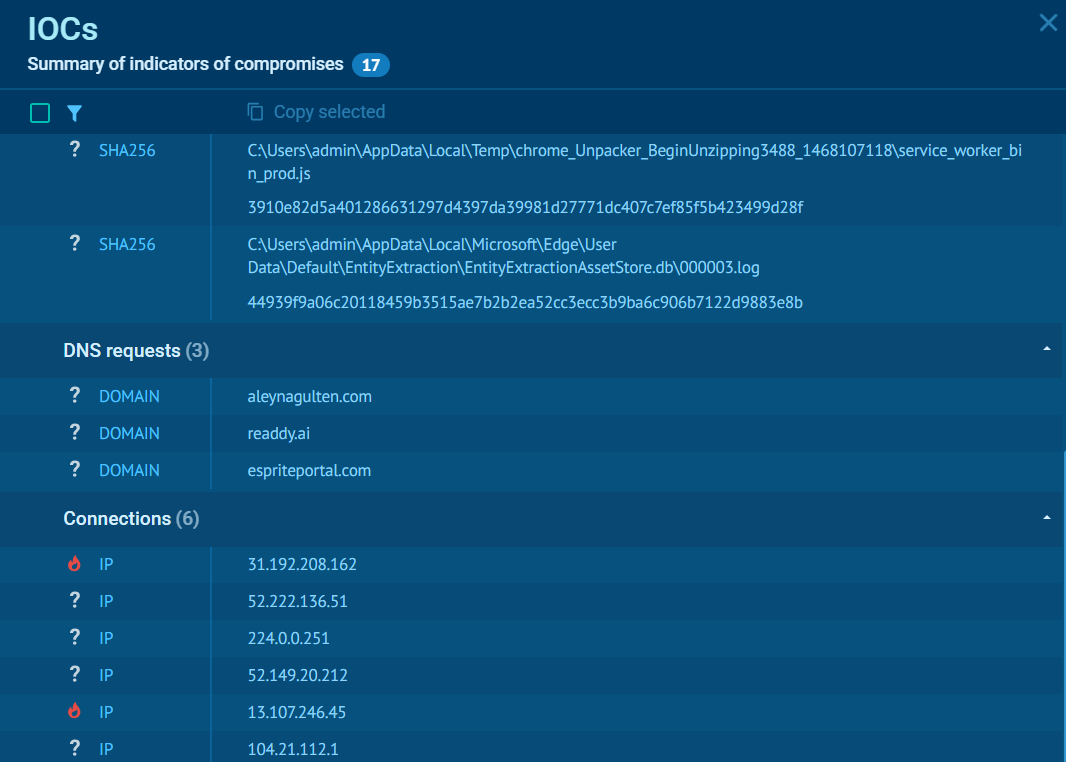
Sneaky 2FA IOCs in the Sandbox Sneaky 2FA IOCs from a sandbox analysis

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Sneaky 2FA illustrates the evolution of phishing attacks, demonstrating how cybercriminals continue to adapt their tactics to bypass increasingly sophisticated security measures. The threat's ability to circumvent two-factor authentication through adversary-in-the-middle techniques highlights the limitations of traditional security approaches and the need for more comprehensive protection strategies. The combination of technical controls, user education, and threat intelligence provides the best defense against this evolving threat landscape.

Gather actionable intelligence via ANY.RUN’s TI Lookup: start with 50 trial requests.
HAVE A LOOK AT

Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More
Sliver screenshot
Sliver
sliver
Sliver is an open-source command-and-control (C2) framework that has been increasingly adopted by threat actors as an alternative to tools like Cobalt Strike. Developed by security firm Bishop Fox, Sliver was initially intended for legitimate security testing and red teaming exercises. However, its robust features and open-source nature have made it attractive to malicious actors seeking to control compromised systems.
Read More
SnappyClient screenshot
SnappyClient is a sophisticated C++-based command-and-control (C2) implant first identified in December 2025. Delivered primarily via the modular HijackLoader, it functions as a versatile remote access tool with strong information-stealing capabilities, particularly focused on cryptocurrency wallets, browser data, and system control. It employs advanced evasion techniques, encrypted communications, and modular configurations to maintain persistence and evade detection.
Read More
Virlock screenshot
Virlock
virlock
Virlock is a unique ransomware strain that combines encryption capabilities with file infection techniques. First observed in 2014, it stands out due to its polymorphic nature and ability to embed its code into compromised files, ensuring continued propagation. Once it infects a system, it encrypts files and locks the screen, demanding a ransom for file recovery and system access.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More