Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Raspberry Robin

123
Global rank
109 infographic chevron month
Month rank
92 infographic chevron week
Week rank

Raspberry Robin is a trojan that primarily spreads through infected USB drives and exploits legitimate Windows commands. This malware is known for its advanced obfuscation techniques, anti-debugging mechanisms, and ability to gain persistence on infected systems. Raspberry Robin often communicates with command-and-control servers over the TOR network and can download additional malicious payloads.

Trojan
Type
Unknown
Origin
1 September, 2021
First seen
6 October, 2026
Last seen

How to analyze Raspberry Robin with ANY.RUN

Type
Unknown
Origin
1 September, 2021
First seen
6 October, 2026
Last seen

IOCs

IP addresses
48.209.138.168
104.18.23.222
23.59.18.102
184.24.77.17
172.211.123.249
23.11.41.157
150.171.22.17
150.171.109.105
150.171.28.11
150.171.109.98
23.207.210.139
48.192.1.65
8.8.8.8
2.16.204.160
204.79.197.203
150.171.27.11
74.178.76.128
150.171.109.99
142.251.14.132
20.190.160.130
Hashes
8232c450f967d7f2f22c54582f0667f4c033ae62e6d450ff8a35c47486249443
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
6c69ce0fe6fab14f1990a320d704fee362c175c00eb6c9224aa6f41108918ca6
5f4229d18e5606330146ee13bdf726e10c1e06cbb15368c47f1ae68abe9ce4ba
ec78ddd4ccf32b5d76ec701a20167c3fbd146d79a505e4fb0421fc1e5cf4aa63
41ce6a7b18364efecced0419b42165d4f86c43643bbe1043014d4142cf86186a
57f81a5fcbd1fefd6ec3cdd525a85b707b4eead532c1b3092daafd88ee9268ec
89082fb05229826bc222f5d22c158235f025f0e6df67ff135a18bd899e13bb8f
e848603b7a73a88e3fe7bffa20e83397f5d1e93e77babb31473cc99e654a27b7
Domains
_8080._https.w0.pm
fe3cr.delivery.mp.microsoft.com
edge.microsoft.com
w0.pm
google.com
www.bing.com
slscr.update.microsoft.com
go.microsoft.com
th.bing.com
static.edge.microsoftapp.net
login.live.com
config.edge.skype.com
edge-consumer-static.azureedge.net
edge-mobile-static.azureedge.net
oneocsp.microsoft.com
ocsp.digicert.com
www.microsoft.com
copilot.microsoft.com
edge-cloud-resource-static.azureedge.net
activation-v2.sls.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:nndhaf4-q9cqvx7uq91ipg2qnji2cprurpsddyhh5mc&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://edge.microsoft.com/linkdoctor/api/v1/getcorrections
https://copilot.microsoft.com/c/api/user/eligibility
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://edge.microsoft.com/autofillservice/core/page/5701739080754199609/4016115957318418533?cidalgoversion=2
https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d292%2526e%253d1
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791324354&lafgdate=0
https://update.googleapis.com/service/update2/json?cup2key=14:2woryyxojmounszjoieldjqzymrmfqai7b1gs5eua54&cup2hreq=868022b8db6ac41a7e3cdd758f5e01dad91b17743c84064111f282e6dfbcd0b5
https://www.bing.com/api/shopping/v1/user/shoppingsettings?enabledservicefeaturesv2=edgeserverux.shopping.cashbackeumarkets,edgeserverux.shopping.msedgeshoppingcashbackdismisstimeout2s
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=domains_config_gz&version=3.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
https://edge.microsoft.com/abusiveadblocking/api/v1/blocklist
https://clients2.googleusercontent.com/crx/blobs/azpvhcqildrgqxyclcenwovmaua7lwu2mln7dephdl7eqkp9gczqmiehkjncu7a_eigr4ip8elijgyg1mgbqewwsojngu_j8zva9cfi_aj--ikwjbypwnpfv9nmzws17bigaxlka5c7tdptpcgaddf44n1nzr3cqv7qk/ghbmnnjooekpmoecnnnilnnbdlolhkhi_1_110_1_0.crx
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 230
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2820
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4352
comments 0

What is Raspberry Robin malware?

Raspberry Robin is a worm malware that has been tracked since 2021. The malware has been used to target organizations across various industries and sectors, with finance, manufacturing, and government being particularly affected.

Initially, infections with Raspberry Robin appeared to lack a specific end goal. However, it soon began to distribute other malware, including the LockBit ransomware and SocGholish (FakeUpdates).

A notable characteristic of this threat is its utilization of compromised network-attached storage (NAS) devices from QNAP, as part of its infrastructure. Another distinctive feature of the malware is its exploitation of legitimate Windows commands, such as msiexec.exe and odbcconf.exe, to retrieve, deploy, and execute malicious DLLs.

Researchers have noted a connection between Raspberry Robin and the Dridex malware, a recognized banking trojan. It is likely that these two malicious programs have been operated by the same threat actor group.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Raspberry Robin execution process

To take a closer look at Raspberry Robin’s functionality, we can submit its sample for analysis to the ANY.RUN sandbox.
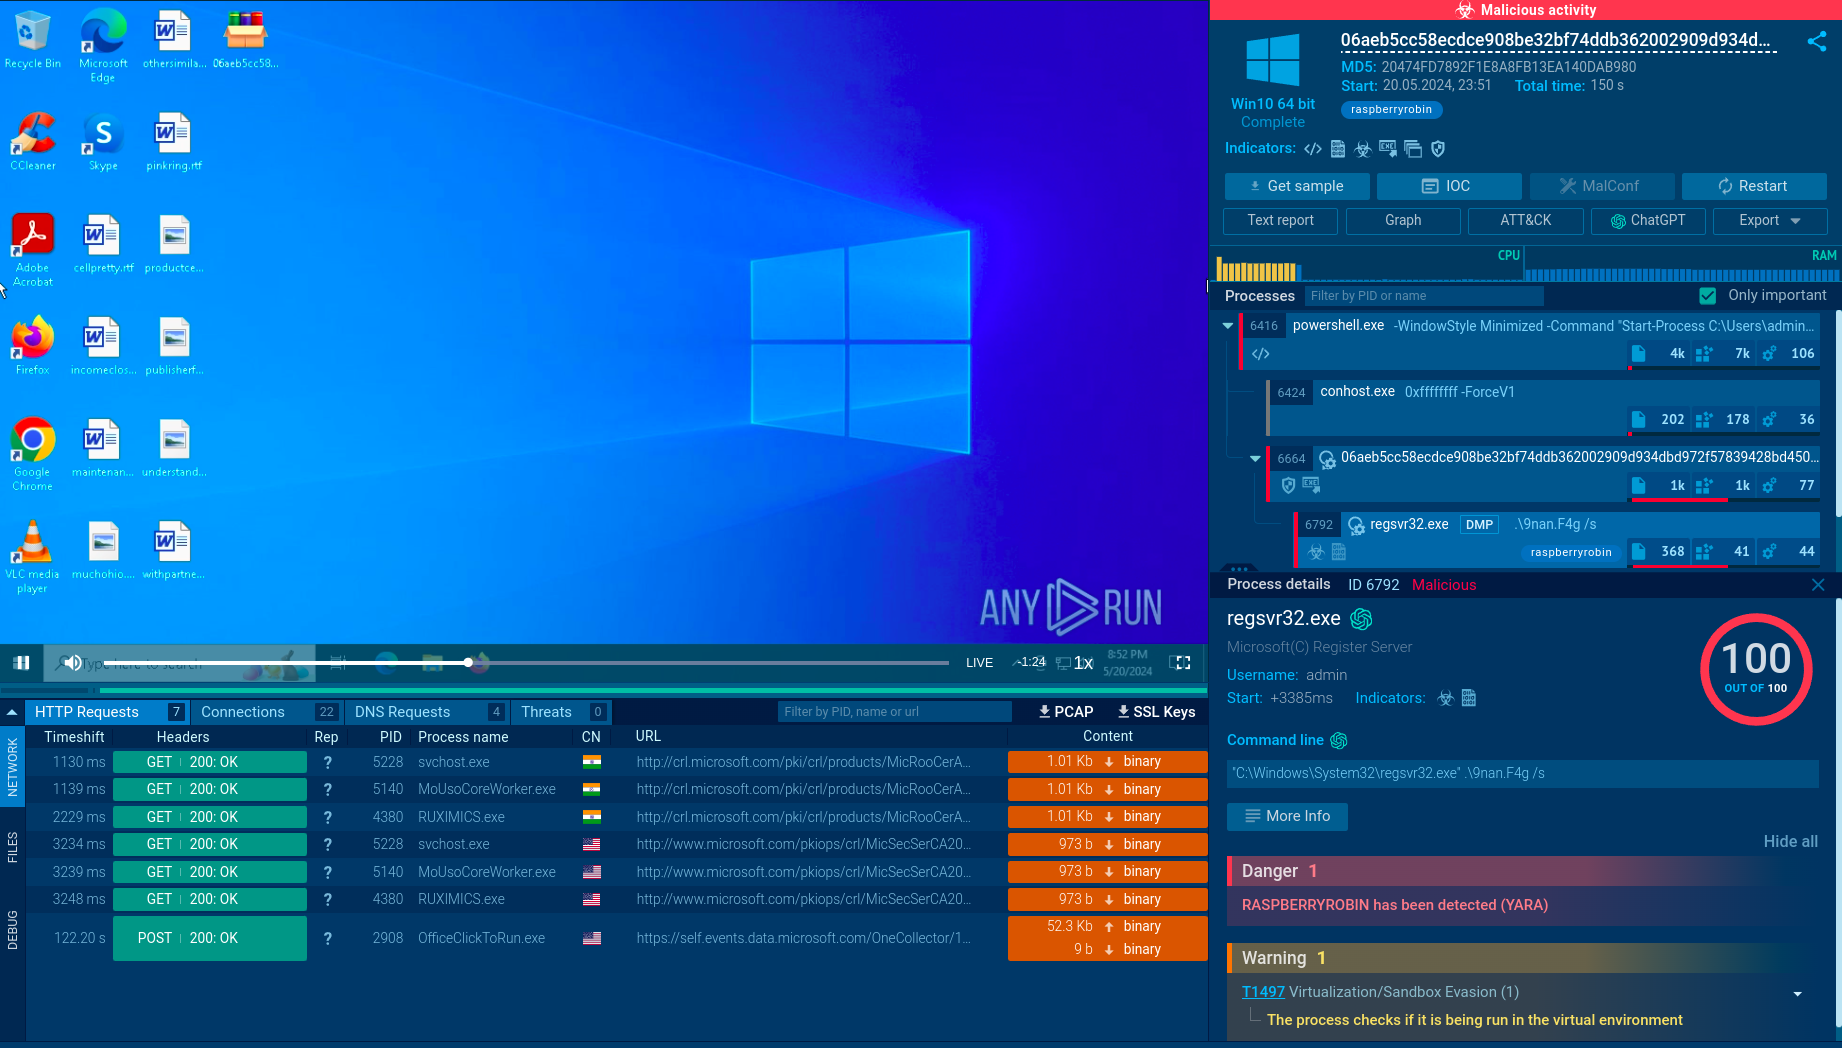
Raspberry Robin analysis in ANY.RUN Analysis of Raspberry Robin in ANY.RUN

Raspberry Robin is typically delivered through infected external disks or USB drives containing a Windows Shortcut file (.lnk). Upon connecting the infected USB device and launching the .lnk file, a command processor (cmd.exe) is initiated and executes a Microsoft Installer Executable (MSIExec).

This action ultimately downloads a payload from a compromised QNAP network-attached storage (NAS) device or a web server.
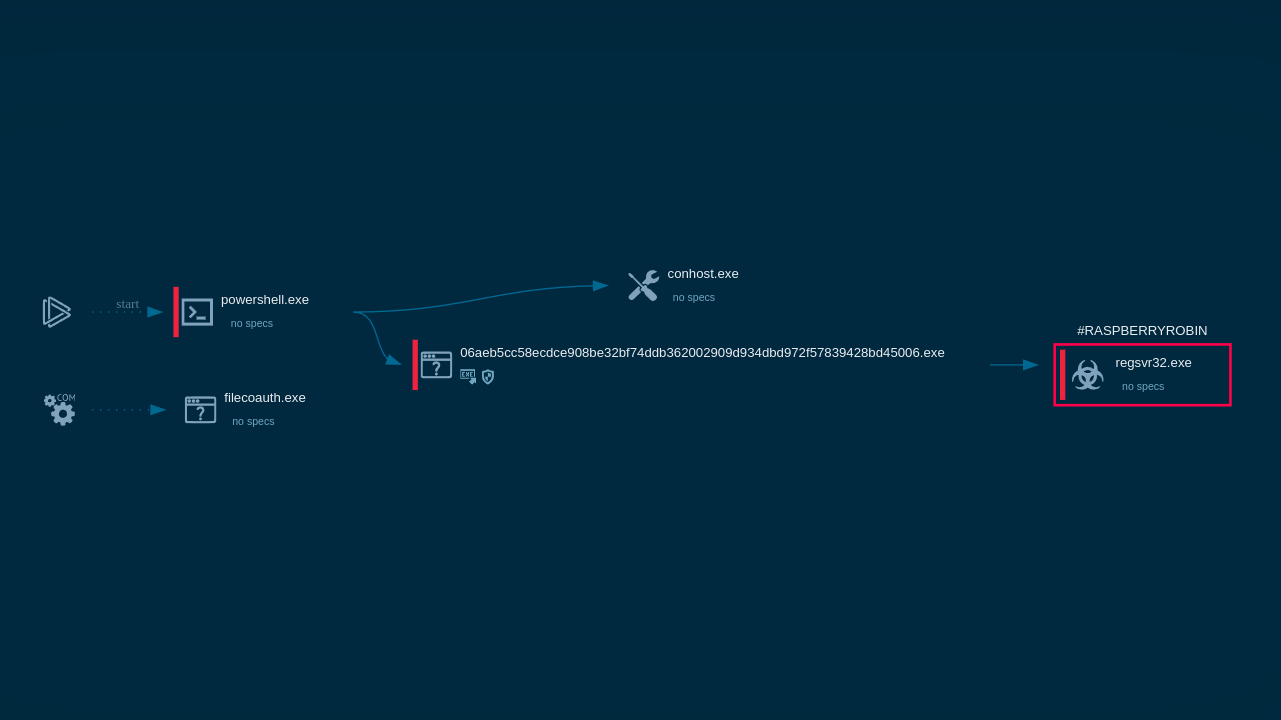
Raspberry Robin process graph in ANY.RUN Raspberry Robin process graph demonstrated by ANY.RUN sandbox

The payload is stored in the local AppData folder and executed using msiexec.exe, which activates the Raspberry Robin malware.

The malware communicates with command-and-control (C2) servers over the TOR network and is capable of downloading and executing additional payloads, including other malware families such as Cobalt Strike, IcedID, BumbleBee, and Truebot.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Raspberry Robin malware technical details

The malware often injects dozens of legitimate processes on the infected device, including dllhost.exe and rundll32.exe, which are then utilized to maintain command-and-control (C2) communication.

Some samples of the malware have been subjected to advanced obfuscation, packing, anti-debugging, and evasion mechanisms. One unique method involves downloading a fake payload after the threat detects a virtual environment. Other anti-VM techniques include identifying the system's Mac address and processor information. Learn more about how you can counter anti-VM techniques in a sandbox.

The malware can also detect common antivirus software, such as Avast and BitDefender, by checking if the system has active processes related to these programs.

Raspberry Robin establishes persistence on the system by adding registry keys and employing other techniques to ensure it runs automatically at startup. The malware can gain elevated privileges on the machine through a User Account Control bypass.

Once it gains persistence on the system, the malware may initiate connections to TOR nodes to communicate with its command-and-control (C2) server via TCP ports, such as 8080.

Raspberry Robin malware distribution methods

Since Raspberry Robin is a worm type of malware, it has the ability to self-replicate and spread without requiring human interaction. This malware has been spreading primarily through infected USB drives, which has allowed it to achieve a significant scale of distribution across numerous machines. As users unknowingly connect infected USB drives to their devices and execute the malicious files, the malware propagates to new systems, expanding its reach and potential impact.

In addition to infected USB drives, another vector of attack for Raspberry Robin may involve an archive distributed through Discord. It usually contains Oleview.exe, a legitimate Windows application, alongside a malicious .dll file. When a user extracts and launches Oleview.exe from the archive, it side-loads the malicious .dll file, leading to the infection.

Conclusion

Raspberry Robin is still an active threat, which means that thousands of systems worldwide are at risk of being targeted by it. To effectively counter Raspberry Robin, implement strong security policies, maintain updated software, and provide ongoing security awareness training. Using a quick and effective sandbox should be one of the core elements of this strategy.

ANY.RUN's cloud sandbox provides many benefits for examining malware, such as:
  • Quickly finding threats in files and URLs (in less than 40 seconds)
  • Directly interacting with samples and the system for a realistic analysis
  • Customizing Windows and Linux virtual machines to fit your needs
  • Generating detailed reports that explain the identified threats and their impact
  • Showing all harmful activities related to the network, registry, files, and processes

Create your FREE ANY.RUN account today!

HAVE A LOOK AT

Ransomware screenshot
Ransomware
ransomware
Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying.
Read More
Bluesky Ransomware screenshot
BlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
Read More
Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More