Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Mallox

160
Global rank
155 infographic chevron month
Month rank
116 infographic chevron week
Week rank

Mallox is a ransomware strain that emerged in 2021, known for its ability to encrypt files and target database servers using vulnerabilities like RDP. Often distributed through phishing campaigns and exploiting exposed SQL servers, it locks victims' data and demands a ransom. Mallox operates as a Ransomware-as-a-Service (RaaS), making it accessible to affiliates who use it to conduct attacks.

Ransomware
Type
Unknown
Origin
1 May, 2021
First seen
4 October, 2026
Last seen

How to analyze Mallox with ANY.RUN

Type
Unknown
Origin
1 May, 2021
First seen
4 October, 2026
Last seen

IOCs

IP addresses
20.165.94.63
48.209.6.48
40.126.32.134
95.100.158.121
23.52.181.141
104.26.13.205
48.192.1.65
20.190.160.4
172.211.123.249
74.178.76.54
2.19.198.16
48.209.138.189
23.11.41.157
2.23.246.101
23.48.23.35
23.52.181.212
48.209.138.168
95.100.102.9
104.18.33.89
135.232.92.97
Hashes
5f7aeadb4fc434549463129f1d55fb8f69ba7340fbfd7634f56ac83a0f31c06c
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
044f70eb07e40c07aa9b548518b79b2c243583dcf152781a53c814815a701a2a
25484c4fad7dca98fe50ddf4509d7ce3e9ac5077a702306d9401cc2197fbe57e
6a6c12c010bdd23c12790ac40fa004c4d6df5a16cef316f224ceaebfcc0304b3
d71c98b36f47353074809d19617eacc3ed18427a4e9b7a6d85afbb4864a6a986
79aedd8f1e484d3eebf97ba740bedfe01fa0fb6eb686fb167d5506be856c7a95
0cd17b94ec70a33604a62f2e162d2ab425e0fa1d94e319a458acdb677b78b041
6e729b11539e9c76624be45c515a7eec4bc9f8bea3dc387e1df305e56bd4f3d7
3704e639e1985596076183a296c4c0f96650506c6b697586282bae1d334b355b
20679130123a678ecaf7f8a360fa6558a2c2e3faf6cee60336e3f6659cc1e40a
70d8275a4e3f8b3d99d3b3397d108087e96ac8902cc5eb6a75c05a0ea8ccd87d
366a68a5a3b7c90a89624f6f4dc5f70ed4e1d12fa3146fbbadb5b5b9a06fafa9
f2690a93be81694f3b49de64238c28011e21d8a6fa8026a7a22968691c53407a
3d8284261961b512edec5afe90fb7791cbc7f79ff03e4f5fd1780d6e20063fd9
2a2f08db38799d89670720bff9093ff26b7faba5a9c42a49fb7d47fcf08e8929
e446d414e21bbe356b413b6f2e24f2a0c7879dd09305c9853dd7494d5cd2c07f
3e502c2316d863965a7ae758c0ee10b9c8f97650fff5b8ee4ecd3e43dd3fbdbf
c5b3c0a700f7f253854d9401aa6fb11e131cfde3e3ba8ce1acfb0f07ce0fef4e
de4c49144405d84e5271b4100d5121f0e13cefc4d68e5cc93dd674f254698bd9
Domains
go.microsoft.com
slscr.update.microsoft.com
www.microsoft.com
ocsp.digicert.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
google.com
client.wns.windows.com
crl.microsoft.com
self.events.data.microsoft.com
login.live.com
api.ipify.org
activation-v2.sls.microsoft.com
ecs.office.com
nexusrules.officeapps.live.com
th.bing.com
oneocsp.microsoft.com
ocsp.digicert.cn
www.bing.com
messaging.engagement.office.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://api.ipify.org/
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Mallox ransomware?

Mallox is a ransomware strain that emerged in 2021 and has since become a known threat, particularly targeting organizations with vulnerable SQL servers and RDP configurations.

Its method of operation involves encrypting victims' files and appending unique extensions like ".mallox" to the encrypted data, effectively making the files inaccessible. Victims are then presented with a ransom note demanding payment, usually in cryptocurrency, in exchange for the decryption key.

When analyzing the Mallox ransomware inside the ANY.RUN’s sandbox, we can see the whole process of its attack chain, including the displayed ransom note:
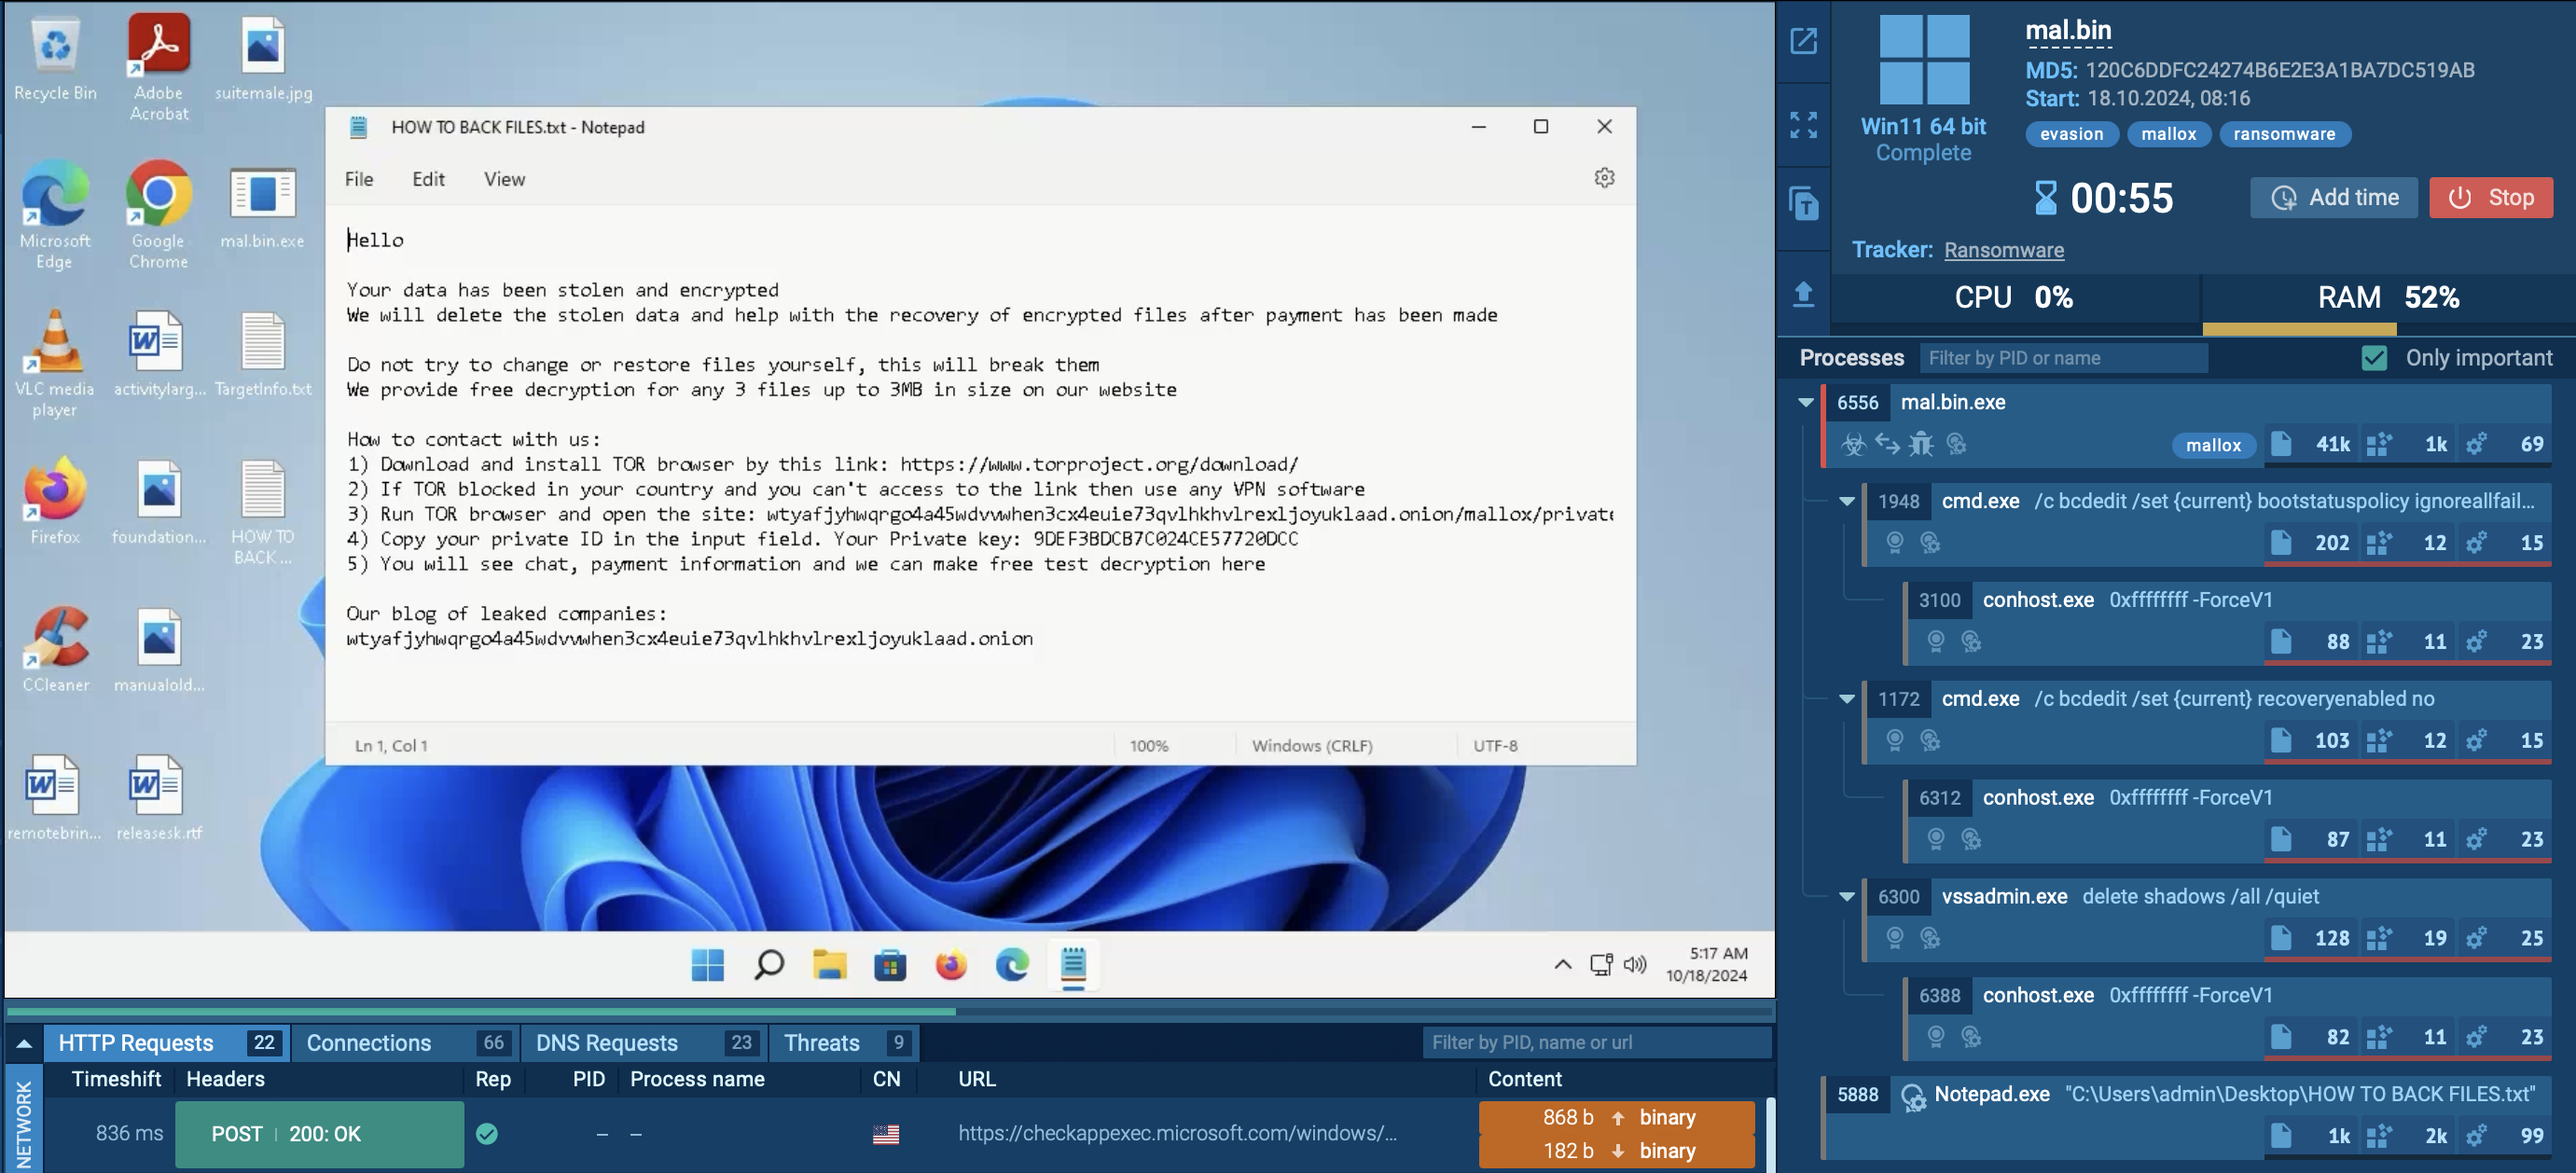
Ransom note of Mallox in ANY.RUN sandbox Analysis of Mallox inside ANY.RUN’s Interactive Sandbox showing a ransom note

Mallox operates through a Ransomware-as-a-Service (RaaS) model, making it accessible to various threat actors who can customize and distribute the ransomware. It employs advanced techniques like modifying boot configurations, disabling Windows recovery options, and using PowerShell scripts for downloading and executing payloads.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Mallox ransomware technical details

The primary functionalities of Mallox ransomware include:

  • Encrypts files using strong encryption algorithms, making them inaccessible.
  • Steals sensitive data before encryption to increase pressure for ransom payment.
  • Targets unsecured MS-SQL servers using brute-force dictionary attacks
  • Downloads ransomware using command-line tools and PowerShell. It injects into processes like Aspnet_Compiler.exe to avoid detection
  • Modifies BCD settings with bcdedit commands to disable system recovery
  • Steals data before encryption to pressure victims during negotiations
  • Encrypts files, adding a “.mallox” extension
  • Drops a ransom note in affected directories, demanding payment.
  • Changes registry settings to prevent shutdown and restarts, ensuring uninterrupted encryption
  • Guides victims to reach out through TOR or email using a unique ID

This ransomware collects detailed system data, such as total disk space, operating system version, computer name, locale settings, and the architecture of the processor. It then sends this information to its command-and-control (C2) server to aid in managing the infection.

Additionally, it uses an external API, like api.ipify.org, to determine and retrieve the device's public IP address, allowing the attackers to gain further insight into the network environment.

This action can be observed in ANY.RUN’s sandbox when detected by Suricata rules.
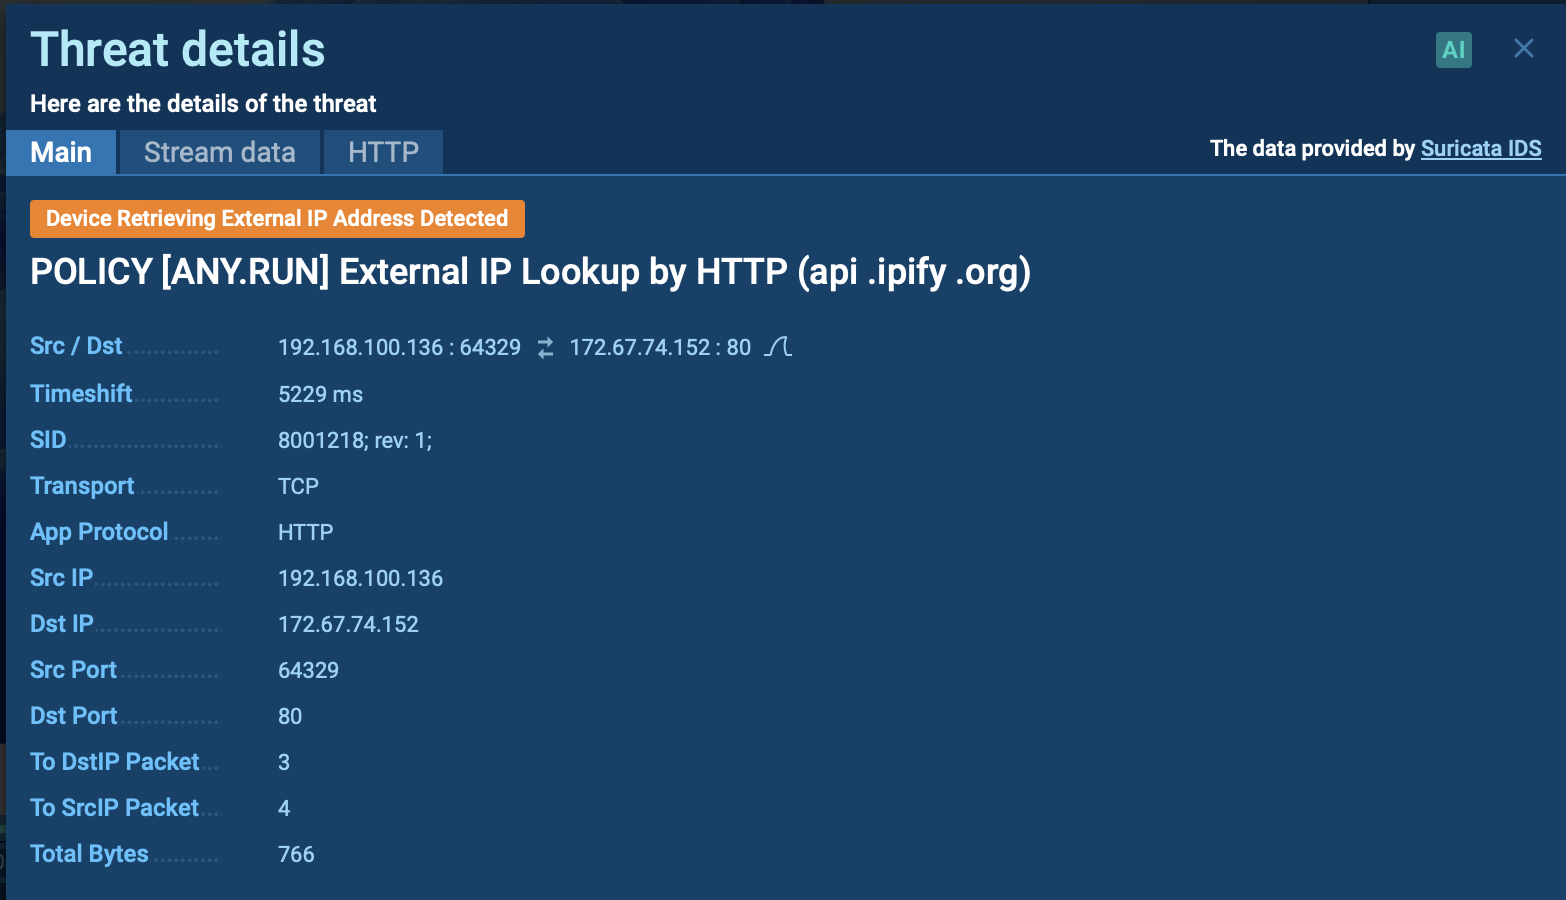
Suricata rule for Mallox in ANY.RUN sandbox External IP address retrieval detected inside ANY.RUN’s sandbox

Mallox ransomware execution process

To see how Mallox ransomware operates, let’s upload its sample to the ANY.RUN sandbox.

Mallox ransomware employs a sophisticated attack chain, sometimes beginning with initial access through brute-force attacks on unsecured Microsoft SQL servers.

Once inside, the ransomware executes various commands and scripts to facilitate its malicious activities, culminating in file encryption and ransom demands.
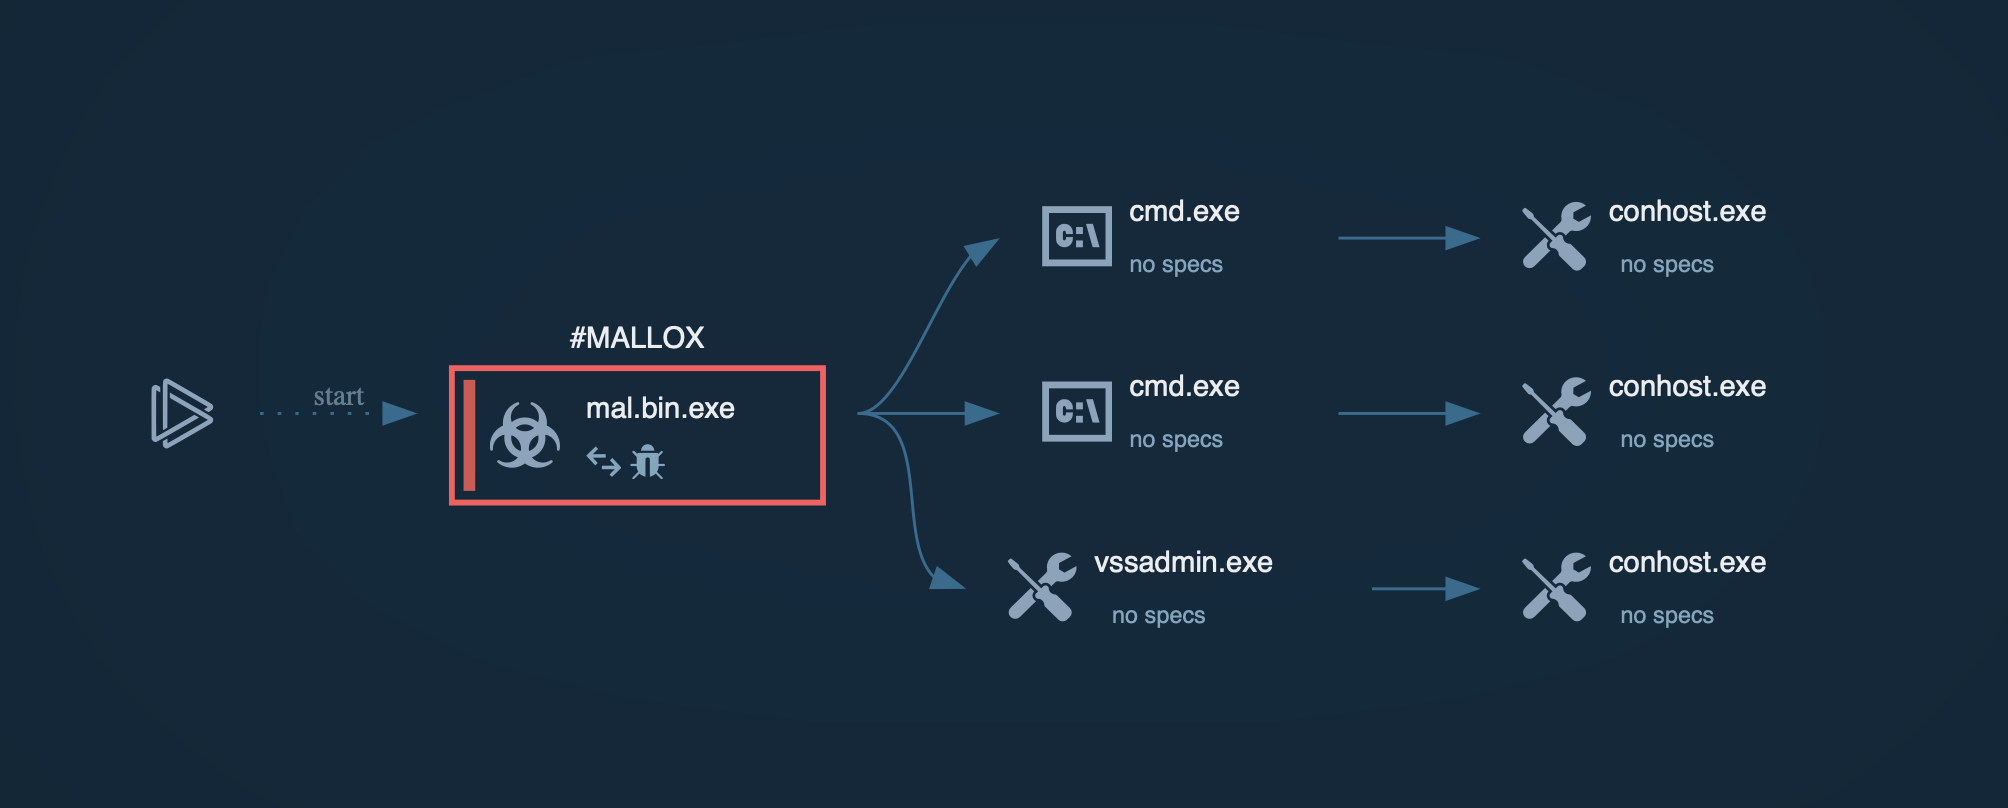
Process graph of Mallox in ANY.RUN sandbox Process graph of Mallox ransomware displayed inside ANY.RUN’s sandbox

Mallox primarily targets unsecured Microsoft SQL servers by using dictionary brute-force attacks to gain access to the victim's network. After compromising the SQL server, the attackers utilize command-line tools and PowerShell scripts to download the ransomware payload from a remote server.

The downloaded payload may inject itself into legitimate processes (e.g., Aspnet_Compiler.exe) using techniques like process hollowing, allowing it to evade detection by traditional antivirus software.

Upon execution, Mallox modifies Boot Configuration Data (BCD) settings to disable recovery options, making it harder for users to restore their systems post-infection.

The ransomware encrypts files on the infected system, appending a ".mallox" extension to the encrypted files. It also generates ransom notes named “HOW TO BACK FILES.TXT” in each folder containing encrypted files.

Before encryption, Mallox may exfiltrate sensitive data from the system, which is later used against victims who refuse to pay the ransom.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Victims are instructed to contact the attackers via TOR or email, with unique identifiers (private ID in our sample) provided for negotiation purposes. The ransom notes often threaten to expose the stolen data if demands are not met.

Besides this, the ransomware modifies Windows registry settings to disable shutdown, restart, and sign-out options, effectively locking users out of their systems to prevent interruption of the encryption process.

If users attempt to shut down or reboot their systems, Mallox displays warnings about potential data loss, further pressuring victims to comply with ransom demands.

Mallox ransomware distribution methods

Mallox ransomware is typically distributed through a few primary methods, making it a significant threat to targeted systems:

  • Brute-force attacks on Microsoft SQL servers: One of the most common methods is targeting exposed MS-SQL servers using brute-force attacks. Attackers exploit weak credentials to gain access to these servers, often through dictionary-based password cracking methods
  • PowerShell scripts and Command-Line tools: Once access is established, attackers use PowerShell scripts to download and execute the ransomware payload. This often involves using a remote server to deliver the malicious code directly onto the compromised system
  • Malicious email campaigns: Phishing emails are another avenue for distribution. These emails may contain infected attachments or links that, when opened, initiate the download of the ransomware onto the victim's computer
  • Exploiting vulnerabilities: Mallox has also been observed leveraging known vulnerabilities in SQL servers, such as remote code execution (RCE) flaws, to gain unauthorized access and deploy its payload

Gathering Threat Intelligence on Mallox Ransomware

To collect the latest intelligence on Mallox ransomware, you can utilize Threat Intelligence Lookup.

This service offers access to an extensive database with insights from numerous malware analysis sessions conducted within the ANY.RUN sandbox. It includes over 40 search parameters, enabling you to explore specific details like IP addresses, domains, file names, and various process artifacts.
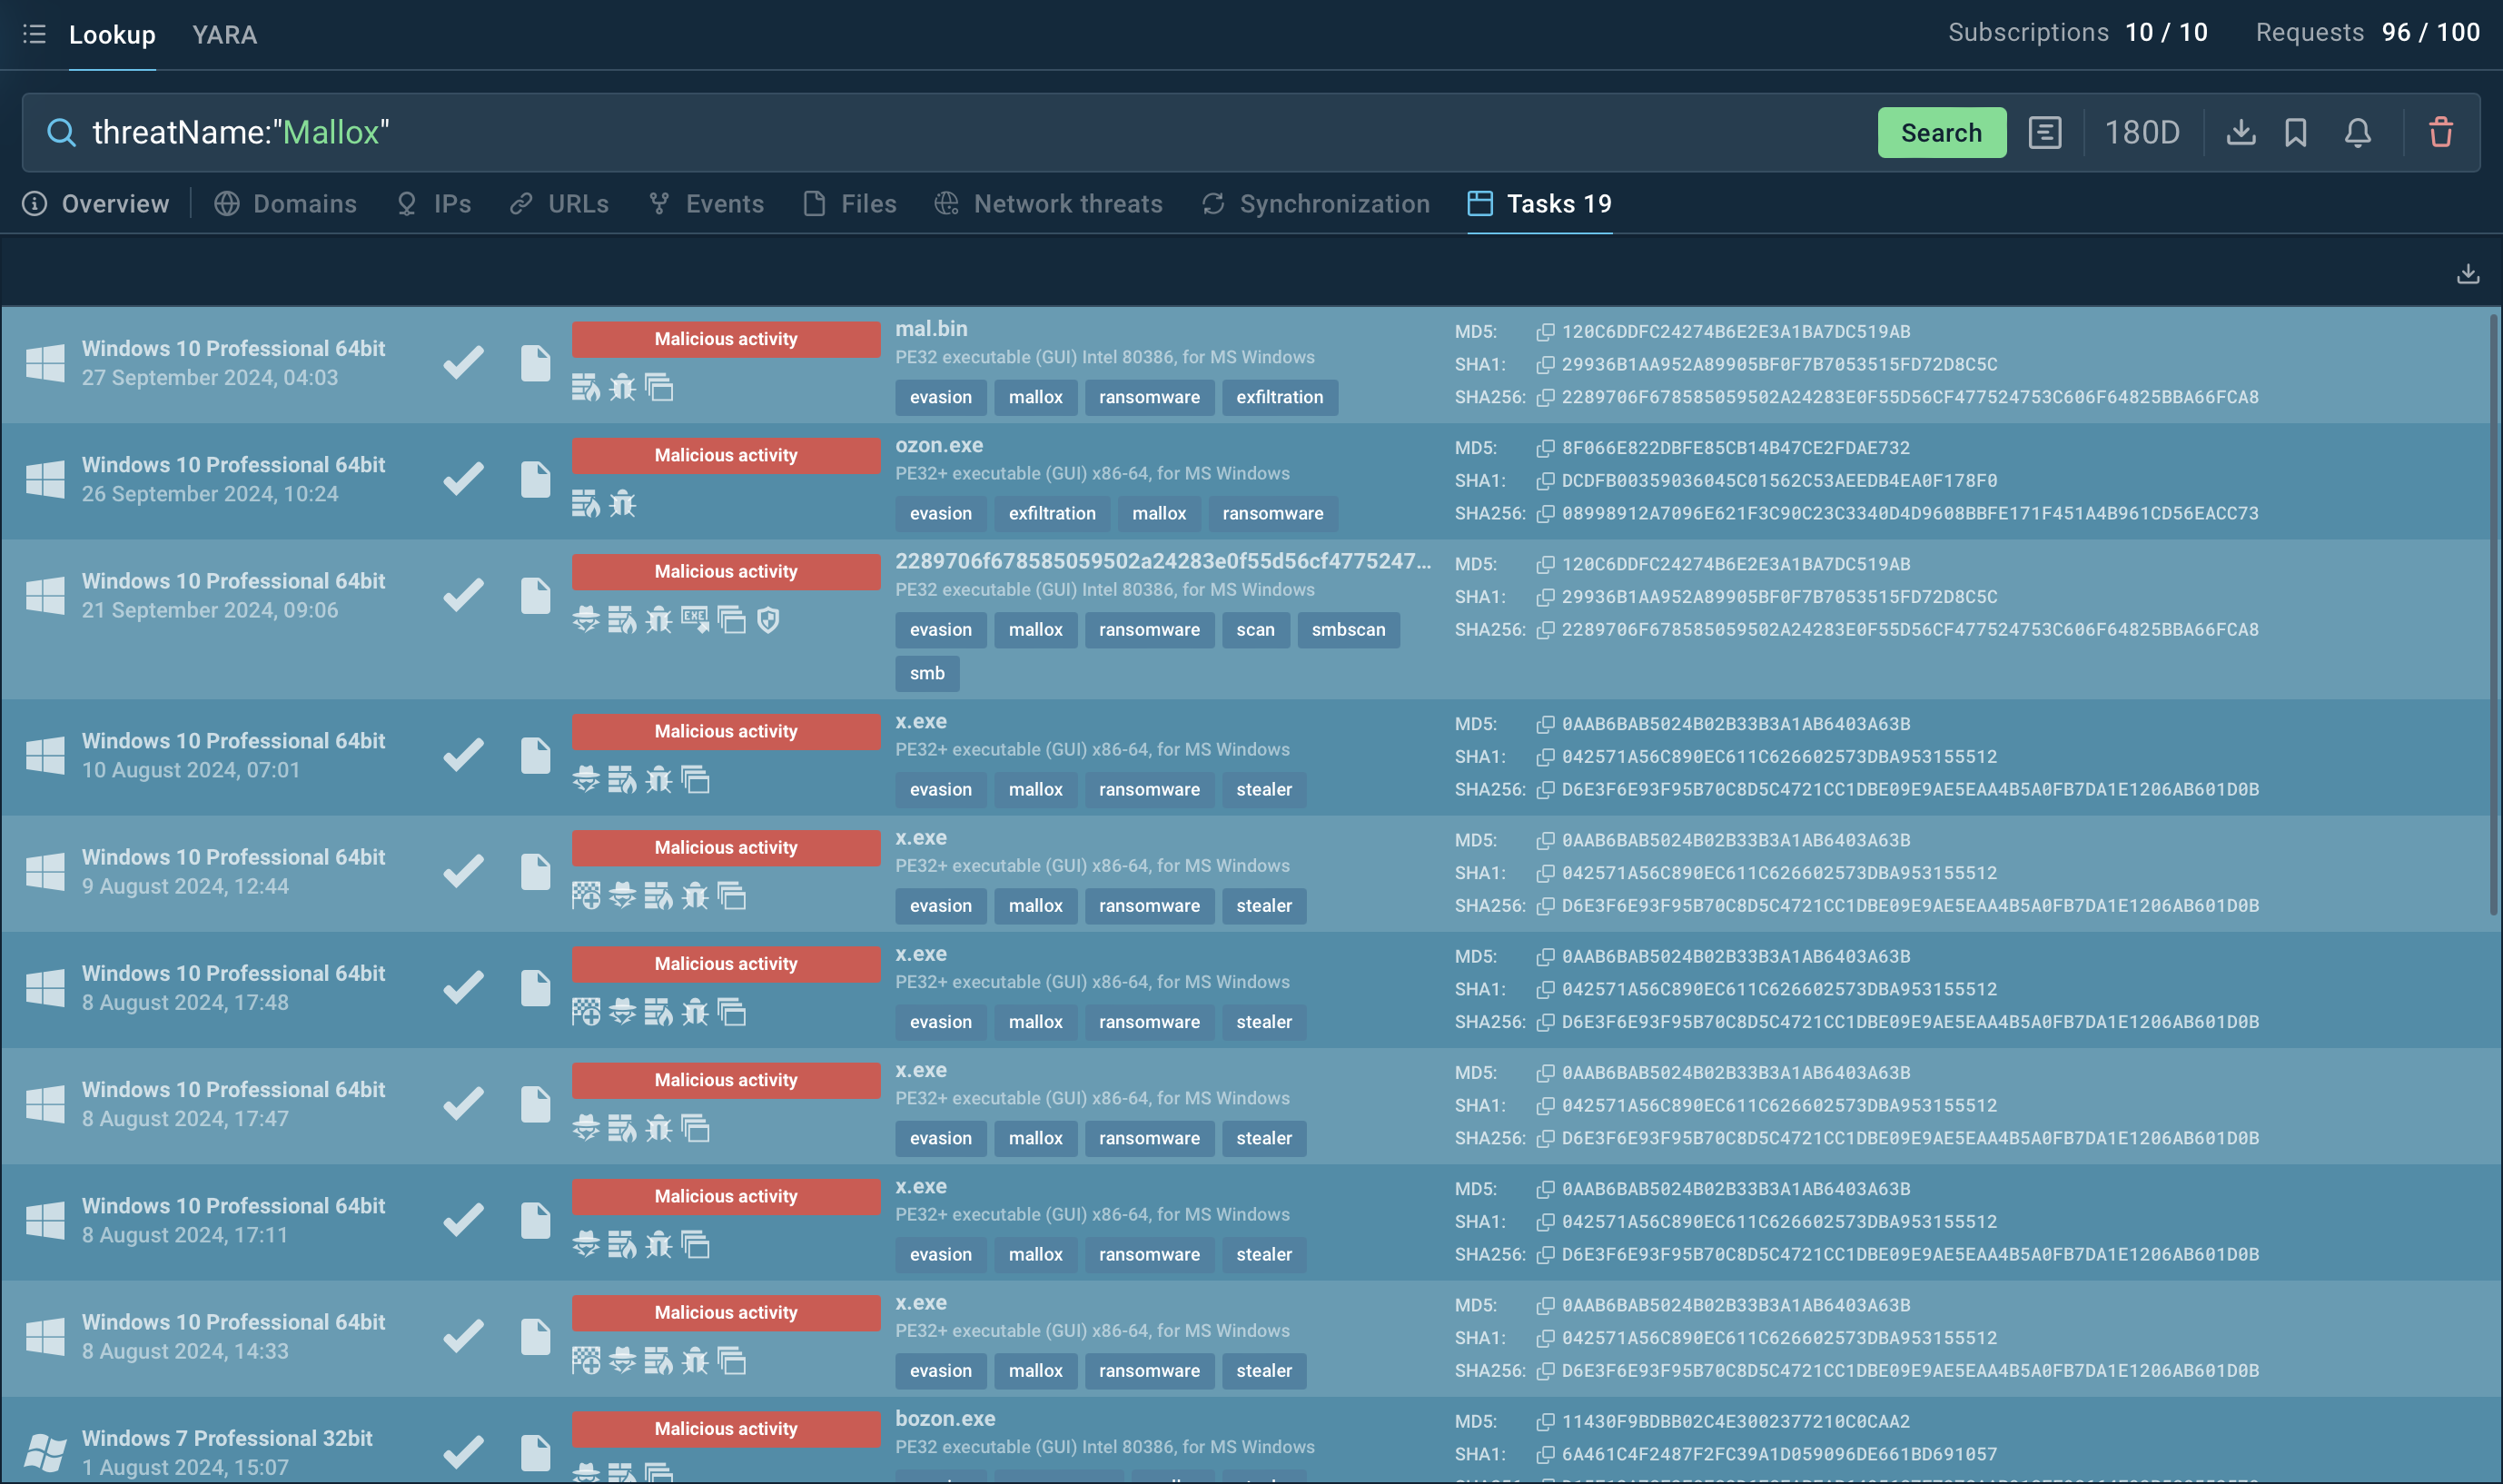
Lookup results for Mallox in ANY.RUN sandbox Search results for Mallox in Threat Intelligence Lookup

Using Threat Intelligence Lookup, you can search directly for a threat name or use a related artifact. For instance, by entering a query like threatName:"mallox" AND domainName:"", you can quickly access Mallox threat data along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Get a 14-day free trial of Threat Intelligence Lookup along with the ANY.RUN sandbox.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Mallox ransomware poses a significant threat due to its ability to encrypt critical files, exfiltrate sensitive data, and disable recovery mechanisms. To mitigate such threats, integrating tools like ANY.RUN is crucial for proactively analyzing suspicious files and URLs before they cause harm.

ANY.RUN offers a real-time threat analysis with detailed process graphs, in-depth network traffic analysis, and a user-friendly interface that allows analysts to simulate real-world threat scenarios effectively.

Sign up for a free ANY.RUN account today and enhance your malware analysis capabilities.
HAVE A LOOK AT

DEVMAN screenshot
DEVMAN
devman
DEVMAN is a fast-evolving malware family targeting Windows environments with a mix of credential theft, remote control capabilities, and persistence techniques typical of modern crimeware. Initially observed in early 2025, DEVMAN quickly became a favorite tool among cybercriminal groups thanks to its stealth, modular structure, and ability to bypass traditional AV solutions.
Read More
Razr screenshot
Razr
razr
Razr is a destructive ransomware that infiltrates systems to encrypt files, rendering them inaccessible to users. It appends the ".razr" extension to the encrypted files and drops a ransom note, typically named "README.txt," instructing victims on how to pay the ransom to obtain the decryption key. The malware often spreads through phishing emails with malicious attachments or by exploiting vulnerabilities in software and operating systems. Razr employs strong encryption algorithms, making it challenging to decrypt files without the attackers' key.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More
RondoDox screenshot
RondoDox
rondodox
RondoDox is an emerging Linux-based botnet malware that exploits dozens of known vulnerabilities in internet-facing devices like routers, DVRs, and web servers to build massive networks for DDoS attacks, cryptomining, and data exfiltration. First spotted in mid-2025, its "exploit shotgun" tactic (firing multiple payloads at once) has made it a rapid escalator in the IoT threat landscape, compromising unpatched edge devices worldwide.
Read More
WannaCry screenshot
WannaCry
wannacry ransomware
WannaCry is a famous Ransomware that utilizes the EternalBlue exploit. This malware is known for infecting at least 200,000 computers worldwide and it continues to be an active and dangerous threat.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More