Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Salvador Stealer

185
Global rank
190 infographic chevron month
Month rank
177 infographic chevron week
Week rank

Salvador Stealer is a powerful, information-stealing Android malware designed to silently infiltrate systems, extract sensitive data, and exfiltrate it to cybercriminals. Often sold on underground forums, it is part of the growing ecosystem of “stealers-as-a-service” (SaaS) tools that target individuals and organizations alike.

Stealer
Type
Unknown
Origin
1 February, 2025
First seen
6 August, 2026
Last seen

How to analyze Salvador Stealer with ANY.RUN

Type
Unknown
Origin
1 February, 2025
First seen
6 August, 2026
Last seen

IOCs

IP addresses
142.251.155.119
34.104.35.123
142.251.110.100
216.239.35.4
142.251.168.81
142.250.154.94
142.251.154.119
142.251.153.119
192.178.183.94
142.251.14.100
142.251.127.81
142.251.13.101
142.251.151.119
216.239.34.223
142.251.20.113
216.239.35.8
216.239.35.0
142.251.152.119
216.239.35.12
142.251.110.101
Hashes
bb9f8df61474d25e71fa00722318cd387396ca1736605e1248821cc0de3d3af8
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
8e89bbb65cdd9fffc294660ba897eb044424a9f80306f1f1f165aeea01d9b8ec
fa5461196322167a7cc4c013494f368dfad803352a43132b600a2cf93abd824c
7796f1920d44d3cb581b2cf2849d69d8c15327969d68ad69fd84eefbdfcb1fa6
4cd7cbe973cc22000b6f56a652f74d5f4499a5bdab2addf8b078fcfb3f58a9d0
deb3ca9bb445fe7175c606a0ce5177c69ed68c53126845f47d730b846746fac7
6d5cfac553ca6372b75a56f50e754d174c7c9ff5fdeb38916fea07bbe180dd2e
d67dcaeb439c1fe2f6318e94755fd46e3efcf8f18a589f3c8227ab9b7678b680
632e6f3624cb496daed384beaeee6ca2bc48088da340fb548591f270b75c35b6
968cf4eedc332ba2ed89d6282e524acf7bdd686375843093793a5146e2e27604
3993ae5d572f3f141c20dd0bedfba3aa6e0a434b735f04b107bfc93087d9ff4b
1005a525006f148c86efcbfb36c6eac091b311532448010f70f7de9a68007167
fbcfe23a2ecb82b7100c50811691dde0a33aa3da8d176be9882a9db485dc0f2d
0f1bad70c7bd1e0a69562853ec529355462fcd0423263a3d39d6d0d70b780443
71cc283f39f64025d20f81608d6ed192a09d003c963777795df5bff62cea216a
3b9d18d5cc3af6c0cb3e903327ae3da35634c7c3a0b11413b9a3b1c10c640d5e
b824e5c9ab8c8f27bab84b1c251d54fb597f317c252d2b4e3678ef0fb7783bca
6e269ac687111549b497baa7f6dbe09701f2b486c0d8c5b89bd16ca83b887e08
5a9b6e33ca96baa77881cce4380f70574b4b6e0a50d7c57010ae6f594d08092a
Domains
google.com
clientservices.googleapis.com
edgedl.me.gvt1.com
time.android.com
update.googleapis.com
staging-remoteprovisioning.sandbox.googleapis.com
e09.fatehcity.cloud
www.google.com
connectivitycheck.gstatic.com
t15.muletipushpa.cloud
play.googleapis.com
URLs
http://connectivitycheck.gstatic.com/generate_204
https://www.google.com/generate_204
https://clientservices.googleapis.com/chrome-variations/seed?osname=android_webview&milestone=137
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:fetcheekchain
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabn9atorobilsty-ejfg0rjzfe9c1kglott5g=&request_id=ceb9ca38-0a46-4ec3-a19e-cae9b2f75b64
https://update.googleapis.com/service/update2/json?cup2key=15:nuz2jbyivwjfolsnglh9igrmcfy3qh4ucrt0go-phru&cup2hreq=df887b5bd1a1fa9189e0df41c48e6b884356ddce8a82b997c37e236d065d064d
https://update.googleapis.com/service/update2/json
https://edgedl.me.gvt1.com/edgedl/release2/chrome_component/acmmwq7dser4xm5sepzjv74g65vq_2023.7.28.10/cffplpkejcbdpfnfabnjikeicbedmifn_2023.07.28.10_all_acgbwixmcanakp2bkoppyszsbkrq.crx3
http://play.googleapis.com/generate_204
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabnnk_iribilsty5aqp-unwkl_9mczwvoenck=&request_id=844c7fef-e126-46e6-906f-39c11b94ba22
https://update.googleapis.com/service/update2/json?cup2key=15:orzrozyouut51enua-wrwf3z5je7pnblfqmhaws8zd0&cup2hreq=b9cd6de503c9154ad86d31213ce77508ea8938095a5fb823a48446fac55897b4
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabnnlbccsbilsty18xudcszj50wvuozodsvlu=&request_id=37ea3b83-4efb-47ca-aca4-183789529cf1
https://update.googleapis.com/service/update2/json?cup2key=15:7uujnuocuphon0ah9scremkiyt_j31b-qmbfsnqzpnw&cup2hreq=b9406b2b592a0c895d8f59511d77e266f284a51e1ad85b7d956d7695098e2590
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 2474
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 4783
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 7302
comments 0

What is Salvador Stealer malware?

Salvador Stealer is a sophisticated Android banking malware that emerged in early 2025, designed to steal sensitive financial information through advanced social engineering and credential harvesting techniques. This mobile banking trojan masquerades as legitimate banking applications. It employs phishing infrastructure to capture critical user data including banking credentials, one-time passwords (OTPs), and personal identification information.

It is a multi-stage mobile stealer that operates through a dropper-payload architecture. Its primary components are a dropper APK that appears as a legitimate banking application, and a secondary payload (base.apk) containing the core malicious functionality. The malware uses sophisticated obfuscation techniques, including XOR encryption with the key "npmanager" to hide its malicious strings and communications.

Salvador bypasses traditional security measures by leveraging WebView technology to embed phishing pages directly within the application. This approach allows the malware to create a convincing user interface that mimics legitimate banking applications while maintaining direct communication with command and control servers. The persistence mechanisms include automatic restart capabilities and boot-time execution, ensuring continuous operation even after device reboots or manual termination attempts.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Salvador Stealer Victimology

The stealer primarily targets mobile banking users in India and other South Asian regions, as evidenced by its focus on collecting Aadhaar numbers and PAN card details (identification documents specific to the Indian financial system). The malware specifically targets users of popular Indian banking institutions by mimicking their mobile applications and branding.

Its broad spectrum of victims aggregates individuals, small businesses, and large enterprises. It focuses on users with access to valuable data, such as corporate credentials, financial accounts, or cryptocurrency wallets. Organizations in sectors like finance, healthcare, and technology are particularly vulnerable due to the high value of their data. Remote and hybrid work environments, especially those using Bring Your Own Device (BYOD) policies, are at higher risk because of relaxed security controls and increased attack surfaces.

What Salvador Stealer Can Do to User Device

Once installed on an endpoint device, Salvador Stealer can:

  • Steal Credentials: Extracts usernames, passwords, and session cookies from browsers and applications.
  • Harvest Financial Data: Targets credit card details, bank account information, and cryptocurrency wallet credentials.
  • Capture Keystrokes: Uses keyloggers to record user inputs, including unsaved passwords.
  • Hijack Clipboards: Replaces or steals data copied to the clipboard, such as account numbers or crypto addresses.
  • Take Screenshots: Captures screen content to gather sensitive information displayed at critical moments.
  • Exfiltrate Files: Collects local files, such as PDFs or documents containing personal or corporate data.

The malware significantly compromises device security by requesting and abusing critical Android permissions including SMS reception, SMS sending, and internet access. It creates fake notifications to maintain user engagement and establish a legitimate appearance. It also modifies system behavior by registering broadcast receivers that ensure automatic execution upon device startup and network changes.

How Salvador Stealer Threatens Businesses and Organizations

Salvador Stealer poses severe risks to businesses by enabling:

  • Data Breaches: Stolen credentials can lead to unauthorized access to corporate networks, facilitating larger attacks like ransomware.
  • Financial Loss: Theft of financial data or cryptocurrency can result in direct monetary losses.
  • Lateral Movement: Compromised credentials allow attackers to move within networks, targeting critical systems or data repositories.
  • Reputational Damage: Leaked customer or proprietary data can erode trust and lead to regulatory penalties.
  • Ransomware Enablement: Stolen data is often sold to ransomware groups for extortion or further attacks.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

How Does Salvador Stealer Function?

Salvador Stealer operates by infiltrating a system and running in the background to avoid detection. It employs a modular architecture, allowing attackers to customize its payload for specific targets. Upon execution, it scans for valuable data, such as browser-stored credentials, session tokens, and cryptocurrency wallets. The malware communicates with a command-and-control (C2) server to exfiltrate stolen data, often using encrypted channels to evade detection (including Telegram Bot API integration and traditional HTTP POST requests to attacker-controlled servers). Its lack of persistence mechanisms means it focuses on quick data theft, leaving minimal traces unless detected early.

The stealer spreads through common attack vectors, including phishing emails, malicious downloads, social engineering, and malwertising. Phishing pages are designed using WebView technology to closely mimic legitimate banking interfaces, complete with proper branding and user experience elements. The malware injects malicious JavaScript code that intercepts XMLHttpRequest operations, ensuring that all user inputs are captured and forwarded to the attackers.

Advanced SMS interception capabilities allow Salvador Stealer to capture one-time passwords and two-factor authentication codes in real-time. The malware implements dynamic SMS forwarding, where it contacts remote servers to retrieve current forwarding numbers, allowing attackers to modify their collection infrastructure without updating the malware. This flexibility makes the malware particularly dangerous as it can adapt to changing operational requirements.

Salvador Stealer Attack Chain Live

We can see how exactly the above-mentioned tactics, technologies, and approaches combine Salvador’s execution chain by watching its sample detonated in ANY.RUN’s Interactive Sandbox.

View sandbox analysis of Salvador Stealer
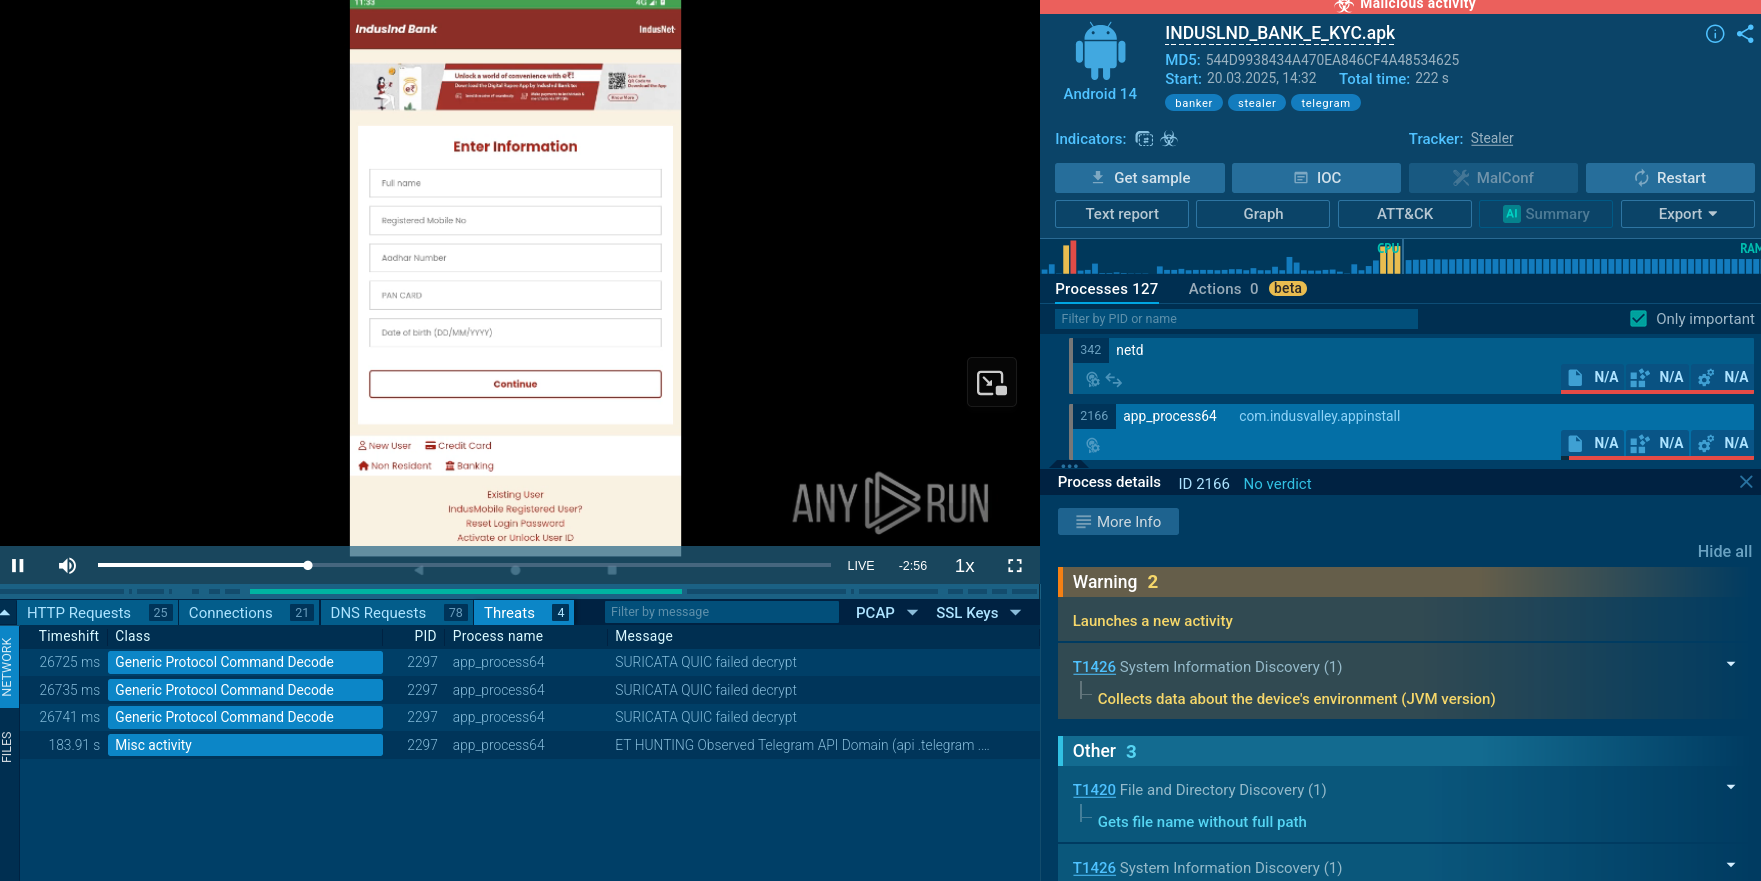
Salvador Stealer malware analysis in the Sandbox Salvador Stealer malware analysis in the Sandbox

The two key components art Dropper APK that installs and triggers the second-stage payload, and Base.apk, the actual payload responsible for data theft.

The dropper APK declares specific permissions and intent filters in its AndroidManifest.xml, including package installing.

Once executed, base.apk exhibits several key behaviors:

  1. It establishes a connection to Telegram, which the attackers use as a Command and Control (C2) server to receive stolen data and manage the infection.
  2. It triggers the signature “Starts itself from another location,” confirming that it was dropped and launched by the initial dropper APK rather than being installed directly.

After loading the phishing WebView it requests several Android permissions, including:

  • RECEIVE_SMS
  • SEND_SMS
  • READ_SMS
  • INTERNET

These permissions are essential for the malware’s goals: intercepting one-time passwords (OTPs) and forwarding them. Once the permissions are granted, the initiateForegroundServiceIfRequired() method is called, launching the Fitzgerald service.

This foreground service creates a fake notification (“Customer support”) and more importantly, it immediately registers a broadcast receiver to intercept incoming SMS. This is the real starting point of the OTP interception process. Every incoming message is captured and parsed by Earnestine. From the PDU, the malware extracts the message body, sender’s number, and timestamp.

Even if the user or system tries to terminate the app’s background service, the malware is programmed to automatically restart it. When the Fitzgerald service is killed or swiped away, it immediately schedules a recovery task using Android’s WorkManager.

If the device itself is rebooted, a separate class named Ellsworth waits for reboot completion and triggers the Fitzgerald service again.

The Salvador Stealer tricks users into entering their banking credentials through a fake banking interface phishing page embedded in the app. Once the user submits their credentials, the data is immediately sent to both the C2 server and a Telegram bot. The data lands on a phishing website controlled by the attacker.
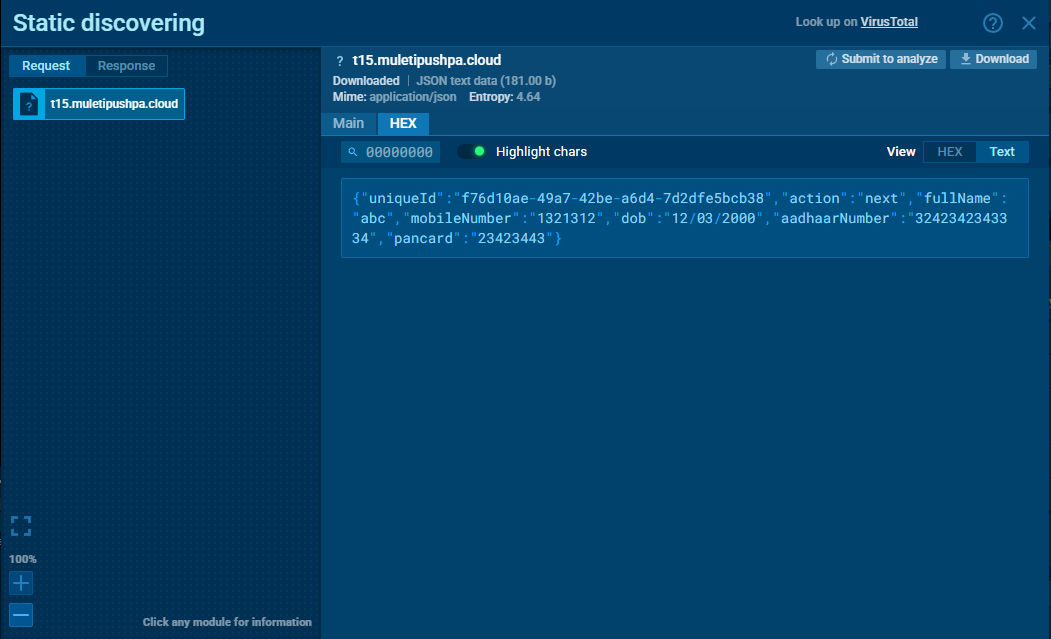
Salvador Stealer sends data to phishing site Stolen data sent to phishing site

By enabling HTTPS MITM Proxy mode in ANY.RUN’s Android sandbox, we were able to intercept and verify the exfiltration of user data in real time.
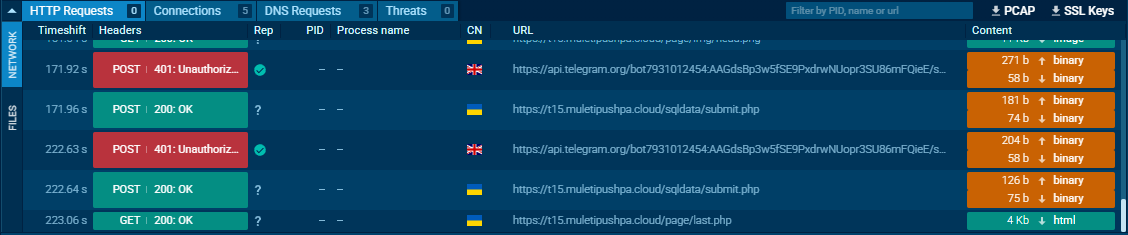
Credential theft attempts Credential theft attempts captured in the HTTP request logs

ANY.RUN’s analysts researched Salvador Stealer in depth by decoding the malware files and performing technical analysis, and made a number of interesting discoveries.

Gathering Threat Intelligence on Salvador Stealer malware

Threat intelligence provides critical insights into Salvador Stealer’s tactics, techniques, and procedures (TTPs). By analyzing data, organizations can:

  • Identify emerging Salvador Stealer campaigns and their delivery methods.
  • Use indicators of compromise(IOCs) like C2 server IPs or malware signatures to improve detection.
  • Update security policies based on intelligence about new variants or evasion techniques.

Use ANY.RUN’s Treat Intelligence Lookup to find more Salvador samples dissected in the Interactive Sandbox, watch their behavior in the network and on device, collect IOCs and IOBs.
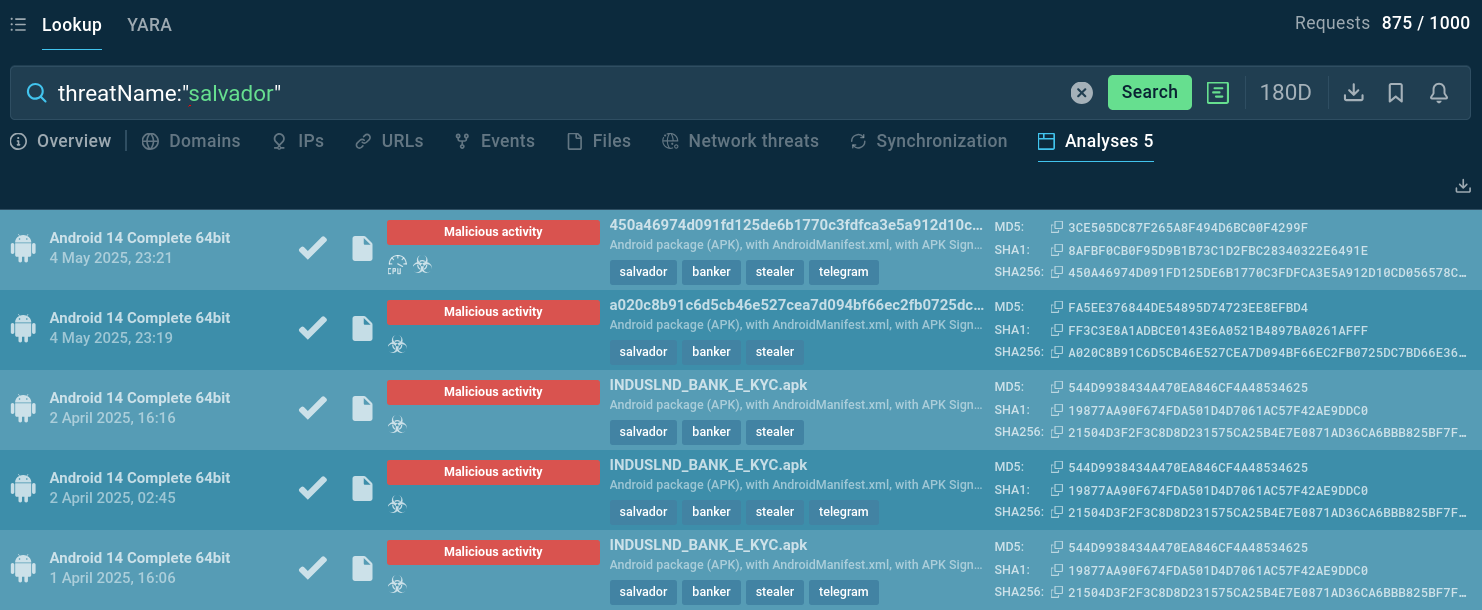
threatName:"salvador"

Salvador Stealer samples found via TI Lookup Salvador Stealer public sandbox analyses found via TI Lookup

Security teams should integrate threat intelligence feeds that include mobile malware indicators, especially Android banking trojans and their associated infrastructure.

Collecting indicators and understanding the TTPs of Salvador Stealer operators enables better detection and prevention strategies. This intelligence should inform security awareness training programs and help organizations adapt their security controls to address specific threat actor behaviors.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Salvador Stealer represents a significant evolution in mobile banking malware with its sophisticated technical capabilities and clever social engineering. Its advanced persistence mechanisms, real-time data exfiltration capabilities, and multi-channel command and control infrastructure make it particularly dangerous to both individual users and organizations.

Continuous vigilance and adaptation are required to enhance security practices. Businesses must invest in mobile security technologies, threat intelligence capabilities, and user education programs to stay ahead of these evolving threats.

Gather actionable intelligence via ANY.RUN’s TI Lookup: start with 50 trial requests.
HAVE A LOOK AT

EvilTokens screenshot
EvilTokens
eviltokens
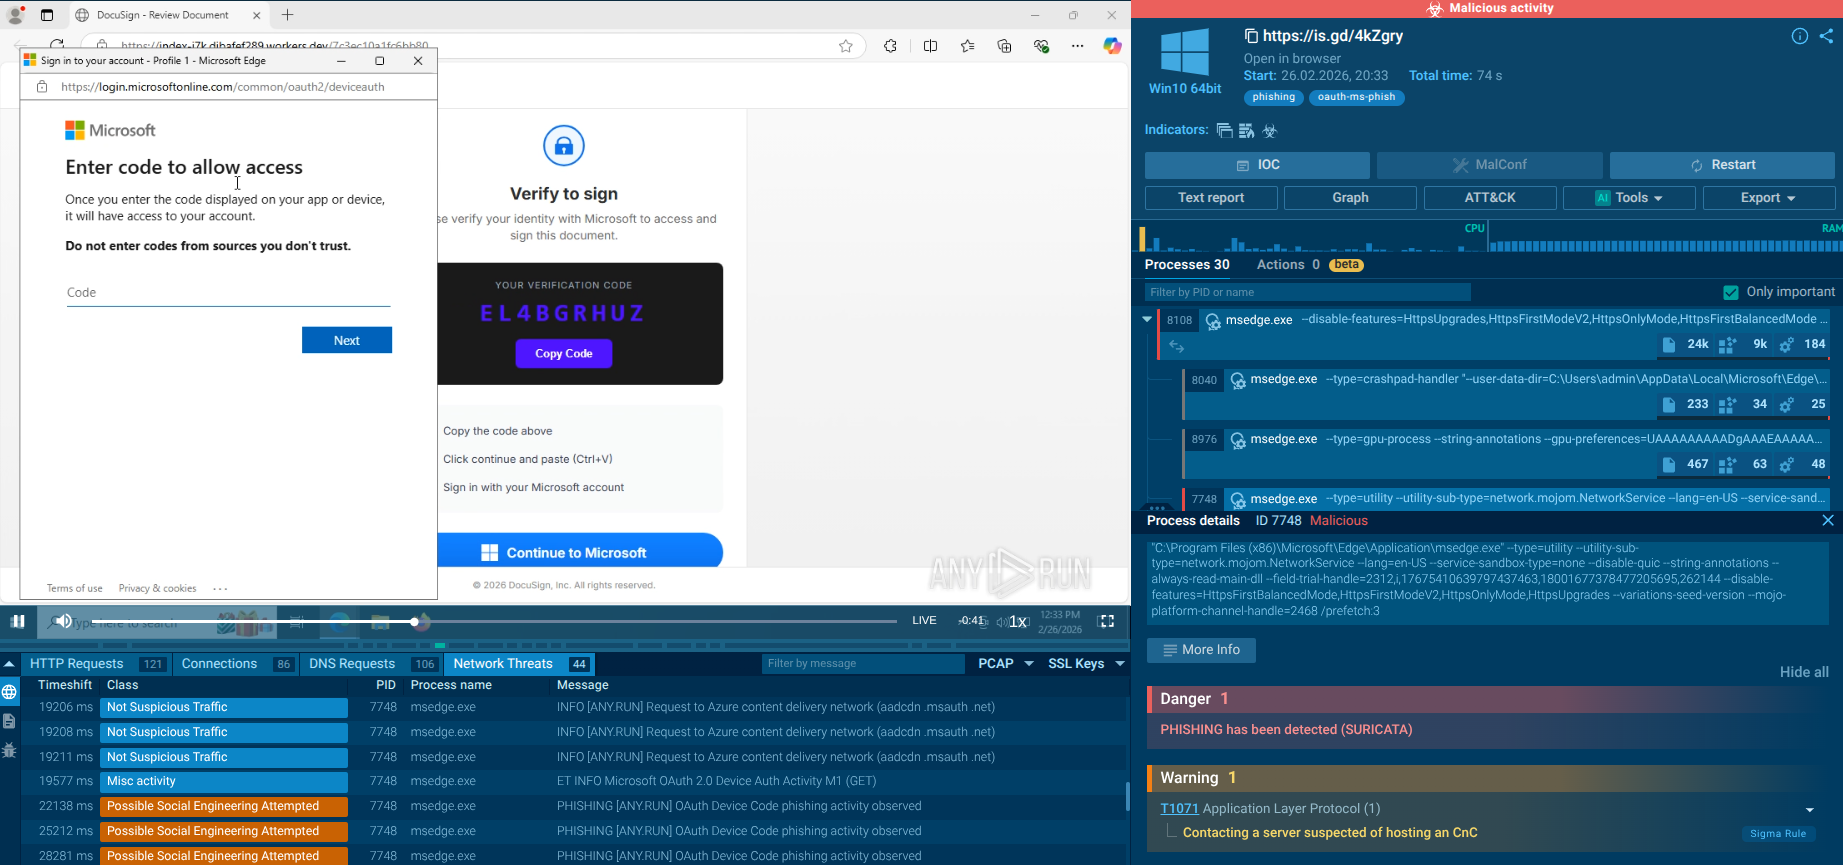
EvilTokens is a phishing-as-a-service (PhaaS) toolkit that emerged in mid-February 2026. It automates device code phishing attacks against Microsoft 365 and Entra ID environments. Unlike traditional credential-harvesting phishing, EvilTokens tricks users into completing legitimate authentication on Microsoft's own login pages, resulting in the issuance of valid OAuth access and refresh tokens directly to the attacker, effectively bypassing MFA without stealing passwords.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
DonutLoader screenshot
DonutLoader
donutloader donut
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
DarkComet screenshot
DarkComet
darkcomet rat darkcomet rat
DarkComet RAT is a malicious program designed to remotely control or administer a victim's computer, steal private data and spy on the victim.
Read More
Chaos Ransomware screenshot
Chaos ransomware is a malware family known for its destructive capabilities and diverse variants. It first appeared in 2021 as a ransomware builder and later acted as a wiper. Unlike most ransomware strains that encrypt data to extort payment, early Chaos variants permanently corrupted files, while later versions adopted more conventional encryption techniques.
Read More
 screenshot
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
Read More