Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

HijackLoader

37
Global rank
44 infographic chevron month
Month rank
47 infographic chevron week
Week rank

HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.

Loader
Type
Unknown
Origin
1 July, 2023
First seen
8 October, 2026
Last seen

How to analyze HijackLoader with ANY.RUN

Type
Unknown
Origin
1 July, 2023
First seen
8 October, 2026
Last seen

IOCs

IP addresses
23.11.41.157
48.209.138.168
74.178.240.61
2.16.204.141
40.126.31.69
150.171.109.98
48.192.1.64
172.211.123.249
23.59.18.102
74.179.77.164
190.144.146.90
131.253.33.203
172.211.123.248
150.171.109.101
2.16.204.159
142.251.110.94
151.101.1.91
151.101.193.91
142.251.153.119
142.251.127.84
Hashes
573e3260eed63604f24f6f10ce5294e25e22fda9e5bfd9010134de6e684bab98
7e1f9048d457369e50ee2ccc3659c897a740ecf722036858c88390115e5612a1
564cad30db98cbac3fd6c64e57d741ca2802cd4d9e981ef3696f5f301486c7c9
576e1b7f8848b4a73a05829205c38bb0388ef478b904031f6e6ea571f9c0f579
a67723129855a7d7fb79d57ef56f73e6bd907fcdad7a8d019753b11e194d582c
6824f8a5e160b5bbf4bbb47d445b199529c85c66f21d7d38bf46eeeeefbff959
9abfbcc6a8bcde755b12dacd88f81c63f201b25d9caea703f357075560c8554d
cbe0b63a8e5e19c6b2805d71567d83ba8a12f9d159fc7bb0e37ff3ed224ebbf7
8002feae245dd9bd5f112bfbfa93924c75d8e6f7dba697183cc831a00b871413
fb4f99cd0da2a02975e84206a39202eee74f0384846f2caf4417704f44e254e9
505916e8b40fdd031ee21eea40a8bee0adeac0d04e23c3a6b10ecee0217d2416
a5a6868aaa4bf8208ab9a29d76456dbe5148a81c67808c01776a8553fdc67074
2dc5a31f67fe877ca0eb95113873749def2beb0a205c62de206ccd7a668fce14
6d5a84ce35c0dc04c8c9c99d27a4b2eb695ab9a5c10ce5dcce121985af35b056
30f7129b7b2bcf674f797c8ab80f436baf1748db192d2197cf94ffc5f3614ddd
f4e70abe2e83f9b91e7d768ed7158c51008ffdc1f425ca5d9c28f9c4896278a3
20a41ea17da0f120c232cba1ba382c7491d1308b5d83b88275bb690834d174e5
e3faecf2c0d899e2d6f62822285da4f49eaed5ceb33ebe06add5e85562d482e6
a019980cb22a5598fa8e811217ccb01ed8c679a95be58c4052005b73661fa978
e63e86df007fde84792032d4e5bf815bf0382eeb6a2917c4ab3877a870517249
Domains
slscr.update.microsoft.com
servis.vidrisoctsa.com
self.events.data.microsoft.com
www.microsoft.com
ecs.office.com
login.live.com
client.wns.windows.com
fe3cr.delivery.mp.microsoft.com
activation-v2.sls.microsoft.com
www.bing.com
ocsp.digicert.com
crl.microsoft.com
settings-win.data.microsoft.com
google.com
oneocsp.microsoft.com
www.gstatic.com
tagesschau.de
normandy.tombstone.experimenter.prod.webservices.mozgcp.net
update.googleapis.com
edge-mobile-static.azureedge.net
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f8%2f2026%2c%207%3a08%3a23%20pm
https://www.bing.com/th?id=odswg.dd482747-0b27-423b-a458-0ac58ffc4b0e&pid=dsb
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:4l4bxdq38lvrp1-igo6v0cikkazcrfcng7ggc5f1v-8&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791464585&lafgdate=0
https://google.com/
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://www.google.com/
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 3170
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 5311
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 8067
comments 0

What is HijackLoader malware?

HijackLoader is a loader malware that possesses strong evasion capabilities, allowing it to bypass mainstream security solutions. It has been observed to deliver numerous persistent malware families, such as DanaBot and the RedLine stealer.

Most of the known attacks involving HijackLoader began with phishing emails. As of the end of 2023, it continues to be an active threat. The modular design of the malware is one of the key factors behind its popularity. It enables HijackLoader to ensure a more flexible approach to deployment on the infected system and further execution of the final payloads.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of the HijackLoader malicious software

HijackLoader is notorious for its ability to evade detection. One way it does this is by utilizing a modified Windows C Runtime (CRT) function to gain a foothold on the device.

During the initial stage, HijackLoader also ascertains whether the final payload is embedded in the binary or has to be downloaded from external sources. It does this through the use of an array of DWORD values.

It can also check if the device is connected to the Internet by attempting to connect to legitimate websites. The network connectivity check is a clever strategy that allows HijackLoader to remain undetected while the network is unavailable. In a similar fashion, the malware can delay the execution of different parts of its code to once again avoid early detection.

To make it more difficult for reverse engineers to analyze its code, the malware uses dynamic API loading via a custom hashing method. This makes it harder to locate the specific API calls used during execution.

HijackLoader’s AVDATA module is designed specifically for the purpose of identifying security software installed on the system and adjusting its operation depending on the results of its scanning.

Execution process of HijackLoader

Let’s take a closer look at the execution flow of a HijackLoader sample by uploading it to the ANY.RUN sandbox.

HijackLoader is a typical loader, and its execution flow is also straightforward and simple. This simplicity allows malware to remain less active inside infected systems, making it more challenging to detect. However, it can still attract attention in certain cases.

In our example, the loader leveraged the CMD utility to stay under the radar. It, in turn, initiates the MSBuild process, which downloads and runs the Phonk which downloads the miner. HijackLoader demonstrates evasion capabilities that aid in staying undetected by certain security solutions.

Analyze malware for free in a fully interactive cloud sandbox – sign up now!
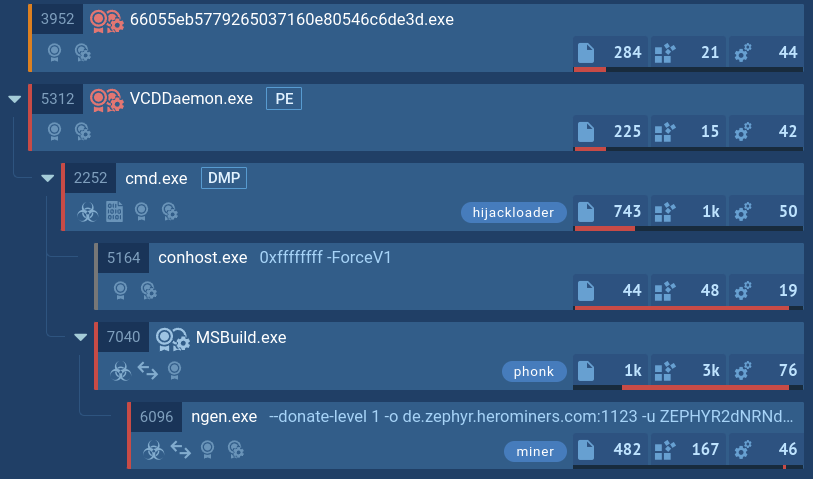
HijackLoader process tree shown in ANY.RUN HijackLoader's process tree demonstrated in ANY.RUN

Distribution methods of the HijackLoader malware

The preferred method of infiltration among the attackers behind HijackLoader is phishing attacks, where cybercriminals craft emails that appear to be from legitimate sources, hoping to trick recipients into opening malicious attachments or clicking on infected links.

In one notable instance, hotels were targeted with emails from fake clients claiming to be staying at the hotel and requesting staff to download a file containing information on their allergy. Once opened, the file kickstarted the infection chain resulting in the deployment of HijackLoader on the victim’s device.

Conclusion

Keeping your infrastructure safe from a HijackLoader infection requires a proactive cybersecurity approach. An indispensable part of it is a reliable malware analysis sandbox like ANY.RUN.

With ANY.RUN, you can example incoming emails to determine any malicious intent behind them with ease. The service’s interactive cloud environment enables you to effectively investigate even the most intricate phishing campaigns and uncover multi-stage attacks in no time. The service delivers comprehensive text reports encompassing detailed information about the submitted files and links, including fresh IOCs.

Adopt a proactive cybersecurity approach by leveraging ANY.RUN.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

DarkComet screenshot
DarkComet
darkcomet rat darkcomet rat
DarkComet RAT is a malicious program designed to remotely control or administer a victim's computer, steal private data and spy on the victim.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
EvilTokens screenshot
EvilTokens
eviltokens
EvilTokens is a phishing-as-a-service (PhaaS) toolkit that emerged in mid-February 2026. It automates device code phishing attacks against Microsoft 365 and Entra ID environments. Unlike traditional credential-harvesting phishing, EvilTokens tricks users into completing legitimate authentication on Microsoft's own login pages, resulting in the issuance of valid OAuth access and refresh tokens directly to the attacker, effectively bypassing MFA without stealing passwords.
Read More
DEVMAN screenshot
DEVMAN
devman
DEVMAN is a fast-evolving malware family targeting Windows environments with a mix of credential theft, remote control capabilities, and persistence techniques typical of modern crimeware. Initially observed in early 2025, DEVMAN quickly became a favorite tool among cybercriminal groups thanks to its stealth, modular structure, and ability to bypass traditional AV solutions.
Read More
AsyncRAT screenshot
AsyncRAT
asyncrat
AsyncRAT is a RAT that can monitor and remotely control infected systems. This malware was introduced on Github as a legitimate open-source remote administration software, but hackers use it for its many powerful malicious functions.
Read More