Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Akira Ransomware

89
Global rank
97 infographic chevron month
Month rank
170 infographic chevron week
Week rank

Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.

Ransomware
Type
Unknown
Origin
1 March, 2023
First seen
28 September, 2026
Last seen

How to analyze Akira Ransomware with ANY.RUN

Type
Unknown
Origin
1 March, 2023
First seen
28 September, 2026
Last seen

IOCs

IP addresses
23.52.181.141
48.209.6.48
74.179.77.204
2.21.20.144
2.21.20.152
23.11.40.157
128.24.231.65
95.100.102.101
74.179.77.164
23.52.181.212
20.190.177.146
172.211.123.249
92.123.104.64
2.23.246.9
48.209.138.189
23.59.18.102
40.126.53.11
128.24.231.64
20.165.94.63
2.16.204.135
Hashes
9ca333b2e88ab35f608e447b0e3b821a6e04c4b0c76545177890fb16adcab163
e8f64f6f49b8231476e1028b75f2a3e5317ed506db6d1a265dbf3c28eb3e1d1a
3d8784c6f596cdba0f9ca298ce53b401358d7ea24247ab1243ef12b59f9cf8f2
41dff22022cc25cbbd94ffdd2e645d0c7100726692c4b13570421efa44adde64
9bd021f7c618978bafd82a37767d324aa2ec9f994f1579373fa9ef7fdc43b43d
10063e3781e001af225641b4852358cceb2025c8d6999f3334c93e3eede2e4bf
5f4bd012566ea662ff7874d180e7ef31eab45ece9af31862e6c4064cdb7017b8
9f65cf856209e00414cd66f8d5d1aab872322acea99118dc01c60e00e563e6a1
bd010a90ee684c3f2c6823c7a36d80bad1fd715e619a9bebbe6f8eca6f7d987b
c854790ca609182a055463fdf2a74e75d86c9c78b78bda6aa04fcb76e46fb3d8
a32088dd3dcd7d52d209f76fd980e7784e810778a4236243b8168d0edd381ca4
fd0453cee2b284388a66f6947c0461df6a2931fa23cb1dc6794d242a6d1e5630
b509588c54c9e5feff4296fc6cd2ed83a35612bdfbd32be5c95fce58bb0fe212
c494bbe3fa22a7fd783430f9b5dc7a7ba67e5ad33d94b343e44bbe7e2a2549fd
2321681aa2ae4a2c819d9887ff649ddcb0489234a5d66159ffb7003fbde18154
a1c9e9b159bb7c7d994316cc5ad0b00f2ef7307a18a334b73df099b0c8c706fa
0d0fcb5c536ee222ab546fa44fc69e95251785dcaeacb138b30978ffb34f9c58
f86a705642a4753b0b0aca3090360b40fa075169fbae0a0d3891eb078a19cfa4
44cb66efa1b56813c5d596b67e1a4afe7879fcd66ca729f89ca57a614dc10314
8db82cf10e9b2604f4bfcfca9575e1ebe8c526ac54af72ab42ec80c25804c902
Domains
settings-win.data.microsoft.com
google.com
slscr.update.microsoft.com
client.wns.windows.com
activation-v2.sls.microsoft.com
ecs.office.com
crl.microsoft.com
www.microsoft.com
go.microsoft.com
ocsp.digicert.com
self.events.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
login.live.com
www.bing.com
8.100.168.192.in-addr.arpa
api.snapcraft.io
connectivity-check.ubuntu.com
151.1.168.192.in-addr.arpa
dashboard.snapcraft.io
canonical-lgw01.cdn.snapcraftcontent.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://connectivity-check.ubuntu.com/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is Akira malware?

Akira is a ransomware-as-a-service that became known in the spring of 2023 as a weapon in the hands of Howling Scorpius group. Its ability to adapt, exploit vulnerabilities, and employ double-extortion tactics makes it a significant cybersecurity concern. That perception has been well-supported by hundreds of victims with ransom payments surpassing $40 mln.

It targets a spectrum of industries, including finance, technology, healthcare, education, and manufacturing. Being a human-operated ransomware, it can be manually adapted to bypass network defenses.

This ransomware uses a variety of methods to gain initial access to networks, often exploiting weaknesses in external-facing systems or human error. The methods include phishing, stolen credentials, VPN vulnerabilities, exploit kits and RMM tools.
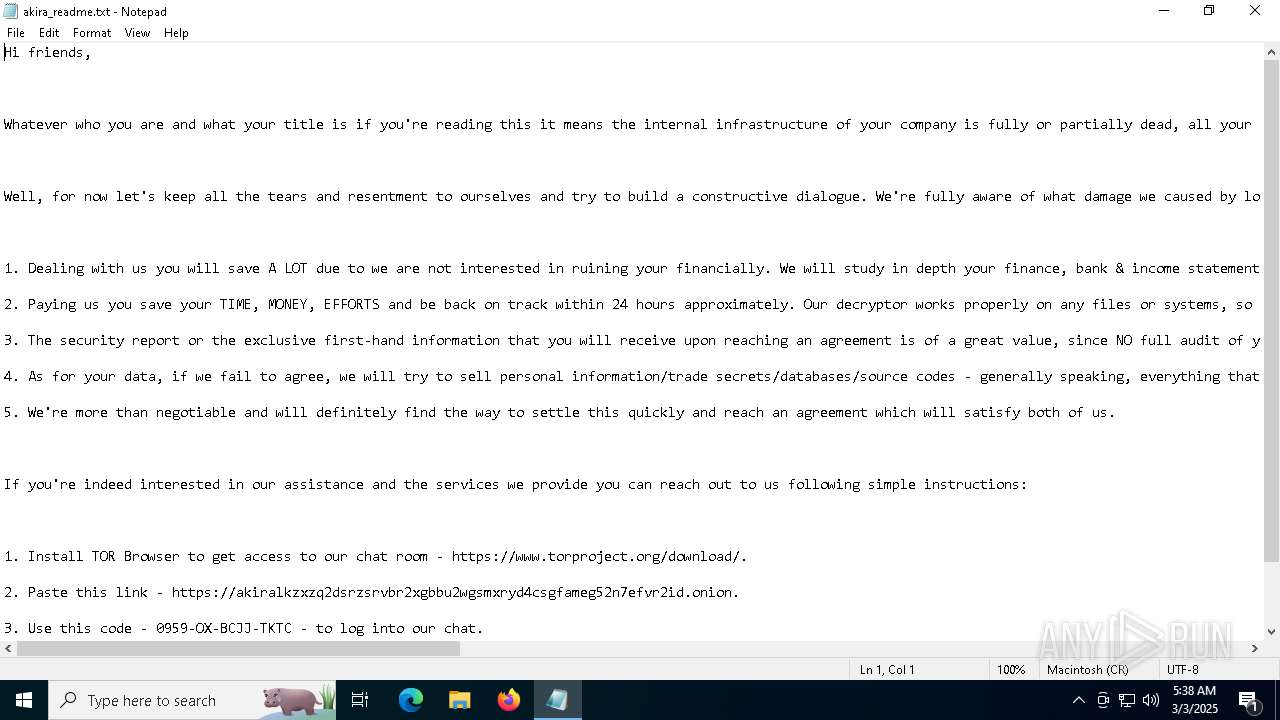
Akira ransomware analysis in ANY.RUN Akira Ransomware ransom note shown inside ANY.RUN's Interactive Sandbox

Once inside the network, Akira conducts a multi-stage attack: first it creates scheduled tasks and registry keys to maintain access, deploys backdoors to allow re-entry. It spreads in the network and scans it for valuable data. It exfiltrates the data and then encrypts it on the endpoint adding an .akira file extension which is a reference to the 1988 Japanese anime "Akira". A ransom note with payment instructions is generated.

Akira is good at evasion: it abuses native Windows tools to execute payloads, leverages process injection and living-off-the-land techniques (LOLBins). Some components execute filelessly, directly in memory, reducing the footprint on disk.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Akira’s Prominent Features

Considering the basic TTPs, Akira is similar to most ransomware families, but it has a number of outstanding features that render it notably dangerous:

  • Akira is not industry specific though it prefers to target small and medium businesses.
  • Hackers actively manage the attack lifecycle. It grants Akira sophistication and adaptability, better evasion, longer dwell time and higher success rate
  • Akira can be quick and has been observed to move from initial access to information exfiltration in just two hours which is much faster than average.
  • Akira’s operators practice a "decryption proof" providing to build trust and pressure victims into paying the ransom.

Akira’s Execution Process and Technical Details

ANY.RUN's Interactive Sandbox allows to detonate Akira on virtual machine with set-up parameters while bypassing its sandbox evasion capabilities.

View sandbox analysis

The execution chain of Akira ransomware involves several key steps, from initial access to data encryption. Initially, Akira operators may gain entry through multiple methods, including exploiting VPNs without multi-factor authentication (MFA) and other known vulnerabilities. Once inside, they focus on privilege escalation and lateral movement.
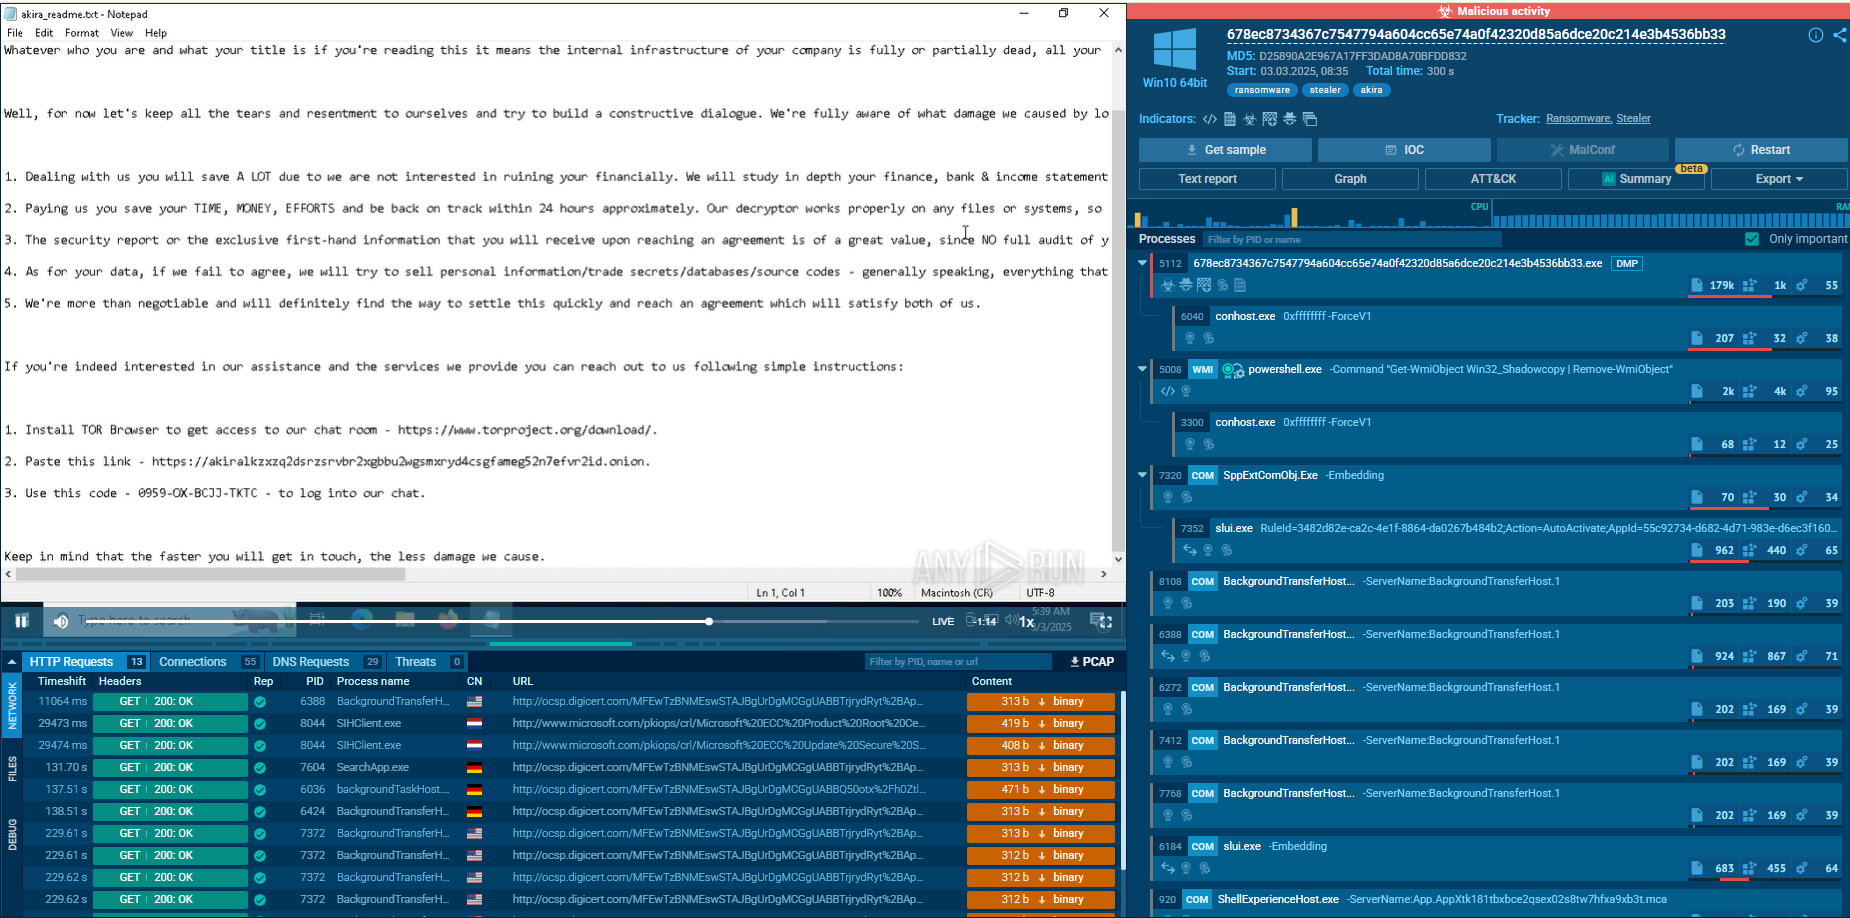
Akira ransomware analysis in ANY.RUN Akira Ransomware analysis inside ANY.RUN's Interactive Sandbox

Post-infiltration, Akira uses tools like Advanced IP Scanner, MASSCAN, PCHunter, SharpHound, AdFind, and net Windows commands to map networks, identify critical systems, and gather domain information.

It uses credential-dumping tools (e.g., Mimikatz, LaZagne) to extract credentials from memory (LSASS) or browsers. In some cases, Akira extracts the NTDS.dit file from domain controllers by manipulating virtual machine (VM) backups, granting access to domain admin privileges.

To evade detection, Akira actors employ various defense evasion strategies. They may use tools such as PowerTool, KillAV, and Terminator to disable antivirus solutions. Registry modifications are performed to disable or reconfigure Microsoft Defender and to hide accounts on the login screen, ensuring their malicious activities remain undetected for as long as possible.
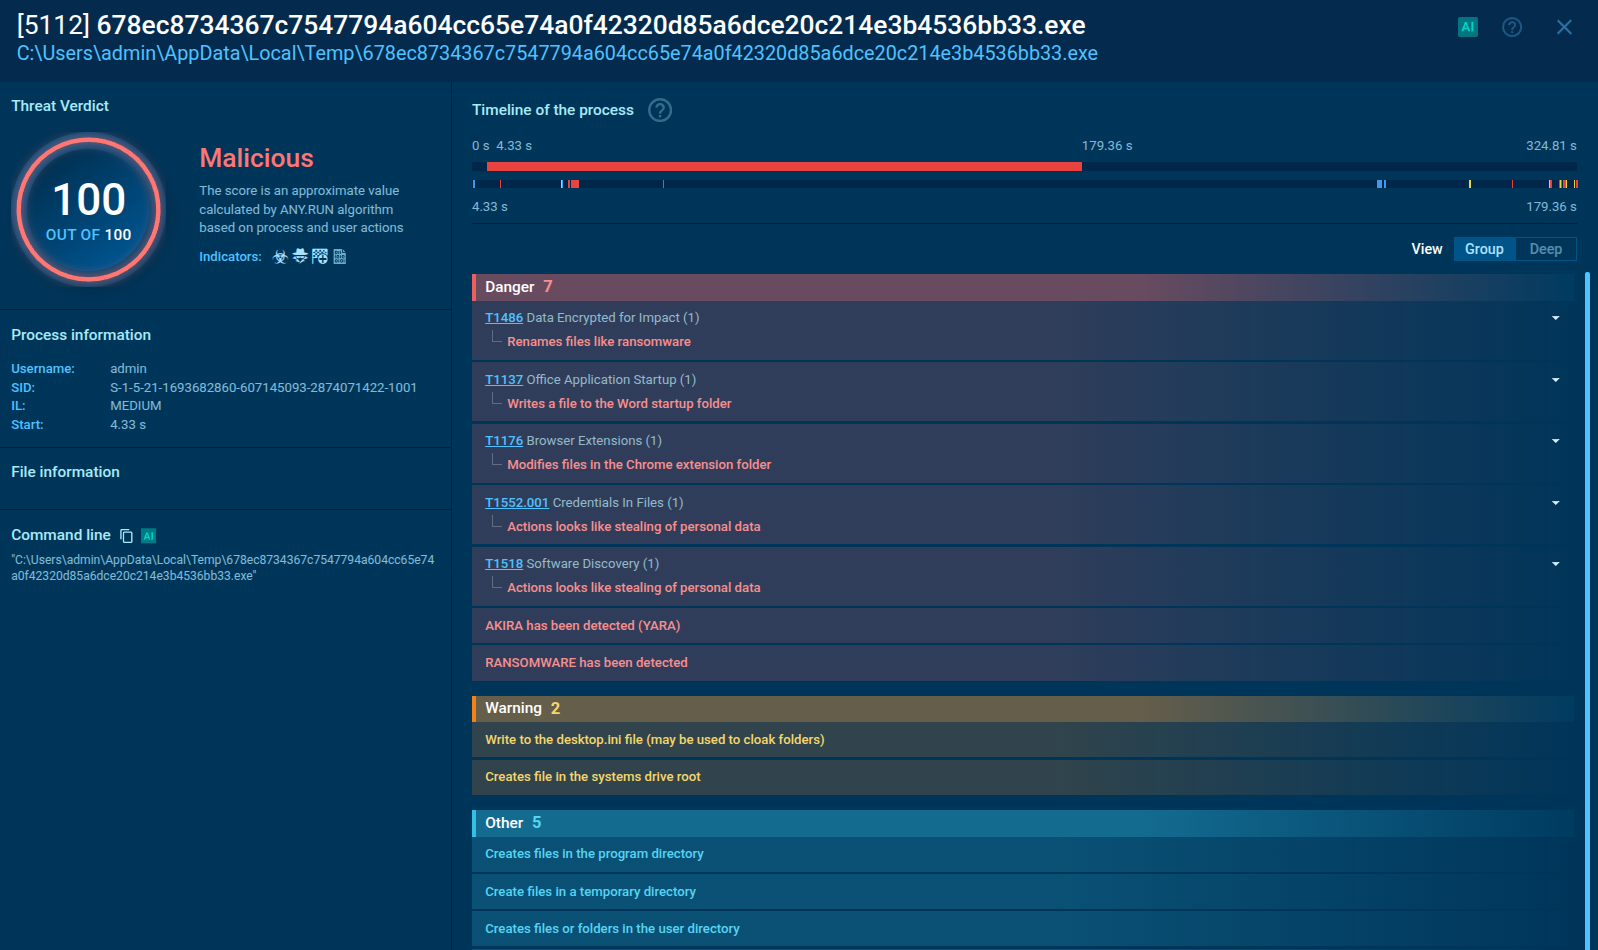
Akira ransomware analysis in ANY.RUN ANY.RUN highlights malicious activities performed by Akira Ransomware

In the final stages, attackers exfiltrate and encrypt data. Akira uses a combination of ChaCha20 and RSA encryption algorithms for secure data encryption. Files are renamed with the .akira extension, and a ransom note is left behind. PowerShell commands are executed to delete Volume Shadow Copy Service (VSS) files—preventing easy file recovery.

In one observed instance, a PowerShell process (PID 5008) deleted these VSS files. Data is also compressed (using tools like WinRAR, FileZilla, WinSCP, Rclone) and exfiltrated, often camouflaged as legitimate traffic to avoid detection.

After encrypting and exfiltrating data, Akira places ransom notes, such as akira_readme.txt, in various directories. These notes provide instructions for victims to recover their encrypted files by paying a ransom. The ransom demand marks the culmination of the attack, as the attackers attempt to extort payment in exchange for the decryption key.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Gathering threat intelligence on Akira malware

Akira continues to steadily spread and to result in more victims calling for special attention by SOC teams for timely prevention and response. Use Threat Intelligence Lookup to track IOCs like C2 domains, hashes, and known IPs related to Akira; apply YARA rules to identify malicious binaries and scripts.
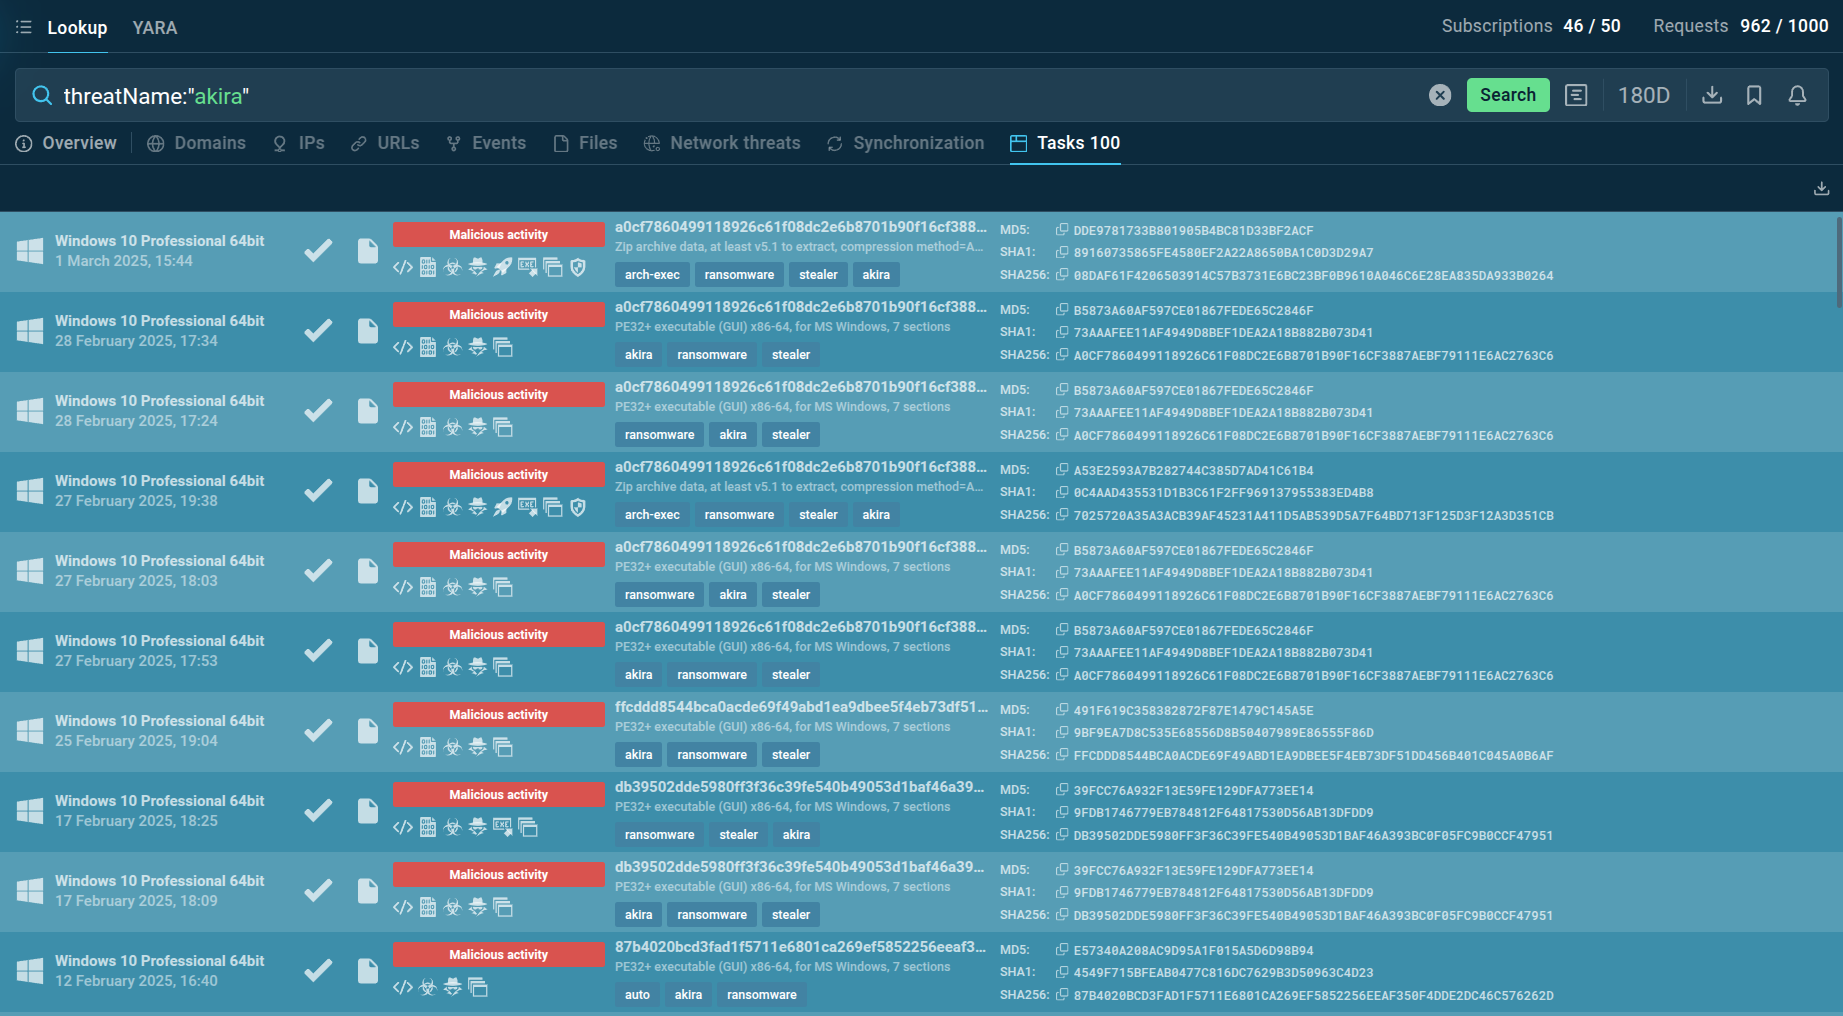
Akira ransomware results in ANY.RUN TI Lookup TI Lookup helps users collect fresh intel on Akira Ransomware attacks

With the use of the query threatName:"akira", we can identify the latest samples of this ransomware and collect fresh intel.

TI Lookup provides a list of recent sandbox sessions featuring analysis of Akira Ransomware. You can explore each of these in more detail and export the findings in JSON.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Akira RaaS has emerged as a significant threat in the landscape because it enables even low-skilled actors to deploy highly sophisticated ransomware attacks and operates encryptors for Windows and Linux operating systems. Organizations should secure their perimeter and ensure proactive defense against this threat by employing threat intelligence tools like TI Lookup to gather the latest IOCs.
Get 50 requests in TI Lookup to collect fresh threat intelligence on Akira and other malware and phishing attacks

HAVE A LOOK AT

 screenshot
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
Read More
Grandoreiro screenshot
Grandoreiro
grandoreiro
Grandoreiro is a Latin American banking trojan first observed in 2016. It targets mostly Spanish-speaking countries, such as Brazil, Spain, Mexico and Peru. This malware is operated as a Malware-as-a-Service (MaaS), which makes it easily accessible for cybercriminals. Besides, it uses advanced techniques to evade detection.
Read More
Razr screenshot
Razr
razr
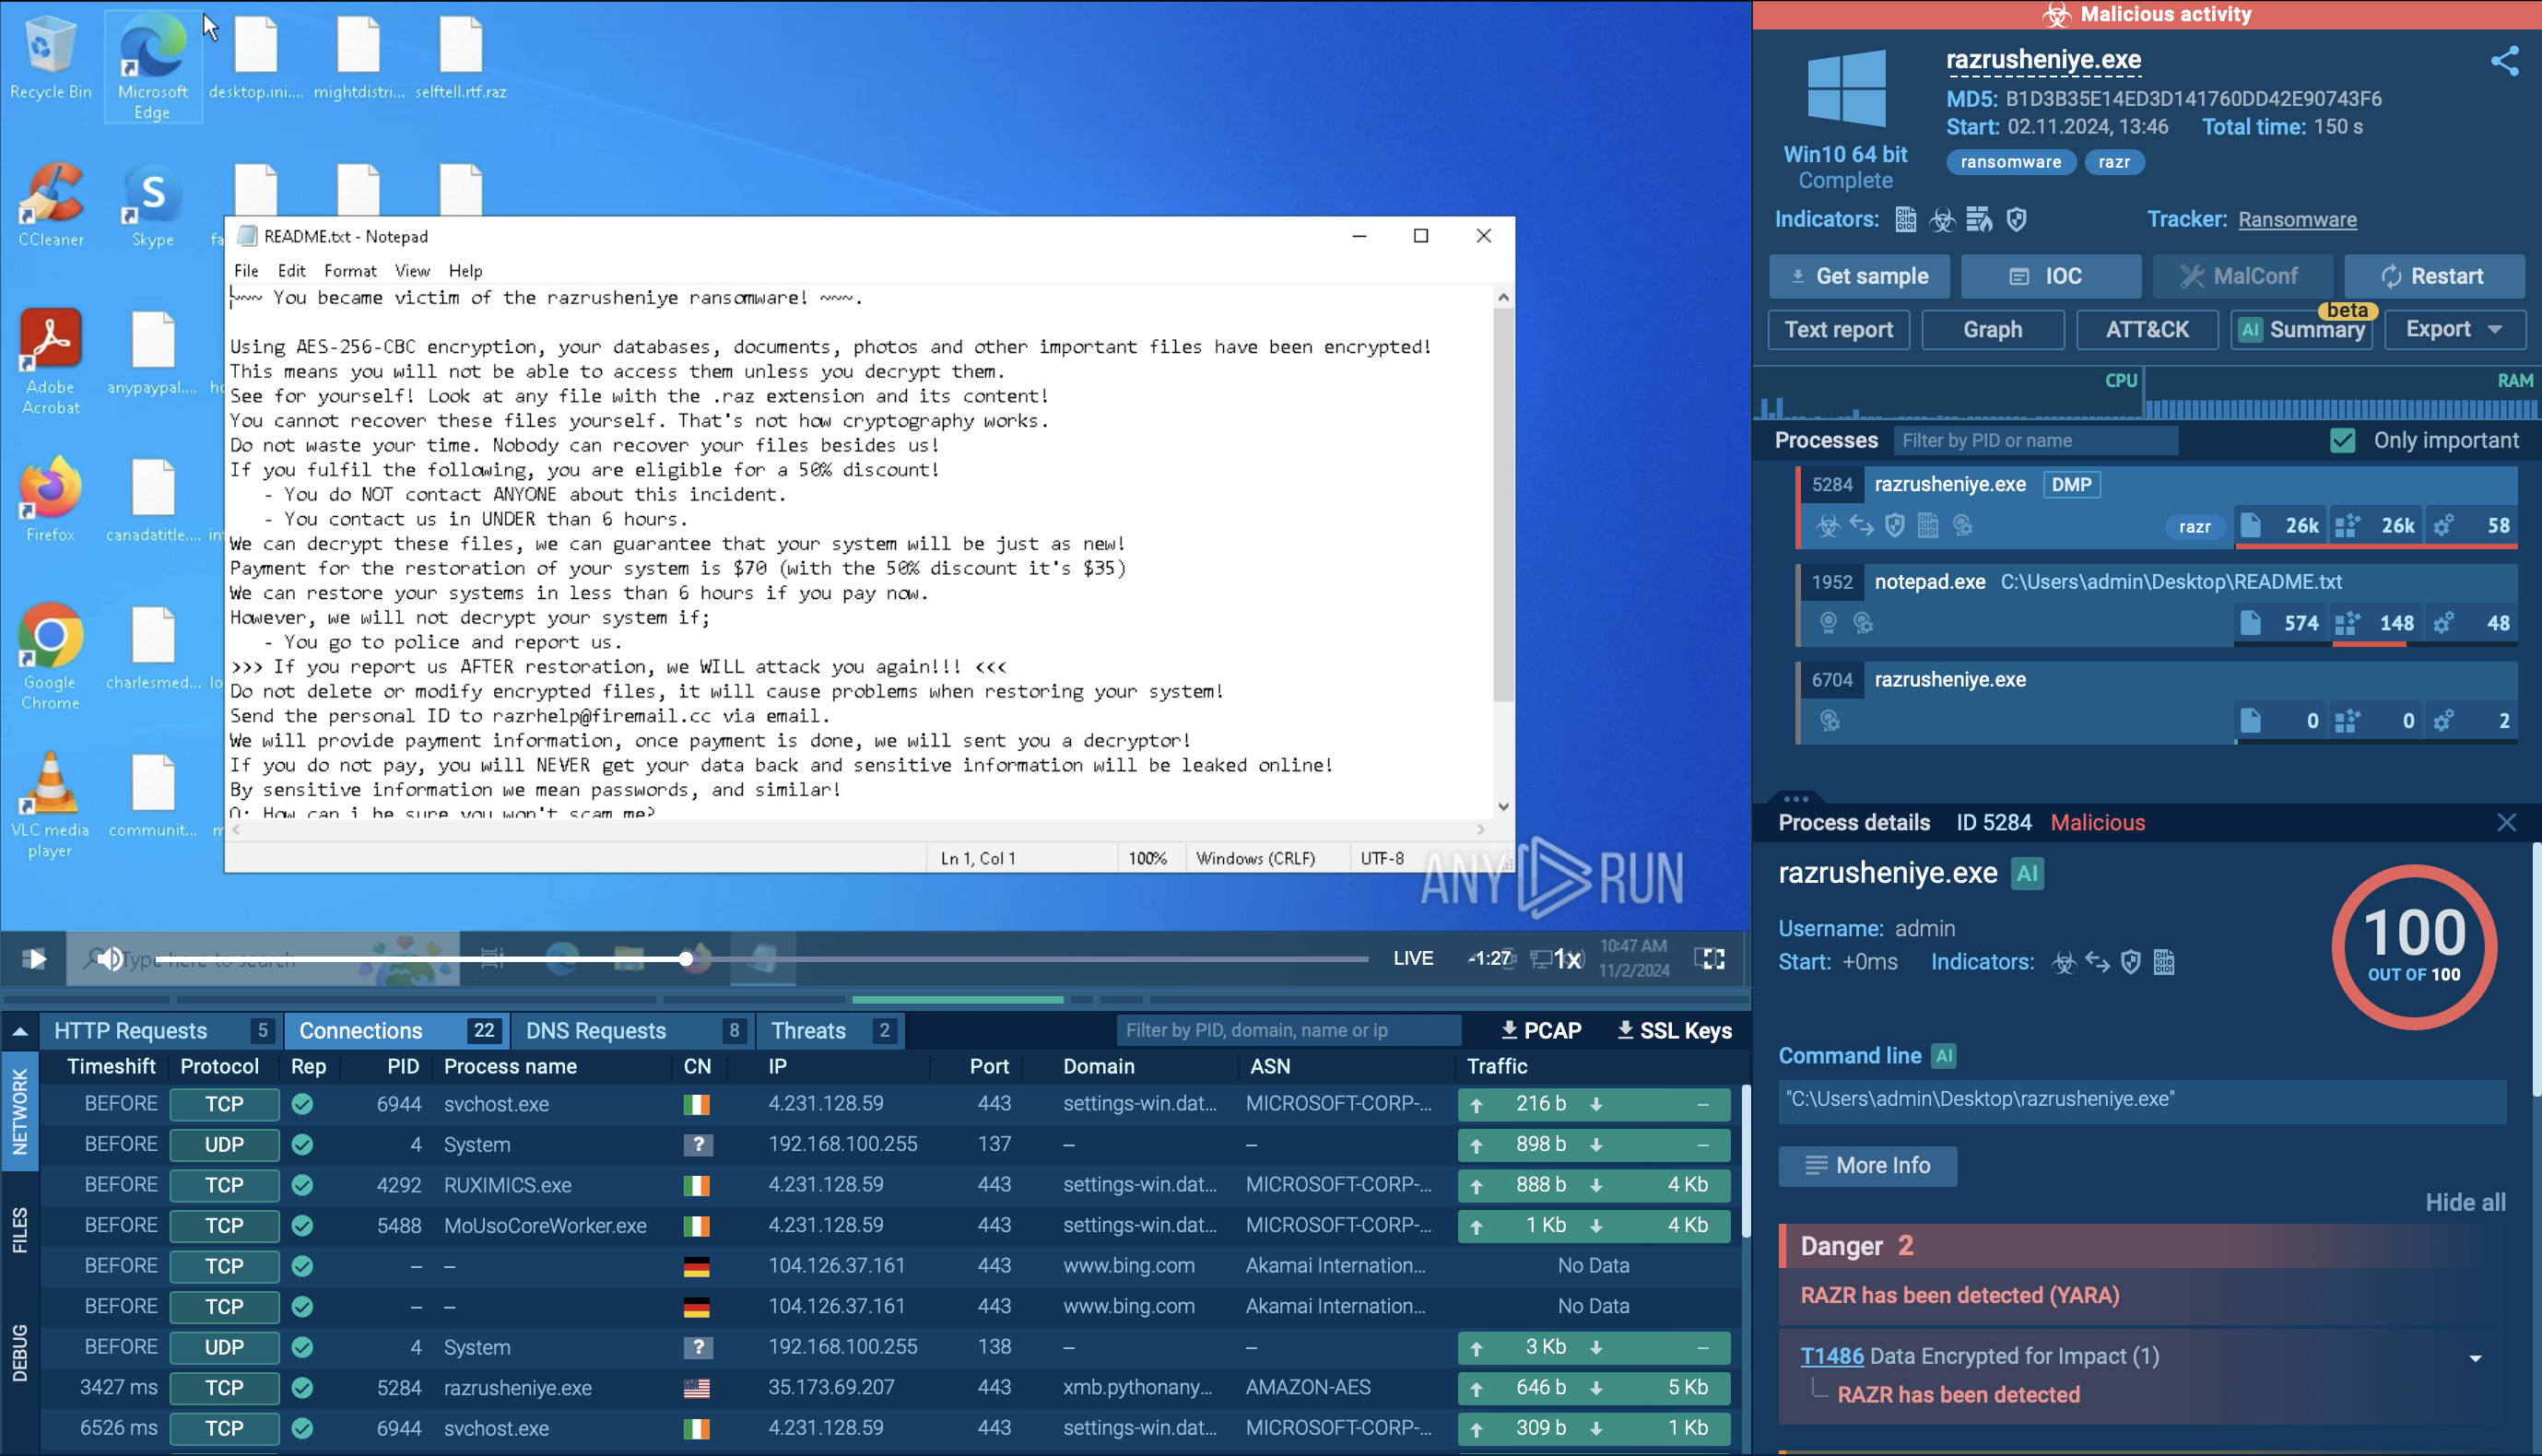
Razr is a destructive ransomware that infiltrates systems to encrypt files, rendering them inaccessible to users. It appends the ".razr" extension to the encrypted files and drops a ransom note, typically named "README.txt," instructing victims on how to pay the ransom to obtain the decryption key. The malware often spreads through phishing emails with malicious attachments or by exploiting vulnerabilities in software and operating systems. Razr employs strong encryption algorithms, making it challenging to decrypt files without the attackers' key.
Read More
RondoDox screenshot
RondoDox
rondodox
RondoDox is an emerging Linux-based botnet malware that exploits dozens of known vulnerabilities in internet-facing devices like routers, DVRs, and web servers to build massive networks for DDoS attacks, cryptomining, and data exfiltration. First spotted in mid-2025, its "exploit shotgun" tactic (firing multiple payloads at once) has made it a rapid escalator in the IoT threat landscape, compromising unpatched edge devices worldwide.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More
WannaCry screenshot
WannaCry
wannacry ransomware
WannaCry is a famous Ransomware that utilizes the EternalBlue exploit. This malware is known for infecting at least 200,000 computers worldwide and it continues to be an active and dangerous threat.
Read More