Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

GuLoader

35
Global rank
40 infographic chevron month
Month rank
50 infographic chevron week
Week rank

GuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.

Downloader
Type
Italy
Origin
1 December, 2019
First seen
5 October, 2026
Last seen
Also known as
CloudEyE
vbdropper

How to analyze GuLoader with ANY.RUN

Downloader
Type
Italy
Origin
1 December, 2019
First seen
5 October, 2026
Last seen

IOCs

IP addresses
48.209.138.168
206.123.152.67
48.209.133.15
23.59.18.102
128.24.231.65
172.211.123.249
2.23.246.9
2.20.142.50
40.126.31.130
91.216.156.118
2.20.142.49
135.232.92.137
40.126.53.8
66.116.237.52
172.211.123.250
117.120.10.191
2.21.239.138
135.233.95.135
2.16.164.89
217.147.232.232
Hashes
28e27e389359e5f5eefbd75f0b02520f5ceab2a679db412363c7ec58179e18c9
44a65c70eda32d6ff9562359a4e5a278c3e3905fed4f9c06d8e74e42348592fd
feeb348f80ad0250960d7bb66201e5c2950b38c2fe56fb844cd3b8f73db94c34
9305f9d71bec7e4e5526e437e5345eeed538b6f63cf05eeca43924599508315e
7fc24074043cff9cb2a523e967497175881a86d6ddff8b56ddaf755b94e4050e
60ef363c0c552c684d952e833f6920b9b0fdc74d80568df6cb4efa8e88d53893
636ddf0f55d593fef687b28b96f60521e2cc3508f71be65f9641b7202b7b3c42
9a1b4e8fb16d69690e52748aac601ace68dc9c1186e2d886fa26220cb8486be1
035db4bb1698e67eed83c217b196e342dc8ab8bb6ace3c2960f413a2bfab3158
27f95d26ff132d1b3537fc735db9442122f38b50686615d0a900685274690a0e
8fe4ebb79231ead134e2f1f1c38bcdf1a128358efe448045d51ae9902f4a2dc5
222ba4a0c26d1f4181034a3fe6f83d3665ca857a0637b586216eeea959202504
1c55b4d57abc6dd034147ecc004fed8e1cf5a1daabaa3fc27de58a494a4f01c9
cfd610d599bc56cfd8b8a850549ab62aa11694de82e5a9f8ce5ca2b1ef79c5b8
0220ed0d05ab594030789dab3614edb67411b05201e322949676ed9e860e0adc
32a4d142a57341c42218e0709ed38578c983eae5c521651954212e4af4bf743e
4f698ff38b5fbb83b2be3e24a4ec2619f1b83233ace2c0c5bdc08e2839d0936a
fb2ab5e42cf67dc8b4f68f5eeed4053ca4ec5063ccd85efe8a2d5950fc50b004
d5bd529881c3af0cfac853d0bd0cb7d8529c968cb4b46a44e65f2f2673467e11
cdf2094b933b353a90e4270b2713d8cc7148207c4c01c8a8ab91d2349991c86d
Domains
crl.microsoft.com
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
login.live.com
self.events.data.microsoft.com
th.bing.com
google.com
daroughgan8hajous30.duckdns.org
do.optioway.com
daroughgan8hajous20.duckdns.org
settings-win.data.microsoft.com
ecs.office.com
www.microsoft.com
daroughgan8hajous50.duckdns.org
nexusrules.officeapps.live.com
www.bing.com
activation-v2.sls.microsoft.com
go.microsoft.com
daroughgan8hajous40.duckdns.org
slscr.update.microsoft.com
URLs
https://do.optioway.com/dysoxidizable.u32
https://fitman.ro/emlrbtqudstbcwkebrjm172.bin
https://oz-courses.com/emlrbtqudstbcwkebrjm172.bin
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f5%2f2026%2c%207%3a32%3a21%20am
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://login.live.com/rst2.srf
https://www.bing.com/th?id=odswg.4fccac27-392c-4926-b734-be106ec284a3&pid=dsb
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://www.bing.com/th?id=odswg.46916458-4eb1-44b5-bf72-ff1f5697eec2&pid=dsb
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
https://login.live.com/ppsecure/deviceaddcredential.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/ping
Last Seen at
Last Seen at

Recent blog posts

post image
Threat Coverage Digest: New Malware Reports a...
watchers 6945
comments 0
post image
Phishing Response Protocol: 3 Essential SOC S...
watchers 9046
comments 0
post image
Major Cyber Attacks in September 2026: US and...
watchers 13157
comments 0

What is GuLoader malware

Just like the name suggests, GuLoader (sometimes also called CloudEyE and vbdropper) is a first-stage trojan designed to infect a system and drop a final payload. Typically other trojans or RATs. Once the malware makes its way into the victim's system, it attempts to establish a remote connection and download a malicious executable.

This malware is infamous for using advanced anti-detection and obfuscation techniques. It evades network detection, stops executing in virtual environments, and can slip past automatics security systems.

Researchers first observed GuLoader in December 2019, when it was used in a campaign delivering Remcos RAT. Throughout 2020, the trojan kept gaining popularity, at one point accounting for 25% of all packeted samples recorded by Check Point Research. Today, GuLoader remains a highly active threat. It often delivers NanoCore, Agent Tesla, LokiBot, and FormBook.

General description of GuLoader downloader

GuLoader is written in encrypted shellcode wrapped in a Visual Basic 6 (VB6) executable. Notably, it stores second-stage payloads in cloud drive services. Usually, in Google Drive or Microsoft OneDrive. This way, it can establish a connection and download the executable without raising any red flags. The payload is usually encrypted, allowing it to slip past the cloud host’s security measures.

This loader is infamous for its use of anti-analysis techniques:

  1. The shellcode is heavily obfuscated and mixed with generous amounts of junk code.
  2. It detects sandboxes with EnumWindows by counting the number of application windows on the screen and terminates with an error message.
  3. It tampers with debugging software, causing crashes.
  4. It uses process hollowing to inject malicious code into a benign process and evade detection by an antivirus.
  5. To confuse analysts, its PE header contains only generic GetProcAddress instructions.

Like many downloaders, GuLoader is offered as a service. Prices start at $100 per month. It is distributed in the clearnet by a company with a domain name in the .eu zone. The website markets it under the name CloudEye, claiming that this is a security tool intended for protecting applications against cracking. However, the same site contains links to YouTube tutorials that clearly display how to use the software maliciously. They also show how to abuse cloud drives.

Researchers managed to link GuLoader to an Italian-based hacking group by analyzing emails left as contact details in old forum threads. One of the users behind the loader is known under the alias sonykuccio. He advertised a malware variant as far back as 2011 and offered paid services, claiming that he could make other malicious programs harder to detect. That is why GuLoader uses so many intricate anti-evasion techniques.

How to get more information from GuLoader malware

ANY.RUN helps researchers perform malware analysis of GuLoader and track its execution process in an interactive sandbox.
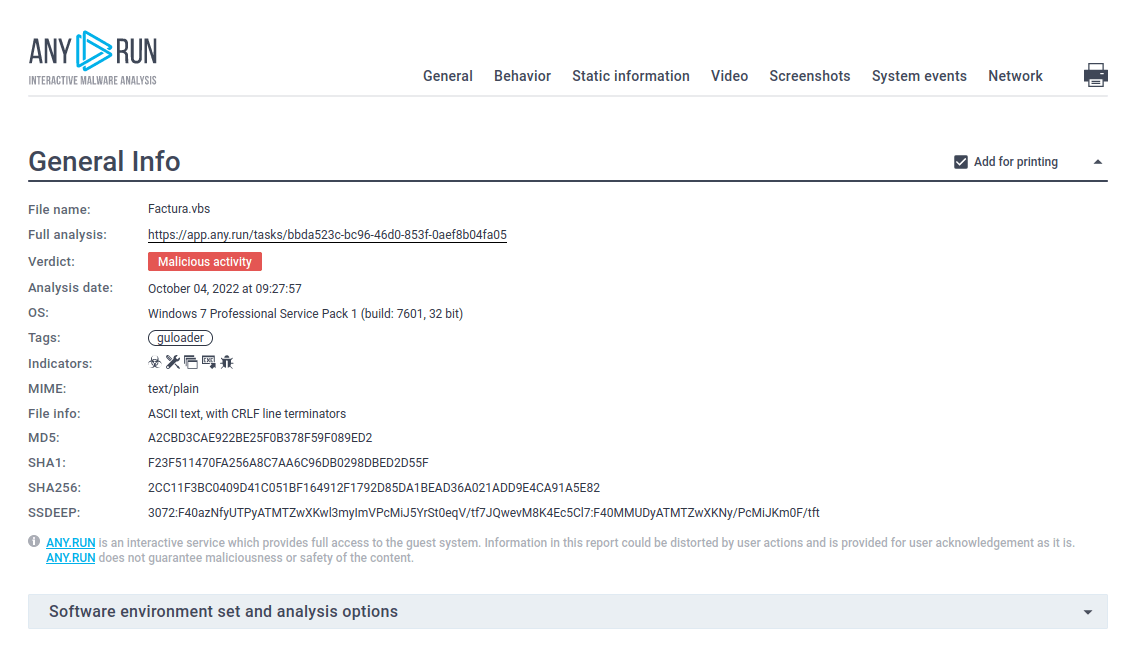
GuLoader text report

Figure 1: GuLoader text report generated by ANY.RUN

ANY.RUN allows users to save time during analysis and present crucial information extracted from malware immediately. Analysts may take a look inside GuLoader malware configuration 10 second after its process started.
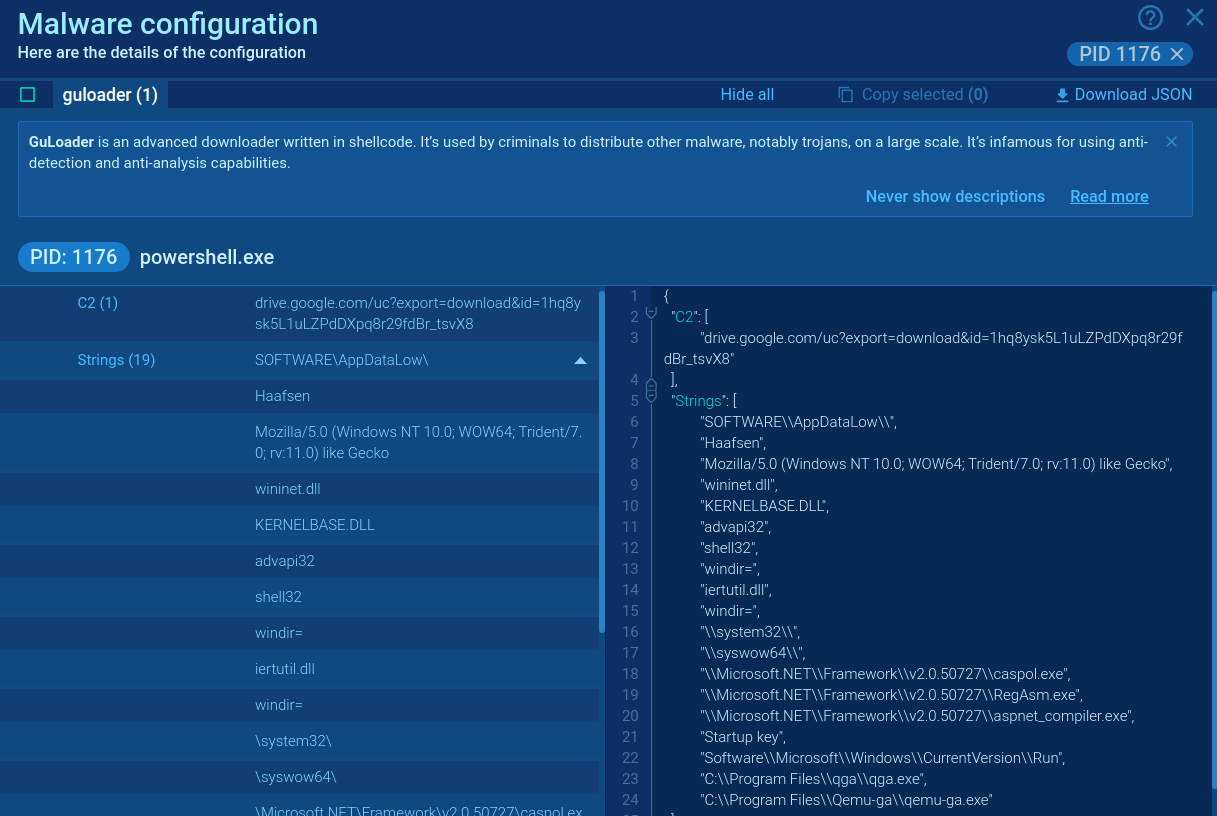
GuLoader malware configuration

Figure 2: GuLoader malware configuration

GuLoader execution process

The distribution method of GuLoader has changed over time, but its execution flow has remained fairly straightforward. The main purpose of GuLoader is to download the primary payload to the infected system. Upon starting, it checks whether it is running inside a virtual environment. If the check passes, it establishes a connection and downloads the payload. Once the payload is downloaded and executed, GuLoader stops.

But even if loader didn't connect to C2 during analysis, you always may look in extracted malware configuration to find out from where GuLoader is wants to receive payload!

Read a detailed analysis of GuLoader in our blog.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Distribution of GuLoader

The distribution method of GuLoader is very typical. The loader is usually delivered as an Office document attachment in spam email campaigns. When downloaded, it uses a macro to install the malicious program. Sometimes it is also delivered as an executable in a .rar archive.

During the pandemic, many campaigns exploited the fear surrounding Covid-19 by mentioning the virus. More recently, attackers have been using fake payment invoices. They will impersonate a bank and use social engineering to trick the victim into downloading an infected file to check “payment details.”

Conclusion

GuLoader is available as a service for a relatively low price, can be easily found in the clearnet, and comes with easy-to-follow instructions. No wonder, then, that creators claim they already have over 5000 clients. Thanks to the combination of advanced anti-evasion tricks and ease of use, we expect its popularity to continue to grow.

Thankfully, GuLoader is easily detectable in ANY.RUN sandbox. It only takes a few minutes to launch an interactive emulation and identify the threat.
HAVE A LOOK AT

Phorpiex screenshot
Phorpiex
phorpiex
Phorpiex is a malicious software that has been a significant threat in the cybersecurity landscape since 2016. It is a modular malware known for its ability to maintain an extensive botnet. Unlike other botnets, Phorpiex does not concentrate on DDoS attacks. Instead, it has been involved in numerous large-scale spam email campaigns and the distribution of other malicious payloads, such as LockBit.
Read More
XRed screenshot
XRed
xred
XRed operates as a stealthy backdoor, enabling cybercriminals to gain unauthorized remote access to infected systems. XRed has gained particular notoriety for its distribution through trojanized legitimate software and hardware drivers, making it exceptionally dangerous due to its ability to masquerade as trusted applications.
Read More
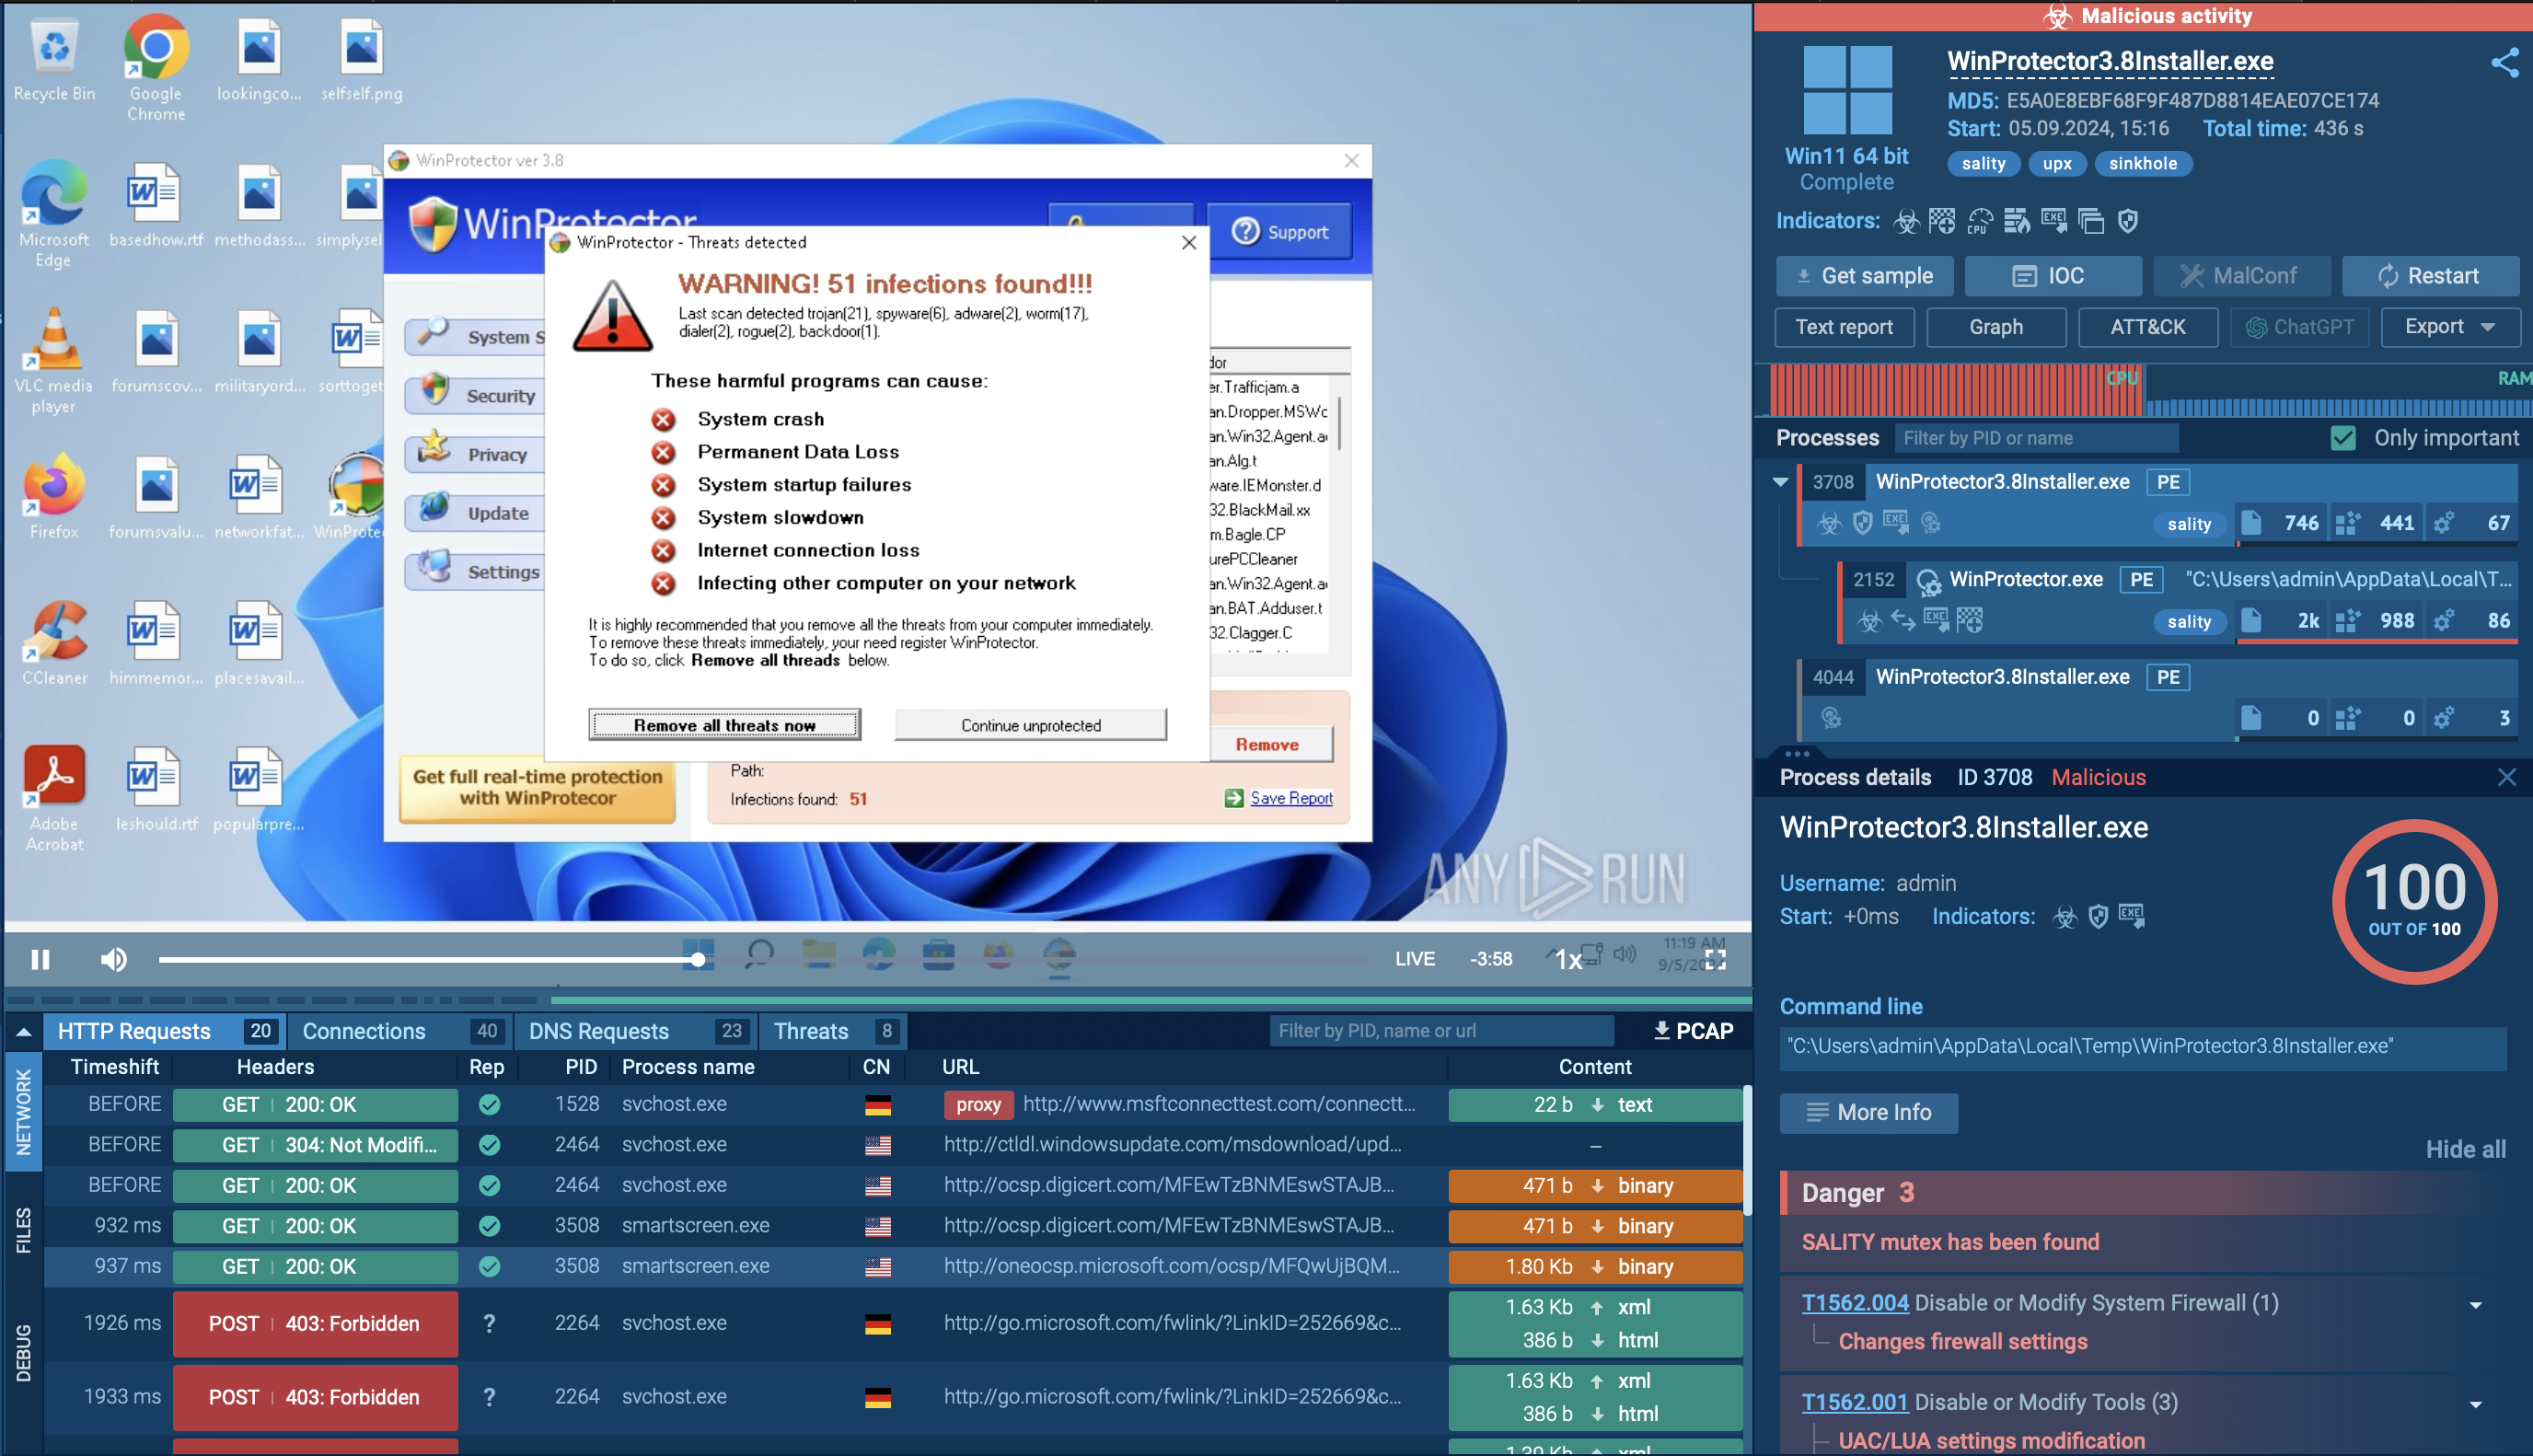
Sality screenshot
Sality
sality
Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.
Read More
Stealc screenshot
Stealc
stealc
Stealc is a stealer malware that targets victims’ sensitive data, which it exfiltrates from browsers, messaging apps, and other software. The malware is equipped with advanced features, including fingerprinting, control panel, evasion mechanisms, string obfuscation, etc. Stealc establishes persistence and communicates with its C2 server through HTTP POST requests.
Read More
EvilProxy screenshot
EvilProxy
evilproxy
EvilProxy is a phishing-as-a-service (PhaaS) platform that enables cybercriminals to bypass multi-factor authentication (MFA) and hijack user sessions. It leverages reverse proxy techniques to harvest credentials and session cookies, posing a serious threat to both individuals and enterprises.
Read More
Diamotrix screenshot
Diamotrix
diamotrix
Diamotrix is a stealthy cryptocurrency clipper malware that silently monitors the Windows clipboard, waiting for the moment a user copies a digital wallet address. Diamotrix replaces it with an attacker-controlled wallet, invisibly redirecting any resulting transaction. Because blockchain transfers are irreversible, victims rarely discover the theft until the funds are long gone.
Read More