Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

ValleyRAT

35
Global rank
30 infographic chevron month
Month rank
29 infographic chevron week
Week rank

ValleyRAT is a classic remote access trojan first documented in 2023, targeting mainly Windows systems. It is used by threat actors to gain persistent access to infected devices, steal data, and control compromised machines. ValleyRAT is notable for its relatively advanced evasion techniques and its connections to a prominent Chinese APT group.

RAT
Type
China
Origin
1 March, 2023
First seen
8 October, 2026
Last seen

How to analyze ValleyRAT with ANY.RUN

RAT
Type
China
Origin
1 March, 2023
First seen
8 October, 2026
Last seen

IOCs

IP addresses
2.23.246.9
142.251.127.132
104.18.19.203
150.171.109.98
23.194.190.139
2.16.204.135
52.123.128.14
48.209.133.15
156.247.40.74
13.107.246.44
23.59.18.102
172.211.123.248
2.16.204.153
184.30.220.140
150.171.22.17
199.232.214.172
150.171.109.99
20.190.159.129
48.192.1.64
135.232.92.97
Hashes
93fa329ba9ef75af1d19df29a2b933bc1eb83336703bbdd3cbc60946a9f668b9
2de8631b2a69ae54c962af917bb57a9ae06949e606da5088f256b866df8cdaba
95e9db2278364c40d924d624dc9865105d277c22ddee7b3f459b069338b8c56a
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
6a5cb307510ec859954146b9b86e3884fa5b108ee3701a21427d0efc883352b9
488a401645c6030b741d7e912aa55ad9ec6b219d36a3247332454c0de867b827
5dd9f78a898b6d956c245d82a1323d513411fa525edca0c6a30c2c5cff59794e
1be16fe0f1efb26b6da07fbeeb5f887df27433f353dfe7d2cfc3e052e4fcb0bd
49c1ce155440eaca41795e5308e625dd5e8f36ad71e5a2e9b3898b625b6022d8
0dfa017a86a8dd9c7b2f8a07af89f6e5a2dbacea8e0d2699b6176e055a8a1a15
5f03cf363d0cc6ea858035722c9ff5ad7290c72695eeb481d01492140011516a
77d9cddcdf03f2e1f02c73df3e6be331435fa58878d9f0e8835b858a1c4cd67a
66e889df958e14400e9be5874c02213de1e81003019103a7b12175e1d22474f8
3e4719c4eece8d4365a95aeef4f71526731435452a797144ec55cd98f50b0434
81ca6f630139d7bfc3efe130e031ab1114a699e57be34bd64a1930528800bd92
438a487d96c184aafaf90bf796dfb7b551fbaec22e8b9ef432eb3675b8c814cf
61fea6de5fff201dcdb338add34ffc820f888ab0a60c7b9f3959d55e8fdba0c2
b452ba00f4971736a7eadcf2187b7c008a145e84fb43b046594807625c065640
8a2cedeec7ca8ac2691f024af0f453170e8b6647a9de382a9a82c9ac8ef73025
66f47b2ef0d2b4c0fefecb0374412d59142cdc44d50c35b85bbb90b470b40fa6
Domains
mem.gfx.ms
oneocsp.microsoft.com
self.events.data.microsoft.com
clients2.googleusercontent.com
crl.microsoft.com
metadata.templates.cdn.office.net
ocsp.digicert.com
browser.events.data.microsoft.com
logincdn.msftauth.net
edge-mobile-static.azureedge.net
binaries.templates.cdn.office.net
login.microsoftonline.com
support.microsoft.com
uhf.microsoft.com
aadcdn.msauth.net
acctcdn.msftauth.net
aadcdn.msftauth.net
js.monitor.azure.com
www.bing.com
slscr.update.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
https://officeclient.microsoft.com/config16/?lcid=1033&syslcid=1033&uilcid=1033&build=16.0.16026&crev=3
https://ecs.office.com/config/v2/office/word/16.0.16026.20146/production/cc?&clientid=%7bd61ab268-c26a-439d-bb15-2a0dedfca6a3%7d&application=word&platform=win32&version=16.0.16026.20146&msoversion=16.0.16026.20002&sdx=fa000000002.2.0.1907.31003&sdx=fa000000005.1.0.1909.30011&sdx=fa000000006.1.0.1909.13002&sdx=fa000000008.1.0.1908.16006&sdx=fa000000009.1.0.1908.6002&sdx=fa000000016.1.0.1810.13001&sdx=fa000000029.1.0.1906.25001&sdx=fa000000033.1.0.1908.24001&sdx=wa104381125.1.0.1810.9001&processname=winword.exe&audience=production&build=ship&architecture=x64&language=en-us&subscriptionlicense=false&perpetuallicense=2019&licensecategory=6&licensesku=professional2019retail&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7bc7014208-3e1f-489d-b280-16d494643eaf%7d&labmachine=false
https://messaging.lifecycle.office.com/getcustommessage16?app=0&ui=en-us&src=bizbar&messagetype=bizbar&hwid=04111-083-043729&ver=16.0.16026&lc=en-us&platform=10%3a0%3a19045%3a2%3a0%3a0%3a256%3a1%3a&productid=%7b1717c1e0-47d3-4899-a6d3-1022db7415e0%7d%3a00411-10830-43729-aa720%3aoffice%2019%2c%20office19professional2019r_retail%20edition&clientsessionid=%7bc7014208-3e1f-489d-b280-16d494643eaf%7d&datapropertybag=%7b%22audience%22%3a%22production%22%2c%22audiencegroup%22%3a%22production%22%2c%22audiencechannel%22%3a%22cc%22%2c%22flight%22%3a%22ofsh6c2b1tla1a31%2cofcrui4yvdulbf31%2cofhpex3jznepoo31%2cofjhlwlmoc1pz531%22%7d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f8%2f2026%2c%2010%3a30%3a02%20am
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.dd482747-0b27-423b-a458-0ac58ffc4b0e&pid=dsb
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:-yvyyqc1trhzlowey-00syldbs5d_tzvb8x4mptiun0&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceasmayxgarewr3pgr9svwmg%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbr0tbevyklx7a9ylold9hqmcwdxfgqu3pggslehmvkx8utfb6ncihnaqhycezmaaaaoqpopjdxrqzsaaaaaaa4%3d
http://crl.microsoft.com/pki/crl/products/miccodsigpca_08-31-2010.crl
http://crl.microsoft.com/pki/crl/products/microsofttimestamppca.crl
http://www.microsoft.com/pkiops/crl/miccodsigpca2011_2011-07-08.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://crl.microsoft.com/pki/crl/products/mictimstapca_2010-07-01.crl
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 1389
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 3845
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 5997
comments 0

What is Valley RAT malware?

ValleyRAT is a C++-based RAT first identified in early 2023. It is associated with the Silver Fox advanced persistent threat (APT) group, a suspected China-based threat actor.

It stands out of the plenty of RATs for its multi-stage infection chain, heavy reliance on shellcode for execution, and a focus on espionage and data theft. It is designed to infiltrate systems, maintain persistence, and provide attackers with extensive remote control. Including the ability to monitor activities, steal data, and deploy additional malicious plugins.

ValleyRAT employs a variety of distribution methods: phishing and spear-phishing emails, compromised websites, social engineering via instant messengers, fake downloads and DLL hijacking. For the initial infection, a loader disguised as a legitimate file is used, which triggers a multi-stage process to deploy the full payload discreetly.

The loader executes shellcode directly in memory thus minimizing its disk footprint and visibility to file-based detection tools.

Once rooted in the system, ValleyRAT provides attackers with its remote control (including keyboard, mouse, screen interaction via WinSta0), allows data exfiltration, file execution, and additional plugin deployment. Screenshot capture, keylogging, and activity monitoring are also performed.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

ValleyRAT Ransomware’s Prominent Features

  • Targeted Espionage: It focuses on high-value roles in finance, accounting, sales, and management, particularly within Chinese enterprises, to steal sensitive corporate data for financial fraud or insider threats.
  • Phased Deployment: (loader → shellcode → C2 → payload) of ValleyRAT is more complex than many single-stage RATs, enhancing stealth.
  • Expanded Attack Surface: By exploiting gaming software and other non-traditional vectors, it broadens its reach beyond typical enterprise targets.
  • Persistent Access: ensures long-term control, enabling prolonged espionage campaigns.
  • Geopolitical Implications: Linked to the Silver Fox APT, ValleyRAT aligns with state-sponsored tactics, suggesting potential use in cyber warfare or intelligence gathering against Chinese-speaking regions.

ValleyRAT Execution Process and Technical Details

The complicated behavior of ValleyRAT is observable in ANY.RUN’s Interactive Sandbox. Let’s explore its processes, IOCs, connections, and other activities.

View sandbox analysis

During the first stages, ValleyRAT may employ techniques such as DLL sideloading and exploiting legitimate signed executables that are vulnerable to DLL search order hijacking. Additionally, process injection is used to inject malicious code into processes like svchost.exe. This allows ValleyRAT to execute its payload, which may include shellcode that decrypts an encrypted PE file in memory for execution without leaving traces on the disk. The payload also includes hooks to bypass security mechanisms like AMSI (Antimalware Scan Interface) and ETW (Event Tracing for Windows).

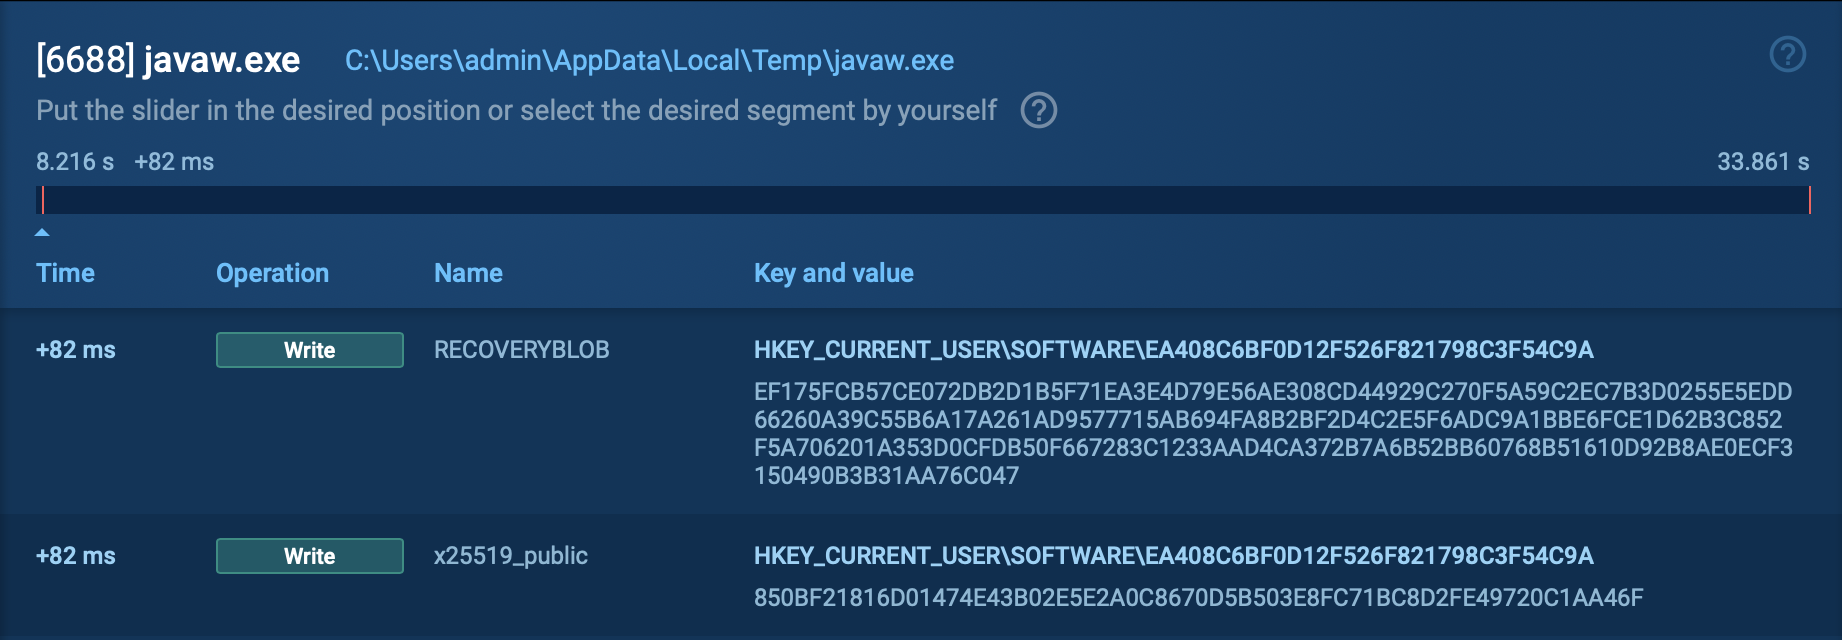
To ensure persistence, ValleyRAT modifies registry settings under Software\Microsoft\Windows\CurrentVersion\Run or, in our analysis, in the startup directory %AppData%\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ by using the Windows Command Shell (CMD). It also stores files in directories such as C:\ProgramData. Once established, ValleyRAT communicates with its Command-and-Control (C2) server using UDP or TCP protocols. The commands supported by ValleyRAT include capturing screenshots, executing files or DLLs, setting startup configurations, filtering processes, and clearing event logs.

To avoid running multiple instances of itself, the malware creates mutexes. In our case, the mutex " V‰°5i™þ«" contains non-standard characters.

It abuses Windows COM interfaces (e.g., CMSTPLUA, fodhelper.exe) to bypass User Account Control (UAC) and gain elevated privileges, often adjusting its security token to SeDebugPrivilege for deeper system access.

ValleyRAT employs multiple stealth mechanisms to evade detection. These include anti-VM checks to detect VMware environments and avoid analysis, as well as keylogging and screen monitoring capabilities to log keystrokes and collect screen data for remote control. Additionally, ValleyRAT injects DLLs into critical processes to prevent security applications from launching. This multi-layered execution chain highlights ValleyRAT’s ability to infiltrate systems stealthily while maintaining persistence and evading detection.
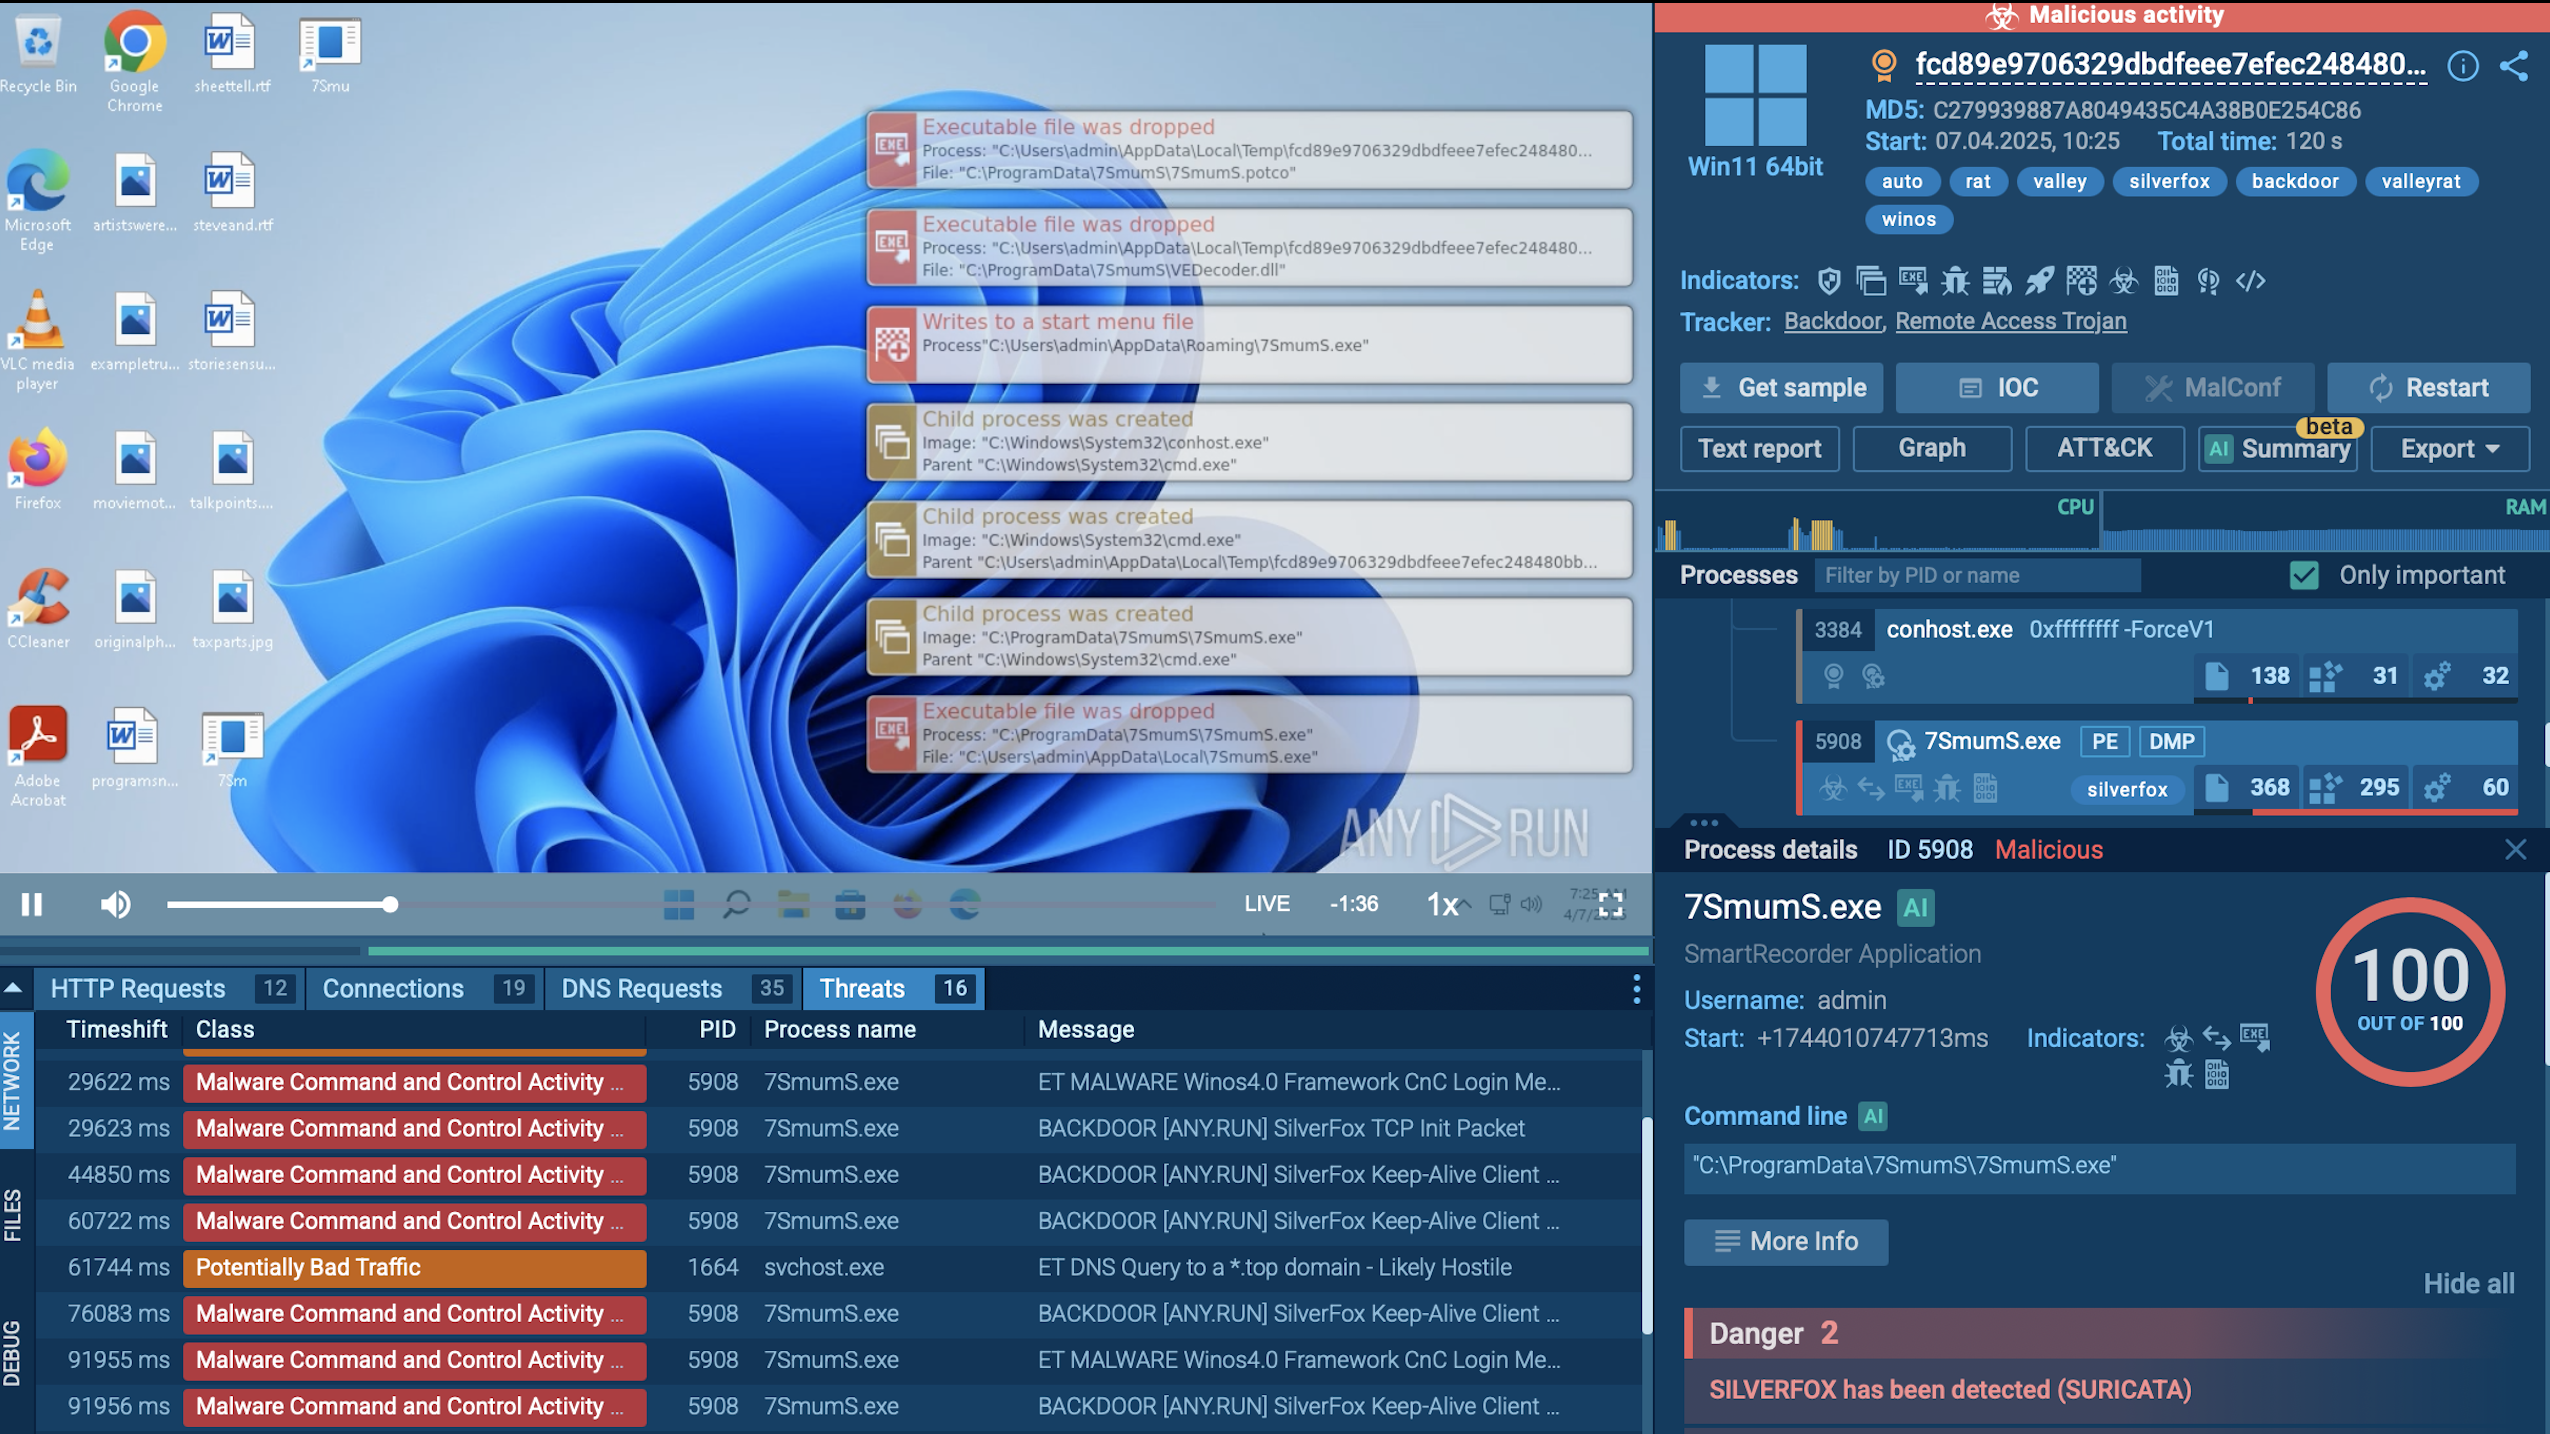
ValleyRAT analysis in ANY.RUN ValleyRAT sample analysis inside ANY.RUN's Interactive Sandbox

Its famous arsenal of evasion tactics includes:

  • Memory-Based Execution: It heavily relies on shellcode executed in memory rather than writing files to disk, reducing its traceable footprint.
  • Process Injection: By injecting malicious code into legitimate processes, it masks its activities within normal system operations.
  • Sleep Obfuscation: It uses sleep routines to alter memory permissions, evading memory scanners and sandbox analysis.
  • Encryption: Shellcode is encrypted (e.g., XOR with keys like 0x27 or AES-256), making it harder for signature-based tools to identify.
  • Anti-VM and Sandbox Checks: It terminates if it detects virtualized environments or common analysis tools (e.g., VMware, WeChat/DingTalk registry checks as a kill switch).
  • Security Tool Disruption: ValleyRAT targets antivirus processes (e.g., Qihoo’s ZhuDongFangYu) for termination and modifies registry settings or Windows Defender exclusions to disable defenses.
  • Legitimate Tool Abuse: It leverages trusted Windows utilities (e.g., MSBuild.exe) and signed executables to blend in with normal activity.

What are the examples of the best-known ValleyRAT attacks?

While specific attacks are not always publicly detailed with victim identities due to the sensitive nature of espionage-driven attacks, cybersecurity researchers have documented key campaigns that highlight ValleyRAT’s success in infiltrating systems, evading detection, and achieving its objectives.

  1. Impersonation of Chinese Telecom Companies (2024): Attackers created fraudulent websites mimicking legitimate Chinese telecom firms to distribute ValleyRAT. It employed DLL hijacking, utilizing legitimate game-related binaries to execute its payload stealthily. Users downloaded malicious software, leading to system compromises.
  2. Targeted Attacks on Chinese-Speaking Enterprises (August 2024): A campaign aimed at Chinese-speaking users of companies in e-commerce, finance, sales, and management sectors.
  3. Resume-Themed PDF Campaign (May 2023): Victims received PDFs mimicking job resumes, which, when opened, directed users to download ValleyRAT via malicious URLs. The RAT was deployed alongside a Rust-based loader, enhancing its stealth and delivery efficiency. This campaign successfully targeted high-value individuals, likely in corporate environments. The use of PDFs broadened its attack surface beyond traditional executable files, catching security systems off-guard.
  4. Trojanized Medical Imaging Software in Healthcare Sector (February 2025): The Silver Fox APT group embedded ValleyRAT within counterfeit versions of Philips DICOM viewer software.
  5. Fake Chrome Download Campaign (February 2025): Victims downloaded a ZIP archive containing “Setup.exe,” which sideloaded malicious DLLs (e.g., “tier0.dll” from Valve games, “sscronet.dll”) via legitimate executables like Douyin.exe. ValleyRAT then logged keystrokes, monitored screens, and established C2 communication, using Donut shellcode for in-memory execution.

The latter campaign’s reuse of URLs, gaming software exploitation, and focus on key organizational roles demonstrated Silver Fox’s strategic shift toward both wider and more precise targeting, cementing ValleyRAT’s reputation as a versatile RAT.

Gathering threat intelligence on ValleyRAT malware

It would be a painful challenge to scrape ValleyRAT out of your system considering its persistence and evasion “talents”. And, of course, losses calculation and mitigation would be even more painful. So, it’s much better not to invite the digital culprit in.

Use threat intelligence to study and recognize ValleyRAT TTPs, and to gather IOCs, IOAs, and IOBs for tuning your monitoring and detection systems. You can also leverage ANY.RUN’s TI Feeds to be updated with the new ValleyRAT’s identificators automatically.

ValleyRAT has a habit of reusing the same URLs or IP addresses across campaigns, and besides, it often employs unique mutexes. Address ANY.RUN’s Threat Intelligence Lookup and start your research with malware’s name:
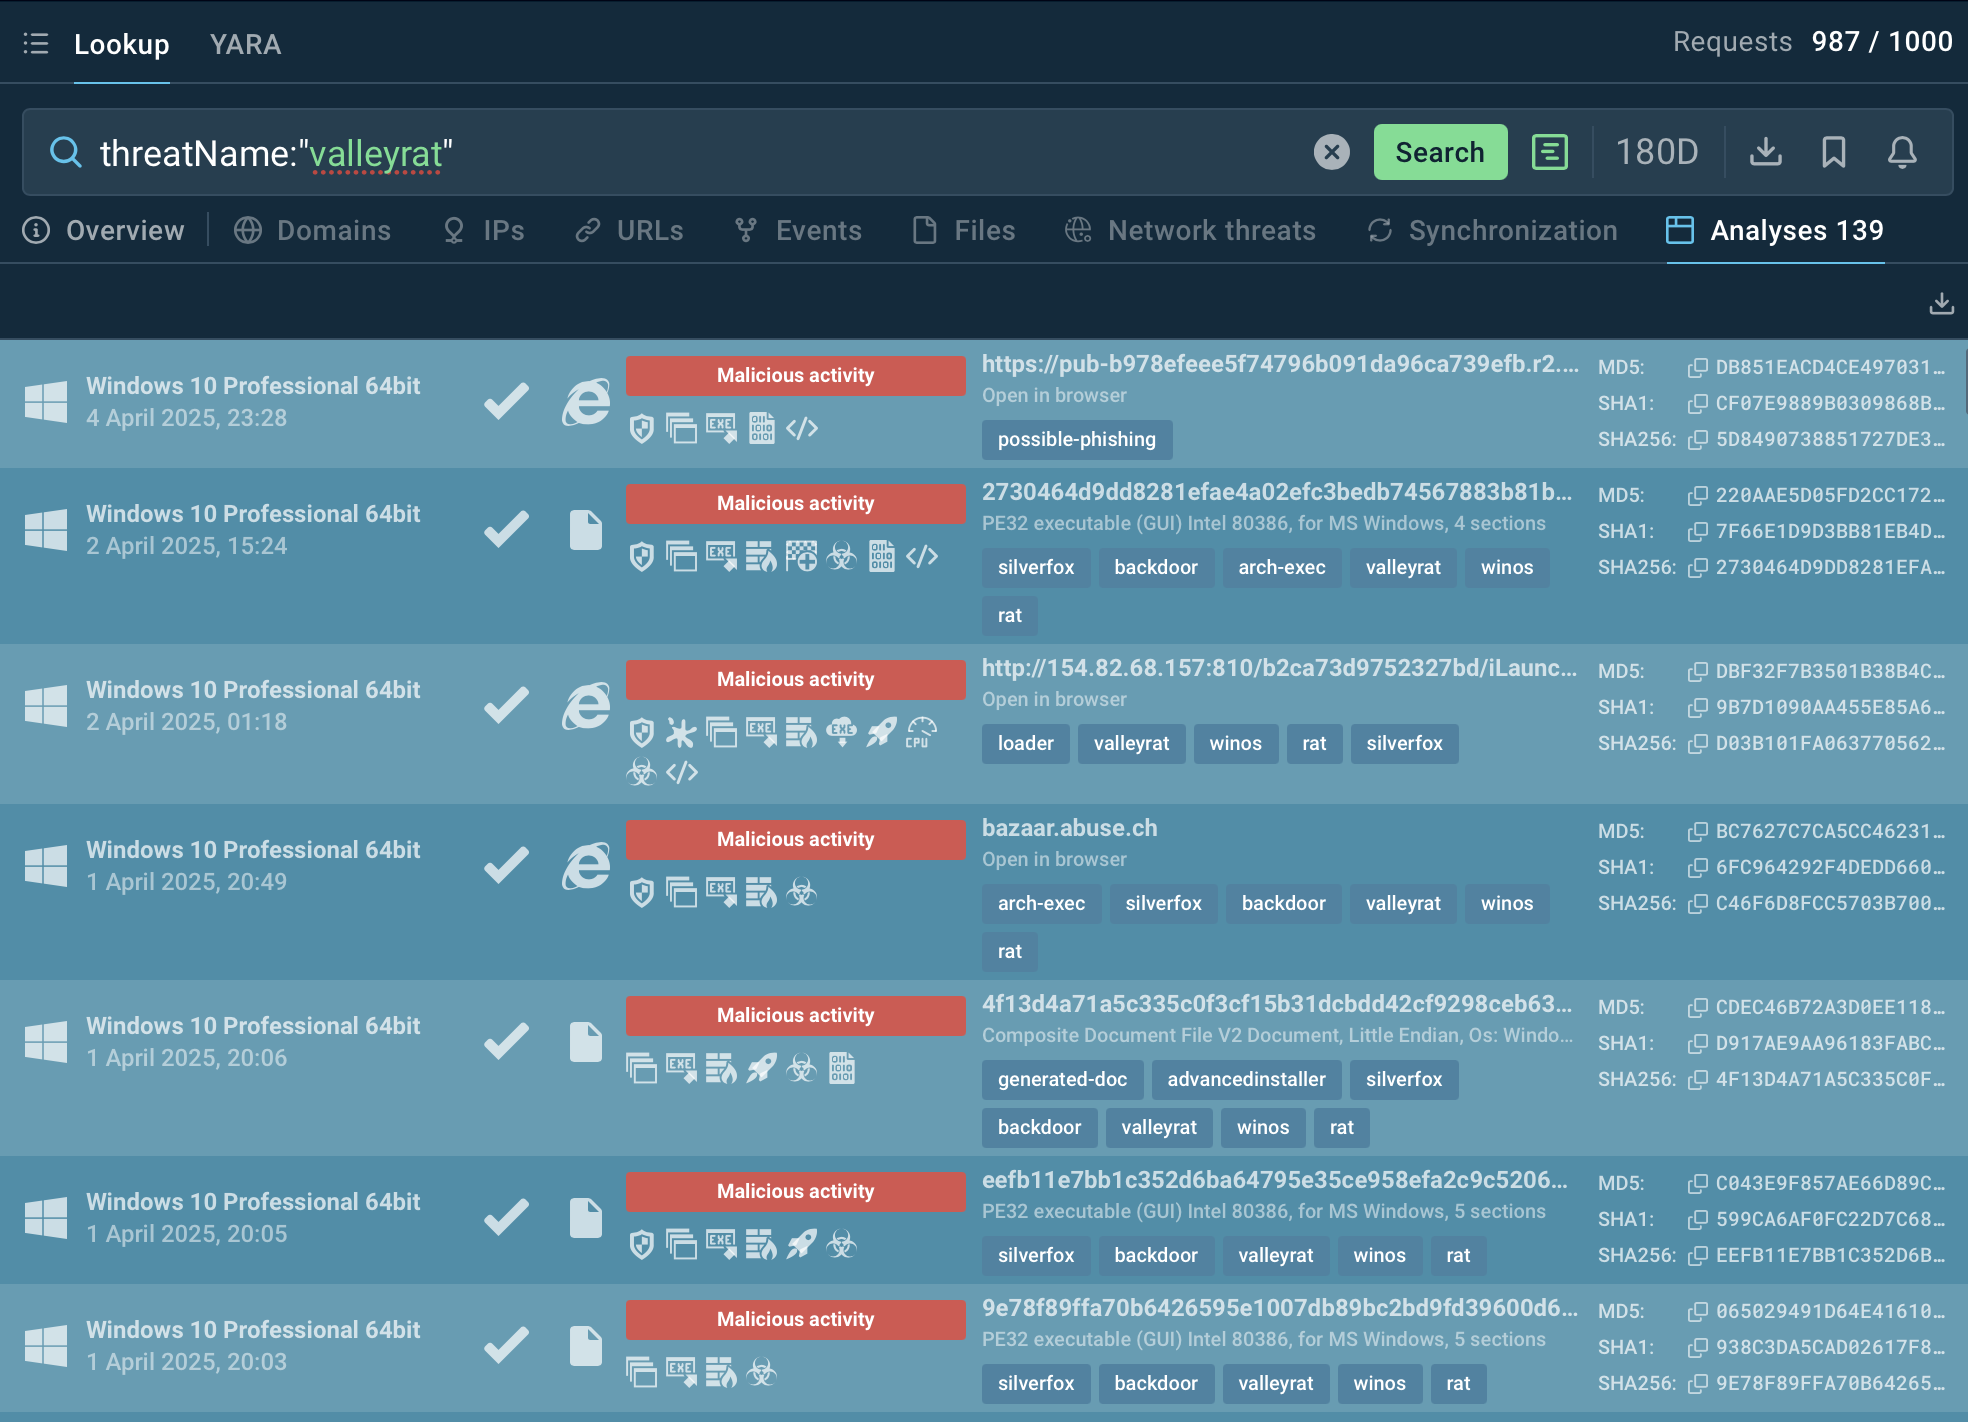
threatName:"valleyrat"

ValleyRAT search results in TI Lookup _ ValleyRAT samples in ANY.RUN’s Sandbox_

ValleyRAT often leaves byte patterns that can be matched by custom or shared YARA rules. Suricata rules are also of much help in detecting the trojan’s malicious processes. This is what the detalization of such process looks like in TI Lookup:
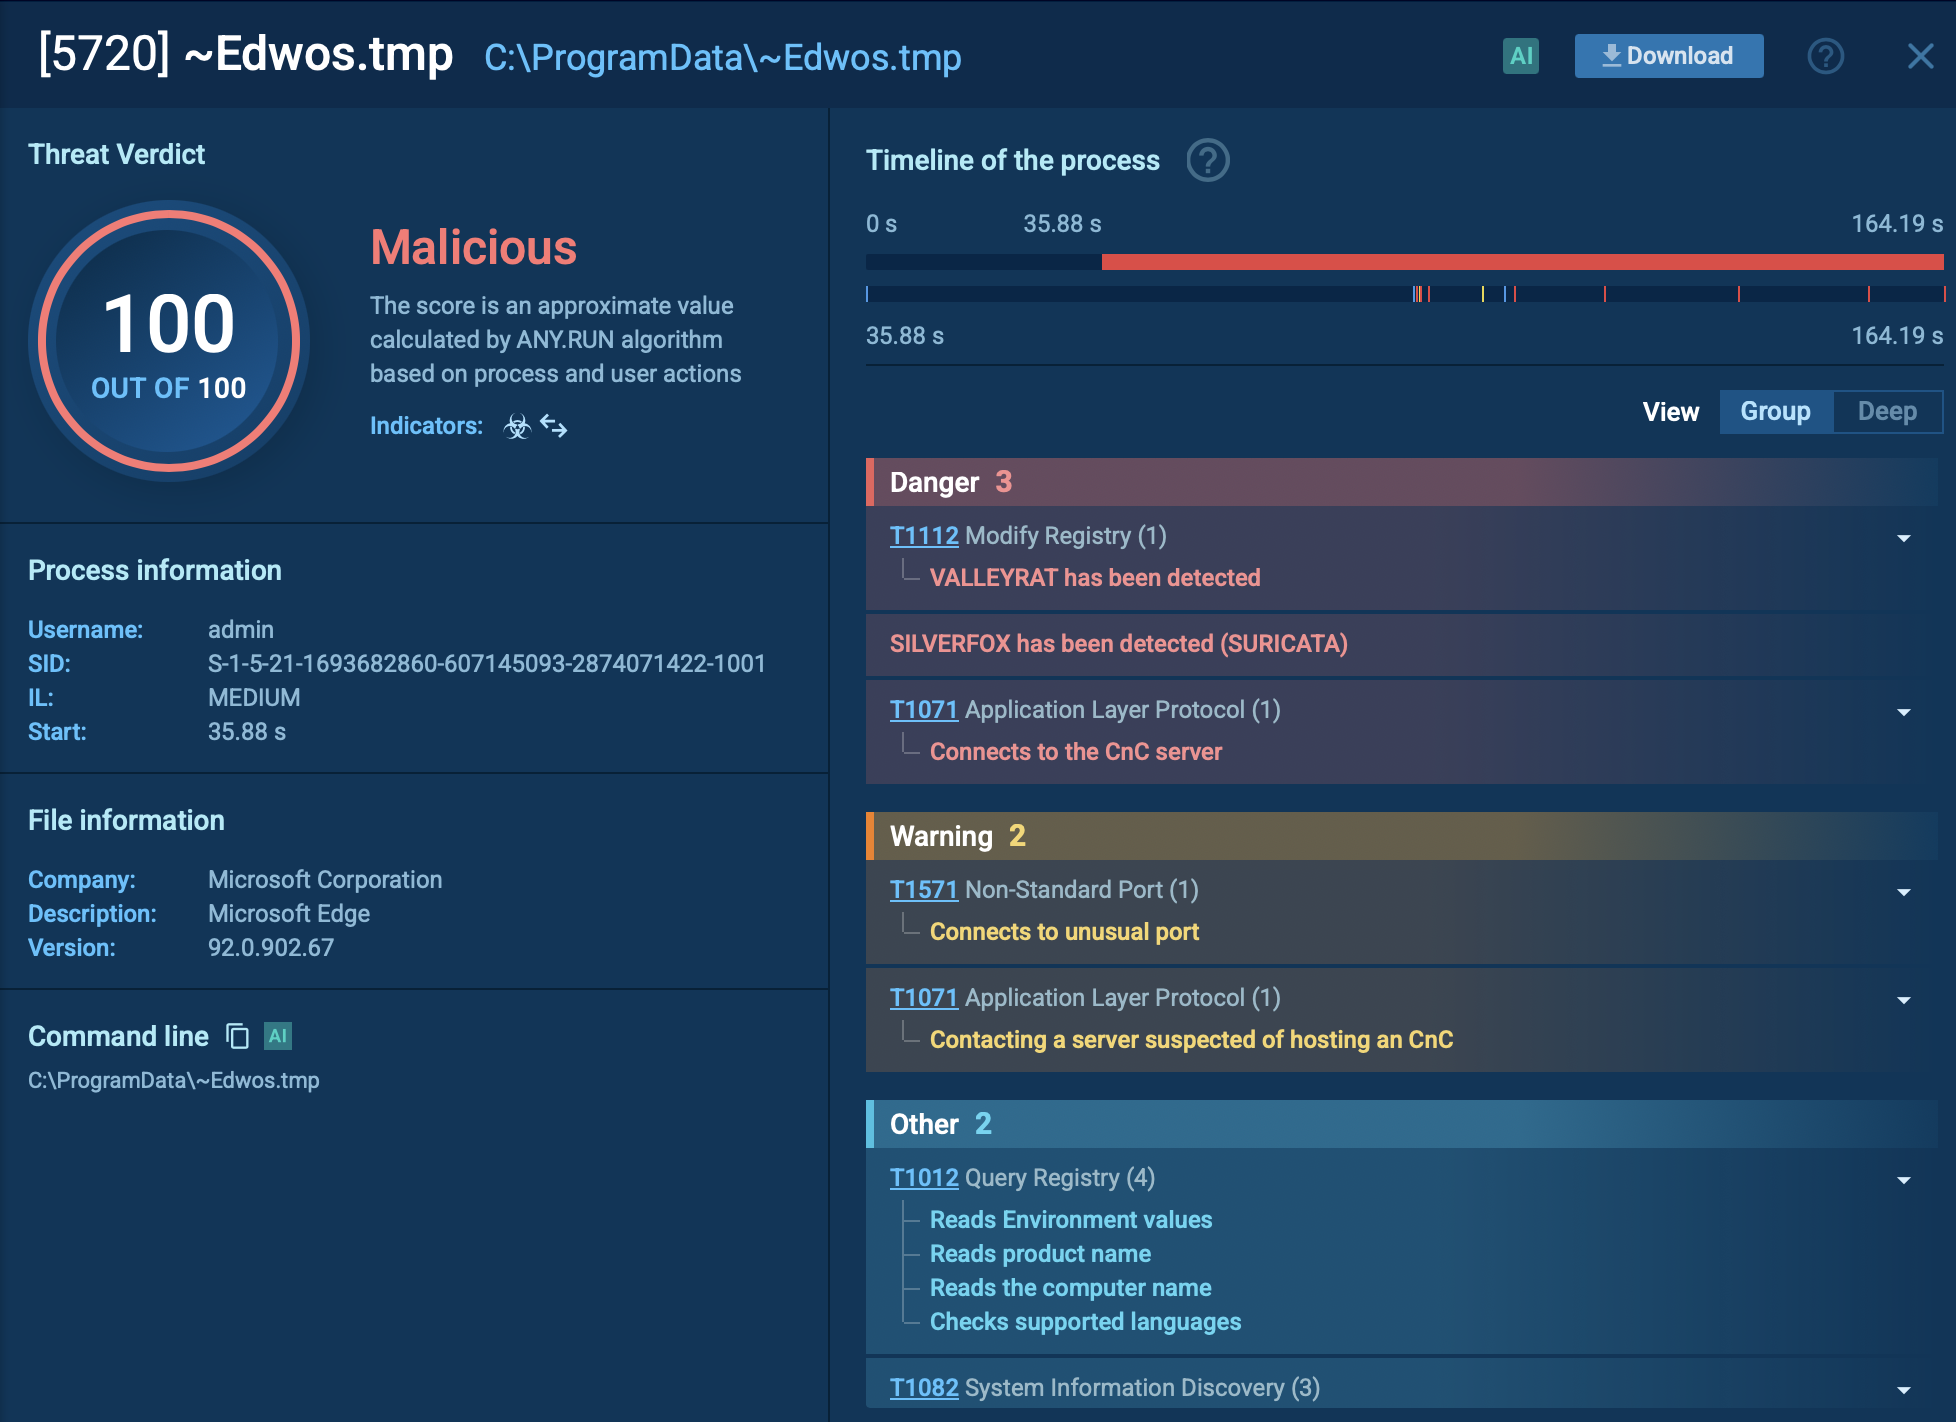
ValleyRAT process detailed Details on ValleyRAT actions in the system

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

ValleyRAT is an example of modern malware evolution, blending traditional RAT functionality with advanced evasion and persistence tactics. Its danger lies in its ability to quietly infiltrate networks, target valuable data, and maintain long-term access. Countering it demands a blend of cutting-edge detection tools, robust threat intelligence, and proactive security measures to stay ahead of its cunning Silver Fox operators.

Though it did start as a threat for Chinese enterprise and users, now, if you are on the opposite side of the world from China, you are not safe. APTs’ appetites always grow, so be ready and proactive against ValleyRAT.

Gather IOCs on ValleyRAT with 50 trial requests in TI Lookup
HAVE A LOOK AT

GREENBLOOD screenshot
GREENBLOOD
greenblood
GREENBLOOD is a Go-based ransomware that uses concurrent ChaCha8 encryption to lock entire Windows environments in under a minute while systematically destroying backups, disabling defenses, and threatening double extortion through a Tor-based data leak site.
Read More
Tykit screenshot
Tykit
tykit
Tykit is a sophisticated phishing-as-a-service (PhaaS) kit that emerged in May 2025, designed to steal Microsoft 365 corporate credentials through an innovative attack vector: malicious SVG files.
Read More
Akira Ransomware screenshot
Akira Ransomware emerged in March 2023 and compromised over 250 organizations by January 2024 with approximately $42 million in ransom payments. It employs double extortion tactics exfiltrating data before encryption and threatening to publish it on a dedicated website.
Read More
Arechclient2 screenshot
Arechclient2
arechclient2
The Arechclient2 malware is a sophisticated .NET-based Remote Access Trojan (RAT) that collects sensitive information, such as browser credentials, from infected computers. It employs various stealth techniques, including Base64 encoding to obscure its code and the ability to pause activities to evade automated security tools. The malware also can adjust Windows Defender settings and uses code injection to manipulate legitimate processes.
Read More
SVCStealer screenshot
SVCStealer
svcstealer
SVCStealer is an information-stealing malware targeting sensitive user data through spear-phishing email attachments. It systematically extracts credentials, financial data, and system information from various applications, including browsers and messaging platforms.
Read More
Bluesky Ransomware screenshot
BlueSky ransomware, first identified in June 2022, shares code similarities with other well-known ransomware families like Conti and Babuk. It primarily spreads via phishing emails and malicious links and can propagate through networks using SMB protocols. BlueSky uses advanced evasion techniques, such as hiding its processes from debuggers via the NtSetInformationThread API, making it difficult for analysts to detect and mitigate its attacks.
Read More