Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Latrodectus

174
Global rank
178 infographic chevron month
Month rank
158 infographic chevron week
Week rank

Latrodectus is a malicious loader that is used by threat actors to gain a foothold on compromised devices and deploy additional malware. It has been associated with the IcedID trojan and has been used by APT groups in targeted attacks. The malware can gather system information, launch executables, and detect sandbox environments. It uses encryption and obfuscation to evade detection and can establish persistence on the infected device.

Loader
Type
Unknown
Origin
1 August, 2023
First seen
11 August, 2026
Last seen
Also known as
Unidentified 111
BLACKWIDOW
IceNova

How to analyze Latrodectus with ANY.RUN

Type
Unknown
Origin
1 August, 2023
First seen
11 August, 2026
Last seen

IOCs

IP addresses
2.16.204.145
48.209.138.189
48.209.138.168
172.64.154.167
48.192.1.64
2.16.204.135
40.126.32.133
23.52.181.141
172.211.123.250
162.159.36.2
74.178.240.51
74.178.76.128
88.221.92.192
48.192.1.65
88.221.169.205
48.209.6.48
40.126.32.68
2.16.241.218
2.16.241.201
172.211.123.248
Hashes
ec29ce8537e112869dfccb8a57574ebd01eecd7ff5c9fff54fdc1b05ea8941b3
62a2cb5aa12f592f3994d8e7a6483ae549b10df8f7c8064a91e9ccb7a2d53bdb
77bf693b39878fdfe8dae97ae541b54ebe3179ea4a98225713908eb1f49a4158
aec5270b320843870d28012bc62676b219d4e3e815e54081a89bdf6b8ffce3ba
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
cbc8b288dbd2c72432081cf33cef431572a94c7fb89dbcd59973b99e3871814e
cd0dd26304b88c20801fe80b33c49c009e2e5d4411b5d7f83252e1d90cd461c6
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
81ff65efc4487853bdb4625559e69ab44f19e0f5efbd6d5b2af5e3ab267c8e06
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
22bc37b47ce8a832f39701641dc358357676e9be187a93a4c5d4b016e29238ae
cc3e9077fcc9bd0dfc5dd3924c6c48b8345f32cee24fccc508c279f45b2abe61
14895bf43ce9b76c0ff4f9aef93dbe8bb6ca496894870cf0c007b189e0cef00e
7ccc7b17bfe01c3c7dd33eff8f80d0b57fc9b175815e766c9c1c1e893725e20f
Domains
google.com
th.bing.com
www.bing.com
settings-win.data.microsoft.com
activation-v2.sls.microsoft.com
fe3cr.delivery.mp.microsoft.com
slscr.update.microsoft.com
client.wns.windows.com
login.live.com
go.microsoft.com
clients2.googleusercontent.com
assets.constantcontact.com
edge.microsoft.com
copilot.microsoft.com
acroipm2.adobe.com
api.edgeoffer.microsoft.com
9868svhbb.cc.rs6.net
ocsp.digicert.com
www.microsoft.com
oneocsp.microsoft.com
URLs
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://th.bing.com/th?id=odswg.1e1da29b-91ea-4d2e-ac12-df81dfa2c53d&w=124&h=154&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9nm5764dbppg_v9_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=opn.pe_5693e5c6-19d1-4c8a-84cb-85248d6405f9&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=opn.pe_d9408c8e-5724-46a9-b7f1-4bf910a26067&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=osk.d9d02de7c418534587e5be687df727a5&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9plgt00f15xs_abtesting_835b67e1-8ab1-490d-a6ab-e8840fad9bde&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9pltx207s22g_v6_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=opn.pe_1e13b6cc-0ab3-4dd6-acf7-218c8c2be53c&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=osk.f5873d89f968cc2d480b0f930e95ae4f&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9p3610rr8qt5_v3_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9p9rpk71ggql_v3_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9njb654d39wx_v12_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=opn.pe_489223ad-97fa-4373-ad93-7f8a6f97c634&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=odswg.d59d4f41-177b-4727-bfd9-f4f300aa3662&w=124&h=154&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9nbckjw55fsv_v6_main&w=86&h=86&c=1&rs=1&p=0
https://th.bing.com/th?id=opn.pe_73774666-380a-41c6-9f06-23e82f450df0&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=osk.3ba19440475e4b7cfe01e20a1b08771e&w=140&h=96&c=1&rs=1&p=0
https://th.bing.com/th?id=odswg.bc00fe98-00b2-46fc-96fe-f385f609e12f&w=124&h=154&c=1&rs=1&p=0
https://th.bing.com/th?id=ocge.9n7hl5s06zk0_abtesting_d91bec27-6f2b-4b8c-b317-00677b8039c6&w=86&h=86&c=1&rs=1&p=0
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is Latrodectus malware?

Latrodectus is a type of malware known as a "loader," which is designed to download and install additional malicious software onto a compromised computer. It is believed to have been developed by the same individuals or group behind the IcedID trojan, a sophisticated and widespread banking malware.

Since 2023, Latrodectus has been extensively used by a variety of threat actors, including advanced persistent threat (APT) groups such as TA578 and TA577, which was previously observed delivering the Qbot malware, a banking trojan family.

Latrodectus is typically delivered as part of multi-stage attacks, which often begin with a phishing email containing a malicious JavaScript file attachment. However, it has also been known to be dropped by other malware, including the DanaBot trojan.

One of the key features that has allowed security researchers to link Latrodectus to the IcedID authors is the use of a similar command and control (C2) infrastructure. C2 servers are used by malware to communicate with their operators, receive instructions, and exfiltrate data.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Latrodectus malware technical details

The primary functionality of Latrodectus is to receive commands from the attackers and perform them.

Some of the key capabilities of Latrodectus include:

  • Getting a list of filenames of files located on the desktop of the infected machine.
  • Listing all the processes currently running on the device.
  • Gathering and transmitting additional system information about the endpoint, such as the OS version and hardware specs.
  • Launching of executable files to install malware or to perform other malicious actions.
  • Detonating dynamic link library (DLL) files.
  • Using Windows command prompt to execute commands.

A typical Latrodectus infection chain begins with a JavaScript file that is responsible for downloading a malicious .msi file, which then leads to the deployment of the final payload on the system.

The malware implements obfuscation techniques, such as encrypting strings, to make it more difficult for researchers to analyze. It communicates with its command and control (C2) server via HTTPS, with both requests and responses encrypted using RC4 and base64 encoding.

Furthermore, Latrodectus has a built-in sandbox detection mechanism that works by enumerating the number of active processes on the device and checking for the presence of a MAC address.

The malware can establish a scheduled task for persistence, ensuring that it remains active on the infected machine even after a reboot. It also verifies if the computer is already infected with Latrodectus and exits execution if the result is positive.

Latrodectus execution process

Let’s detonate a sample of the Latrodectus malware in the ANY.RUN sandbox to observe its execution chain.

The infiltration process of the Latrodectus malware involves a sequence of steps that ultimately lead to its successful operation on a target system.

Upon launching a JavaScript file, it automatically retrieves an installer MSI. This MSI file implants a Latrodectus Dynamic Link Library (DLL) onto the system, allowing the malware to maintain persistence even after the system is rebooted.
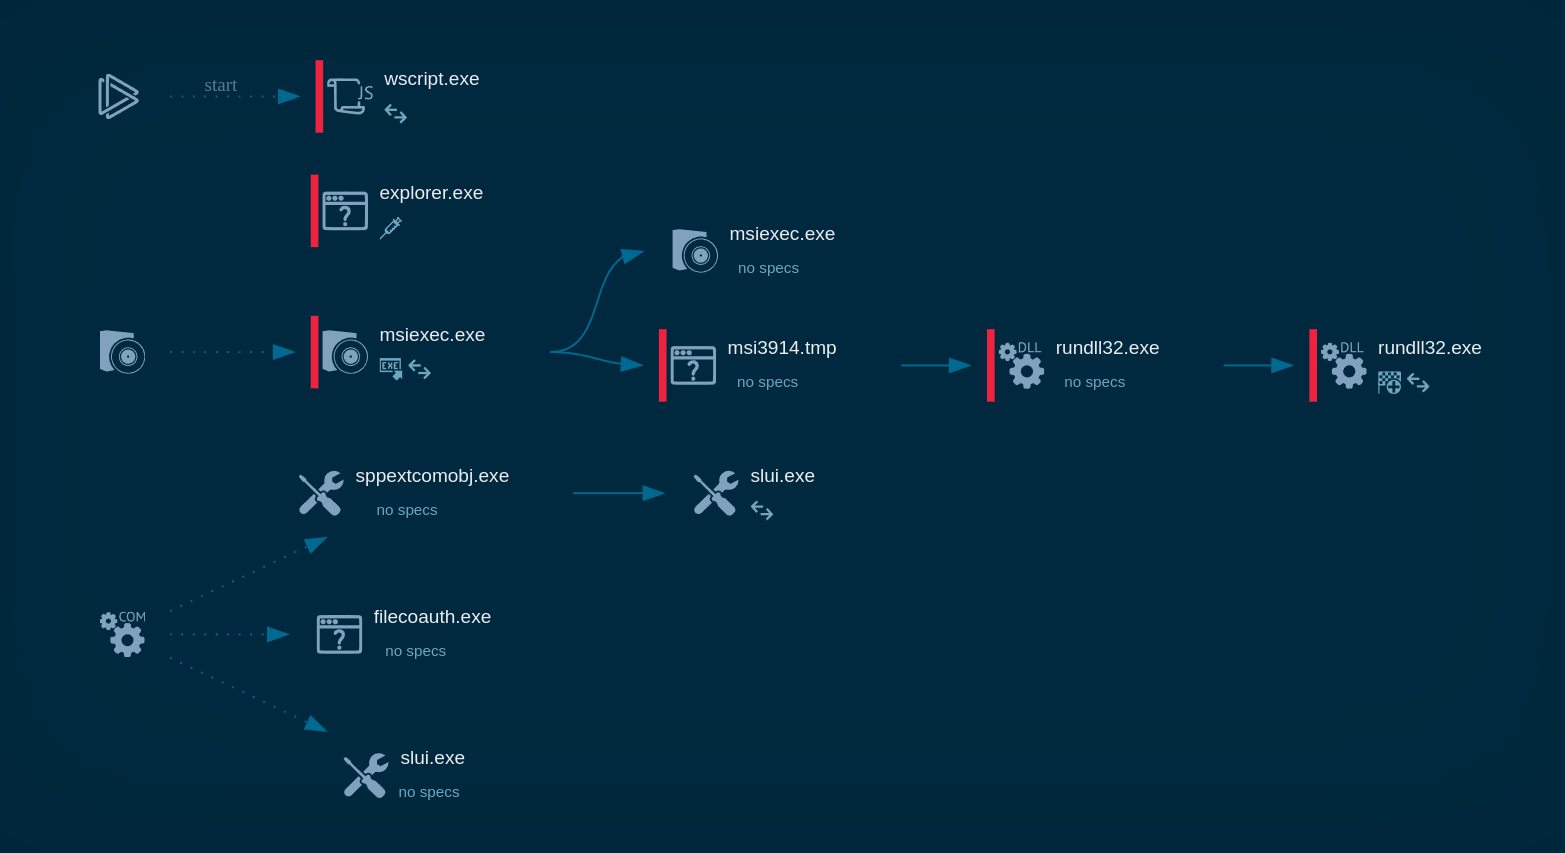
Latrodectus process graph in ANY.RUN Latrodectus process graph in ANY.RUN

Once implanted, the Latrodectus malware establishes communication with its command-and-control (C2) server, providing remote access to the infected device for malicious actors.

Gathering threat intelligence on Latrodectus malware

To collect up-to-date intelligence on Latrodectus, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Latrodectus.
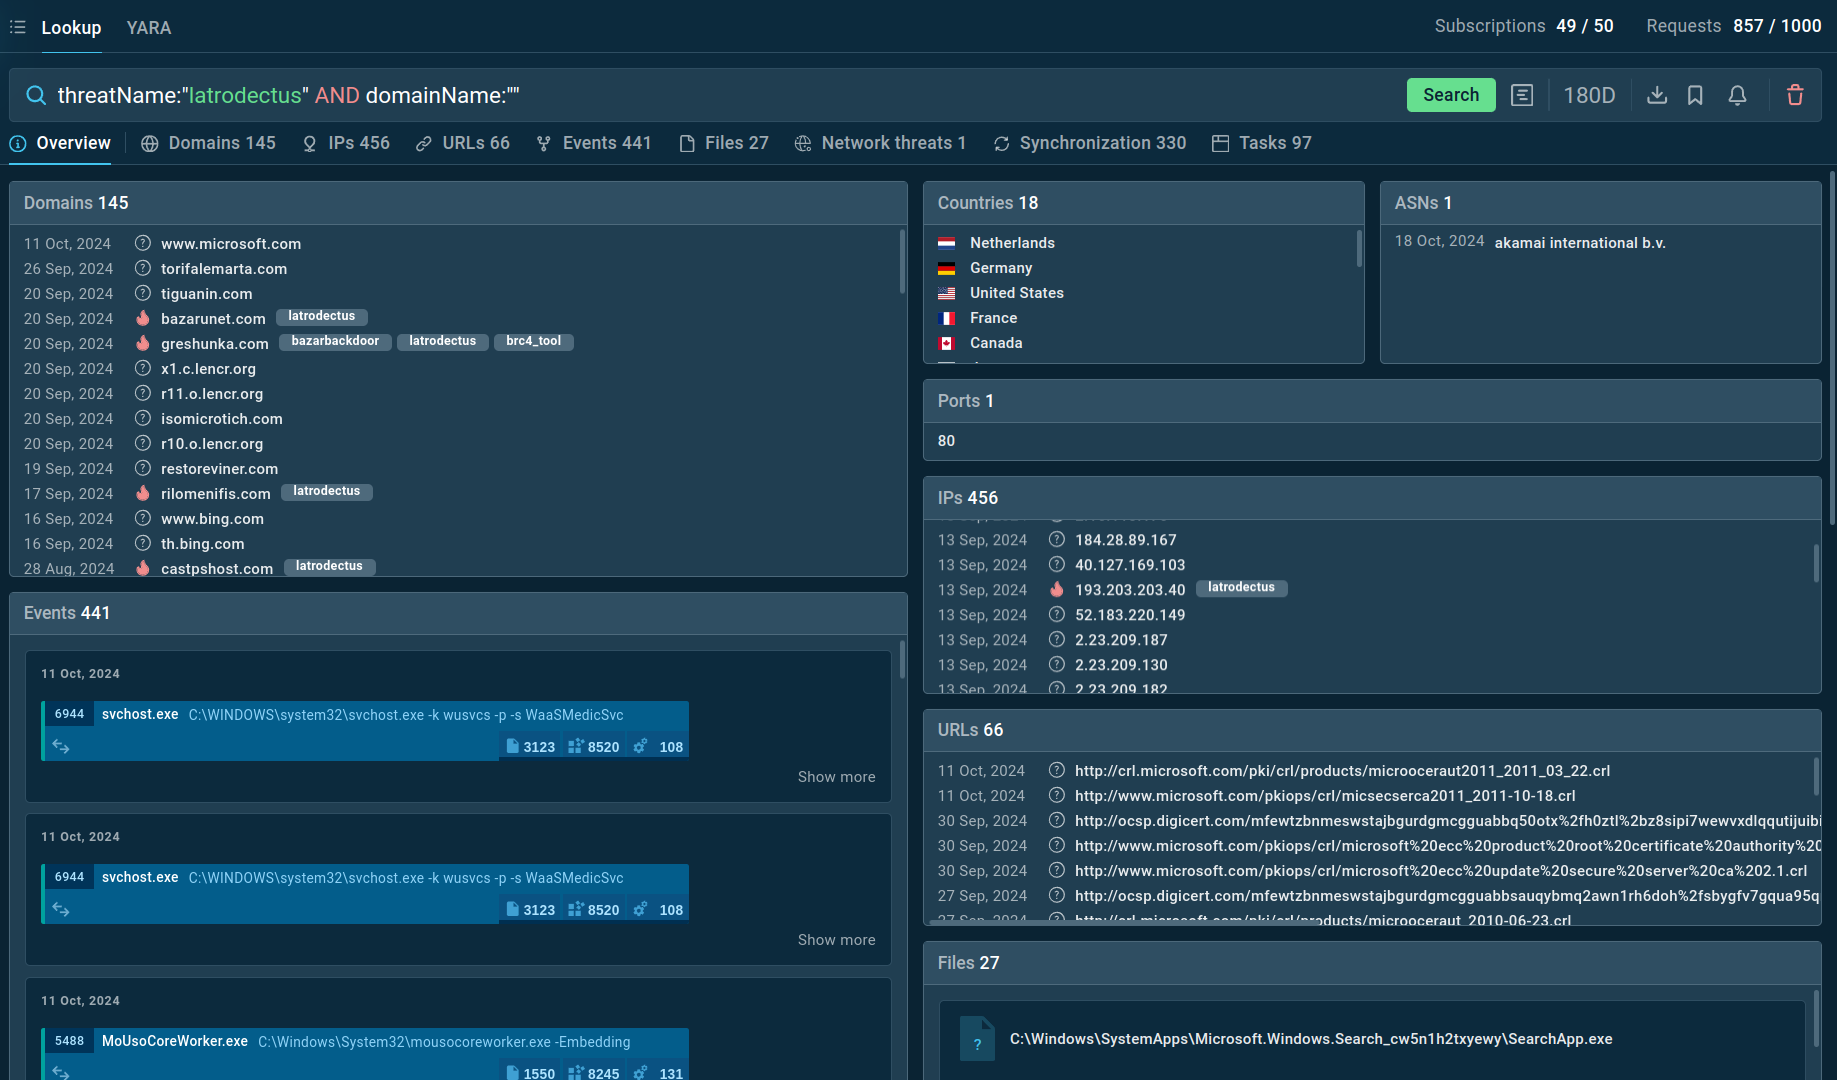
Latrodectus ANY.RUN Search results for Latrodectus in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"latrodectus" AND domainName:"" will generate a list of other data extracted from Lumma samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Latrodectus malware distribution methods

Phishing emails are the most common attack vector by threat actors for distributing Latrodectus malware. These emails are typically designed to appear as if they have been sent from a legitimate organization or individual, to trick the recipient into opening an attached file or clicking on a malicious link.

In one particular campaign, the threat actor group TA578 was observed to be spreading Latrodectus as part of a scheme that involved accusing target companies of copyright infringement. The phishing emails in this campaign were designed to look like they were sent from a legitimate organization.

In another instance, a fake Azure page was used to initiate the infection chain.

Conclusion

Latrodectus is a noteworthy loader that presents a challenge due to its widespread use by professional cyber criminal groups. Its capacity to deploy payloads, along with its advanced obfuscation and evasion methods, as well as continuous development contribute to its potential to become an even more serious threat.

ANY.RUN is a cloud-based service that can be used to safely analyze suspicious files and URLs, including Latrodectus malware. It allows you to observe malware behavior and collect indicators of compromise in a secure environment. Using ANY.RUN can help you understand Latrodectus's tactics and improve your defenses against it.

Create your ANY.RUN account – it’s free!
HAVE A LOOK AT

Ramnit screenshot
Ramnit
ramnit
Ramnit is a highly modular banking trojan and worm that evolved from a file-infecting virus into a powerful cybercrime tool. It specializes in financial fraud, credential theft, remote access, and malware delivery, being a serious threat to businesses and individuals. First spotted in 2010, Ramnit became popular after the 2014 takedown of the GameOver Zeus botnet, as cybercriminals sought alternatives for banking fraud.
Read More
DonutLoader screenshot
DonutLoader
donutloader donut
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More