Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
81
Global rank
54 infographic chevron month
Month rank
86 infographic chevron week
Week rank

Danabot is an advanced banking Trojan malware that was designed to steal financial information from victims. Out of the Trojans in the wild, this is one of the most advanced thanks to the modular design and a complex delivery method.

Trojan
Type
Unknown
Origin
6 May, 2018
First seen
8 October, 2026
Last seen

How to analyze Danabot with ANY.RUN

Type
Unknown
Origin
6 May, 2018
First seen
8 October, 2026
Last seen

IOCs

IP addresses
188.114.96.3
104.26.13.63
150.171.22.17
23.194.190.163
104.21.15.232
41.222.32.25
150.171.28.10
23.207.210.139
51.77.7.204
150.171.73.13
104.21.33.241
188.114.97.3
172.67.169.199
128.24.231.65
104.26.6.70
23.216.77.58
150.171.28.11
40.126.31.67
18.244.18.38
172.178.240.161
Hashes
db0d72bc7d10209f7fa354ec100d57abbb9fe2e57ce72789f5f88257c5d3ebd1
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
474d668707f1cb929fef1e3798b71b632e50675bd1a9dceaab90c9587f72f680
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
6028bd681dbf11a0a58dde8a0cd884115c04caa59d080ba51bde1b086ce0079d
9c70f766d3b84fc2bb298efa37cc9191f28bec336329cc11468cfadbc3b137f4
fbcfe23a2ecb82b7100c50811691dde0a33aa3da8d176be9882a9db485dc0f2d
b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
a41670d52423ba69c7a65e7e153e7b9994e8dd0370c584bda0714bd61c49c578
54241ebe651a8344235cc47afd274c080abaebc8c3a25afb95d8373b6a5670a2
bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
de6d7b7c2427ec4e738407d7834b71941f69166b030355e00f325ff1391df5a1
Domains
qscompute.com
edge.microsoft.com
ntp.msn.com
gpusolutions.net
computermatrix.net
c.msn.com
www.hwcooling.net
sb.scorecardresearch.com
clients2.googleusercontent.com
www.bing.com
srtb.msn.com
fe3cr.delivery.mp.microsoft.com
browser.events.data.msn.com
google.com
wecallshotgun.com
www.pcguide.com
r.bing.com
api.edgeoffer.microsoft.com
api.msn.com
www.computech-solutions.co.za
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://watson.events.data.microsoft.com/telemetry.request
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:ikoa5xshyzfb2m8dsexdzcxfern3i56znmbpkdg4pcy&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://ntp.msn.com/edge/ntp?locale=en-us&title=new%20tab&dsp=1&sp=bing&startpage=1&pc=u531
https://copilot.microsoft.com/c/api/user/eligibility
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1791433814&lafgdate=0
https://ntp.msn.com/bundles/v1/edgechromium/latest/ssr-extension.c8264382acf37d60.js
https://ntp.msn.com/bundles/v1/edgechromium/latest/web-worker.a415d192e77084ef.js
https://assets.msn.com/staticsb/statics/latest/mscmp/1.11/entry.js
https://assets.msn.com/staticsb/statics/latest/fluent-icons/arrow_up_24_regular.svg
https://assets.msn.com/staticsb/statics/latest/js/thirdparty/adsdk/mscmp/1.0.8/sdk.js
https://assets.msn.com/staticsb/statics/latest/icons-wc/icons/circlecompleted.svg
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 230
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2820
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4352
comments 0

What is Danabot banking malware?

Danabot is a banking trojan that was spotted in the wild in 2018. Danabot differs from competing Trojans thanks to its robust delivery system and modular design. Since its first appearance, Danabot has obtained high popularity among cybercriminals and became an active threat in multiple regions of the world.

This malware is constantly updated by the creators, helping the Trojan continue to gain popularity in the hacking community. Danabot is written using the Delphi programming language carries several credential theft functions.

General description of Danabot

When first documented, Danabot malware was being used by just one actor who carried out a campaign against Australian companies. Since then, other malicious actors have started utilizing this malware and expanded the geography of attacks to Europe and North America.

In particular, the Danabot trojan was seen in attacks in Poland, Germany, Italy, Austria, and the US. Particularly, the US campaigns were carried out on a large scale, indicating that the malware is evolving and developing.

As far as the function set of this malware is concerned, Danabot can be classified as a banking trojan, though some of its features suggest that it is becoming a more versatile malware. Danabot is constructed out of three main components. The loader is a program created to download the main payload. The main component, which is installed by the loader, is configured to download the modules that the attacker can specify. Finally, once installed, the modules provide the functionality, which can vary depending on which modules were chosen by the ill-wisher in a particular campaign.

The malware can take screenshots, grant attackers remote control of the victims’ machine, collect system information, steal credentials, and record lists of files stored on infected PCs. Once collected, all information recorded by Danabot is sent to the control server in an encrypted form. Danabot aims to steal sensitive information that can be leveraged by the attackers later, therefore instead of confirming the victim head-on and demanding a ransom. This malware tries to stay hidden and collect valuable data over time. Some of the smaller distribution campaigns featuring Danabot were well made in terms of clever social engineering and carried on with the same philosophy of a more subtle approach.

In addition, researchers noticed that the attackers utilizing Danabot ventured beyond banking credentials theft and started utilizing this banking malware to host other spam and malicious campaigns, using the infected machines of their victims. What’s more, Danabot creators are thought to be collaborating with the group behind a different banking trojan – GootKit. Danabot was recorded as being used to distribute this type of threat. This case is a first for both malicious programs since neither has been distributed or distributed by other malware before.

In January 2019, researchers noticed a new version of the Danabot trojan in the wild. The investigation confirmed the new samples to be the evolution of Danabot, with a different C2 communication protocol that began to use multiple encryption layers and proved very complex. In the new variant, AES and RSA encryption algorithms were employed in particular. On top of that, the core design of the malware was also changed, as the loader was made responsible for downloading all the modules along with the main component. The researchers believe a technique was used to avoid detection on a network level that the attackers could have invented after reading existing analysis material on Danabot.

It should be noted that Danabot features several evasion techniques designed to make research as complicated as possible. For one, the banking malware is loaded with many lines of junk code, implemented solely to mislead the researchers. The malware also uses encryption and Windows API function hashing to fool automated sandboxes and researchers and prevent them from uncovering the true nature of the code.

Malware analysis of Danabot

A video recorded in the ANY.RUN malware hunting service enables us to take a look at Danabot in action.
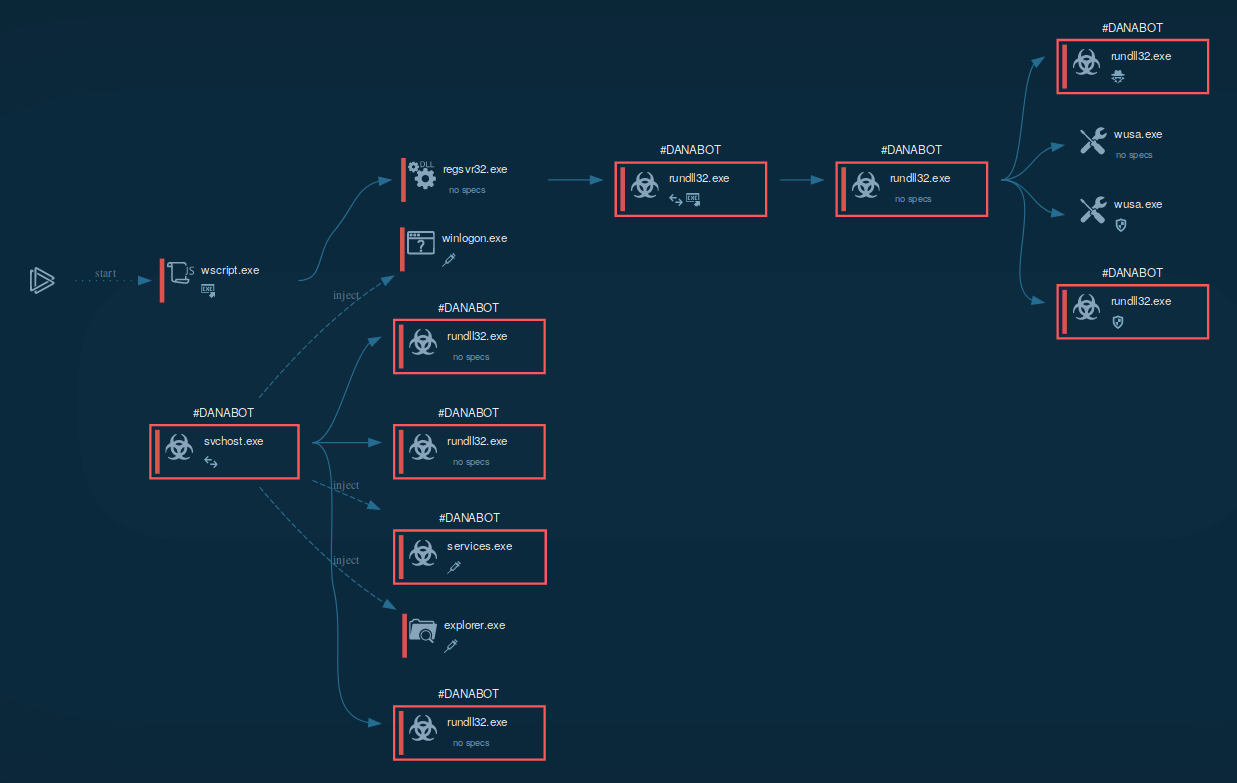
danabot execution process graph

Figure 1: A process graph generated by ANY.RUN for the convenience of the researchers
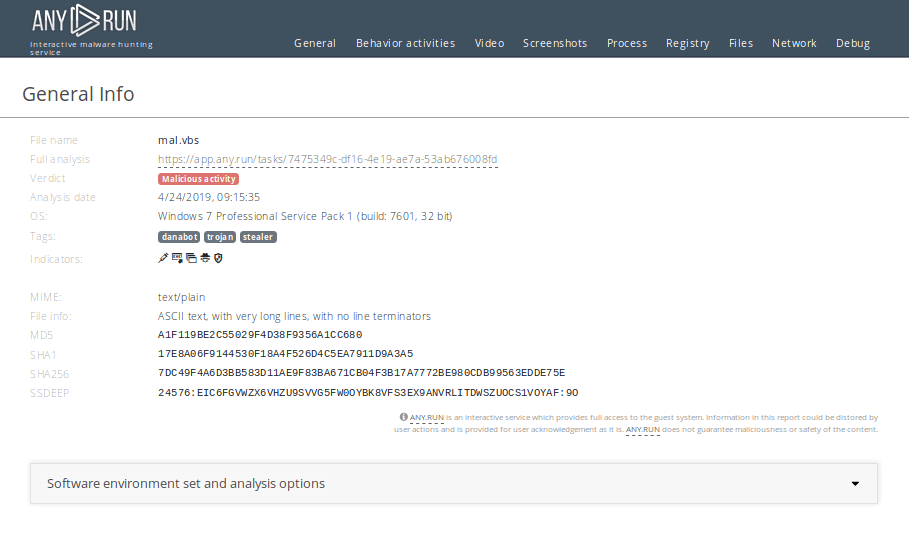
text report of the Danabot malware execution

Figure 2: The text report generated by ANY.RUN is created to allow easy sharing of the study results

Danabot banking malware execution process

Typically Danabot trojan infects devices according to the following scenario. First of all, the downloader establishes a connection with the C2 server and downloads an executable file with a DLL file, which can be either 32-bit or 64-bit based on the infected OS version.

After that, Danabot begins stealing information from the infected OS. The banking malware bypasses user access control by using a DLL hijacking vulnerability in the Windows Update Standalone Installer (wusa.exe). This allows Danabot to create services and execute the injection into system processes. After all of these steps, Danabot receives full system control.

How to avoid infection by Danabot?

Danabot is distributed in email spam campaigns targeting organizations and using social engineering to trick victims into downloading malicious documents the same scenario as

Danabot is also known to get into PCs with another malware called Hancitor. Email campaigns featuring Danabot were considered well crafted by some researchers, who noted that social engineering involved seemed very effective.

Communication with C&C

In older samples of Danabot, the loader component used HTTP protocol to communicate with the control server, whereas the main component utilized the binary protocol. In more recent iterations, both components started to communicate with the C2 server over TCP port 443 using TLS instead.

How to detect Danabot using ANY.RUN?

ANY.RUN uses Suricata IDS rule sets, so if malware trying to communicate with C&C servers, it will be detected. To look at what threats were detected, click on the "Threats" section of the "Network" tab.
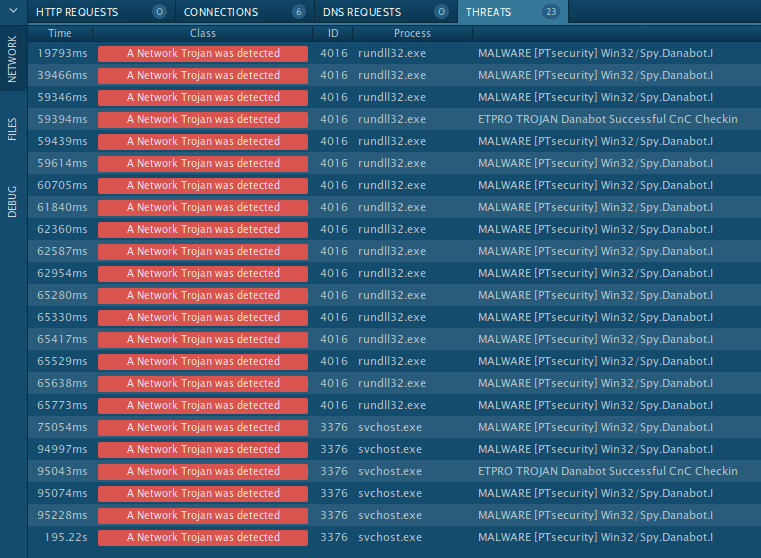
danabot network threats Figure 3: Danabot's network threats

Conclusion

Danabot is a very sophisticated malicious program used as a banking trojan and more. Targeting organizations across multiple continents, Danabot malware poses a high threat to businesses thanks to robust distribution methods and cutting-edge anti-evasion and persistence techniques.

In addition, the module nature of this banking malware allows attackers to fine-tune their campaigns, customizing them for every potential victim. All these traits combined helped make Danabot a very popular banking trojan that is only continuing to gain traction in the criminal community and further expand the geography of attacks.

To establish a reliable cyber defense, security professionals can utilize malware hunting and analysis services such as ANY.RUN, which allows to dissect malware samples and thoroughly study their behavior and architecture.
HAVE A LOOK AT

BlackMatter screenshot
BlackMatter
blackmatter
BlackMatter is a ransomware strain operating as a Ransomware-as-a-Service (RaaS), designed to encrypt files, remove recovery options, and extort victims across critical industries. Emerging in 2021, it quickly became a major concern due to its ability to evade defenses, spread across networks, and cause large-scale operational disruption, forcing security teams to act against a highly destructive and persistent threat.
Read More
Balada Injector screenshot
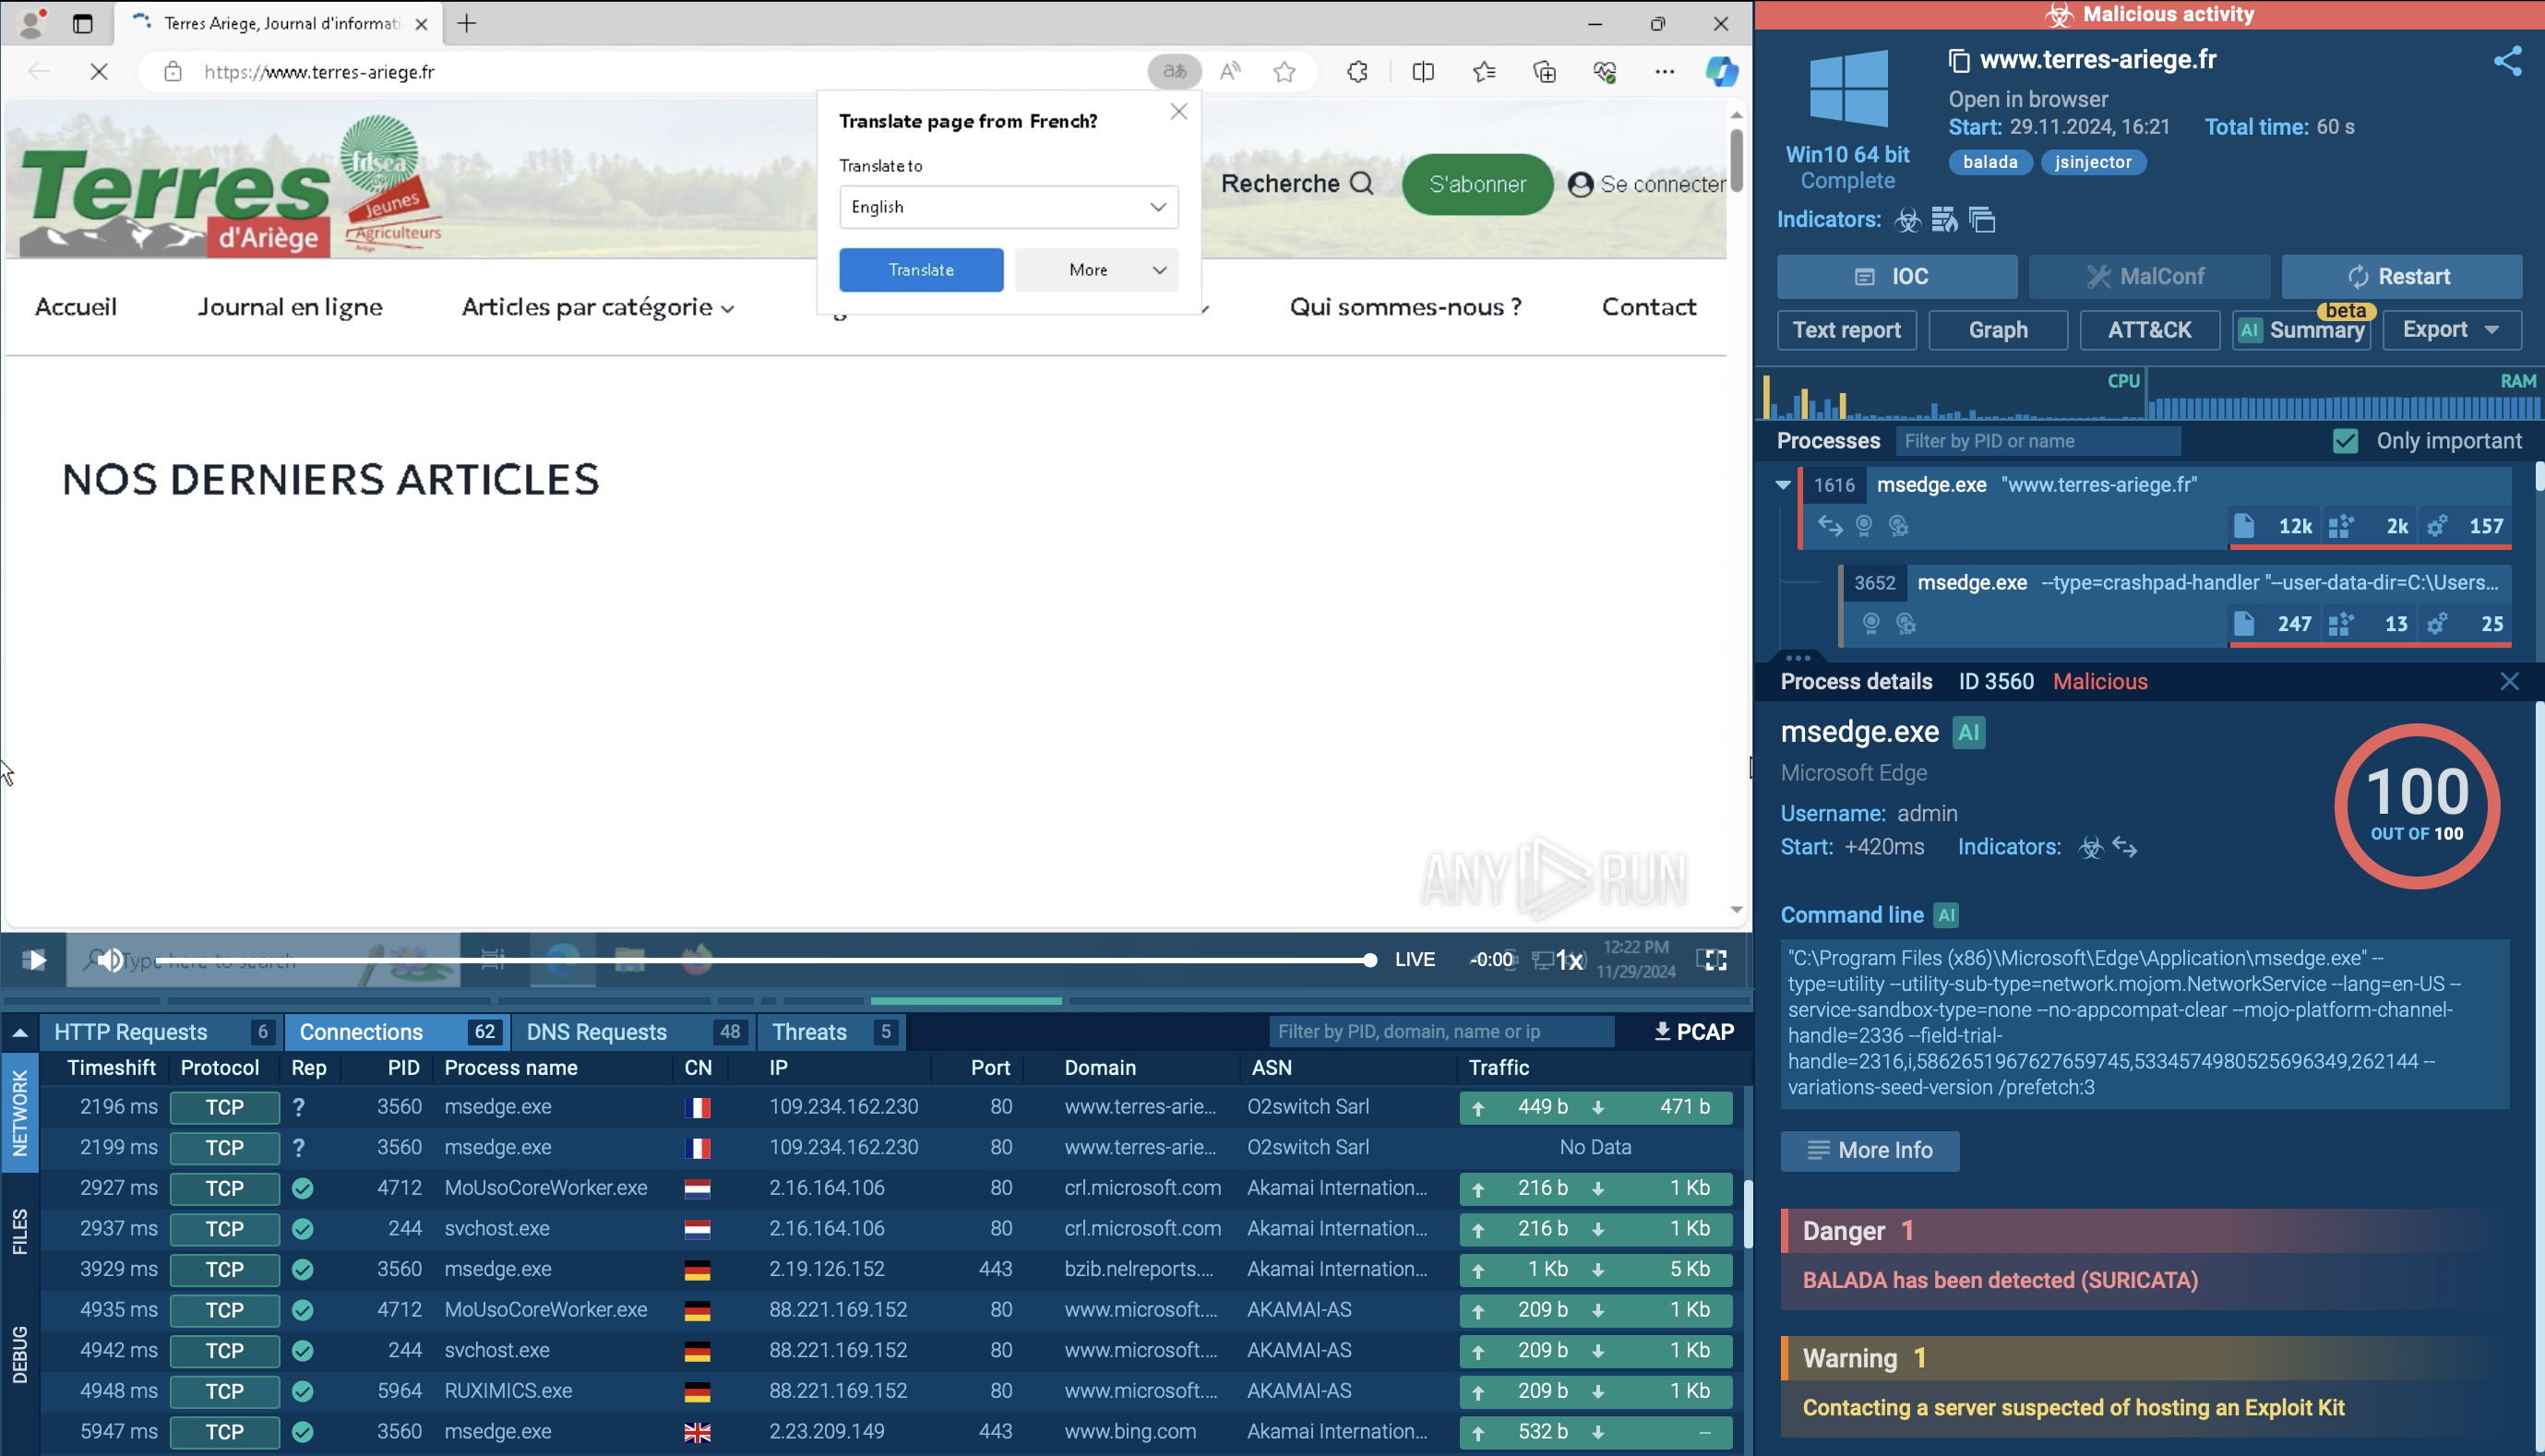
Balada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
Read More
Gunra screenshot
Gunra
gunra
Gunra ransomware, a financially motivated threat actor that emerged in April 2025, deploys double-extortion tactics to encrypt victims' data and threaten leaks of exfiltrated information, primarily targeting Windows and Linux systems across healthcare, manufacturing, and other sectors worldwide.
Read More
Emmenhtal screenshot
Emmenhtal
emmenhtal
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
Read More
Spyware screenshot
Spyware
spyware
Spyware is a stealth form of malware whose primary objective is to gather sensitive information, such as personal data, login credentials, and financial details, by monitoring user activities and exploiting system vulnerabilities. Spyware operates secretly in the background, evading detection while transmitting collected data to cybercriminals, who can then use it for malicious purposes like identity theft, financial fraud, or espionage.
Read More
RedLine screenshot
RedLine
redline stealer redline stealer malware
RedLine Stealer is a malicious program that collects users’ confidential data from browsers, systems, and installed software. It also infects operating systems with other malware.
Read More