ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | mal.vbs |
| Full analysis: | https://app.any.run/tasks/7475349c-df16-4e19-ae7a-53ab676008fd |
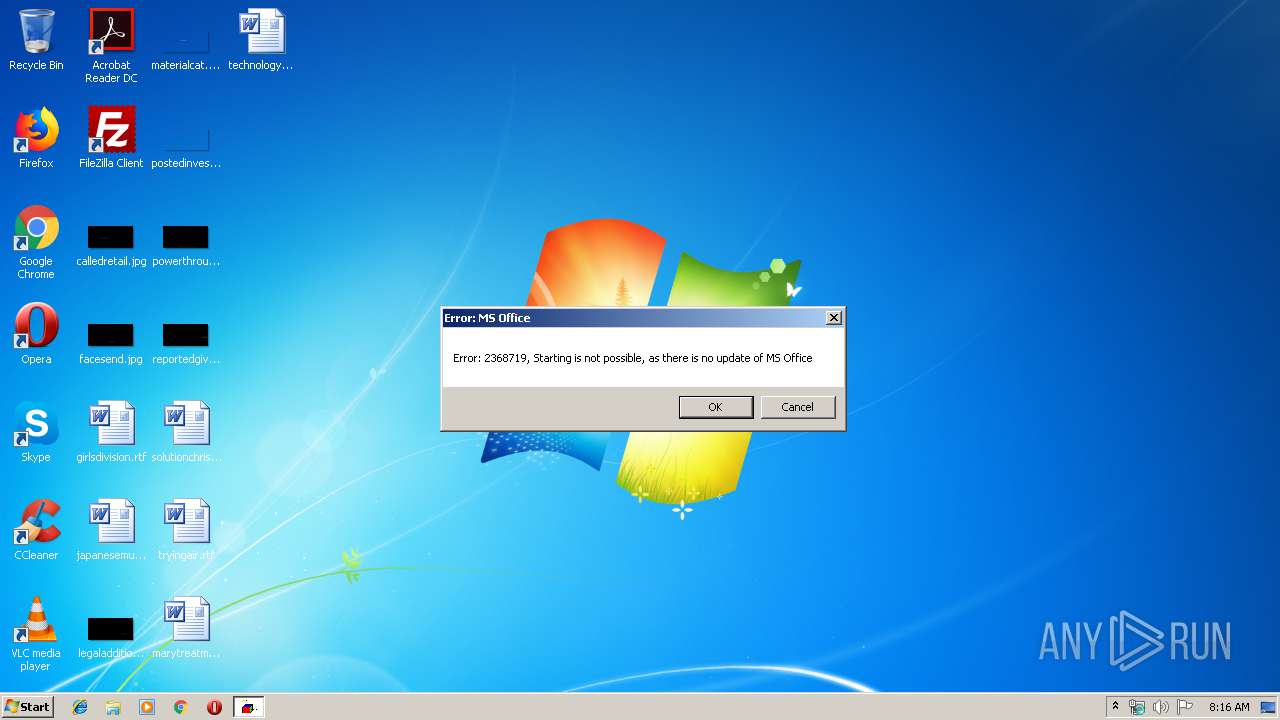
| Verdict: | Malicious activity |
| Threats: | Danabot is an advanced banking Trojan malware that was designed to steal financial information from victims. Out of the Trojans in the wild, this is one of the most advanced thanks to the modular design and a complex delivery method. |
| Analysis date: | April 24, 2019, 07:15:35 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | text/plain |
| File info: | ASCII text, with very long lines, with no line terminators |
| MD5: | A1F119BE2C55029F4D38F9356A1CC680 |
| SHA1: | 17E8A06F9144530F18A4F526D4C5EA7911D9A3A5 |
| SHA256: | 7DC49F4A6D3BB583D11AE9F83BA671CB04F3B17A7772BE980CDB99563EDDE75E |
| SSDEEP: | 24576:EIc6FGvWzX6VhZU9svvg5Fw0OYBK8VFs3eX9ANvrlITDWSzuOcs1VOyAF:9O |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 252 | C:\Windows\Explorer.EXE | C:\Windows\explorer.exe | — | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 444 | winlogon.exe | C:\Windows\System32\winlogon.exe | — | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Logon Application Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 492 | C:\Windows\system32\services.exe | C:\Windows\System32\services.exe | wininit.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Services and Controller app Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2096 | C:\Windows\system32\RUNDLL32.EXE C:\ProgramData\F35802F6\EB29C513.dll,f7 | C:\Windows\system32\RUNDLL32.EXE | svchost.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2136 | C:\Windows\system32\RUNDLL32.EXE C:\ProgramData\F35802F6\EB29C513.dll,f3 | C:\Windows\system32\RUNDLL32.EXE | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2140 | C:\Windows\system32\\rundll32.exe C:\PROGRA~2\F35802F6\EB29C513.dll,f1 C:\Users\admin\AppData\Local\Temp\MiSBxs.dllFFWjGU@4016 | C:\Windows\system32\rundll32.exe | rundll32.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2220 | "C:\Windows\System32\wusa.exe" /quiet | C:\Windows\System32\wusa.exe | — | rundll32.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Update Standalone Installer Exit code: 3221226540 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2828 | "C:\Windows\System32\regsvr32.exe" -s C:\Users\admin\AppData\Local\Temp\\MiSBxs.dllFFWjGU | C:\Windows\System32\regsvr32.exe | — | WScript.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft(C) Register Server Exit code: 4 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2932 | "C:\Windows\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\mal.vbs" | C:\Windows\System32\WScript.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft ® Windows Based Script Host Exit code: 0 Version: 5.8.7600.16385 Modules
| |||||||||||||||
| 3040 | "C:\Windows\System32\wusa.exe" /quiet | C:\Windows\System32\wusa.exe | rundll32.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Update Standalone Installer Exit code: 87 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (252) explorer.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\UserAssist\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\Count |
| Operation: | write | Name: | {Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\jfpevcg.rkr |
Value: 00000000000000000000000003170000000080BF000080BF000080BF000080BF000080BF000080BF000080BF000080BF000080BF000080BFFFFFFFFF000000000000000000000000 | |||
| (PID) Process: | (252) explorer.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\UserAssist\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\Count |
| Operation: | write | Name: | HRZR_PGYFRFFVBA |
Value: 000000000400000002000000FA8A00000200000002000000724300004D006900630072006F0073006F00660074002E004100750074006F00470065006E006500720061007400650064002E007B00310035003900360032003100370035002D0037004400460043002D0042003100440037002D0042003000440031002D004500420034004300300038004600460044003700350034007D000000120200000000CC0B120200000000CC0B12020400050005001F02280C12020800050005001F026CE71F020100000154001F0200000100B8139D75444812020C0003000300000000000500280C12020000000005000000CC0B120201000000C8E91F02C0E91F0200000000C8FDDE02C0FCDE0244E71F023DA9457600000000FBFFFF7F68E71F02987880574F8C6244BB6371042380B1090000000001100211FFFFFFFF00000000000000000000000035EE190651EE190635EE1906000000000000000000000000080000002E006C006E006B0000005300630068006500640075006C00650072002E006C006E006B00000014000000140050000000070000000200060026030200A5863C750800000064021400E72F1B77B5863C753F030000CC04140000001400A86D150011000000B8451700B045170005000000F8F3DD0270E80000F28635BB20E81F028291457670E81F0224E81F022795457600000000ECD2DD024CE81F02CD944576ECD2DD02F8E81F0260CEDD02E19445760000000060CEDD02F8E81F0254E81F020200000002000000724300004D006900630072006F0073006F00660074002E004100750074006F00470065006E006500720061007400650064002E007B00310035003900360032003100370035002D0037004400460043002D0042003100440037002D0042003000440031002D004500420034004300300038004600460044003700350034007D000000120200000000CC0B120200000000CC0B12020400050005001F02280C12020800050005001F026CE71F020100000154001F0200000100B8139D75444812020C0003000300000000000500280C12020000000005000000CC0B120201000000C8E91F02C0E91F0200000000C8FDDE02C0FCDE0244E71F023DA9457600000000FBFFFF7F68E71F02987880574F8C6244BB6371042380B1090000000001100211FFFFFFFF00000000000000000000000035EE190651EE190635EE1906000000000000000000000000080000002E006C006E006B0000005300630068006500640075006C00650072002E006C006E006B00000014000000140050000000070000000200060026030200A5863C750800000064021400E72F1B77B5863C753F030000CC04140000001400A86D150011000000B8451700B045170005000000F8F3DD0270E80000F28635BB20E81F028291457670E81F0224E81F022795457600000000ECD2DD024CE81F02CD944576ECD2DD02F8E81F0260CEDD02E19445760000000060CEDD02F8E81F0254E81F020200000002000000724300004D006900630072006F0073006F00660074002E004100750074006F00470065006E006500720061007400650064002E007B00310035003900360032003100370035002D0037004400460043002D0042003100440037002D0042003000440031002D004500420034004300300038004600460044003700350034007D000000120200000000CC0B120200000000CC0B12020400050005001F02280C12020800050005001F026CE71F020100000154001F0200000100B8139D75444812020C0003000300000000000500280C12020000000005000000CC0B120201000000C8E91F02C0E91F0200000000C8FDDE02C0FCDE0244E71F023DA9457600000000FBFFFF7F68E71F02987880574F8C6244BB6371042380B1090000000001100211FFFFFFFF00000000000000000000000035EE190651EE190635EE1906000000000000000000000000080000002E006C006E006B0000005300630068006500640075006C00650072002E006C006E006B00000014000000140050000000070000000200060026030200A5863C750800000064021400E72F1B77B5863C753F030000CC04140000001400A86D150011000000B8451700B045170005000000F8F3DD0270E80000F28635BB20E81F028291457670E81F0224E81F022795457600000000ECD2DD024CE81F02CD944576ECD2DD02F8E81F0260CEDD02E19445760000000060CEDD02F8E81F0254E81F02 | |||
| (PID) Process: | (2932) WScript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 0 | |||
| (PID) Process: | (2932) WScript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 1 | |||
| (PID) Process: | (2140) rundll32.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 0 | |||
| (PID) Process: | (2140) rundll32.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 1 | |||
| (PID) Process: | (3484) RUNDLL32.EXE | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Tracing\RUNDLL32_RASAPI32 |
| Operation: | write | Name: | EnableFileTracing |
Value: 0 | |||
| (PID) Process: | (3484) RUNDLL32.EXE | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Tracing\RUNDLL32_RASAPI32 |
| Operation: | write | Name: | EnableConsoleTracing |
Value: 0 | |||
| (PID) Process: | (3484) RUNDLL32.EXE | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Tracing\RUNDLL32_RASAPI32 |
| Operation: | write | Name: | FileTracingMask |
Value: 4294901760 | |||
| (PID) Process: | (3484) RUNDLL32.EXE | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Tracing\RUNDLL32_RASAPI32 |
| Operation: | write | Name: | ConsoleTracingMask |
Value: 4294901760 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 4016 | rundll32.exe | C:\ProgramData\F35802F6\37C8843F | — | |
MD5:— | SHA256:— | |||
| 3484 | RUNDLL32.EXE | C:\Users\admin\AppData\Local\Temp\1323875.tmp-shm | — | |
MD5:— | SHA256:— | |||
| 2096 | RUNDLL32.EXE | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\qldyz51w.default\key4.db-journal | — | |
MD5:— | SHA256:— | |||
| 3484 | RUNDLL32.EXE | C:\Users\admin\AppData\Local\Temp\1326109.tmp | — | |
MD5:— | SHA256:— | |||
| 3484 | RUNDLL32.EXE | C:\Users\admin\AppData\Local\Temp\1326109.tmp-shm | — | |
MD5:— | SHA256:— | |||
| 2932 | WScript.exe | C:\Users\admin\AppData\Local\Temp\MiSBxs.dllFFWjGU | executable | |
MD5:69471040BBEEE6C6562DCAC8472A21E9 | SHA256:2662A9750ED240770E38E10DDF70C420712DAD7ED05A3CBA2EAC191F9D4F3231 | |||
| 3484 | RUNDLL32.EXE | C:\Users\admin\AppData\Local\Temp\1317875.tmp | sqlite | |
MD5:60B51BA20224AC3783E213EA9F55F125 | SHA256:0E305BA02985F26B29B234CD79D2C2AF0A51085DA2DB2BED98D20F8C61B76254 | |||
| 2096 | RUNDLL32.EXE | C:\ProgramData\Microsoft\Crypto\RSA\MachineKeys\0479eb5a71ca85ee67e6f14f4d9c32c3_90059c37-1320-41a4-b58d-2b75a9850d2f | dbf | |
MD5:DFC47158CF82C2F1E67720539A1E44D2 | SHA256:8B9C0F374CB1845C0D28D5031B5567F9CD2D3883F513FC792C0D76976D8CAA0C | |||
| 3376 | svchost.exe | C:\ProgramData\F35802F6\62C70540\0D9F79ADB8576C86D7528A0C390FF77A.zip | — | |
MD5:— | SHA256:— | |||
| 3484 | RUNDLL32.EXE | C:\Users\admin\AppData\Local\Temp\1323109.tmp | sqlite | |
MD5:C394A5F8DD1C20D9E22FA71C8C15CD6F | SHA256:806949F008F012CF228BBE536809DB014C0CDE3C1F2A6DF1558BFAC19B088F22 | |||
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4016 | rundll32.exe | 25.235.71.119:443 | — | — | GB | malicious |
4016 | rundll32.exe | 95.179.186.57:443 | — | Cosmoline Telecommunication Services S.A. | GR | malicious |
3376 | svchost.exe | 6.100.192.167:443 | — | — | US | malicious |
3376 | svchost.exe | 195.239.225.127:443 | — | PVimpelCom | RU | malicious |
4016 | rundll32.exe | 172.79.113.253:443 | — | Frontier Communications of America, Inc. | US | malicious |
3376 | svchost.exe | 95.179.186.57:443 | — | Cosmoline Telecommunication Services S.A. | GR | malicious |
PID | Process | Class | Message |
|---|---|---|---|
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |
4016 | rundll32.exe | A Network Trojan was detected | MALWARE [PTsecurity] Win32/Spy.Danabot.I |