Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
183
Global rank
148 infographic chevron month
Month rank
178 infographic chevron week
Week rank

Octo malware, also known as ExobotCompact or Coper, is a sophisticated Android banking trojan that has evolved from earlier malware family Exobot. It poses a significant threat to financial institutions, mobile users, and enterprise networks.

Trojan
Type
Unknown
Origin
1 February, 2021
First seen
28 September, 2026
Last seen
Also known as
ExobotCompact
Coper

How to analyze Octo with ANY.RUN

Type
Unknown
Origin
1 February, 2021
First seen
28 September, 2026
Last seen

IOCs

IP addresses
194.59.31.126
176.123.1.132
94.74.182.52
142.251.151.119
142.251.153.119
142.251.156.119
142.251.154.119
142.251.110.102
142.251.110.94
142.250.154.94
142.251.20.94
142.251.150.119
216.239.35.4
142.251.155.119
142.251.14.94
34.104.35.123
142.251.110.100
142.251.127.81
172.217.117.4
142.251.152.119
Hashes
bb9f8df61474d25e71fa00722318cd387396ca1736605e1248821cc0de3d3af8
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
8e89bbb65cdd9fffc294660ba897eb044424a9f80306f1f1f165aeea01d9b8ec
8b82f6032e29a2b5c96031a3630fb6173d12ff0295bc20bb21b877d08f0812d8
6c0f7584f6bbeb0fcaff4626dc2f031e33a2332fa244fbbd1729233be02e5c54
822431b5ba851126f85acc263068b595d95190f0db8f7e2c2fdd8f0ee96838d3
5a66cb0f25fe5f6d2d0a9057c9b782eae20404dcdf7a017ade45602b06f8bc87
3c4af14d27776e1c5146c3784c5ebe6786241d1bc1d5882a43822ba6c1db581d
e44c6703f8ce2b1ed819f8756b4b888c517095b5ef35917ee916af8318deb3b1
6ec886904f5a6041d39304d3b46699d28f0bab12fcdd4446981d0e1df6a35c18
08b17ce62c0987278f7c4b56684ebc1a18433dcc1b2e9346f4e0edf03c21ff41
063f3565965de1291fe41761620587adac8b337fc4a4ba38592170af97b51be1
065bfa94d0d21ba1a1722a26f52731a6512c8f005d56ead13856e91c19bcade4
e80c0e454a89e4feaa0eb18df6c92efd3e9fe6d0f4c131dd130512aeb7f60020
86957584483bcf6dae8085b280b20da11af5ebe4e6824ae4ca1b0ddcffe8d509
4a17496b5f81cfe4e0d290cd9bbb6820fb15140664c560eb7918f6d9146215f4
1472ab5c93bf9cb22f582b535565efdf0c4be72fabfbd537646e10be728eda11
69a464ba66e320797c3bf568975e0062ac92019f755bbf8ac7fcee16d9b6262a
d5fc42f4d8531eae51ce3d8726bd925da43e4e2e2e860e2b3faf4727432a9775
af8d008200fc56bf9b96286261f4118962303d90c9d1bb3fa5edc17e73354fc2
Domains
www.google.com
connectivitycheck.gstatic.com
play.googleapis.com
344d23b6606asd1211f9813c0c4d18f2a5f.com
clientservices.googleapis.com
staging-remoteprovisioning.sandbox.googleapis.com
google.com
update.googleapis.com
time.android.com
54623b606ada1211f9813c0c4d18f2a5f.com
edgedl.me.gvt1.com
www.ip-api.com
thhausgajk.com
URLs
http://connectivitycheck.gstatic.com/generate_204
http://play.googleapis.com/generate_204
https://www.google.com/generate_204
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:fetcheekchain
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaaboofzrx4bilsty-c_xrrr_h1zilsmybbwh8i=&request_id=1c1ca05c-9ade-4939-82ac-0c81a57f0027
https://clientservices.googleapis.com/chrome-variations/seed?osname=android_webview&milestone=137
https://update.googleapis.com/service/update2/json?cup2key=15:qdh6p4irx0jsmyekk0tsm1ztgieboy7dfmfecktqkho&cup2hreq=12fef204ca88fac17878a773a058b093e6b69624f1672566f4ae8d9cb183af5b
https://update.googleapis.com/service/update2/json
https://edgedl.me.gvt1.com/edgedl/release2/chrome_component/acmmwq7dser4xm5sepzjv74g65vq_2023.7.28.10/cffplpkejcbdpfnfabnjikeicbedmifn_2023.07.28.10_all_acgbwixmcanakp2bkoppyszsbkrq.crx3
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabooe0bd8bilsty-ogje_codrhxflbxbmvhde=&request_id=56428c47-c146-4eca-a50c-b9bbe120c5e7
https://update.googleapis.com/service/update2/json?cup2key=15:ilfwkryilu0y58bmhyibdwf058ndduxp3ntrjtprckc&cup2hreq=5deaca71f0d22e7778e4dc912cdbeb6a7435e5bb100e9551f6bcd2536e11b9ee
http://www.ip-api.com/json
https://thhausgajk.com/mwnhmji2otkynja3/
https://thhausgajk.com/mwnhmji2otkynja3/?language=en&model=samsung+galaxy_s9&is_xiaomi=0&is_samsung=1&app=bawag%20psk%20security
http://www.google.com/gen_204
https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signcertificates?challenge=aaabnf189csbilstywbvahcows7ctwi3wpfruzs=&request_id=d17110e9-14e7-4114-bfa2-630b22663b5d
https://update.googleapis.com/service/update2/json?cup2key=15:luiool8oxfs7f0hlrj-bp98aglovoiulxng7yacoemi&cup2hreq=9a05f8d9b8ef18723c5b80e19c78b223cf7c0576dbfaba8254045fa10fd04646
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1648
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 3378
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10879
comments 0

What is Octo malware?

Octo, also known as Coper or ExobotCompact, is an Android banking Trojan that evolved from the Exobot malware family, first observed in 2016. Initially based on the Marcher Trojan, Exobot targeted financial institutions globally until 2018, when a lighter version, ExobotCompact, emerged.

By 2021, a new variant appeared, named Coper by some antivirus vendors, but later renamed as Octo — a rebranded and enhanced ExobotCompact. In 2024, Octo2, an even more advanced iteration, was released, driven partly by the leak of Octo’s source code. The Malware-as-a-Service (MaaS) model makes Octo accessible to even novice cybercriminals.

Lineage:

  • Exobot, an Android banking trojan that went inactive, and its source code leaked.
  • ExobotCompact, a more compact version with no dependency on older Android APIs.
  • Octo, enhanced version with powerful remote access and evasion features.
  • Coper is sometimes considered a separate but related strain, circulating in Latin America, sharing infrastructure/code.

Octo’s Distribution

The malware targets Android devices through social engineering and malicious app distribution:

  • Fake Apps and Droppers: Octo disguises itself as legitimate apps like Google Chrome, NordVPN, or banking apps, often using a dropper service called Zombinder to bundle with legitimate APKs. These are typically distributed via third-party app stores, malicious websites, or phishing campaigns, though some droppers.
  • SMS Phishing (Smishing): Messages with malicious links trick users into downloading fake apps posing as WhatsApp, Netflix, or banking services. This functionality is similar to that of Salvador Stealer, another Android banking trojan.
  • Social Engineering: Campaigns often impersonate trusted brands or simulate urgent software updates. Regional targeting, such as fake Bancolombia apps for Colombian users, enhances credibility.

Once installed, Octo prompts users to enable Accessibility Services and give out Device Admin privileges, granting extensive control over the device, and enhances remote access stability.

Its communications with C2 servers include dynamic configurations to target specific apps (e.g., to block push notifications from banking apps).

Octo’s Key Operation Vectors

  • Keylogging: to capture credentials, PINs, and lock patterns. Data is temporarily stored in the device’s data directory before deletion to avoid detection.
  • Overlay Attacks: the trojan displays fake login screens or overlays mimicking banking apps to steal credentials and card details. Overlays adapt dynamically to the active app, increasing deception.
  • SMS and Notification Interception: Intercepts messages and push notifications, enabling attackers to bypass two-factor authentication (2FA).
  • Remote Access (VNC): Uses Android’s MediaProjection for near-real-time screen streaming (1 screenshot per second. Sends live feed to C2, allowing attackers to see everything that happens on the device.
  • Device Takeover: Can simulate clicks and actions in real-time.
  • Ransomware-Like Locking: Some variants (like Coper) can lock screens and demand ransom.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Why Octo Is Especially Dangerous

  • Full Remote Control of Mobile Devices.
  • Live Monitoring and Fraud: Attackers perform fraud while victims are active, bypassing behavioral fraud detection.
  • Two-Factor Authentication Bypass: Through SMS or code-grabbing overlays.
  • Modular Structure: Can load updated components from C2 without user knowing.
  • Enterprise Risk: Can be used as an entry point into corporate networks via compromised employee devices (BYOD); targets banking customers and employees.

Octo’s Execution Process and Evasion Techniques

ANY.RUN’s Interactive Sandbox supports the analysis of APK files and enables the research of Android malware. Let us observe the behavior of an Octo sample where the malware is disguised as Google Chrome browser.

View Octo analysis session in the Sandbox

Once installed, Octo — also known as Coper or ExobotCompact — connects to its command and control (C2) server, potentially using a domain generation algorithm (DGA) to maintain resilient, encrypted communication. In our case, the address was toplamakampiyolculukhazirlik[.]xyz, visible in the DNS requests tab, though unresolved. The C2 provides configuration files and commands specifying which apps to target and what actions to take. In this task, the C2 was already offline.

Octo abuses Android’s Accessibility Service and MediaProjection APIs to gain full remote control, enabling real-time screen streaming, simulated taps, gestures, clipboard access, and text input. To stay hidden, it can display a black screen, dim brightness to zero, and disable notifications.

The malware supports keylogging, SMS and notification interception, blocking app alerts, screen locking/unlocking, muting sound, launching apps, and sending SMS. Attackers use AES-encrypted, Base64-encoded commands to control these features and perform on-device fraud—initiating and confirming transactions without triggering alarms.
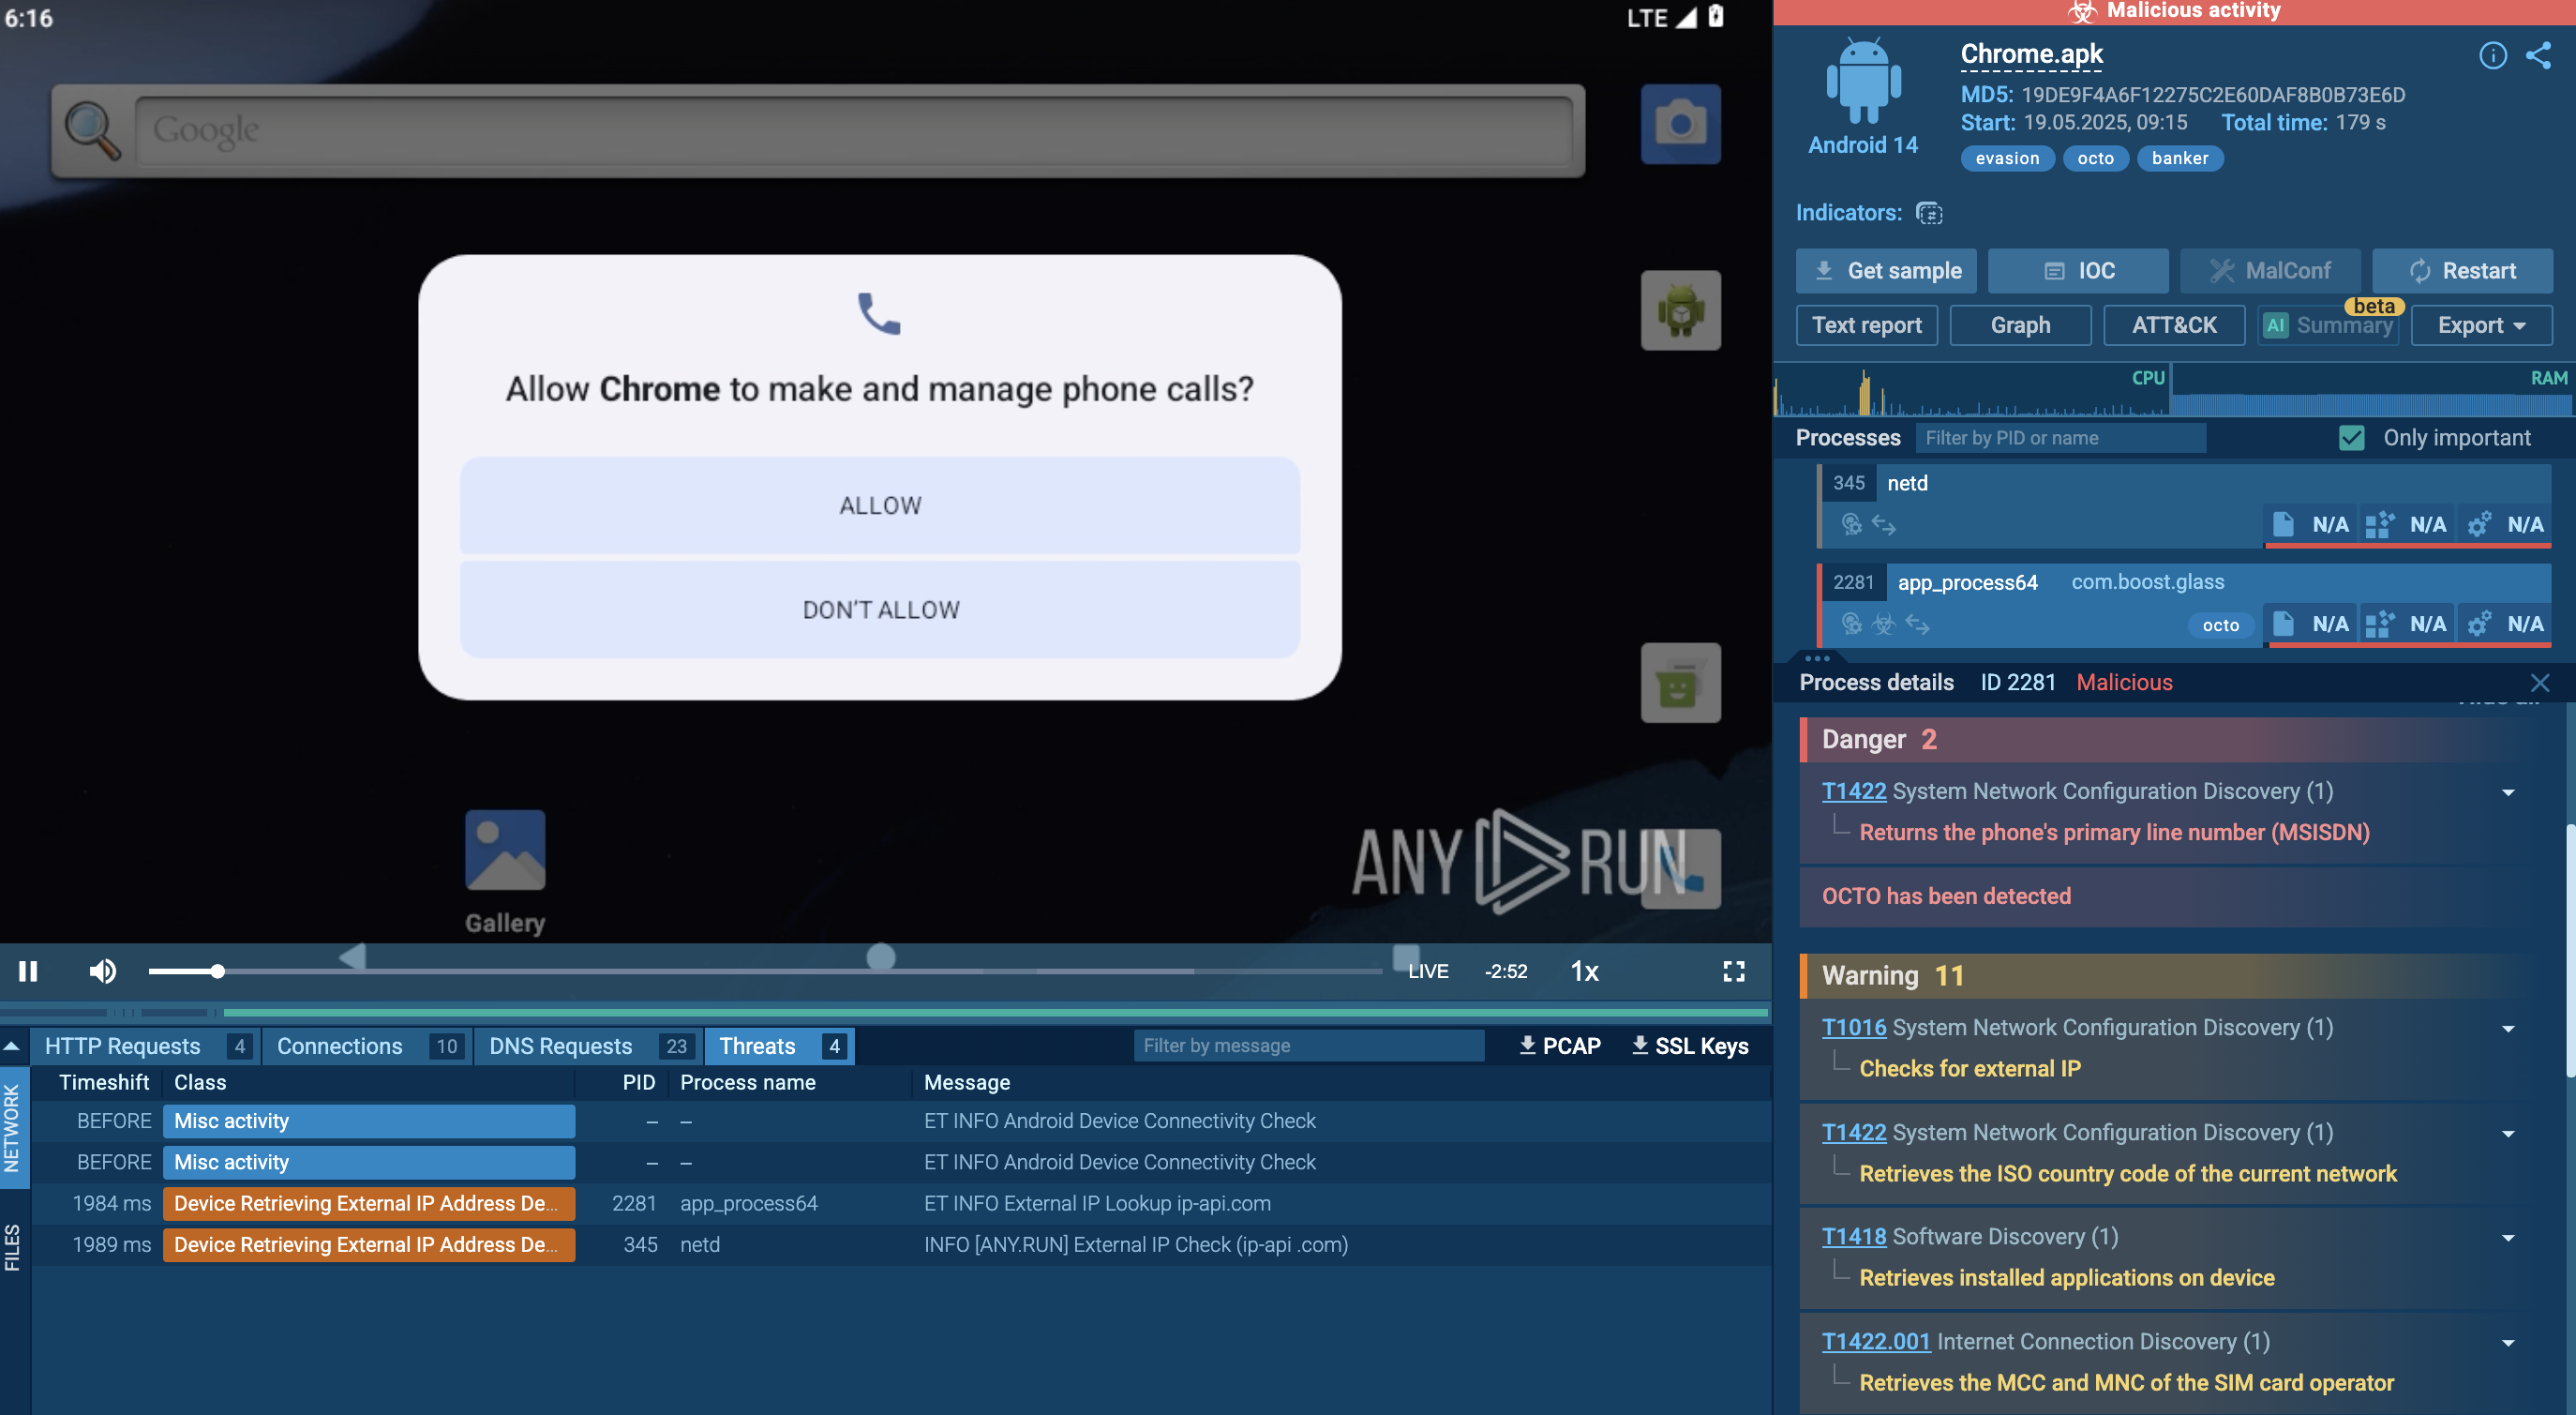
Octo sample analysis in ANY.RUN Sandbox Octo mobile trojan analysis in ANY.RUN's Interactive Sandbox

Octo can also inject fake overlays to steal credentials and uninstall competing or security apps to maintain persistence and avoid detection.

This malware employs advanced methods to avoid detection. It requires no root access using Accessibility Services for control. Its small, modular codebase demonstrates a lightweight footprint helping to avoid detection by traditional antiviruses. Besides, obfuscation is applied, along with multi-layered code encryption, dynamic loading of malicious libraries. Continuous updates by developers and forks from the 2024 source code leak keep Octo ahead of traditional detection methods.

Expose malicious activities and get IOCs with ANY.RUN sandbox

  • Analyze malware in Windows 7, 10, and 11 VMs
  • Interact with files and links, just like on your own computer
  • Work in a private team space with your colleagues
Request 14-day free trial

What are the best-known Octo attacks?

While many campaigns are not publicly attributed due to the nature of mobile malware distribution, several have been documented by security vendors and researchers.

Year Campaign / Actor Region Method Targets
2022 Coper (Octo variant) Latin America Fake banking apps, smishing Colombian & Peruvian banks
2022 Octo advertised on dark web Global Malware-as-a-Service (MaaS) European banks
2022 Fake Chrome Update Global Smishing, fake update Generic users, credential theft
2022–23 Google Play fake apps Global Dropper apps Banking and crypto users

Gathering Threat Intelligence on Octo malware

Octo can be detected by such indicators as C2 domains, IPs, and unusual DNS traffic. Among the behavioral indicators, analysts should pay attention to background services that relaunch on boot, the use of Accessibility APIs, and unexpected overlays over banking apps. Its APK signatures include package names often mimicking known apps and typical permissions requests, like SYSTEM_ALERT_WINDOW, BIND_ACCESSIBILITY_SERVICE.

To start gathering actionable data via ANY.RUN's Threat Intelligence Lookup, search for the malware name and its aliases:

threatName:"octo" OR threatName:"exobot*"
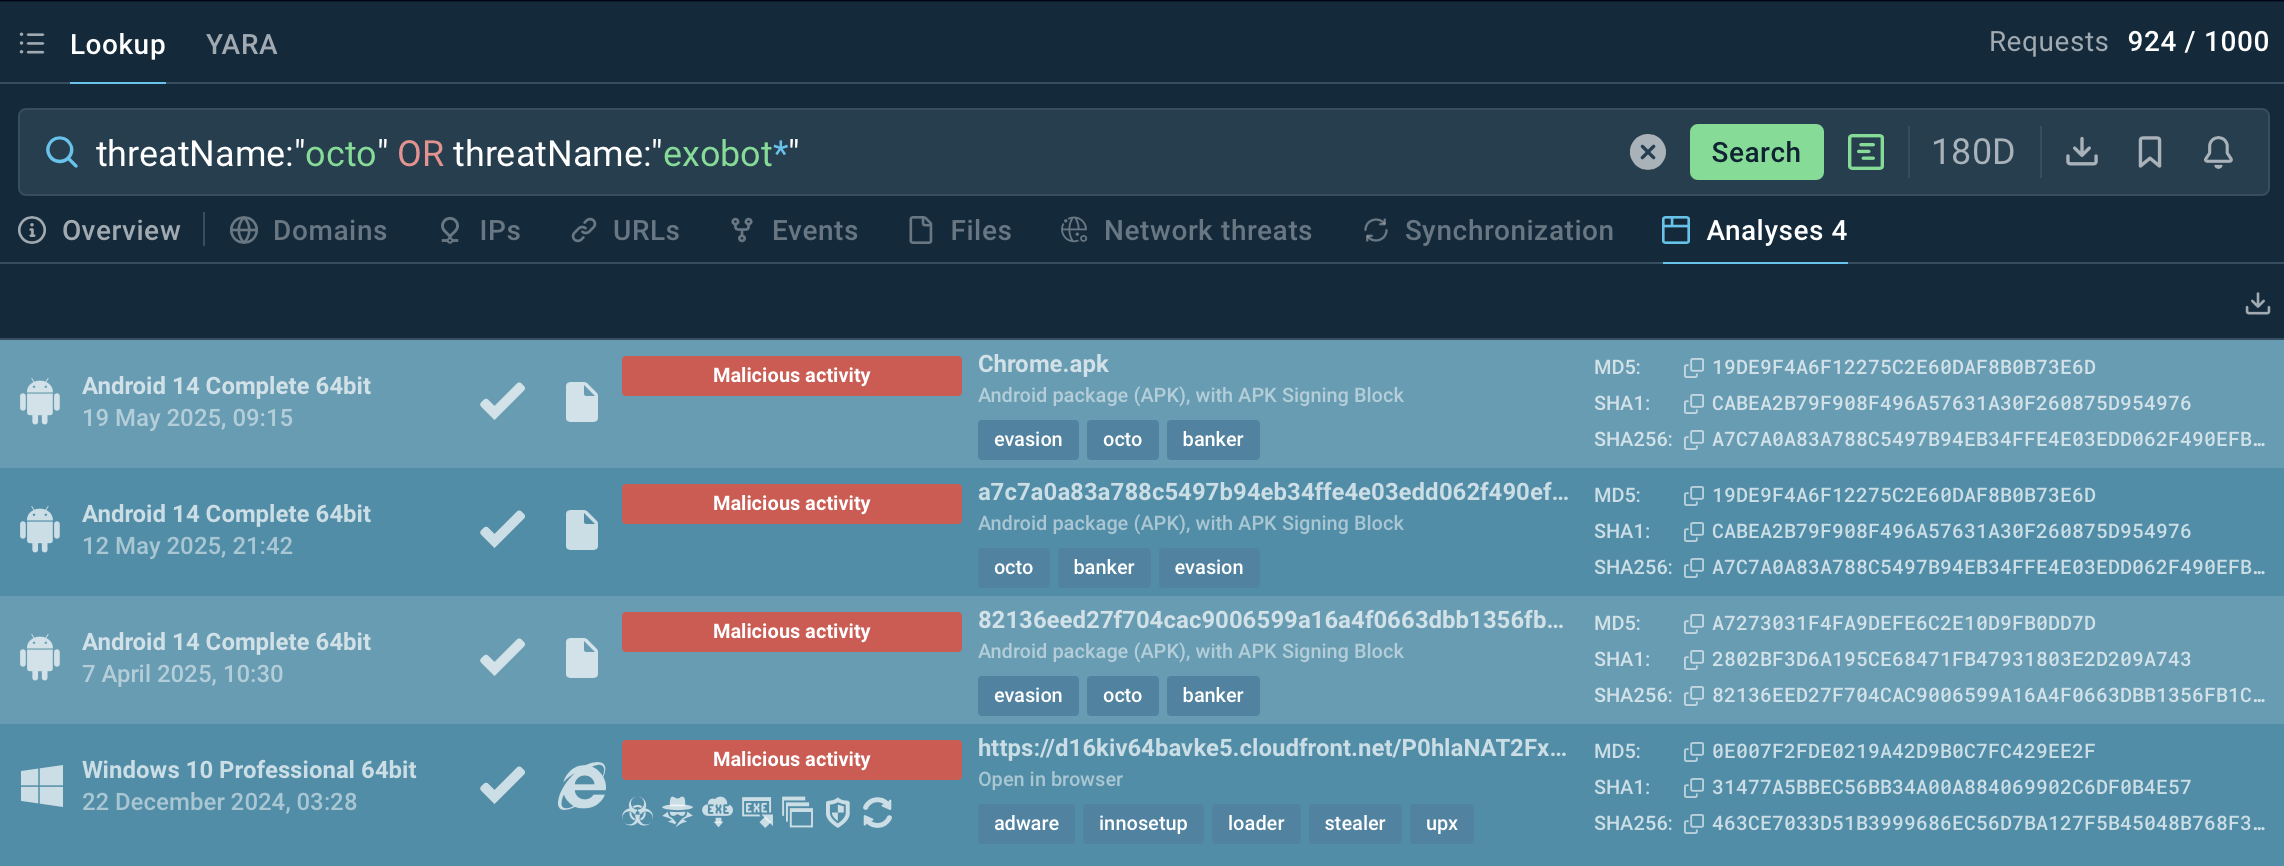
Octo search in TI Lookup Add all of the Octo’s names to a single search request

Select and view analysis sessions to collect IOCs, IOBs, view processes, and study the malware’s TTPs to set up detection and response system, to develop prevention and mitigation strategies.
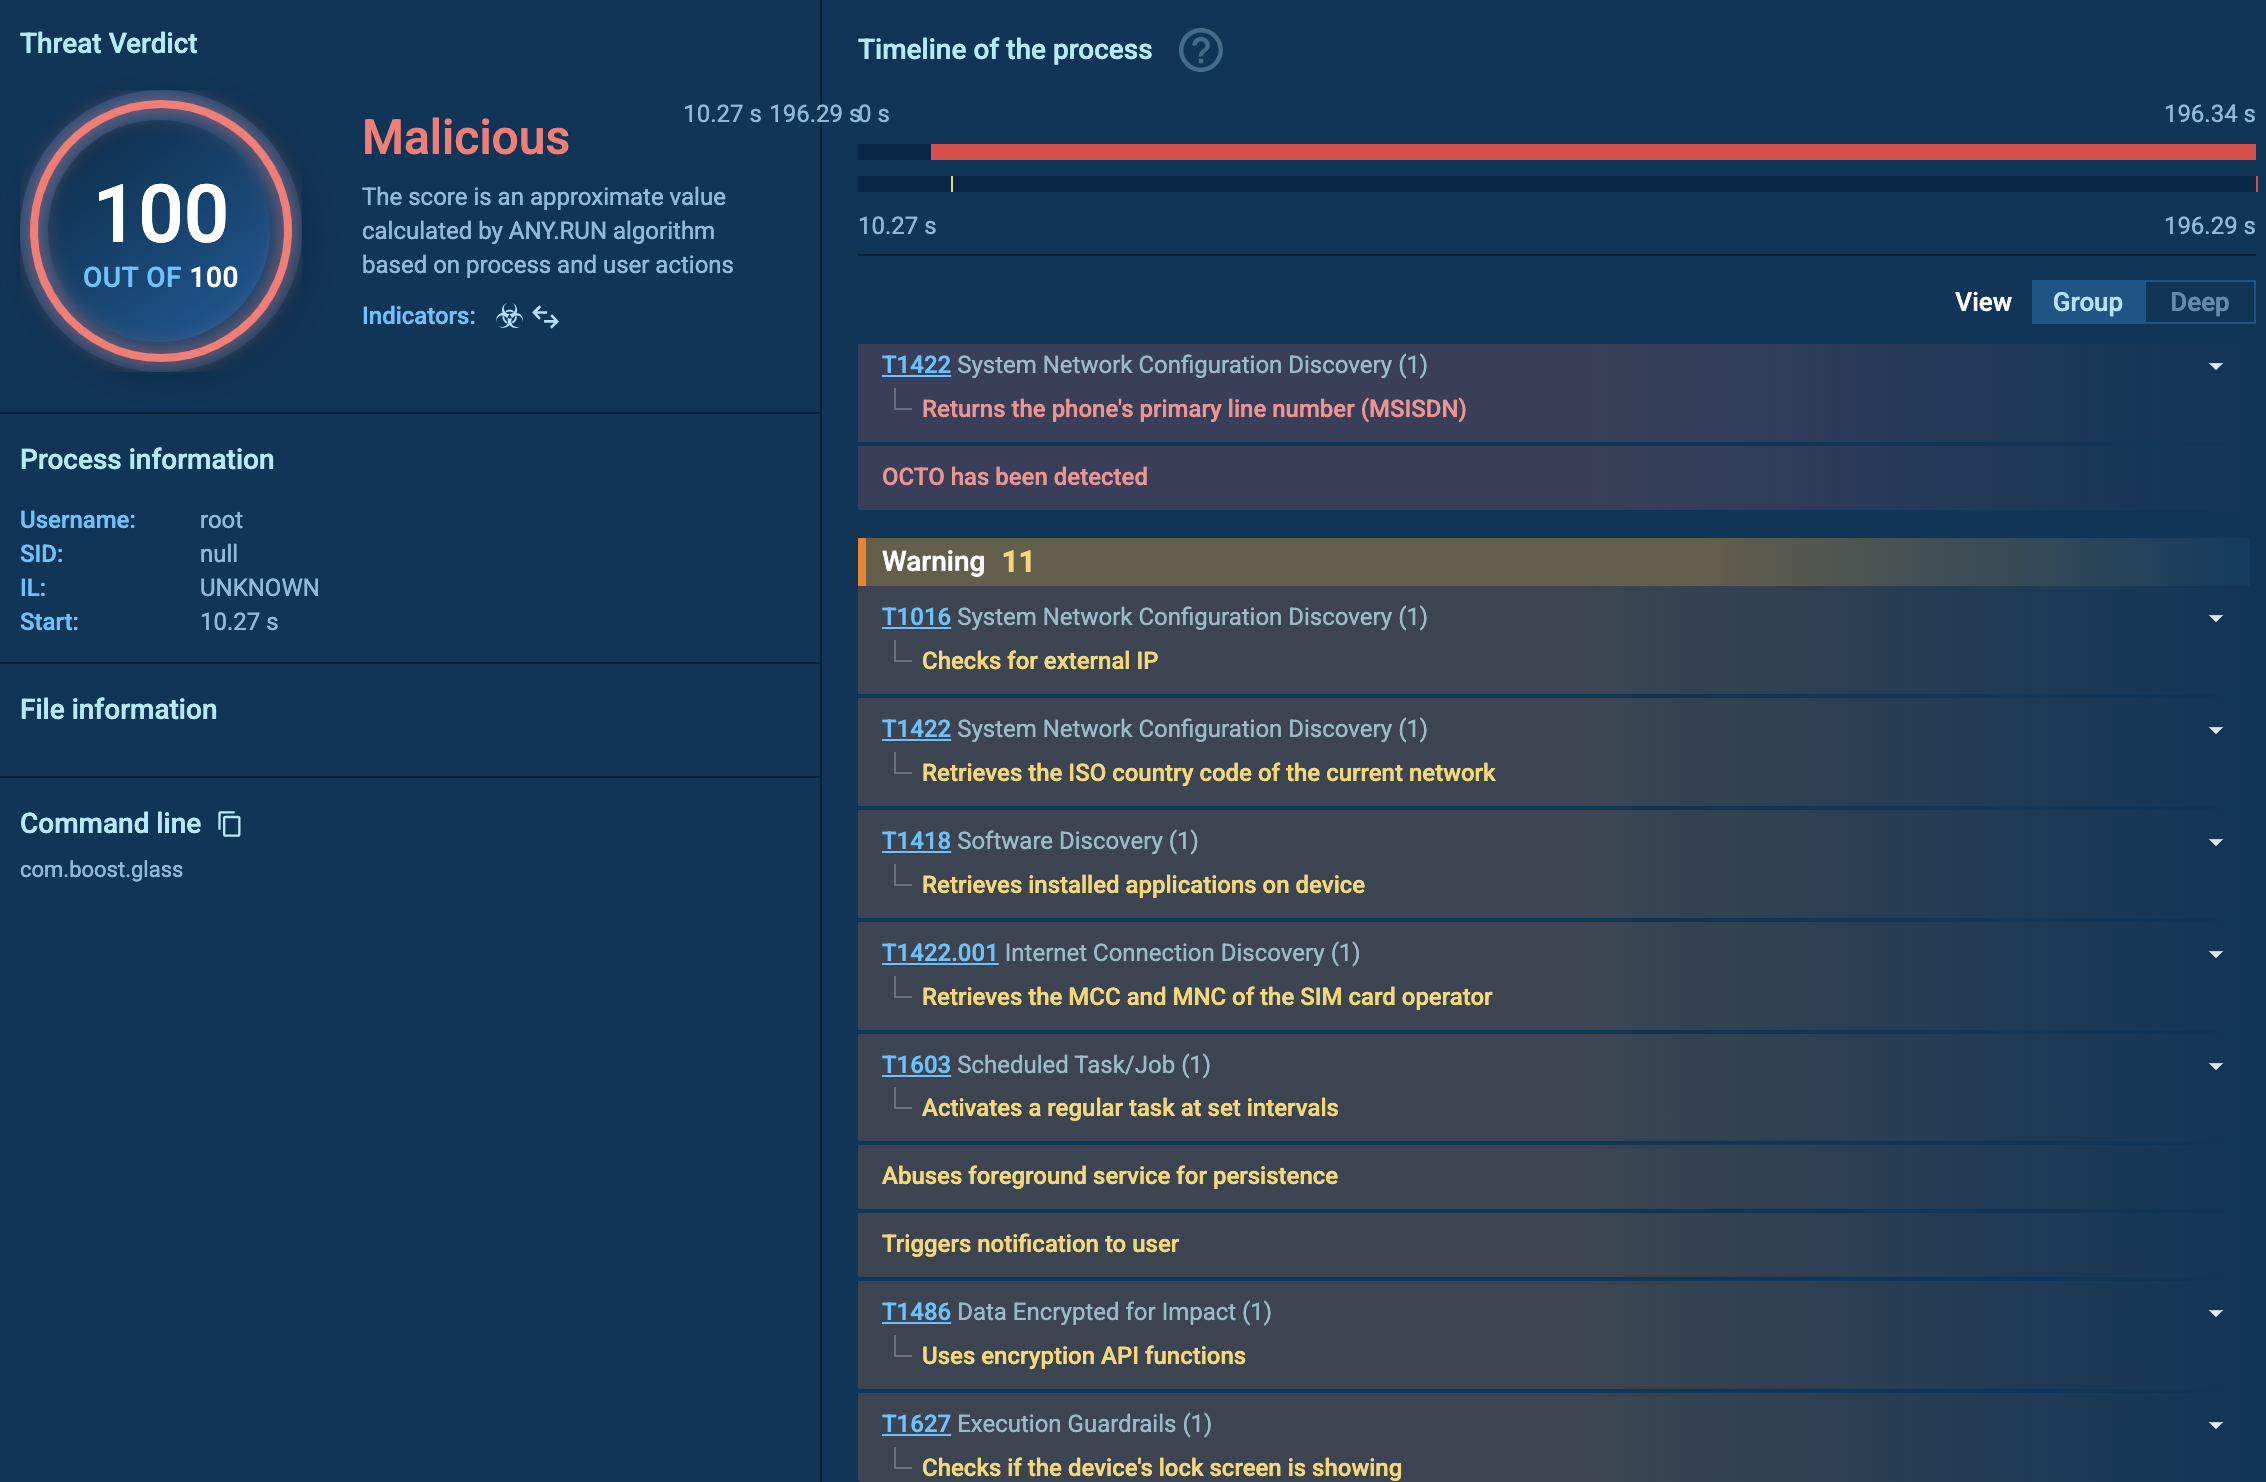
Octo’s malicious process in TI Lookup View malicious processes in detail

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

Octo malware (ExobotCompact / Coper) is one of the most advanced mobile threats in circulation, particularly dangerous because it provides real-time remote access and can bypass many layers of authentication and fraud detection. While it mainly targets banking users, its modularity and stealth make it a viable tool for cybercrime groups and potential APT-style attacks against enterprises. Countering Octo demands robust threat intelligence, proactive user education, and strict device security practices.

Start with 50 requests in TI Lookup to collect IOCs on the evolving Android malware
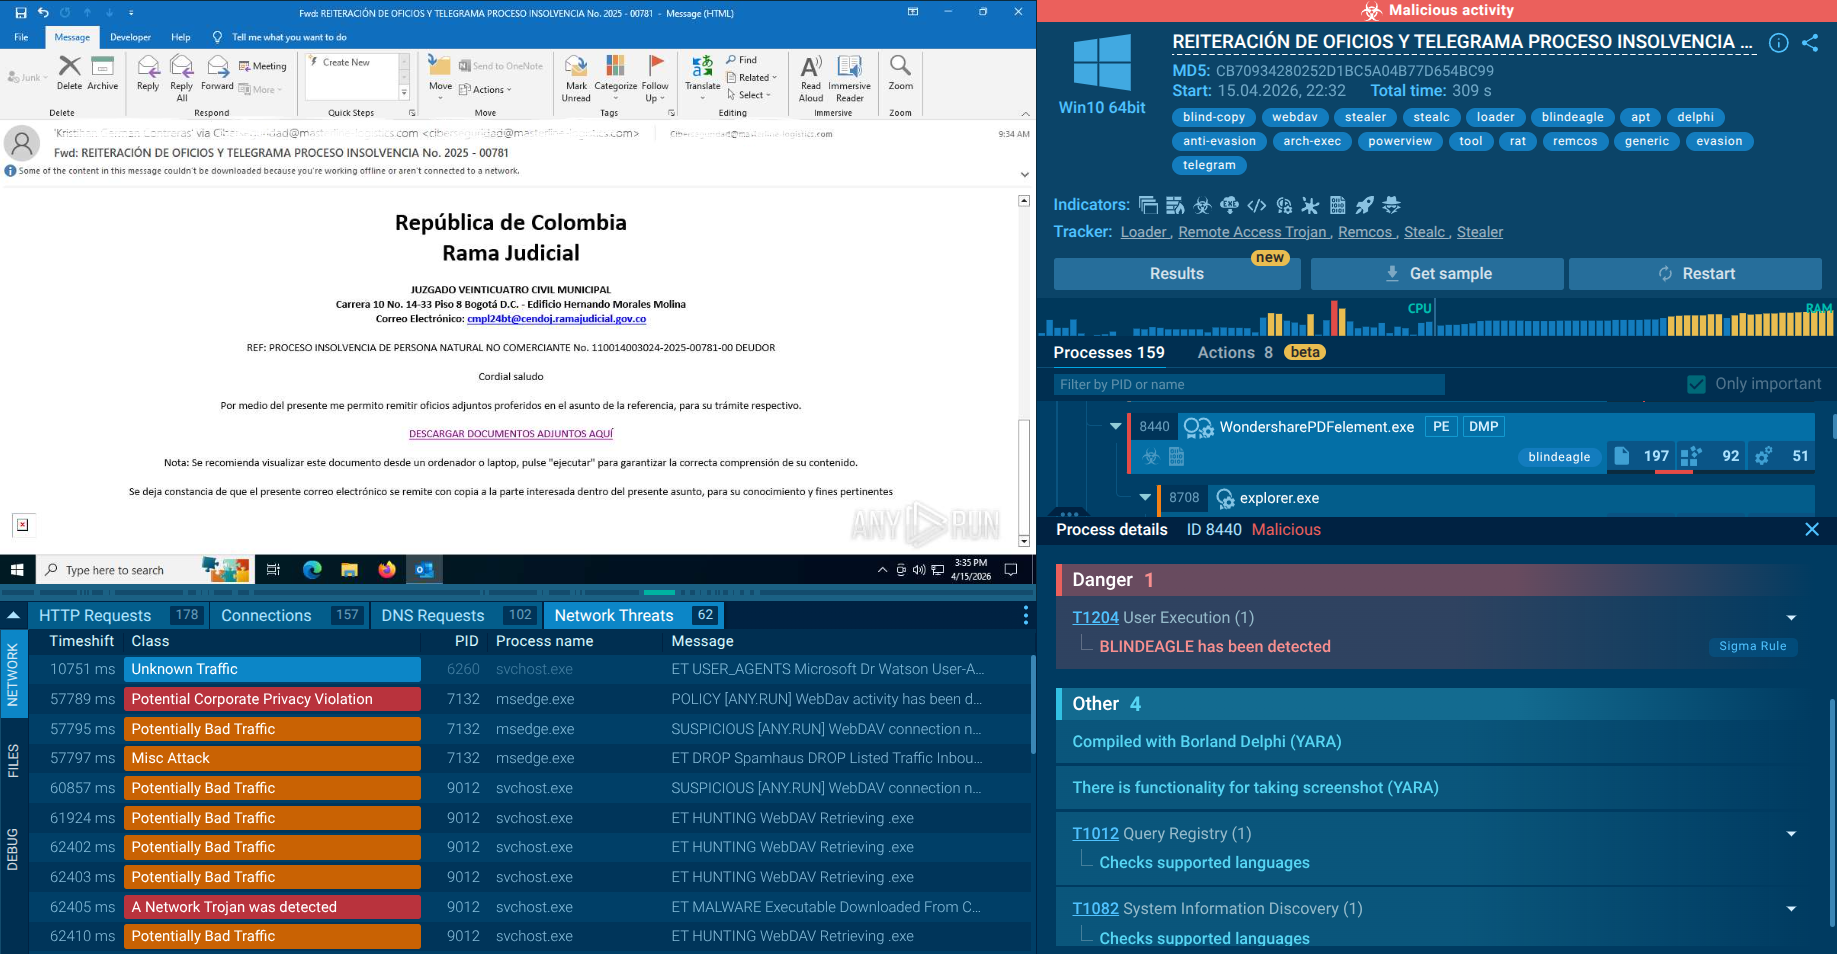
HAVE A LOOK AT

BlindEagle screenshot
BlindEagle
blindeagle
BlindEagle is a cyber threat actor primarily associated with espionage and credential theft campaigns targeting organizations in Latin America, especially Colombia. Active since at least 2018, the group relies heavily on phishing, remote access trojans (RATs), PowerShell scripts, and social engineering to infiltrate systems and maintain persistence. BlindEagle is known for continuously evolving its delivery mechanisms and malware stack to bypass detection and compromise high-value targets.
Read More
Emmenhtal screenshot
Emmenhtal
emmenhtal
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
Read More
Balada Injector screenshot
Balada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
Read More
BlackMatter screenshot
BlackMatter
blackmatter
BlackMatter is a ransomware strain operating as a Ransomware-as-a-Service (RaaS), designed to encrypt files, remove recovery options, and extort victims across critical industries. Emerging in 2021, it quickly became a major concern due to its ability to evade defenses, spread across networks, and cause large-scale operational disruption, forcing security teams to act against a highly destructive and persistent threat.
Read More
Play Ransomware screenshot
Play aka PlayCrypt ransomware group has been successfully targeting corporations, municipal entities, and infrastruction all over the world for about three years. It infiltrates networks via software vulnerabilities, phishing links and compromised websites. The ransomware abuses Windows system services to evade detection and maintain persistence. Play encrypts user files and steals sensitive data while demanding a ransom.
Read More
VanHelsing Ransomware screenshot
VanHelsing is a sophisticated ransomware strain that appeared in early 2025, operating via the Ransomware-as-a-Service (RaaS) model and targeting primarily USA and France. It threatens mostly Windows systems but has variants for Linux, BSD, ARM, and ESXi, making it a multi-platform malware. It is also notable for its advanced evasion techniques, double extortion tactics, and rapid evolution.
Read More