Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

DarkTortilla

165
Global rank
180 infographic chevron month
Month rank
160
Week rank

DarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.

Crypter
Type
Unknown
Origin
1 August, 2015
First seen
23 August, 2026
Last seen

How to analyze DarkTortilla with ANY.RUN

Crypter
Type
Unknown
Origin
1 August, 2015
First seen
23 August, 2026
Last seen

IOCs

IP addresses
135.232.92.137
48.209.138.189
20.190.160.66
74.178.76.54
40.126.32.72
88.221.169.152
88.221.169.205
135.233.45.221
172.211.123.250
57.153.246.3
184.86.251.10
23.216.77.28
172.211.123.249
2.16.241.19
23.11.40.157
4.210.24.68
2.18.66.36
40.126.32.76
135.233.45.223
74.178.76.128
Hashes
1b3d6e1878afbd806dc16b15bf36ea113429b64c7597236f81c91406cf727b1c
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
54a49d9771307f97f1cdcdb468e4a38adebe3f42678a3ad178feab614f2b5bee
245c6e532b24bf98c20e31d5accc290ead3a1e3ba0b5c2c56f242456e775c75a
ffab1d58dd5ce0909e31822429e4cc913eed44f2ca0213adbf848826e91b231e
2e79afb8eec711792849b7b0f49a32f78791958bd63c53ad3b825011bdc26261
19533f322dc1161595eb0da438d8987867e34cf646533cb42359990d0f700696
67dceccb016d05af91872e29d18d67f22e93586eacf8a316ec15940dfbdf2769
96774b1fbe41acbba3a3cd0474a1eed4413e1e05c0007d4949cc4115e3b54a74
caf95e611d3d17607704c847d663afc0b1552bfe03d215d87c57ed3fec969d2a
0e4e0247476003c3efef81eba6fdc6c98876d15ae4fd81994a2a58c598c2011d
e0d04cb94620739c101d4e83f3003afa793978fd4433d2647fe71c1b0c568356
50375ba71086bf28c2012db1f8fbf683430b35ec94425a0aff0de8f23ed7f8be
1820b4bac4441a499f20f5fd6730b4a5a8167c837a1f93a7c3dae86fee27dfee
df482ab336eebe1932e5a8bb4327d49040ee6386d4b2fb1e91efaaf2177a717c
d1a1b7b777f59096d297717a197e7b56c04214629dcfa59584d6c75f6a94ee19
ea6619931941b56b8c736d2000beab0d9727ef0839341e1ffefaffb7abe7b54a
57000db41942e88e8998d8227595a16b4e2d3dc174d0c92e17a1982075df8be5
989093655a9a46c4254c45fcf5cc2f0a4638dd8ff9e82cde854c817c2d222b92
4f1a58a22c32a0ffc513c8476522b48b1c5d95792a2f91c4e28d04767f3189bb
Domains
slscr.update.microsoft.com
crl.microsoft.com
client.wns.windows.com
settings-win.data.microsoft.com
google.com
licensing.mp.microsoft.com
ocsp.digicert.com
fe3cr.delivery.mp.microsoft.com
www.microsoft.com
www.bing.com
login.live.com
watson.events.data.microsoft.com
go.microsoft.com
activation-v2.sls.microsoft.com
nexusrules.officeapps.live.com
oneocsp.microsoft.com
self.events.data.microsoft.com
api.ipify.org
fd.api.iris.microsoft.com
arc.msn.com
URLs
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/rst2.srf
https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://watson.events.data.microsoft.com/telemetry.request
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://settings-win.data.microsoft.com/settings/v3.0/waas/featuremanagement?isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&currentbranch=vb_release&accountfirstchar=&activationchannel=retail&oemmodel=dell&flightring=retail&attrdataver=186&installlanguage=en-us&osuilocale=en-us&webexperience=1&flightingbranchname=&chassistypeid=1&osskuid=48&app=cdm&installdate=1661339444&appver=&osarchitecture=amd64&defaultuserregion=244&telemetrylevel=1&osversion=10.0.19045.4046&devicefamily=windows.desktop
https://licensing.mp.microsoft.com/v7.0/licenses/content
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Darktortilla crypter?

DarkTortilla is a crypter that has been utilized since 2015 to deliver some of the most popular RATs, such as NanoCore, AsyncRat, and AgentTesla, as well as information stealers like RedLine. It is equipped with obfuscation and anti-analysis functionality.

DarkTortilla is a multi-stage crypter. To deploy on the target host and start operating, it relies on a loader and a .DLL core processor. It can run its harmful payload entirely in the computer's memory (RAM). This means it does not need to save any files to the hard drive, making it more difficult for traditional security software to detect.

The crypter can make use of social engineering by displaying fake messages to users that look like real software errors or updates. This tricks victims into thinking that is is a safe and legitimate program. By doing this, the malware can continue to operate without raising suspicion

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

DarkTortilla crypter execution process

Let's upload a sample of DarkTortilla to ANY.RUN sandbox to see how it operates.

The infection begins when the victim unknowingly runs the initial loader, which is often concealed within an archive or a malicious document. This loader is responsible for retrieving the .NET-based DLL (core processor). The DLL might be embedded within the loader's resources or downloaded from external sources like Pastebin.
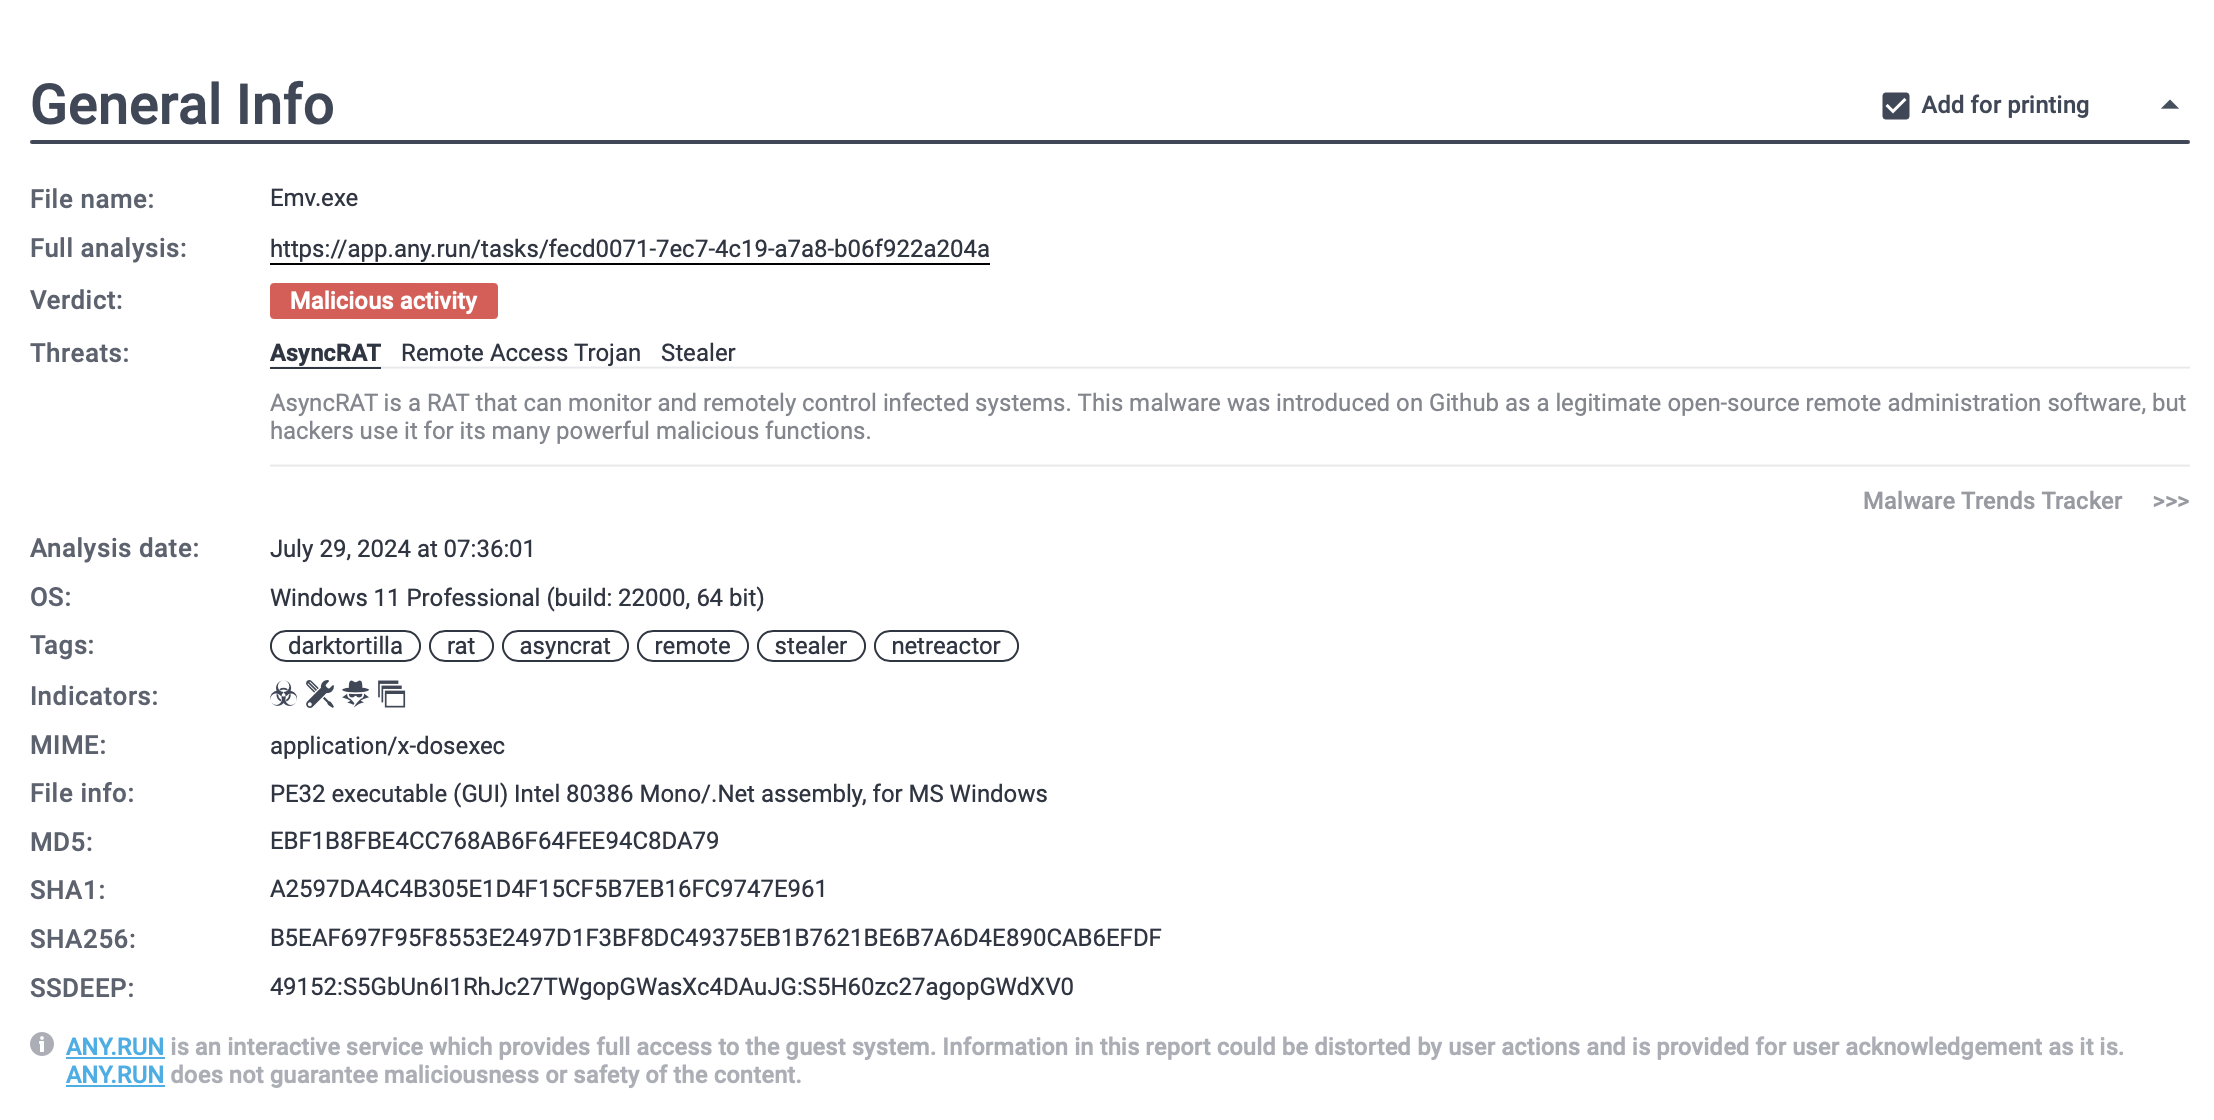
DarkTortilla report in ANY.RUN DarkTortilla threat report generated by ANY.RUN

Once the initial loader is executed, it decodes and loads the core processor. This core component performs several tasks based on its configuration, including:

  • Displaying Fake Messages: It shows fake message boxes to deceive users, making them believe the crypter is a real program.
  • Evading Detection: It performs checks to detect if it is running in a virtual machine or a sandbox environment, which are commonly used by security researchers.
  • Establishing Persistence: It ensures that the malware stays on the system by modifying system files or using techniques like moving its execution to the Windows %TEMP% directory. This makes it difficult to remove the malware completely. It can achieve persistence by modifying user .LNK files' target path to point to its executable. DarkTortilla ensures that it can execute again even after a system reboot. This further complicates the removal process and helps the malware remain active on the infected system.

The core processor then injects the main malicious payload into the system. This payload can be various types of malware, such as Remote Access Trojans (RATs) or information stealers.
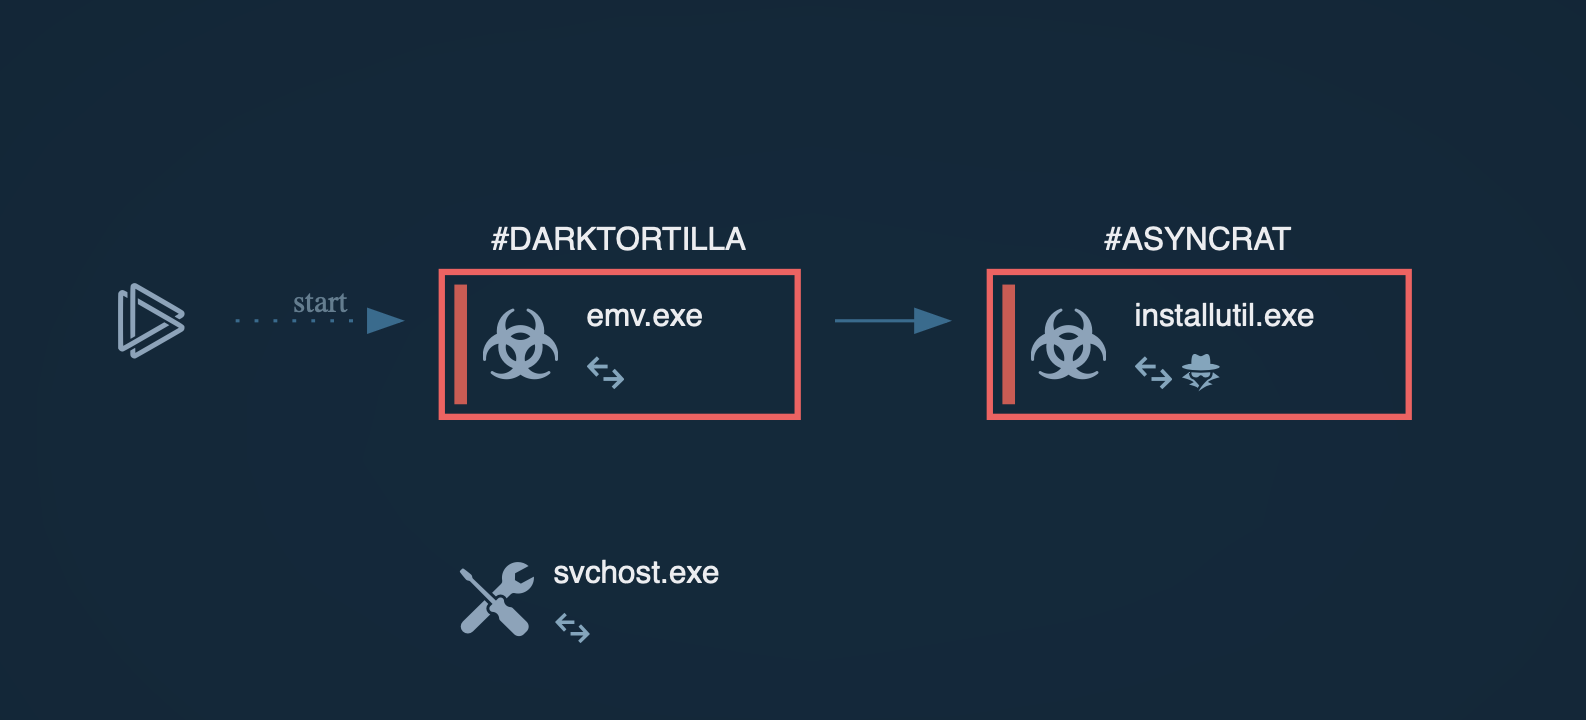
DarkTortilla graph in ANY.RUN Process graph generated by ANY.RUN allows us to see the main process of AsyncRAT injection through DarkTortilla

In our case, the payload is AsyncRAT. The sandbox session lets us see how the injection process is done in memory.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

DarkTortilla crypter delivery methods

DarkTortilla spreads using different methods, yet the two main ones include:

  • Malicious attachments: The attackers send emails that look like they come from trusted sources. These emails usually come with attachments in the form of archives (like .zip or .tar). These files often hide the initial loader that starts the infection process.
  • Fake websites: Another way DarkTortilla can be delivered to the victim's machine is through phishing websites. Users are usually asked to download a file, which then turns out to be a loader.

Conclusion

DarkTortilla’s advanced encryption methods, in-memory execution, and anti-analysis capabilities make it particularly challenging to detect and mitigate. To avoid malware infection by DarkTortilla, it’s important to focus on a combination of security practices, including using a malware sandbox to proactively analyze any suspicious email, file, or link.

The ANY.RUN sandbox provides valuable tools for researchers to analyze and understand threats like DarkTortilla. By using it, security professionals can expose malware and phishing threats in seconds.

Create your free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

Botnet screenshot
Botnet
botnet
A botnet is a group of internet-connected devices that are controlled by a single individual or group, often without the knowledge or consent of the device owners. These devices can be used to launch a variety of malicious attacks, such as distributed denial-of-service (DDoS) attacks, spam campaigns, and data theft. Botnet malware is the software that is used to infect devices and turn them into part of a botnet.
Read More
INC Ransomware screenshot
INC Ransomware is a ransomware-as-a-service (RaaS) spotted in mid-2023. It targets industries like retail, real estate, finance, healthcare, and education, primarily in the U.S. and UK. It encrypts and exfiltrates data demanding a ransom. It employs advanced evasion techniques, destroys backup, and abuses legitimate system tools at all the stages of the kill chain.
Read More
Quasar RAT screenshot
Quasar RAT
quasar trojan rat
Quasar is a very popular RAT in the world thanks to its code being available in open-source. This malware can be used to control the victim’s computer remotely.
Read More
LockBit screenshot
LockBit
lockbit
LockBit, a ransomware variant, encrypts data on infected machines, demanding a ransom payment for decryption. Used in targeted attacks, It's a significant risk to organizations.
Read More
Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More