Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Xeno RAT

65
Global rank
37 infographic chevron month
Month rank
22 infographic chevron week
Week rank

Xeno RAT is an open-source malware mainly distributed through drive-by downloads. The core capabilities of this threat include remote control, keystroke logging, webcam and microphone access. Equipped with advanced utilities, such as Hidden Virtual Network Computing and Socks5 reverse proxy, Xeno RAT is most frequently used in attacks against individual users.

RAT
Type
Unknown
Origin
1 October, 2023
First seen
7 October, 2026
Last seen

How to analyze Xeno RAT with ANY.RUN

RAT
Type
Unknown
Origin
1 October, 2023
First seen
7 October, 2026
Last seen

IOCs

IP addresses
23.11.41.157
48.209.138.189
23.3.89.97
23.194.190.156
20.190.160.65
74.178.76.128
2.21.239.138
23.52.181.212
135.234.160.245
204.79.197.203
188.114.97.3
74.178.240.51
48.192.1.65
172.187.86.72
23.59.18.102
48.209.6.48
2.16.164.130
104.21.69.74
48.192.1.64
135.233.95.144
Hashes
60c1da5e2e7ef58cef79504e7209086509d74d27ef347ea59a7f432c4cf56041
f503f62c81c5ca541d6b3cca94537f372a2e83924829d0b8b889149baf2dca69
9a30667f8a16794f3a5c4301bc1208356a3b9104dd2e3bbacbfe7ca62d05289e
6639f12e93d569c3cf0d37d2971fe589744935f65db168addd60dfab145e4010
f81fc8574daf56e8ad9183e60d56e829ebd123976e095a09eb30beb9bef2113a
4237080f2855a49462cf9ae6be03465afa37f0b74ee4a523ecde1128b386916c
cbe2fbb0b1c6ba350935aee9c50646b7413f9372725bdfbabb83b40df8f9d87c
446a6087825fa73eadb045e5a2e9e2adf7df241b571228187728191d961dda1f
f233e9ece75d7d63e5f4491f5960c713b0940f5244743b057b2894d097db7f36
52ff7fad0986fe2b9c8232534c7abfab614772cf6589a43260b9fd85b0e96590
c832515aa85a199fbb3454fb848f624f8a023464fc6997e1b24a4161b6436c10
e03e62489ca2915b62fb188016a55110cccf10abaa6adb784fc46d2b05a21743
bf8fe504ff92a30b4acf9564638893d886a04221affc609800b2c77a3f8d9632
83ad6ea5c240002d70a2fa3df1f50a91d87dcc5cc157e71a3c845748fbe61ef3
aeed7303001c2d38b4fdb580857e6110a1131faaf2e5e10e41221abe37ad6ee0
154fb975b0696e7c9105736f9638f4cc5e9a84a928620ba9ec880d87a4e7206f
a22436bd4f5dc7ad5055ad707ceee43c0b8a6ff728aedc8d20b9e15e0736a8fa
e15810d889f7da2466132bd11be3faeada6ced424c65c7d29ba31a95bfa25ecd
82b041b34ca7e3511c2fa9280f34bc465ea73eedde2c96dfb133c8ee4dc1387b
b1ad932b54b08d4d08960fb5b439f83373de869ceaaa4e2e8365b409e9af4482
Domains
ecs.office.com
www.xn88.network
www.microsoft.com
google.com
www.bing.com
watson.events.data.microsoft.com
th.bing.com
activation-v2.sls.microsoft.com
settings-win.data.microsoft.com
self.events.data.microsoft.com
crl.microsoft.com
fe3cr.delivery.mp.microsoft.com
client.wns.windows.com
xn88.network
slscr.update.microsoft.com
oneocsp.microsoft.com
login.live.com
ocsp.digicert.com
www.millioncasinobonus.info
millioncasinobonus.info
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://xn88.network/
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://xn88.network/index.php
https://login.live.com/ppsecure/deviceaddcredential.srf
http://xn88.network/wp-admin/
http://xn88.network/wp-json/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
http://xn88.network/wp-login.php
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://watson.events.data.microsoft.com/telemetry.request
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 1024
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 2815
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 10289
comments 0

What is Xeno RAT malware?

Xeno RAT is an open-source remote access trojan (RAT) distributed openly through GitHub. The creator behind this malicious software states that it was created for educational purposes only. This, however, does not prevent threat actors from leveraging it in their attacks to steal sensitive data and spy on their victims.

Since Xeno RAT is available free-of-charge, there are many amateur and experienced attackers that employ it. Since 2023, the malware has been involved in several campaigns primarily targeting individual users through drive-by downloads.

Xeno RAT is written in C# and is intended to operate on Windows systems. Since the malware is being continuously updated, it poses a serious threat to organizations and users around the world.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Xeno RAT malware technical details

Xeno RAT’s range of capabilities is similar to that of other RATs, such as Asyncrat and njRAT. Some of the malicious activities that can be performed using Xeno RAT include:

  • Xeno RAT allows attackers to remotely control a victim's computer, including accessing and modifying files, installing and uninstalling software, and executing commands.
  • The malware can record every keystroke made on the infected computer, including in the offline mode.
  • One of the standout features of Xeno RAT is the ability to access the webcam and microphone of the infected computer, allowing them to spy on the victim and their surroundings.
  • The malware can be used to steal files from the device, as well as passwords stored in web browsers, email clients, and other software.
  • Attackers using Xeno RAT can also reboot the infected computer, turn off its display, and edit the registry.

Out of all features available to the attackers using the Xeno RAT malware, Hidden Virtual Network Computing offers the most extensive functionality for conducting malicious activities. This utility lets criminals not only take full control of the victim’s computer but also do it stealthily and completely without their notice.

The Socks5 reverse proxy feature of Xeno RAT allows attackers to route their network traffic through a compromised computer, effectively hiding it.

Xeno RAT usually achieves persistence on the compromised system using Scheduled Tasks. It has also been observed to leverage process injection to evade detection.

Xeno RAT execution process

To see how Xeno RAT operates, let’s upload its sample to the ANY.RUN sandbox.

The execution chain of Xeno RAT may be relatively simple, involving only one or two processes, but it can also become complex with the utilization of multiple processes, including built-in OS tools.
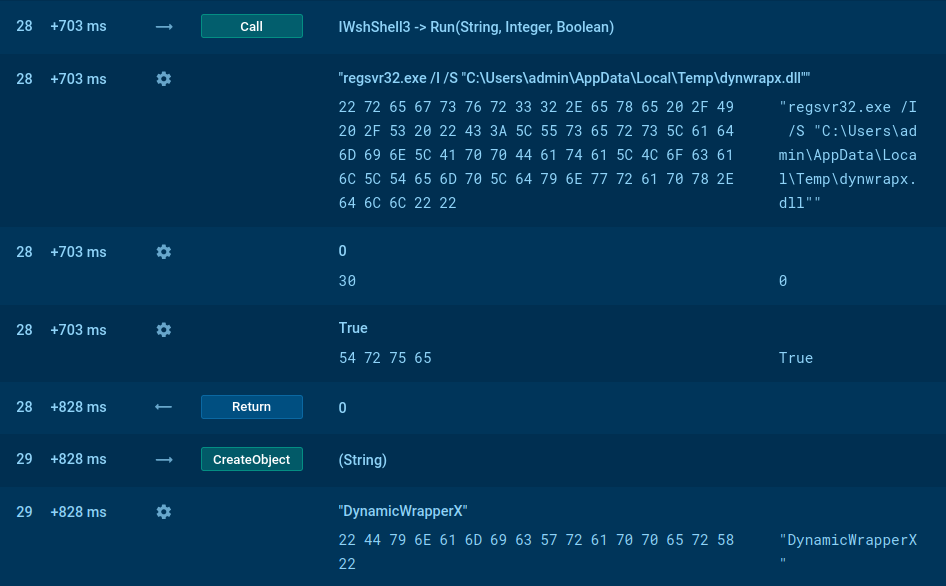
XenoRAT scripts in ANY.RUN Xeno RAT script analysis in ANY.RUN

The main malicious activities are carried out by the injected RegAsm process.

In our example, the execution involves multiple processes such as WScript.exe, regsvr32.exe, and RegAsm.exe. The malware creates files in the Startup directory to achieve persistence and loads the dynwrapx.dll (DynamicWrapperX) file. These activities can be monitored using Script Tracer.

For persistence and stealth, XenoRAT can bypass User Account Control (UAC) and maintain its presence even after system reboots using startup functions. It spreads primarily through phishing, exploiting software vulnerabilities, and other typical methods such as downloading from compromised websites or deceptive advertisements.
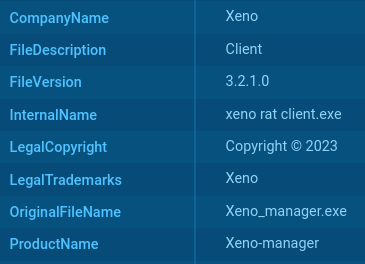
XenoRAT metadata in ANY.RUN Xeno RAT metadata in ANY.RUN

Sometimes, Xeno RAT builds may inadvertently reveal themselves by naming directories after the malware, such as "xeno rat client" or "XenoManager," or by embedding its name in PE metadata, for instance, as the company name or product name.

Xeno RAT malware distribution methods

As for the most common delivery methods, drive-by downloads constitute the main vector of Xeno RAT attacks. Individual users are the primary target of these. As a result, to trick their victims into downloading and running the malicious software, threat actors may disguise it as video games or software updates.

Conclusion

Xeno RAT’s wide range of features and capabilities, including HVNC, make it a versatile tool for conducting cyber attacks. The open-source nature of this threat highlights the importance of having proper security measures in place to prevent potential attacks.

Using a sandbox like ANY.RUN to analyze suspicious files and URLs should one of such measures. The cloud-based service allows you to detonate any malicious file in a safe and secure environment, while also having the ability to interact with the system just like on your own computer. Use ANY.RUN to study the behavior of malware, understand its TTPs, and collect indicators of compromise.

Create your ANY.RUN account – it’s free!
HAVE A LOOK AT

BlackMatter screenshot
BlackMatter
blackmatter
BlackMatter is a ransomware strain operating as a Ransomware-as-a-Service (RaaS), designed to encrypt files, remove recovery options, and extort victims across critical industries. Emerging in 2021, it quickly became a major concern due to its ability to evade defenses, spread across networks, and cause large-scale operational disruption, forcing security teams to act against a highly destructive and persistent threat.
Read More
Gunra screenshot
Gunra
gunra
Gunra ransomware, a financially motivated threat actor that emerged in April 2025, deploys double-extortion tactics to encrypt victims' data and threaten leaks of exfiltrated information, primarily targeting Windows and Linux systems across healthcare, manufacturing, and other sectors worldwide.
Read More
Crypto malware screenshot
Crypto malware
miner xmrig jsminer
Crypto mining malware is a resource-intensive threat that infiltrates computers with the purpose of mining cryptocurrencies. This type of threat can be deployed either on an infected machine or a compromised website. In both cases the miner will utilize the computing power of the device and its network bandwidth.
Read More
BlindEagle screenshot
BlindEagle
blindeagle
BlindEagle is a cyber threat actor primarily associated with espionage and credential theft campaigns targeting organizations in Latin America, especially Colombia. Active since at least 2018, the group relies heavily on phishing, remote access trojans (RATs), PowerShell scripts, and social engineering to infiltrate systems and maintain persistence. BlindEagle is known for continuously evolving its delivery mechanisms and malware stack to bypass detection and compromise high-value targets.
Read More
Tycoon 2FA screenshot
Tycoon 2FA
tycoon
Tycoon 2FA is a phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) protections, particularly targeting Microsoft 365 and Gmail accounts. Its advanced evasion techniques and modular architecture make it a significant threat to organizations relying on MFA for security.
Read More
SalatStealer screenshot
SalatStealer
salatstealer
SalatStealer, also known as WEB_RAT or Salat Stealer, is a Go-based information-stealing malware targeting Windows systems. It operates as a Malware-as-a-Service (MaaS) focusing on harvesting browser credentials, cryptocurrency wallets, and session data from popular applications like Telegram and Steam.
Read More