Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
63
Global rank
69 infographic chevron month
Month rank
65 infographic chevron week
Week rank

DarkComet RAT is a malicious program designed to remotely control or administer a victim's computer, steal private data and spy on the victim.

RAT
Type
France
Origin
12 February, 2008
First seen
10 October, 2026
Last seen
Also known as
Breut
Fynloski
klovbot

How to analyze DarkComet RAT with ANY.RUN

RAT
Type
France
Origin
12 February, 2008
First seen
10 October, 2026
Last seen

IOCs

IP addresses
158.178.201.63
40.126.31.130
199.232.210.172
48.209.138.189
92.123.104.67
52.123.243.67
150.171.109.104
192.178.183.94
23.207.210.139
23.53.40.11
150.171.109.101
4.150.223.97
150.171.27.10
20.42.65.90
23.194.190.151
208.95.112.1
23.52.181.212
150.171.28.11
18.244.18.32
135.232.92.137
Hashes
b9fa2d52a4ffabb438b56184131b893b04655b01f336066415d4fe839efe64e7
225d669e47eb14d8c969799c92aaef27b66cd984872ea09284e48db46521e651
75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
fd4c9fda9cd3f9ae7c962b0ddf37232294d55580e1aa165aa06129b8549389eb
3dbd2c90050b652d63656481c3e5871c52261575292db77d4ea63419f187a55b
b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
a41670d52423ba69c7a65e7e153e7b9994e8dd0370c584bda0714bd61c49c578
54241ebe651a8344235cc47afd274c080abaebc8c3a25afb95d8373b6a5670a2
bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
de6d7b7c2427ec4e738407d7834b71941f69166b030355e00f325ff1391df5a1
cf26310b073b0891996ecd761c6cb53f00193dee524213a9fb34225d636ec4b7
aa12205b108750cf9fa0978461a6d8881e4e80da20a846d824da4069d9c91847
Domains
fys2b9ubqn.localto.net
ntp.msn.com
img-s-msn-com.akamaized.net
static.edge.microsoftapp.net
activation-v2.sls.microsoft.com
settings-win.data.microsoft.com
config.edge.skype.com
www.bing.com
browser.events.data.msn.com
c.msn.com
edge-cloud-resource-static.azureedge.net
edge.microsoft.com
update.googleapis.com
assets.msn.com
api.edgeoffer.microsoft.com
oneocsp.microsoft.com
go.microsoft.com
srtb.msn.com
sb.scorecardresearch.com
c.pki.goog
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:ntt7b6l_guffoqizn3qkmu4pybder4dro0-vc_lb4v8&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
http://c.pki.goog/r/gsr1.crl
http://c.pki.goog/r/r4.crl
http://c.pki.goog/we1/qon3-paxuq8.crl
https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0
https://copilot.microsoft.com/c/api/user/eligibility
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
https://ntp.msn.com/edge/ntp?locale=en-us&title=new%20tab&dsp=1&sp=bing&startpage=1&pc=u531
https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1ukivs.img?w=16&h=16&q=100&m=6&f=png&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1ql42j?w=16&h=16&q=100&m=6&f=png&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1sc3ex.img?w=64&h=64&q=60&m=6&f=jpg&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1tqbxn.img?w=64&h=64&q=60&m=6&f=jpg&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1v258b.img?w=64&h=64&q=60&m=6&f=jpg&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1qb56j.img?w=64&h=64&q=60&m=6&f=jpg&u=t
https://img-s-msn-com.akamaized.net/tenant/amp/entityid/aa1qotil.img?w=64&h=64&q=60&m=6&f=jpg&u=t
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 6005
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 7821
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 11434
comments 0

What is DarkComet RAT?

DarkComet is a remote access trojan developed by Jean-Pierre Lesueur in 2008. According to him, the program was never intended to be used illegally. But it got viral in 2012 after the Syrian incident: the government used the RAT to spy and destroy the protestor’s network.

It’s a standard remote control malware – a hacker rules over the infected computer and gets access to the camera and microphone. That is why DarkComet serves as a tool to monitor victims’ actions, take screenshots, do key-logging, or steal credentials.

The malware has had several versions, and DarkComet 5.3.1 is still available in 2022.

Crooks try to make targets download and run the RAT using different social engineering techniques. And in some cases, attackers use DarkComet to deliver other malicious programs to the infected machine. Hackers may involve the victim machine in a botnet scheme, such as sending spam.

DarkComet malware analysis

ANY.RUN allows researchers to analyze DarkComet samples and monitor the malware’s activity in real-time using an interactive sandbox
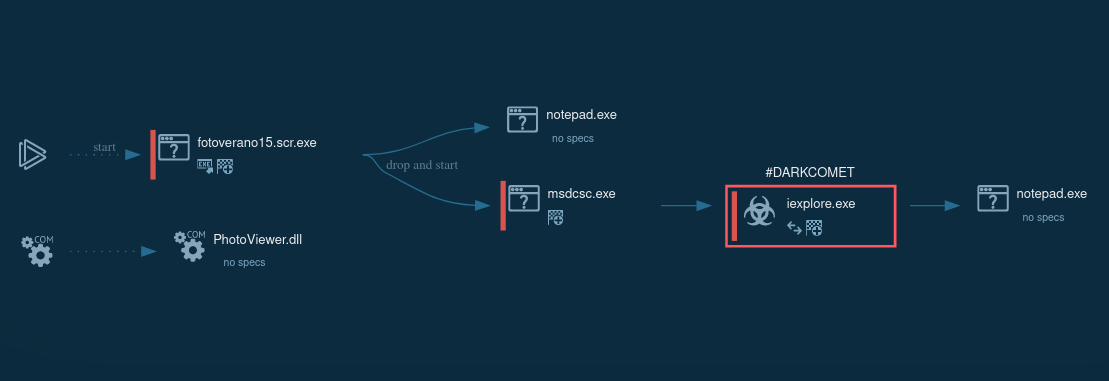
darkcomet rat process graph

Figure 1: Process graph of DarkComet execution generated by ANY.RUN

DarkComet Execution process

DarkComet has a typical RAT execution.

The infected system connects to the hacker’s computer and gives the attacker full access. Crooks may exploit all the system's features: the infected machine is ready to get packets and perform the commands.

Systems communicate via TCP to the chosen DarkComet malware port on the selected IP/domain. Then C&C traffic begins with RC4-256 encryption.

The execution process of the DarkComet varies depending on the sample and version. The most straightforward execution is just one process that makes all activities in the infected system.

In some cases, malware may use system utilities to defend against evasion or persistence. For example, in this task, it uses the T1564.001 technique: malware starts attrib.exe through cmd.exe to hide the main executable. In the system process, iexplorer was injected with malicious code and provided the main malicious activity afterward.

Distribution of DarkComet malware

To trick people into downloading and installing programs such as Quasar RAT, njRAT, and DarkComet cybercriminals use:

  • other trojans
  • suspicious file or software download channels
  • fake software updates and/or unofficial activation tools
  • phishing

Emails may include malicious content in various formats like Microsoft Office documents, PDF documents, .exe files, ZIP and RAR archives, JavaScript files, etc.

After a user is tricked into downloading and then opening a file, it installs other malware.
How to detect DarkComet using ANY.RUN?

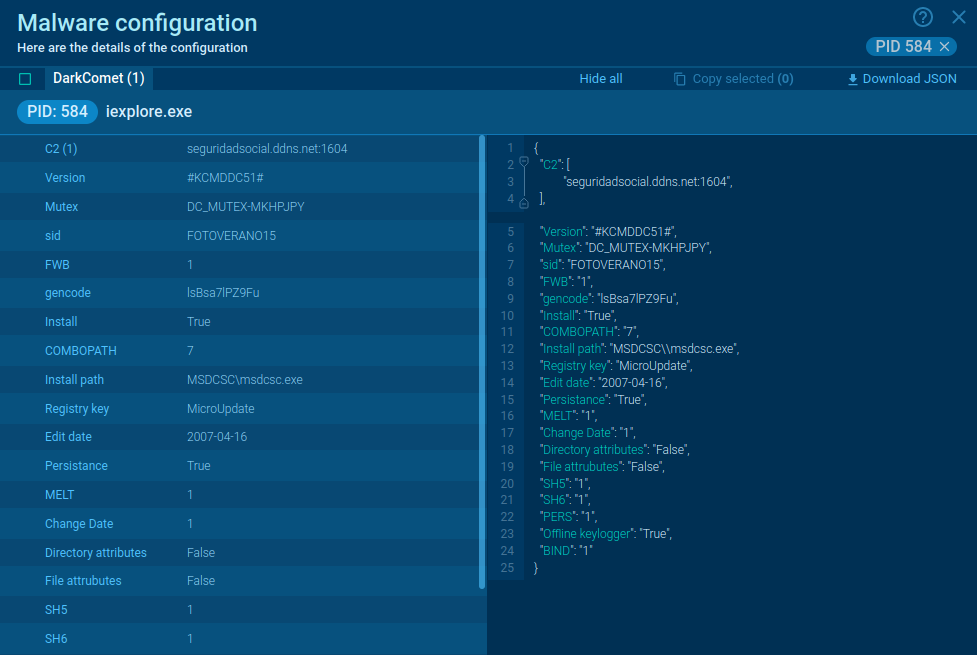
darkcomet rat memory dump

Figure 2: DarkComet memory dump

ANY.RUN automatically creates a memory dump of the running process and matches it with the Yara rule. After DarkComet detection, its config is available to researchers for subsequent analysis in no time.

In our example, malware configuration was extracted just 10 seconds after the task launch.

Conclusion

Having DarkComet downloaded on your working station can cause severe issues. And it’s better to get rid of it immediately. Concerning the SOC’s specialists' goal, the analysis of the RAT’s infection should be carried out as soon as possible. And with ANY.RUN sandbox it’s easy to do.
HAVE A LOOK AT

PXA Stealer screenshot
PXA Stealer
pxastealer
PXA Stealer is an information-stealing malware that targets individuals and organizations in 60+ countries. It spreads via phishing, archives, and fake software updates. DLL sideloading, decoy documents, and obfuscation help it evade security tools. Exfiltrated data is exfiltrated and monetized through underground marketplaces.
Read More
DeerStealer screenshot
DeerStealer
deerstealer
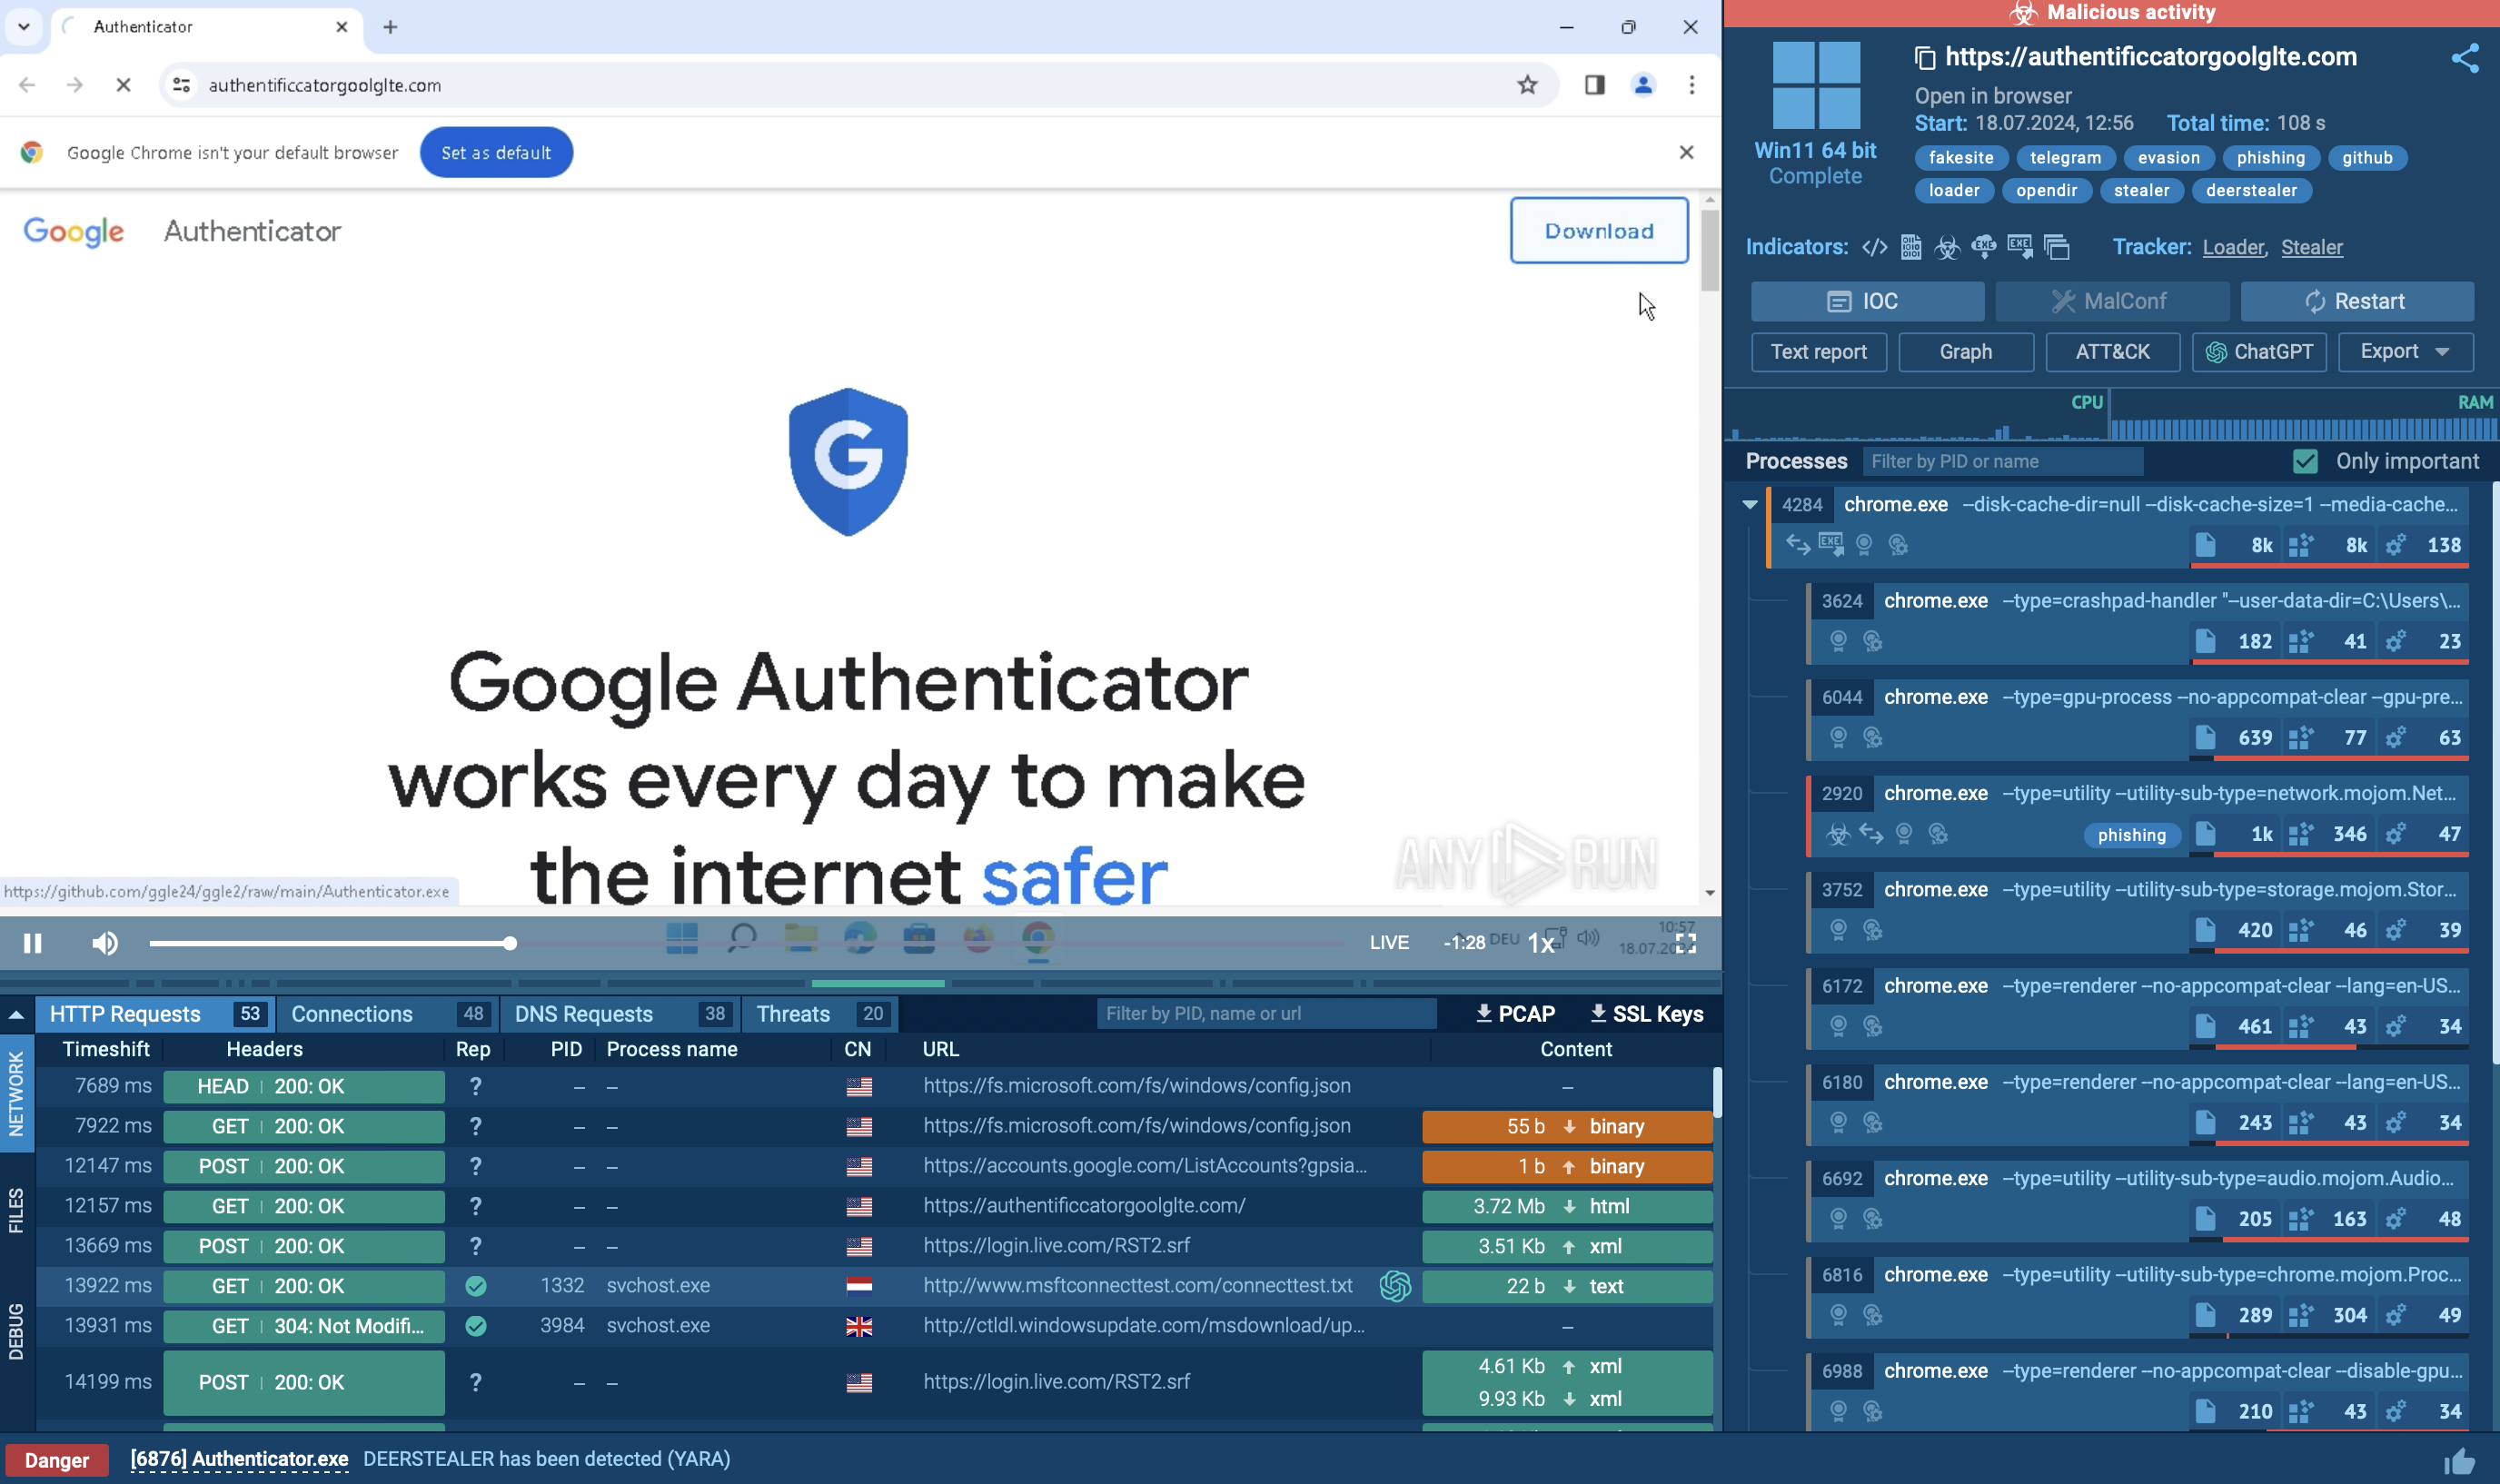
DeerStealer is an information-stealing malware discovered in 2024 by ANY.RUN, primarily targeting sensitive data such as login credentials, browser history, and cryptocurrency wallet details. It is often distributed through phishing campaigns and fake Google ads that mimic legitimate platforms like Google Authenticator. Once installed, it exfiltrates the stolen data to a remote command and control (C2) server. DeerStealer’s ability to disguise itself as legitimate downloads makes it particularly dangerous for unsuspecting users.
Read More
Salvador Stealer screenshot
Salvador Stealer
salvador
Salvador Stealer is a powerful, information-stealing Android malware designed to silently infiltrate systems, extract sensitive data, and exfiltrate it to cybercriminals. Often sold on underground forums, it is part of the growing ecosystem of “stealers-as-a-service” (SaaS) tools that target individuals and organizations alike.
Read More
Rootkit screenshot
Rootkit
rootkit bootkit
A rootkit is a type of malicious software designed to provide unauthorized administrative-level access to a computer or network while concealing its presence. Rootkits are tools used by cybercriminals to hide their activities, including keyloggers, spyware, and other malware, often enabling long-term system exploitation.
Read More
CastleLoader screenshot
CastleLoader
castleloader
CastleLoader is a modern malware loader designed to quietly establish initial access and deliver follow-up payloads such as stealers, RATs, and ransomware. It focuses on stealth, flexibility, and rapid payload rotation, making it an effective tool for financially motivated threat actors and a persistent problem for enterprise defenders.
Read More
DarkCloud screenshot
DarkCloud
darkcloud
DarkCloud is an infostealer that focuses on collecting and exfiltrating browser data from the infected device. The malware is also capable of keylogging and crypto address swapping. DarkCloud is typically delivered to victims’ computers via phishing emails.
Read More