Forg365
- 9
- Global rank
- 2
- Month rank
- 3
- Week rank
Forg365 is a Microsoft 365 PhaaS platform supporting AiTM and device-code phishing, conditional visitor filtering, and identity-focused account takeover.
- Phishingkit
- Type
- Unknown
- Origin
- 1 July, 2026
- First seen
- 2 November, 2026
- Last seen
How to analyze Forg365 with ANY.RUN
IOCs
IP addresses
- 135.233.95.144
- 150.171.28.11
- 151.101.193.155
- 48.209.138.168
- 23.52.181.212
- 2.16.110.147
- 207.180.242.53
- 74.179.77.164
- 150.171.109.106
- 104.16.179.112
- 23.11.41.157
- 150.171.27.11
- 172.211.123.248
- 48.192.1.65
- 35.190.80.1
- 150.171.109.107
- 188.114.97.3
- 104.26.13.205
- 20.190.160.67
- 104.18.23.222
Hashes
- 68b4790fb50f6b5ded57acfbe064f8c93b4b0ef6d8367a934a1bd3268241733c
- 75da533888189d13fc340d40637b9fc07a3f732e3fcf33ec300f4c7268790a62
- 907f2709d1d3c8fa26294938f4080bc477e62281c4c50a082c22db0195cda663
- 22ca9415e294d9c3ec3384b9d08cdaf5164af73b4e4c251559e09e529c843ea6
- 3d0361a85adfcd35d0de74135723a75b646965e775188f7dcdd35e3e42db788e
- b3ece279943b28c8d855ec86ac1ce53bdfb6a709240d653508764493a75f7518
- 4ecedb9c1f3dd0d0e3aeb86146561b3d7e58656cbdbed1a39b91737b52ec7f2c
- e758273c25fbad804fe884584e2797caefbbd1c2877dfd6f87ab1340cd25252e
- 3377a873db531113d79919e7a89369a79a602bac6ae09b9864b9378dc285f345
- a3eb276fbd19dce2b00db6937578b214b9e33d67487659fe0bf21a86225ece73
- bbd37d41b7de6f93948fa2437a7699d4c30a3c39e736179702f212cb36a3133c
- 35872a3343d4b4768fe4702a8dc18b749933e81210db13466ad172bd2880f6eb
- de6d7b7c2427ec4e738407d7834b71941f69166b030355e00f325ff1391df5a1
- cf26310b073b0891996ecd761c6cb53f00193dee524213a9fb34225d636ec4b7
- aa12205b108750cf9fa0978461a6d8881e4e80da20a846d824da4069d9c91847
- 08978a1425dec304483bbb7dd0e55a7d850c4561abd41bac1be5d93d70465174
- 243befbd6b67a21433dcc97dc1a728896d3a070dc20055eb04d644e1bb955fe7
- e98c5cfe277a338a938e7277deec132f5ea82a53ebdb65ff10e8a2ff548ac198
- 4f70eca8e28541855a11ec7a4e6b3bc6dd16c672ff9b596ecfb7715bb3b5898c
- 275e7fadb93a810328e3adead8754dd0a19a062d5d20a872f7471ffab47aa7b3
Domains
- cdnjs.cloudflare.com
- slscr.update.microsoft.com
- settings-win.data.microsoft.com
- crl.microsoft.com
- shamlinkslimited.com
- self.events.data.microsoft.com
- vwnkizysza.cedarandstakes.com
- a.nel.cloudflare.com
- update.googleapis.com
- api.edgeoffer.microsoft.com
- edge.microsoft.com
- fe3cr.delivery.mp.microsoft.com
- google.com
- www.microsoft.com
- edge-consumer-static.azureedge.net
- cdn.jsdelivr.net
- api.ipify.org
- ocsp.digicert.com
- code.jquery.com
- clients2.googleusercontent.com
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:zgze39rfgmixi_53jjgjyf5c1fcdyw0j1rqqlyrtqbe&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- http://shamlinkslimited.com/page.php
- https://copilot.microsoft.com/c/api/user/eligibility
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://shamlinkslimited.com/page.php
- https://shamlinkslimited.com/favicon.ico
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://xpaywalletcdn.azureedge.net/mswallet/expresscheckout/v1/getglobalconfig?edgechannel=stable&edgeversion=133.0.3065.92&configversion=0
- https://www.bing.com/bloomfilterfiles/expandeddomainsfilterglobal.json
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edgeruntime%2cedgeruntimeconfig%2cedgedomainactions&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1793634261&lafgdate=0
- https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://edge.microsoft.com/extensionwebstorebase/v1/crx?os=win&arch=x64&os_arch=x86_64&nacl_arch=x86-64&prod=edgecrx&prodchannel=&prodversion=133.0.3065.92&lang=en-us&acceptformat=crx3,puff&x=id%3djmjflgjpcpepeafmmgdpfkogkghcpiha%26v%3d1.2.1%26installedby%3dother%26uc%26ping%3dr%253d318%2526e%253d1
- https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=arbitration_priority_list&version=24.*.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
- https://edge.microsoft.com/entityextractiontemplates/api/v1/assets/find-assets?name=edge_hub_apps_manifest_gz&version=4.11.*&channel=stable&key=d414dd4f9db345fa8003e32adc81b362
Last seen at
Key Takeaways
- Forg365 focuses on Microsoft 365 identity compromise: Its attack options include AiTM and device-code phishing.
- The exposed population is broad: Any organization that depends on Microsoft 365 and Entra ID can face the risk, even without evidence of sector-specific targeting.
- Successful attacks can enable more than credential theft: Session access can support mailbox compromise, BEC, fraud, and trusted-account abuse.
- Interactive sandboxing strengthens phishing triage: Forg365 can filter visitors and serve different content depending on the environment, so a single static URL check can give analysts false confidence. ANY.RUN’s Interactive Sandbox helps the SOC reproduce the victim path, confirm which attack branch is actually active, capture evidence for escalation, and turn verified indicators into hunting and detection actions.
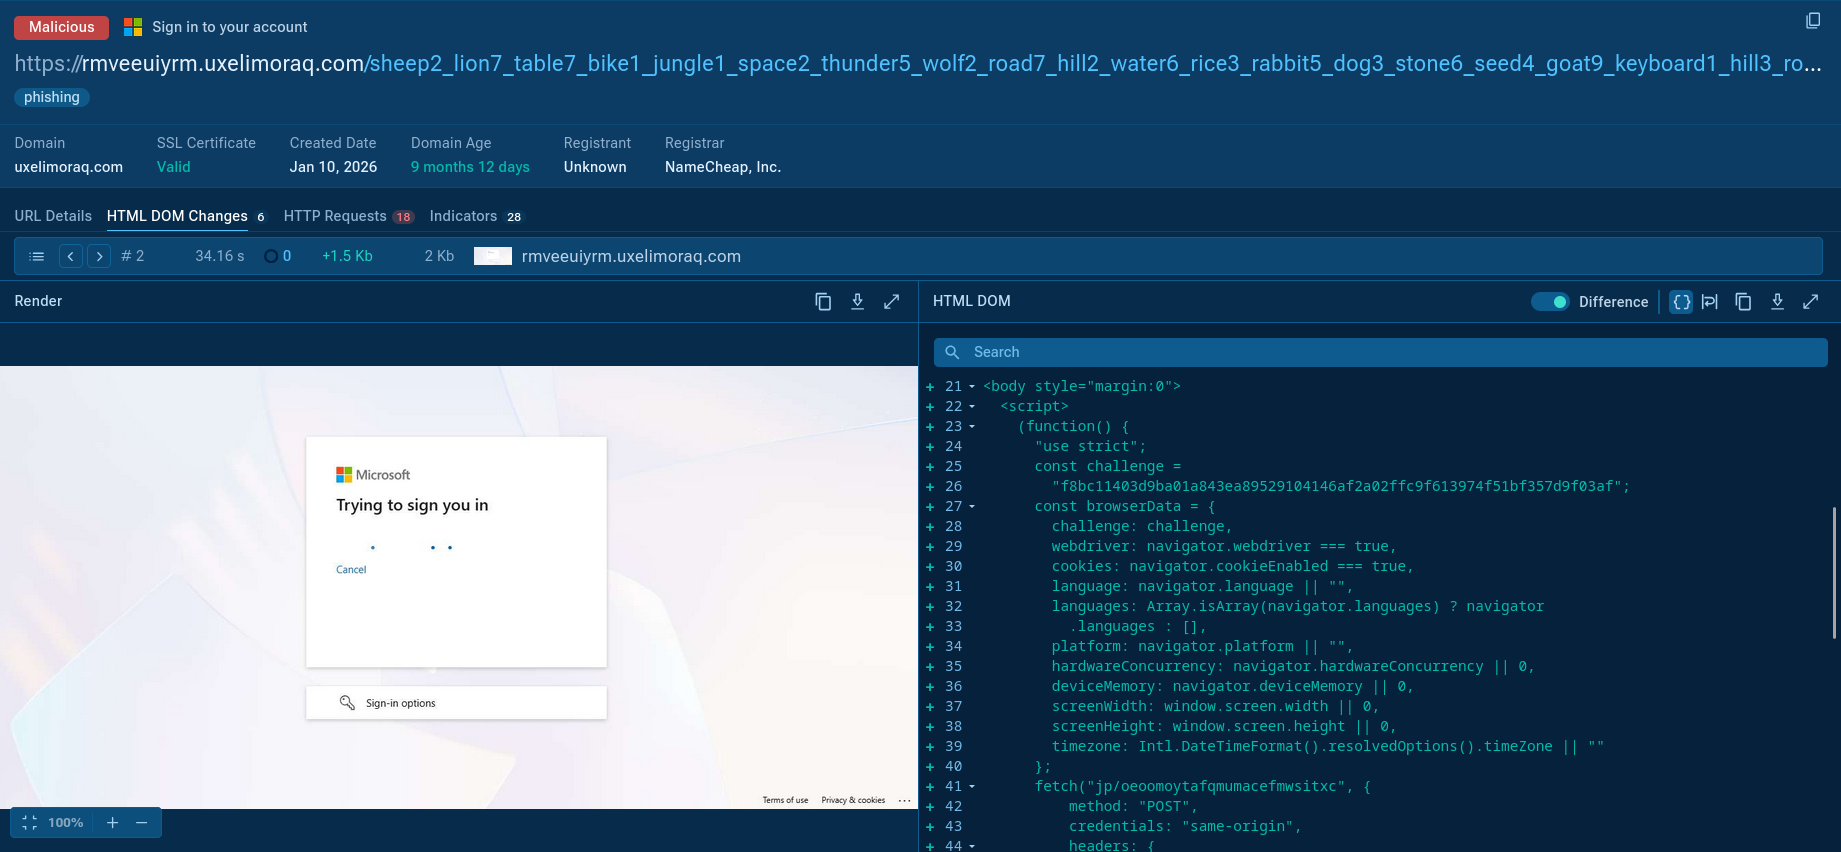
- Behavioral indicators can outlast domains: Scenario-selection requests, SVG resources, and generated route patterns provide useful hunting context.
- Identity controls are central to defense: Device-code restrictions, phishing-resistant MFA, and token/session revocation directly address the attack paths.
- Cross-control visibility matters: Email, browser, proxy, and identity telemetry should be investigated as one chain.
What Is Forg365?
Forg365 is a commercial phishing-as-a-service platform designed around Microsoft 365 authentication abuse. Public research has documented both AiTM and device-code phishing capabilities.
That distinction matters because the victim may encounter an authentication flow that looks legitimate or is partly legitimate. In a device-code scenario, a real Microsoft authentication page can be part of the compromise path. In an AiTM scenario, the attacker relays the authentication process while attempting to capture credentials and session material.
For organizations, the downstream risk is account and session misuse. A compromised mailbox can become a platform for business email compromise, fraud, internal phishing, or access to sensitive communications.
There is not enough evidence to claim that Forg365 belongs to one sector-specific campaign. The safer conclusion is broader: organizations using Microsoft 365 and Entra ID should consider themselves potentially exposed if their authentication and monitoring controls allow these flows.
What Organizations Are Vulnerable to Forg365?
Organizations that rely heavily on Microsoft 365 and Entra ID face the clearest exposure to Forg365 because the campaign is built around Microsoft identity and session abuse. ANY.RUN's Threat Intelligence data shows particularly strong industry risk signals across technology (56%), manufacturing (31%), consulting (19%), and banking (18%), suggesting that Forg365-related activity is relevant across several business environments rather than a single vertical.
The geographic distribution also points to broad exposure. 51% of Forg365-related submissions come from the United States, followed by the United Kingdom at 6%, Australia at 5%, and Mexico at 2%. These figures show where Forg365-related activity is being observed and investigated in ANY.RUN, but they should not be treated as proof of deliberate geographic targeting.
The greatest organizational risk comes from compromising accounts connected to sensitive business processes, including finance operations, shared mailboxes, administrative functions, and customer or supplier communications. A successful session takeover can expose mailbox content, provide unauthorized access to Microsoft services, and create opportunities for follow-on account abuse, fraud, or business email compromise.
For SOC and security leaders, Forg365 should therefore be treated as an identity and account-takeover threat rather than only a phishing-page problem. Teams need visibility across authentication activity, session behavior, and post-compromise telemetry to determine whether an initial phishing interaction has developed into a broader Microsoft 365 incident.
How Forg365 Attacks Work: Detailed Analysis
We can trace the attack flow in detail by uploading a sample to ANY.RUN’s Interactive Sandbox.
The observed ANY.RUN session begins before the final authentication page. This part of the chain is important because it creates detection opportunities that are easy to miss when analysts focus only on the last page.
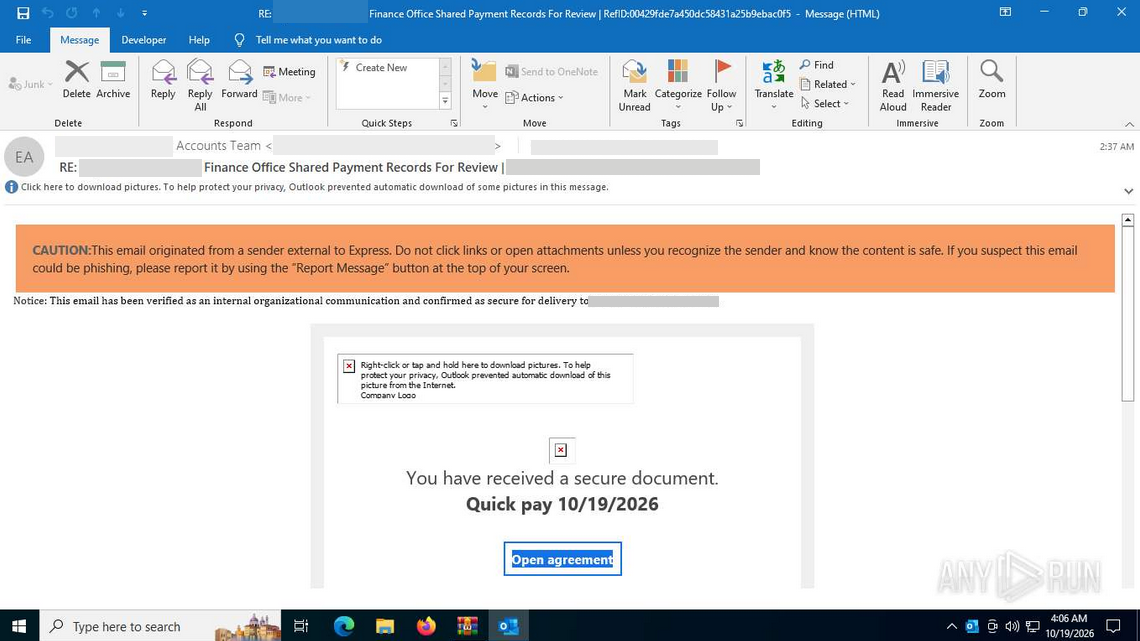
First, the victim receives a fake quarantine notification. The lure directs the user into a redirect chain, with the victim email carried as a parameter.
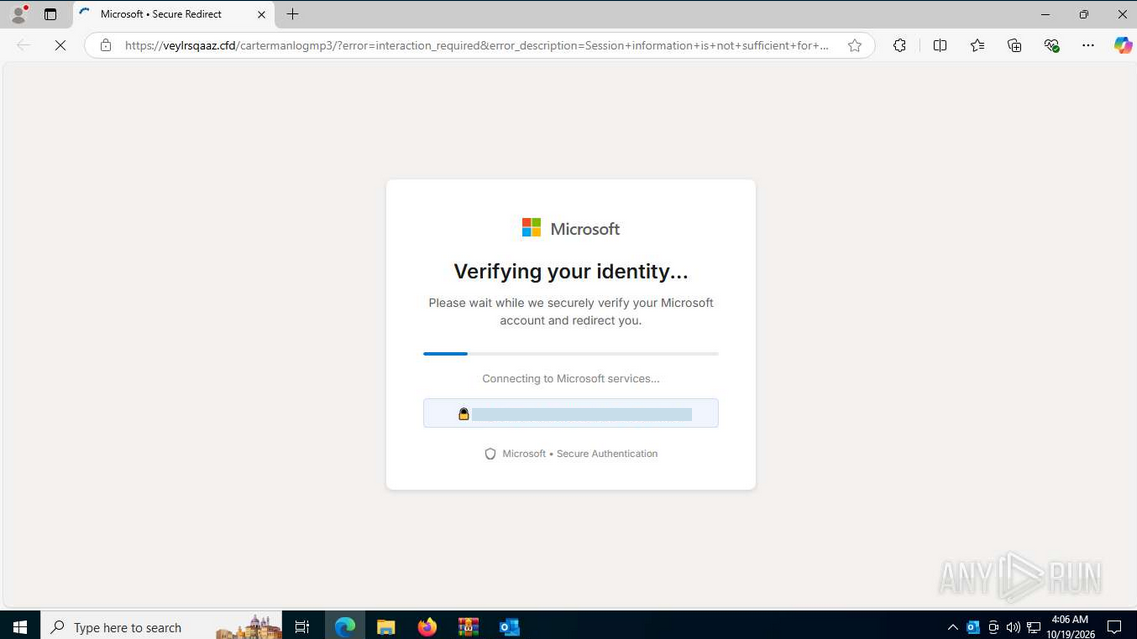
Next, the browser encounters a fake CAPTCHA and client-side checks. The observed logic can distinguish VPN traffic, bots, and research environments from other visitors.
Finally, the session reaches the AiTM branch. Forg365 also supports device-code phishing at the platform level, but that path was not executed in this analysis.
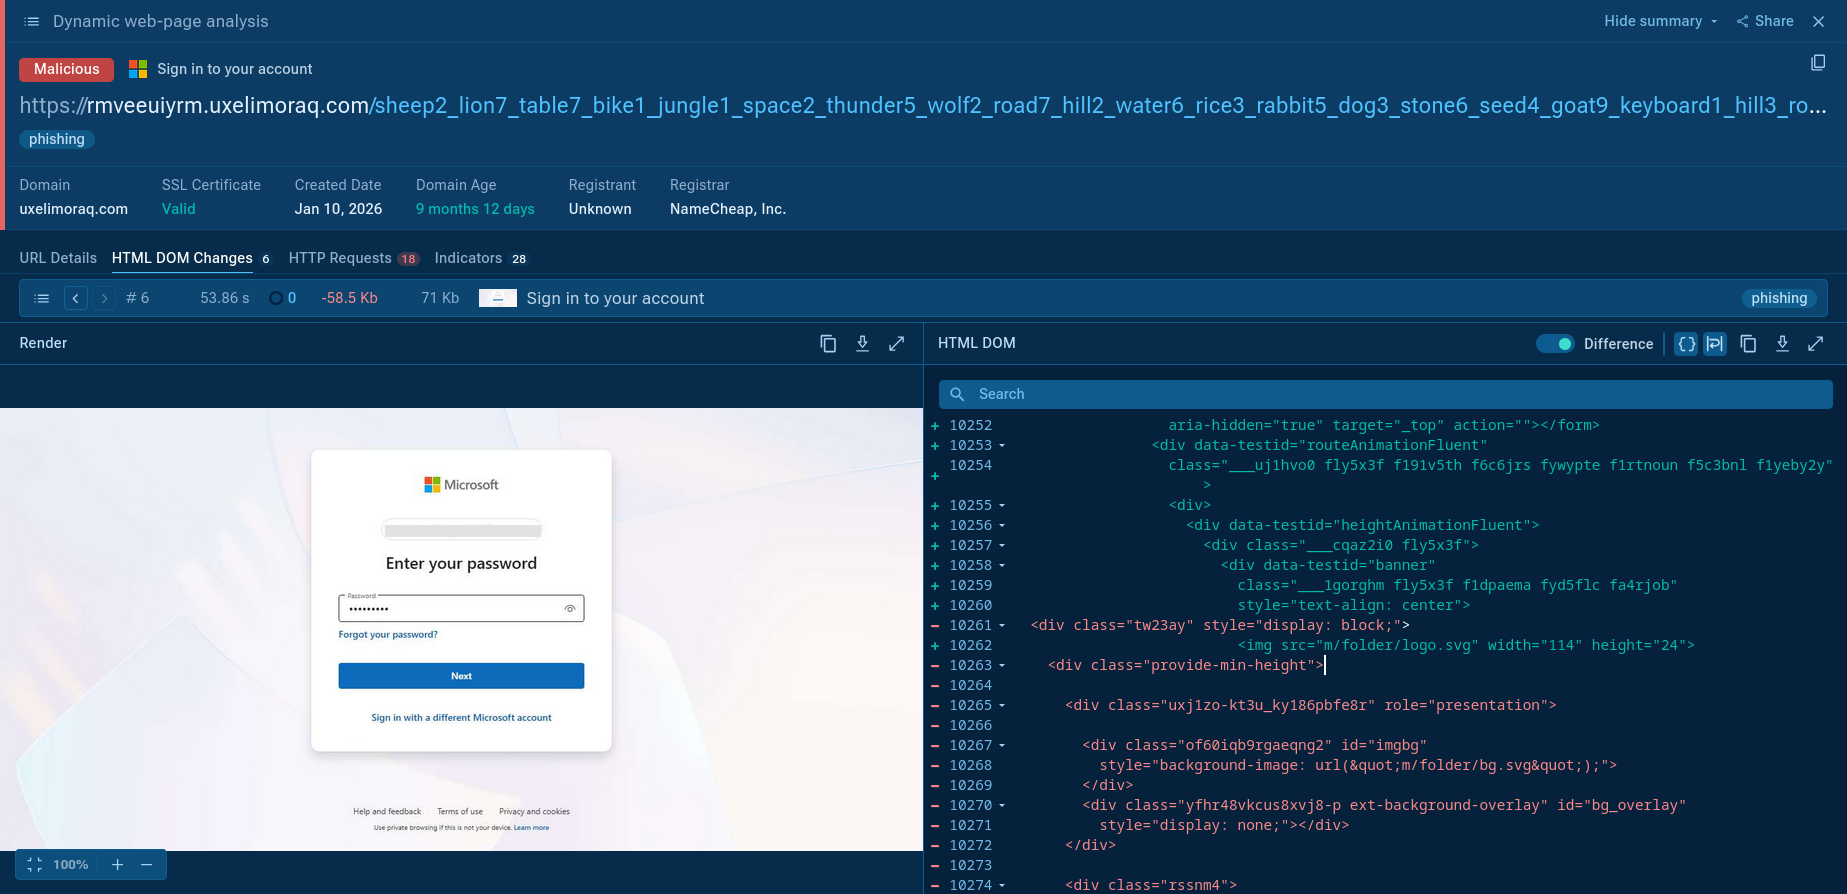
This high-level sequence is more important than any single domain. The infrastructure can move, while the combination of lure, redirects, visitor classification, and authentication abuse gives defenders a more durable model of the threat.
The Sandbox analysis shows the attack as a live browser sequence instead of a static phishing page.
Redirects Can Be Reconstructed as One Session
The browser follows several redirects before the authentication stage. The victim email is passed through the flow in a URL parameter.
This provides useful context for correlating the original lure with proxy or browser activity and helps analysts preserve the full path for later incident scoping.
Anti-Analysis Behavior Changes What Different Visitors See
The fake CAPTCHA and client-side checks appear before the phishing page.
This matters operationally because a suspicious URL can look inactive in one environment and malicious in another. Interactive execution gives analysts a better chance to see the content presented to a real user.
Request Patterns Create Detection Pivots
The observed web traffic includes several characteristic patterns:
POST /m/sc/*: Associated with attack-scenario selection;GET /m/folder/key.svg: Loads a landing resource;GET /m/folder/logo.svg: Loads another resource;- Long
GETpaths built from repeated word-number segments: Used as generated route structures.
One observed route used a structure similar to:
/sheep2_lion7_table7_bike1_jungle1_space2_thunder5_...
The route value itself can change. The combination of request pattern, redirect context, and authentication theme is more useful for hunting.
How Threat Intelligence Helps Investigate Forg365
Behavioral analysis shows how the phishing flow behaves in the browser. Threat intelligence helps the SOC move beyond that single session and determine whether confirmed indicators connect to other activity worth investigating.
Analysts can start with a family-level search such as threatName:"forg365" to look for analyses and indicators associated with the threat name. Any relationships surfaced by the search can then be validated using behavior, infrastructure, timing, and other evidence before activity is clustered or escalated.
Threat Intelligence Lookup can be used to pivot from domains, URLs, IP addresses, and other indicators confirmed during the analysis. Analysts can use those pivots to look for related analyses, connected infrastructure, and recurring indicators that may help scope the incident or support threat hunting.
To move from one-time investigation to proactive detection, security teams can integrate Threat Intelligence Feeds into their existing security stack. The feeds continuously deliver fresh malicious indicators collected from real-world threat analyses, helping SOC teams keep detection rules, monitoring systems, and enrichment workflows aligned with newly observed infrastructure.
For threats such as Forg365, this gives defenders a way to identify suspicious domains, URLs, and other indicators earlier, expand coverage beyond the artifacts found in a single investigation, and reduce the need to manually search for new infrastructure. Feeding current IOCs into SIEM, SOAR, EDR, XDR, or TIP workflows also helps teams automate enrichment and detection while keeping threat intelligence closer to the controls used for day-to-day monitoring.
What Security Leaders Should Prioritize
Forg365 highlights four areas that security leadership can address directly.
Reduce Unnecessary Device-Code Exposure
Use Microsoft Entra Conditional Access to restrict device-code authentication where the organization does not have a clear business need.
This removes one of the platform's attack options and makes remaining device-code events easier for the SOC to triage.
Move High-Risk Users to Phishing-Resistant MFA
Administrators, finance staff, executives, and other high-impact identities should receive priority for FIDO2 keys or passkeys.
This improves resilience against authentication-interception attacks that rely on turning a successful sign-in into reusable access.
Treat Account Compromise as a Token and Session Incident
If compromise is confirmed, revoke active sessions and refresh tokens, review OAuth grants and device registrations, and investigate mailbox activity.
A password reset alone should not be the only containment action when session material may already be in attacker hands.
Ensure the SOC Can Correlate the Whole Chain
Email, browser, network, and identity data should be accessible during one investigation.
That correlation is what turns several weak signals into a stronger conclusion and helps teams distinguish a blocked lure from an actual account compromise.
Conclusion
Forg365 illustrates why modern phishing should be treated as a cross-layer identity problem. The threat targets Microsoft 365 users through AiTM and device-code techniques, while the ANY.RUN analysis shows conditional delivery that can hide the phishing content behind redirects and visitor checks. The practical defensive priorities are clear: reduce unnecessary device-code exposure, deploy phishing-resistant MFA for high-risk users, include session and refresh-token revocation in response, and correlate email, browser, network, and Entra telemetry. That combination gives both analysts and security leadership a stronger path from detection to containment.
Frequently Asked Questions: Forg365
1. What Is Forg365?
Forg365 is a Microsoft 365 phishing-as-a-service platform that supports AiTM and device-code phishing.
2. Which Organizations Are at Risk?
The relevant exposure is Microsoft 365 and Entra ID usage. Current evidence does not justify limiting Forg365 to one industry.
3. What Is the Main Business Risk?
Successful compromise can produce account or session access that supports mailbox abuse, BEC, fraud, and trusted-account phishing.
4. What Did the ANY.RUN Analysis Show?
The analysis reproduced a quarantine lure, redirects, a fake CAPTCHA, visitor classification, the observed AiTM branch, and distinctive request patterns.
5. Why Does Conditional Delivery Matter?
The phishing content can depend on the visitor environment, so a scanner or researcher may not receive the same page as the intended victim.
6. What Should Security Teams Fix First?
Priority actions include limiting device-code authentication, deploying phishing-resistant MFA, revoking sessions and refresh tokens after confirmed compromise, and improving cross-layer telemetry correlation.
7. How Can ANY.RUN Help?
Interactive Sandbox can expose the browser-dependent attack chain and extract useful behavior and indicators. Threat Intelligence Lookup can then help analysts investigate confirmed infrastructure or related observations.
Other malware & phishing threats
 MassLoggerMassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems.
It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
 MoonriseMoonrise RAT is a newly discovered Go-based remote access trojan with zero detections at launch, featuring credential theft, keylogging, webcam access, clipboard hijacking, and UAC bypass.
 NetSupport RATNetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
 Predator the ThiefPredator, the Thief, is an information stealer, meaning that malware steals data from infected systems. This virus can access the camera and spy on victims, steal passwords and login information, and retrieve payment data from cryptocurrency wallets.
 GuLoaderGuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
 RatonRATRatonRAT is a .NET-based Remote Access Trojan targeting Windows systems. It supports credential theft, screen capture, system and hardware discovery, persistence, and C2 communication. Samples use techniques such as Registry Run keys and scheduled tasks for persistence, with some variants employing anti-analysis and evasion techniques.