Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
122
Global rank
139 infographic chevron month
Month rank
143 infographic chevron week
Week rank

Ficker Stealer is a malware that steals passwords, files, credit card details, and other types of sensitive information on Windows systems. It is most often distributed via phishing emails and can perform keylogging, process injection, and browser tracking.

Stealer
Type
ex-USSR
Origin
10 August, 2020
First seen
29 September, 2026
Last seen

How to analyze Ficker Stealer with ANY.RUN

Type
ex-USSR
Origin
10 August, 2020
First seen
29 September, 2026
Last seen

IOCs

IP addresses
48.209.6.48
104.26.12.205
2.16.241.9
44.244.22.128
48.192.1.65
23.59.18.102
48.209.138.168
172.211.123.248
48.209.138.189
135.232.92.137
20.190.160.64
2.19.86.20
104.26.13.205
95.100.102.101
20.165.94.54
23.216.77.36
48.209.133.15
128.24.231.65
23.11.41.157
2.16.241.215
Hashes
c9621fc1cdb618e122c1a4db2ccdd65e5208dc0912008bf6dbc74d7fd3594765
94e60de577c84625da69f785ffe7e24c889bfa6923dc7b017c21e8a313e4e8e1
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
a73acef4776b41cb972119be6293f9ca9bdcb551f50715eedb193ccb370c62b4
860706c47e7f046e27a06fc13c1a00b9eb264feca3484ec8110483d427405b3c
e8f64f6f49b8231476e1028b75f2a3e5317ed506db6d1a265dbf3c28eb3e1d1a
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
e52e3b342c9b0a66df2b1947da83ff74fa3052c2842fcda31b2841461051b9a1
66a0e7324e54336460ed01ef2e6ab34428f67684a8ddd1941db8c1f82dcfec28
3c401be72280bc53d5e4f4eaff1dedf8685bb968a12a778e059aa6f740da2647
c66fe0094b97bee5553b43d4598c821406abd63bde2b269752ede0bae85bcc48
ef3327ff49c7be5f5e4fb7928d0d4624060e1dc8e2fd2b2e7942c8c6d431accf
9727dda78161dcbe9fda1d608fa86ce5bee615d804f291ba752dd80c7ca3b17a
beb3be5ffbb8ee46941d41c97555698903e18561730ec5aaf8f2ed60210206da
10810bbdba098e92cf6cac44e14d45c56d5cef5dfeb706947754c3dd96f9f4a4
dd8842e3a814108b30a53def809da10b1db44b49f4a59775450d5ff0b80c8761
09b75675fa4289b666384bff62b192acfc617b3cb0ea6f26f3b1438c2a2b6851
b3d123f822c99f06b28e7c98734dc531f0052a3f0dbf137e0ff253f3cd023f1f
6a421bee4d81a42337ab579a2f110dcd82f6e6d812e63ca7620188edb7b4063d
bb030a7915fd11c69a0d7557ee9367d93fcdb16d38df638ed0bd0bce4fea2f45
Domains
api.ipify.org
client.wns.windows.com
activation-v2.sls.microsoft.com
crl.microsoft.com
settings-win.data.microsoft.com
google.com
sweyblidian.com
www.microsoft.com
slscr.update.microsoft.com
ecs.office.com
go.microsoft.com
fe3cr.delivery.mp.microsoft.com
self.events.data.microsoft.com
ocsp.digicert.com
login.live.com
www.bing.com
binaries.templates.cdn.office.net
oneocsp.microsoft.com
messaging.lifecycle.office.com
fs.microsoft.com
URLs
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasmedic?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&appver=10.0.19041.3758&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://api.ipify.org/?format=xml
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://login.live.com/rst2.srf
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://login.live.com/ppsecure/deviceaddcredential.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
Last Seen at

Recent blog posts

post image
Fake AI Tools Put US Companies at Risk: Insid...
watchers 1677
comments 0
post image
What's Really Attacking Your Industry? Insigh...
watchers 2985
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 10621
comments 0

What is Ficker Stealer malware?

Ficker Stealer is a type of malicious software written in the Rust programming language, which is openly sold on the internet via the Malware-as-a-Service (MaaS) model. Its primary function is to extract confidential data from computers running Windows operating systems. Due to its modular design, the malware can be easily configured to steal specific forms of data. For instance, some of the common types of information targeted by it include passwords, Windows Credential Manager data, crypto wallets, credit card details, and email and chat content.

The malware has been active since 2020 and continues to receive full support from its developers to this day. In fact, it possesses the capability of self-updating, allowing it to automatically get fresh updates from the C2 server. Although the original creators of Ficker Stealer remain unidentified, it is likely that they hail from one of the ex-USSR countries.

Technical details of the Ficker Stealer malicious software

Ficker Stealer sets itself apart from other stealers such as RedLine or Arkei by utilizing Rust, a programming language that offers improved performance and safety features compared to its predecessors such as C++. Rust's efficiency helps criminals develop more complex malicious programs, while its built-in safety mechanisms prevent various vulnerabilities within the code. As a result, identifying and combating Rust-based malware can be a tall order for researchers.

Ficker Stealer is engineered to illicitly extract confidential data from a victim's computing system. Once executed, it deploys an array of sophisticated techniques to collect sensitive information, including:

  • Keylogging: It records the victim's keyboard input to obtain passwords and other confidential data.
  • Browser tracking: it is capable of tracking users’ browser activities and harvesting information such as login credentials, autocomplete data, cookies, and browsing history.
  • Process injection: Ficker can inject itself into legitimate processes within the victim's system, gaining access to protected parts of the system.
  • File extraction: The malware can be configured to gather various files from the compromised machine.
  • Loader functionality: Attackers can utilize the malware to drop and execute other malicious programs.

Additionally, to safeguard the data transferred to its C2 from being intercepted, Ficker Stealer utilizes encryption. What’s more, it reports back to the attackers following each successful operation, leaving no records or logs on the target computer. Subsequently, tracking Ficker's activities can be an intricate task. It also operates without the need for any extra DLLs to be downloaded or loaded at runtime, which enhances its stealth and efficiency.

Execution process of Ficker Stealer

The malicious behavior of Ficker Stealer can be easily uncovered by uploading it to the ANY.RUN sandbox. Here is a sample of this malware on the platform.
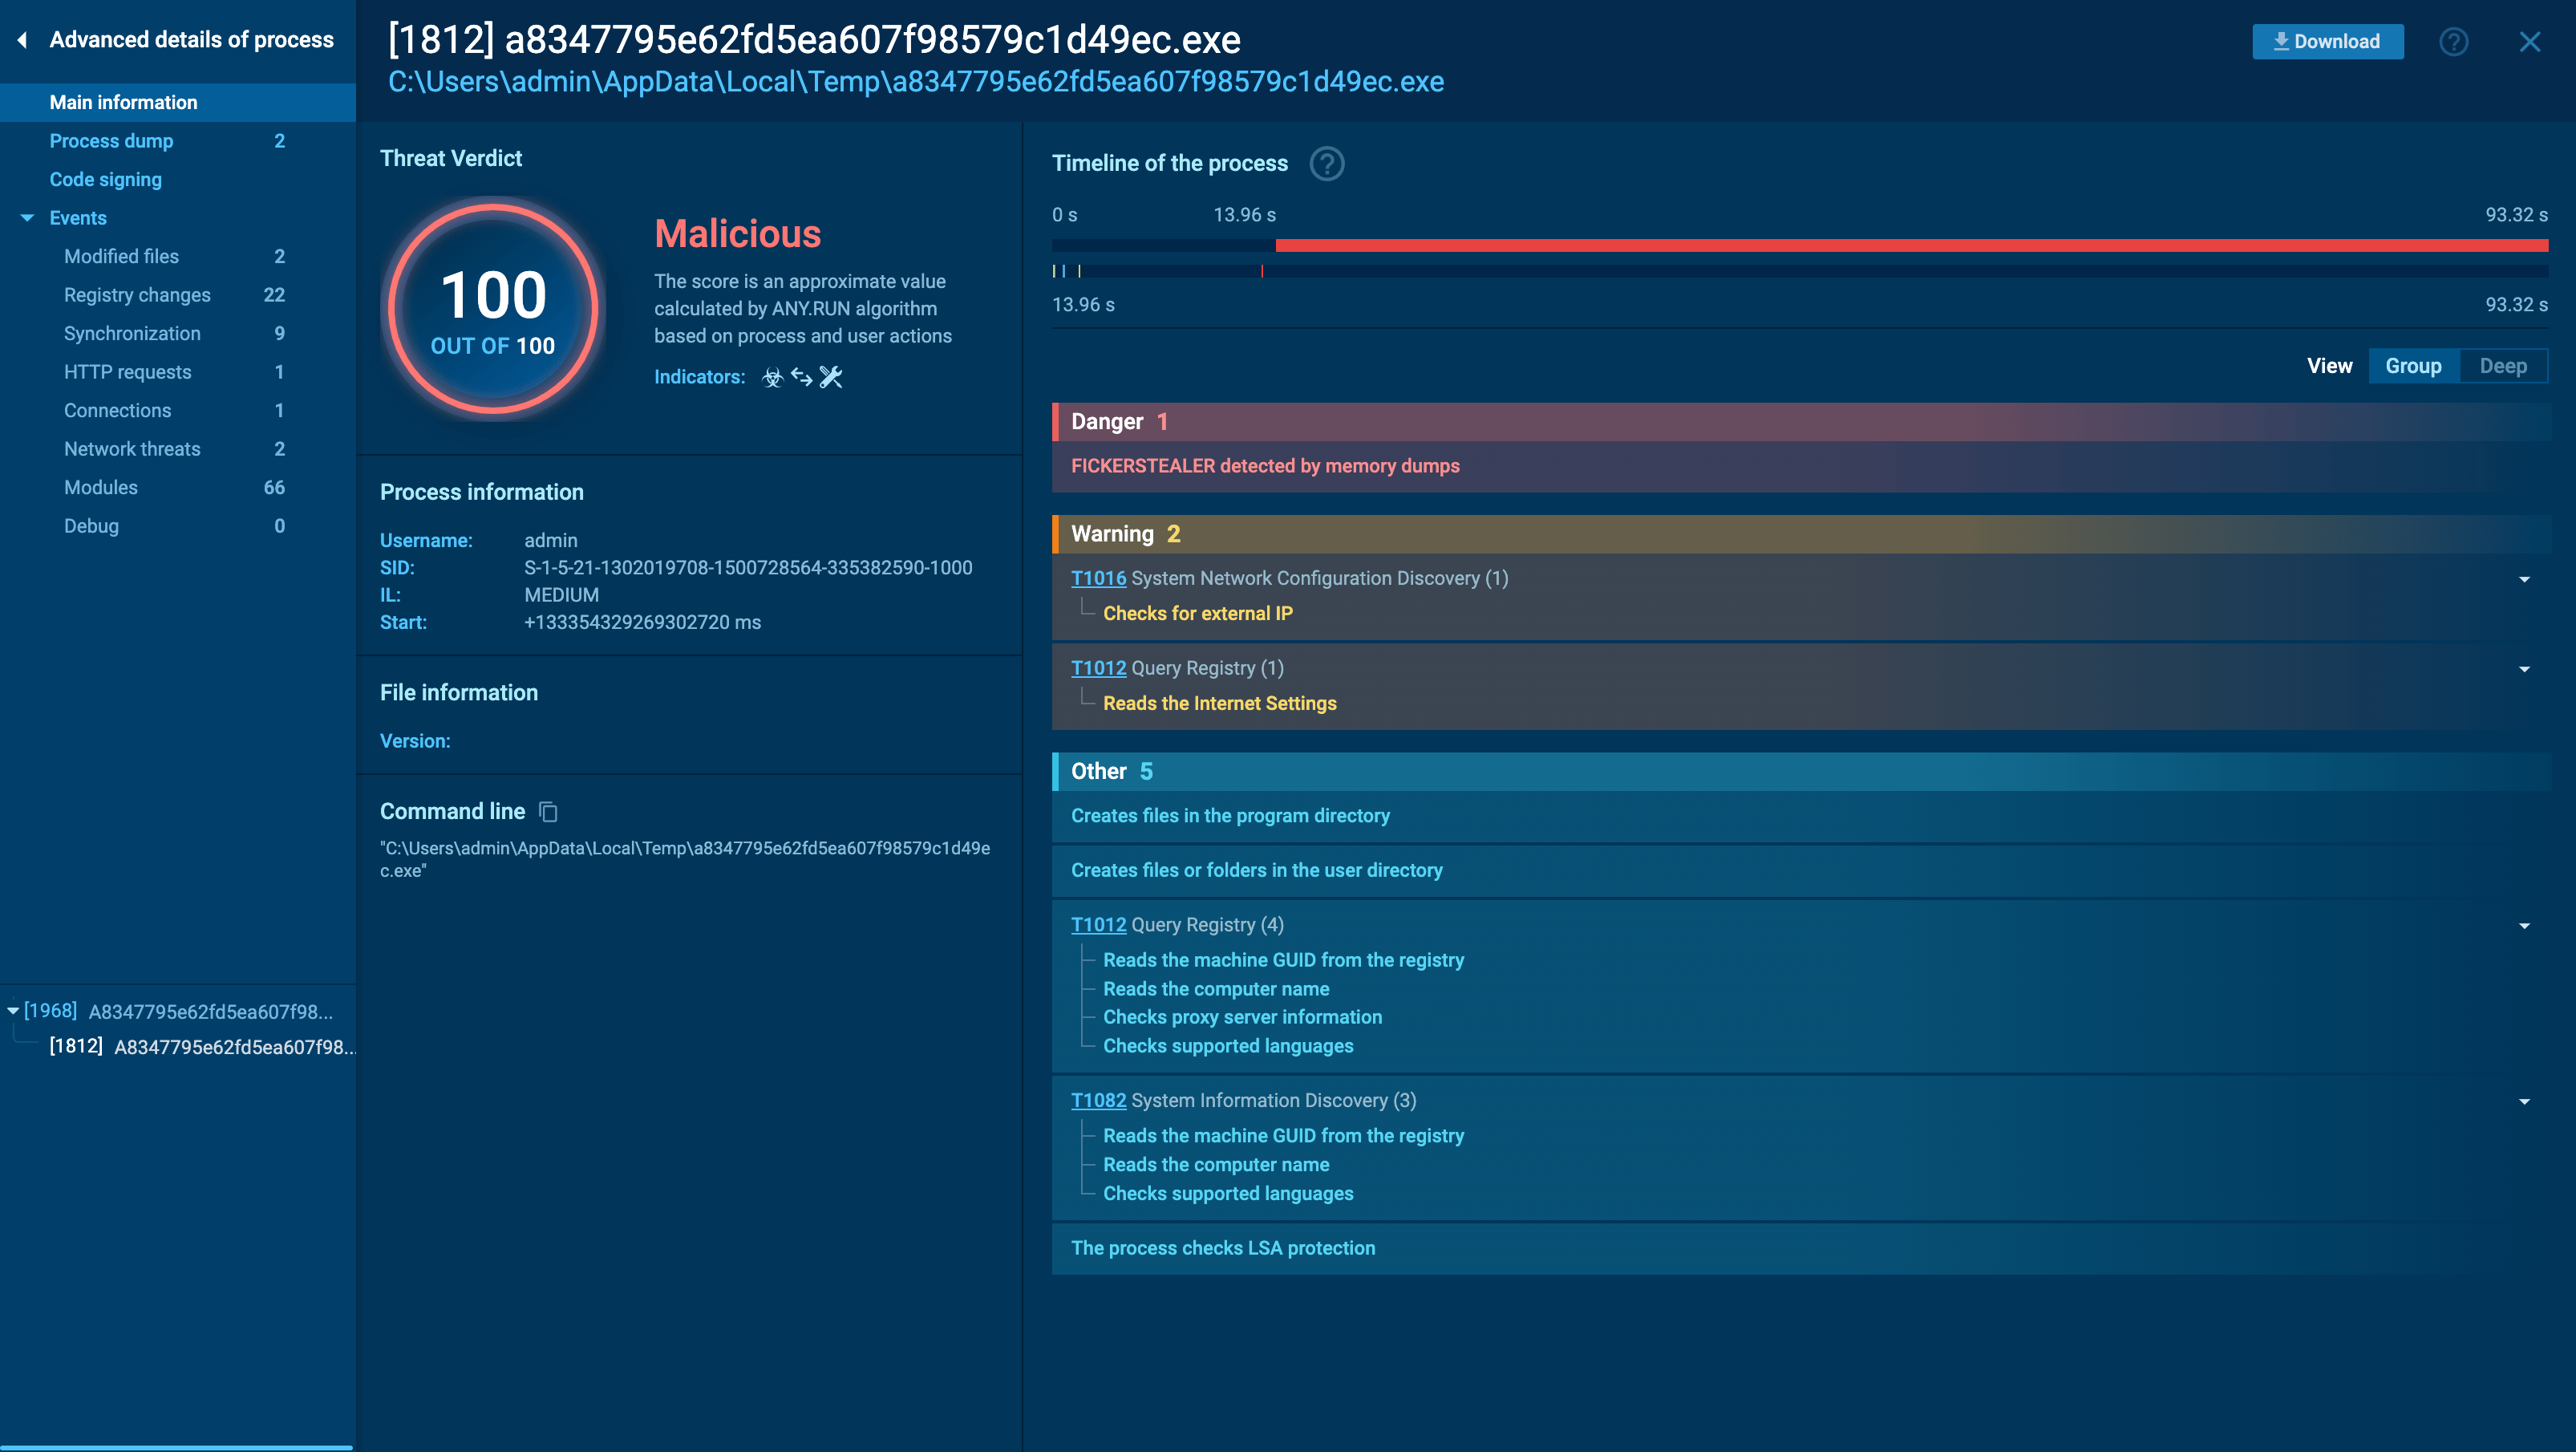
Ficker Stelaler in ANY.RUN Ficker Stelaler in ANY.RUN

Ficker is a typical representative of the stealer malware family. It creates as little noise as possible in the infected system. The main idea: make its way into the system, start execution, steal information and credentials and try to stay invisible without alerting security solutions about the threat for as long as possible.
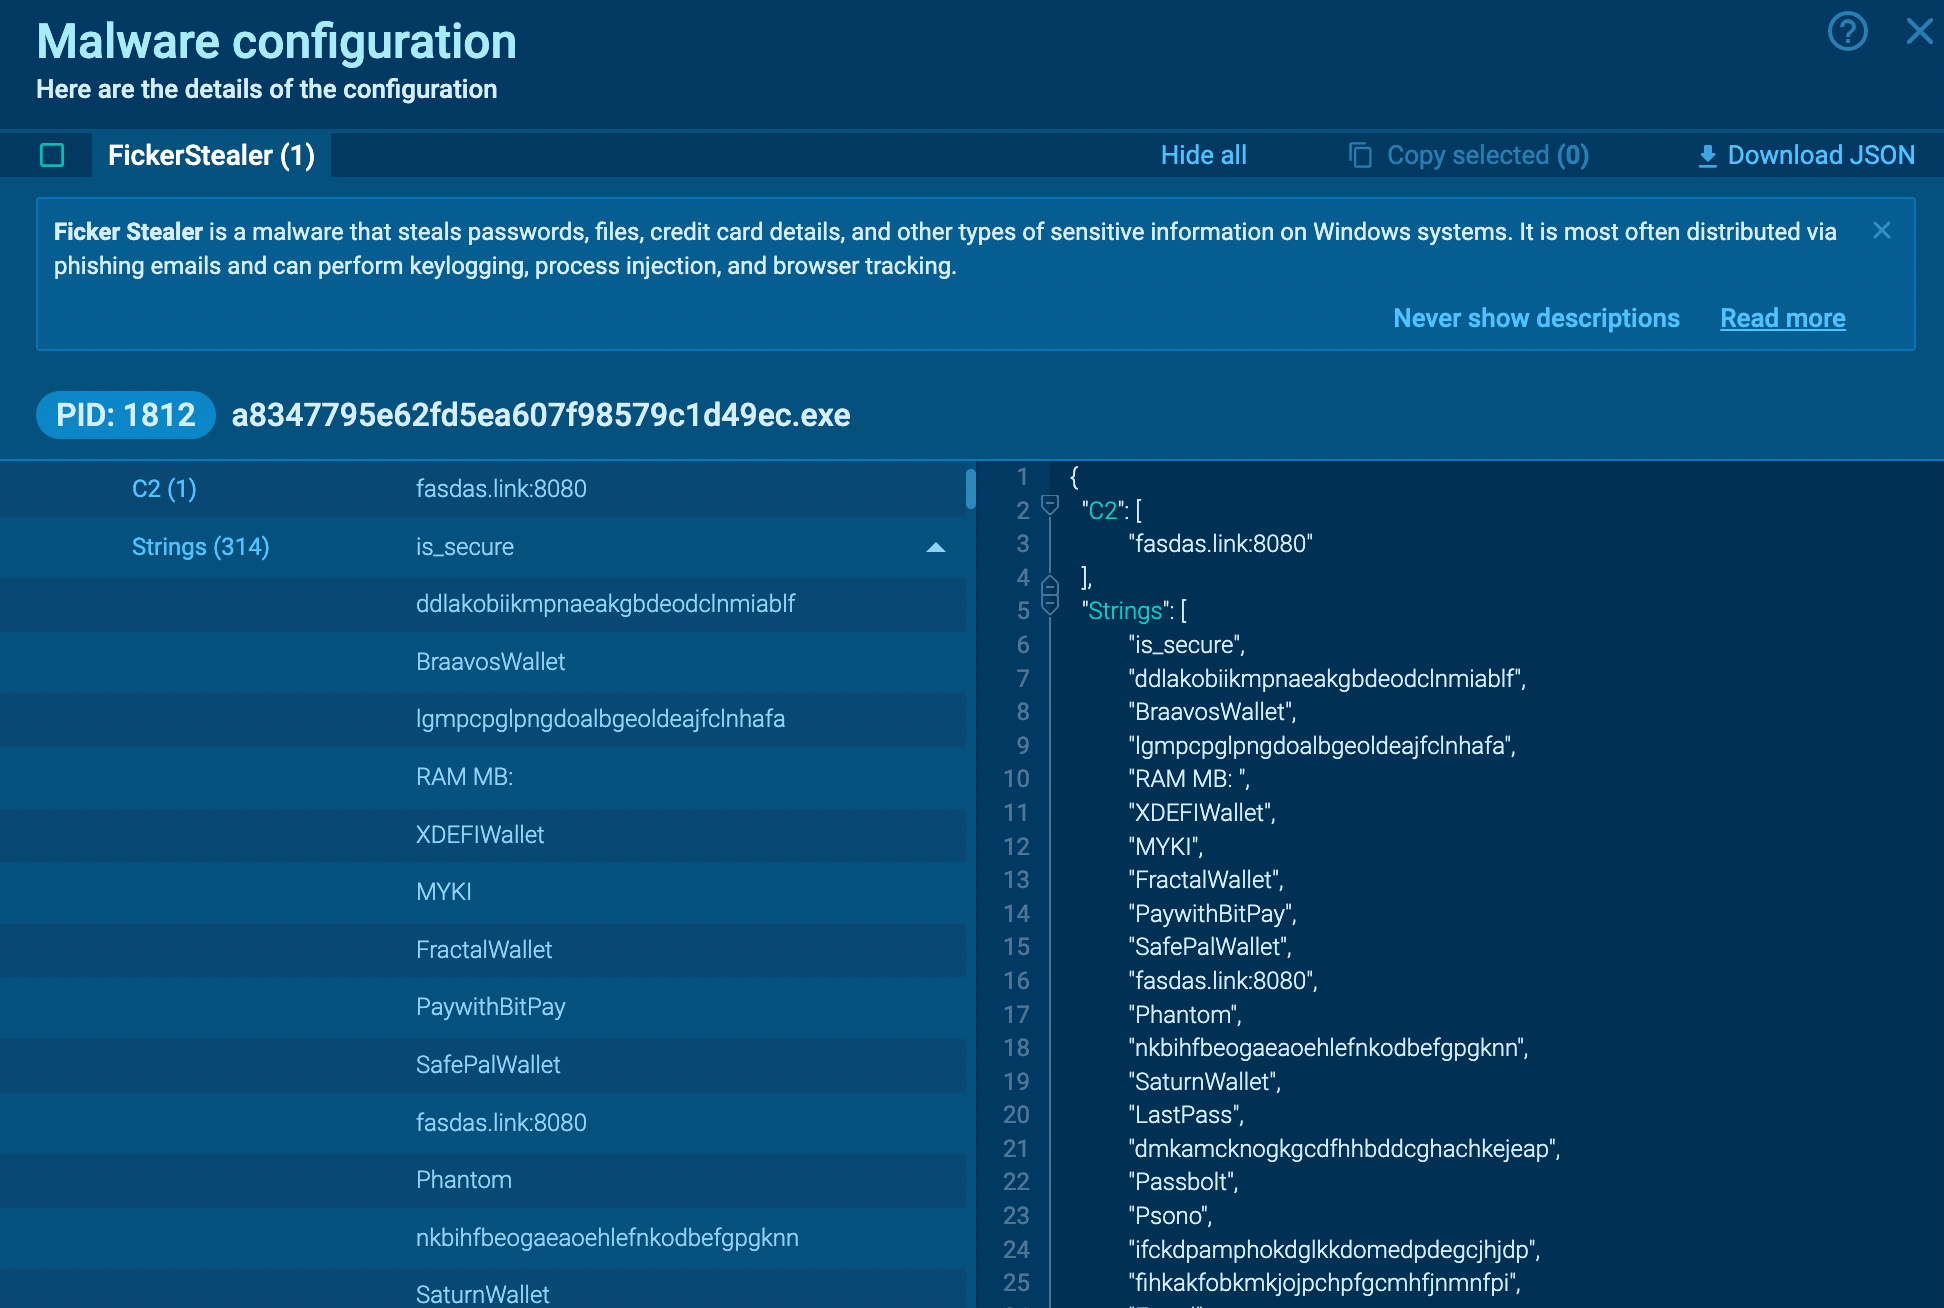
Ficker Stelaler configuration extracted in ANY.RUN Ficker Stelaler configuration extracted in ANY.RUN

Like other malware families, this particular family may alter execution flows, but it will do so in a way that remains plain and simple. Stealers usually attempt to be less visible, so you may notice reduced activity during the execution of the Ficker, compared to what you might typically expect. After all the information is stolen, the malware may halt its execution and delete itself from the infected system. However, this behavior can vary across different versions and settings.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Distribution methods of the Ficker Stealer malware

Ficker Stealer can end up on a victim’s PC in several ways:

  • Attackers may implant malicious code into websites’ infrastructure, which then gets automatically downloaded onto the devices of visitors. Such websites may look legitimate and, as a result, users may execute these downloaded files, while not being aware that their device has been compromised.
  • Yet, the most common way Ficker Stealer reaches target computers is through phishing email campaigns. Attackers may exploit social engineering techniques to get people to download a file containing malicious macros. It has been observed that in many instances Ficker Stealer relies on the Hancitor loader for delivery.

Conclusion

Ficker Stealer is a serious threat to MS Windows users. To protect your system from this malware, you must exercise caution when accessing your email inbox. If you come across an email from an unfamiliar sender or if its contents appear suspicious, it is in your best interest to refrain from opening it or clicking on any links.

Instead, you can analyze these samples in the ANY.RUN malware analysis sandbox to promptly discover whether your file or URL is malicious or not. The platform lets you interact with malware in a safe VM environment in real time. Thanks to ANY.RUN, you can get an exhaustive overview of any threat’s behavior and gain insight into its IOCs, TTPs, and other crucial details.

Try ANY.RUN for free – request a demo!
HAVE A LOOK AT

DonutLoader screenshot
DonutLoader
donutloader donut
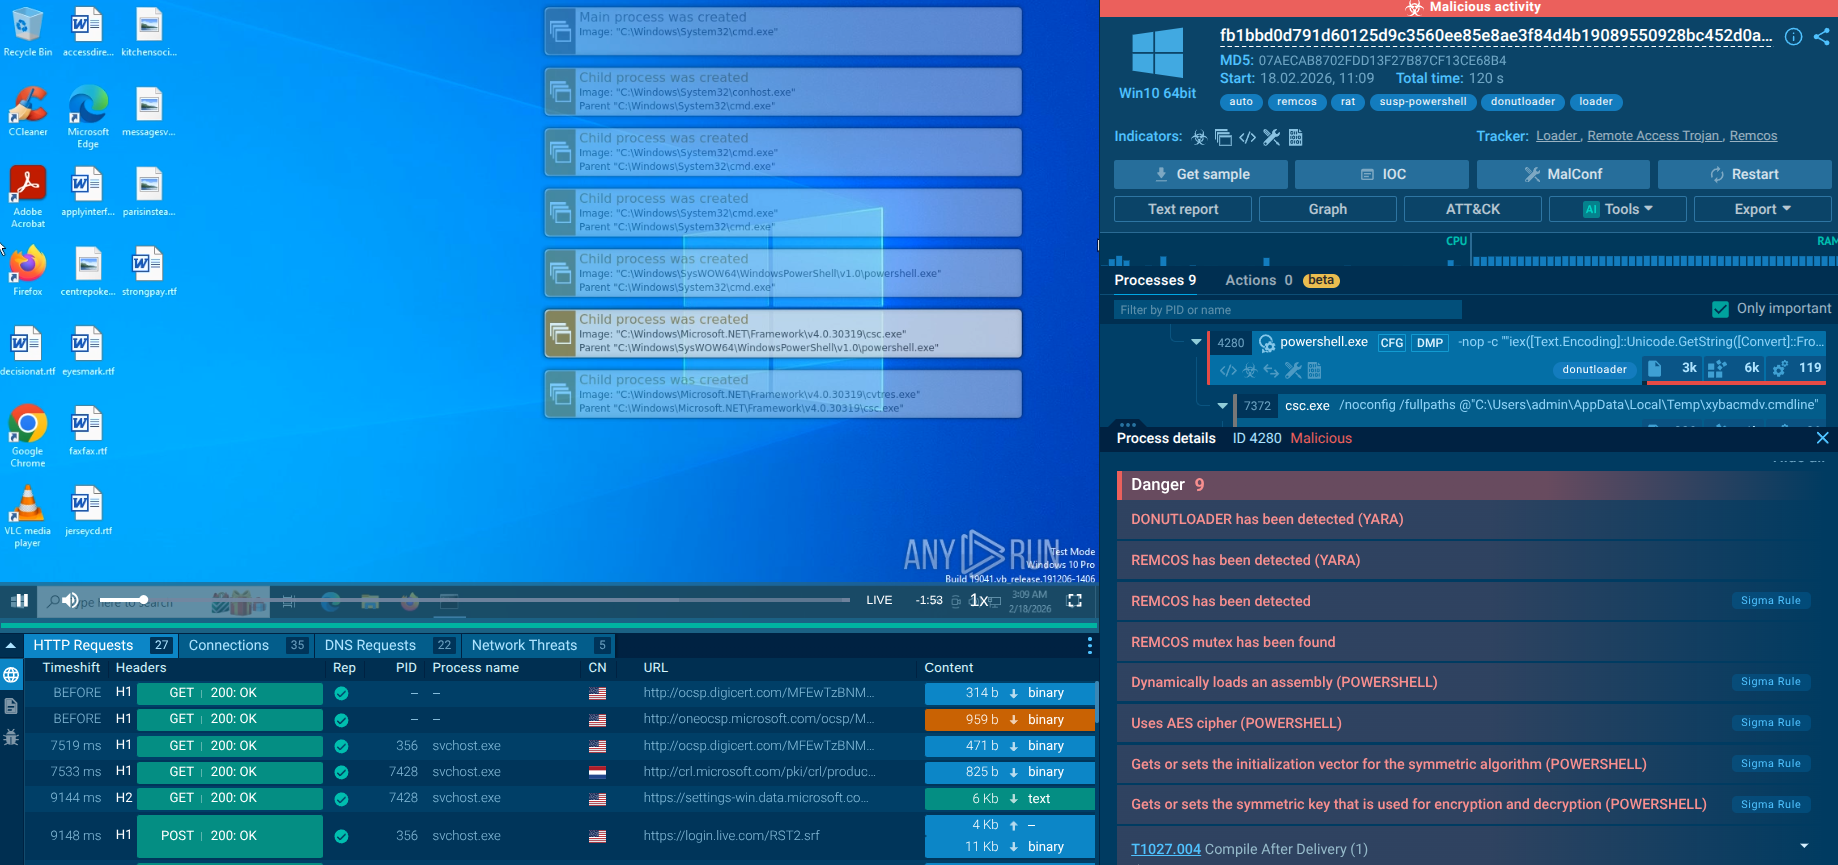
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
EvilTokens screenshot
EvilTokens
eviltokens
EvilTokens is a phishing-as-a-service (PhaaS) toolkit that emerged in mid-February 2026. It automates device code phishing attacks against Microsoft 365 and Entra ID environments. Unlike traditional credential-harvesting phishing, EvilTokens tricks users into completing legitimate authentication on Microsoft's own login pages, resulting in the issuance of valid OAuth access and refresh tokens directly to the attacker, effectively bypassing MFA without stealing passwords.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
DarkComet screenshot
DarkComet
darkcomet rat darkcomet rat
DarkComet RAT is a malicious program designed to remotely control or administer a victim's computer, steal private data and spy on the victim.
Read More
Chaos Ransomware screenshot
Chaos ransomware is a malware family known for its destructive capabilities and diverse variants. It first appeared in 2021 as a ransomware builder and later acted as a wiper. Unlike most ransomware strains that encrypt data to extort payment, early Chaos variants permanently corrupted files, while later versions adopted more conventional encryption techniques.
Read More
 screenshot
Cephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
Read More