Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

X-Files

115
Global rank
106 infographic chevron month
Month rank
166 infographic chevron week
Week rank

X-FILES Stealer is a sophisticated malware designed to infiltrate systems and steal sensitive information, targeting login credentials for email, social media, and other personal accounts. It captures data and transmits it back to the attacker’s command-and-control server. X-FILES Stealer employs advanced evasion techniques to avoid detection, making it a persistent threat in the cyber landscape.

Stealer
Type
Unknown
Origin
15 March, 2021
First seen
29 September, 2026
Last seen

How to analyze X-Files with ANY.RUN

Type
Unknown
Origin
15 March, 2021
First seen
29 September, 2026
Last seen

IOCs

IP addresses
20.190.159.0
48.209.138.189
135.233.95.144
23.11.40.157
48.209.133.15
23.59.18.102
88.221.169.205
20.190.160.66
23.216.77.21
48.209.6.48
2.16.204.161
128.24.231.65
20.165.94.54
20.190.160.4
74.179.77.164
23.216.77.19
162.159.36.2
172.211.123.248
88.221.169.152
40.126.31.69
Hashes
96ad1146eb96877eab5942ae0736b82d8b5e2039a80d3d6932665c1a4c87dcf7
e8f64f6f49b8231476e1028b75f2a3e5317ed506db6d1a265dbf3c28eb3e1d1a
7dd0f969d34bcf859f9f51d9a89e04fb148bcab5c53deeb0639f6f6caca1fcf5
ffc5a5b764fa73b53fdbe64635b9c9b6b0b4970f630b09c764a95f3dbdb6f39a
6711eeecd086805bec03e70bda9e67b61672a742e0b1bad2b850b557fca8b4c2
644fbcdc20086e16d57f31c5bad98be68d02b1c061938d2f5f91cbe88c871fbf
cb87767c4a384c24e4a0f88455f59101b1ae7b4fb8de8a5adb4136c5f7ee545b
23dbf7014e99e93af5f2760f18ee1370274f06a453145c8d539b66d798dad131
1d99606f22103835ff578762993275bbea5c2a2e39c95c47fead6e58d675fc40
28825ea8245e6bcd88c3b4d744e07712f905d316d7005845629b4f98b7d533b9
30c33f3014bfcb787ce179885102110fba44ef77616d8588d6a75be083d8c737
c5b0c7f557f169fa82d559ec0d4489ddaf1f55f40e93187deecd367f5897e517
0dd5f95e389b3ee3ee3fb3d979ca8d9aa1bddd86e54b45d32eb06ef681a9bcb1
a8efb52ac958f52d0b31cea90502e34e3adc9a08a6c33ce90e9ec32391069a5b
e1bcdc31e8eb46e6a218c54ef75e170a0715598395294c9775722bf7e4b5b672
43eaecc6758a0394e9027776ebf163717281172eed6b7cbff4a73921db80feae
daef40b3421ccffdd6565bdd86991560515a9ef0ea118d4ba42e2acfd2b667f0
fbafe89d3e3e5b0325a6d9cd9b4cee60aef1504025cc86874f9b857a336e2c92
1ce6d277a48b0d00d3e948346e0ecf866e954a75233f110aef7024c3038c6cbb
ab5a6d62d091d97c302989b572c74b689593750d4d2aa257450a45473857cb58
Domains
settings-win.data.microsoft.com
www.microsoft.com
google.com
crl.microsoft.com
go.microsoft.com
slscr.update.microsoft.com
self.events.data.microsoft.com
login.live.com
activation-v2.sls.microsoft.com
ocsp.digicert.com
fe3cr.delivery.mp.microsoft.com
164.77.179.74.in-addr.arpa
client.wns.windows.com
ecs.office.com
dns.msftncsi.com
nexusrules.officeapps.live.com
watson.events.data.microsoft.com
www.bing.com
oneocsp.microsoft.com
processhacker.sourceforge.net
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://login.live.com/rst2.srf
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 2474
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 4783
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 7302
comments 0

What is X-FILES malware?

X-FILES is a sophisticated infostealer that primarily targets sensitive data, including login credentials, financial information, and other personal details. Since its initial discovery in March 2021, the malware has undergone various updates that have enhanced its capabilities and delivery methods.

While specific campaigns are not widely publicized, X-FILES Stealer has been involved in various phishing campaigns targeting users and organizations, particularly focusing on individuals who store sensitive information in browsers and email clients.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

X-FILES malware technical details

X-FILES Stealer steals login credentials, hijacks accounts, and exfiltrates other sensitive data to its command-and-control (C2) servers. The malware can also use the compromised accounts to spread further infections.

The primary functionalities of X-FILES malware include:

  • Steals sensitive information like login credentials, cookies, browsing history, and cryptocurrency data.
  • Gains unauthorized access to personal and corporate accounts, including email and social media.
  • Alters startup directories or registry settings to ensure the malware runs on every system boot.
  • Runs its payload directly in memory to evade traditional detection methods.
  • Uses complex encoding and decryption to avoid detection by security tools.
  • Exploits known vulnerabilities through phishing emails with malicious attachments or links.

Cybercriminals often use a variety of file types to deliver X-FILES Stealer and other malware through phishing emails. These files include executable files (.exe), archive files like RAR and ZIP, and documents such as PDFs, JavaScript files, and Microsoft Office documents. The attachments are designed to appear legitimate, luring users into opening them and unknowingly initiating the malware infection.

A significant aspect of X-FILES Stealer’s operation is its integration with Telegram. The malware utilizes Telegram as a communication platform to exfiltrate stolen data.

This method is advantageous for attackers because Telegram offers end-to-end encryption, providing a level of anonymity and security that makes it difficult for cybersecurity professionals to trace the data back to its source. The malware sends the exfiltrated data directly to a Telegram bot or channel controlled by the attackers, where it can be accessed remotely and anonymously.

X-FILES Stealer execution process

To see how X-FILES stealer operates, let’s upload its sample to the ANY.RUN sandbox.

The infection chain usually begins with phishing emails containing malicious attachments, which are often disguised as legitimate documents, such as Word, Excel, or other Office files. When users open these documents, they may unknowingly execute embedded scripts that trigger the malware's payload.

One of the recent variants of X-FILES uses the Follina vulnerability (CVE-2022-30190), which allows attackers to execute PowerShell commands simply by opening a Word document. This document contains an OLE object that references an external HTML file, which subsequently executes JavaScript to download the malware payload.
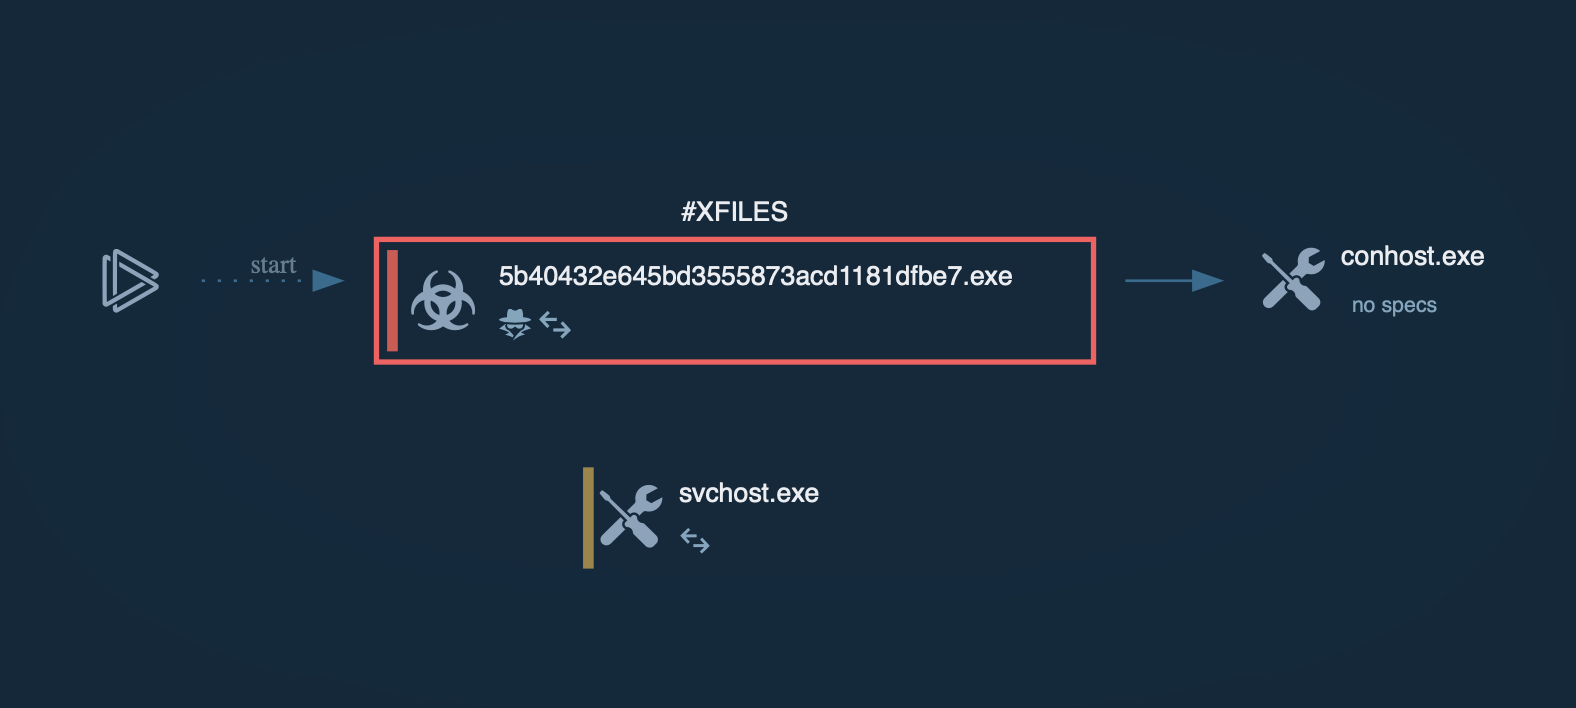
X-FILES Stealer process graph in ANY.RUN X-FILES Stealer process graph shown in ANY.RUN sandbox

Once the document is opened, it retrieves a base64-encoded string containing PowerShell commands. These commands establish persistence on the infected machine by placing the malware in the Windows startup directory and executing it.

The main payload includes encrypted shellcode, which is decrypted and executed in memory. This approach enables the malware to run without leaving significant traces on the disk, making it more difficult to detect.

The stolen data is typically stored in newly created directories on the infected machine and is exfiltrated using secure channels, often via Telegram, providing attackers with a degree of anonymity.

X-FILES Stealer delivery methods

X-FILES Stealer is distributed through a variety of methods, each designed to exploit common vulnerabilities and user behaviors:

  • Infected email attachments: The most common method involves phishing emails with infected attachments, tricking users into opening them and initiating the malware.
  • Malicious online advertisements: Also known as malvertising, this method involves embedding malware in online ads. When users click on these ads, they are redirected to a compromised website or directly download the malware, unknowingly initiating the infection.
  • Social engineering: Attackers employ deceptive tactics like fake security alerts or bogus software updates to convince users to download and install the malware.
  • Pirated software: X-FILES Stealer is often bundled with pirated software and 'cracks,' leading users who download these tools to unknowingly infect their systems.

Conclusion

X-FILES Stealer’s focus on hijacking accounts and exfiltrating sensitive data highlights the need for strong security measures. Protecting against X-FILES Stealer requires a combination of security practices, including proactive analysis of suspicious emails, files, or links using a malware sandbox.

ANY.RUN offers a powerful solution for this, allowing anyone to analyze and understand the behavior of threats like X-FILES Stealer in a controlled environment. By using ANY.RUN, you can proactively identify and respond to these threats before they can compromise your data.

Sign up for a free ANY.RUN account to analyze malware and phishing without limits!
HAVE A LOOK AT

BTMOB RAT screenshot
BTMOB RAT
btmob
BTMOB RAT is a remote access Trojan (RAT) designed to give attackers full control over infected devices. It targets Windows and Android endpoints. Its modular structure allows operators to tailor capabilities, making it suitable for espionage, credential theft, financial fraud, and establishing long-term footholds in corporate networks.
Read More
Fog Ransomware screenshot
Fog is a ransomware strain that locks and steals sensitive information both on Windows and Linux endpoints. The medial ransom demand is $220,000. The medial payment is $100,000. First spotted in the spring of 2024, it was used to attack educational organizations in the USA, later expanding on other sectors and countries. Main distribution method — compromised VPN credentials.
Read More
Interlock screenshot
Interlock
interlock
Interlock is a relatively recent entrant into the ransomware landscape. First identified in 2023, it's a multi-functional malware strain used in ransomware-as-a-service (RaaS) operations.
Read More
Overlord RAT screenshot
Overlord RAT
overlord
Overlord RAT is a cross-platform remote access framework with Go-based agents and a TypeScript/Node/Bun server. It supports encrypted WebSocket C2, remote control, persistence, and multiple operating systems, including Windows, Linux, and macOS.
Read More
Raspberry Robin screenshot
Raspberry Robin
raspberryrobin
Raspberry Robin is a trojan that primarily spreads through infected USB drives and exploits legitimate Windows commands. This malware is known for its advanced obfuscation techniques, anti-debugging mechanisms, and ability to gain persistence on infected systems. Raspberry Robin often communicates with command-and-control servers over the TOR network and can download additional malicious payloads.
Read More
Mirage2FA screenshot
Mirage2FA
mirage2fa
Mirage2FA is a Phishing-as-a-Service toolkit designed to compromise Microsoft 365 accounts and bypass conventional MFA through Adversary-in-the-Middle attacks. It uses malicious HTML, XHTML, and SVG files to deliver JavaScript loaders that connect victims to attacker-controlled phishing infrastructure. The toolkit relays authentication in real time, capturing credentials, 2FA codes, and authenticated session cookies. It also uses browser fingerprinting, WebSockets, obfuscation, and rotating infrastructure to evade detection and maintain access to compromised accounts.
Read More