Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

WhiteSnake

82
Global rank
80 infographic chevron month
Month rank
71 infographic chevron week
Week rank

WhiteSnake is a stealer with advanced remote access capabilities. The attackers using this malicious software can control infected computers and carry out different malicious activities, including stealing sensitive files and data, recording audio, and logging keystrokes. WhiteSnake is sold on underground forums and often spreads through phishing emails.

Stealer
Type
Unknown
Origin
1 September, 2023
First seen
4 October, 2026
Last seen

How to analyze WhiteSnake with ANY.RUN

Type
Unknown
Origin
1 September, 2023
First seen
4 October, 2026
Last seen

IOCs

IP addresses
140.82.121.3
163.171.128.100
185.199.109.133
176.126.167.7
124.161.226.110
144.31.167.1
172.211.123.248
196.13.6.189
64.89.163.22
185.199.108.133
144.172.71.105
43.228.157.73
116.131.226.149
140.116.87.225
40.126.32.74
211.43.189.159
212.3.113.22
214.2.232.180
218.12.76.157
214.2.205.132
Hashes
a32e0a83001d2c5d41649063217923dac167809cab50ec5784078e41c9ec0f0f
ceebae7b8927a3227e5303cf5e0f1f7b34bb542ad7250ac03fbcde36ec2f1508
3ad2dc318056d0a2024af1804ea741146cfc18cc404649a44610cbf8b2056cf2
275a021bbfb6489e54d471899f7db9d1663fc695ec2fe2a2c4538aabf651fd0f
602c4c7482de6479dd2e9793cda275e5e63d773dacd1eca689232ab7008fb4fb
d95aed234f932a1c48a2b1b0d98c60ca31f962310c03158e2884ab4ddd3ea1e0
8e015cdf2561450ed9a0773be1159463163c19eab2b6976155117d16c36519da
a5b733e3dce21ab62bd4010f151b3578c6f1246da4a96d51ac60817865648dd3
5d9767d8cca0fbfd5801bff2e0c2adddd1baaaa8175543625609abce1a9257bd
f3a7a9c98ebe915b1b57c16e27fffd4ddf31a82f0f21c06fe292878e48f5883e
1ef06c600c451e66e744b2ca356b7f4b7b88ba2f52ec7795858d21525848ac8c
e63550608dd58040304ea85367e9e0722038ba8e7dc7bf9d91c4d84f0ec65887
5cf5bbb861608131b5f560cbf34a3292c80886b7c75357acc779e0bf98e16639
b0eda99eabd32fefecc478fd9fe7439a3f646a864fdab4ec3c1f18574b5f8b34
1a916c0db285deb02c0b9df4d08dad5ea95700a6a812ea067bd637a91101a9f6
dd14133adf5c534539298422f6c4b52739f80aca8c5a85ca8c966dea9964ceb1
f9d3f380023a4c45e74170fe69b32bca506ee1e1fbe670d965d5b50c616da0cb
b56bc94e8539603dd2f0fea2f25efd17966315067442507db4bffafcbc2955b0
a3d5715a81f2fbeb5f76c88c9c21eeee87142909716472f911ff6950c790c24d
d3f6c4e1b8e6d11661d4bdf79b438382bb5951e7a42cedbcac3ebbe88012373c
Domains
rx.indonesias.me
urlhaus.abuse.ch
cid.gov.so
download.pdf00.cn
baolongwes.oss-ap-southeast-1.aliyuncs.com
stdown.dinju.com
activation-v2.sls.microsoft.com
wittenhorst.eu
ecs.office.com
99194034-96-20180108171507.webstarterz.com
cl.ssouy.com
www.zhikey.com
google.com
makemewin.club
tweakz-dream-launcher.lovable.app
hseda.com
m.meta-dm.com
download.haozip.com
cfs5.tistory.com
safeifm.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
http://185.213.240.64/bot.exe
http://193.178.158.57/bin/bc116af5e724cfa4_zx.exe
http://193.178.158.57/bin/67dbf1a8e19934e4_thread_hijacking_cayoy4nb.exe
http://45.135.194.95/bin/support.client.exe
http://151.242.30.165/s.ps1
http://45.135.194.95/bin/screenconnect.clientsetup.exe
http://193.178.158.57/bin/e6efd8bd3bf0fae2_moratorium_0.96.2.9_install.exe
http://158.94.208.124/bin/screenconnect.clientsetup.exe
http://158.94.208.124/bin/support.client.exe
http://178.16.54.109/suckdick.exe
http://84.200.33.163/302/token.cmd
http://178.16.52.209/agent.exe
http://176.65.139.219/bot.exe
http://87130921-60-20220830152356.webstarterz.com/new/secured_stub.ps1
http://87130921-60-20220830152356.webstarterz.com/secured_stub.ps1
http://193.178.158.57/bin/d39b2eac249e8c65_build_x64.exe
Last Seen at
Last Seen at

Recent blog posts

post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2720
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4259
comments 0
post image
Threat Coverage Digest: New Malware Reports a...
watchers 11807
comments 0

What is WhiteSnake malware?

WhiteSnake is a stealer malware whose activity was first observed in early 2023. This malware is designed to infiltrate computer systems and exfiltrate a variety of sensitive information to the attacker’s servers, including saved passwords, autofill information, and browsing history.

WhiteSnake operates as a malware-as-a-service (MaaS), a business model where the developers offer the malware to other cybercriminals for a fee. In the case of WhiteSnake, the developers provide a subscription service for several hundred dollars.

According to the threat intelligence researcher @RussianPanda9xx, the malware’s notable feature is the support of different payload formats like BAT, MSI, SCR, etc.

The distribution and sale of WhiteSnake primarily occurs on DarkWeb forums and Telegram. The availability of the malware contributes to its spread and increases its potential impact.

WhiteSnake has been distributed through various vectors like phishing campaigns, where unsuspecting users are tricked into downloading the malware, and even through open-source repositories.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

WhiteSnake malware execution process

Let’s upload a sample of WhiteSnake to the ANY.RUN sandbox.
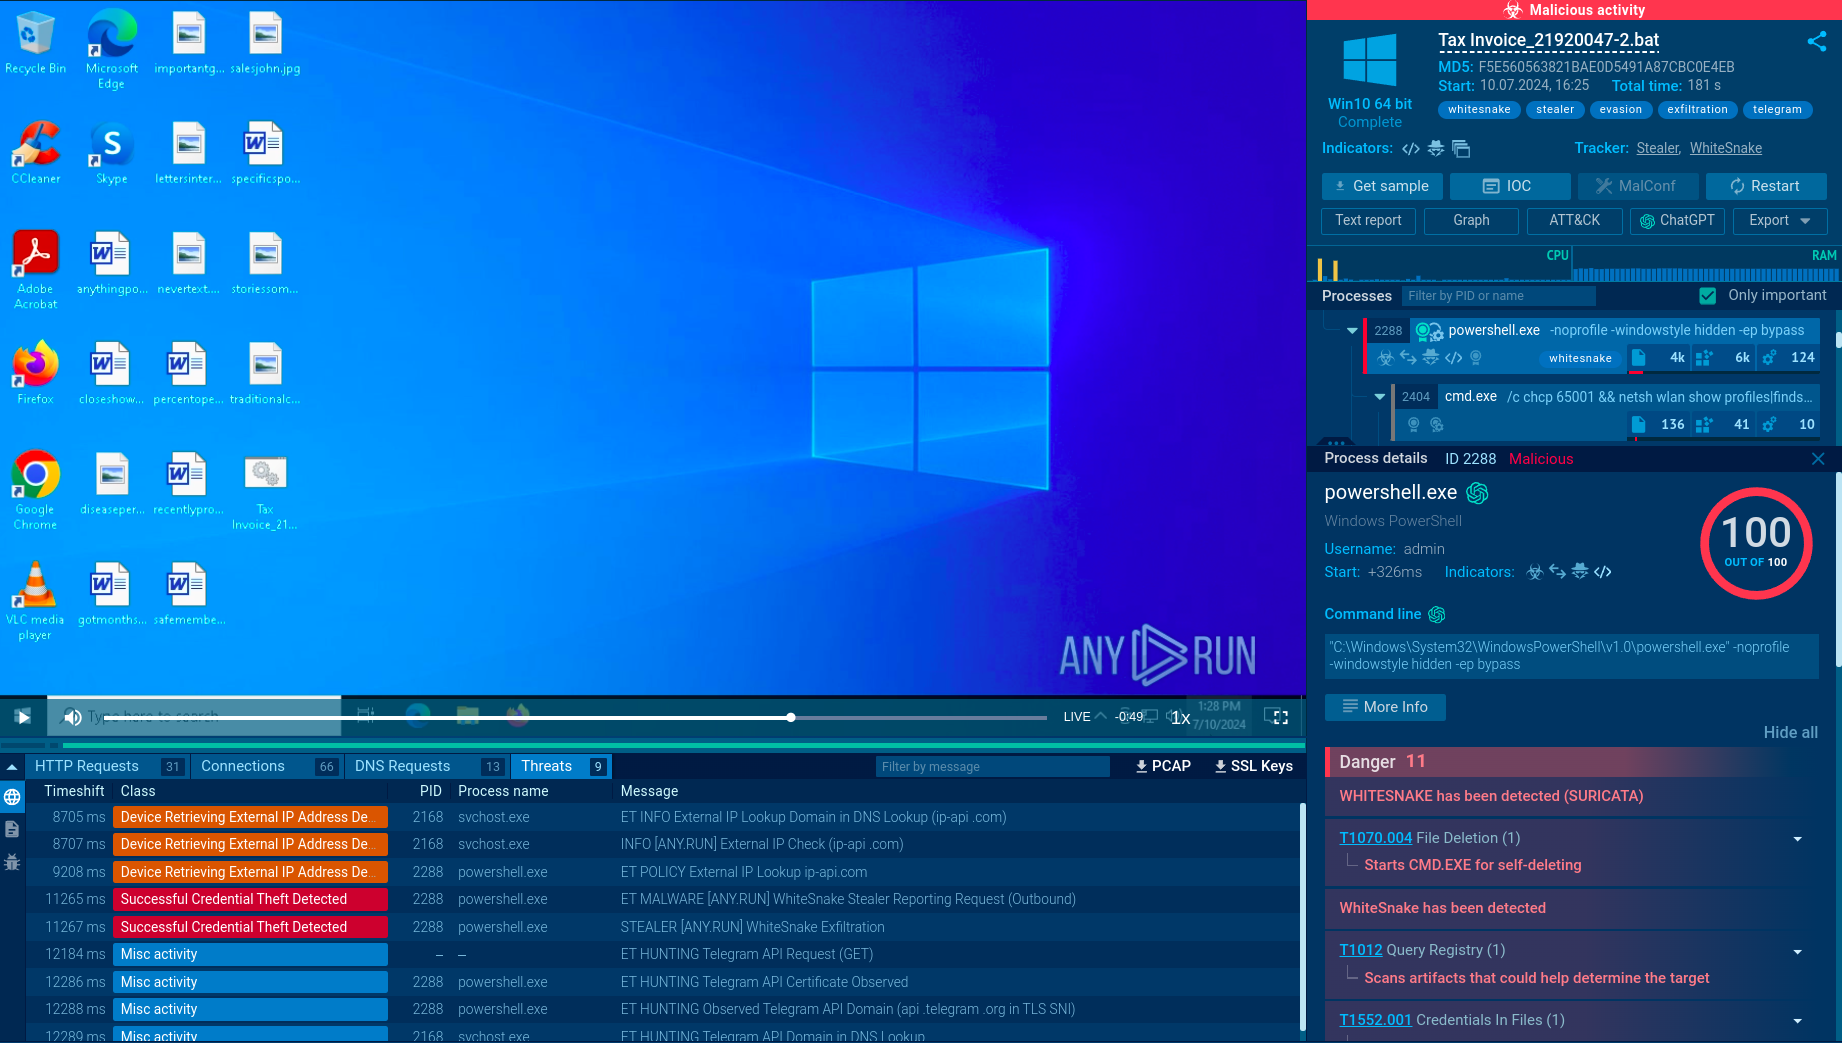
WhiteSnake analysis in ANY.RUN WhiteSnake analysis in ANY.RUN sandbox

WhiteSnake first performs anti-VM checks to detect if it is running in a virtual environment or sandbox. It does this by querying the Windows Management Instrumentation (WMI) to retrieve the "Manufacturer" and "Model" properties of the system. It then checks if any of these properties contain strings associated with virtual machines or sandboxes, such as "virtual," "vmware," "virtualbox," etc. If any of these strings are detected, the malware will exit to avoid analysis.
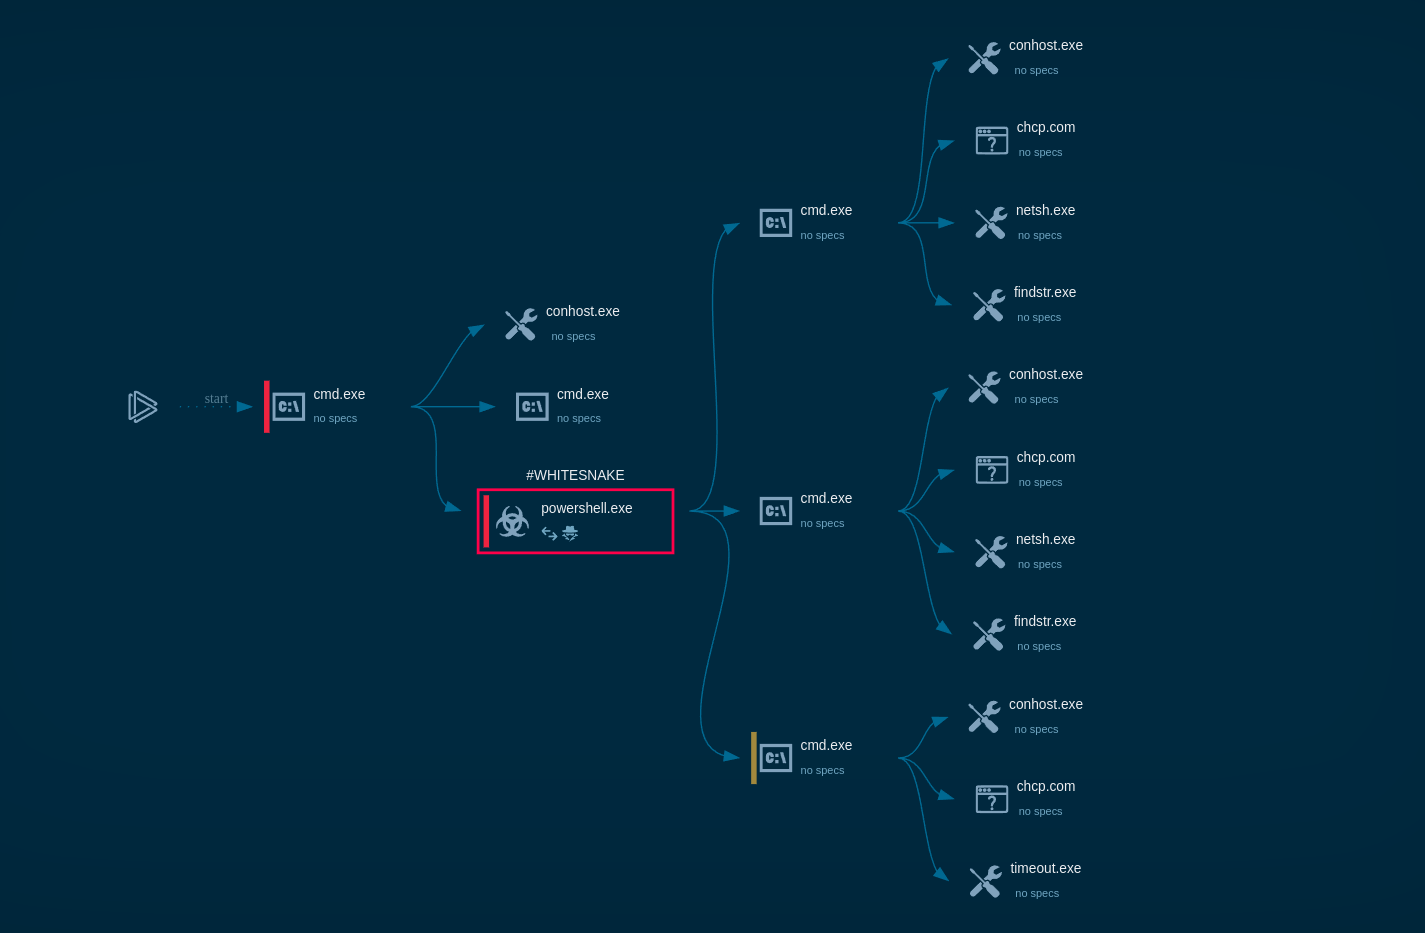
WhiteSnake process graph in ANY.RUN WhiteSnake process graph demonstrated by ANY.RUN sandbox

The malware in our task performs system discovery and uses the command line to display information about available Wi-Fi networks, including SSID, BSSID, and signal strength. It also checks if a mutex (a synchronization object) is already present to prevent multiple instances of the malware from running simultaneously. In our sample, the mutex is "lcy9igxycx."

Then WhiteSnake proceeds to gather sensitive information from the infected system. This includes:

  • Browsing data (cookies, autofill, login data, history, etc.) from various web browsers like Chrome, Firefox, Edge, etc.
  • Cryptocurrency wallet data from popular wallets like Ledger, Atomic, Wasabi, Binance, etc.
  • Cryptocurrency browser extension data from extensions like MetaMask, Ronin, Binance Chain, etc.
  • Other system information like username, computer name, etc.

The gathered information is then encrypted and uploaded to one of the attacker-controlled servers specified in the malware's configuration.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

WhiteSnake stealer technical details

Let’s sum up what the WhiteSnake stealer is capable of. Thanks to its remote command execution functionality. attackers can remotely control the infected system and perform various malicious activities that include:

  • Pulling data from browsers, including Chrome and Firefox, and File Transfer Protocol (FTP) clients.
  • Taking screenshots of the infected system, providing attackers with visual information about the user's activities.
  • Recording audio using the machine's microphone.
  • Taking shots using the web camera.
  • Capturing victims’ keystrokes, which lets attackers discover their login credentials, credit card numbers, and other sensitive information entered by the user.
  • Stealing dozens of crypto wallets, including popular extensions like MetaMask and Phantom, and desktop wallets like Exodus.

One of the key features of this malware is its use of mutex to avoid running on systems that have already been infected. This helps prevent detection and conflict with other instances of the malware.

It is also designed to avoid analysis in a sandbox or virtual machine. The malware includes anti-VM functionality that allows it to detect when it is running in a virtual environment and stop its operation.

WhiteSnake can maintain persistence on the infected system. It automatically runs via a scheduled task, ensuring that it remains active even after the system is restarted.

WhiteSnake malware distribution methods

As mentioned, WhiteSnake is distributed through various methods. However, as with most stealers, including Stealc and Amadey, phishing emails with malicious attachments and links constitute the most widespread vector of attack. In one campaign, criminals leveraged fake documents masquerading as official correspondence from a government agency.

In another attack, threat actors attempted to spread the WhiteSnake stealer through the open-source Python Package Index repository. Attackers uploaded malicious code hoping it would be downloaded and executed by unsuspecting users.

Given that WhiteSnake is a MaaS, available for purchase to various criminals, it is likely that new methods of distributing this threat will be used by criminals in the future.

Conclusion

WhiteSnake is a relatively new but serious cybersecurity threat for organizations worldwide. To prevent infection, it's important to have good security measures in place. One important part of a strong security plan is using a malware analysis sandbox.

ANY.RUN’s interactive sandbox has many features that make analyzing malware easier and faster. It can:
  • Identify threats in files and URLs in less than 40 seconds.
  • Let you interact with samples and the system, just like on a regular computer.
  • Give you customizable Windows and Linux virtual machines to fit your needs.
  • Create detailed reports that explain the threats that were found.
  • Show all activities related to the network, registry, files, and processes.

Create your FREE ANY.RUN account today!

HAVE A LOOK AT

Ramnit screenshot
Ramnit
ramnit
Ramnit is a highly modular banking trojan and worm that evolved from a file-infecting virus into a powerful cybercrime tool. It specializes in financial fraud, credential theft, remote access, and malware delivery, being a serious threat to businesses and individuals. First spotted in 2010, Ramnit became popular after the 2014 takedown of the GameOver Zeus botnet, as cybercriminals sought alternatives for banking fraud.
Read More
DonutLoader screenshot
DonutLoader
donutloader donut
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More