Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Stealc

12
Global rank
26 infographic chevron month
Month rank
28 infographic chevron week
Week rank

Stealc is a stealer malware that targets victims’ sensitive data, which it exfiltrates from browsers, messaging apps, and other software. The malware is equipped with advanced features, including fingerprinting, control panel, evasion mechanisms, string obfuscation, etc. Stealc establishes persistence and communicates with its C2 server through HTTP POST requests.

Stealer
Type
ex-USSR
Origin
1 January, 2023
First seen
8 October, 2026
Last seen

How to analyze Stealc with ANY.RUN

Type
ex-USSR
Origin
1 January, 2023
First seen
8 October, 2026
Last seen

IOCs

IP addresses
150.171.27.11
151.101.129.91
150.171.28.11
40.126.32.68
142.251.110.139
172.211.123.250
104.18.23.222
151.101.1.91
52.123.243.204
142.251.13.132
188.245.231.9
142.251.127.84
142.251.13.113
172.217.118.4
23.11.41.157
48.209.133.15
142.251.14.113
104.21.93.196
34.149.226.178
20.165.94.54
Hashes
81b2bd4ea98c8db66554fbc8d7637a1a69a130f331feb732b75caab4c4868fd5
5c3a5b578ab9fe853ead7040bc161929ea4f6902073ba2b8bb84487622b98923
226eec4486509917aa336afebd6ff65777b75b65f1fb06891d2a857a9421a974
7bfbc8202b8cdbdcc597a0e789240f0dc0b0e94fa6597e576eaf436bc6223e18
cc5dacf370f324b77b50dddf5d995fd3c7b7a587cb2f55ac9f24c929d0cd531a
6e31099ed85eee0f7f89cebe11b2ed14794c2607aecd9a7416c57267f26b27b0
8ff00d859349a3ea206706cdd3fa2762ae7c8efe2fdd33a95a72fee45aac6bc4
884b04032e2e70a002956218e8ec3491f2b753c4596cee6e4894dc49afa0a681
b6dcec10039fba99019a6de818d433847efad62fae59851e328ec42396dfd9cb
0cf098dfe5bbb46fc0132b3cf0c54b06b4d2c8390d847ee2a65d20f9b7480f4c
9b32c491d0bfebdca1455f73c3c6f71796d433a39818c06c353da588de650f81
2824cf97513dc3ecc261f378bfd595ae95a5997e9d1c63f5731a58b1f8cd54f9
64e01bc292ba2ea1699576fcc445367047520ee895e290ccee20c24c9336d8ef
792955295ae9c382986222c6731c5870bd0e921e7f7e34cc4615f5cd67f225da
00ad9799527c3fd21f3a85012565eae817490f3e0d417413bf9567bb5909f6a2
f9d31b278e215eb0d0e9cd709edfa037e828f36214ab7906f612160fead4b2b4
2445cad863be47bb1c15b57a4960b7b0d01864e63cdfde6395f3b2689dc1444b
ff702ca753a7e3b75f9d9850cc9343e28e8d60f8005a2c955c8ac2105532b2c9
af889c1deb6f9248961c2f8ba4307a8206d7163616a5b7455d17cead00068317
728d8cbd71263680a4e41399db65b3f2b8175d50ca630afd30643ced9ffe831f
Domains
client.wns.windows.com
api.edgeoffer.microsoft.com
safebrowsingohttpgateway.googleapis.com
example.org
self.events.data.microsoft.com
copilot.microsoft.com
clientservices.googleapis.com
config.edge.skype.com
update.googleapis.com
accounts.google.com
ocsp.digicert.com
fe3cr.delivery.mp.microsoft.com
edge.microsoft.com
www.bing.com
firefox.settings.services.mozilla.com
clients2.googleusercontent.com
www.google.com
settings-win.data.microsoft.com
clients2.google.com
go.microsoft.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f7%2f2026%2c%2011%3a23%3a13%20pm
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.dd24d9ab-b64b-48ec-9cd9-dc7f2e98579e&pid=dsb
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://telegram.me/bj00tyr
https://kl.333vip.org/
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
http://clients2.google.com/time/1/current?cup2key=8:zgzlmp3hrh_3yixcq58ns_ixciqwbpb7c0gzcpupg1w&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://safebrowsingohttpgateway.googleapis.com/v1/ohttp/hpkekeyconfig?key=aizasya2klwbx3mkfo30om9lufyqhpqloa_bnhe
https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=133
https://accounts.google.com/listaccounts?gpsia=1&source=chromiumbrowser&json=standard
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 230
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2820
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4352
comments 0

What is malware: Stealc?

Stealc is an infostealer written in C that has been promoted and sold on DarkWeb forums since the beginning of 2023. This malware is primarily used to steal sensitive data from programs, such as web browsers, email clients and messengers. Some examples of such software include Discord, Telegram, and Outlook. This malicious software also has the capability to grab files from infected systems and drop additional malware on them.

According to an interview conducted by threat researcher g0njxa with the developers of the malware, the unique feature of Stealc is the provision of a PHP control panel that has to be hosted on the operator's own server, which gives them more privacy.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Stealc malicious software technical details

Stealc has a range of functions that make it a serious threat. Here are some of its notable features:

  • Fingerprinting: Stealc collects different info about the infected system, including public IP address, geolocation, hardware ID, OS version, etc.
  • Control Panel: Attackers are provided with a control panel for managing attacks and configuring the malware. The panel allows attackers to manipulate stolen data and make changes to their campaigns.
  • Evasion Mechanisms: Stealc checks for virtual or sandbox environments to evade detection. It also uses unconditional jumps to make the decompilation process more time-consuming and error-prone. Additionally, Stealc checks for the presence of antivirus software and terminates itself if it detects any.
  • String obfuscation: The malware relies on RC4 encryption and base64 encoding to protect its strings.
  • Dropping Other Malware: Stealc can also upload additional malicious software on to the victim’s machine, such as Laplas Clipper, which intercepts clipboard data and replaces cryptocurrency wallet addresses with the attacker's own address.

Stealc requires external DLLs that are not embedded in the PE but rather downloaded from a specific URL hosted by the C2. The downloaded DLLs include sqlite3.dll, freebl3.dll, mozglue.dll, etc. These DLLs provide additional functionality to the malware, such as interacting with SQLite databases, encrypting data, and interacting with Mozilla-based applications.

After establishing persistence, Stealc begins its communication with the C2 server, first requesting its configuration and then exfiltrating stolen data with the help of HTTP POST requests.

In summary, Stealc is a sophisticated malware that can steal sensitive data, evade detection, establish persistence, and communicate with a C2 server. Its unique features and capabilities make it a significant threat to cybersecurity. It is crucial for individuals and organizations to take proactive measures to protect themselves from such threats.

Stealc execution process

To analyze Stealc, we can upload its sample to the ANY.RUN sandbox for detailed analysis.

Stealc malware typically operates through a multi-stage execution chain to compromise systems and steal sensitive information. Initially, it may infiltrate a target system through various means such as phishing emails, malicious downloads, or exploiting software vulnerabilities. Once inside, it may establish persistence mechanisms to ensure its continued operation even after system reboots. Stealc then proceeds to escalate its privileges to gain deeper access to the system and evade detection.

It often employs techniques like code injection or hooking to hide its presence from security software. Finally, the malware executes its primary function of stealing data, such as login credentials, financial information, or personal documents, and exfiltrates it to remote servers controlled by the attackers. Throughout this process, Stealc may employ encryption and obfuscation techniques to further mask its activities and evade detection by security measures.
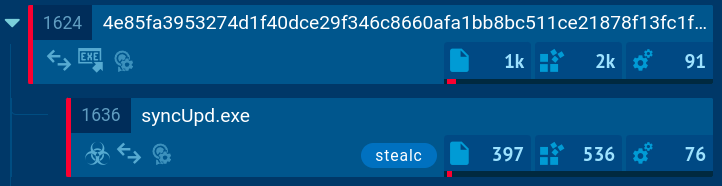
Stealc process tree shown in ANY.RUN Stealc process tree demonstrated in ANY.RUN

In the example, the malware checks the operating system language and creates a scheduled task through the Windows Task Scheduler to repeatedly execute malicious code. However, the execution chain of Stealc often consists of a single process that performs all malicious activities.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Stealc malware distribution methods

Attackers employ various methods to distribute Stealc malware. One of the most common methods is the use of fake websites offering legitimate software for download. Users are tricked into downloading Stealc instead of the program they were looking for.

Another distribution method is through malicious email attachments. Attackers send phishing emails with malicious attachments, such as Microsoft Office documents or PDF files, that contain the Stealc payload.

Stealc can also be dropped by loaders, malicious programs that are designed to download and install other malware onto a compromised system. One example is CrackedCantil, which is a loader that has been observed dropping Stealc, as well as other ones, such as Lumma, RisePro, and RedLine.

Conclusion

Stealc is an advanced malware that can steal sensitive data, evade detection, and maintain persistence on compromised devices. To safeguard against such threats, individuals and organizations need to take proactive measures. ANY.RUN is an online sandbox that provides an effective solution for this purpose.

ANY.RUN's sandbox provides a secure and isolated environment for running and analyzing malware samples. This allows users to observe the behavior of the malware without putting their systems at risk. The detailed technical reports generated by ANY.RUN provide insights into the malware's functionality, communication patterns, and other important characteristics.

Create your ANY.RUN account – it’s free!
HAVE A LOOK AT

LockBit screenshot
LockBit
lockbit
LockBit, a ransomware variant, encrypts data on infected machines, demanding a ransom payment for decryption. Used in targeted attacks, It's a significant risk to organizations.
Read More
Quasar RAT screenshot
Quasar RAT
quasar trojan rat
Quasar is a very popular RAT in the world thanks to its code being available in open-source. This malware can be used to control the victim’s computer remotely.
Read More
Oblivion RAT screenshot
Oblivion RAT
oblivion
Oblivion RAT is a sophisticated Android Remote Access Trojan (RAT) offered as Malware-as-a-Service (MaaS) on cybercrime forums for as little as $300 per month. It equips even novice attackers with a complete toolkit, including a web-based APK builder, dropper generator mimicking Google Play updates, and a real-time C2 panel. The RAT enables full device takeover, data theft, and financial fraud through deceptive social engineering and Accessibility Service abuse.
Read More
Keylogger screenshot
Keylogger
keylogger
A keylogger is a type of spyware that infects a system and has the ability to record every keystroke made on the device. This lets attackers collect personal information of victims, which may include their online banking credentials, as well as personal conversations. The most widespread vector of attack leading to a keylogger infection begins with a phishing email or link. Keylogging is also often present in remote access trojans as part of an extended set of malicious tools.
Read More
Mispadu screenshot
Mispadu is a Windows banking trojan known for targeting online banking credentials, cryptocurrency wallets, and sensitive financial information. First identified in Latin America, the malware has continuously evolved with improved evasion techniques, phishing campaigns, and credential theft capabilities. Its reliance on social engineering rather than software vulnerabilities makes it an enduring threat to organizations whose employees interact with financial services online.
Read More
Prometei screenshot
Prometei
prometei
Prometei is a modular botnet malware family that silently infiltrates systems, hijacking their resources for illicit Monero (XMR) mining. Active since at least 2016, it combines stealth, persistence, and lateral movement capabilities. Notable for its global reach and opportunistic infection strategy, it is also used for credential theft.
Read More