Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
145
Global rank
113 infographic chevron month
Month rank
89 infographic chevron week
Week rank

Zloader is a banking trojan that uses webinjects and VNC clients to still banking credentials. This Trojan is based on leaked code from 2011, but despite its age, Zloader’s popularity has been only increasing through early 2020, when it relied on COVID-19 themed attacks.

Banking trojan
Type
Unknown
Origin
1 May, 2016
First seen
9 October, 2026
Last seen
Also known as
Terdot
Zbot
DELoader

How to analyze Zloader with ANY.RUN

Banking trojan
Type
Unknown
Origin
1 May, 2016
First seen
9 October, 2026
Last seen

IOCs

IP addresses
40.126.31.73
48.209.138.168
92.123.104.27
135.232.92.137
20.165.94.54
172.211.123.250
150.171.109.105
23.52.181.212
57.153.246.3
95.100.158.106
48.209.138.189
135.233.95.144
95.100.102.101
172.211.123.248
23.48.23.177
74.178.76.54
2.16.241.215
48.192.1.65
2.16.241.7
23.59.18.102
Hashes
549fd604fcf3fa026cad3ec20923b004d0b38c8b78ce9bafae895e3d9a26c735
b753e5e87586515dbb546f7c6b8434c06ae470abe0cba72de49fbd1411e4ad19
8f08500677b6b9fd236e33f36e8157e57fd11e692d7b7b285210197df39cd410
f4caed5f38e269a84d583267662a9aa1952bf9c41a949268e42f2463f5fb868f
80092b078bdfa49fc30e0bfd7e1d16e530ab0a74a40540cb5b458bcb1a0b3659
e30e97c4b7cbf75398d58f9ebed0e74a5cbfb4399f26cb44601389b396fad62a
f3bc041a3286f39b32d4acbaaa01c6f0823ce0fc9904f5b82da5901ffaff6420
371735e61f95740aa3847d4adb0d78122f79fb2410bfd37ea80ac1926d5ecb9c
2e411744c99b0311ed1aecccd4a1209ce50037f27f52ee17205a7b847eeb3ab9
cbe219e1b91683750cbcfa21ef53f6c6406eef5046bf74b936f75744d99c1058
7c716d619793deeaf7b5454a0235a12fb4670c48f6c34229fcf0d74a074f88ff
fd2e596433ffa085f2b66a29035c7301117042762b45af376af91edfe36ae0ca
9a1b4e8fb16d69690e52748aac601ace68dc9c1186e2d886fa26220cb8486be1
035db4bb1698e67eed83c217b196e342dc8ab8bb6ace3c2960f413a2bfab3158
13515db126c36118b819b2207bcbcb8dcada59e97a4e88eda3fcf80f2c74d4f6
0ae7cd0ceb54cc1a7e2902002a599e60d3feaefed87de3088f6092758317a0d0
f49b515eedeed1abe391bc32f15ce43d3582cb6c41ff944fa9c79f476d5824ba
4525eb26933d425b79448dfc697c2648312a5ecb805726013000c1b0e3083734
b3b83f42fb87c7f87a4fdea07808517a8829436a094d81d6df4b408749f699e8
ee3920a7d69c74255c50eaad8b98cf01f3ba15a317ac668ff067aaa08052a0f5
Domains
crl.microsoft.com
login.live.com
www.microsoft.com
fe3cr.delivery.mp.microsoft.com
ecs.office.com
google.com
slscr.update.microsoft.com
settings-win.data.microsoft.com
self.events.data.microsoft.com
client.wns.windows.com
www.bing.com
activation-v2.sls.microsoft.com
nexusrules.officeapps.live.com
go.microsoft.com
softwareserviceupdater5.com
ocsp.digicert.com
ctldl.windowsupdate.com
v10.events.data.microsoft.com
mrodevicemgr.officeapps.live.com
dns.msftncsi.com
URLs
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.2.crl
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20time-stamp%20pca%202010(1).crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20signing%20ca%202.1.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
http://softwareserviceupdater5.com/web/post.php
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
Last Seen at

Recent blog posts

post image
What's Really Attacking Your Industry? Insigh...
watchers 1699
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 9585
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 10824
comments 0

What is Zloader?

Zloader, also known as Terdot and Zbot is a banking trojan. It uses web injects to steal passwords and auth codes of its victims. The trojan was first spotted in 2016 but it has seen a sudden surge of activity in the winter of 2019, appearing in over 100 email campaigns.

Zloader is constructed using the leaked code of the well-known ZeuS malware. ZeuS code was made public in 2011 and became a base for various malware samples. The fact that its variants are still being used goes to show how effective the original malware was.

General description of Zloader malware

Researchers first observed Zloader, also known at the time as DELoader, in 2016, when it started attacking Canadian banking organizations. The malware’s name highlights two facts: the letter “Z” shows that it is based on the Zeus Banking Trojan and the word “loader” highlights the malware’s unique design. Zloader makes its way into the machines of the victims using a loader that installs the final payload.

Zloader became quite popular and served as the main tool for several hackers, with TA511 also known as Hancitor being the most acknowledged. After working with Zloader for almost 2 years, Hancitor made a jump to Panda Banker. Others soon followed suit and Zloader became abandoned until 2019, when researchers detected a sudden surge of attacks.

Possibly, attackers pursued the opportunity presented with the confusion that surrounds the COVID crisis, launching a new wave of campaigns in December 2019, with the number of sightings only increasing by March 2020.

Although, previously Zloader focused on finding victims in Canada, starting with 2020 it expanded the geography of operations. The newer campaigns attack financial institutions all over the world, including the US, Australia, and Europe.

The malware uses a technique called web injects to trick victims into revealing their authentication codes. Zloader replaces the banking website of the victim with an identical copy fetched from a custom file so that unsuspecting users give away credentials thinking that they are logging into their bank. In reality, the sensitive information, including auth codes, is sent to the C&C controlled by the attackers.

Additionally, Zloader can fetch information from browsers, accessing cookies and passwords — a standard functionality for banking trojans.

Interestingly, the 2019 version of Zloader is less advanced than its predecessor, seen in 2016. Researchers think that it might be a revision of an older iteration of the malware that lacked some of the sophisticated malicious techniques.

Among the missing features are code obfuscation and string encryption — those are both techniques threat actors use to complicated static analysis of malware by making the code unreadable.

However, that does not mean that Zloader should be taken lightly. It's still top-level malware and it is highly dangerous.

For example, if attackers manage to get a hold of the credentials, they use a smart technique to log into the account without raising red flags with the bank. The threat actors log in with a virtual network computing client, so all the bank sees is another session from the normal victim’s machine. This way, not only can attackers withdraw money without raising any alarms but proving that the transaction fraudulence is also difficult.

On top of that, the malware still uses some anti-evasion techniques like Command & Control blacklisting and Windows API function hashing, making the analysis more complicated. Another worrying sign is the constant maintenance of Zloader. No less than 18 versions have been seen circulating in the wild from January to March 2020. The malware is being constantly improved.

Zloader malware analysis

We can watch the complete execution process of Zloader in a video recorded in the ANY.RUN interactive malware hunting service. Moreover, check out other malware analyses such as FlawedAmmyy.
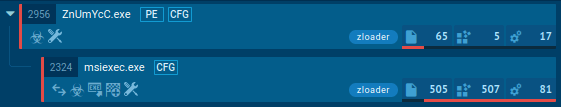
Zloader process graph

Figure 1: Shows the process graph, automatically created in ANY.RUN

Zloader execution process

Zloader usually makes its way into systems as an executable or as a script file. When entering as a script file, it runs and compiles into the library by the wscript process. As an executable file, the malware makes an injection into the msiexec.exe process. After that Zloader tries to connect to Command & Control server over HTTPS to download additional modules.

Zloader distribution

Zloader is distributed to victims with malspam. Emails are crafted to look like government notices or financial support offered due to the COVID-19 epidemic. Attached to emails are malicious files, normally with Microsoft Office file extensions, but PDF files were also observed.

When opened, the files ask the victim to enable macros. If users compile, the macros download a loader that establishes a connection with the command and control server and installs the final payload — Zloader.

How to detect Zloader?

Since Zloader creates registry keys with pseudo-random names under HKEY_CURRENT_USER\Software\Microsoft and directories with pseudo-random names inside the %APPDATA% directory. This activity can help analysts detect this malware family. To take a look at the registry changes and created directories, just click on the msiexec process and then click on the “More info” button.

Conclusion

Despite being based on code that was leaked no less than 9 years ago, Zloader still poses a massive threat to cybersecurity.

From late 2019, this banking trojan targets financial institutions all around the world with COVID-19 themed attacks. It appeared in over 100 email campaigns after being inactive for nearly 2 years and now wreaks havoc on the banking world, using web injects and VNC sessions to steal credentials.

Thankfully, using ANY.RUN, researchers can analyze Zloader in a secure online environment and take advantage of our interactive sandbox. With our service, malware hunters can get results on the fly, while still being in control of all simulation variables, saving massive time on dynamic analysis. Studying threats like Zloader is a sure way to develop a sound cybersecurity strategy or prepare an action plan should your organization come under attack.
HAVE A LOOK AT

Crocodilus screenshot
Crocodilus
crocodilus
Crocodilus is a highly sophisticated Android banking Trojan that emerged in March 2025, designed for full device takeover. Disguised as legitimate apps, it steals banking credentials, cryptocurrency wallet data, and enables remote control, rapidly evolving into a global threat targeting financial users across Europe, South America, and Asia.
Read More
NetSupport RAT screenshot
NetSupport RAT
netsupport
NetSupport RAT is a malicious adaptation of the legitimate NetSupport Manager, a remote access tool used for IT support, which cybercriminals exploit to gain unauthorized control over systems. It has gained significant traction due to its sophisticated evasion techniques, widespread distribution campaigns, and the challenge it poses to security professionals who must distinguish between legitimate and malicious uses of the underlying software.
Read More
GuLoader screenshot
GuLoader
guloader
GuLoader is an advanced downloader written in shellcode. It’s used by criminals to distribute other malware, notably trojans, on a large scale. It’s infamous for using anti-detection and anti-analysis capabilities.
Read More
RatonRAT screenshot
RatonRAT
raton
RatonRAT is a .NET-based Remote Access Trojan targeting Windows systems. It supports credential theft, screen capture, system and hardware discovery, persistence, and C2 communication. Samples use techniques such as Registry Run keys and scheduled tasks for persistence, with some variants employing anti-analysis and evasion techniques.
Read More
StrelaStealer screenshot
StrelaStealer
strela
StrelaStealer is a malware that targets email clients to steal login credentials, sending them back to the attacker’s command-and-control server. Since its emergence in 2022, it has been involved in numerous large-scale email campaigns, primarily affecting organizations in the EU and U.S. The malware’s tactics continue to evolve, with attackers frequently changing attachment file formats and updating the DLL payload to evade detection.
Read More
UpCrypter screenshot
UpCrypter
upcrypter
UpCrypter is a sophisticated malware loader that functions as a delivery mechanism for remote access tools. Distributed through global phishing campaigns targeting Windows systems, this actively maintained tool serves as the central framework for deploying various RATs including PureHVNC, DCRat, and Babylon RAT, enabling attackers to establish persistent remote control over compromised systems.
Read More