
American trucking and logistics companies rely on digital platforms to verify carriers, onboard brokers, exchange documents, and coordinate freight. Cybercriminals increasingly exploit these routine business processes.
ANY.RUN researchers investigated three campaigns targeting the US logistics sector: HelloFriends, NodeRemote, and Fake Freight Portals. Each uses familiar business interactions to steal sensitive data, deploy malware, or gain remote access.
For SOC and MSSP teams, these campaigns highlight a key challenge: effective defense requires more than blocking suspicious files. Analysts must understand attack behavior, connect indicators to broader threats, and turn investigation findings into actionable detection.
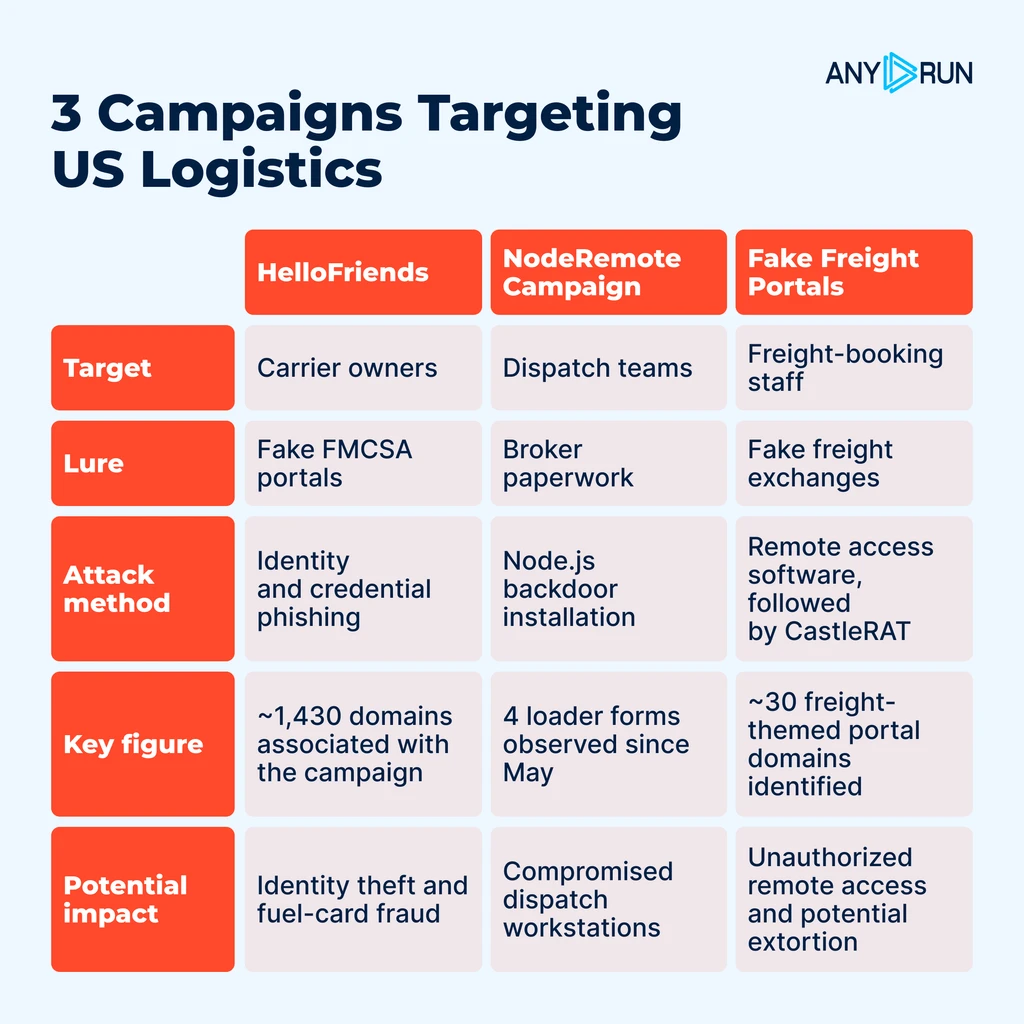
HelloFriends: Fake Carrier Verification Portals Steal Sensitive Data
HelloFriends is a credential-harvesting campaign targeting US trucking companies through fraudulent websites impersonating legitimate carrier verification services, including SAFER and Motus.
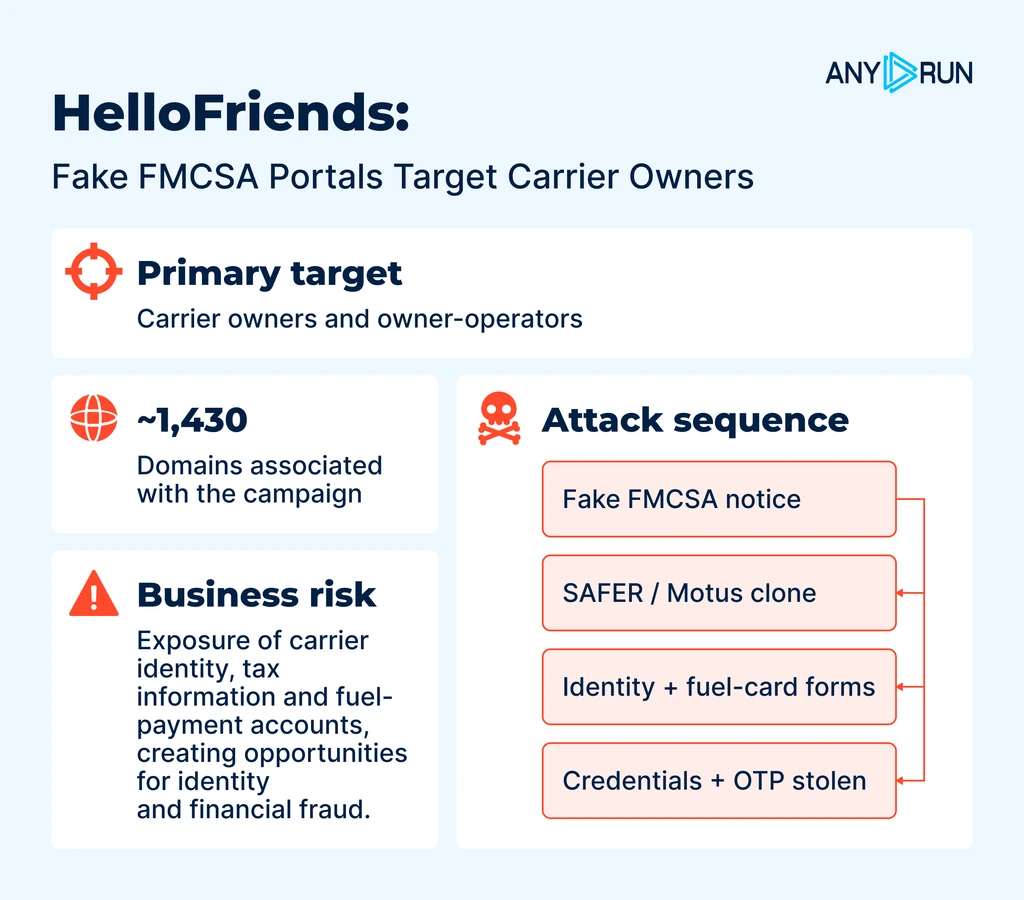
The attackers personalize these portals using information such as a company’s USDOT number, making the pages appear relevant and trustworthy. Victims are prompted to submit sensitive business and personal information, including Social Security numbers, EINs, fuel-card credentials, and passwords.
Some pages request passwords twice and use OTP prompts to capture additional authentication data. The collected information is then transmitted to the attackers through Telegram.
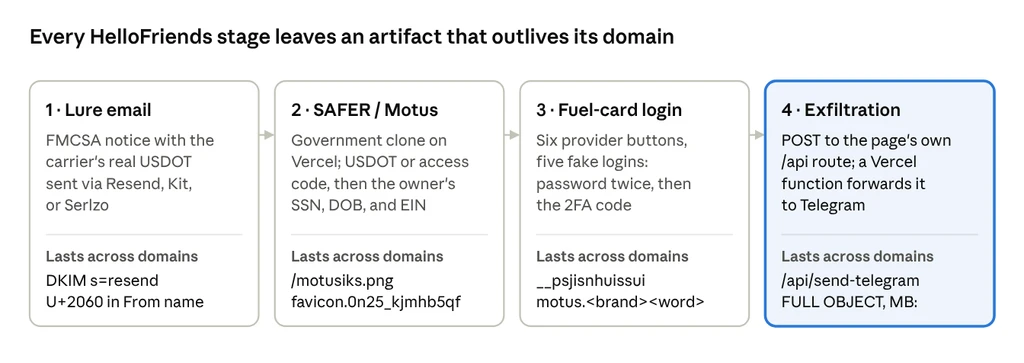
The campaign showcases how routine compliance and verification procedures can become credential-harvesting opportunities. For logistics companies, a request to verify carrier information may look like an ordinary administrative task. The danger lies in trusting the workflow without validating the destination.
NodeRemote: Broker Documents Deliver a Persistent Backdoor
NodeRemote uses another familiar interaction: receiving paperwork from a prospective broker or business partner.
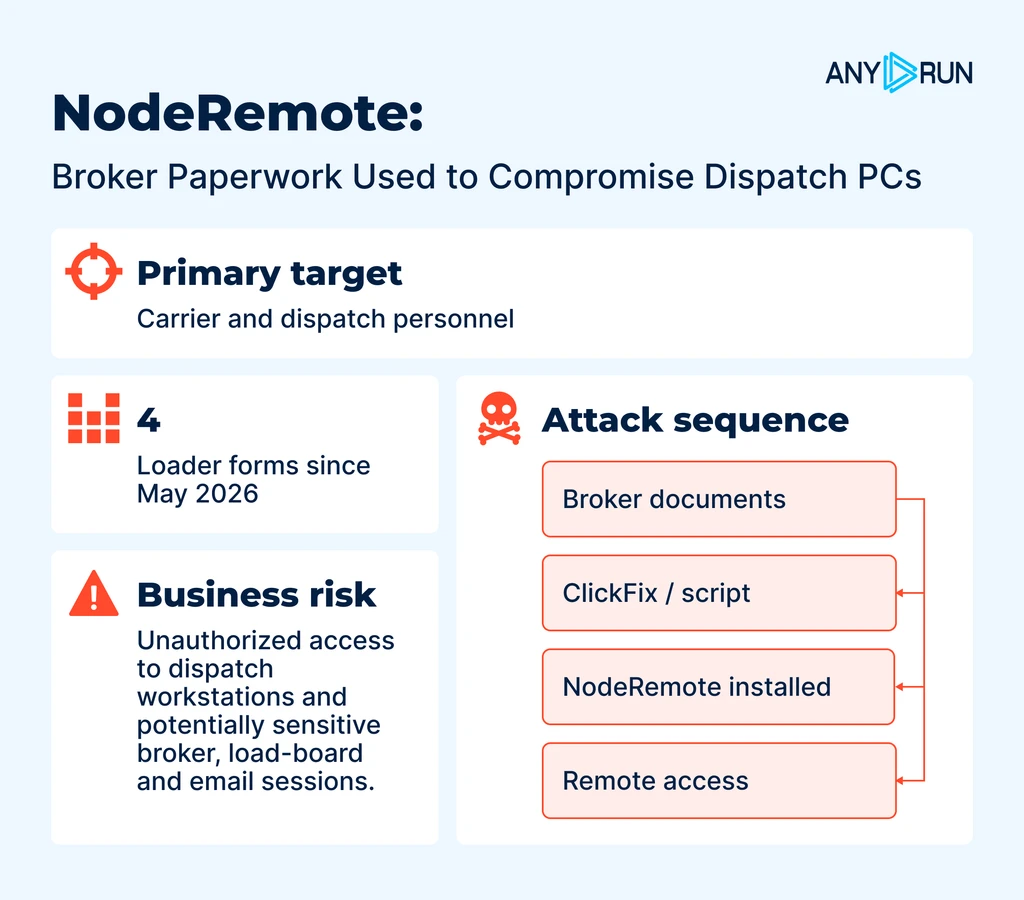
Victims encounter malicious files disguised as legitimate logistics documents. In observed infection chains, execution may involve ClickFix-style instructions, PowerShell, or VBS scripts, eventually leading to the deployment of a Node.js-based backdoor.
Once installed, the malware can establish persistence and communicate with attacker-controlled infrastructure. Researchers observed relay configuration mechanisms involving blockchain, DNS, and GitHub, helping the operators maintain communication with compromised systems.
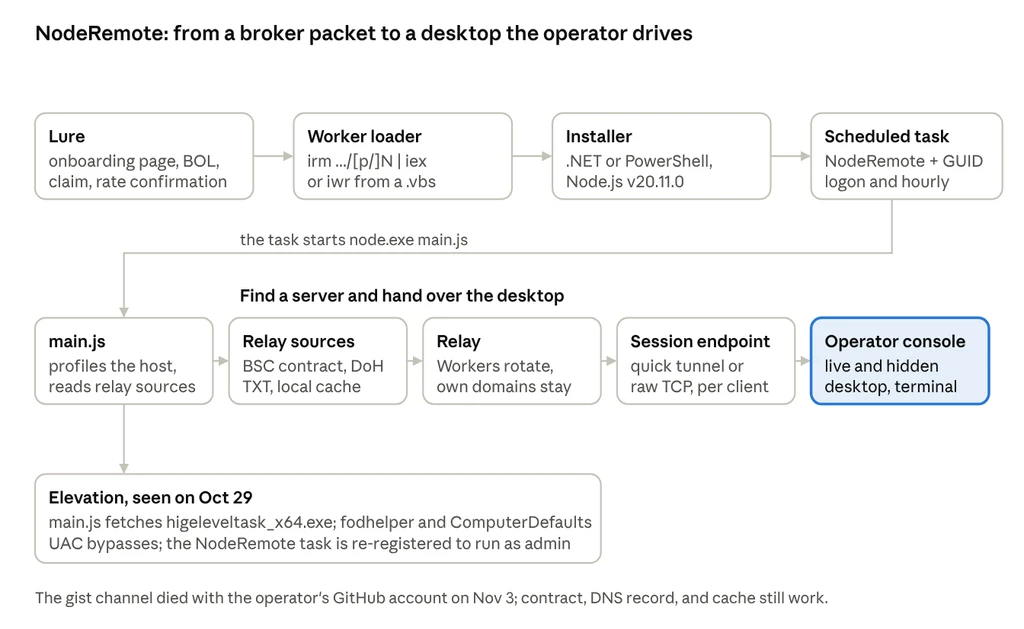
The investigation also identified UAC bypass capabilities. Some functionality was visible in the malware’s control-panel code, although not every capability was confirmed in observed infections.
NodeRemote demonstrates how a seemingly routine document exchange can become the starting point for long-term access to a company’s environment.
Fake Freight Portals: Remote Access Hidden Behind Booking Tools
The Fake Freight Portals campaign impersonates freight-related platforms, including TIMOCOM and DAT, to lure logistics professionals into malicious interactions.
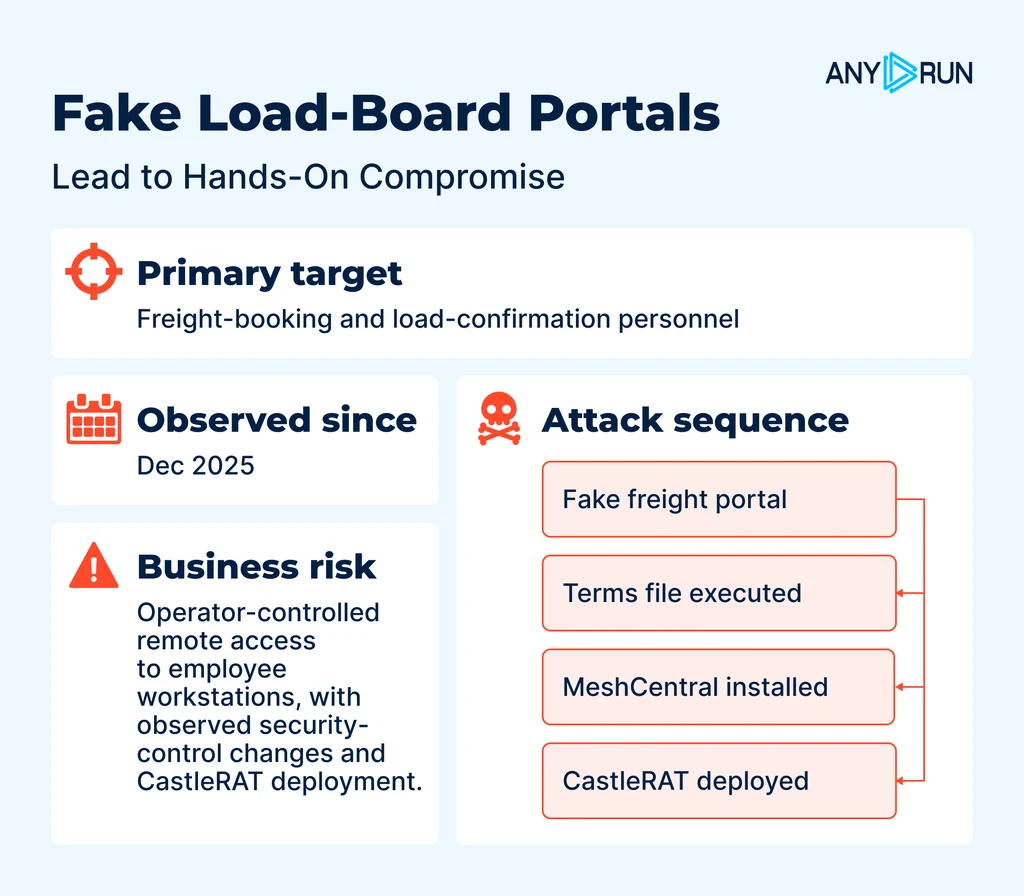
In one observed infection chain, victims download a WebDAV shortcut disguised as a business resource. Following execution, the attackers deploy MeshCentral, a legitimate remote administration tool that can be abused for unauthorized access.
The infection chain also includes attempts to obtain BitLocker recovery keys, configure Defender exclusions, and deploy CastleRAT.
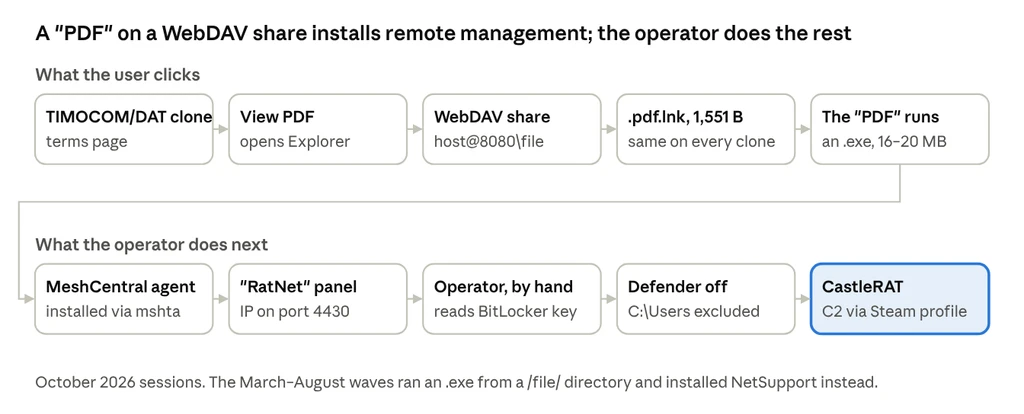
These techniques provide attackers with more than a single compromised account. They can establish remote access, weaken security controls, and potentially maintain access to infected endpoints.
The campaign highlights a recurring challenge for defenders: legitimate remote administration software can become difficult to distinguish from malicious activity when introduced through trusted business workflows.
Commodity Threats Also Target Logistics Companies
Not every attack against logistics organizations involves a sector-specific campaign.
ANY.RUN researchers also observed Microsoft 365 phishing and ClickFix activity affecting logistics-related websites and users. These techniques rely on widely used attack infrastructure and social engineering rather than exclusively targeting freight operations.
The distinction matters. Logistics organizations face both campaigns designed around their business processes and commodity threats that exploit common enterprise tools.
When a Suspicious File Becomes an Unknown Attack Chain
A suspicious broker document or freight portal link may be the entry point to a larger attack. Documents can launch scripts, download payloads, establish persistence, or contact attacker infrastructure. Phishing pages may redirect users, load hidden content, or steal credentials and one-time passwords.
For SOCs and MSSPs, uncovering these steps takes more than checking a file’s reputation. Static analysis can flag suspicious code but rarely reveals the complete execution chain. Analysts need to see how processes interact, where network connections lead, and what changes occur on the system. Reconstructing this activity manually can slow down investigations.
ANY.RUN’s Interactive Sandbox gives analysts an isolated, interactive environment to execute suspicious files and URLs and observe their behavior in real time. They can follow process execution, inspect network traffic, track file and registry modifications, and identify additional payloads.
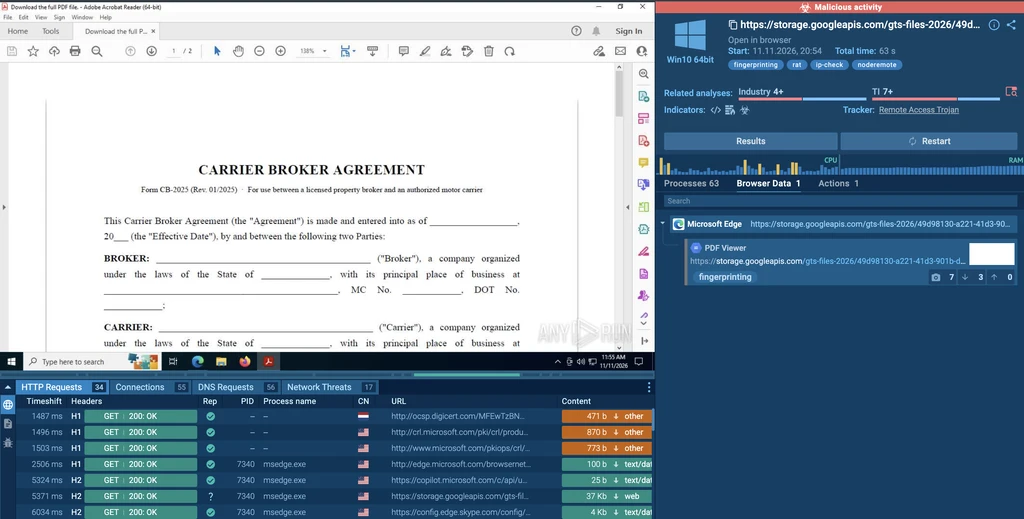
For example, an analyst investigating a malicious broker document can trace the scripts it launches and connections it makes. When examining a phishing portal, they can interact with the page to uncover redirects, credential collection mechanisms, and suspicious network activity.
Investigation speed is equally important during high-volume triage. Virtual machines in ANY.RUN’s Sandbox start in under 10 seconds, and a detailed Tier 1 report with AI-generated summary and recommendations is available in about 40 seconds. SOC and MSSP teams can begin examining suspicious activity without the setup and maintenance overhead of a dedicated malware analysis environment.
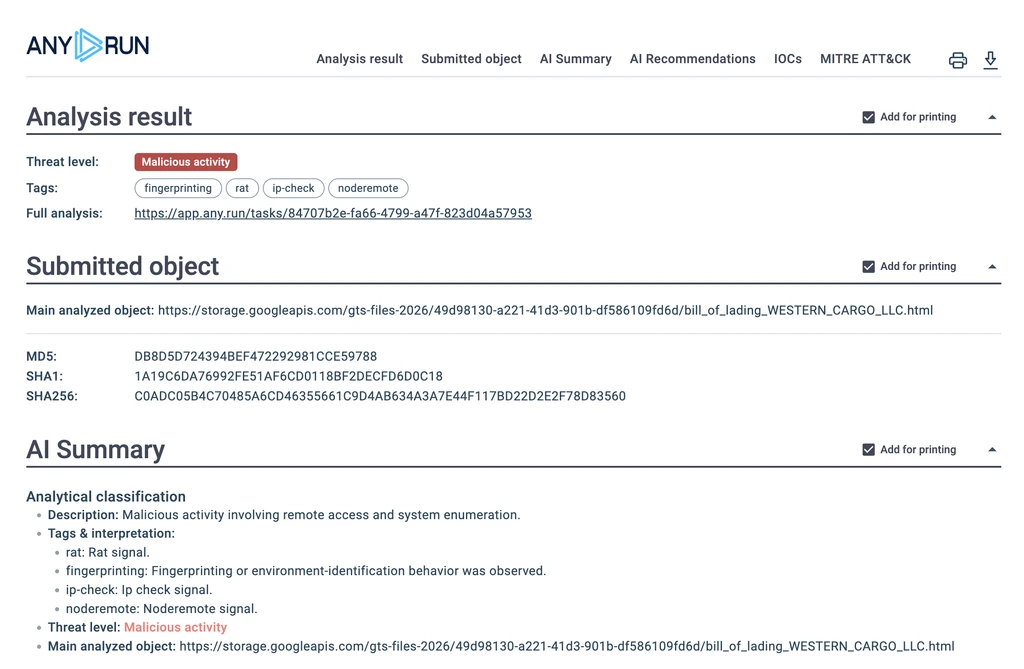
The resulting behavioral evidence helps teams identify indicators, map observed techniques to MITRE ATT&CK, and share findings through SOC-ready reports. This gives analysts a stronger basis for escalation and response while reducing manual investigation effort.
Reproducing Regional Conditions to Reveal Hidden Threat Behavior
The simulated environment can also affect the results. Some threats adapt their behavior to the victim’s geographic location or system locale, potentially concealing activity when analyzed under different conditions.
ANY.RUN supports residential proxies and locale settings to help reproduce the target environment.
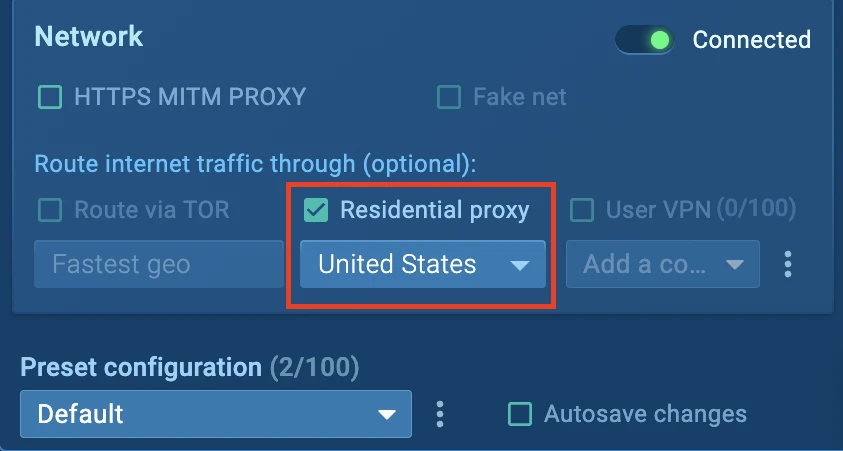
For a campaign targeting American trucking companies, SOC and MSSP analysts can select a US residential proxy and matching locale to observe the threat as a US-based visitor would. Saved presets make these regional configurations easy to reuse across investigations.
When SOCs and MSSPs Lack Context to Connect the Dots
Identifying a suspicious indicator is only the start. SOC and MSSP teams also need to know whether it has appeared in previous investigations, targets their industry, or connects to other infrastructure and campaigns.
ANY.RUN’s Sandbox provides this context through a powerful new capability for enterprise users — Related Threat Context, also known as Related analyses. It connects indicators in the current session to related investigations from the analyst’s team, their industry, and ANY.RUN Threat Intelligence.
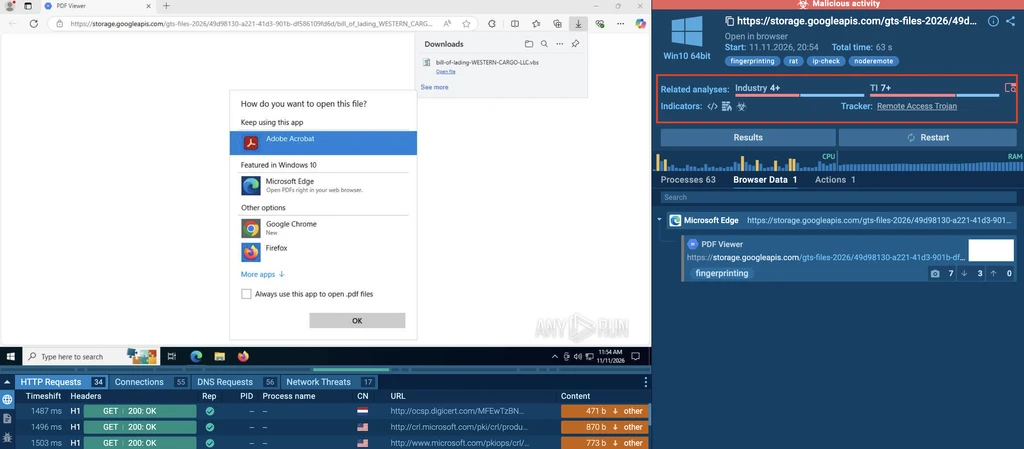
SOCs and MSSPs can access previous sessions, additional IOCs, and behavioral findings without manually searching internal history or external sources. This intelligence draws on public analyses and shared anonymized threat data from a community of more than 700,000 security professionals and 16,000 organizations.
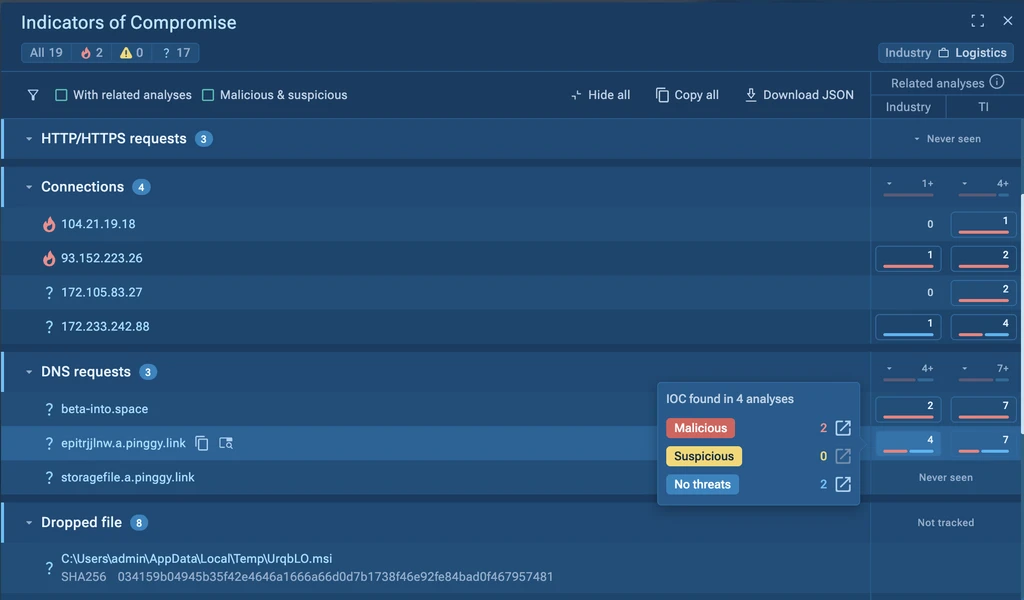
For example, an indicator found in a suspicious broker document may also appear in earlier investigations targeting logistics companies. Those sessions can reveal related infrastructure and previously observed behaviors.
For deeper research, ANY.RUN Threat Intelligence Lookup (TI Lookup) lets analysts search IPs, domains, URLs, hashes, registry keys, processes, and other artifacts, then explore their relationships. Results take about two seconds, and TI Lookup can help uncover up to 24 times more IOCs per case.
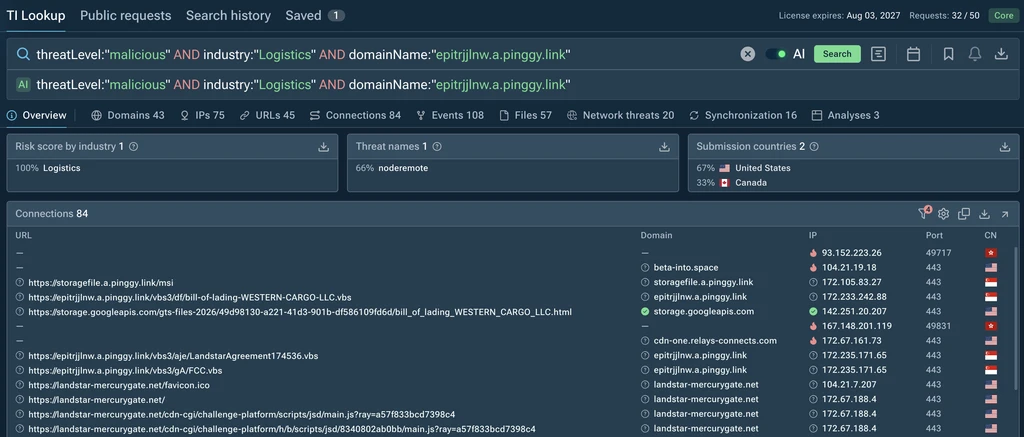
Together, these capabilities reduce manual enrichment and help SOC and MSSP teams connect current activity to known threats, prioritize investigations, and strengthen threat hunting.
Why Wait for an Investigation to Discover a Known Threat?
Some malicious infrastructure has already been observed by the security community. Yet organizations may still spend valuable analyst time investigating indicators that are already known to be malicious.
ANY.RUN Threat Intelligence Feeds (TI Feeds) help bridge this gap by delivering continuously updated malicious IP addresses, domains, and URLs derived from Sandbox investigations. The indicators are enriched with threat context and can be integrated into existing security infrastructure through supported connectors, API/SDK, and STIX/TAXII.
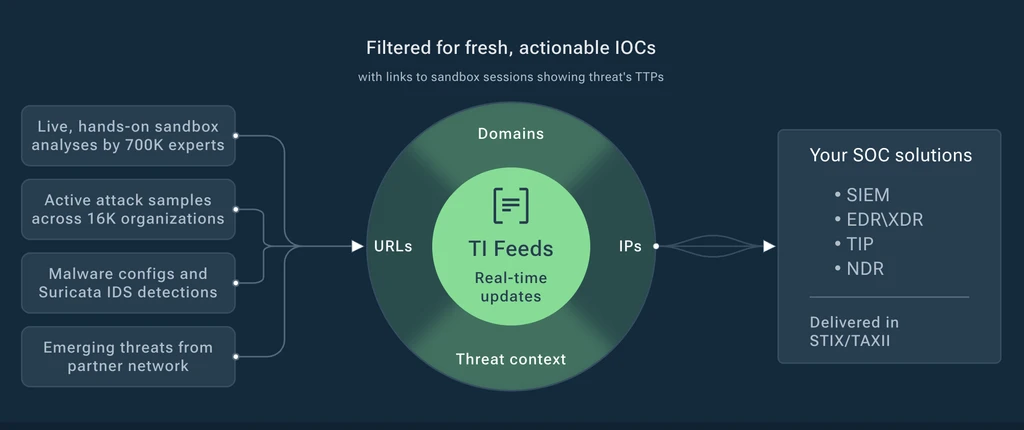
The practical value goes beyond adding another source of threat data. ANY.RUN‘s internal analysis found that nearly 30% of unique malicious IOCs identified in Interactive Sandbox sessions had already been observed by ANY.RUN and were available in TI Feeds.
This means that when one of these indicators appears in an organization’s telemetry, existing security controls may be able to match it against TI Feeds before an analyst manually investigates the activity in Sandbox. A known malicious domain or IP address can therefore become a detection opportunity much earlier in the investigation process.
Indicator quality matters just as much as coverage. 99% of the unique, high-confidence IOCs added to ANY.RUN’s TI Feeds undergo strict validation. For SOCs and MSSPs dealing with alert fatigue, this helps address a familiar problem: adding more threat data is not useful if it also creates more false positives and manual review.
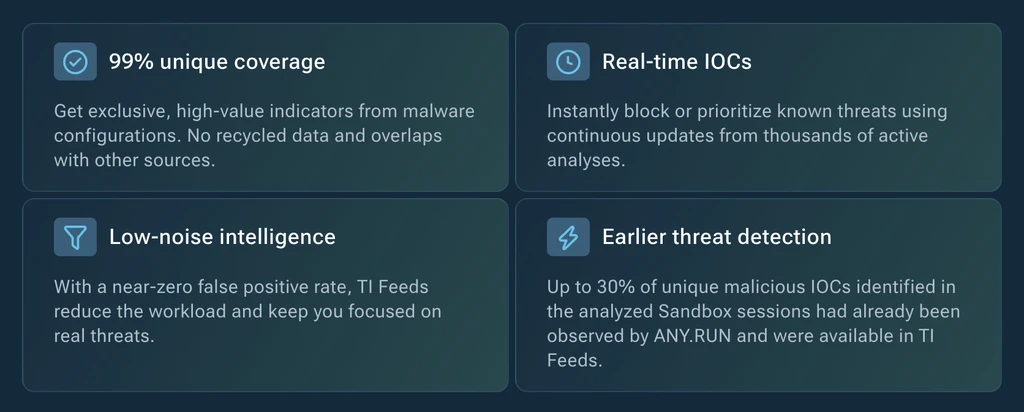
By integrating relevant intelligence into SIEM, XDR, and other supported security systems, organizations can enrich alerts, prioritize suspicious activity, and make better use of their existing detection infrastructure.
Keeping Up with Threats Beyond Your Own Investigations
Even well-equipped SOC and MSSP teams cannot investigate every campaign or malware family themselves. Without broader research, emerging techniques and relevant threats may remain outside their immediate visibility.
ANY.RUN Threat Intelligence Reports (TI Reports) provide analyst-curated research into campaigns, malware families, and evolving attacker techniques.
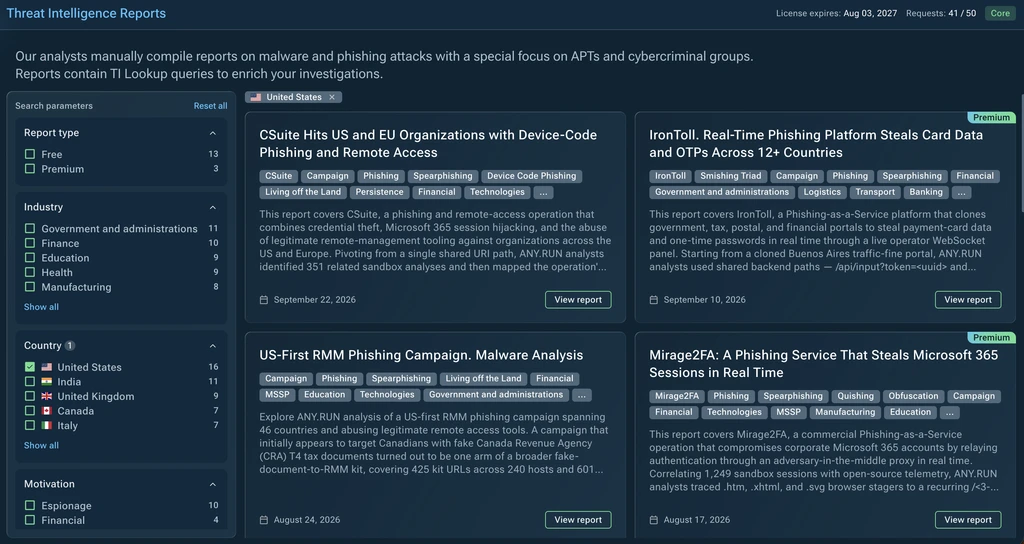
By connecting technical findings to broader threat activity, reports help teams identify hunting opportunities, refine detection priorities, and make informed response decisions without having to conduct every investigation internally.
Turning Individual Investigations into Stronger Security
The logistics campaigns show why teams need both behavioral visibility and broader threat context.
ANY.RUN supports different stages of the security workflow:
- Interactive Sandbox reveals how suspicious files and URLs behave, exposes infection chains, and provides evidence for investigation and response.
- Related Threat Context and TI Lookup connect indicators and behaviors to previous investigations and related threats, helping analysts uncover wider attack activity.
- Threat Intelligence Feeds deliver verified indicators into existing security systems to strengthen detection and support earlier response.
- Threat Intelligence Reports provide expert research and campaign context that inform threat hunting, incident response, and security planning.
These capabilities also address a wider SOC and MSSP challenge: getting more value from limited analyst capacity. With richer context available during triage, junior analysts can make more informed decisions, while experienced analysts can spend less time on repetitive enrichment and more time on complex investigations.
The impact extends across daily operations. For instance, ANY.RUN solutions help organizations identify up to 58% more threats overall. Combined with behavioral analysis and threat intelligence, this can help security teams uncover activity that standard defenses might miss.
Improved outcomes give CISOs a clearer view of threat exposure and a solid basis for evaluating security investments, while helping SOC managers standardize investigations, strengthen detection coverage, and make better use of analyst capacity.
Conclusion
Protecting logistics companies means looking beyond traditional security boundaries and recognizing the risks hidden in everyday business processes. Carrier verification, broker onboarding, freight booking, and document exchange can all become entry points for cyberattacks.
The key is to understand how these attacks unfold, identify the infrastructure and techniques behind them, and turn investigation findings into timely defensive action. With better visibility and threat context, security teams can detect emerging risks earlier, respond more effectively, and keep critical logistics operations running.
About ANY.RUN
ANY.RUN provides cybersecurity solutions that help organizations investigate cyber threats, analyze malicious activity, and strengthen their security operations. More than 700,000 security professionals across 16,000+ organizations worldwide use ANY.RUN.
The company’s solutions include Interactive Sandbox for real-time analysis of suspicious files and URLs, Threat Intelligence Lookup for searching indicators and exploring threat connections, Threat Intelligence Feeds for enriching security systems with validated threat data, and Threat Intelligence Reports for insights into emerging threats and attack campaigns.
ANY.RUN also maintains SOC 2 Type II attestation, reflecting its commitment to security, availability, and data protection.
Frequently Asked Questions
Logistics companies rely on digital platforms for carrier verification, broker onboarding, freight booking, and document exchange. Attackers exploit these routine workflows to steal credentials, deploy malware, and gain access to business systems.
HelloFriends uses fake carrier verification portals impersonating legitimate services such as SAFER and Motus. The pages are personalized with USDOT details and designed to steal sensitive information, including SSNs, EINs, fuel card credentials, passwords, and one-time codes.
NodeRemote uses fake broker documents and ClickFix-style instructions to trick victims into executing malicious commands. The infection chain can deploy a Node.js backdoor, establish persistence, and communicate with attacker infrastructure.
Fake Freight Portals impersonate legitimate freight platforms such as TIMOCOM and DAT. They use malicious WebDAV shortcuts to deliver remote administration tools and malware, including MeshCentral and CastleRAT, while also attempting to steal BitLocker recovery keys.
ClickFix is a social engineering technique that tricks users into copying and executing commands, often through fake error messages or verification prompts. It can bypass the suspicion users may have toward conventional executable downloads.
Analysts can execute suspicious files and URLs in an interactive sandbox to observe process activity, network connections, file changes, and other behaviors. This helps uncover payloads, credential theft, persistence, and attacker infrastructure.
Threat intelligence helps analysts connect individual indicators to known campaigns, infrastructure, and attack techniques. This context supports faster investigations, better prioritization, and more informed detection decisions.
Organizations should strengthen verification procedures for carriers and brokers, train employees to recognize suspicious documents and instructions, monitor identity and endpoint activity, and enrich security monitoring with validated threat intelligence.
0 comments