Recent posts
SkyW4lker (SkyW4lker x365 Sentinel) is an active device-code phishing kit targeting Microsoft 365 users in the United States, Europe, and other regions. By abusing Microsoft’s legitimate authentication process, the kit can give attackers access to corporate accounts without stealing passwords or bypassing MFA. This puts business emails, sensitive documents, and other Microsoft 365 resources at risk of unauthorized access.
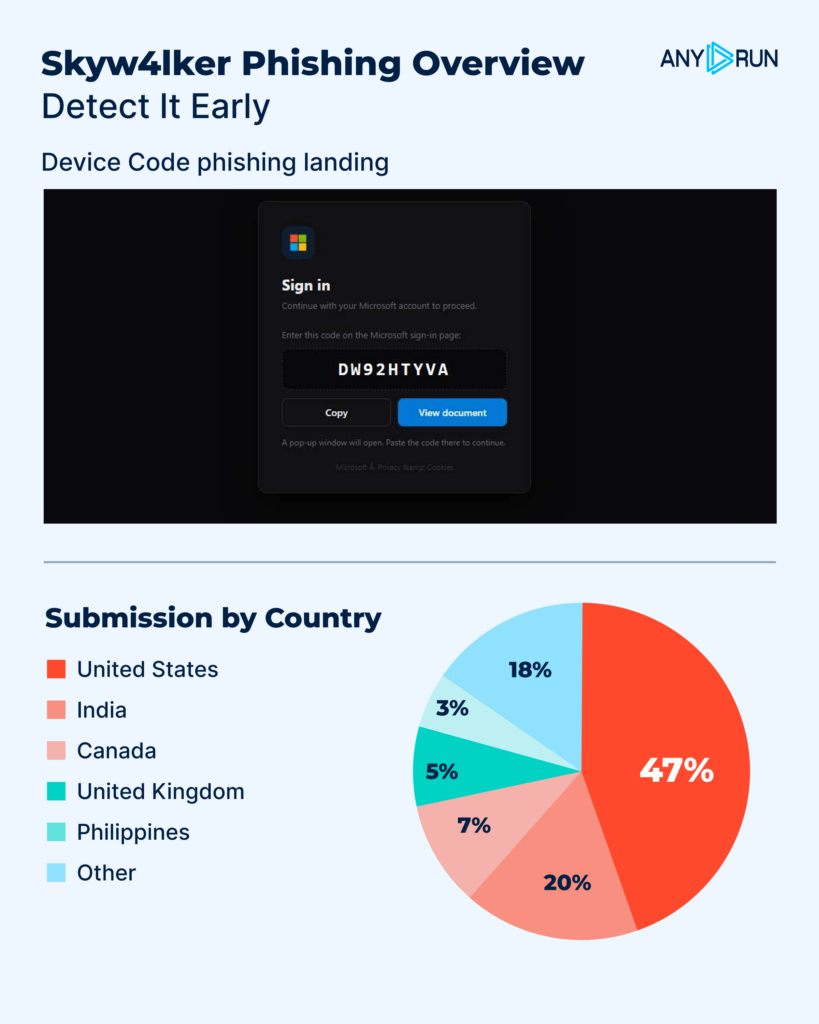
The ANY.RUN team identified 618 sandbox analyses related to SkyW4lker between June and October 21, 2026, with 46% of submissions coming from the United States. Activity increased from 20 analyses in June to 200 in September, highlighting the growing exposure of organizations relying on Microsoft 365.
Key Takeaways
- SkyW4lker is distributed through phishing emails with a password-protected malicious attachment; the password is provided in the email body. After a chain of decoy pages, the victim reaches a page that asks for a Microsoft device code.
- The kit consists of a PHP backend and obfuscated JavaScript. Its main features are IP-based geolocation of visitors and periodic polling of the backend to check whether the victim has completed authentication.
- ANY.RUN’s powerful new capability, Related Threat Context, helped analysts accelerate the SkyW4lker investigation by instantly surfacing connections to previous sandbox analyses. This reduced manual correlation work, enabled faster expansion of the campaign cluster, and ultimately helped uncover the phishing kit’s administration panel.
- As a result, 618 analyses were identified over the past six months (as of October 21, 2026), with monthly submissions growing from 20 in June to 200 in September. They were submitted mainly by organizations in the technology, manufacturing, and government sectors, most often from the United States, India, Canada, and the United Kingdom.
- SkyW4lker shares its JavaScript modules, landing-URL format, and part of its hosting infrastructure with Gabagool, a credential phishing kit active since April 2026. We assess with high confidence that both kits were built by the same developer.
- SkyW4lker exploits routine business workflows, using contracts, invoices, and service proposals as phishing lures. By directing employees through familiar platforms and legitimate Microsoft authentication pages, attackers make malicious requests harder to distinguish from normal business activity.
SkyW4lker Threat Overview
| Threat Type | Phishing Kit |
|---|---|
| Objective | Microsoft 365 / OAuth credentials |
| Capabilities | JavaScript obfuscation (obfuscator.io), Device-Code phishing, Geolocation detection, IP-address detection, CAPTCHA verification |
| Delivery | Email attachments (.pdf, .docx, .xls/xlsx and others), redirection links and lure pages (including Google Maps, Google Images, Miro, Zoom and others) |
| Motivation | Possible financial |
| Operator / brand | SkyW4lker (SkyW4lker x365 Sentinel) |
| Known links | URL patterns: /session_public.php?action= /endpoints/confirm_visit.php /js/url_helper.js /js/endpoint.js /js/client_geo.js |
| Activity window | 2026-06 – now |
SkyW4lker Activity Across US Organizations
The United States accounts for 47% of SkyW4lker-related sandbox submissions, more than twice the share of any other country. With the campaign exploiting legitimate Microsoft authentication processes and routine business communications, these findings raise concerns for US enterprises about how effectively existing security controls can identify suspicious activity before it leads to account compromise.
What SkyW4lker Means for Enterprise Security
SkyW4lker highlights several security risks that organizations need to account for when protecting business-critical systems and employee identities:
- Identity security gaps: Device-code phishing can succeed even when MFA is enabled, raising questions about whether existing authentication policies sufficiently restrict unnecessary access methods.
- Detection challenges: Attackers abuse legitimate Microsoft authentication flows and trusted platforms, making it harder for security teams to distinguish malicious activity from normal employee behavior.
- Broader organizational exposure: A compromised account could provide access to multiple business applications and create opportunities for further attacks against employees, customers, and partners.
- Higher response costs: Investigating suspicious authentication activity, identifying affected resources, and containing unauthorized access can increase SOC workload and incident response costs.
Technical Analysis of SkyW4lker
You can examine the full SkyW4lker attack chain in this ANY.RUN Sandbox analysis.
View analysis session and gather IOCs
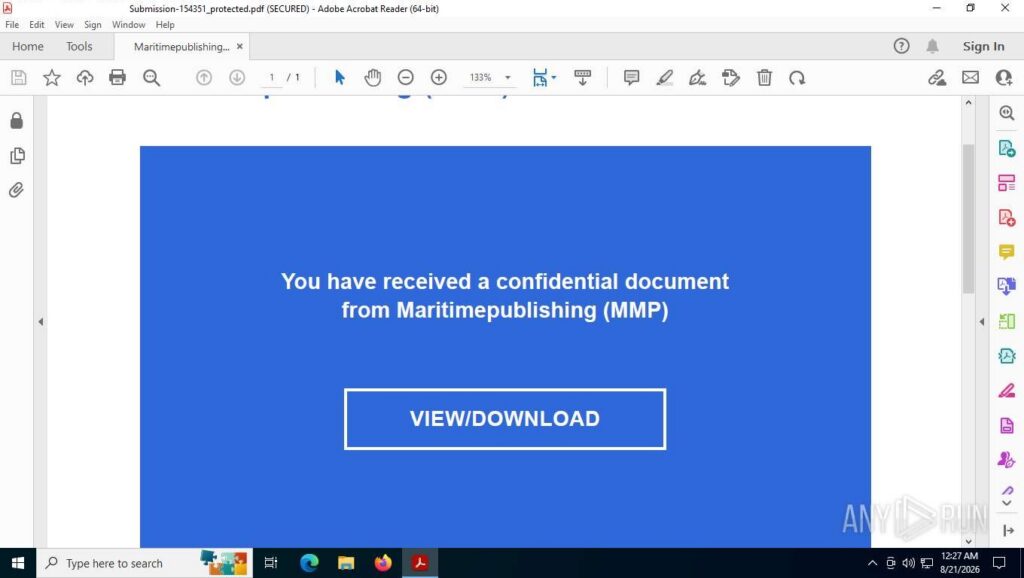
The attack unfolds in three main stages:
- The attacker sends the victim a phishing email with a password-protected attachment. Typical subjects involve commercial offers, contracts, invoices, or confidential documents. The attachment is a PDF, DOCX, or XLSX file, and the password is provided in the email body.
- The document contains a link to a CAPTCHA page. Some variants include an additional lure page hosted on a legitimate service such as Miro, Google Sites, or Zoom, which redirects the victim to the next step.
- Finally, the victim is directed to a phishing page that instructs them to enter a device code on Microsoft’s legitimate authentication page, potentially granting the attacker access to their Microsoft 365 account.
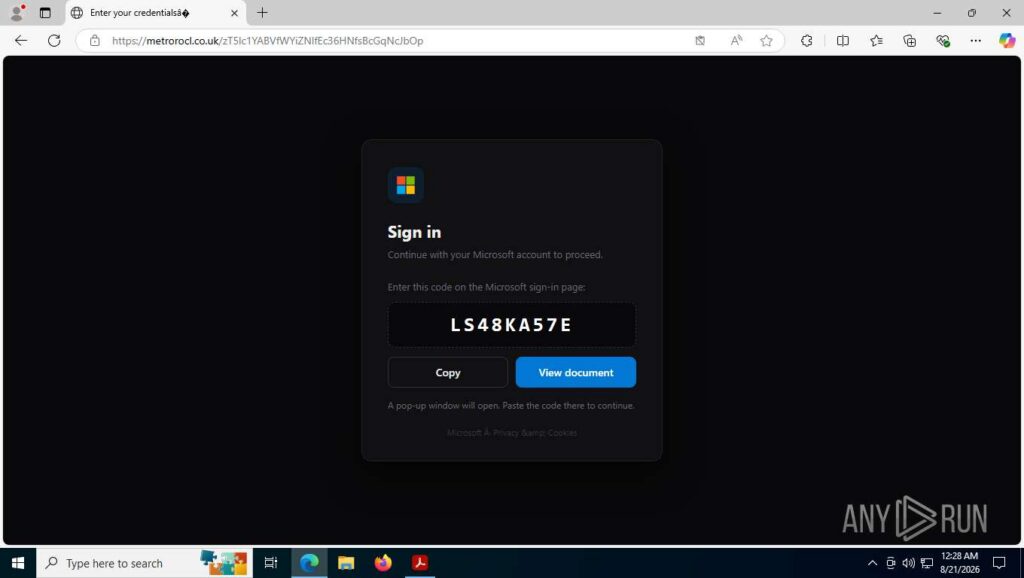
The phishing page relies on obfuscated JavaScript functions and separate script files. Using ANY.RUN’s In-Browser Data Inspection, analysts can examine the page’s DOM and HTTP activity to understand how these scripts operate.
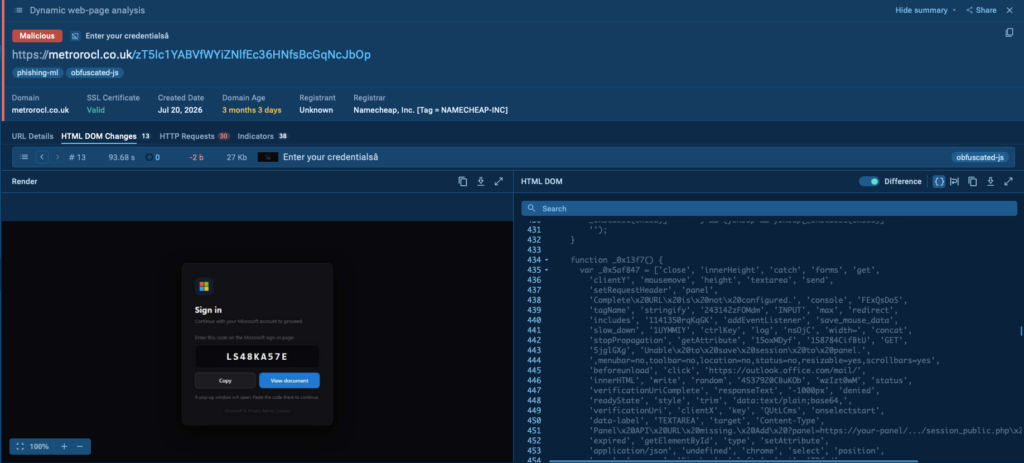
The scripts keep the page in regular contact with the PHP backend and determine the location of the victim from their IP address. Within the page DOM, the main script loads additional modules, sets click handlers on buttons and builds GET requests to the PHP endpoint /session_public.php with the action parameter (start or poll).
With action=start, the script sends the geolocation and IP address of the victim and receives a session ID. After that, it sends a request with action=poll every few seconds to check whether the victim has authenticated.
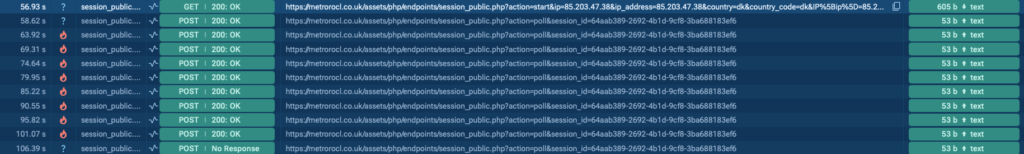
The other modules of the phishing page are listed below:
| Module | Purpose |
|---|---|
| client_geo.js | Determines the location of the victim from the response of one of three services: ip-api[.]com, ipapi[.]co or ipwho[.]is. The location can also be obtained through the PHP endpoint php/endpoints/client_geo.php. |
| url_helper.js | Base script with helper wrappers for URL handling, such as building GET parameters and appending slashes. |
| endpoint.js | Tracks the state of the victim. It logs the e-mail address, password, browser, MFA status, country and other auxiliary fields used during authentication and sends them to the PHP backend at php/endpoints/accounts.php. |
A Shortcut for the Entire Investigation: From One URL Into a Bigger Threat Picture with Related Threat Context
A single phishing URL can be the starting point for uncovering an entire campaign. In the SkyW4lker investigation, identifying the malicious page was only the beginning. Analysts needed to trace related activity, identify additional infrastructure, and determine how far the campaign extended. Traditionally, connecting these findings requires repeated IOC lookups, manual correlation, and searching through previous investigations.
ANY.RUN’s major new upgrade, Related Threat Context, makes this process significantly faster and easier. By bringing connections to previous sandbox investigations and threat intelligence directly into the Interactive Sandbox, it helps analysts discover related threats, reuse existing findings, and expand investigations with fewer manual steps.
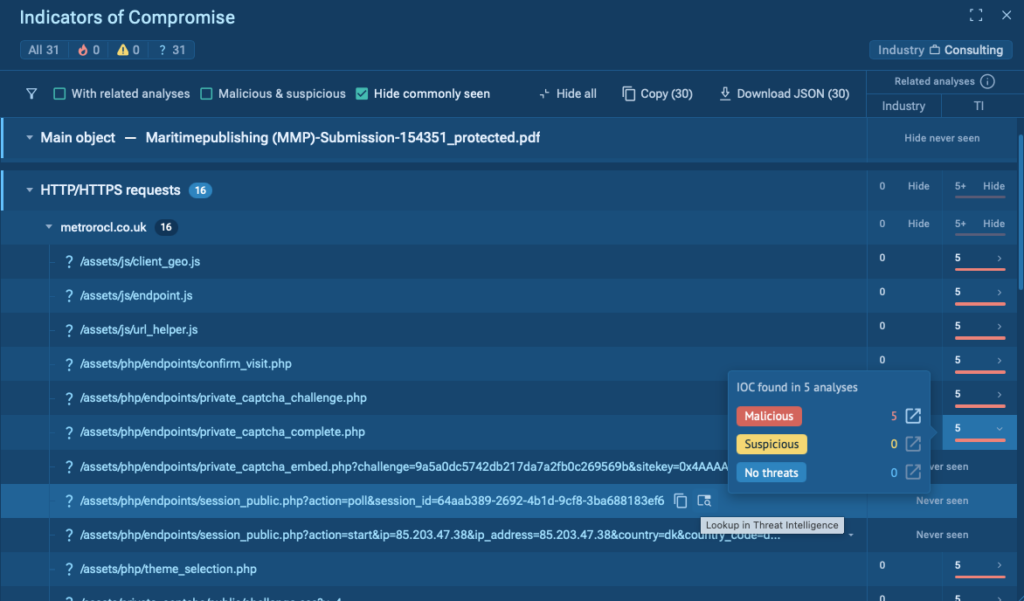
With more than 700,000 security professionals and 16,000 organizations worldwide using ANY.RUN, analysts can draw on a vast pool of real-world investigation data to uncover connections that might otherwise take considerably longer to find.
How Related Threat Context Helped Uncover More of SkyW4lker
During our SkyW4lker investigation, the new Related analyses section surfaced previous sandbox sessions sharing the same URL patterns. This gave analysts an immediate starting point for tracing related activity instead of manually searching for connections across individual investigations.
Using the distinctive PHP endpoint /session_public.php, we moved into ANY.RUN Threat Intelligence Lookup in a single click, discovered additional phishing activity, and expanded the campaign cluster.
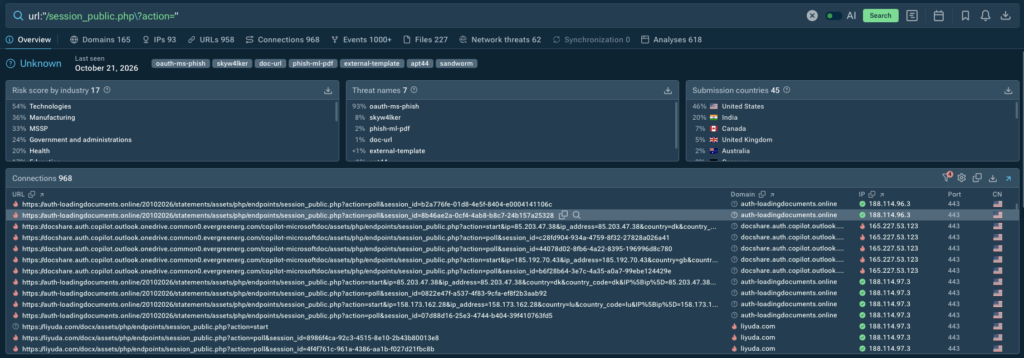
The investigation demonstrates the practical value of Related Threat Context: less time spent searching for connections, faster discovery of related infrastructure, and more evidence available to guide the next investigation step.
Reduce Manual Triage and Strengthen SOC Investigations
The same approach can be applied to other suspicious URLs and indicators, allowing SOC teams to build on previous investigations and uncover related threat infrastructure faster.
Tier 1 analysts spend less time on repetitive IOC research, gaining more evidence to support accurate triage and escalation decisions. Tier 2 analysts receive richer investigation context, helping them focus on cases that genuinely require deeper analysis.
By connecting individual alerts to existing threat intelligence, Related Threat Context helps SOC teams shorten investigation cycles, reduce unnecessary manual work, and make better-informed response decisions.
Attribution: The Connection Between SkyW4lker and Gabagool
Each phishing page has its own backend, so the administration panel is likely to be hosted on the same domain. Further analysis of the Threat Intelligence Lookup results and data from other sources revealed an administration panel at /admin/index.php.
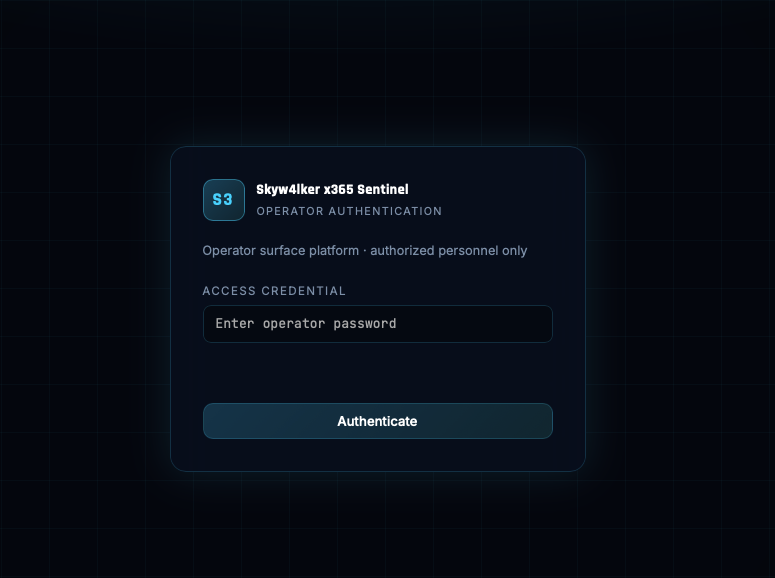
The CSS styles (command-center.css) suggest the following capabilities of the kit:
- Authentication with MFA via Telegram
- Dashboard with victim statistics based on the client_geo.js module
- Server management
- Generation of new links
- Live notifications about new visits to phishing links
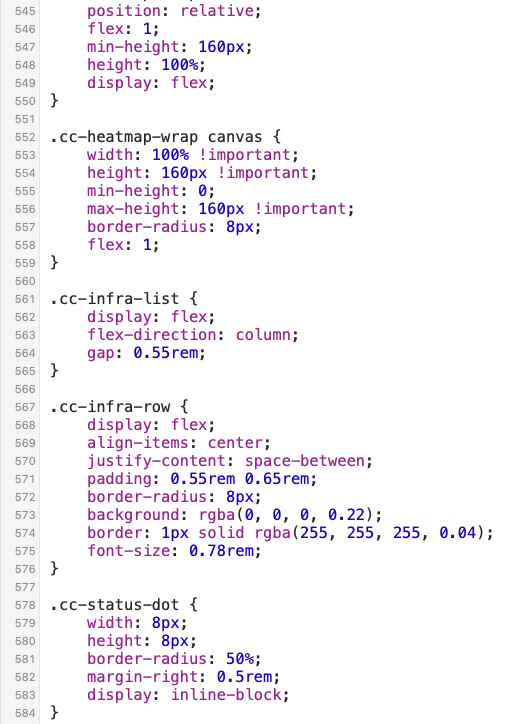
Further investigation revealed another important finding: SkyW4lker shares several technical components with Gabagool, a credential phishing kit.
A search in ANY.RUN Threat Intelligence for the unique module paths of SkyW4lker url:”/js/client_geo.js” or url:”/js/url_helper.js” or url:”/js/endpoint.js”) also returns sandbox sessions tagged gabagool. Gabagool was first observed on 23 April 2026, two months before SkyW4lker, and has used the endpoint.js and url_helper.js modules since late April and early May. The two kits share several other features:
| Feature | SkyW4lker | Gabagool |
|---|---|---|
| First seen | 23 June 2026 | 23 April 2026 |
| Analyses in six months | 618 | 458 |
| Shared JavaScript modules | client_geo.js, url_helper.js, endpoint.js (since July 2026) | client_geo.js, url_helper.js, endpoint.js (since late April 2026) |
| Visit endpoint | /assets/php/endpoints/confirm_visit.php | /assets/php/endpoints/confirm_visit.php |
| Self-hosted CAPTCHA | /assets/private_captcha/public/widget.js?v=4 | /assets/private_captcha/public/widget.js?v=4 |
| Landing token | zt[A-Za-z0-9]{32}op; it[A-Za-z0-9]{32}us from 10 August | zt[A-Za-z0-9]{32}op; it[A-Za-z0-9]{32}us from 5 August |
| Same directory on shared hosts | 5200m[.]com/kvme2/ (16 Oct), torvion[.]life/ofulium/ (5 Oct), ghethim[.]com/hyllen/ (28 Sep – 2 Oct) | 5200m[.]com/kvme2/ (15 Oct), torvion[.]life/ofulium/ (6 Oct), ghethim[.]com/hyllen/ (8 Oct) |
| Hosting | mostly DigitalOcean | mostly DigitalOcean; shared IP 172.86.85[.]51 (priorispace[.]biz) |
| Main endpoint | session_public.php (device-code phishing) | accounts.php (login and password harvesting) |
Moreover, some sandbox sessions tagged gabagool load the kit from directories named skywalker:
goldcreekconcrete[.]com/example/skywalker/ (sandbox session) and goldcreekconcrete[.]com/skywalker/example/ (sandbox session). On goldcreekconcrete[.]org, which also hosted Gabagool (sandbox session), the directory /skyw4lker/skydirectory/ with the same modules appeared on 29 September (sandbox session).
We therefore assess with high confidence that Gabagool and SkyW4lker are built by the same developer. Gabagool harvests logins and passwords through accounts.php, whereas SkyW4lker abuses the device-code flow through session_public.php, so we regard them as two attack modes of one platform. The identical directories on shared hosts may also point to a common operator; however, the available data does not allow us to distinguish one operator from several customers of the same platform.
How to Detect SkyW4lker and Reduce Enterprise Exposure
The SkyW4lker investigation reveals several technical indicators and attack patterns that security teams can use to identify related phishing activity. For organizations, these findings also highlight opportunities to strengthen identity security and reduce the impact of potential account compromise.
For SOC Analysts and Threat Hunters
- Hunt for SkyW4lker’s technical fingerprints. Look for requests to /session_public.php?action=start and repeated /session_public.php?action=poll calls. Check the JavaScript modules and URL patterns identified in this research to uncover related infrastructure.
- Connect phishing activity with suspicious sign-ins. Monitor Microsoft Entra ID logs for unexpected device-code authentication, particularly following suspicious emails or document-sharing requests. Correlating authentication events with phishing indicators can help identify potential account compromise.
- Expand investigations beyond individual IOCs. ANY.RUN’s newly introduced Related Threat Context puts connected sandbox analyses at analysts’ fingertips, with a one-click pivot to threat intelligence context for deeper threat hunting. In the SkyW4lker investigation, this helped expand the campaign cluster, while further analysis revealed shared infrastructure and code similarities with Gabagool.
- Investigate potential follow-on activity. When account compromise is suspected, review subsequent Microsoft 365 activity to identify affected resources, unauthorized access, and possible attempts to target other users.
For CISOs and Security Leaders
SkyW4lker demonstrates why organizations need to look beyond traditional phishing prevention and MFA when evaluating identity security. Three priorities deserve attention:
- Close authentication policy gaps. Review where device-code authentication is genuinely required. Restrict or block unnecessary use through Microsoft Entra Conditional Access to reduce opportunities for attackers to abuse legitimate authentication flows.
- Strengthen detection across email and identity systems. Ensure the SOC can connect suspicious attachments, phishing infrastructure, and unusual authentication events. Better visibility across these stages helps teams identify potential compromises before attackers expand their access.
- Reduce investigation time and escalation costs. Equip Tier 1 analysts with historical threat context and clear escalation criteria. Establish procedures for containing compromised accounts and reviewing unauthorized activity, helping Tier 2 teams focus on incidents requiring deeper investigation.
Conclusion
SkyW4lker continues to evolve, with new endpoints, changing URL patterns, and growing activity across sandbox analyses. Its connection to Gabagool suggests that the same developer is supporting both device-code and credential phishing, giving attackers different ways to compromise business accounts through shared infrastructure.
For organizations, the findings highlight a broader security challenge: attackers are increasingly exploiting legitimate authentication processes and trusted business services, making malicious activity harder to distinguish from normal operations.
As phishing kits evolve, security teams need more than traditional email filtering and MFA. Stronger identity controls, visibility into suspicious authentication activity, and access to connected threat context can help SOCs identify attacks earlier, investigate them faster, and reduce the potential impact on business operations.
About ANY.RUN
ANY.RUN provides cybersecurity solutions that help SOC and MSSP teams detect and investigate threats, make faster decisions, and reduce the time and resources spent on incident response.
The company’s solutions include Interactive Sandbox for analyzing suspicious files, URLs, and phishing attack chains, and ANY.RUN Threat Intelligence with Threat Intelligence Lookup, Threat Intelligence Feeds, and Threat Intelligence Reports. Together, these solutions help security teams uncover related threat activity, track evolving attack infrastructure, and strengthen detection with intelligence from real-world investigations.
Today, ANY.RUN is trusted by more than 16,000 organizations and 700,000 security professionals worldwide. The company is SOC 2 Type II certified, with security controls designed to protect customer data.
TTPs (MITRE ATT&CK)
| Tactic | Technique | Procedure |
|---|---|---|
| Reconnaissance | T1589.002 Gather Victim Identity Information: Email Addresses |
The SkyW4lker operator collected recipient e-mail addresses to personalise phishing links using the landing-URL suffix ? |
| Reconnaissance | T1590.005 Gather Victim Network Information: IP Addresses | The SkyW4lker phishing kit recorded the visitor's IP address, ISP, organisation and location to profile victims using client_geo.js and the request /assets/php/endpoints/session_public.php?action=start&ip=…&isp=…&org=…&org_type=. |
| Resource Development | T1583.001 Acquire Infrastructure: Domains | The SkyW4lker operator registered look-alike domains of real companies to host phishing pages using typo-squatted names under Microsoft-themed subdomain chains, e.g. sdocshares.auth.outlook2026common.copilos26.csr-rooflng[.]com and pdocshared.payments2026.outlooks.common.ecmholdlnggroup[.]com. |
| Resource Development | T1583.001 Acquire Infrastructure: Domains | The SkyW4lker operator obtained free dynamic-DNS subdomains to host phishing pages using flow505.mooo[.]com, bigbrain.chickenkiller[.]com and off365acess.jumpingcrab[.]com. |
| Resource Development | T1583.003 Acquire Infrastructure: Virtual Private Server | The SkyW4lker operator rented virtual private servers to run the PHP backend using DigitalOcean hosting (50 of 92 backend IP addresses), e.g. 162.243.64[.]121 and 67.205.154[.]32. |
| Resource Development | T1608.005 Stage Capabilities: Link Target | The SkyW4lker operator staged intermediate pages to forward victims to the kit using public cloud buckets and site builders, e.g. pub-177b3aa5a54d4f9087a649de5ec766d5.r2[.]dev/docsonedrive2026.html, carcabaoperadologistca.fr-par-1.linodeobjects[.]com/document_excel.html and bethom-contracting-llc.mintlify[.]site. |
| Initial Access | T1566.001 Phishing: Spearphishing Attachment |
The SkyW4lker operator sent password-protected attachments to deliver the phishing link using PDF, XLS, DOCX and EML lures named |
| Initial Access | T1566.002 Phishing: Spearphishing Link | The SkyW4lker operator sent links hosted on legitimate services to pass e-mail reputation checks using Google Sites, Axure Cloud and Smartsheet pages and the maps.google[.]ie/url?q= redirect, e.g. sites.google[.]com/heatherrasekhomes.com/talbert-manufacturing-inc-0049/home. |
| Execution | T1204.001 User Execution: Malicious Link |
The SkyW4lker phishing kit relied on the victim opening the landing link to start a phishing session using the path / |
| Defense Evasion | T1656 Impersonation |
The SkyW4lker operator imitated routine business correspondence to make the lures credible using subjects such as New Submission From |
| Defense Evasion | T1497 Virtualization/Sandbox Evasion | The SkyW4lker phishing kit placed a CAPTCHA in front of the phishing page to hide it from automated scanners using Cloudflare Turnstile and the self-hosted /assets/private_captcha/public/widget.js?v=4 with /assets/php/endpoints/private_captcha_challenge.php. |
| Defense Evasion | T1027 Obfuscated Files or Information | The SkyW4lker phishing kit obfuscated its JavaScript to hinder analysis using obfuscator.io-style code (520 of 618 analyses carry the obfuscated-js tag). |
| Credential Access | T1528 Steal Application Access Token |
The SkyW4lker phishing kit abused the Microsoft OAuth 2.0 device-code flow to obtain the victim's access tokens using login.microsoft[.]com/device and login.microsoftonline[.]com/common/oauth2/deviceauth while polling /assets/php/endpoints/session_public.php?action=poll&session_id= |
| Collection | T1056.003 Input Capture: Web Portal Capture | The SkyW4lker phishing kit logged the victim's e-mail, password, browser, MFA status and country to collect credentials using endpoint.js and the backend php/endpoints/accounts.php. |
IOCs
All indicators were observed in ANY.RUN analyses between 23 June and 21 October 2026.
URL patterns:
| Pattern | Purpose | Seen |
|---|---|---|
|
/ |
Landing page token; may end with ? |
2026-08-10 – 2026-10-19 |
|
/ |
Earlier landing page token | 2026-06-25 – 2026-09-28 |
|
/assets/php/endpoints/session_public.php?action=start&ip= |
Session registration with visitor geolocation | 2026-06-23 – 2026-10-21 |
|
/assets/php/endpoints/session_public.php?action=poll&session_id= |
Polling of device-code authentication status | 2026-06-23 – 2026-10-21 |
| /assets/js/client_geo.js | Visitor geolocation module | 2026-07-07 – 2026-10-19 |
| /assets/js/endpoint.js | Session state and credential logging module | 2026-07-22 – 2026-10-20 |
| /assets/js/url_helper.js | URL helper module | 2026-07 – 2026-10 |
| /assets/php/endpoints/confirm_visit.php | Visit confirmation endpoint | 2026-08-31 – 2026-10-15 |
| /assets/private_captcha/public/widget.js?v=4, /assets/private_captcha/public/widget.css, /assets/php/endpoints/private_captcha_challenge.php | Self-hosted CAPTCHA gate | 2026-07-07 – 2026-09-28 |
| /assets/php/attach/js/mstoken_document_(adobe|onedrive|excel)_[A-Za-z0-9]{50}.js | Brand-specific document script | 2026-07-20 – 2026-10-20 |
|
(docshare|sdocshares|pdocshared|pdfdocshared|efaxdoc|reauth|statement|copilot|login|auth).*(outlook|onedrive|copilot|office365).*. |
Microsoft-themed hostname chain on look-alike domains | 2026-06 – 2026-10 |
Domains hosting the phishing kit (173):
0350pvas.acs-wcst[.]com
0ff365access.mooo[.]com
0utlook0ffice365admin.twilightparadox[.]com
1355bcra.ck29material[.]com
1717emxr.acs-wcst[.]com
5200m[.]com
5375jngu.prefform[.]us
6662nyde.acs-wcst[.]com
6695lkmo.prefform[.]us
7301eqny.acs-wcst[.]com
7criccasinobonus[.]cc
aachem-za[.]co
accordhealth[.]cc
acrobat-adobe-com-4464uswc.egllo[.]com
advancedsteelbuilding[.]com
alasilla[.]com
albertamo[.]com
alfabricationinc[.]com
apexpartsdepot[.]com
apinows[.]com
atlantictriad.ignorelist[.]com
atlassgroupinc[.]com
auth-loadingdocuments[.]online
auth.login.office365.cloud.onedrive.outlook.atlarchitacts[.]com
authorize.copilot.outlook.common.microsoft0365.atlarchitacts[.]com
awemode.outlookoffice365.microsoftcopilots.docshare.linnwest[.]us
azgymfloor[.]com
bandg-electrics[.]com
bennett002.mooo[.]com
bezpartien[.]online
bigbrain.chickenkiller[.]com
bloomfleldcapital[.]com
bramum[.]online
buckslu[.]org
bxcelcounselling[.]org
caine-wenier[.]com
calebchemicals[.]com
calmechc[.]net
canacedesotogroup[.]com
celestialtremor[.]org
celliottelliott-wellman[.]org
celvarioncorn[.]org
centipedtourspa[.]com
claronevents[.]com
cleggs.my03[.]com
clingard[.]pro
clubdenut[.]club
copilot.login.office365outlook.cloud.onedrive.atlarchitacts[.]com
copilots.outlook.cloud.microsoft.andersonelevators[.]com
copilots.outlook.cloud.microsoft.syrosconstructlon[.]com
coreansdmain[.]com
csr-rooflng[.]com
ctr-wooding[.]com
darap-it[.]co
detroitgardenswork[.]com
devtachsales[.]com
dguidrycardinazprofessional[.]com
docshare.auth.copilot.outlook.onedrive.common.earthlink-net[.]com
docshare.auth.copilot.outlook.onedrive.common.evergreenerg[.]com
docshare.auth.copilot.outlook.onedrive.common.northemheating[.]com
docshare.auth.copilot.outlook.onedrive.common0.evergreenerg[.]com
docshare.auth.copilot.outlookonedrive.common.northemheating[.]com
docshare.auth2026.onedrive.outlooksdocument.csr-rooflng[.]com
docshares.auth2026.outlookcommon.copilots.commm.csr-rooflng[.]com
document.akiflx[.]com
dpincoli[.]com
dutchfarrms[.]com
eccentric-authentication[.]com
ecosys.newdocument2026.pdfdocshared.tntileandmarbleinc[.]com
efaxdoc.auth.login.outlook.office365.tescoccontrols[.]com
efaxdoc.auth.outlook2026common.copilos26.bettylnc[.]com
efaxdoc.auth.outlook2026common.copilos26.ikextal-co-kr[.]com
efaxdoc.auth.outlook2026common.copilos26.kone-inc[.]com
efaxdoc.documents2026.cmc.docs.shared.matchlinemechanicallc[.]com
efaxdoc.documents2026.docs.shared.lakeviewscustom[.]com
eurosforgroup[.]com
flow505.mooo[.]com
flow55.chickenkiller[.]com
fosterswifts[.]com
frontdesk[.]click
gcotoncovingtoncontracting[.]com
ghethim[.]com
glafondbottamconstruction[.]com
globlasumi[.]com
gregor.justdied[.]com
grincool[.]xyz
haevy-llc[.]com
hcnyecom[.]com
hivezoom[.]com
ideahom[.]world
incommecialre[.]com
innvisoin[.]net
insigthinvestments[.]com
investomind[.]biz
jacobpwpinc[.]org
jjnysnobiogtx[.]org
kilishy.qhigh[.]com
kuer[.]online
lampadasdeslgn[.]com
lawyer.cuztools[.]com
lifetimeroofsystem[.]net
linking.mefound[.]com
linogomes-pt[.]cc
lionheartsecurityservice[.]com
liyuda[.]com
login.microsoft365.outlook.copilotsoffice365.lntactpr[.]com
login.office365outlooks.microsoft.cloud-outlook.naregruop[.]com
m365cloud.login.outlook.office365.azgymfloor[.]com
maqaigiapelhani[.]cam
metlarnelaw[.]com
metrorocl.co[.]uk
mgproparties[.]com
minda-mo[.]com
mouphyweb[.]com
naregruop[.]com
nicewayrealestate[.]cc
noxband[.]com
off365acess.jumpingcrab[.]com
off365mail[.]club
office0365login.2waky[.]com
outlookdrive.microsoftonline.common.oauth2.client.buycerm[.]com
outlookoffice365.microsoftcopilots.vigilantlnc[.]com
paulecosconnect[.]com
payapp.auth.outlook2026common.copilos26.bettylnc[.]com
pdfdocshared.auth.outlook2026common.copilos26.ikextal-co-kr[.]com
pdlhaelth[.]com
pdocshared.documents2026.docs.shared.ecmholdlnggroup[.]com
pdocshared.payments2026.outlooks.common.ecmholdlnggroup[.]com
photosofus[.]com
plusoptlx[.]com
priorispace[.]biz
psionicsandhorses[.]net
rapid-scale[.]net
reauth.copilot.auth.outlook.mcloud365.buycerm[.]com
reauth.copilot.auth.outlook.mcloud365.myhalnc[.]com
reauth.copilot.common.outlook.mcloud365.atlarchitacts[.]com
reauth.docs.copilot.auth02.outlook.mcloud365.argentventuras[.]com
rektham[.]online
rubinsrudman[.]com
rustlnsurance[.]com
sdocshares.auth.outlook.copilos26.general.csr-rooflng[.]com
sdocshares.auth.outlook2026common.copilos26.csr-rooflng[.]com
sdocshares.authoutlooks.common.copilots2026.hathormson[.]com
seatacsmarine[.]com
sedocs.docs.payrol2026.common.copilots2026.vatrarnsformer[.]com
shared.paymentsclouds.statementsapproved.jetbusinesscapltal[.]com
slybee[.]com
snk-s[.]org
solutions00fileptroduct[.]com
sorensenmaysflower[.]blog
statement.docdriveoauth.authorized.copilot.syrosconstructlon[.]com
statement.outlookoffice365.microsoftcopilots.calmechc[.]net
statements.outlook.office365microsoft.payment.run.stoneclty[.]com
stellarntis-fs[.]com
studeseliamechan[.]link
sunraycontractlng[.]com
sunstateaquips[.]com
swiftii.chickenkiller[.]com
tentkit[.]com
thepaybank[.]com
thewiginton[.]com
topcoatmetalsfinishing[.]com
toplinebuy[.]com
torvion[.]life
unitadrentals[.]com
unitedwirescompany[.]com
us-agricultures[.]com
vasquezmyth[.]com
westlakeproduces[.]com
whitfillsnursery[.]com
wsochares.authpayments.common.paid2026.bullochdirtwroks[.]com
wwriwashingtonenergy[.]com
zrs-wooding[.]com
ShiFu
I'm a Threat Intelligence Analyst focused on tracking cybercriminal groups and other malicious activity clusters. I previously worked as an Application Security Engineer and have a background in CTF competitions, with experience in offensive security, malware analysis, and application security.
0 comments