Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Sality

48
Global rank
106 infographic chevron month
Month rank
113 infographic chevron week
Week rank

Sality is a highly sophisticated malware known for infecting executable files and rapidly spreading across networks. It primarily creates a peer-to-peer botnet that is used for malicious activities such as spamming, data theft, and downloading additional malware. Sality has strong persistence mechanisms, including disabling security software, making it difficult to remove. Its ability to spread quickly and silently, along with its polymorphic nature, allows it to evade detection by traditional antivirus solutions.

Botnet
Type
ex-USSR
Origin
1 June, 2003
First seen
7 October, 2026
Last seen

How to analyze Sality with ANY.RUN

Type
ex-USSR
Origin
1 June, 2003
First seen
7 October, 2026
Last seen

IOCs

IP addresses
23.194.190.156
135.233.95.144
23.11.41.157
2.21.239.135
48.209.138.168
40.126.32.138
2.16.204.147
172.211.123.250
74.179.77.164
23.59.18.102
48.192.1.65
204.79.197.203
95.100.102.101
20.190.159.73
2.23.246.9
2.16.241.197
48.209.138.189
2.16.241.7
74.178.76.54
74.179.77.204
Hashes
d99aaa09108e56886ab53484575db5b11f400a8a6461d32adf630935ccd4b4d9
e2c2da27bf6e2c2f8d076b9a95419a249754dc51ce6a4940c80b4af6ec9472e1
cc2061daca3f976432c1ebdb2d76486bec7a59b2fe8d57ddd68dff08beda2668
33685b6605e7fccdfa150f296d30d331892451336ad45d027dd321a2560ff319
337d2fb5252fc532b7bf67476b5979d158ca2ac589e49c6810e2e1afebe296af
31aee70f9705f6578c6b41849ea3b5a948a446f494f24befcf5b169a1c2a71d2
6d0de9903f25ee1fcd9b2642bdf5bb4083ebc9a72385f740f8fe85658f02345b
41618b0199a1269bdbfc7290159c4bda8e5473280cc578821174d3c3483b4aa6
3ae7de963b55631bcf739d25d4f593d93fb1e280ccdc0473d0e7ab765ffab45b
6e790f1424b4b5c892e3f32c5234c628d4587f9908ab72f0a455aa539bfa94e3
decb14c09f68602f9548d5bde4e2bbc89e3b1135c3f305848c03d2a0cbffddad
a8bd79d517ce20c88626ef5df4e216c46a4a7770223a7f6f11d926afaaee606f
b9eb96fe13bbc94b3d494ee247dbd18c9899d58b4aefa70e8fc6bfa2a9cad996
aa945c7f150ea4cee481e78dfb9f1cf4516079a2e02291960d2d09b905de980b
80bb3c56d40c39beca7775b82408e726baa1f30eeeaff1df7ac4b458882b0921
546e3e401aef46030266b8bc73a6cbbcf6ae2bb37bfc12d93edadfec33444e86
7b2ee52e8fcbd361df74ee49d1796a3acaa6adc2b657dc4e7fdd07e7a0b9fc03
fbc0168b9d9ff457e1e97aa126d03194960f159770077ef90b27a422192db621
03e0c6c4ca8a24f961477887763397045e67862e059f7494014aefc21891d40e
3e5e033f1b11bf0fc122d1b16eb5b376e608cb1ae287362dd646f4c76c370914
Domains
self.events.data.microsoft.com
oneocsp.microsoft.com
slscr.update.microsoft.com
client.wns.windows.com
ecs.office.com
www.microsoft.com
activation-v2.sls.microsoft.com
crl.microsoft.com
th.bing.com
ocsp.digicert.com
login.live.com
settings-win.data.microsoft.com
fe3cr.delivery.mp.microsoft.com
google.com
www.bing.com
go.microsoft.com
eip-terr-eu.cdp1.digicert.com.akahost.net
prod.ingestion-edge.prod.dataservices.mozgcp.net
dns.msftncsi.com
ctldl.windowsupdate.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.3.crl
http://www.microsoft.com/pkiops/crl/microsoft%20update%20signing%20ca%202.2.crl
Last Seen at
Last Seen at

Recent blog posts

post image
Making Threat Intelligence Work for SOC Teams...
watchers 230
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 2820
comments 0
post image
IronChain Ransomware Threatens Businesses wit...
watchers 4352
comments 0

What is Sality malware?

Sality is a file-infecting virus and botnet malware first observed around 2003. It primarily targets Windows systems, infecting executable files (.exe) and spreading rapidly across networks and removable drives.

Over time, it has become highly persistent and adaptive, evading traditional security measures through polymorphism, constantly changing its code to avoid detection.

Similar to other botnet malware like Phorpiex and Mirai, Sality has infected hundreds of thousands of computers globally, creating a massive botnet. The malware operators use this network for various purposes, ranging from relatively "benign" tasks like generating spam to more malicious activities, such as distributing password stealers. In 2011, one of the programs distributed through the Sality botnet focused on stealing web credentials, particularly targeting Facebook and Google Blogger accounts.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Sality malware technical details

The primary functionality of Sality malware includes:

  • Spreads by infecting executable files and removable drives.
  • Uses polymorphic techniques to change its code with every infection, making it harder for antivirus software to detect or create consistent signatures.
  • Creates a P2P botnet for malicious activities like data theft and DDoS attacks.
  • Disables antivirus and firewall protections and uses rootkit techniques to hide its presence on the system.
  • Modifies the infected system’s hosts file to block access to security websites, preventing the user from downloading tools or updates that might detect or remove the virus.
  • Allows attackers to update and control infected systems remotely.

Sality connects infected machines to command and control (C2) servers or other infected systems within its botnet. This allows attackers to issue commands, download additional malware, and update the virus, ensuring it remains persistent and adaptive in its attack methods. Through this botnet, Sality can be used for a wide range of malicious activities, including:

  • Spamming
  • Distributed Denial of Service (DDoS) attacks
  • Data theft
  • Downloading additional malware

The data exchanged between the infected system and C2 servers is often encrypted, making it difficult for security experts to analyze the malware's activities.

Sality malware execution process

To see how Sality operates, let’s upload its sample into the ANY.RUN sandbox.

Once the Sality malware is executed, the stub decrypts and runs a secondary code segment known as the loader. The loader operates in a separate thread within the infected process and is responsible for executing the malware's main payload.

Sality actively targets security software by terminating antivirus-related processes and deleting files critical to system security. It may also modify system settings to reduce security levels and block the execution of security tools.
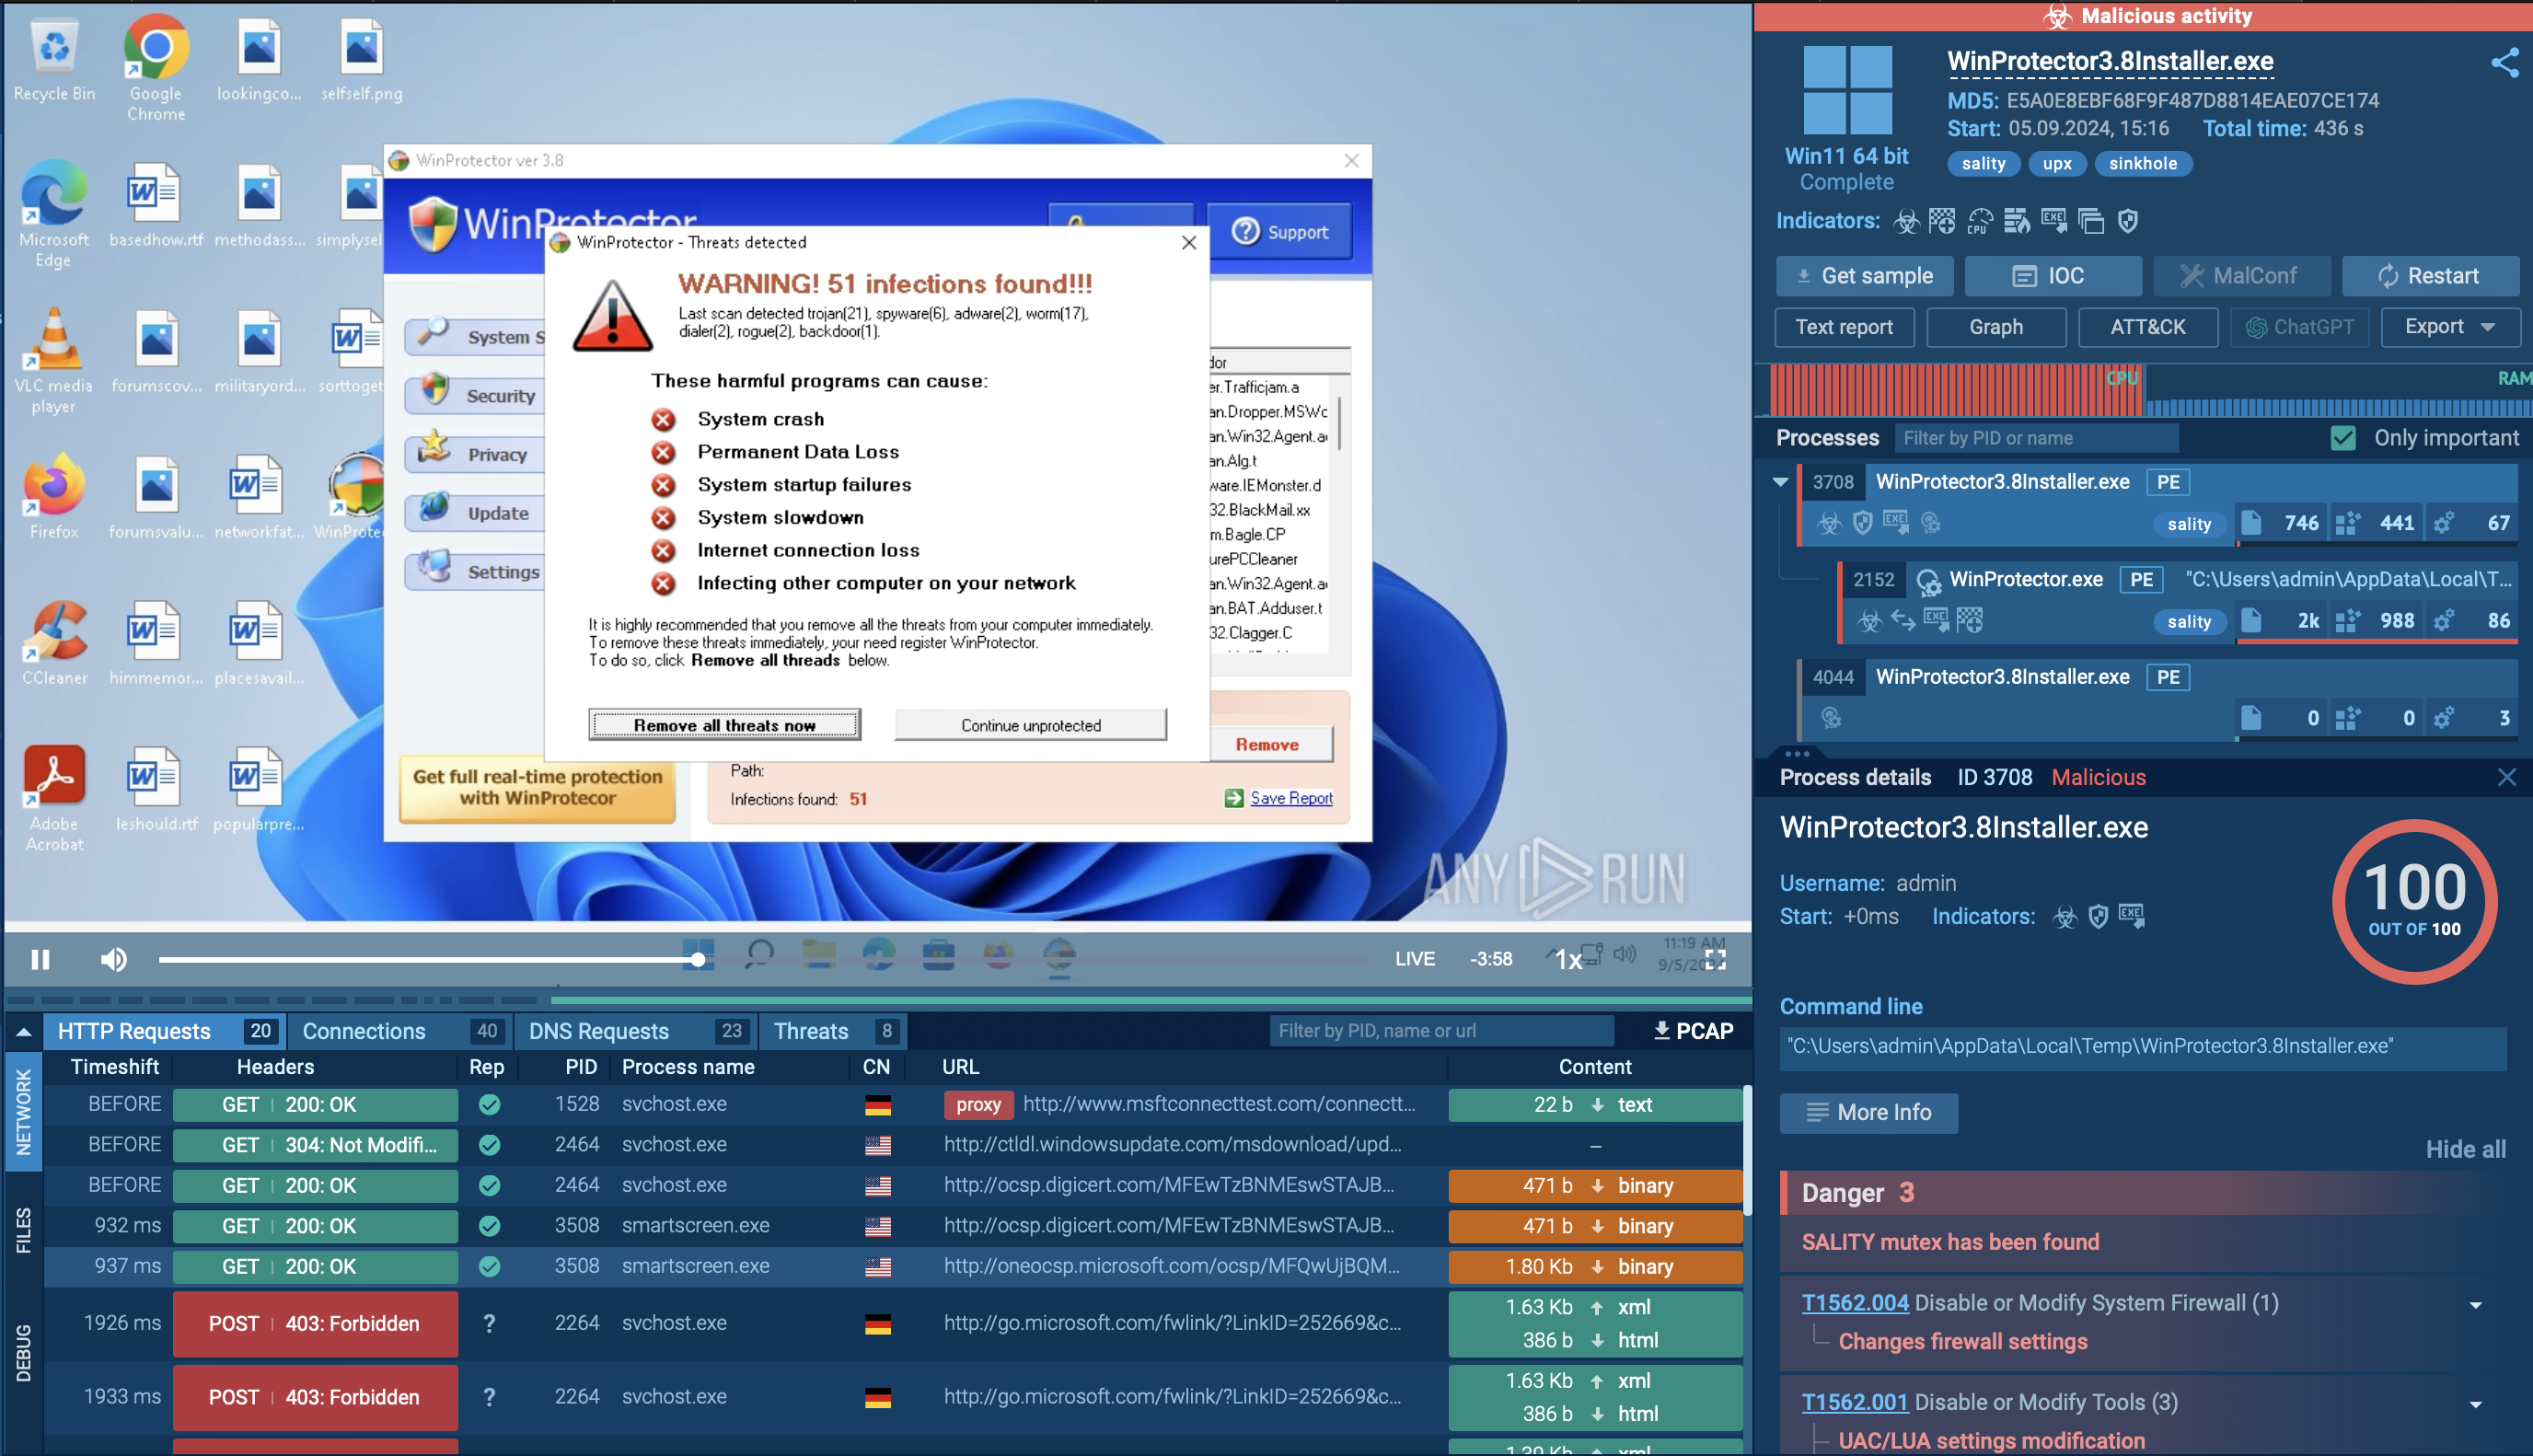
Sality malware in ANY.RUN Sality malware analyzed in the ANY.RUN sandbox

The malware is capable of stealing sensitive information, such as cached passwords and keystrokes, and can search for email addresses to send spam. It communicates with remote command and control (C2) servers, often utilizing a peer-to-peer (P2P) network to download additional malicious payloads or updates.

Modern Sality variants can form botnets, enabling attackers to control multiple infected machines. The botnets can be used for various malicious activities, including distributed denial-of-service (DDoS) attacks and further malware propagation.

Sality can also download and execute other malware, often through a preconfigured list of peers within its P2P network, allowing it to expand its capabilities and maintain persistence on infected systems.

Use ANY.RUN free for 14 days

Try the full power of interactive analysis

Start your free trial

Sality malware distribution methods

Sality malware employs several distribution methods that allow it to spread widely across networks and systems:

  • File infection: Sality primarily infects executable files (.exe) on infected machines, which helps it spread as these files are shared or transferred across systems.
  • Removable drives: The malware spreads through infected USB drives, external hard drives, and other removable media. When these drives are connected to other machines, Sality automatically infects them.
  • Network shares: It can spread across local networks by infecting shared folders and files, making it highly effective in corporate or organizational environments with multiple connected systems.
  • Peer-to-Peer (P2P) botnet: Sality creates a decentralized botnet, enabling it to communicate with other infected machines, spreading its payload and receiving updates from the attacker.
  • Self-replication: Once inside a system, Sality can modify system files, allowing it to replicate itself and infect more files and applications.

Gathering threat intelligence on Sality malware

To collect up-to-date intelligence on Sality and its latest variants, use Threat Intelligence Lookup. The service helps you search across a vast database of quality threat data sourced from millions of malware analysis sessions conducted in the ANY.RUN sandbox. It lets you use over 40 different search parameters and their combinations, including IPs, domains, command line artifacts, and process names.

Let's use a mutex fragment found in one Sality sample to find more samples. To do this, we'll submit the following query: syncObjectName:".EXEM_"
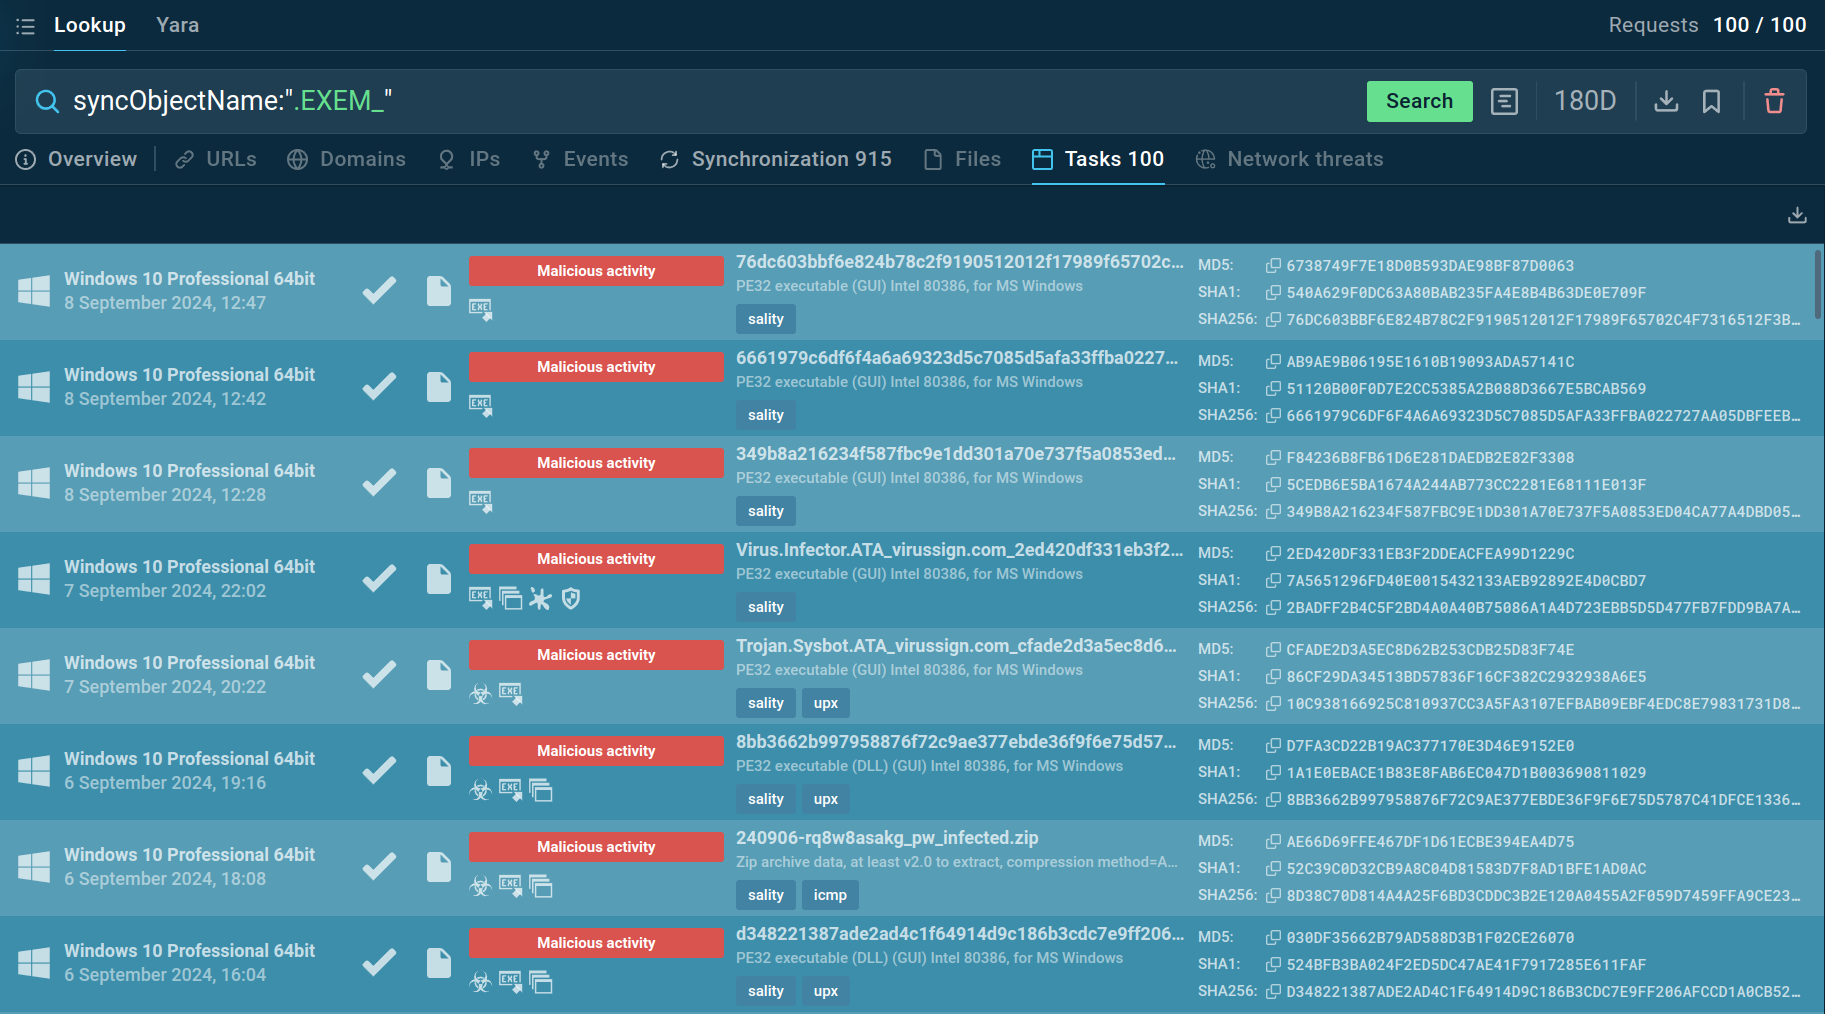
Sality query in ANY.RUN Sality mutex query in Threat Intelligence Lookup

The service returns one hundred sandbox sessions that we can explore further.

Get a 14-day free trial of Threat Intelligence Lookup along with the ANY.RUN sandbox

Conclusion

Sality’s ability to spread through infected files, disable security software, and form a botnet makes it a potential threat. Its focus on persistence and evading detection highlights the need for strong security measures. To effectively protect against Sality, it's important to use tools like malware sandboxes to thoroughly analyze suspicious files and detect threats early.

ANY.RUN offers a powerful solution, allowing users to safely examine and understand threats like Sality in real-time. By utilizing ANY.RUN, you can quickly detect and neutralize malware before it can cause harm to your systems.

Sign up for a free ANY.RUN account today and start analyzing malware with no limits!
HAVE A LOOK AT

BlackMatter screenshot
BlackMatter
blackmatter
BlackMatter is a ransomware strain operating as a Ransomware-as-a-Service (RaaS), designed to encrypt files, remove recovery options, and extort victims across critical industries. Emerging in 2021, it quickly became a major concern due to its ability to evade defenses, spread across networks, and cause large-scale operational disruption, forcing security teams to act against a highly destructive and persistent threat.
Read More
Balada Injector screenshot
Balada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
Read More
Gunra screenshot
Gunra
gunra
Gunra ransomware, a financially motivated threat actor that emerged in April 2025, deploys double-extortion tactics to encrypt victims' data and threaten leaks of exfiltrated information, primarily targeting Windows and Linux systems across healthcare, manufacturing, and other sectors worldwide.
Read More
Emmenhtal screenshot
Emmenhtal
emmenhtal
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
Read More
Spyware screenshot
Spyware
spyware
Spyware is a stealth form of malware whose primary objective is to gather sensitive information, such as personal data, login credentials, and financial details, by monitoring user activities and exploiting system vulnerabilities. Spyware operates secretly in the background, evading detection while transmitting collected data to cybercriminals, who can then use it for malicious purposes like identity theft, financial fraud, or espionage.
Read More
RedLine screenshot
RedLine
redline stealer redline stealer malware
RedLine Stealer is a malicious program that collects users’ confidential data from browsers, systems, and installed software. It also infects operating systems with other malware.
Read More