Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

Gh0st RAT

21
Global rank
32 infographic chevron month
Month rank
28 infographic chevron week
Week rank

Gh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.

RAT
Type
China
Origin
1 January, 2008
First seen
13 October, 2026
Last seen
Also known as
Ghost RAT

How to analyze Gh0st RAT with ANY.RUN

RAT
Type
China
Origin
1 January, 2008
First seen
13 October, 2026
Last seen

IOCs

IP addresses
8.217.97.89
2.22.251.19
2.19.14.89
40.126.31.69
23.11.40.157
20.190.160.22
48.209.133.15
204.79.197.203
150.171.109.105
48.192.1.64
74.178.76.128
39.103.20.122
128.24.231.65
172.211.123.249
151.101.2.133
2.21.134.137
118.178.60.2
2.22.251.56
135.232.92.97
172.236.108.48
Hashes
b1bb97228519a4d57c6e5d3842e0a0d4a3c6c5c399c6fe35434a271c0c4c4477
45f6a4d88ec16ed17af2c337c7d105395c4f6e715a5ae9d3e359980b0cfd34b1
71510f5a478fc44950a155bc66616b38041cc1e13573aeefaf0d734ef4e88c50
71369dd8ef596d4eefaf21b831dc87f78eeaf2c3436eb95c24981a6d39151dd7
7eb70257593da06f682a3ddda54a9d260d4fc514f645237f5ca74b08f8da61a6
676a2a7b94ca2f8ec76352ee656e4d075bb342bd7ad6efbc7c19c060001eace7
c0627c59e27a670503683d2c5c117e126f4969144815317540895066c819b6f6
7030d5a1b97df460148af34af27501f69cd4822dc7b912fa8c4cb8ef7e8daba2
fad5dfbf59a7c208594aca09f020a2d32c0edf004cbdfffe6bfae7a72c905425
ea41d3b33fcf4929823c1a054d92208bb6275c3281da3b77d8a3521b261b2646
f5bfec979b53dd7b0c467f06ade20b3b2a6a006f1f045530ada92f405b6510c2
a70e8f7d7d850f36f2c39d0d1b7dd964ddb15ee24755e660d14953665890d34a
2b712da245df9ec314512907e368fa5db7c49e560a1603df21359d70a71a73d8
ad888faa532c61a6ac8349f17aedc54ebf96e986c3e402e5899db489f7c167c7
76947997c0288c847e644a37d890fd82262d2520a781272290e696bc16fafc4c
5c30c3481249955427ca5c1bbc333afcfb2a386530253ce04aeffe41e57c9f5e
0cd331d6051f6e994dca509f999b011cf5fc90c1a554c08605a56da64c54c232
69a413227dfe6f72544acb9b193c5a49c77f22818a5cd00eec278e8819e730e4
71166f43035f2ea53ee16f642ee2a25ff17443247b2ede79e9721f1e5eb049a5
ceaf1bbad5b53c9ed8922660ef0b66e4c0ad23baaa403ae3b790a8685ba38645
Domains
cbxjtn.net
crl.microsoft.com
ocsp.digicert.com
self.events.data.microsoft.com
www.microsoft.com
slscr.update.microsoft.com
client.wns.windows.com
login.live.com
th.bing.com
google.com
ecs.office.com
activation-v2.sls.microsoft.com
mm2027.oss-cn-hangzhou.aliyuncs.com
oneocsp.microsoft.com
nexusrules.officeapps.live.com
ocsp.globalsign.com
settings-win.data.microsoft.com
6y0ier.oss-cn-beijing.aliyuncs.com
fe3cr.delivery.mp.microsoft.com
pub-cdd0dd27ae6a4aee9841d397e0496374.r2.dev
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f13%2f2026%2c%201%3a33%3a00%20pm
https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
https://www.bing.com/th?id=odswg.03eba6b0-8221-45bc-973b-b64989784fd1&pid=dsb
https://login.live.com/rst2.srf
https://login.live.com/ppsecure/deviceaddcredential.srf
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://ocsp.globalsign.com/gsgccr46ovtlsca2025/me0wszbjmecwrtajbgurdgmcgguabbtgcaxkorhgdx8jdesq%2bzt9%2b6dr%2fqquaxq%2br8nbazvj7hrbwpp6stcy2qicdg0q%2ftjthupjna5m%2ba%3d%3d
https://6y0ier.oss-cn-beijing.aliyuncs.com/tad
https://6y0ier.oss-cn-beijing.aliyuncs.com/a.gif
https://6y0ier.oss-cn-beijing.aliyuncs.com/b.gif
Last Seen at
Last Seen at

Recent blog posts

post image
What's Really Attacking Your Industry? Insigh...
watchers 1699
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 9585
comments 0
post image
5 Critical Pain Points of Modern US SOCs and...
watchers 10824
comments 0

What is Gh0st RAT malware?

Gh0st RAT is one of the long-standing members of the global threat landscape. Launched in 2008, it remains in full operation to this day. The RAT part in the malware’s name stands for Remote Access Trojan, meaning that it provides attackers with the capacity to control the victim’s machine and manipulate it.

The original developers of Gh0st RAT were from China. However, due to the open-source nature of its code, criminals from many other countries have created their iterations of the malicious software. As a result, there are many versions of this trojan with varying sets of features.

If you're interested in exploring variants of Gh0st, we recommend reading our article about Gh0stBins, Gh0stBins, Chinese RAT: Malware Analysis, Protocol Description, RDP Stream Recovery.

The most notable aspect of Gh0st RAT is that it has been utilized by criminal groups linked to the Chinese government. For instance, in 2009, the malware was used to target Tibetan organizations. There were also instances of attacks on businesses in various fields, including healthcare and banking.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

Technical details of the Gh0st RAT malicious software

The standard set of features of Gh0st RAT includes the following:

  • Mouse and keyboard manipulation: The malware can record the keys that a user presses on their keyboard, as well as the movements of the mouse. Thus, attackers can discover passwords and other credentials used by the victim. It also can disable these devices.
  • Screenshot and webcam capturing: Gh0st can take a picture of the user's computer screen and webcam. This is often employed by threat actors to conduct surveillance.
  • Microphone recording: The malware is also capable of listening to the user's microphone.
  • File system access: The RAT can transfer files between the infected computer and its remote server. Subsequently, it can both steal sensitive information and drop additional malware, as well as execute it and run programs or scripts.
  • System reboot: It can restart the system to gain persistence and shut it down completely to prevent the victim from attempting to mitigate the threat.

To persist on the system, Gh0st RAT adds registry entries that allow it to automatically execute itself on every system startup. The malware can scan the system to determine if it is running inside a virtual machine and if antivirus software is installed. These actions help it hide its behavior from security analysts and avoid detection. It also utilizes encryption to obfuscate its functions.

Essentially, Gh0st operates similarly to other RAT malware families, such as njRAT and DCrat.

Execution process of Gh0st RAT

By uploading a sample of Gh0st RAT to ANY.RUN, an interactive sandbox for malware analysis, we can observe its malicious processes in detail and collect IOCs.

The execution process of the Gh0st Stealer typically begins with a user inadvertently downloading or executing a malicious file, often disguised as legitimate software or attached to phishing emails. Once executed, the malware establishes a connection to a remote command and control (C2) server, allowing the attacker to remotely control the infected system. This malware utilizes various system tools for execution, such as CMD in our example.

Gh0st Stealer then begins its data theft operations, scanning the system for sensitive information such as usernames, passwords, and financial data. Captured data is exfiltrated back to the attacker's server, where it can be used for malicious purposes or sold on the dark web. The malware may also maintain persistence on the compromised system, allowing for continued data theft and remote control capabilities. In our task stealer use steganography techniques in order to prevent the detection of hidden information – It hides an encrypted DLL file inside a downloaded JPEG image.
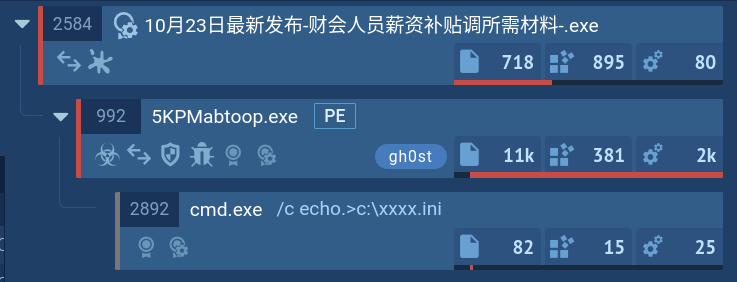
Gh0st process tree shown in ANY.RUN Gh0st process tree demonstrated in ANY.RUN

Gathering threat intelligence on Gh0st RAT malware

To collect up-to-date intelligence on Gh0st RAT, use Threat Intelligence Lookup.

This service gives you access to a vast database filled with insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox.

With over 40 customizable search parameters, including IPs, domains, file names, and process artifacts, you can efficiently gather relevant data on threats like Gh0st RAT.
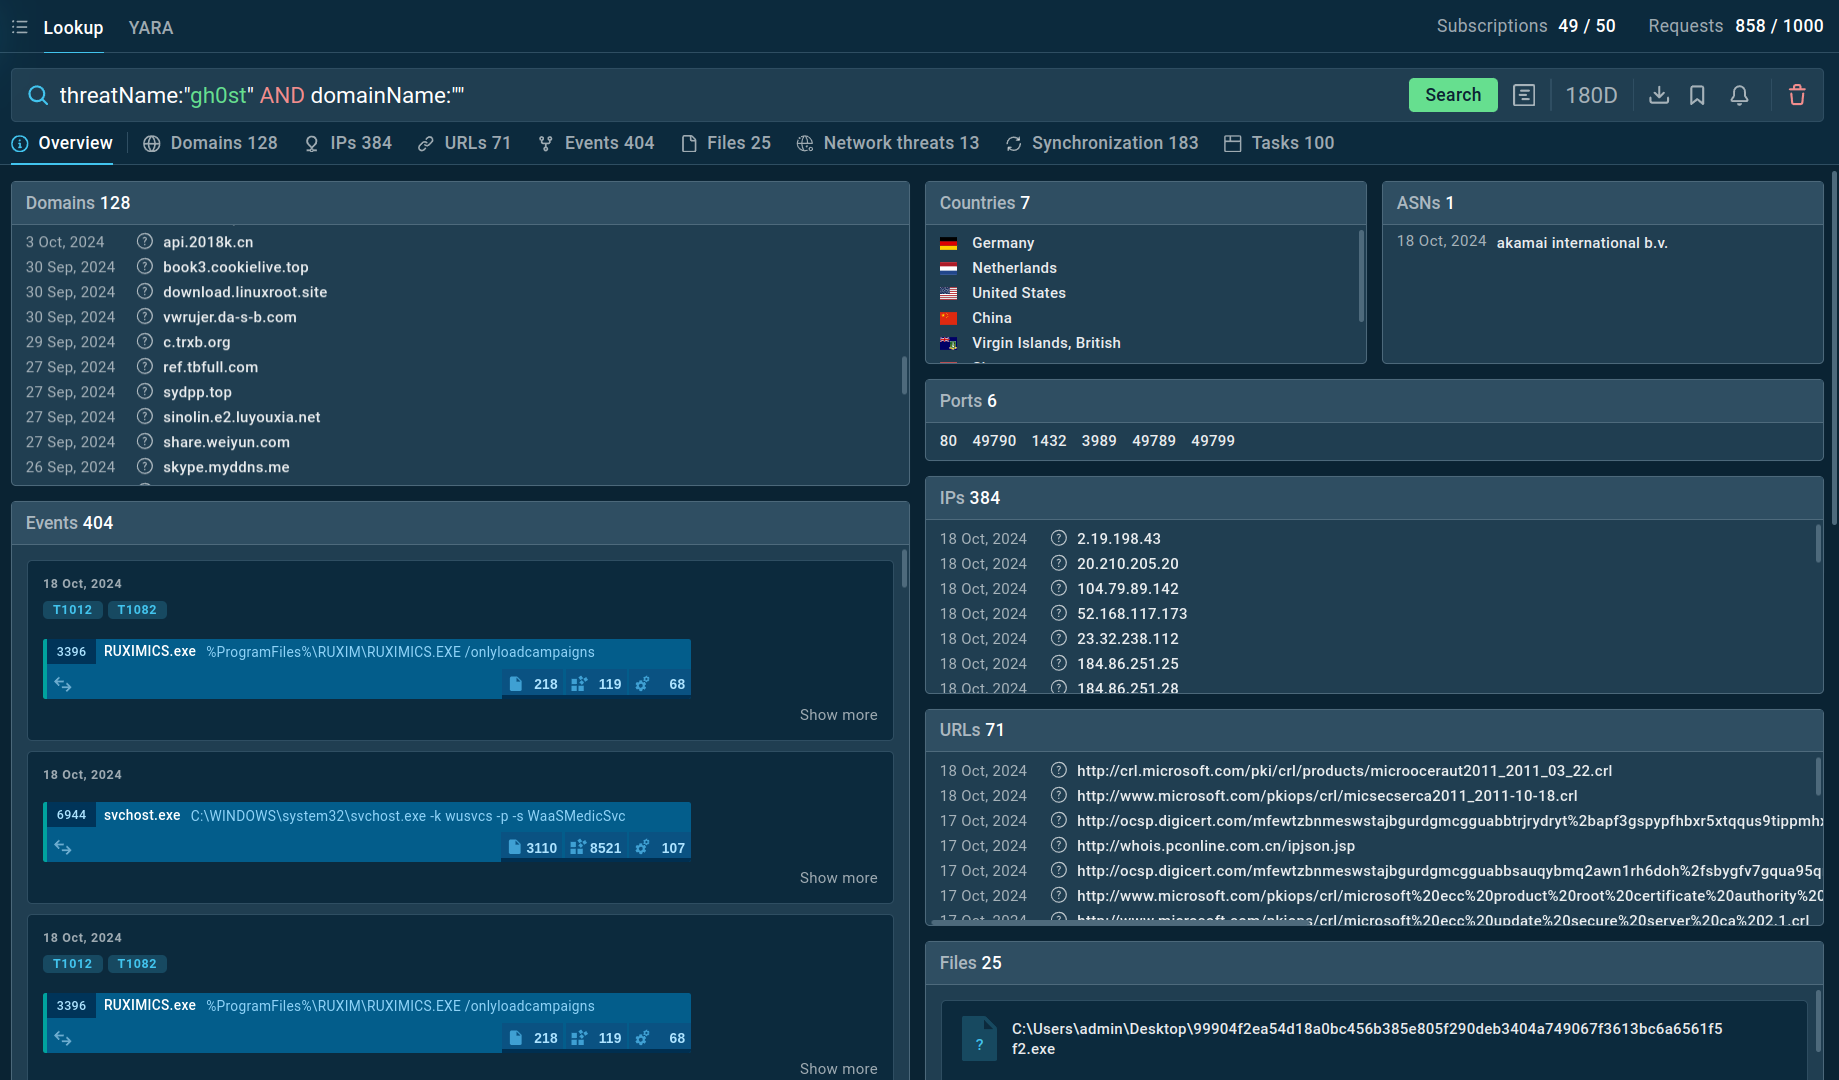
Gh0st RAT ANY.RUN Search results for Gh0st RAT in Threat Intelligence Lookup

For example, you can search directly for the threat name or use related indicators like hash values or network connections. Submitting a query such as threatName:"gh0st" AND domainName:"" will generate a list of files, events, domain names, and other data extracted from Gh0st RAT samples along with sandbox sessions that you can explore in detail to gain comprehensive insights into this malware’s behavior.

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Distribution methods of the Gh0st RAT malware

As mentioned earlier, Gh0st RAT is often used in targeted campaigns against government organizations and businesses. In order to carry out them successfully, attackers implement the method of spear phishing.

This involves composing emails that are similar to those sent by legitimate entities to trick the victim into downloading a malicious attachment or clicking on an unsafe link.

Conclusion

Gh0stRAT is a veteran RAT with an open-source code that continues to be used by both individuals and organized groups in attacks around the world. Due to the fact that phishing campaigns constitute the key starting point of infection, businesses need to exercise extra vigilance when handling suspicious emails.

By analyzing all files and emails from unknown senders in ANY.RUN, companies can quickly identify whether they were targeted by criminals. The service offers conclusive verdicts on the malicious activities of samples and generates comprehensive reports, containing IOCs and configs to ensure future detection.

Try ANY.RUN for free – request a demo!

HAVE A LOOK AT

BQTLock screenshot
BQTLock
bqtlock baqiyatlock
BQTLock is a ransomware-as-a-service (RaaS) malware family that emerged in 2025 and quickly gained attention due to its combination of file encryption, credential theft, and data exfiltration. BQTLock encrypts files using a hybrid AES-256 and RSA-4096 encryption scheme, demands payment in Monero cryptocurrency, and performs data theft and system reconnaissance.
Read More
Black Basta screenshot
Black Basta
blackbasta
Black Basta is a ransomware-as-a-service operated by Storm-1811. It emerged in 2022 and uses double extortion tactics, encrypting data and stealing it for ransom. The malware often gains access through spear-phishing and uses tools like QakBot and Cobalt Strike. It's known for exploiting system vulnerabilities and using advanced obfuscation techniques.
Read More
Jigsaw screenshot
Jigsaw
jigsaw
The Jigsaw ransomware, initially detected in 2016, encrypts files on compromised systems and requires a ransom payment in Bitcoin. If the ransom is not paid, the malware starts deleting files, increasing the pressure on victims to comply. Its source code is publicly accessible, allowing various threat actors to customize and repurpose the malware for different objectives.
Read More
Lynx screenshot
Lynx
lynx
Lynx is a double extortion ransomware: attackers encrypt important and sensitive data and demand a ransom for decryption simultaneously threatening to publish or sell the data. Active since mid-2024. Among techniques are terminating processes and services, privilege escalation, deleting shadow copies. Distribution by phishing, malvertising, exploiting vulnerabilities.
Read More
Mirage2FA screenshot
Mirage2FA
mirage2fa
Mirage2FA is a Phishing-as-a-Service toolkit designed to compromise Microsoft 365 accounts and bypass conventional MFA through Adversary-in-the-Middle attacks. It uses malicious HTML, XHTML, and SVG files to deliver JavaScript loaders that connect victims to attacker-controlled phishing infrastructure. The toolkit relays authentication in real time, capturing credentials, 2FA codes, and authenticated session cookies. It also uses browser fingerprinting, WebSockets, obfuscation, and rotating infrastructure to evade detection and maintain access to compromised accounts.
Read More
Raspberry Robin screenshot
Raspberry Robin
raspberryrobin
Raspberry Robin is a trojan that primarily spreads through infected USB drives and exploits legitimate Windows commands. This malware is known for its advanced obfuscation techniques, anti-debugging mechanisms, and ability to gain persistence on infected systems. Raspberry Robin often communicates with command-and-control servers over the TOR network and can download additional malicious payloads.
Read More